
gitlab-profile
 staxis-platform/gitlab-profile
Modular Node.js runtime orchestrator with HMAC integrity verification, import guards, and sandboxed execution for secure, layered application…
supply-chain-security
staxis-platform/gitlab-profileModular Node.js runtime orchestrator with HMAC integrity verification, import guards, and sandboxed execution for secure, layered application…

 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
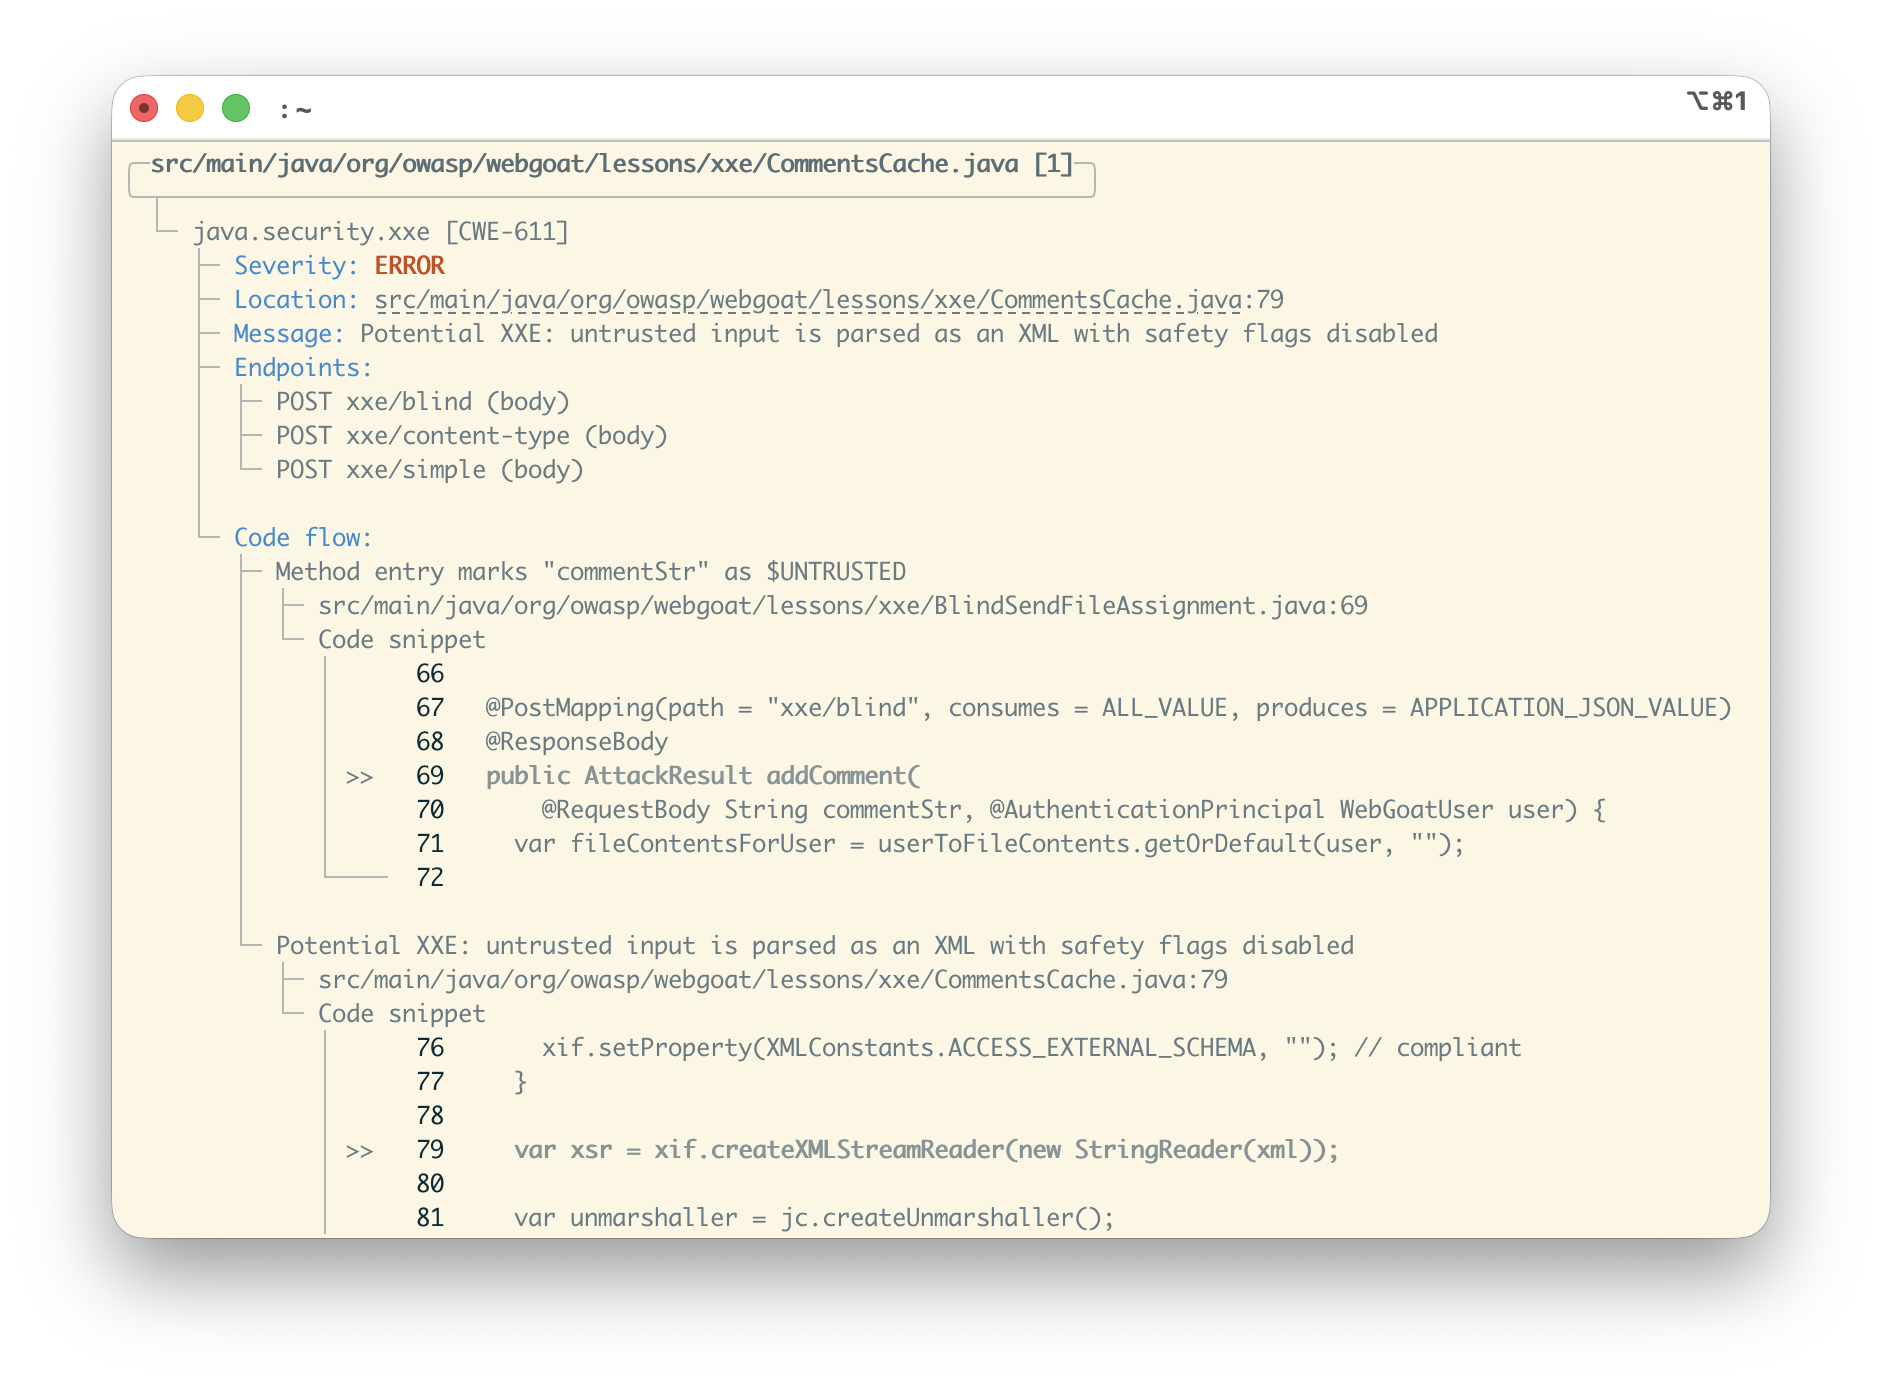 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
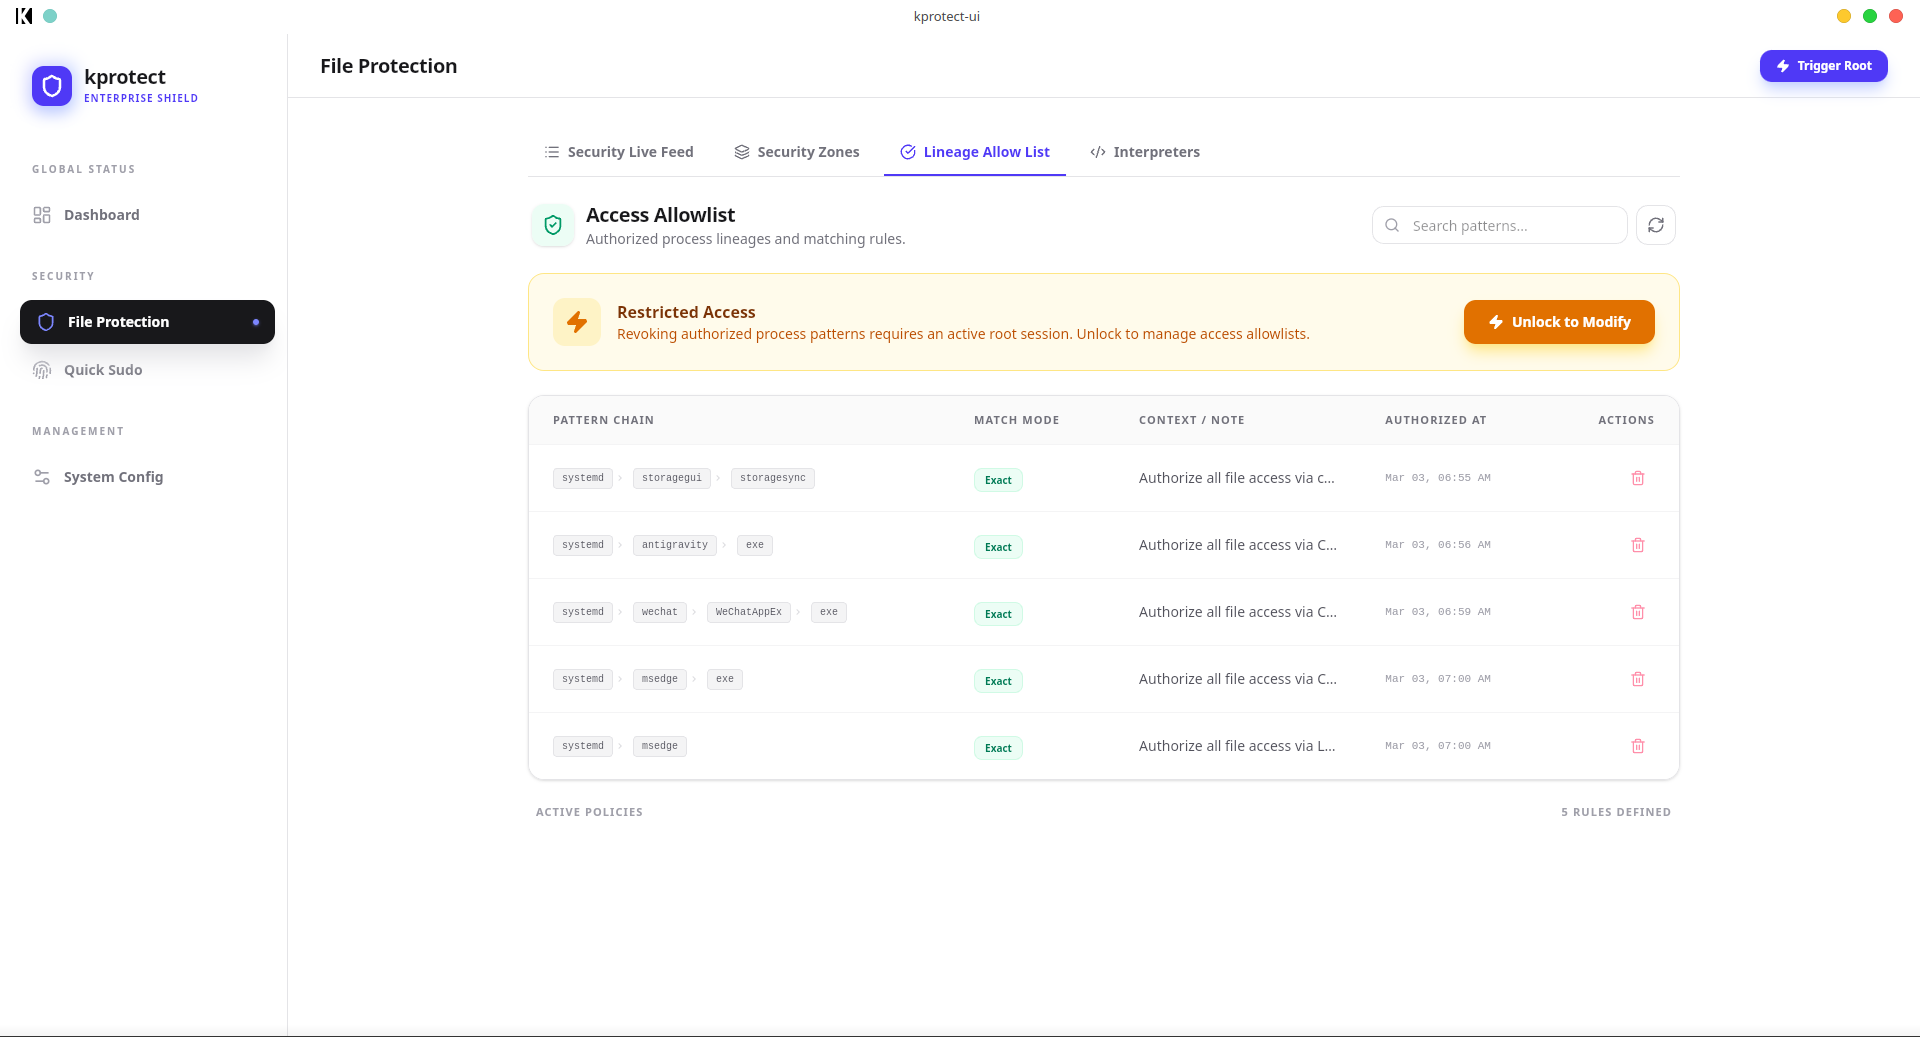 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 wise-security/cve-2026-38945
Proof-of-concept exploit for CVE-2026-38945, demonstrating path traversal in RayVentory Scan Engine's Java detection to execute arbitrary binaries.
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities