
agent-sweep
 ishannaik/agent-sweep
Find and redact secrets in AI coding agent histories (Claude Code, and more).
data-exfiltrationdata-recoveryforensics+3
80
ishannaik/agent-sweepFind and redact secrets in AI coding agent histories (Claude Code, and more).
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 corretto/hotpatch-for-apache-log4j2
An agent to hotpatch the log4j RCE from CVE-2021-44228.
 mhaggis/package-inferno
A Public Package Scanner for The Community
 isecuritytw/seal-security-nuget-demo-net7
.NET 7 fork of seal-security-nuget-demo: same CVE-2024-21907 exploit story, retargeted for customers locked to .NET SDK 7.
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 hackerhermanos/cve-2024-3094_xz_check
This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
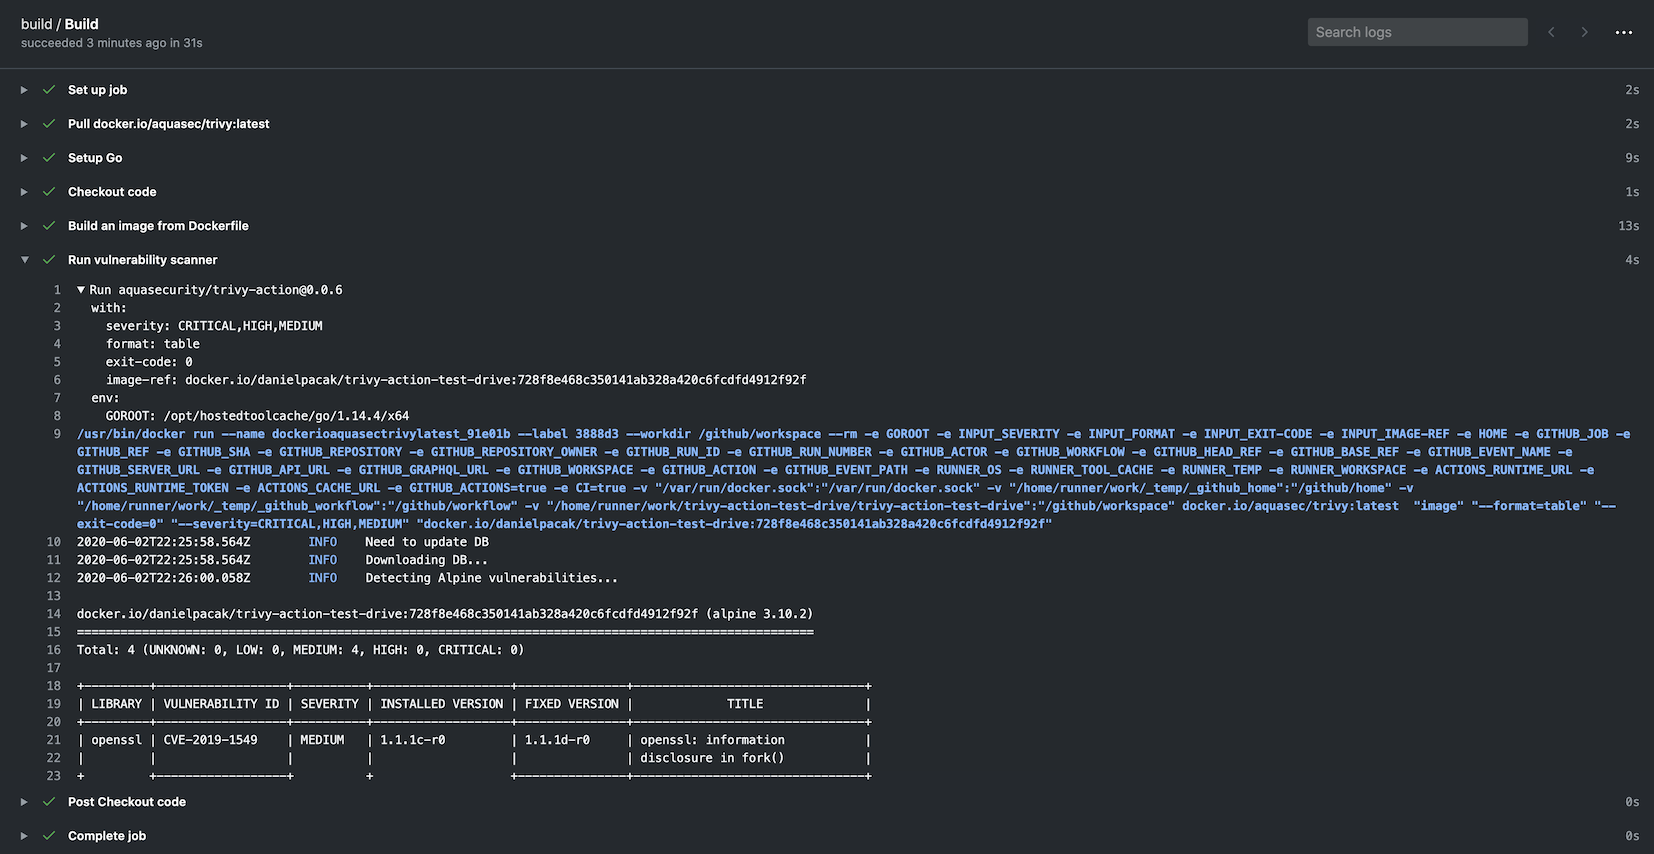 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…