

find-log4j
 perryflynn/find-log4j
Find log4j for CVE-2021-44228 on some places * Log4Shell
incident-responseinformation-gatheringsupply-chain-security+2
2
perryflynn/find-log4jFind log4j for CVE-2021-44228 on some places * Log4Shell
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
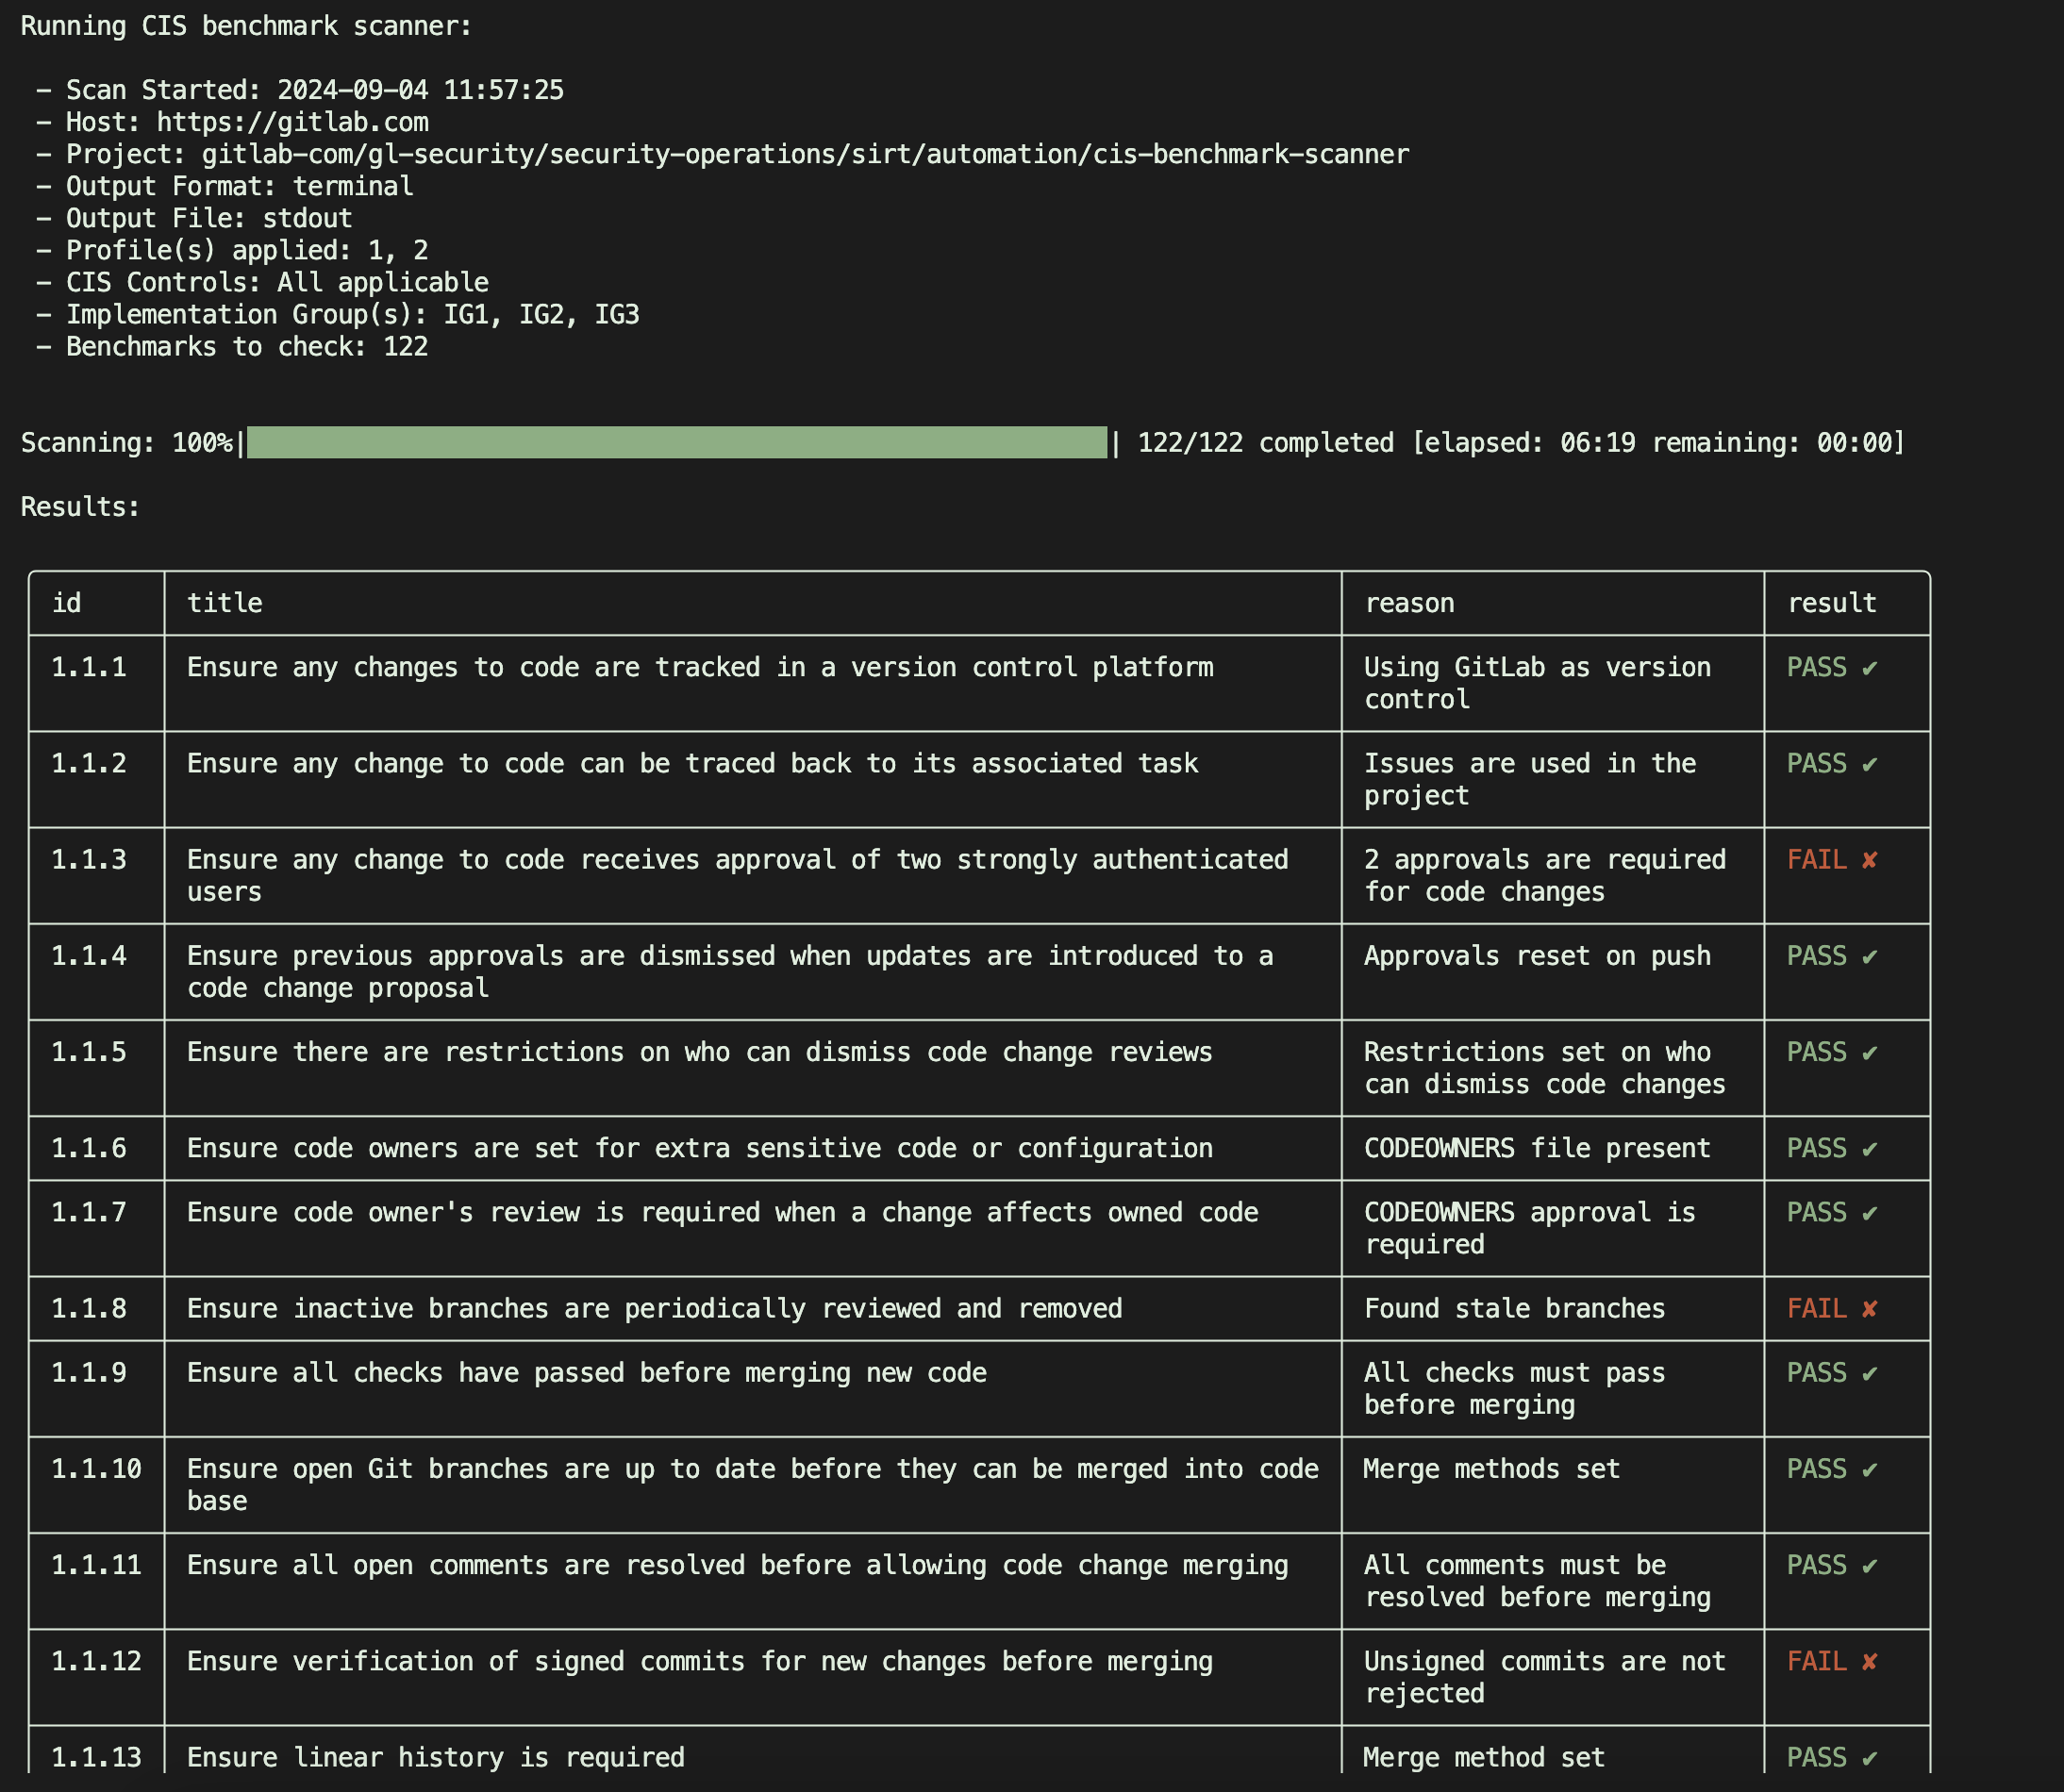
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 s41r4j/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
 vignesh21-git/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 arnica/depsguard
Harden your package manager configs against supply chain attacks.
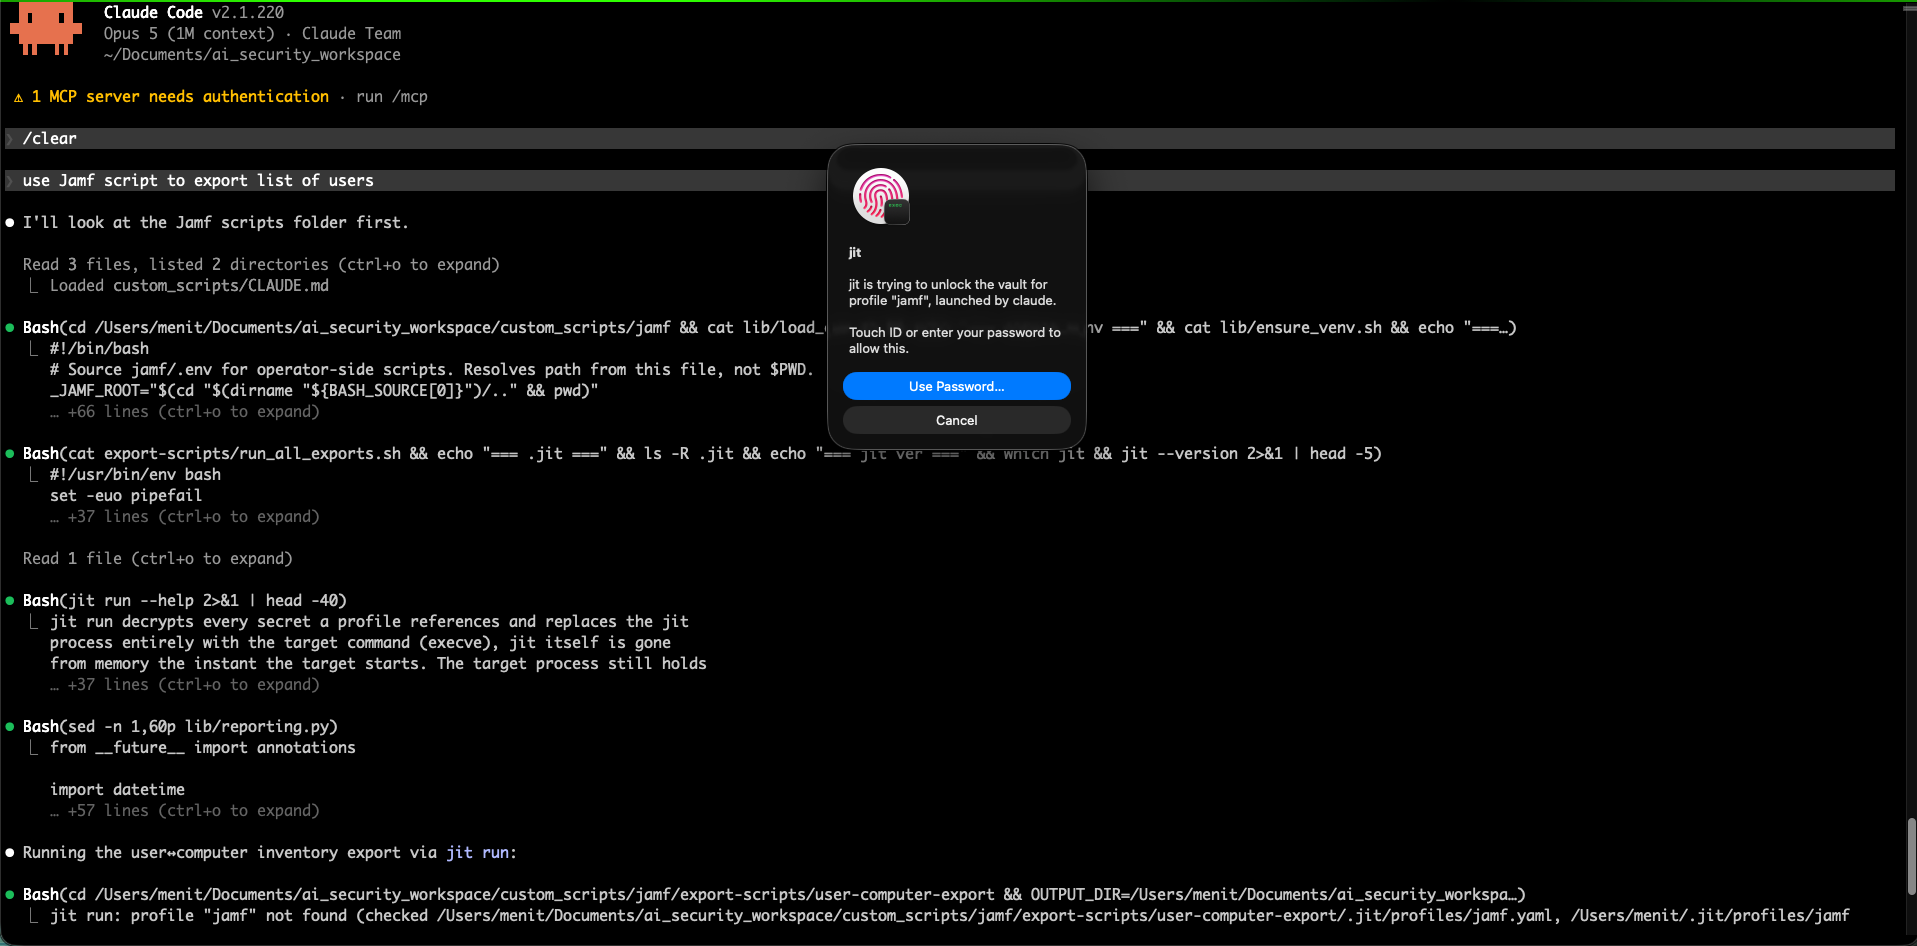 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 vinnimarcon/log4j-updater
Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228
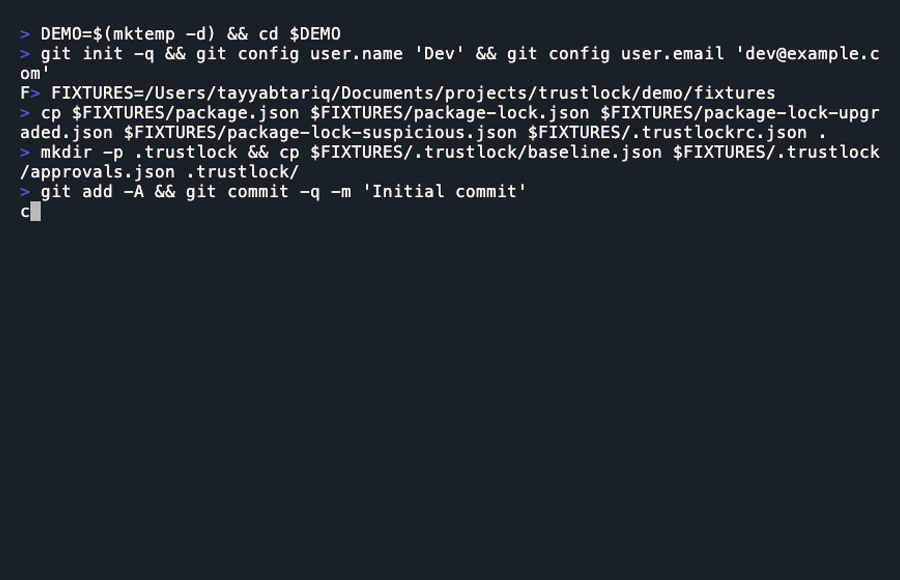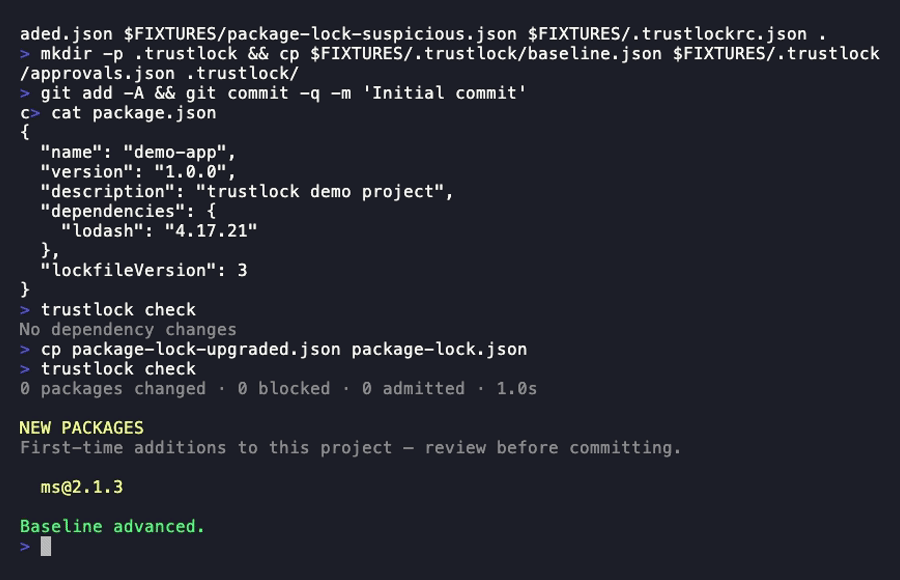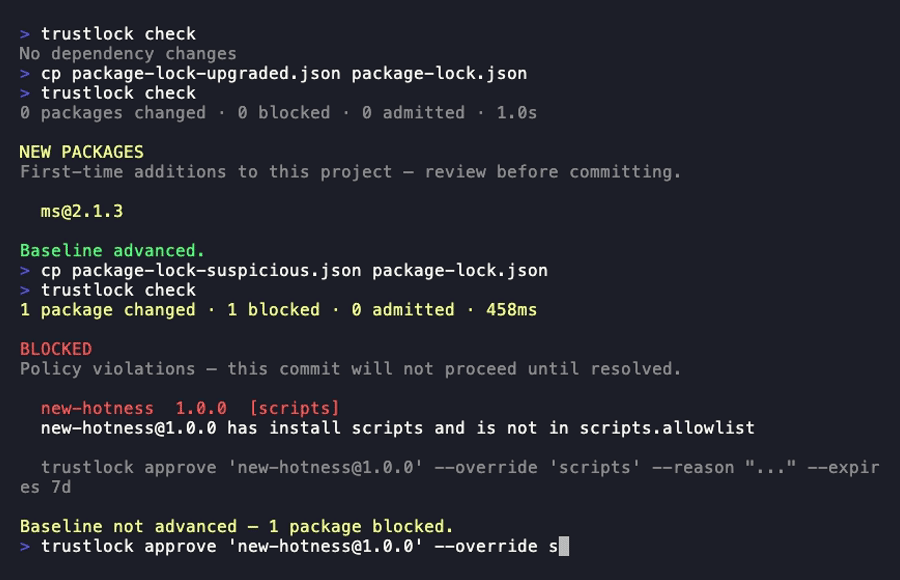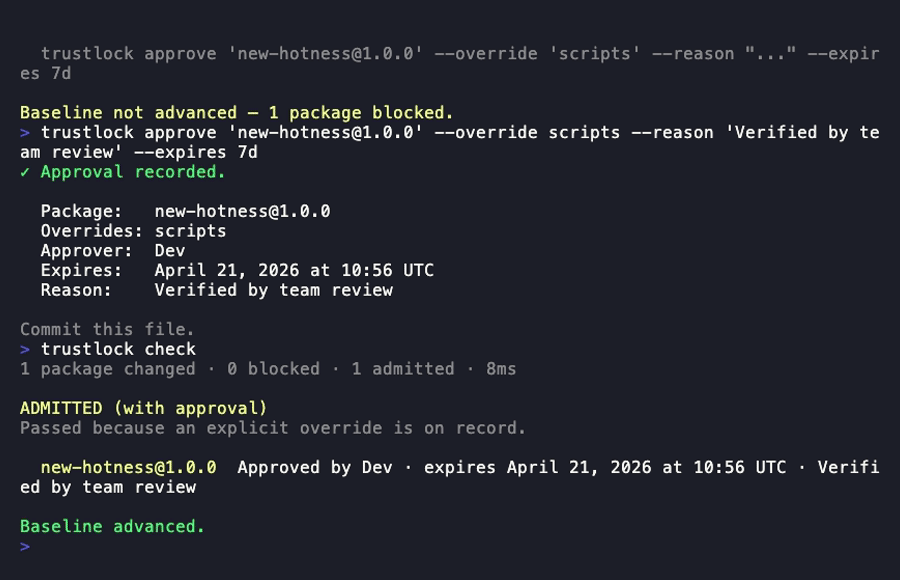 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 joshuaasmith/reproducer-okio-cve-2023-3635
Reproducer for CVE-2023-3635 in Okio 2.9.0, demonstrating how React Native's version catalog pins a vulnerable dependency, affecting Android apps.
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability