
gha-lab-00d54c717d
 pvharmo2/gha-lab-00d54c717d
Security-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f
curated-resourcesdevsecopseducation+2
pvharmo2/gha-lab-00d54c717dSecurity-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f
 pvharmo2/gha-lab-5bce203f66
Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…
 pvharmo2/gha-lab-becf103a54
Authorized security-research reproduction of CVE-2025-15617 (GHSA-6xqr-4q5g-xc7x): artipacked GITHUB_TOKEN leak in wazuh FIM Windows integration…
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 pvharmo2/gha-lab-b1fe4918c0
Authorized security-research lab: reproduction of CVE-2025-32958 (GHSA-8c7v-vccv-cx4q) — GITHUB_TOKEN leaked into workflow artifacts by Adept's…
 pvharmo2/gha-lab-40e23db109
Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…
 pvharmo2/gha-lab-d9fd584b12
Authorized security-research lab reproducing CVE-2024-47179 (GHSL-2024-178): artifact-poisoning pwn-request chain in RSSHub docker-test workflows…
 pvharmo2/gha-lab-456dd8a245
Security-research lab reproducing CVE-2026-41414 (pull_request_target pwn in .github/workflows/pr.yml) — snapshot of skim-rs/skim @ ca986f4, not a…
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 pvharmo2/gha-lab-fb6df3d456
Authorized security-research lab reproducing CVE-2025-46820 (GHSA-cwj7-6v67-2cm4): GITHUB_TOKEN persisted into publicly downloadable CI artifacts in…
 pvharmo2/gha-lab-f894926966
Authorized security-research reproduction lab for CVE-2025-54415 (GHSA-g5hx-xv45-9whg): astronomer/dag-factory snapshot at 464c75a —…
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
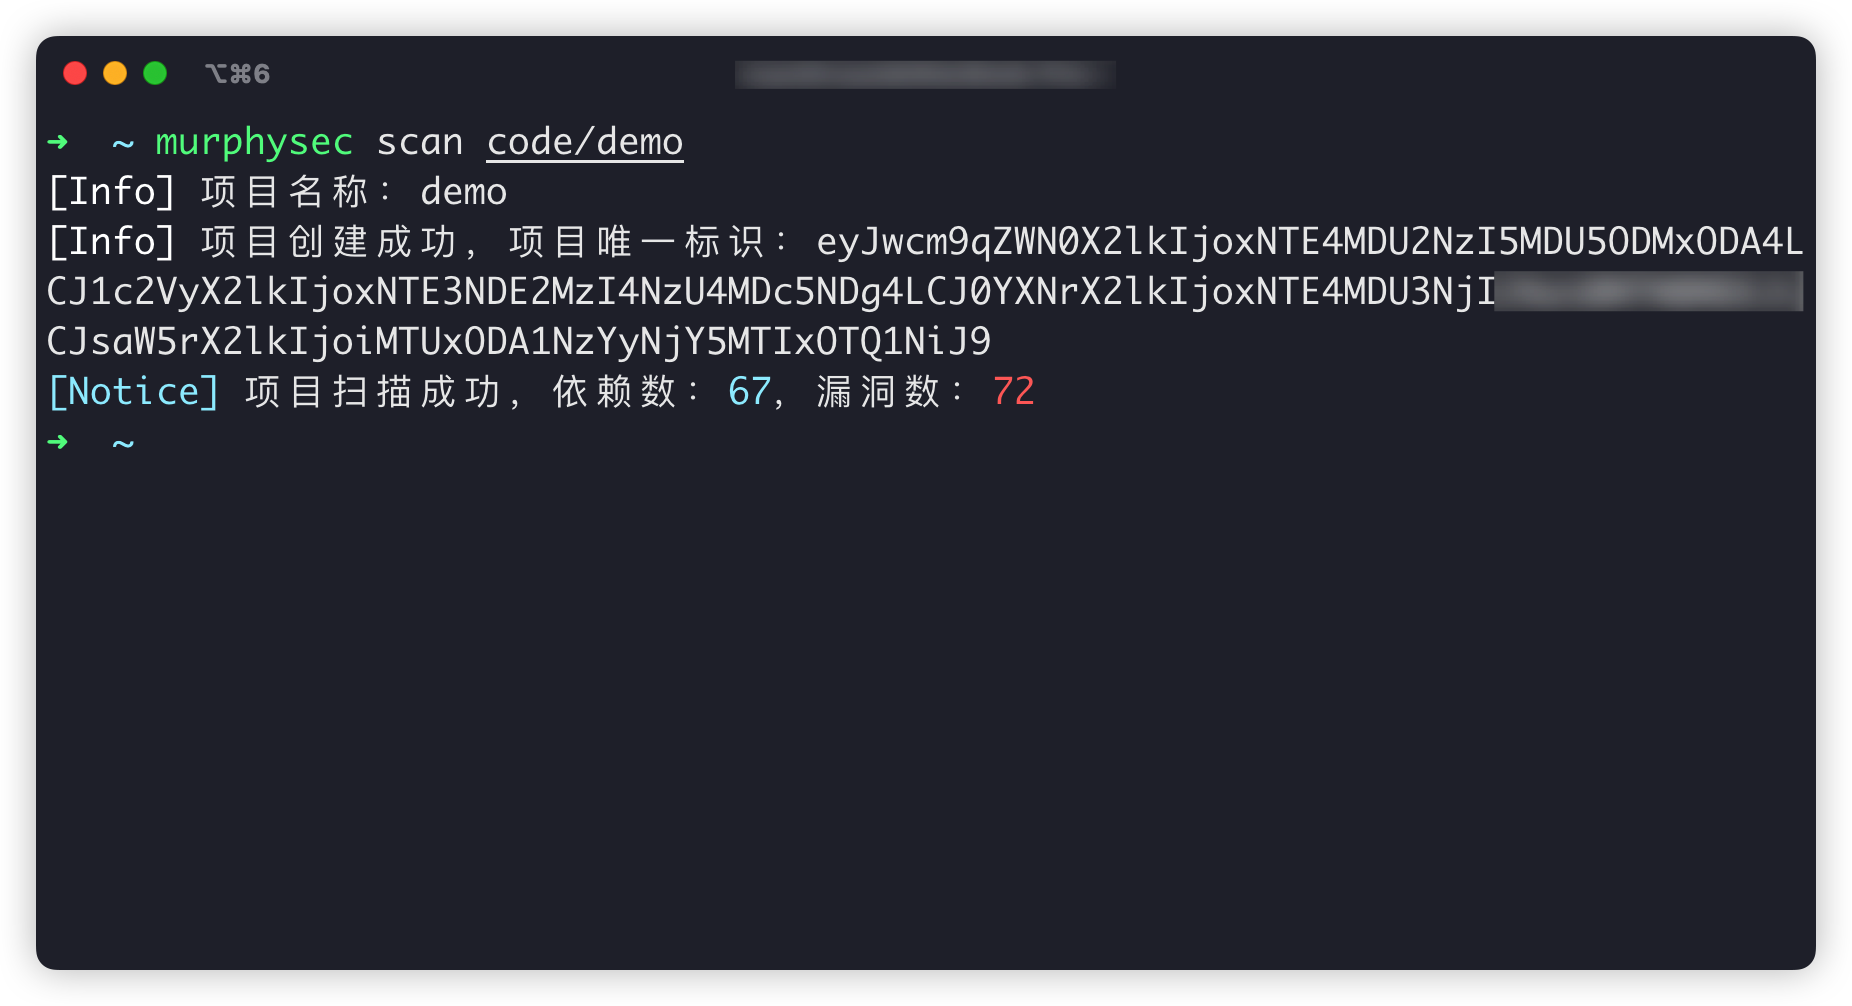 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
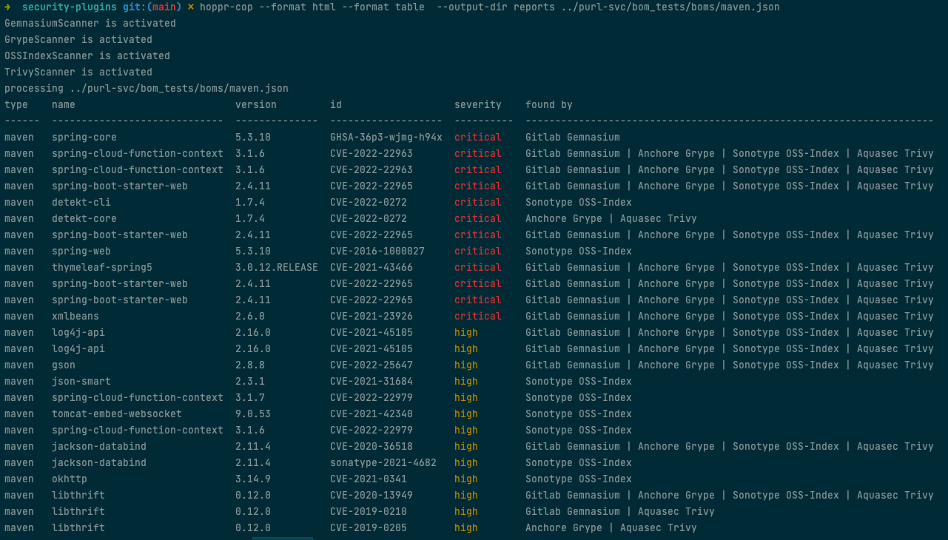
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…