
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
452 results
miasma-toolkit preview

miasma-toolkit

GitHubjchable/miasma-toolkit

Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)

devsecopseducationforensics+7
2 months ago
lab_xz_backdoor preview

lab_xz_backdoor

GitHubstevehenderson/lab_xz_backdoor

Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
educationexploitationforensics+6
3 months ago
CVE-2026-0848 preview

CVE-2026-0848

GitHubhyperps/cve-2026-0848

nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
code-analysiseducationexploitation+3
5 months ago
http-server-node preview

http-server-node

GitHubdannyendortest/http-server-node

Synthetic vulnerable Node.js HTTP server used as a demo target for the EXPOSURE vulnerability scanner, tracking CVE-2021-23797 with a one-click…
educationlabs-practicesupply-chain-security+2
3 months ago
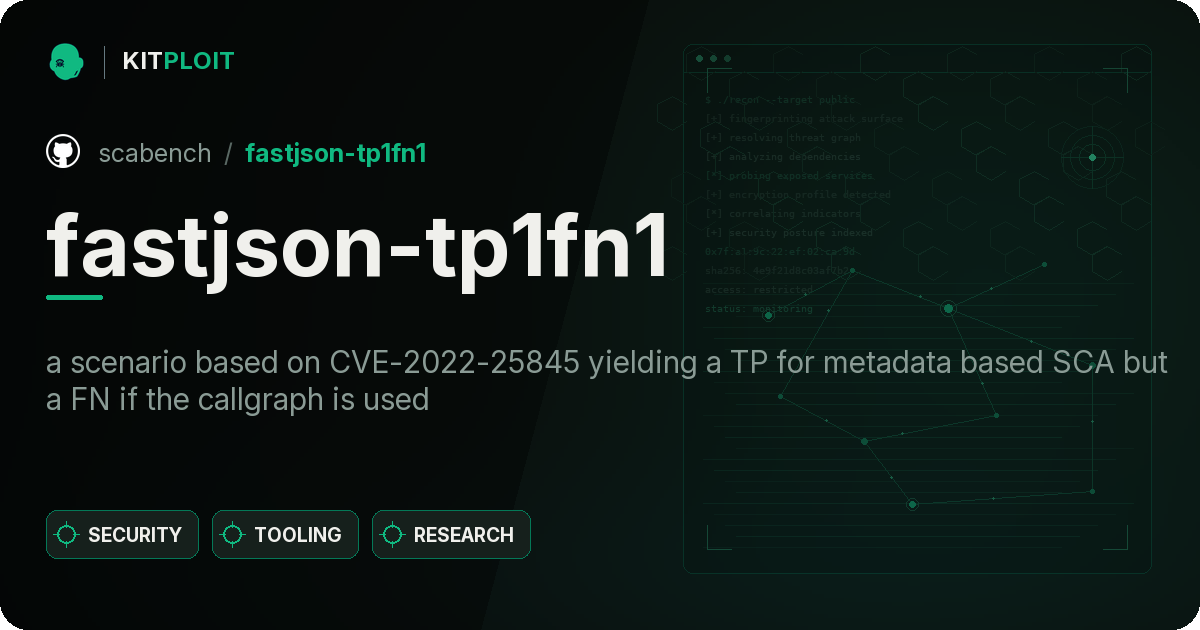
CVE-2021-42574 preview

CVE-2021-42574

GitHubwaseeld/cve-2021-42574

Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…
code-analysiseducationpapers-research+3
14 years ago
fastjson-tp1fn1 preview

fastjson-tp1fn1

GitHubscabench/fastjson-tp1fn1

a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
code-analysiseducationpapers-research+3
2 years ago
dockerscan preview

dockerscan

GitHubcr0hn/dockerscan

The Most Comprehensive Docker Security Scanner

cloud-securityconfiguration-auditingcontainer-security+4
1.7k1 day ago
lunasec preview

lunasec

GitHublunasec-io/lunasec

LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
devsecopssecret-detectionsupply-chain-security+1
1.5k2 years ago
node9-proxy preview

node9-proxy

GitHubnode9-ai/node9-proxy

The Execution Security Layer for the Agentic Era. Providing deterministic "Sudo" governance and audit logs for autonomous AI agents.
ai-securitycloud-securitycommand-and-control+7
2131 day ago
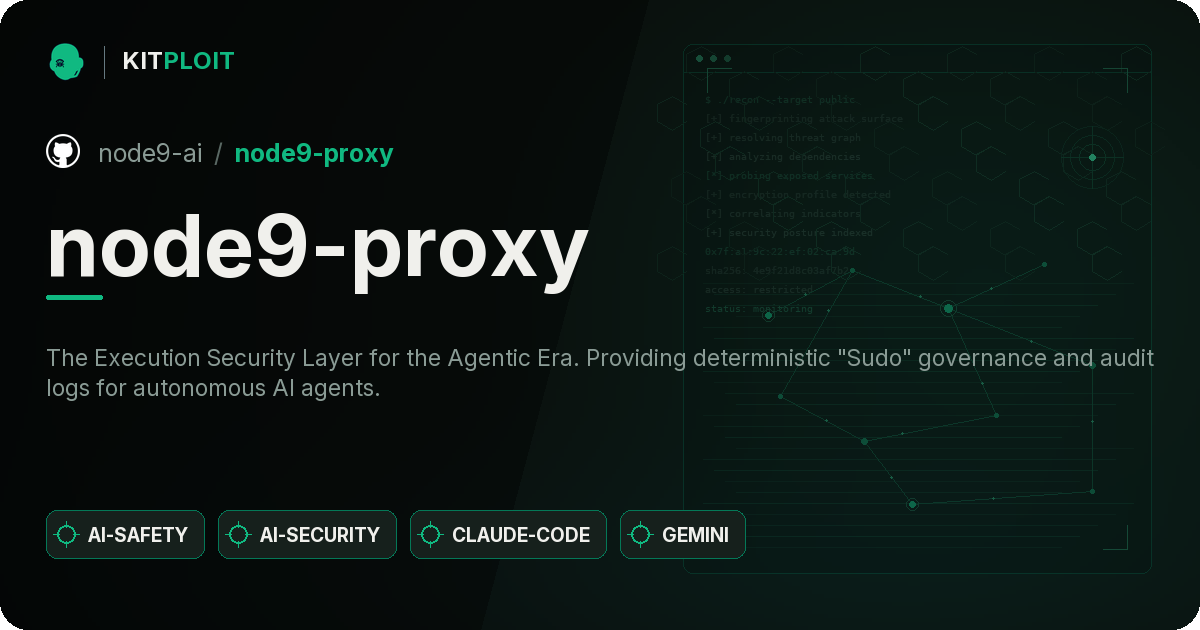
Owasp-top-10-k8s-2025 preview

Owasp-top-10-k8s-2025

GitHubhac01/owasp-top-10-k8s-2025

Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…

cloud-securitycontainer-securityctf+8
492 months ago
Magento-APSB22-48-Security-Patches preview

Magento-APSB22-48-Security-Patches

GitHubemicoecommerce/magento-apsb22-48-security-patches

This repository contains potential security patches for the Magento APSB22-48 and CVE-2022-35698 security vulnerability

code-analysismisconfigurationstatic-analysis+3
373 years ago
FIASSE preview

FIASSE

GitHubowasp/fiasse

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)

code-analysiscurated-resourcesdevsecops+7
1429 days ago
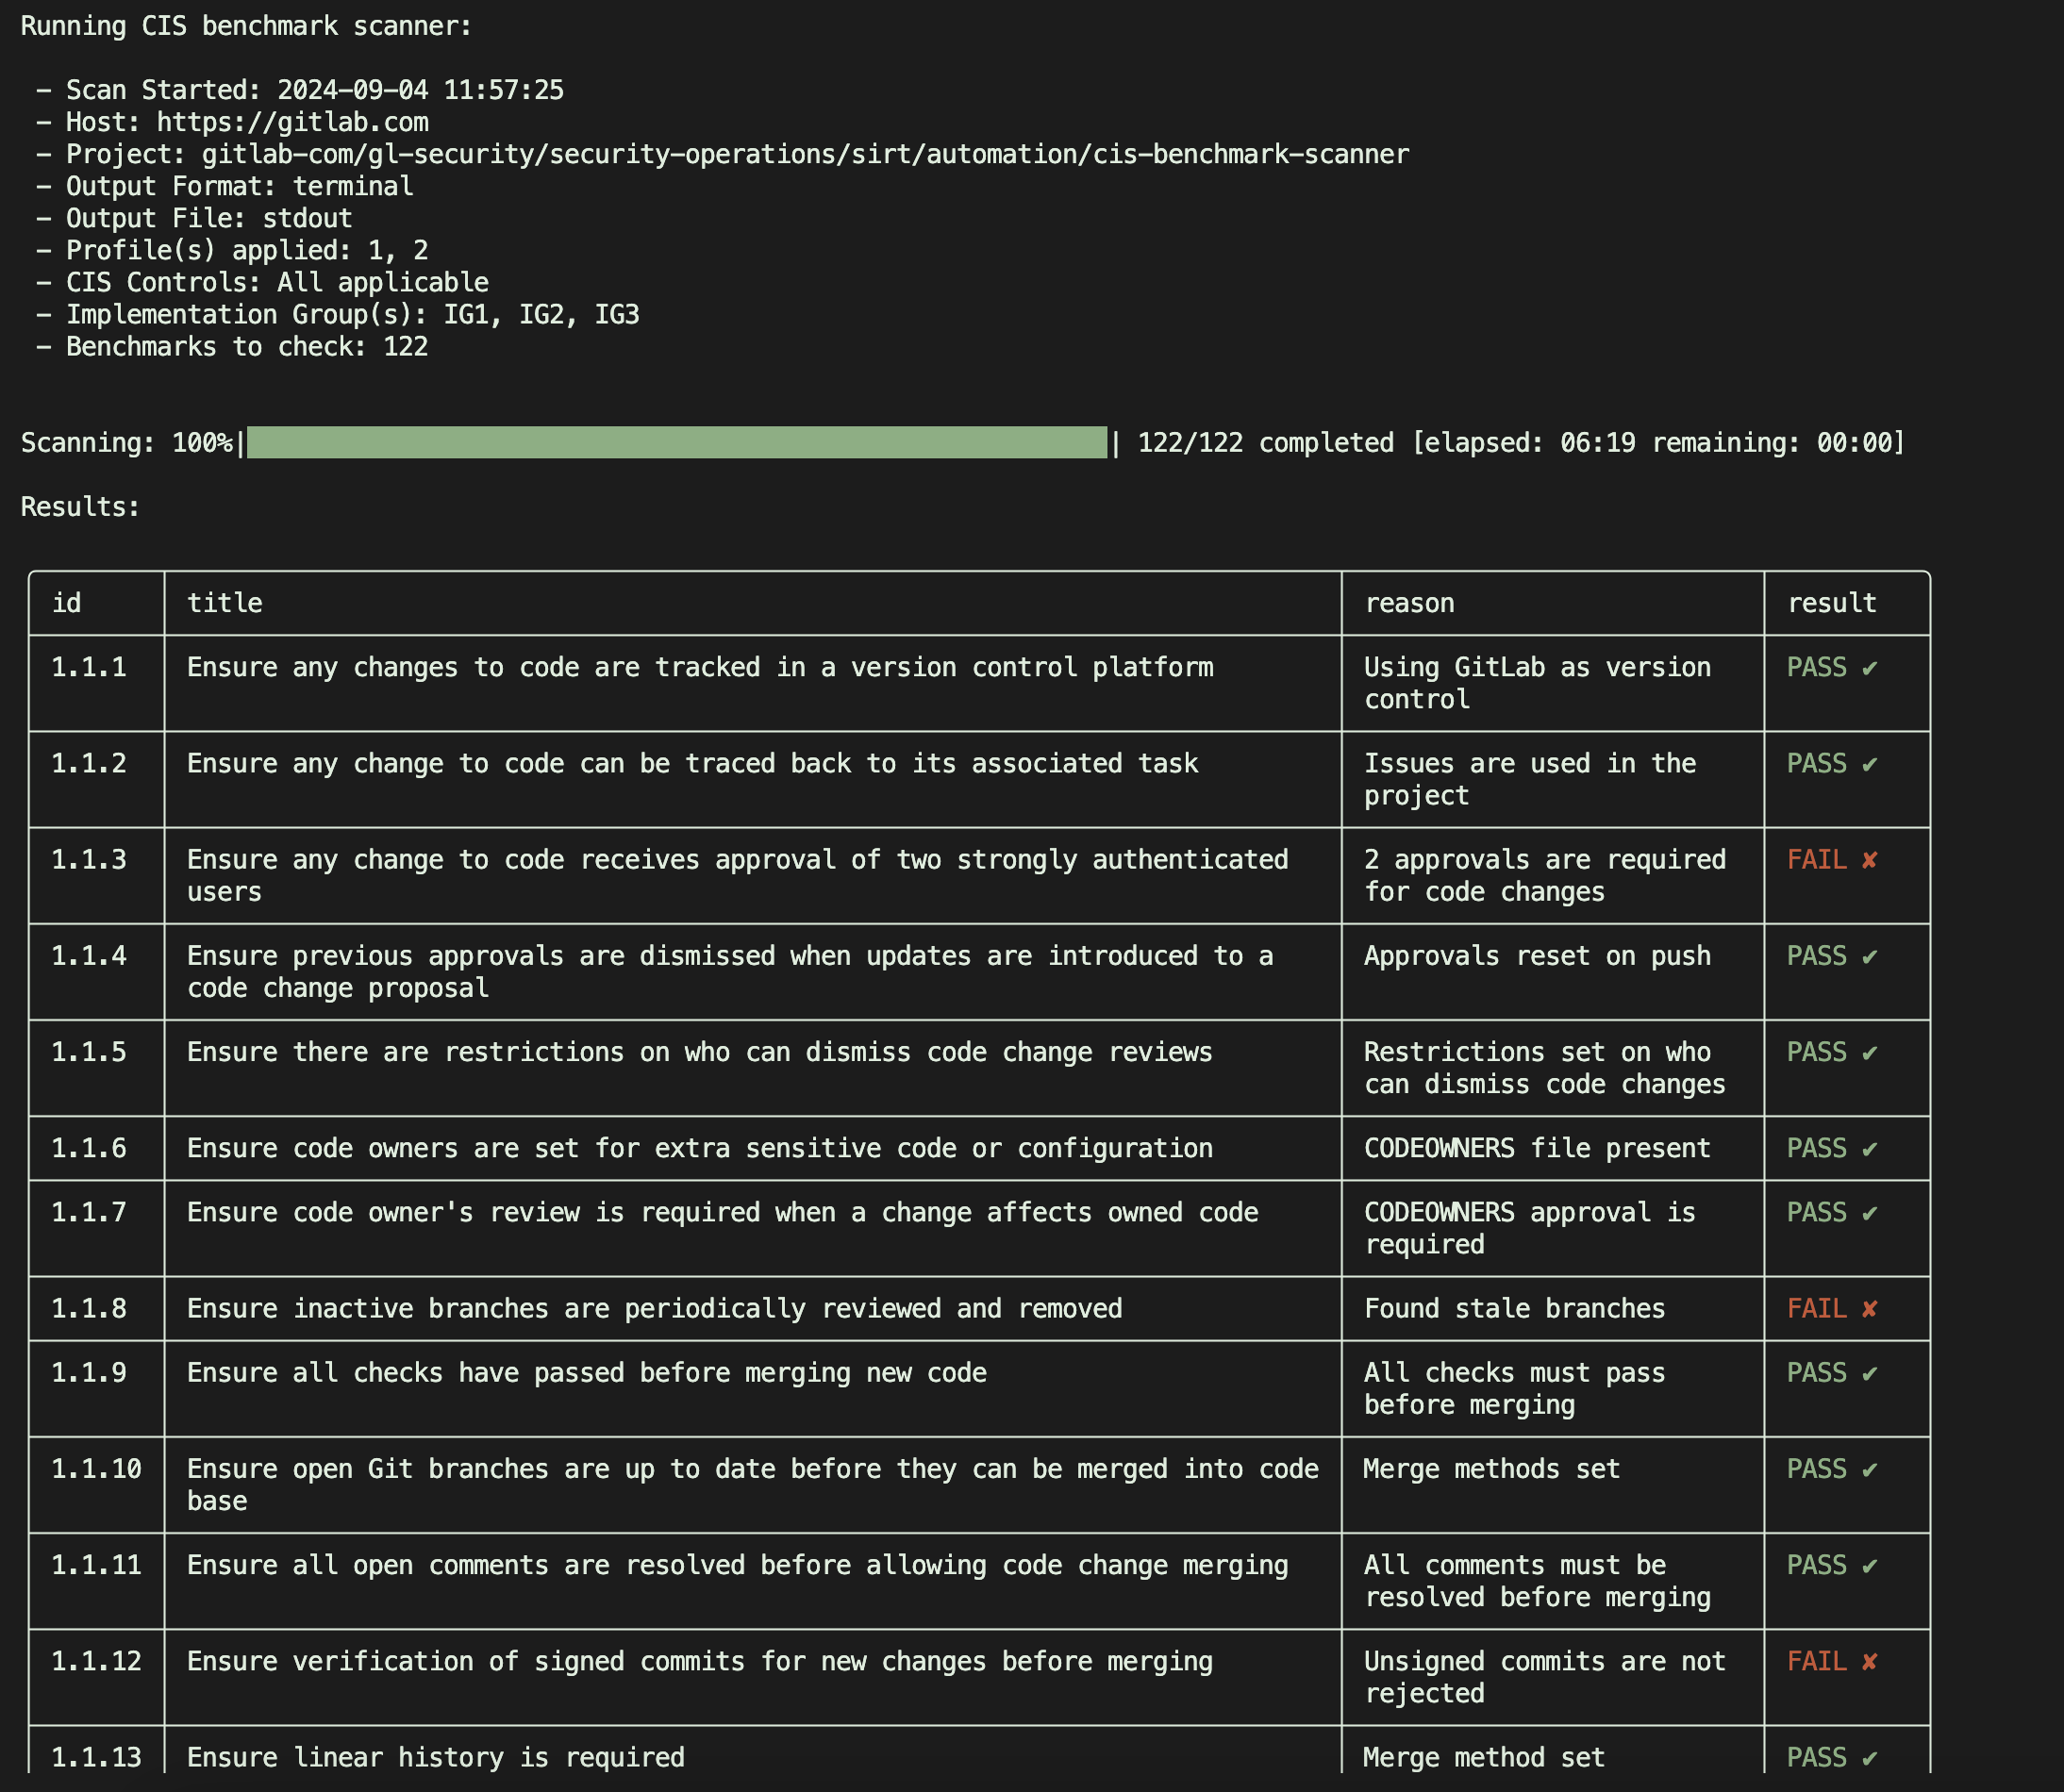
CIS GitLab Benchmark Scanner preview

CIS GitLab Benchmark Scanner

GitLabgitlab-security-oss/cis/gitlabcis

Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
configuration-auditingdevsecopsmisconfiguration+2
1513 days ago
GitHunt preview

GitHunt

GitHubwiz-sec-public/githunt

Demos for Black Hat Europe 2025's The Forensic Trail On GitHub: Hunting For Supply Chain Activity
curated-resourceseducationforensics+4
289 months ago
vibe-coding-security preview

vibe-coding-security

GitHubboxed-dev/vibe-coding-security

Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
ai-securityapi-securityauthentication+9
151 month ago
revera preview

revera

GitHubaaravmaloo/revera

The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
devsecopssupply-chain-securityvulnerability-analysis+1
111 month ago
OWASP-Top-10-AI-Infrastructure-Security-Risks preview

OWASP-Top-10-AI-Infrastructure-Security-Risks

GitHubowasp/owasp-top-10-ai-infrastructure-security-risks

A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…
ai-securitycloud-infrastructure-securitycurated-resources+5
20 days ago
gha-lab-3f1ff30e9c preview

gha-lab-3f1ff30e9c

GitHubpvharmo2/gha-lab-3f1ff30e9c

Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…

cloud-securitycurated-resourcesdevsecops+2
10 days ago
Previous1…181920…26Next