

 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…
 hexbornestudio/atlas-tj-actions-poc
PoC for CVE-2025-54416 tj-actions/branch-names command injection
 ivaavimusic/react19-fix-vibecoders
CVE-2025-55182 Fix for Vibe Coders
 open-flaw/cve-2026-2395
Proof-of-concept demonstrating a race condition in the tar npm package (v7.5.3) causing file collisions during parallel extraction, leading to data…
 dannyendortest/invokeai-consumer
Demo consumer for invokeai 5.0.1 (CVE-2024-10821; version named in CVE prose) — endorctl scan target
 amir-malek/react-cve-2025-55182
Detects and fixes CVE-2025-55182 (React2Shell) in React Server Components and Next.js apps. Scans package versions, suggests safe upgrades, and…
 ikram124/cve-2024-3094-analysis
Security analysis project: Real-world CVE breakdown
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
 simplifi-ed/cve-2024-3094-patcher
Ansible playbook for patching CVE-2024-3094
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 completetech-security/sharp-vectorfreed-check
Offline Sharp / librsvg evidence checker for CVE-2026-96889. Sharp and librsvg version and build evidence. Standalone Python; JSON/CSV/HTML reports;…
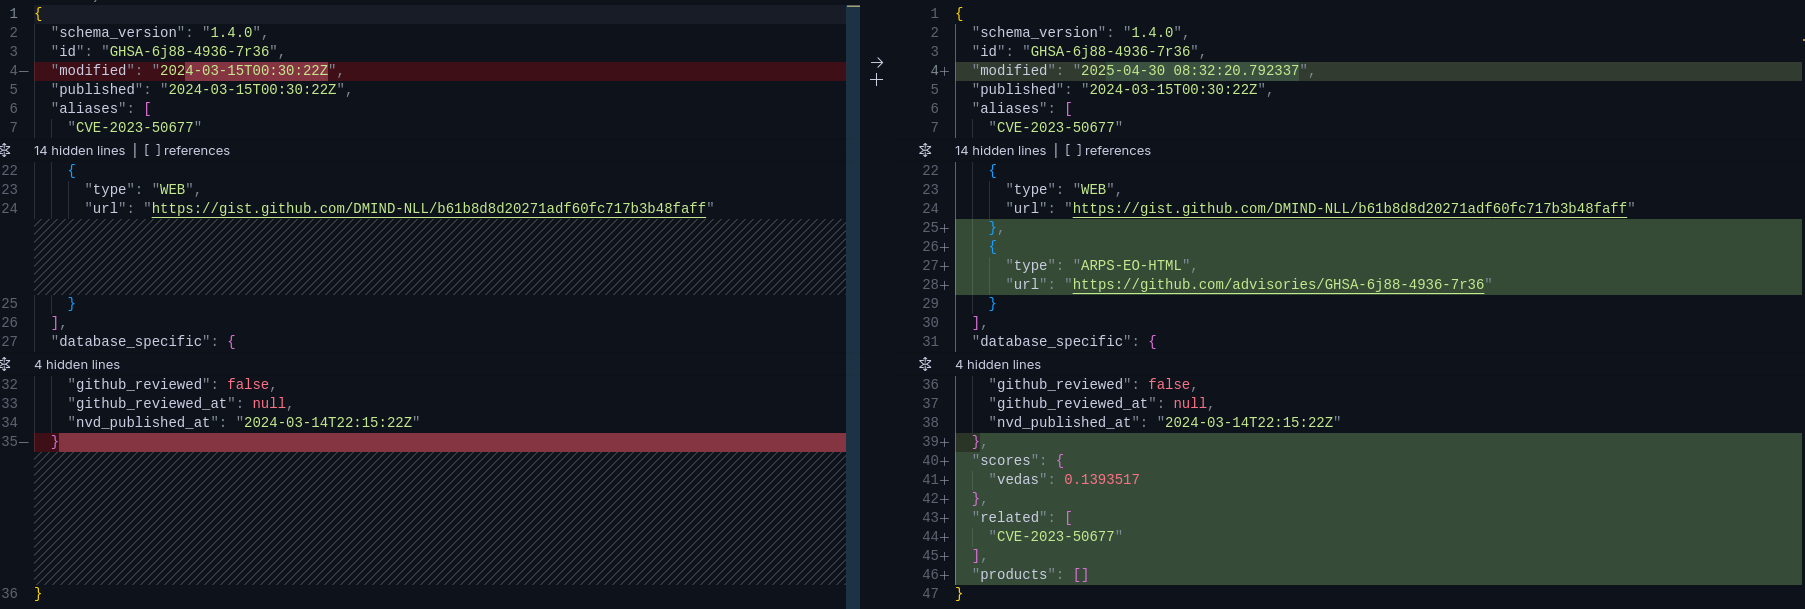 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 ossillate-inc/packj
Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
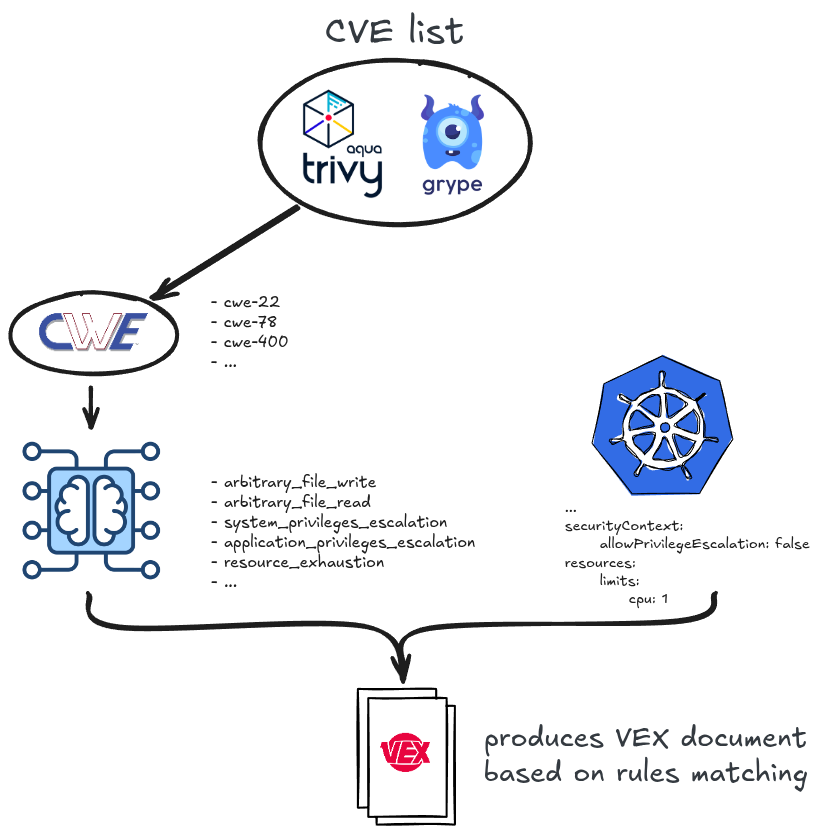 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans