

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k18h 45m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
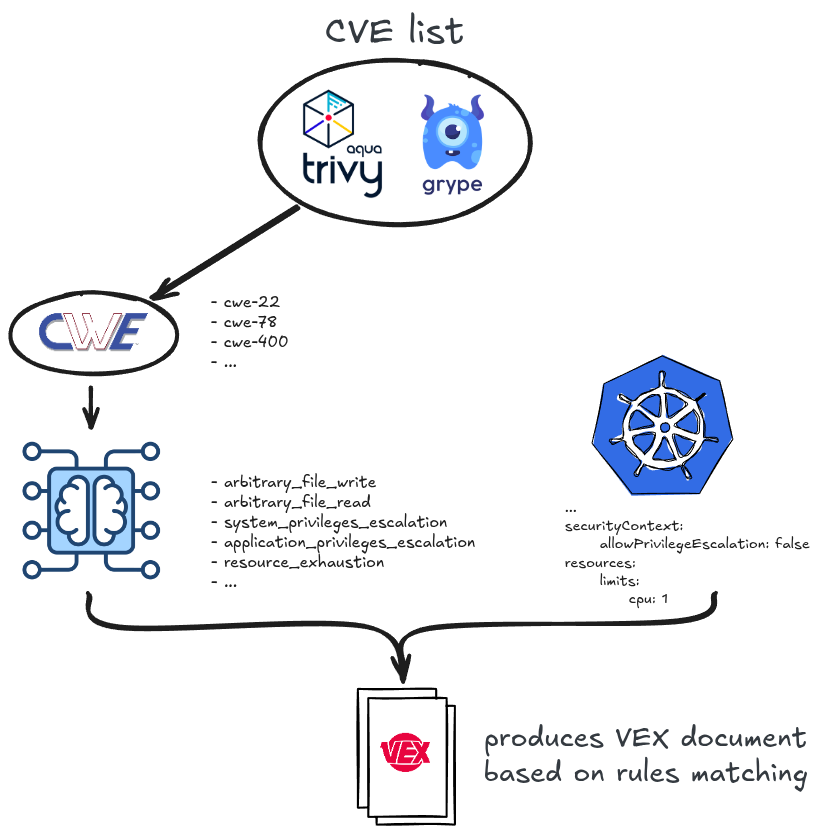 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 xiaoqimikko/bc-check
Offline scanner telling you which of the 2026 Bouncy Castle CVEs actually apply to you - across BC, BC-LTS and BC-FJA (FIPS), which do not share a…
 paultendo/confusable-vision
The world's first font-by-font confusables dataset: which Unicode characters look alike, measured from the outlines of 322 fonts at the size people…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
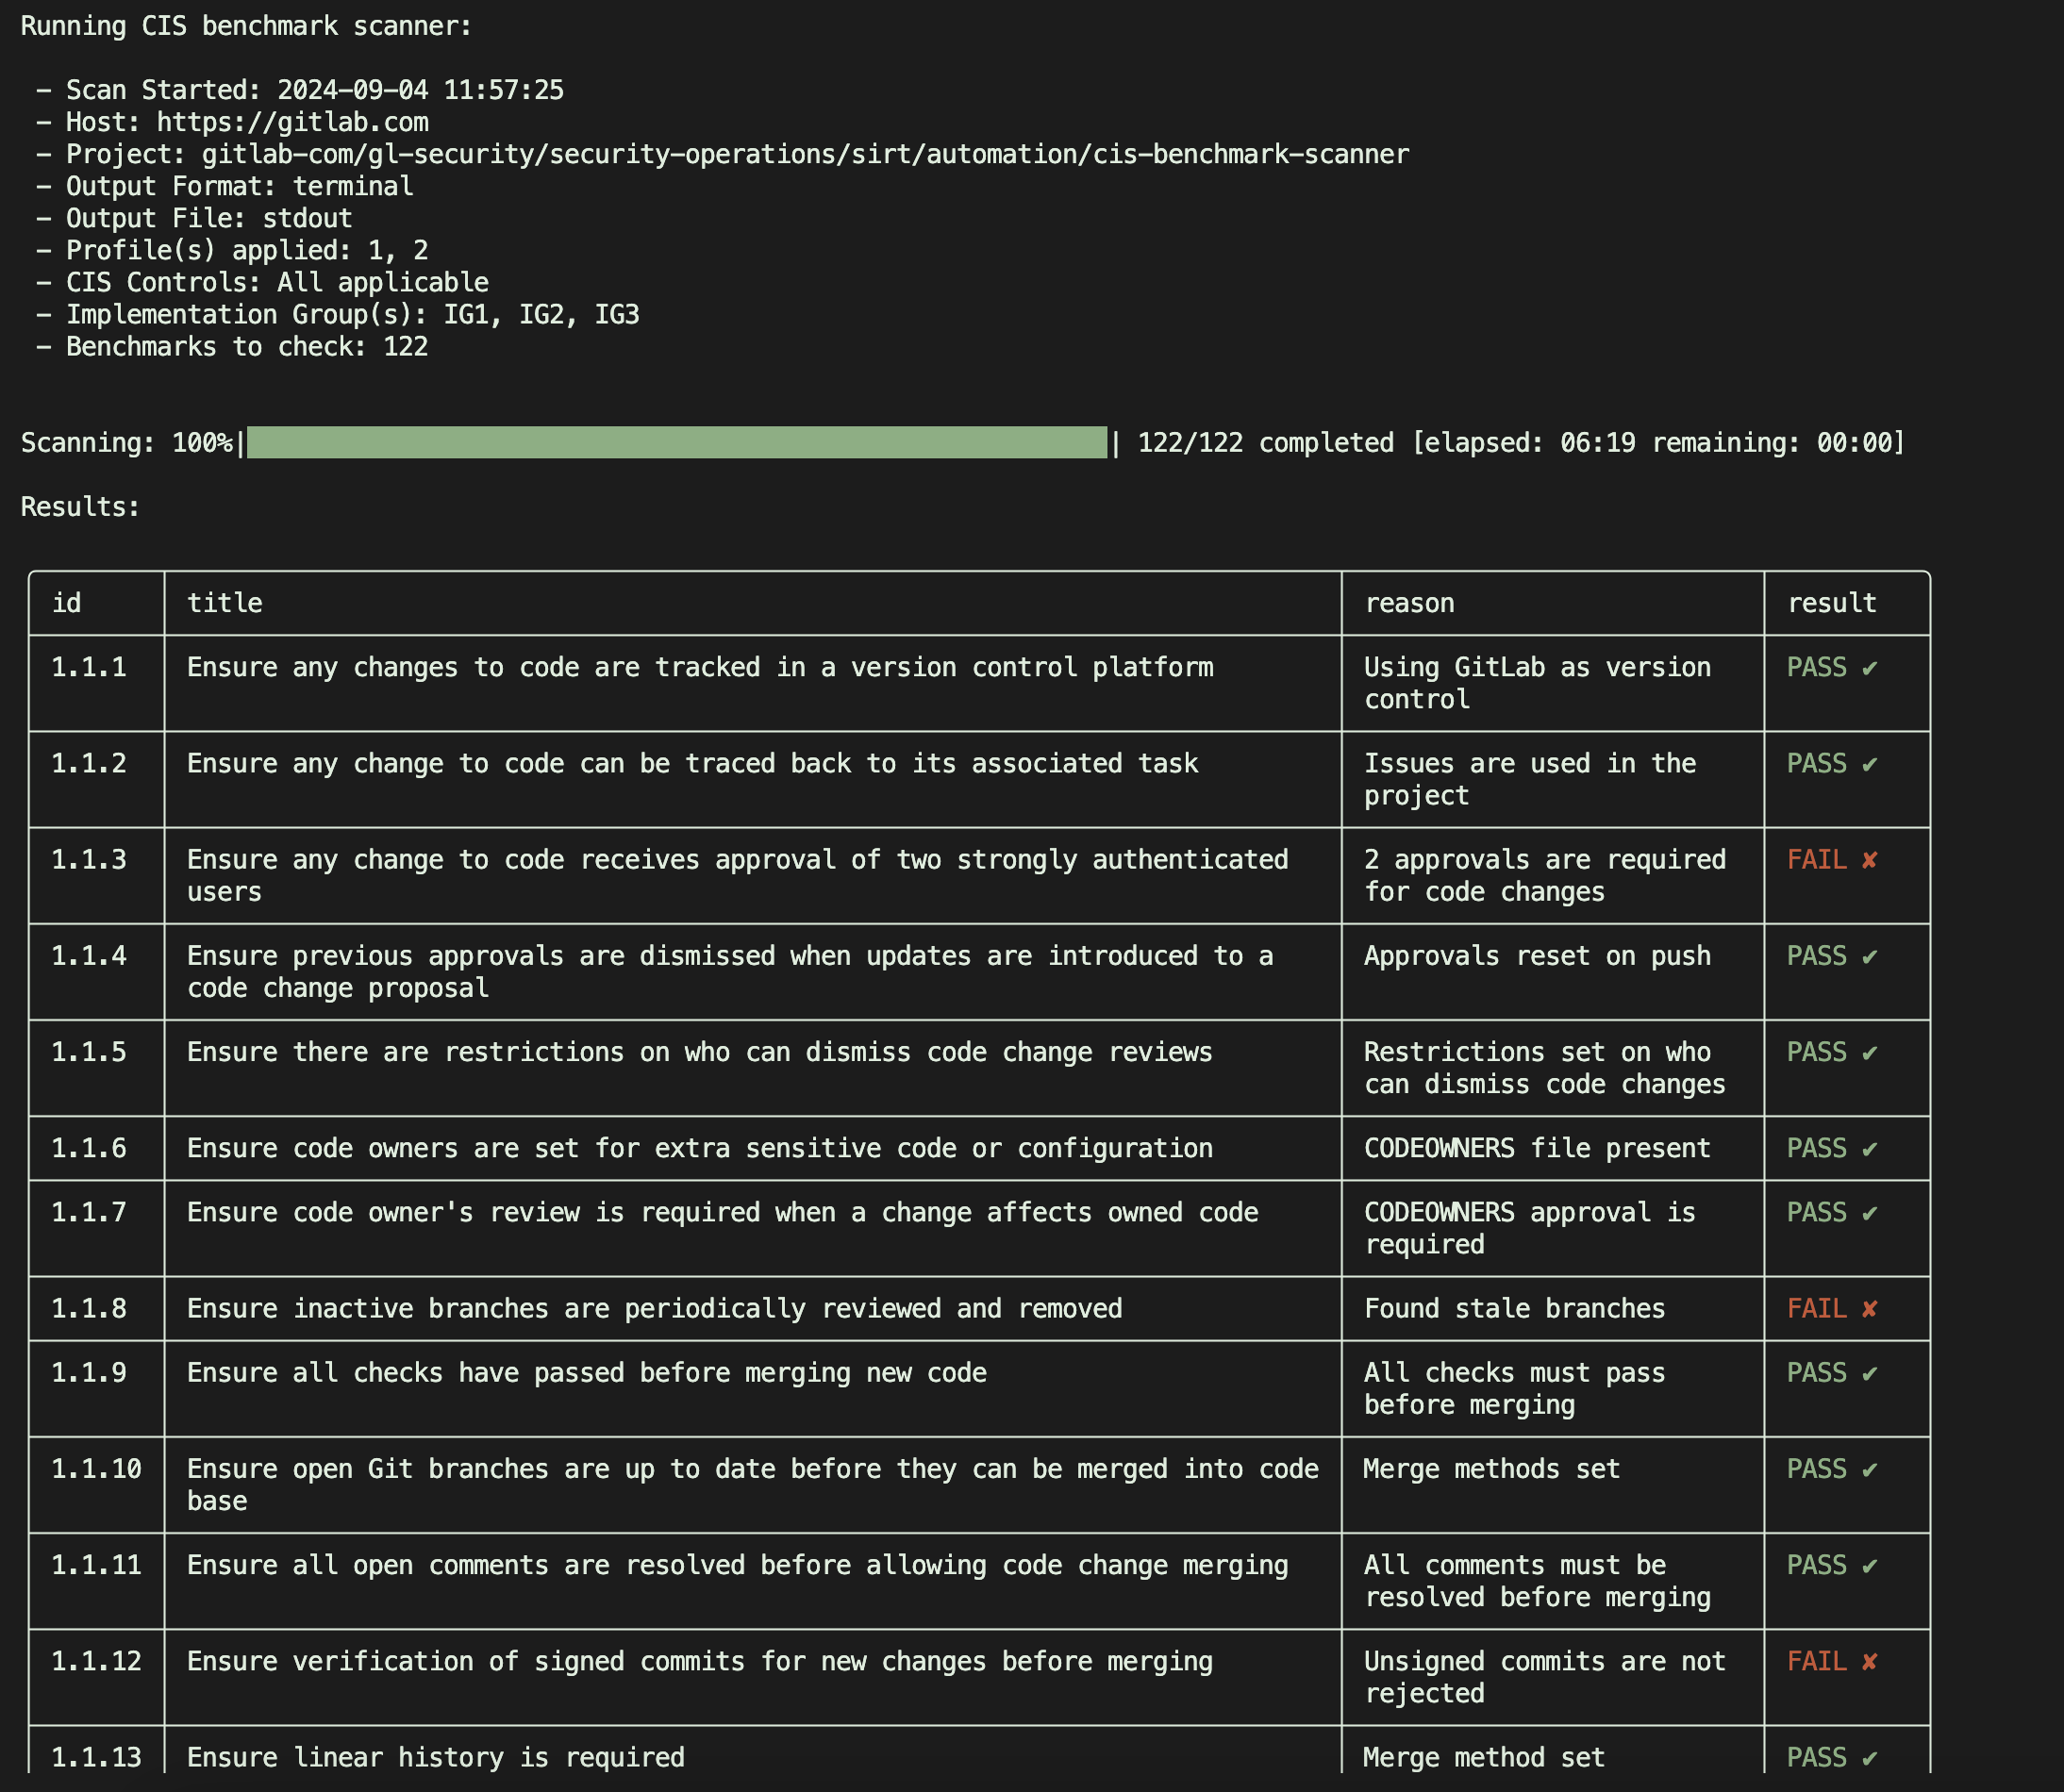
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 george0papasotiriou/cve-2026-23001-hugging-face-transformers-model-deserialization-arbitrary-code-via-pickle-
Proof-of-concept for CVE-2026-23001: demonstrates RCE through unsafe pickle deserialization in Hugging Face Transformers by crafting a malicious…
 george0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-
Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 isecuritytw/seal-security-nuget-demo-net7
.NET 7 fork of seal-security-nuget-demo: same CVE-2024-21907 exploit story, retargeted for customers locked to .NET SDK 7.