
advisory-database
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
curated-resourcesdefensive-toolsdevsecops+5
2.5k
github/advisory-databaseSecurity vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.

 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 google/osv.dev
Open source vulnerability DB and triage service.
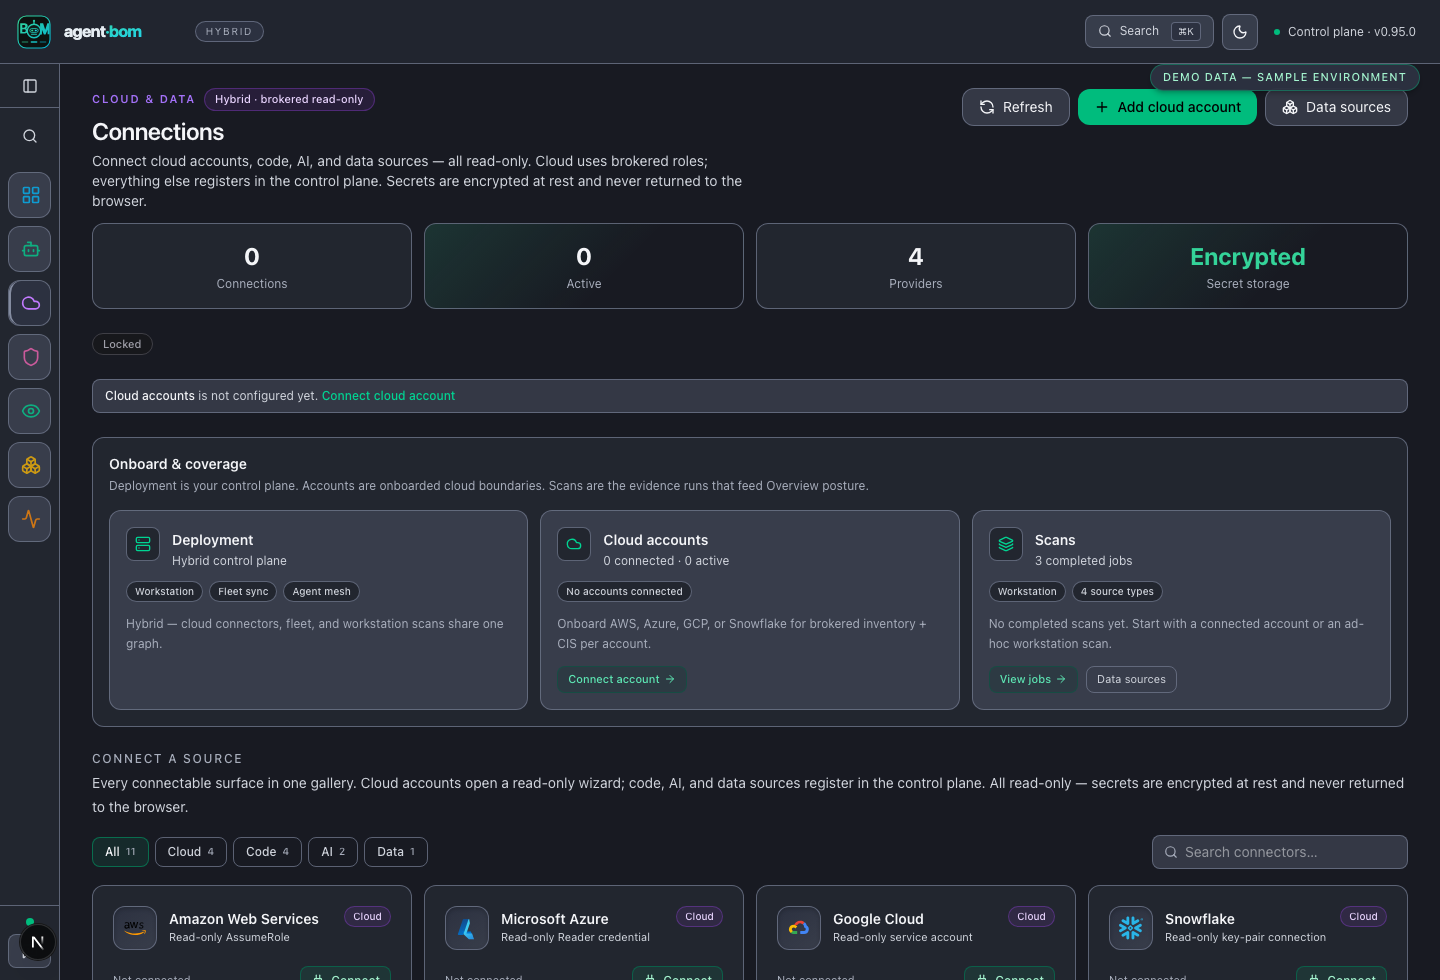 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 canonical/ubuntu-security-notices
Ubuntu vulnerability dataset publishing USN/LSN security notices in OSV and OpenVEX JSON formats for automated vulnerability and VEX-aware dependency…
 8b-is/smart-tree
Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
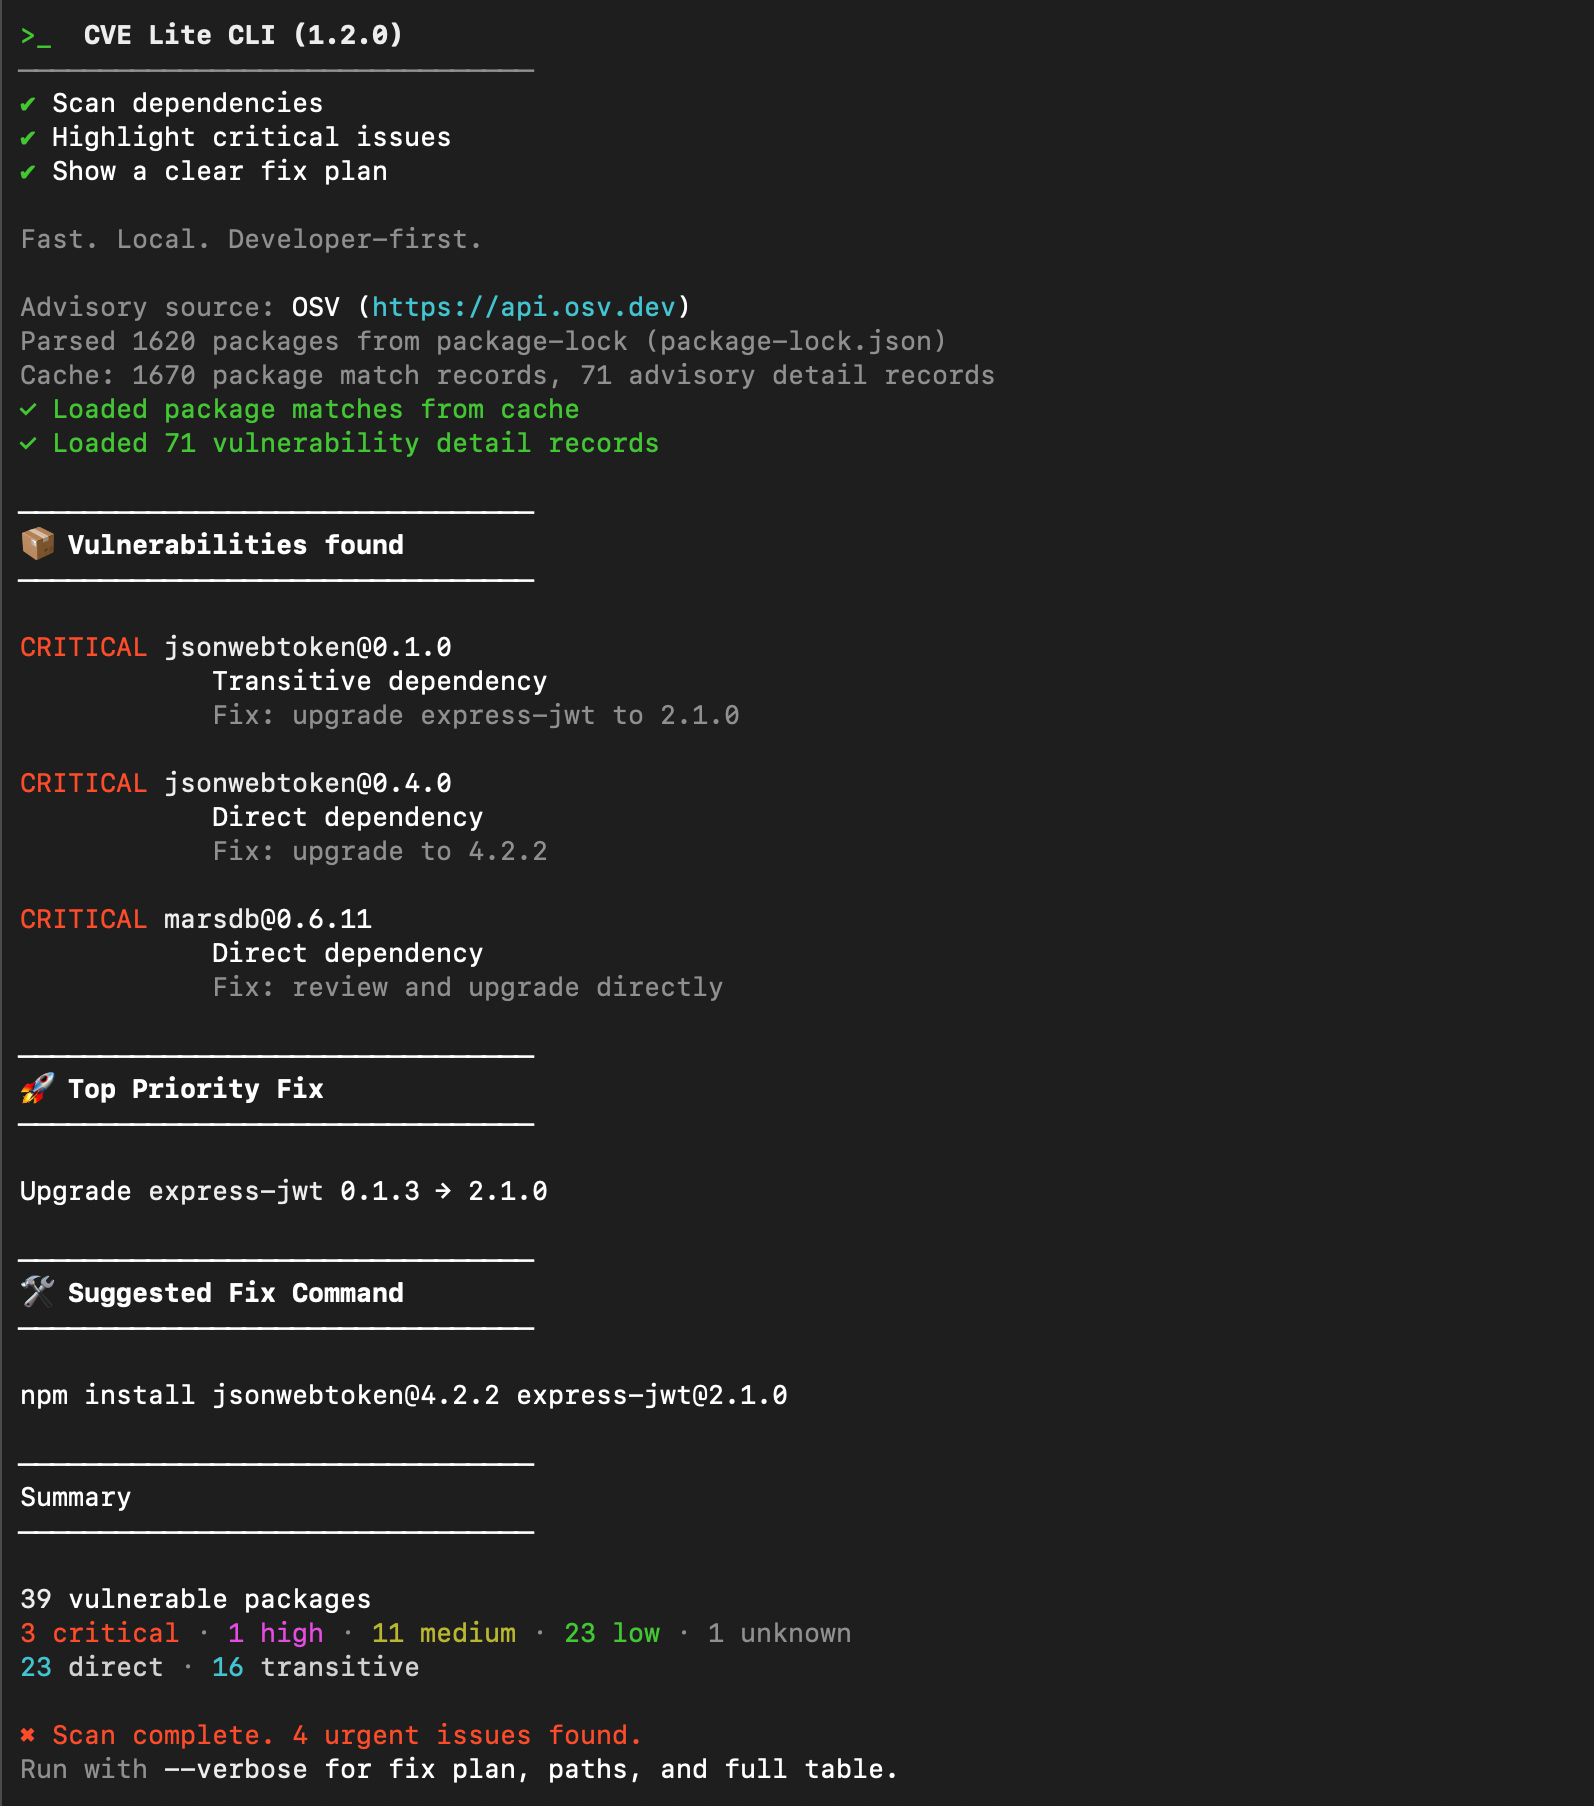 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)