

bromure
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
ai-securitycontainer-securitydynamic-analysis-sandboxing+6
rderaison/bromureProper sandboxing for agentic coding and web browsing
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 anchore/grype
A vulnerability scanner for container images and filesystems
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 safedep/vet
Protect against malicious open source packages 🤖
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
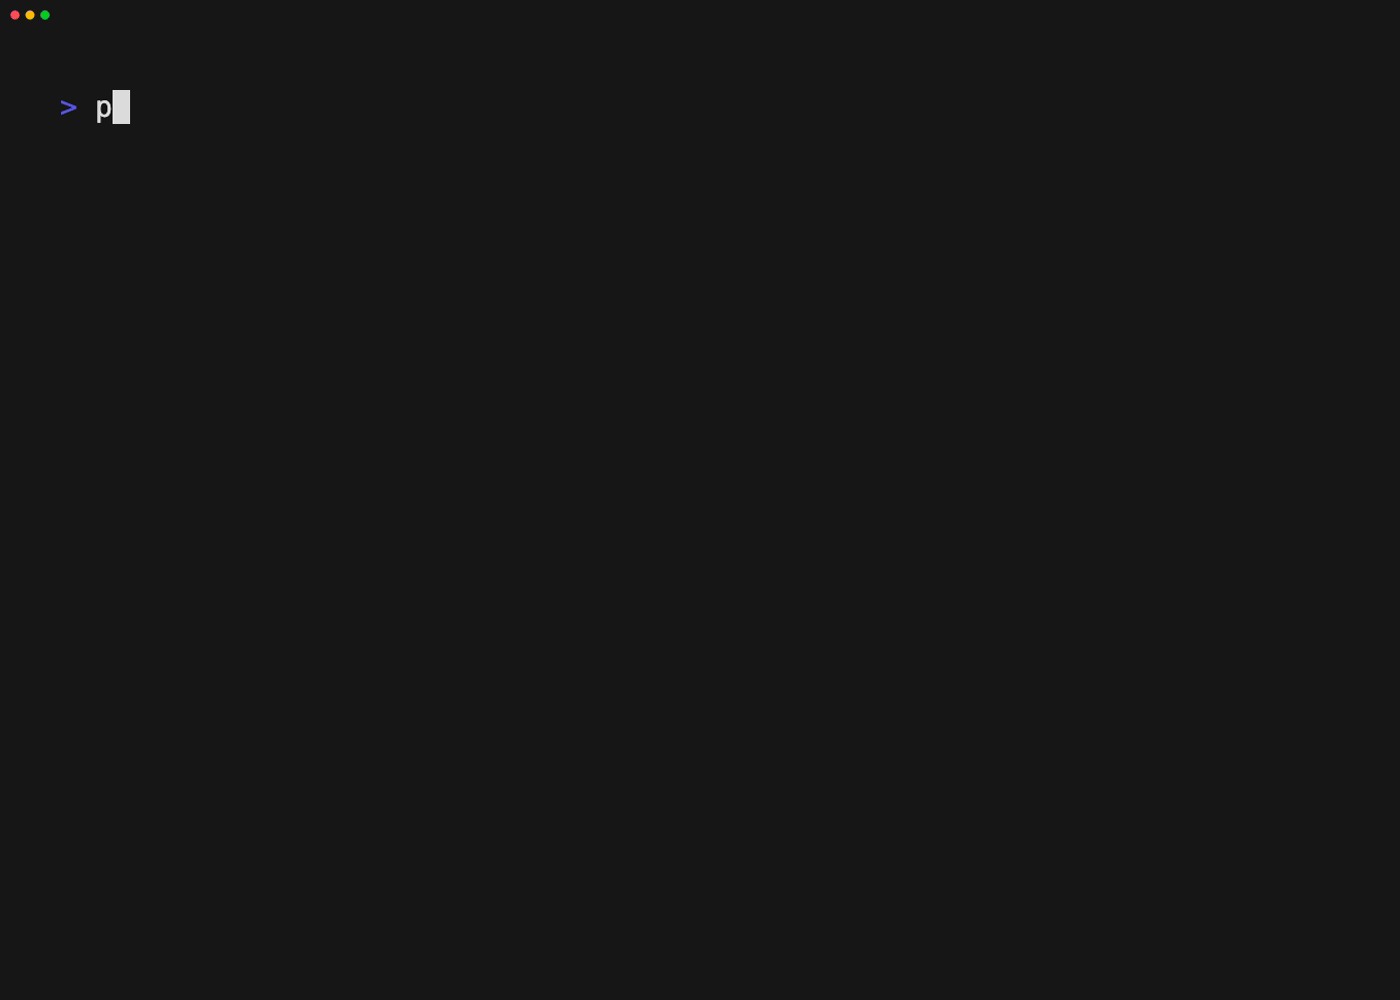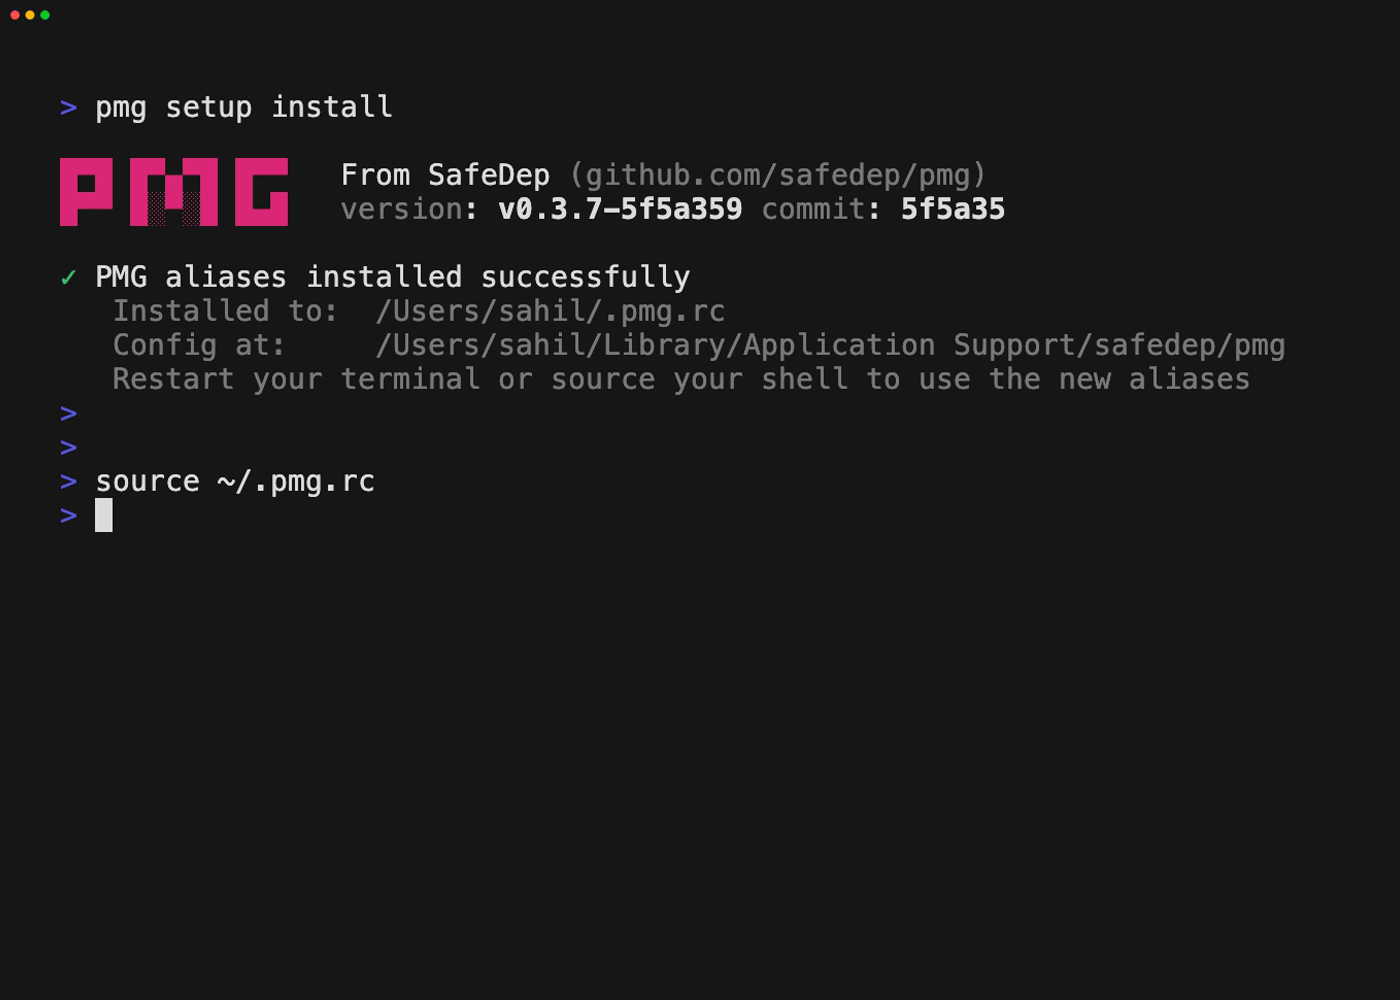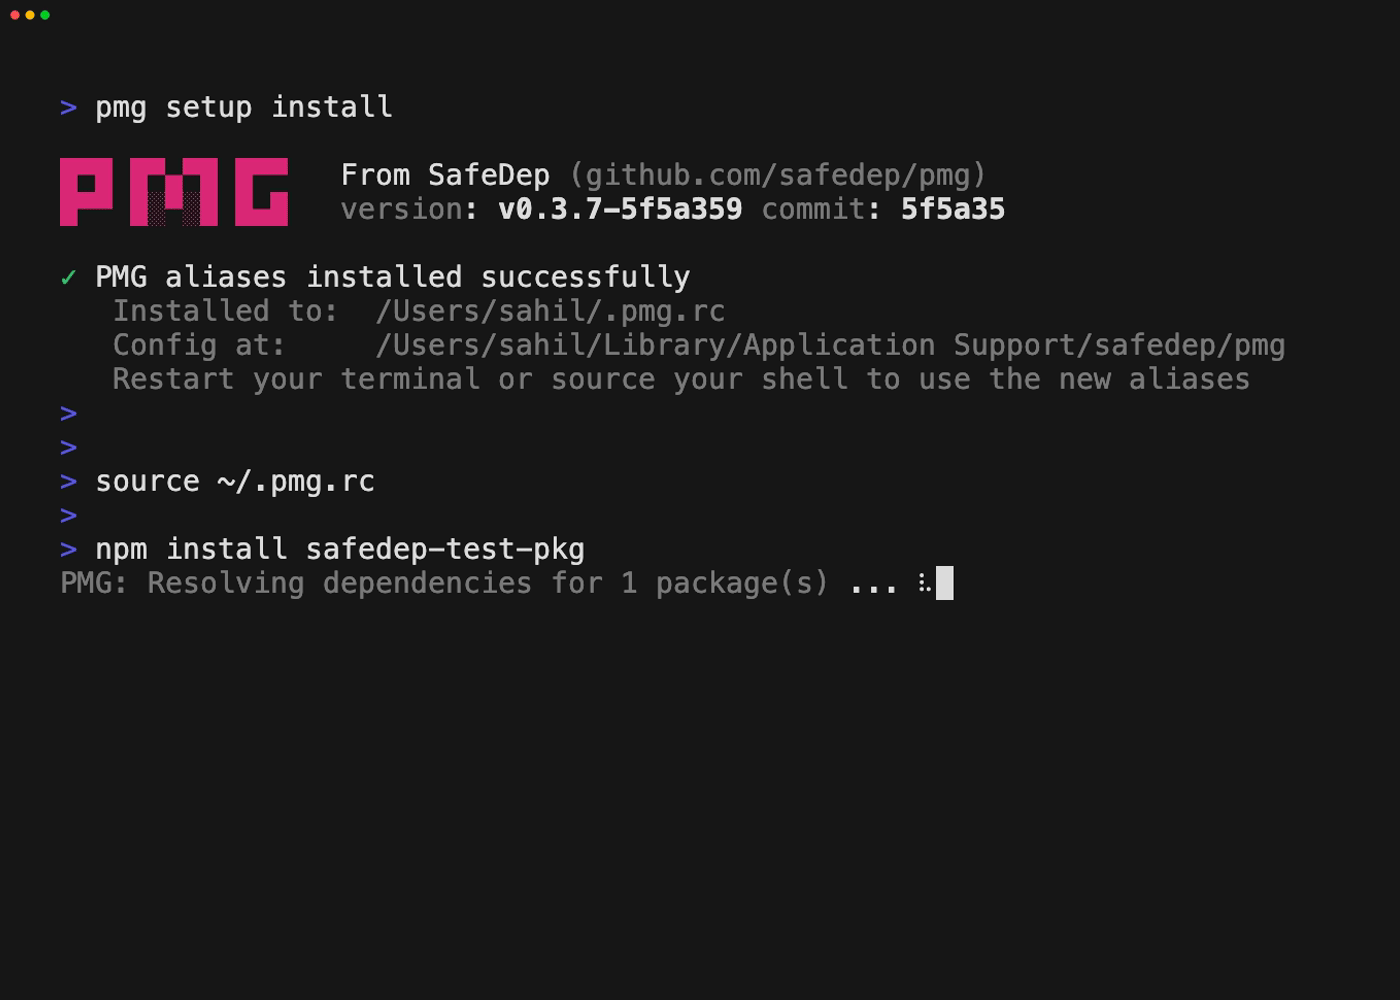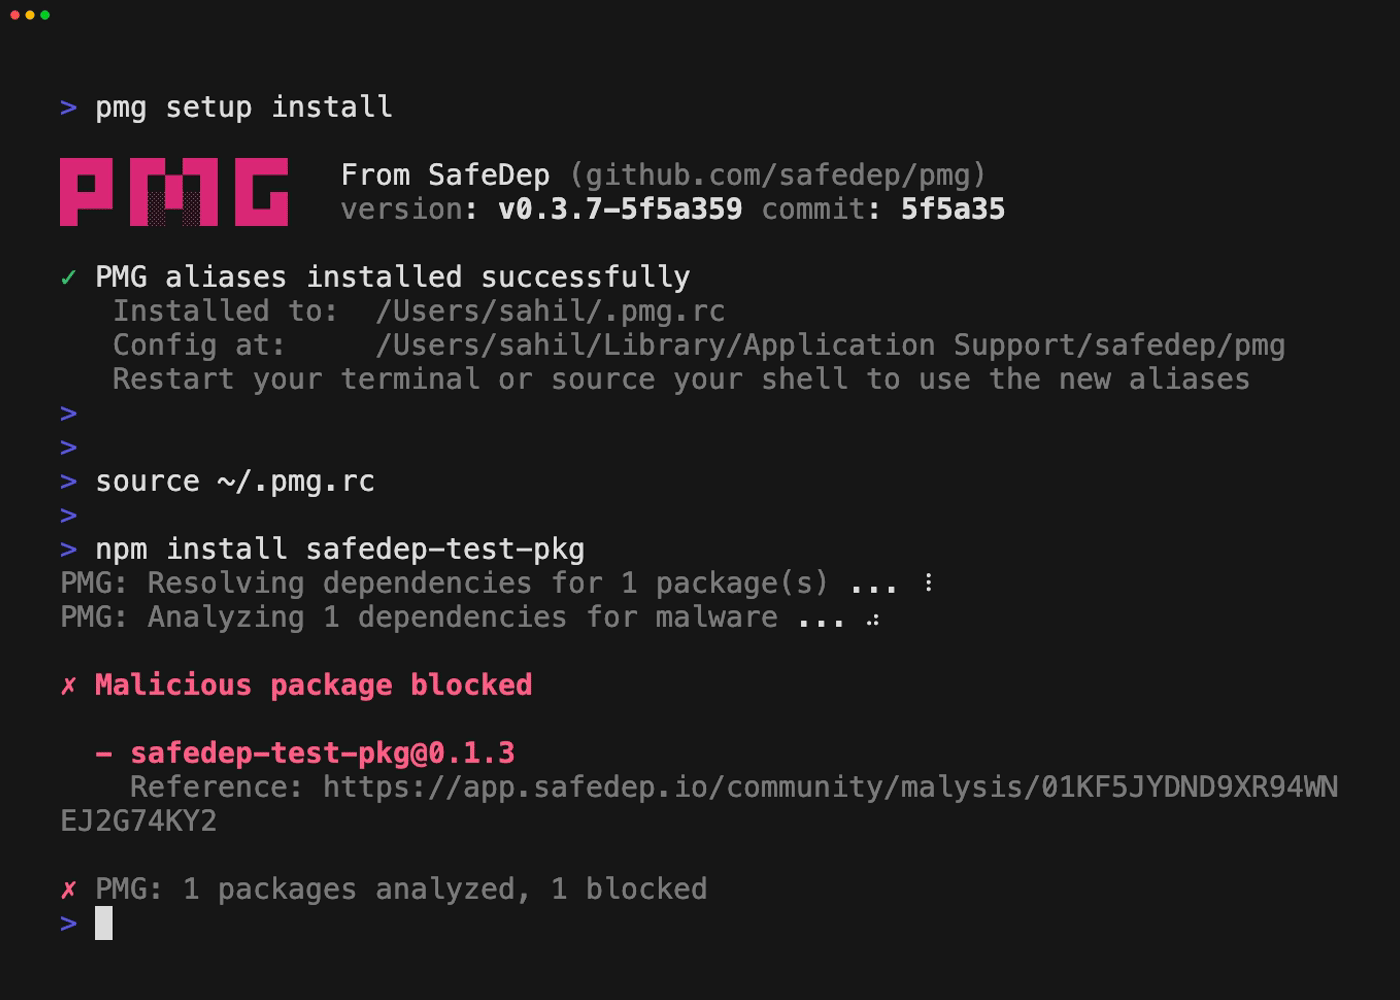 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 joaovicdev/exploit-cve-2026-33634
Deliberately vulnerable Docker lab reproducing CVE-2026-33634: LiteLLM gateway SSRF via api_base plus a trojanized dependency, with a multi-phase…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)