

ship-safe
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
ai-securityapi-security-testingcloud-infrastructure-security+8
847
asamassekou10/ship-safeThe independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…
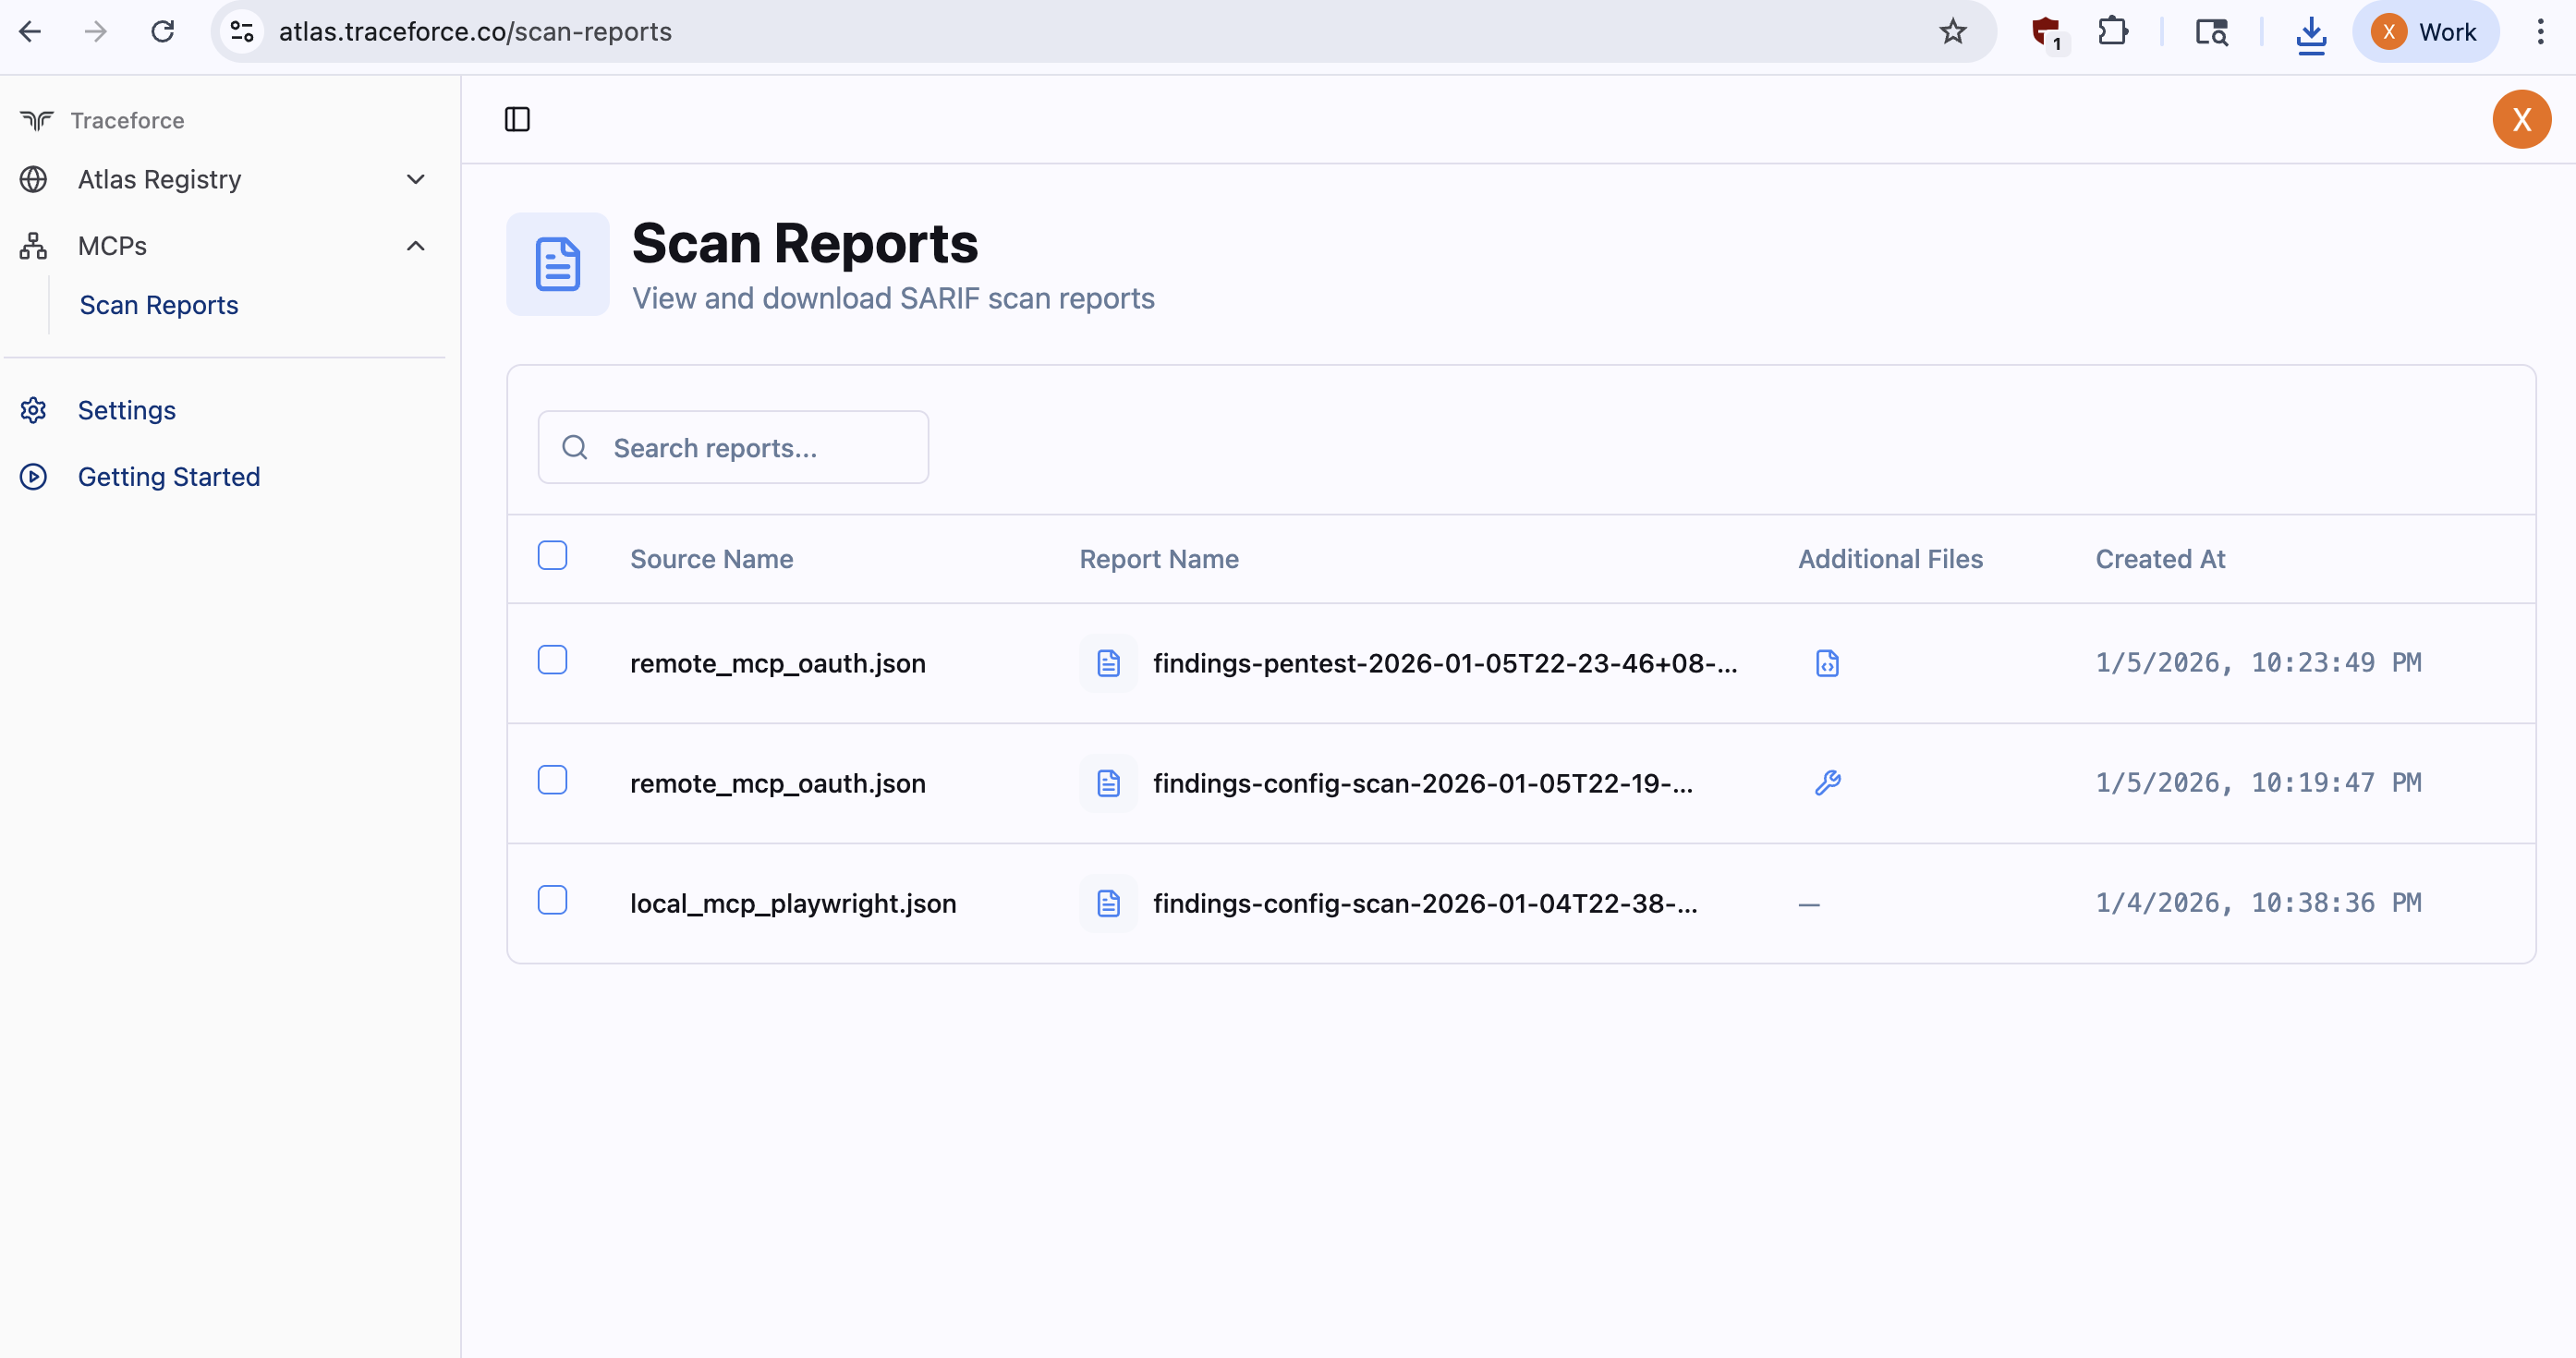 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 h4mr3r/cve-2024-5082
Proof-of-concept exploit for CVE-2024-5082, a remote code execution vulnerability in Sonatype Nexus Repository Manager 2 via crafted Maven artifacts…
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
 lirantal/cve-2024-21533-poc-ggit
Proof-of-concept exploit for CVE-2024-21533, an argument injection vulnerability in the ggit npm package that allows arbitrary command execution via…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 anupamojha-eng/sentinel-transitive-cve-demo
Sentinel demo: transitive snakeyaml CVE-2022-1471 via Spring Boot + exploitable code pattern
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 astaruf/cve-2026-44590
Proof-of-concept exploit for CVE-2026-44590, a command injection in Sherlock's GitHub Actions workflow enabling RCE and GITHUB_TOKEN exfiltration via…
 gouldnicholas/cve-2026-7669-poc
PoC for CVE-2026-7669: SGLang silent trust_remote_code override -> RCE
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…