

hijagger
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
dns-analysisosintreconnaissance+3
firefart/hijaggerChecks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 paultendo/confusable-vision
793 confusable pairs missing from Unicode TR39, world-first cross-script dataset, font-aware SSIM scoring across 230 fonts and 22,000+ characters
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
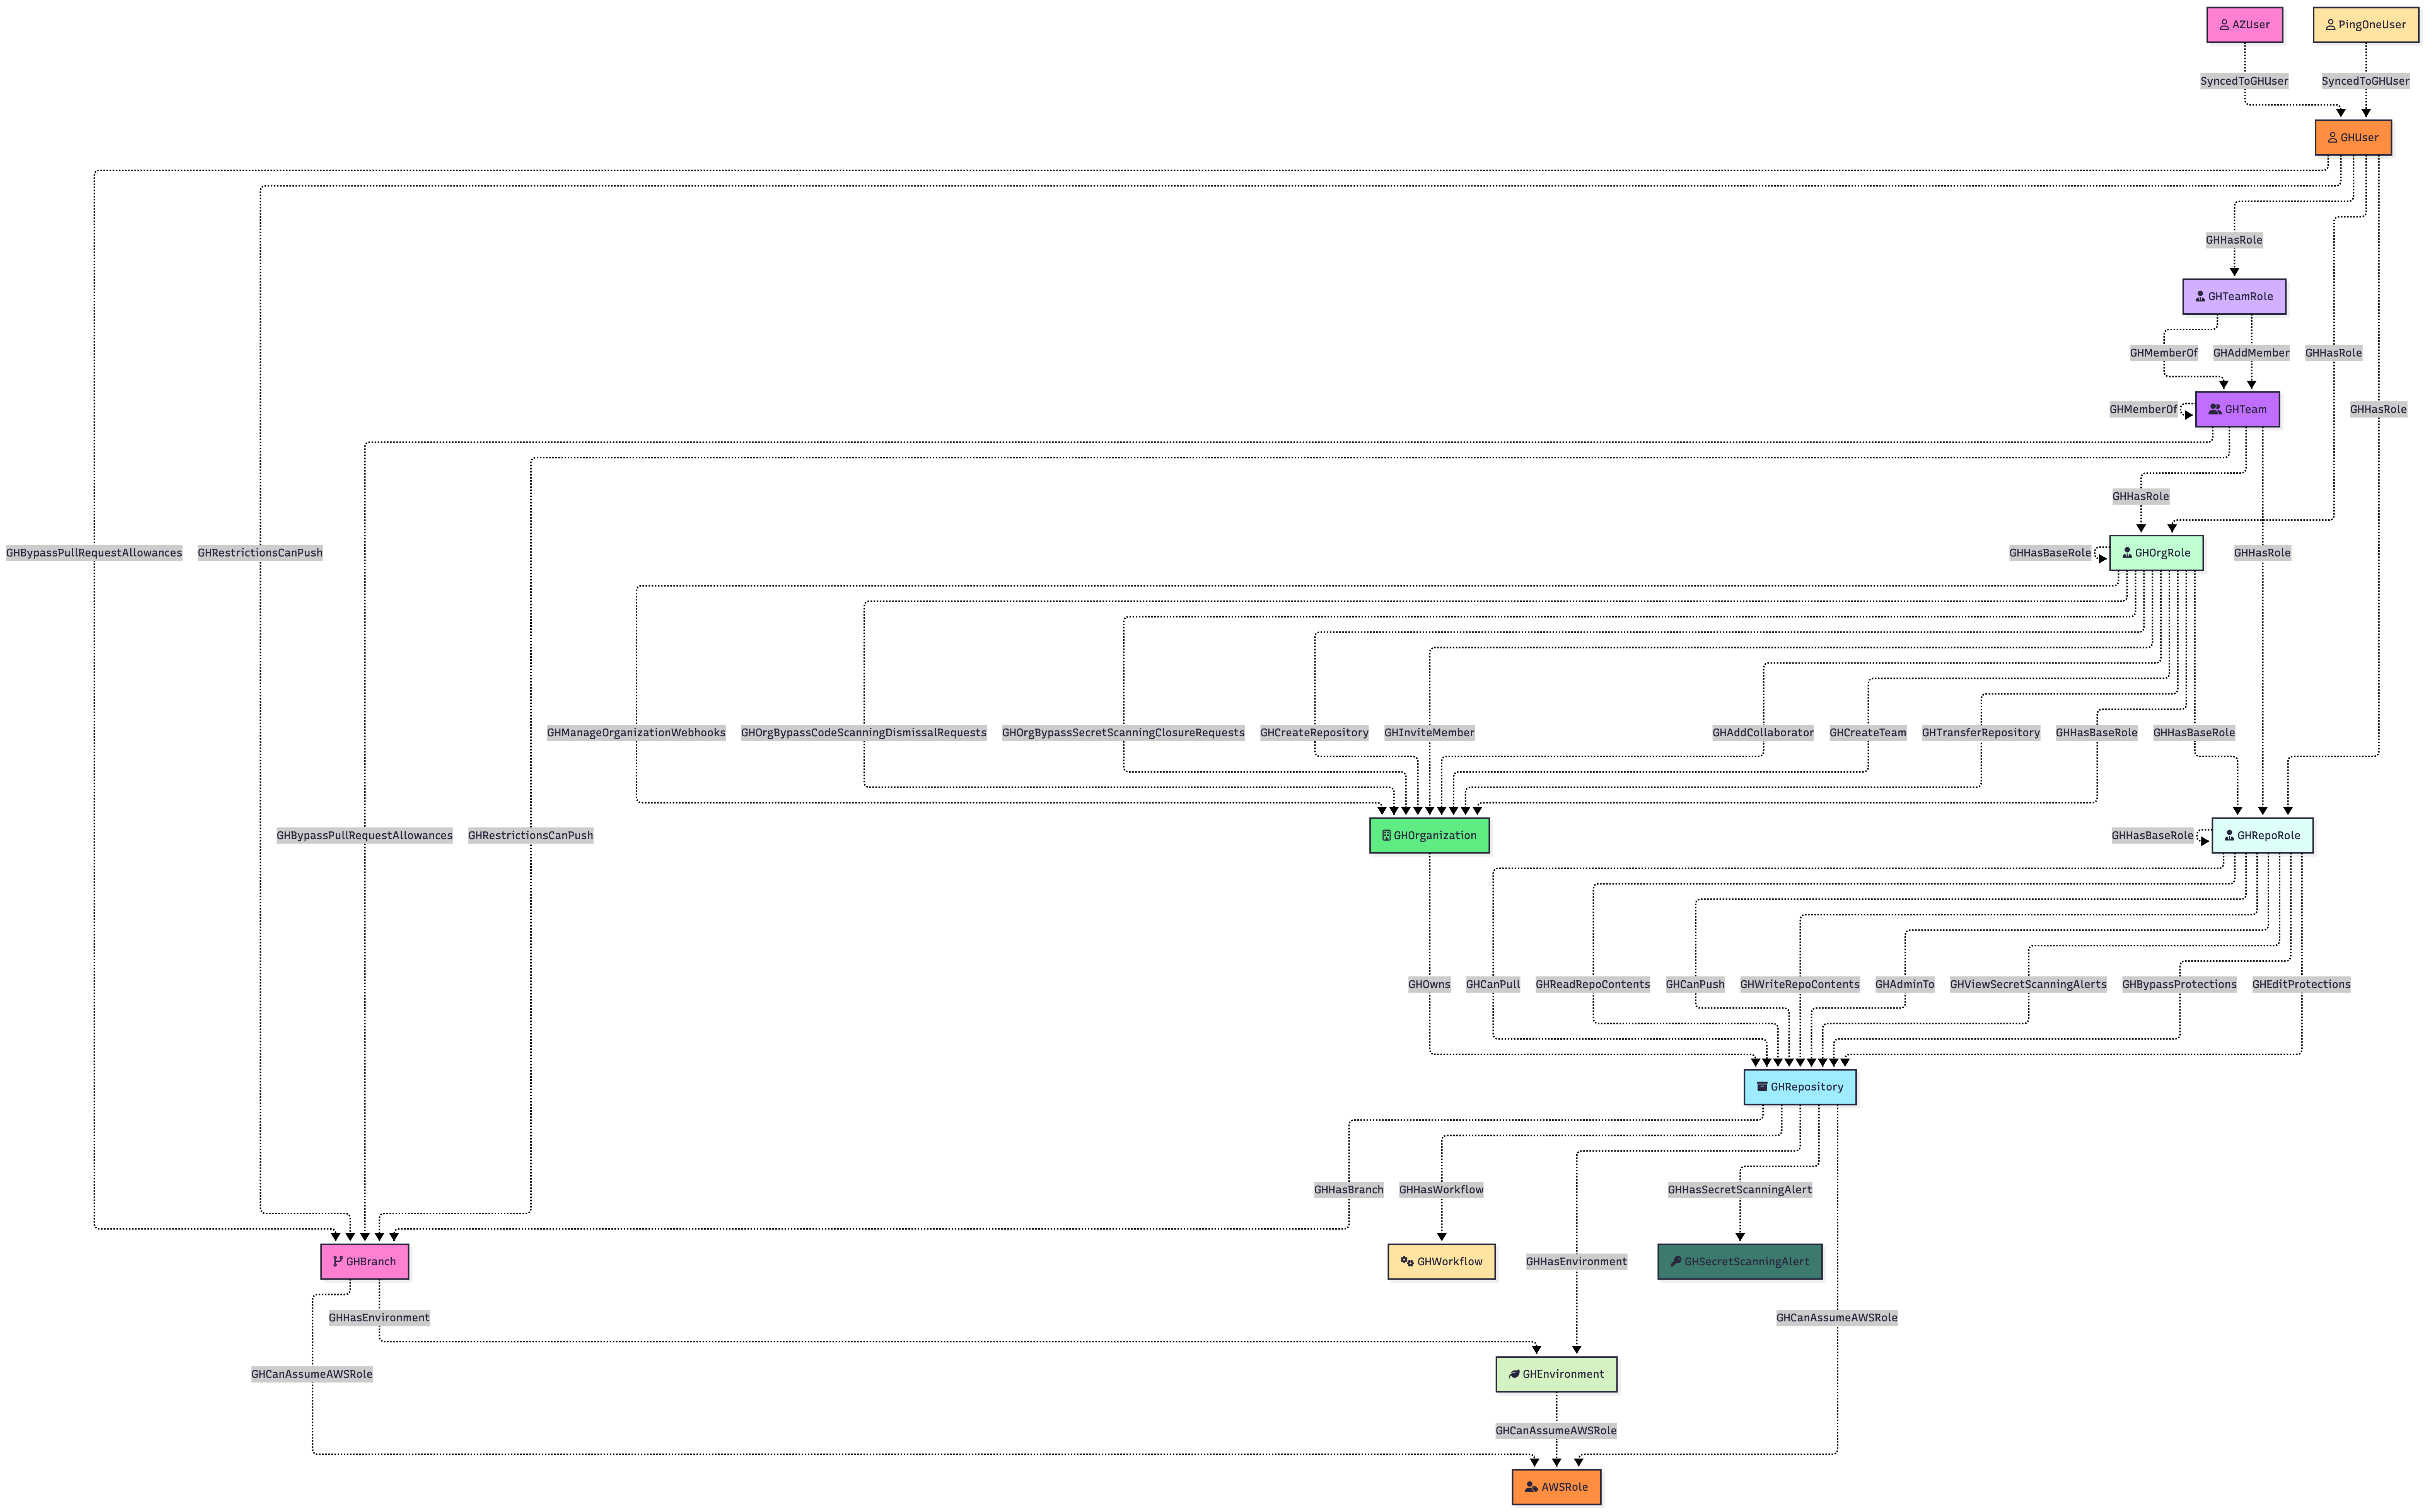 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 george0papasotiriou/cve-2026-1122-iot-firmware-update-signature-bypass-via-low-order-point-injection
Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker