
cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration

Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…

The world's first font-by-font confusables dataset: which Unicode characters look alike, measured from the outlines of 322 fonts at the size people…

Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…

VulnCheck's official command line tool

Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.

AI runtime inventory: discover shadow AI, trace LLM calls

Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.

Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.

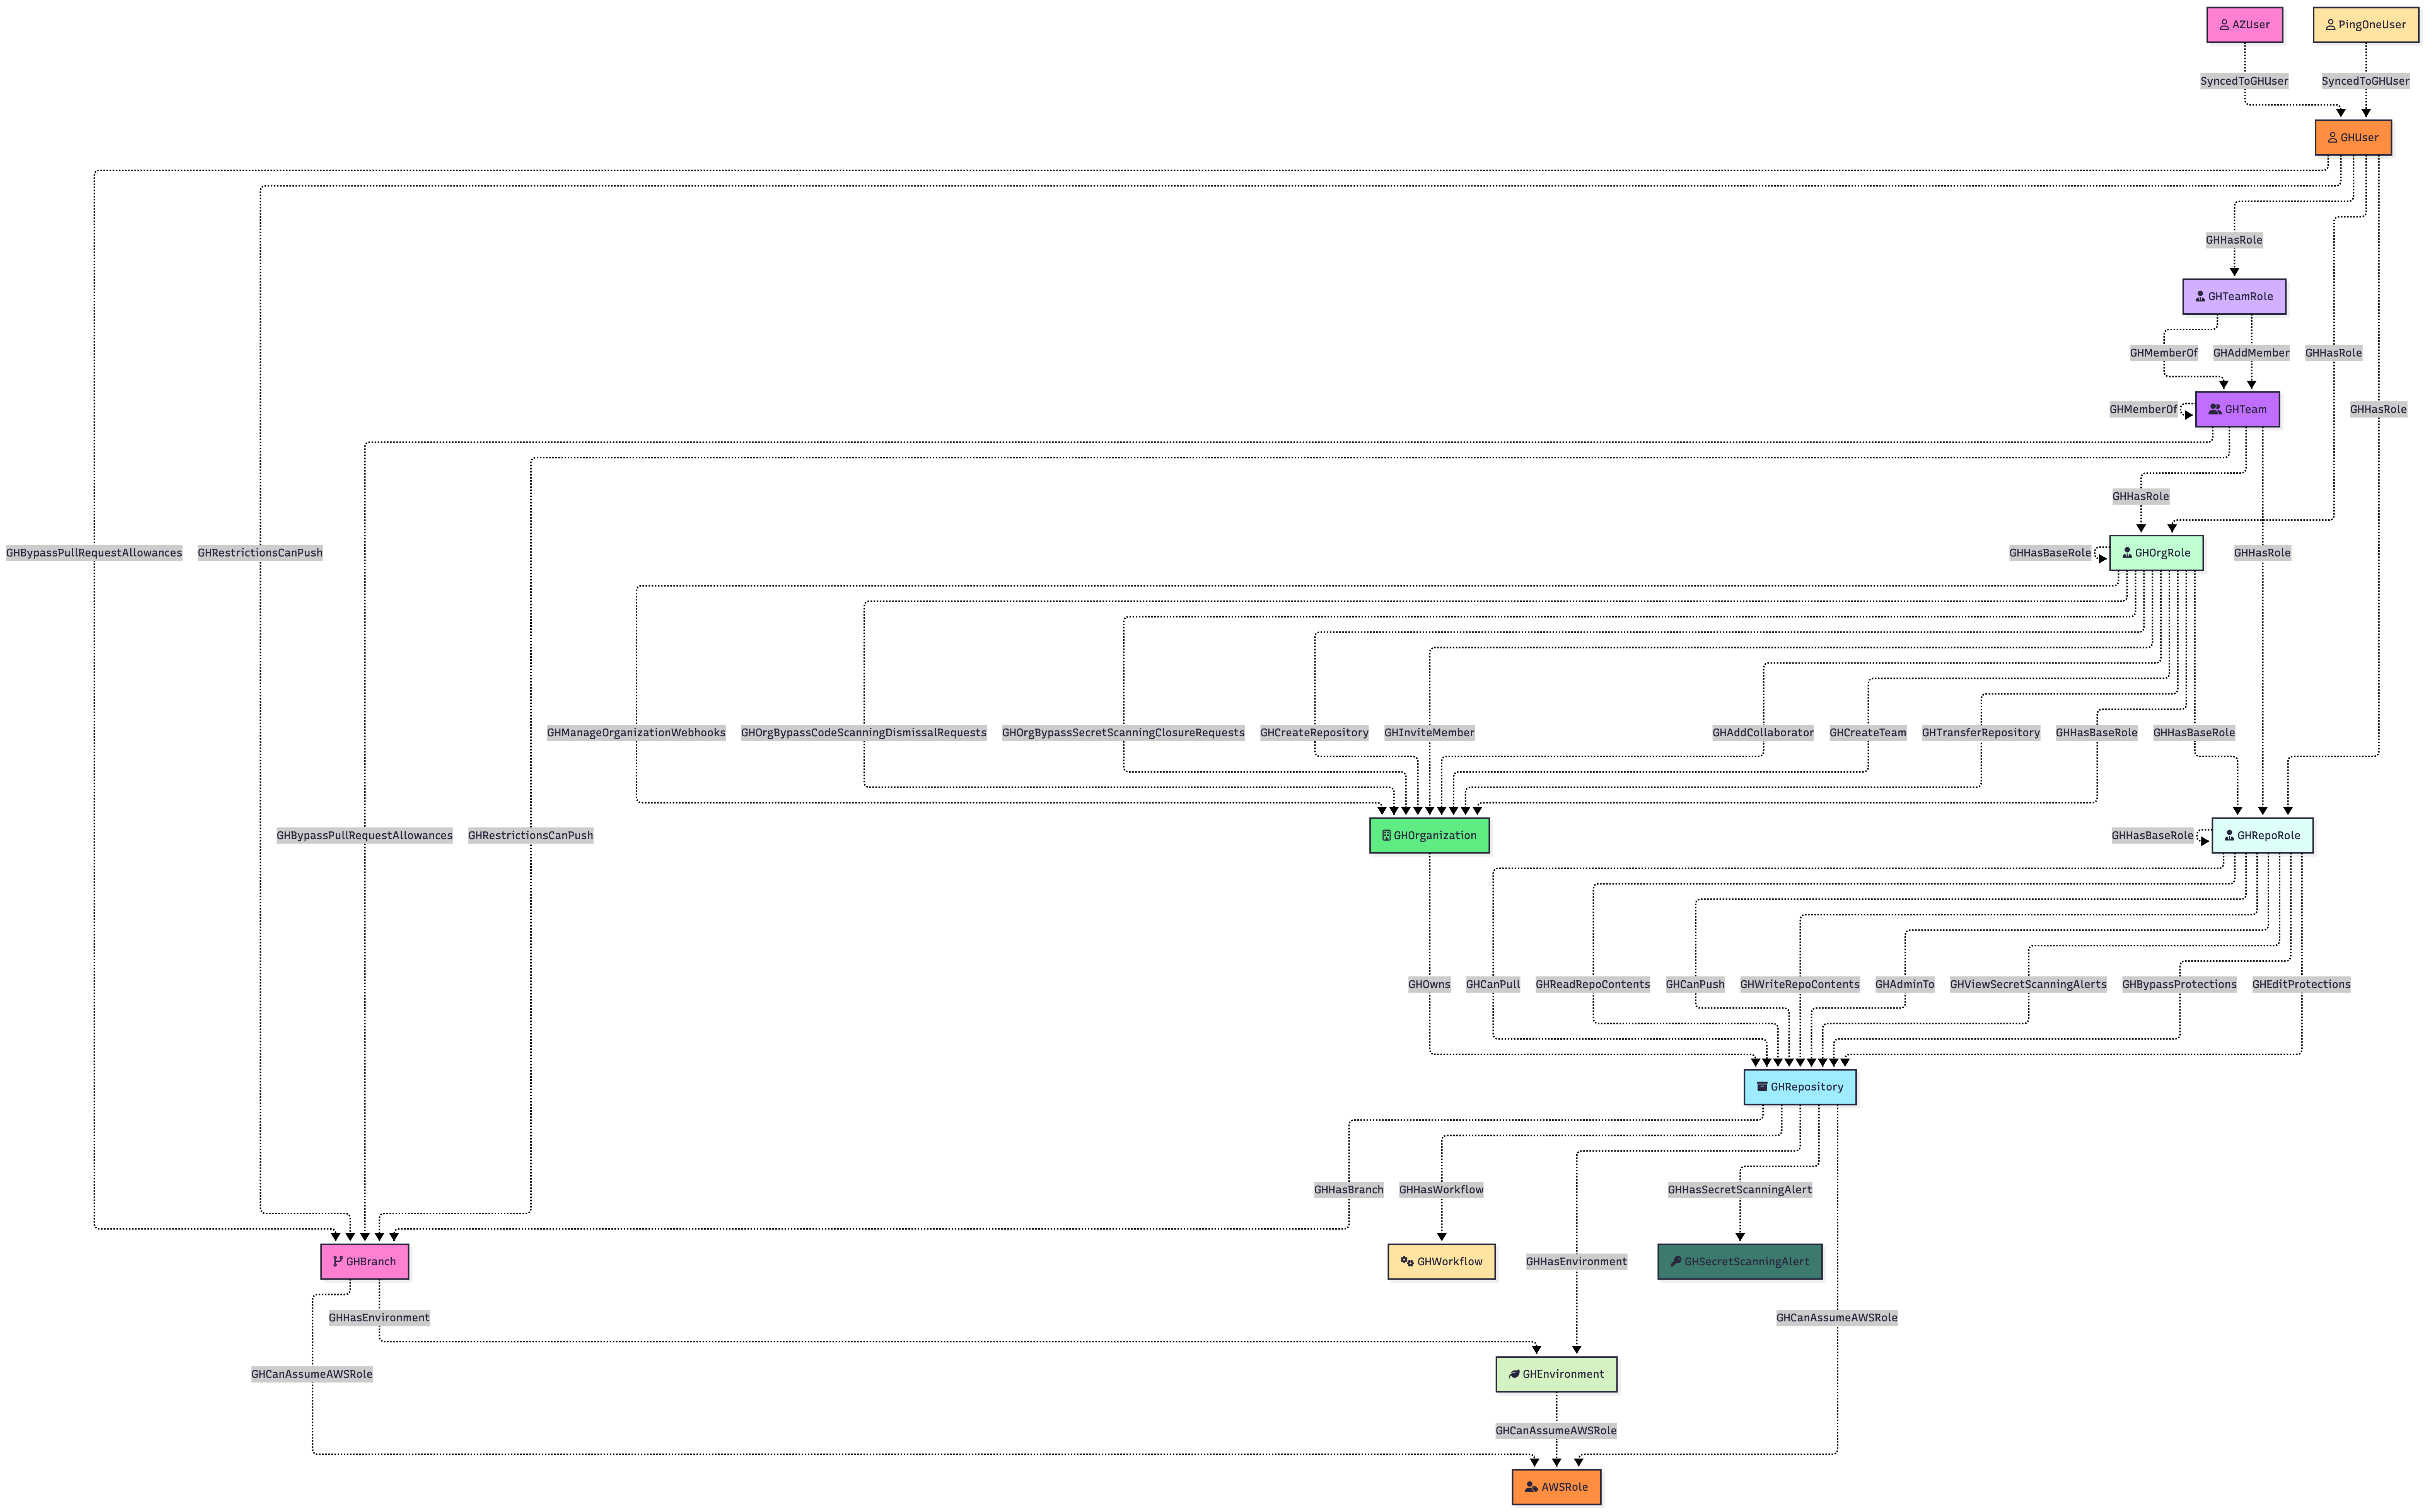
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…

Collection's of Tech Talk that are presented by me :)

Sigma detection rules for AI agent security monitoring

DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…

LLM-backed AI agent security — inbound injection detection + outbound privacy protection

Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…

Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker