
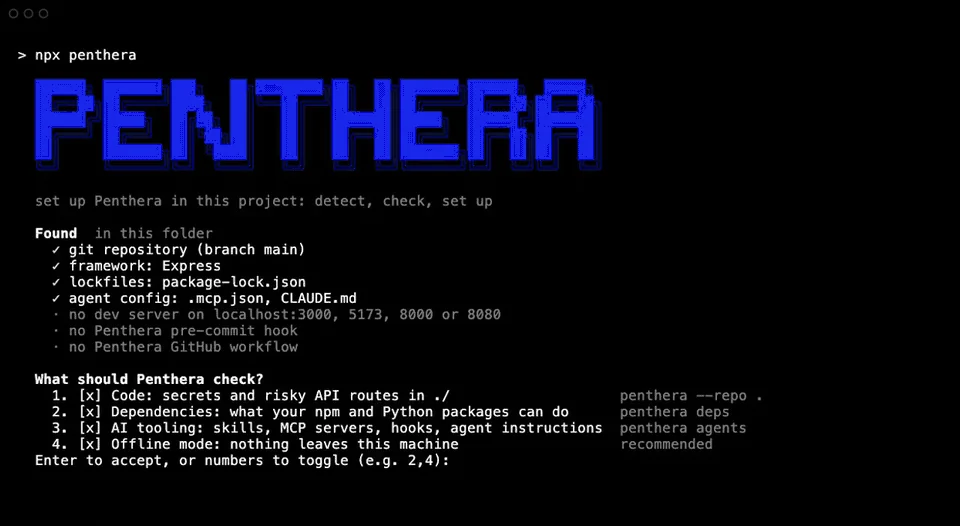
penthera
 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
ai-securitycode-analysisconfiguration-auditing+7
78
danoszz/pentheraOffline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 happyhackingspace/claude-code-backdoor-check
Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
 jschauma/emudhra
Example programs in Go, Java, Node, Perl, Python, Ruby, Rust, and curl that test whether a TLS trust store rejects connections to known-bad eMudhra…
 gmh5225/oz-known-issues
Find the version that the project you currently develop or audit uses and quickly check which are the known smart contract security vulnerabilities…
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 leonlai-tw/php-eol-cve-2026-109618-109619
Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…
 alvm/php2shell-eol-backport
Unofficial fix for CVE-2026-109618 / CVE-2026-109619 (php2shell) for the end-of-life PHP 5.4 / 5.3 packages of RHEL, CentOS and Oracle Linux 7 / 6
 certifi/python-certifi
(Python Distribution) A carefully curated collection of Root Certificates for validating the trustworthiness of SSL certificates while verifying the…
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulncheck-oss/cli
VulnCheck's official command line tool
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 ahmed-elmahgob/poc-cve-2026-102282
CVE-2026-102282: adm-zip LPE via SUID/SGID preservation during archive extraction (fixed in 0.6.1)
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection