

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k0 days ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 anchore/grype
A vulnerability scanner for container images and filesystems
 mmiszczyk/cve-2021-33879
GameLoop update MITM
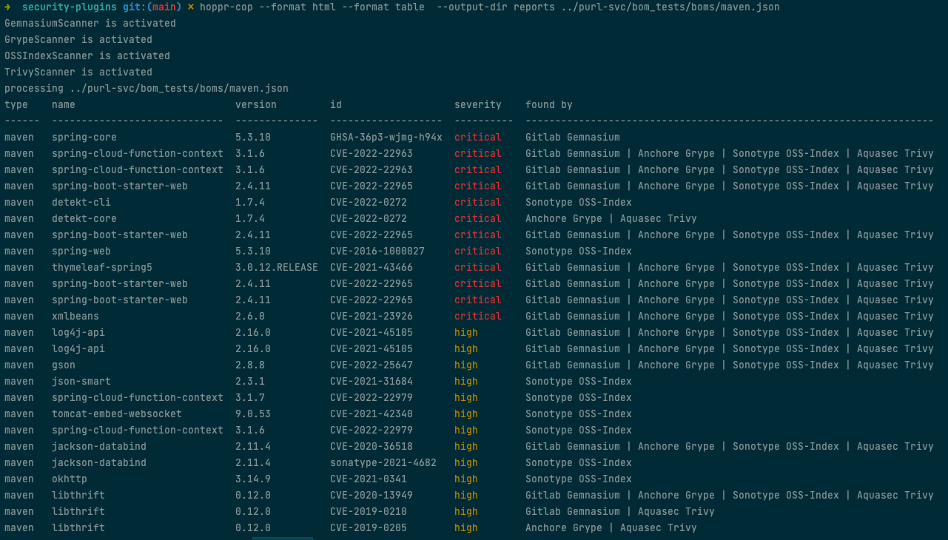
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 pypa/advisory-database
Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…
 google/osv.dev
Open source vulnerability DB and triage service.
 aaravmaloo/revera
The credit score for npm packages. Analyze package reputation, maintenance, security, publisher trust, and ecosystem health before you install any…
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…