

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
124
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 qubesos/qubes-secpack
Curated repository of Qubes OS security bulletins, canaries, PGP keys, and ISO digests, with authenticated verification via git tags and detached…
 agwa/git-crypt
Transparent file encryption in git
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
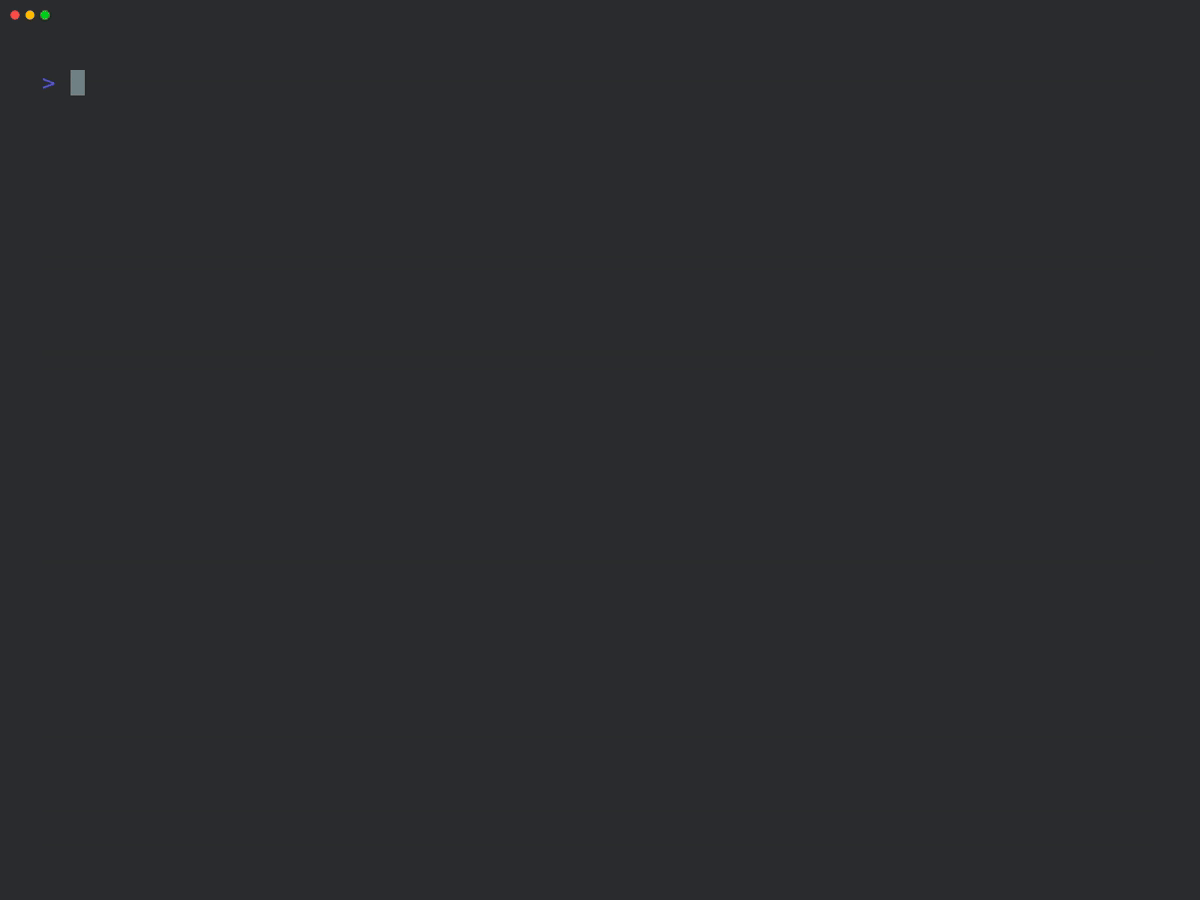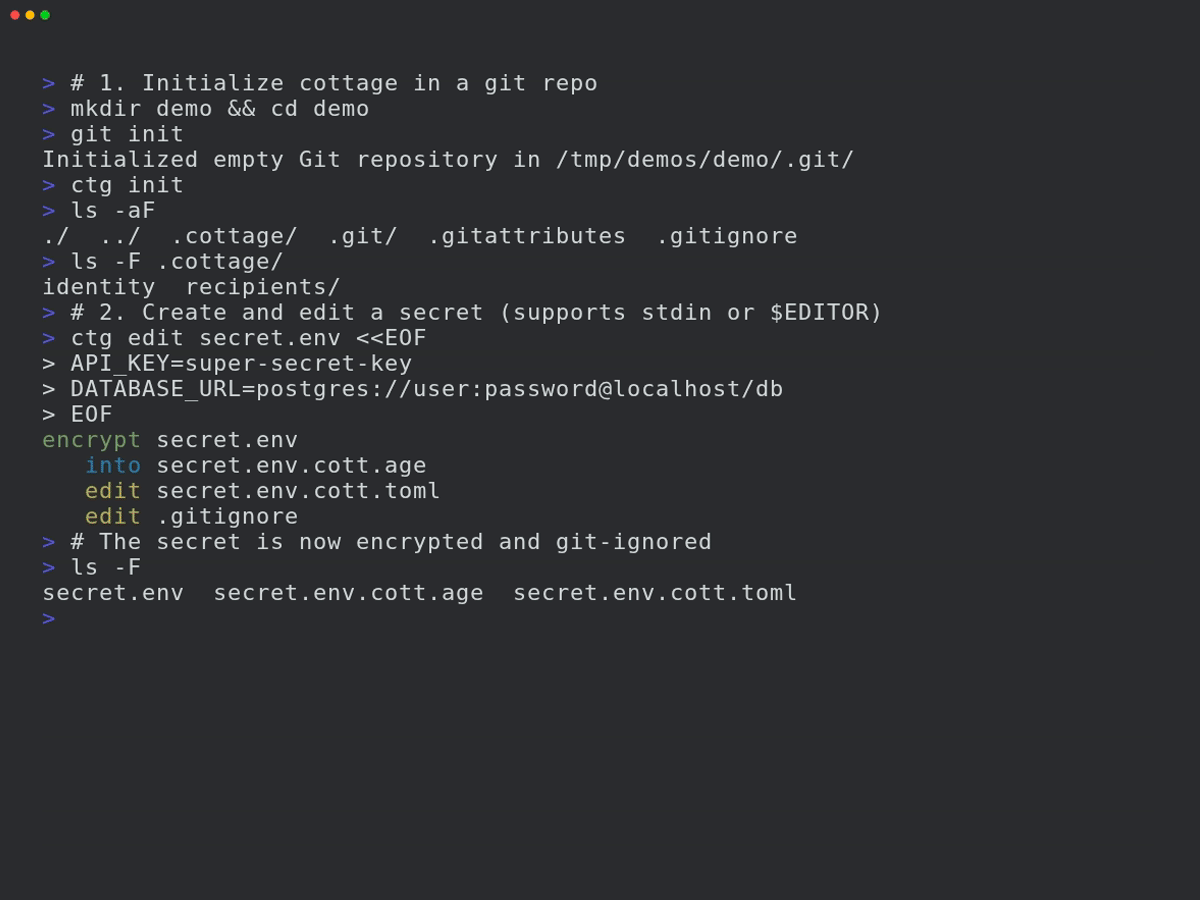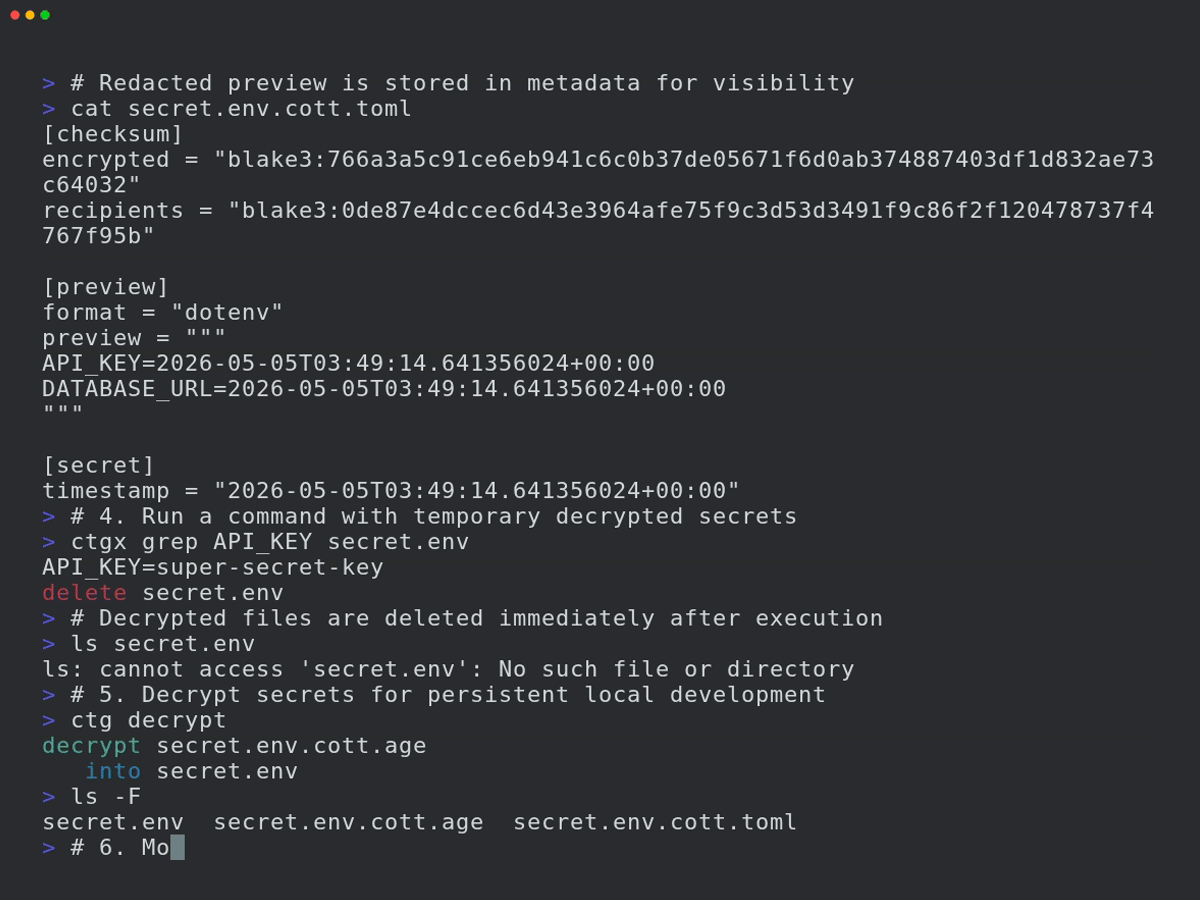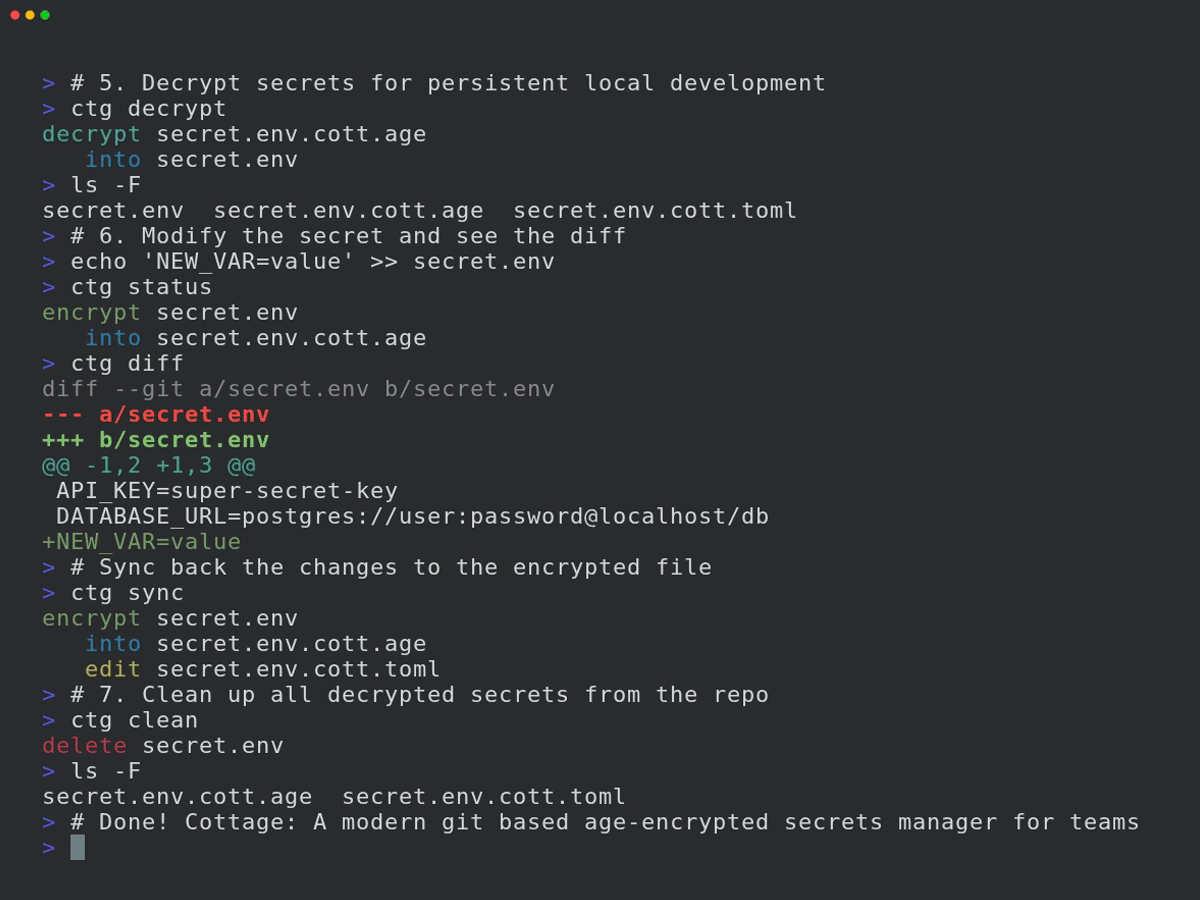 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 sondermc/git-cveissues
vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
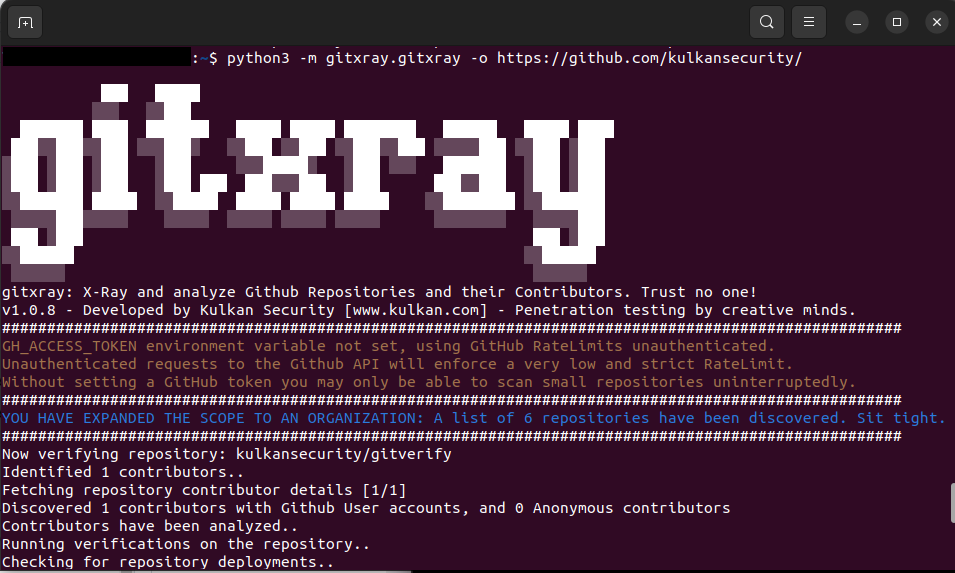 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 reposaur/reposaur
Open source compliance tool for development platforms.
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
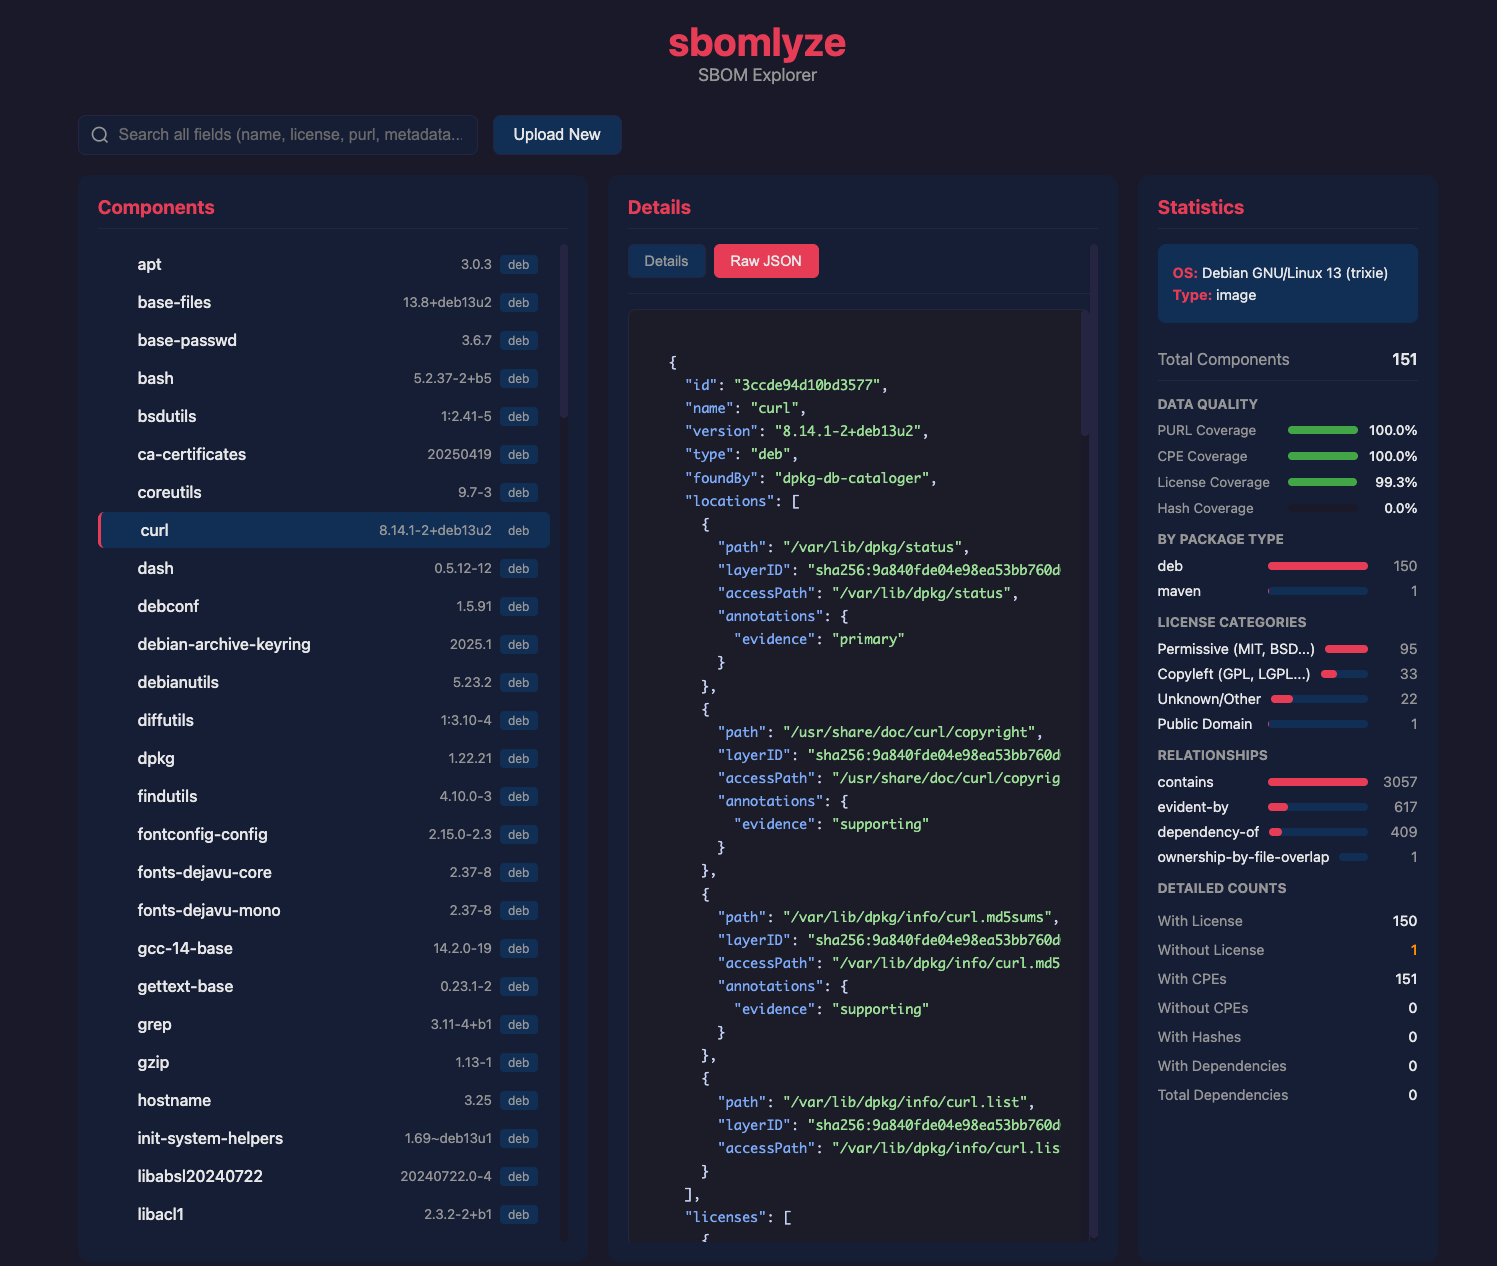 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.