

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.3k1 day ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
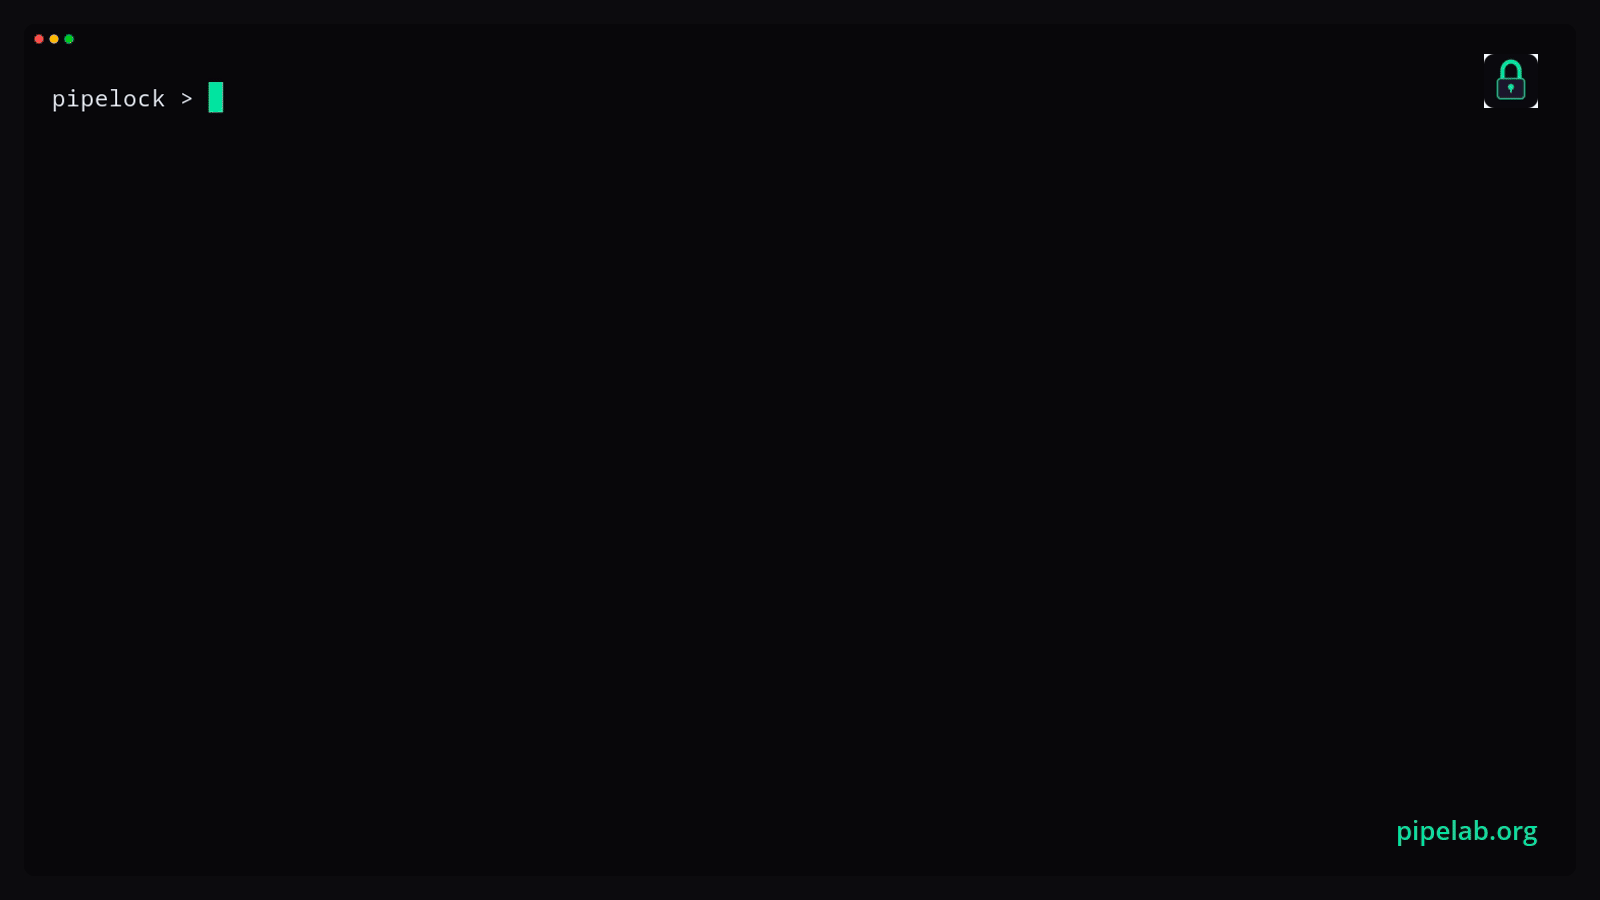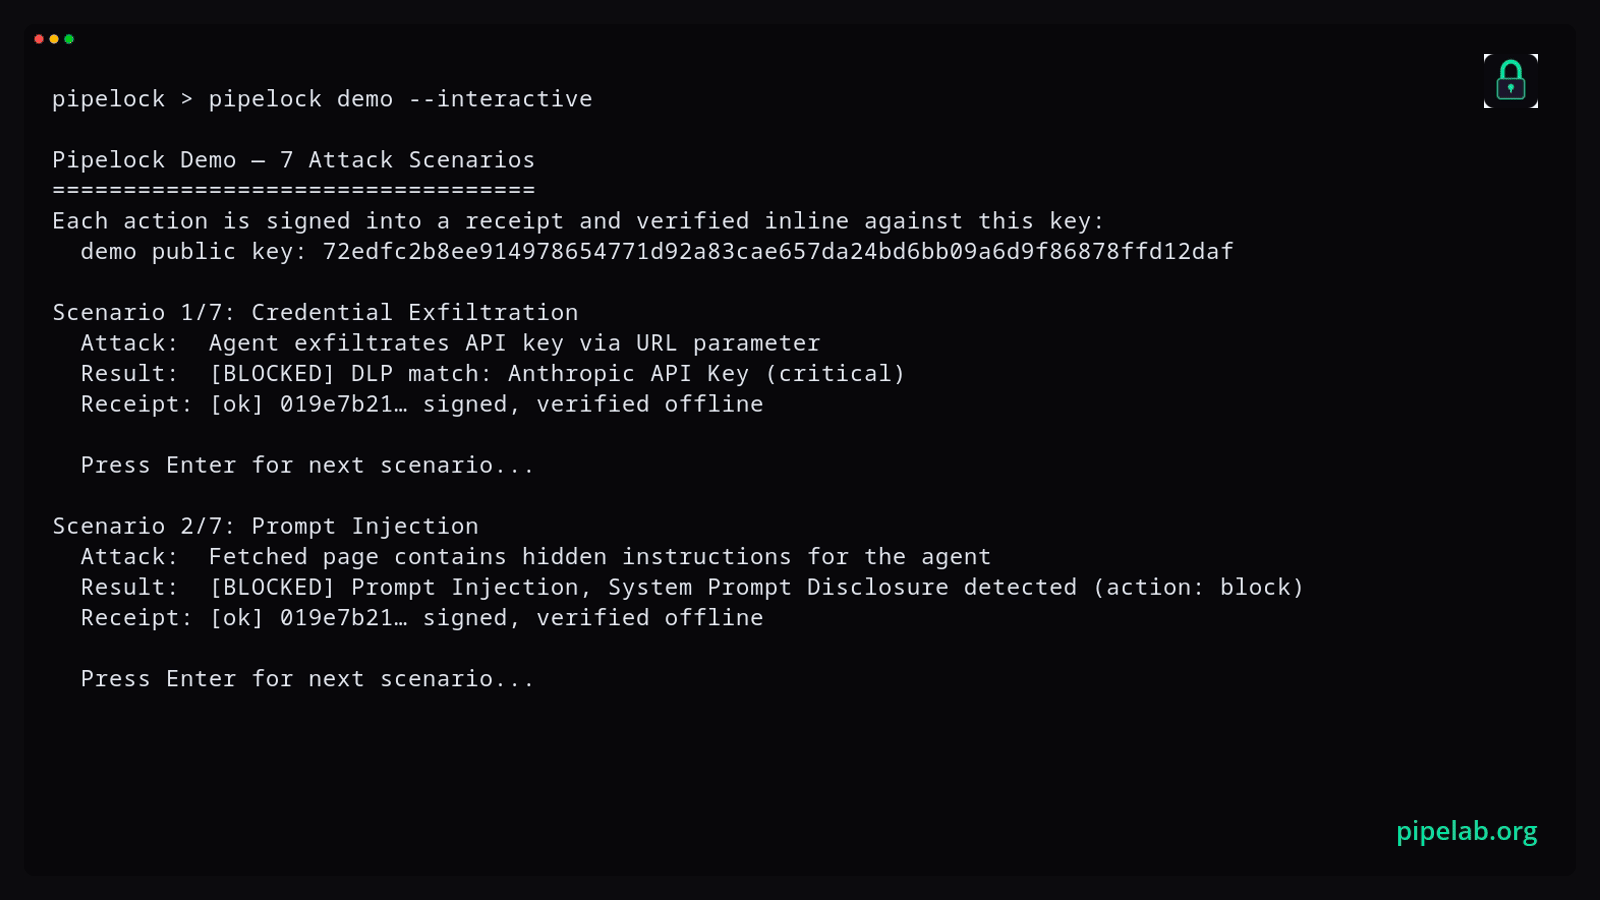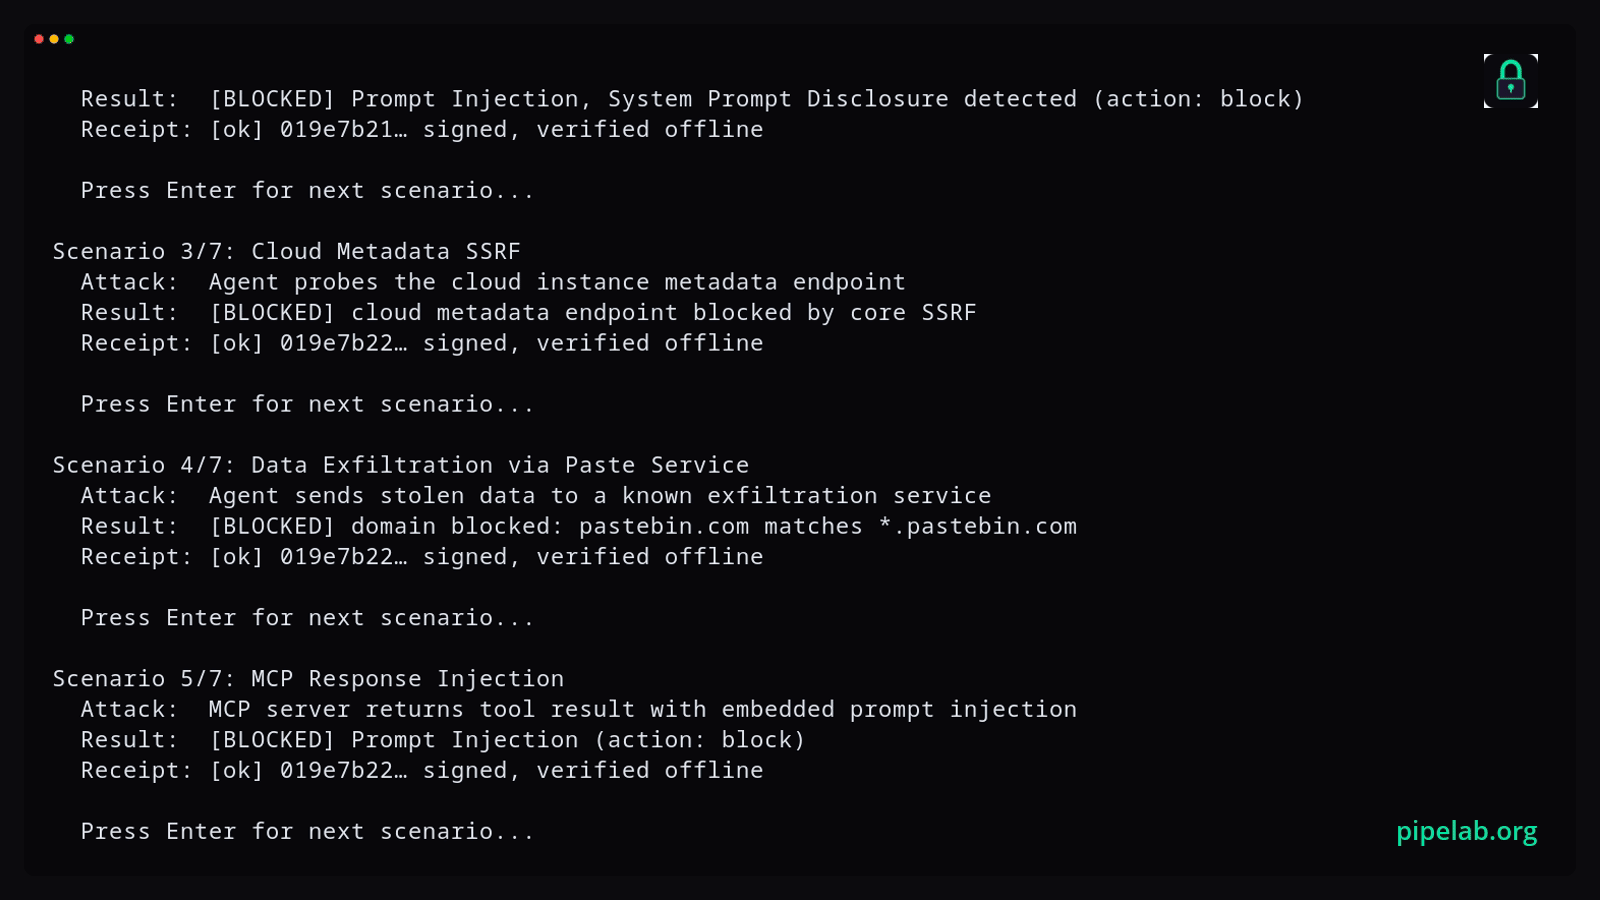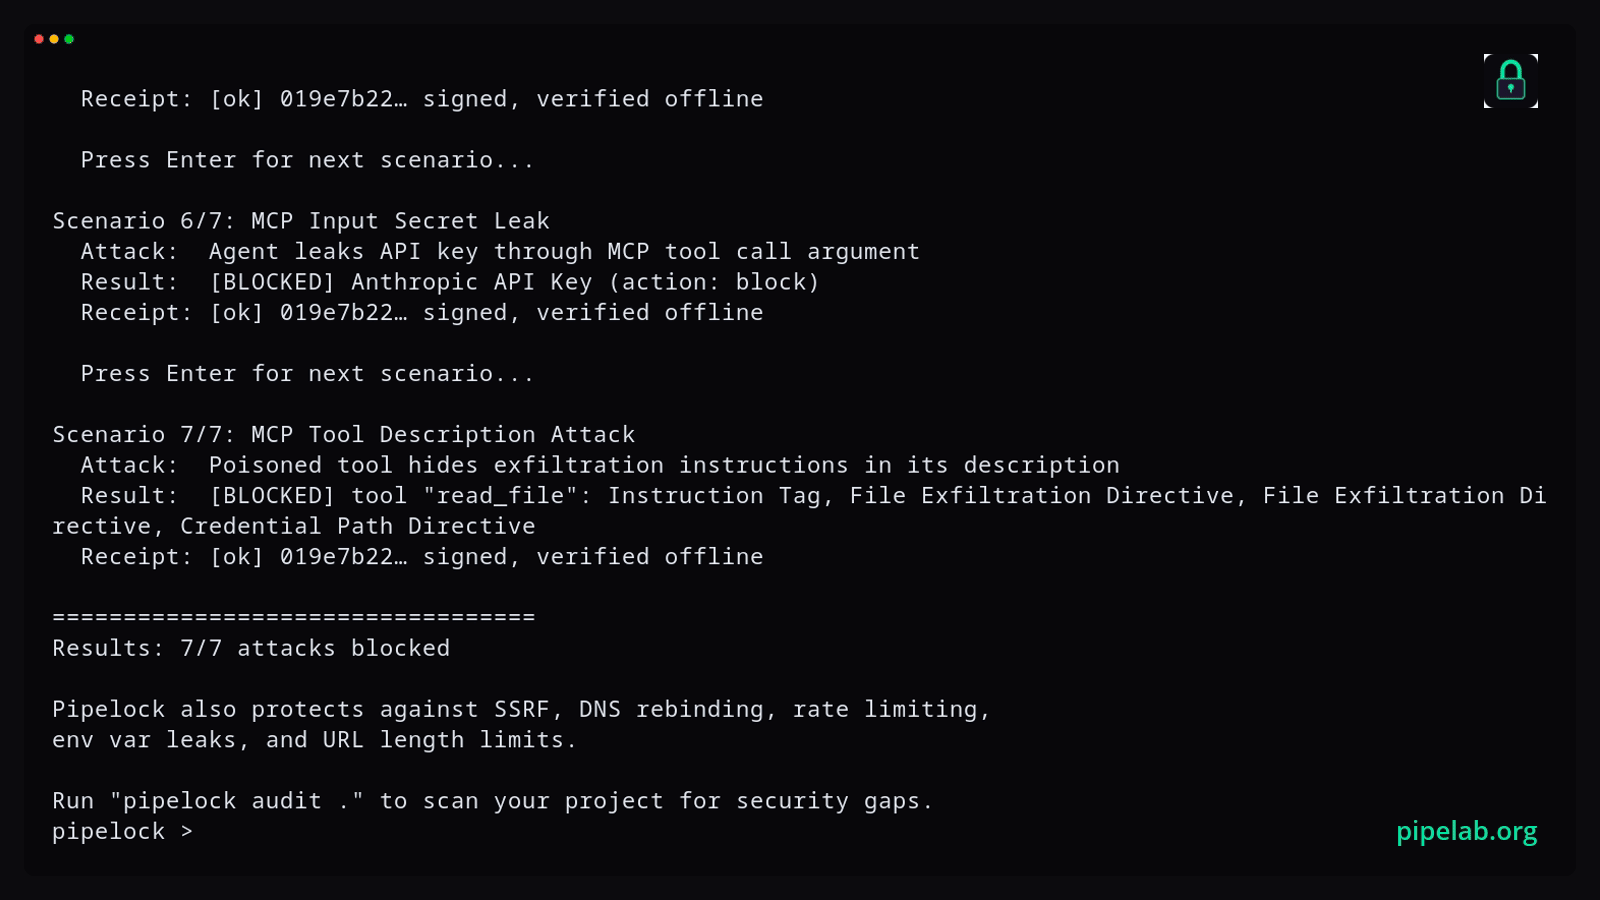 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…