

ApplicationInspector
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
code-analysisdevsecopsstatic-analysis+3
4.4k
microsoft/applicationinspectorA source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
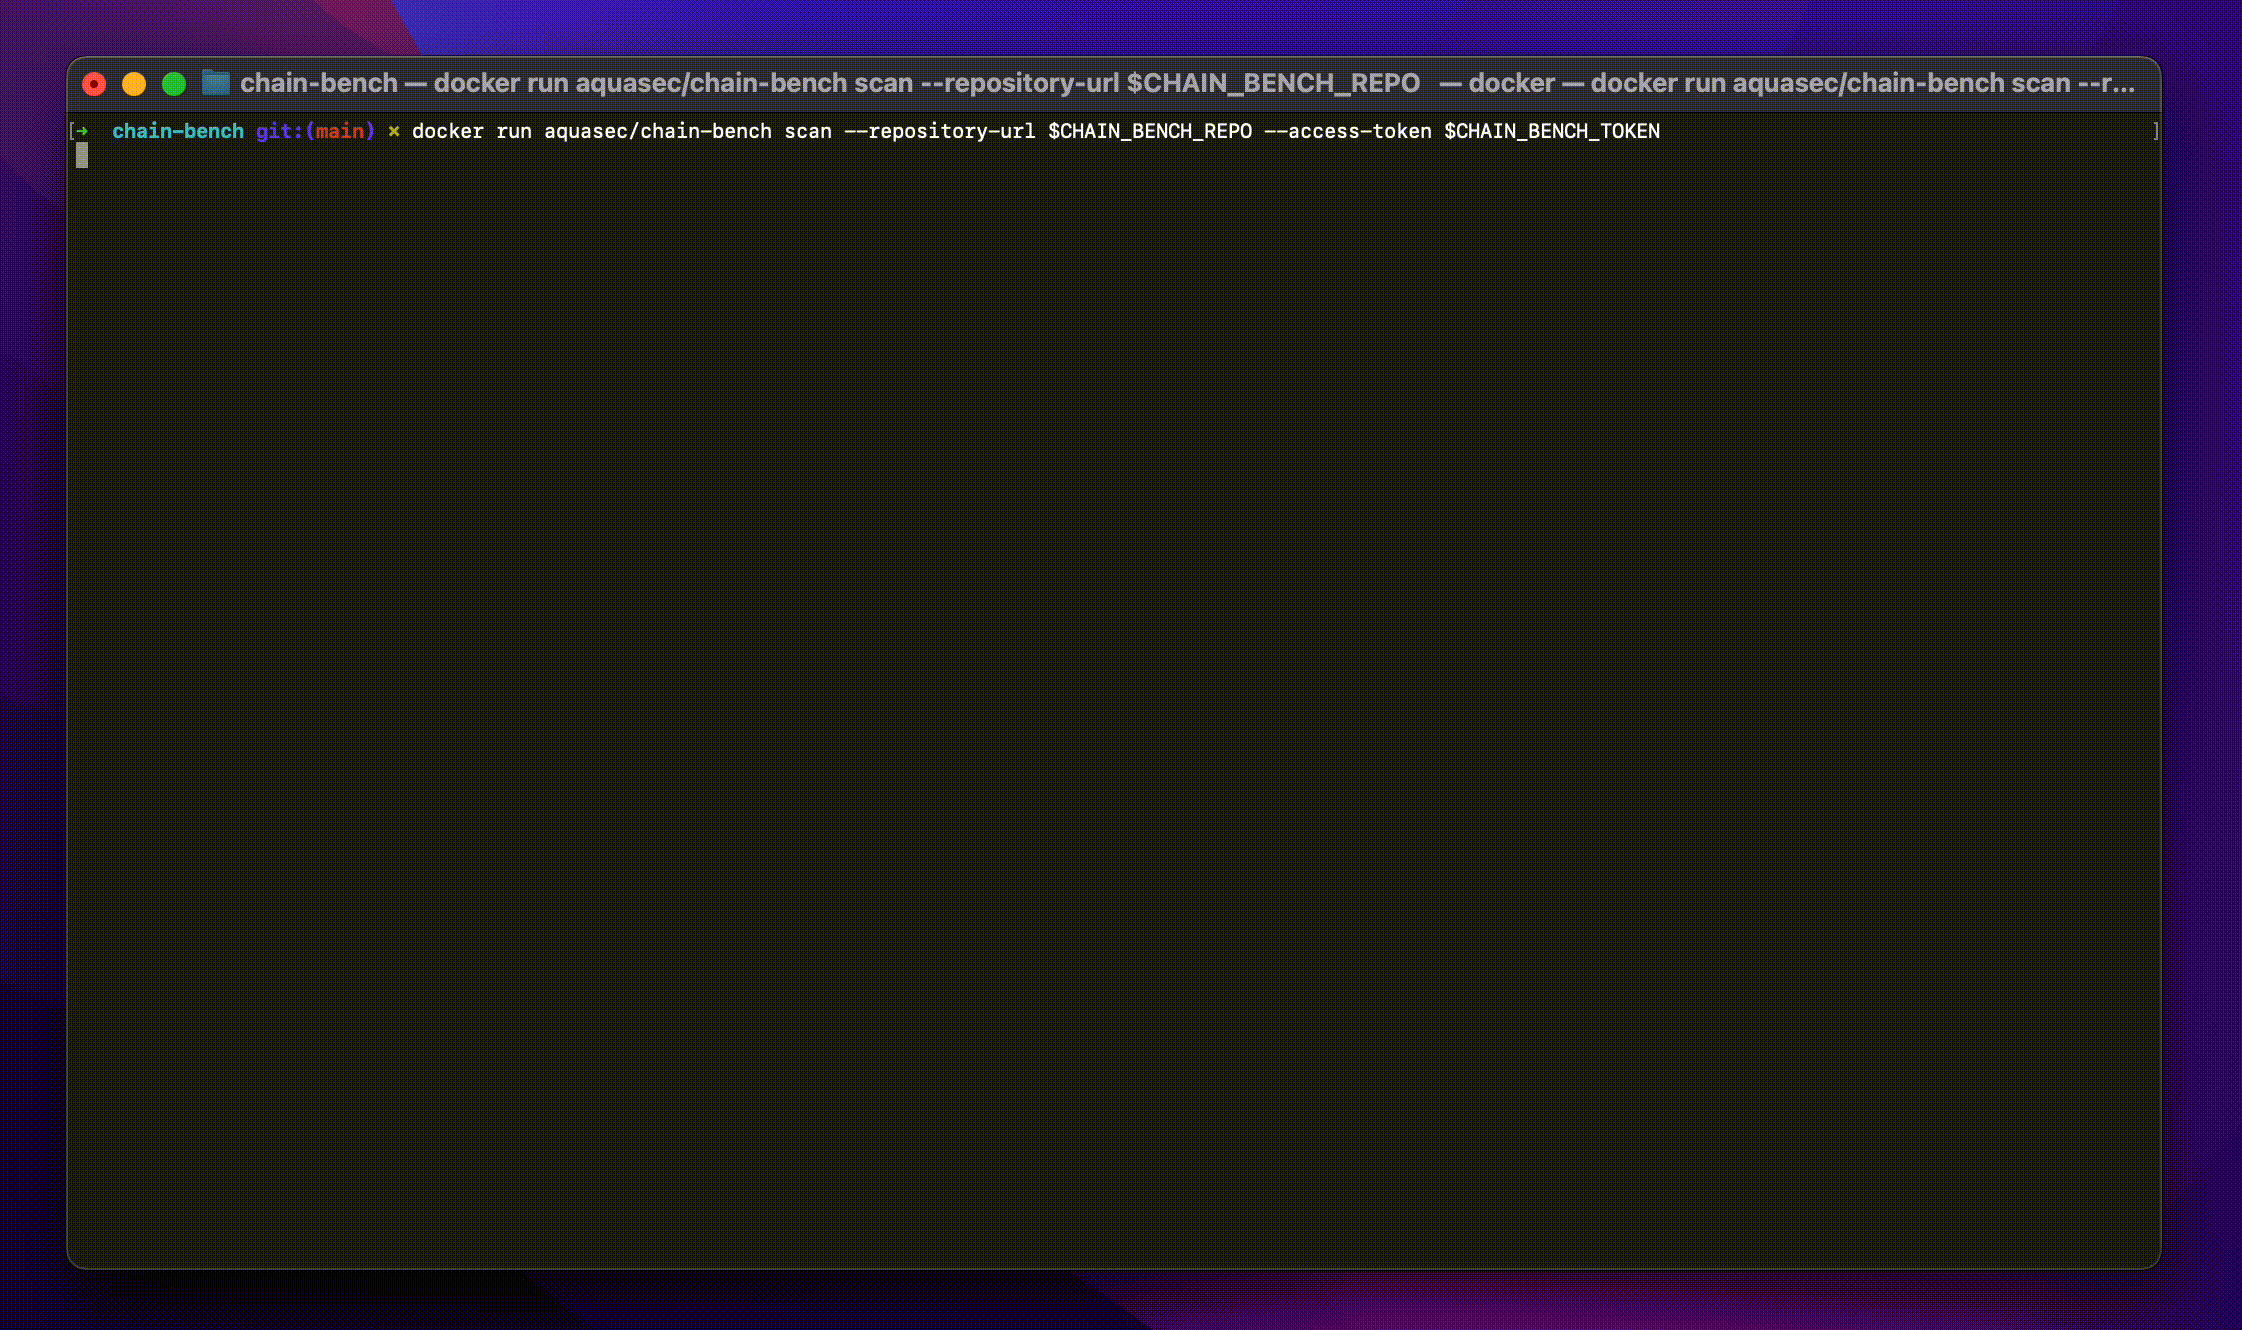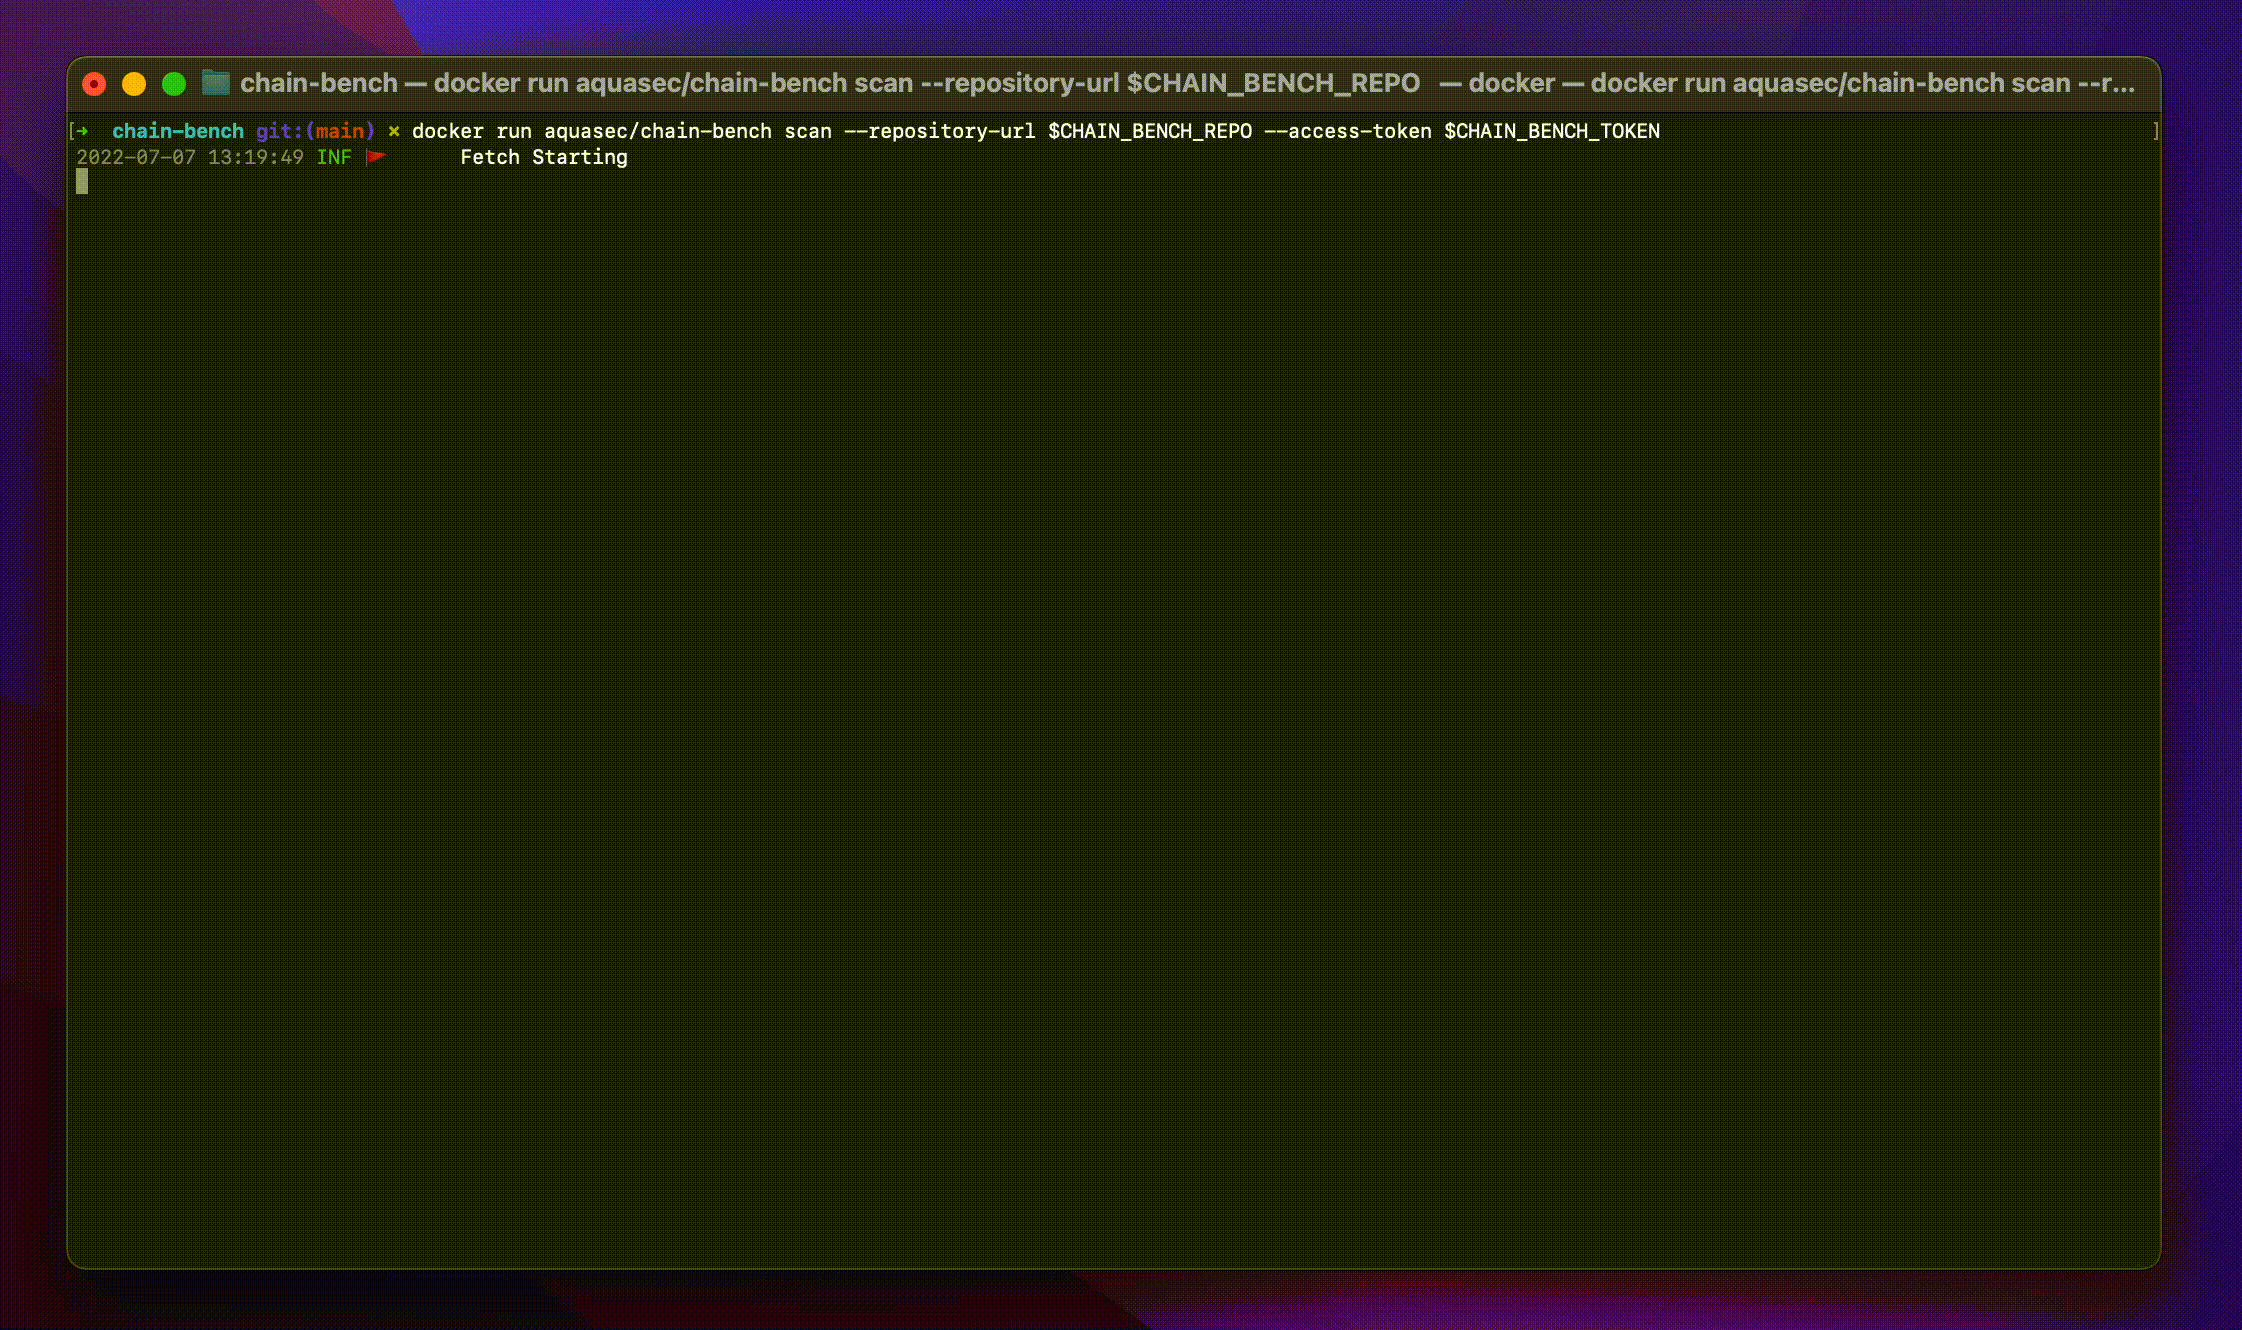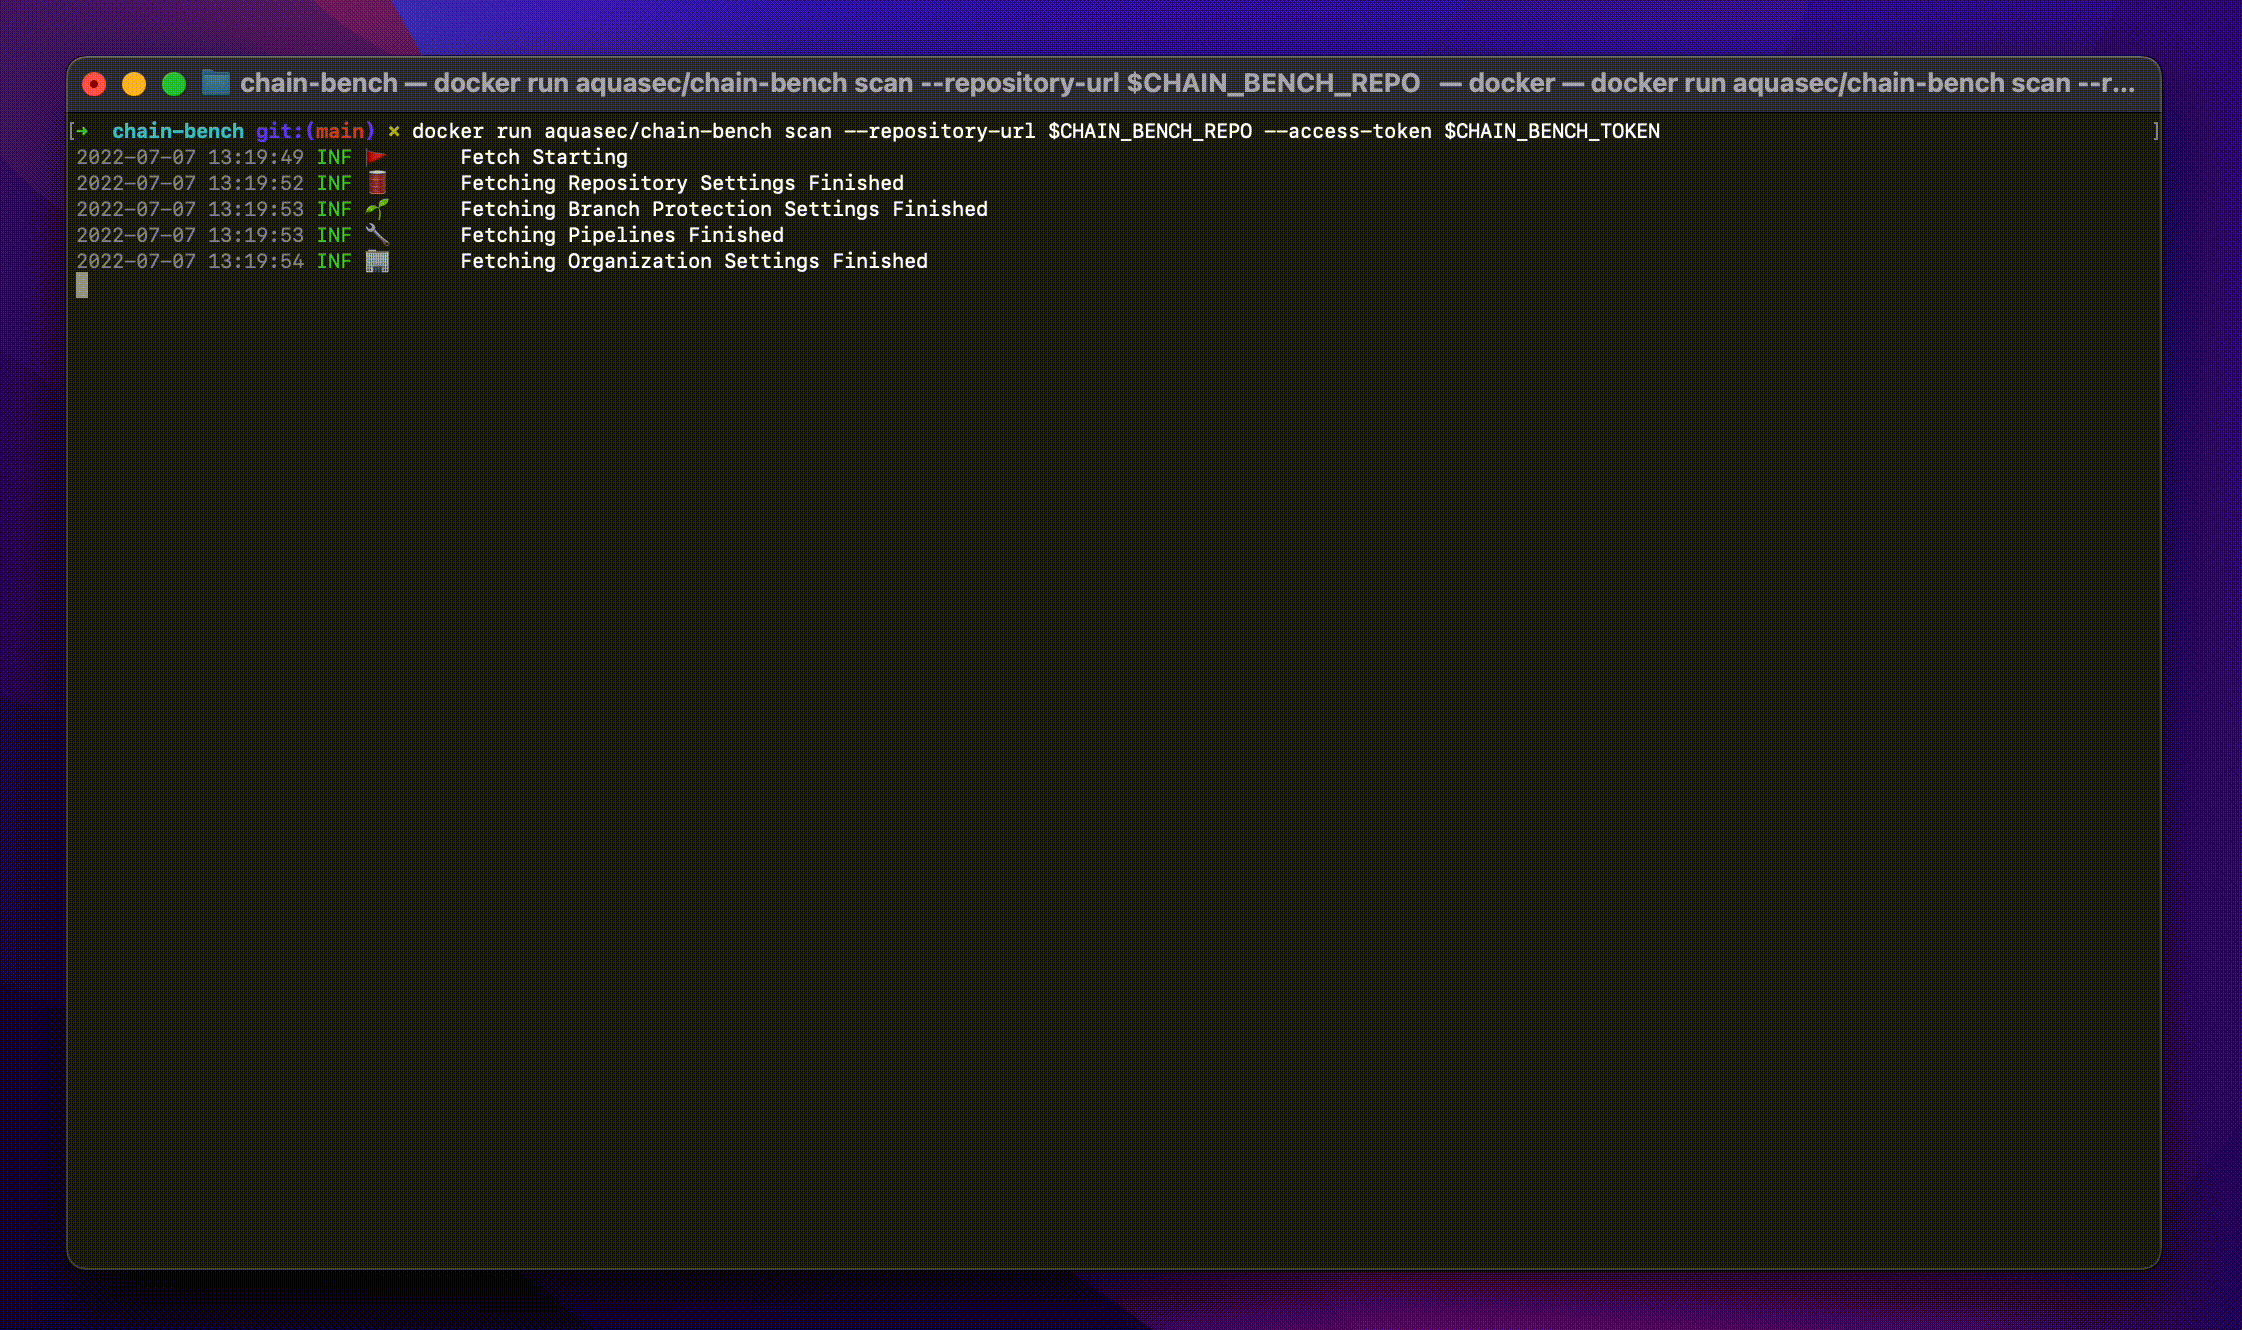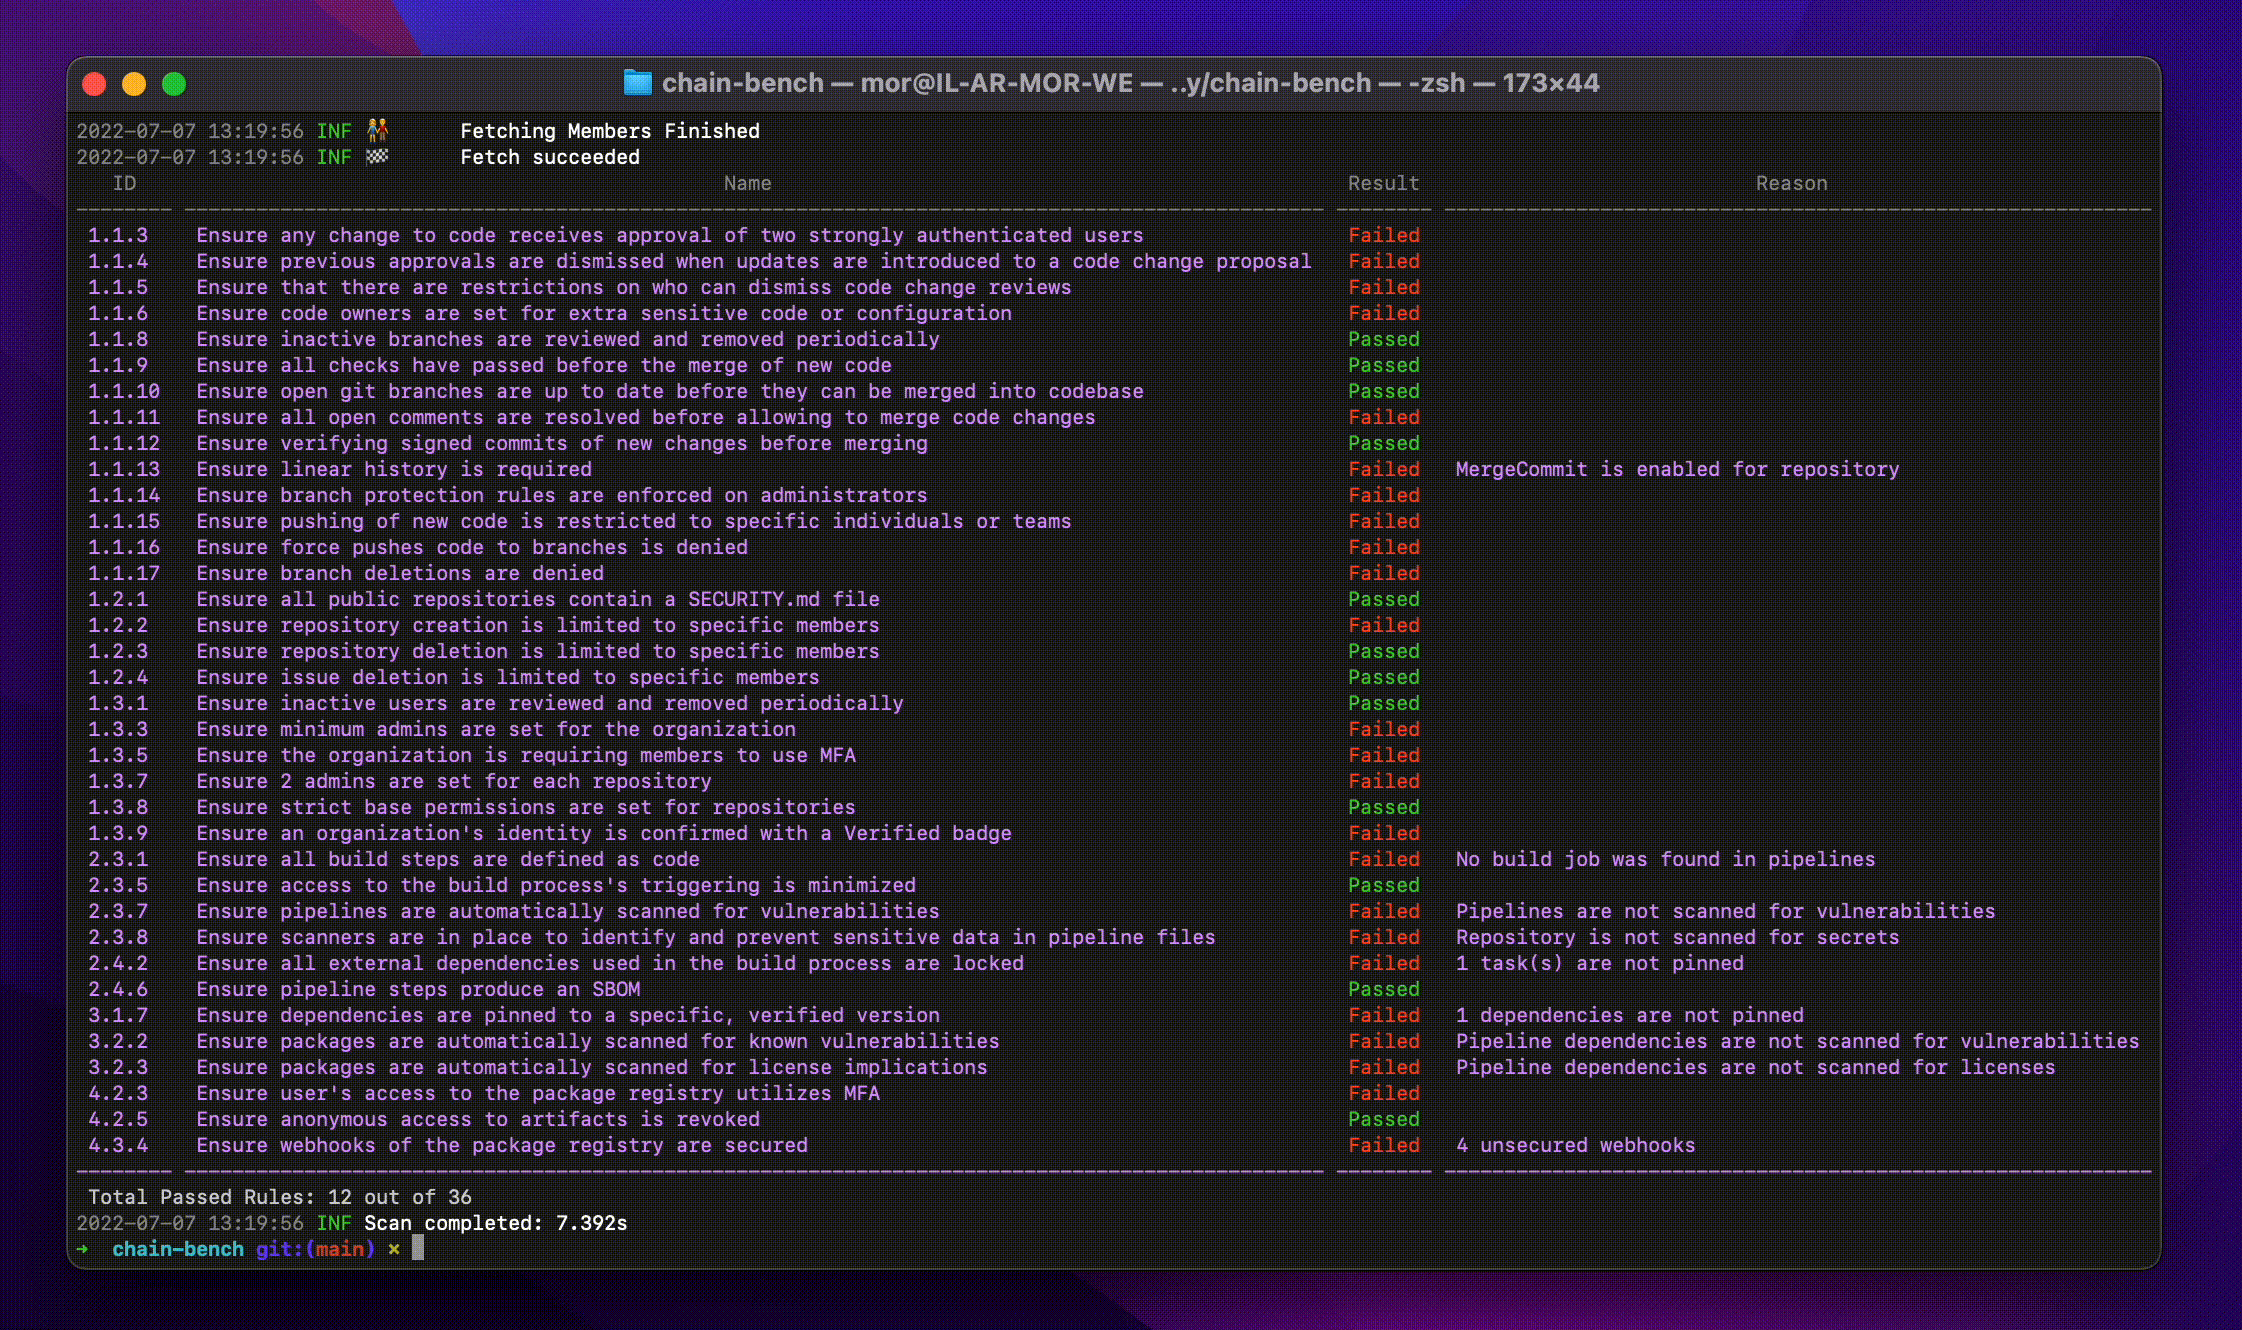 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 project-oak/oak
Meaningful control of data in distributed systems.
 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
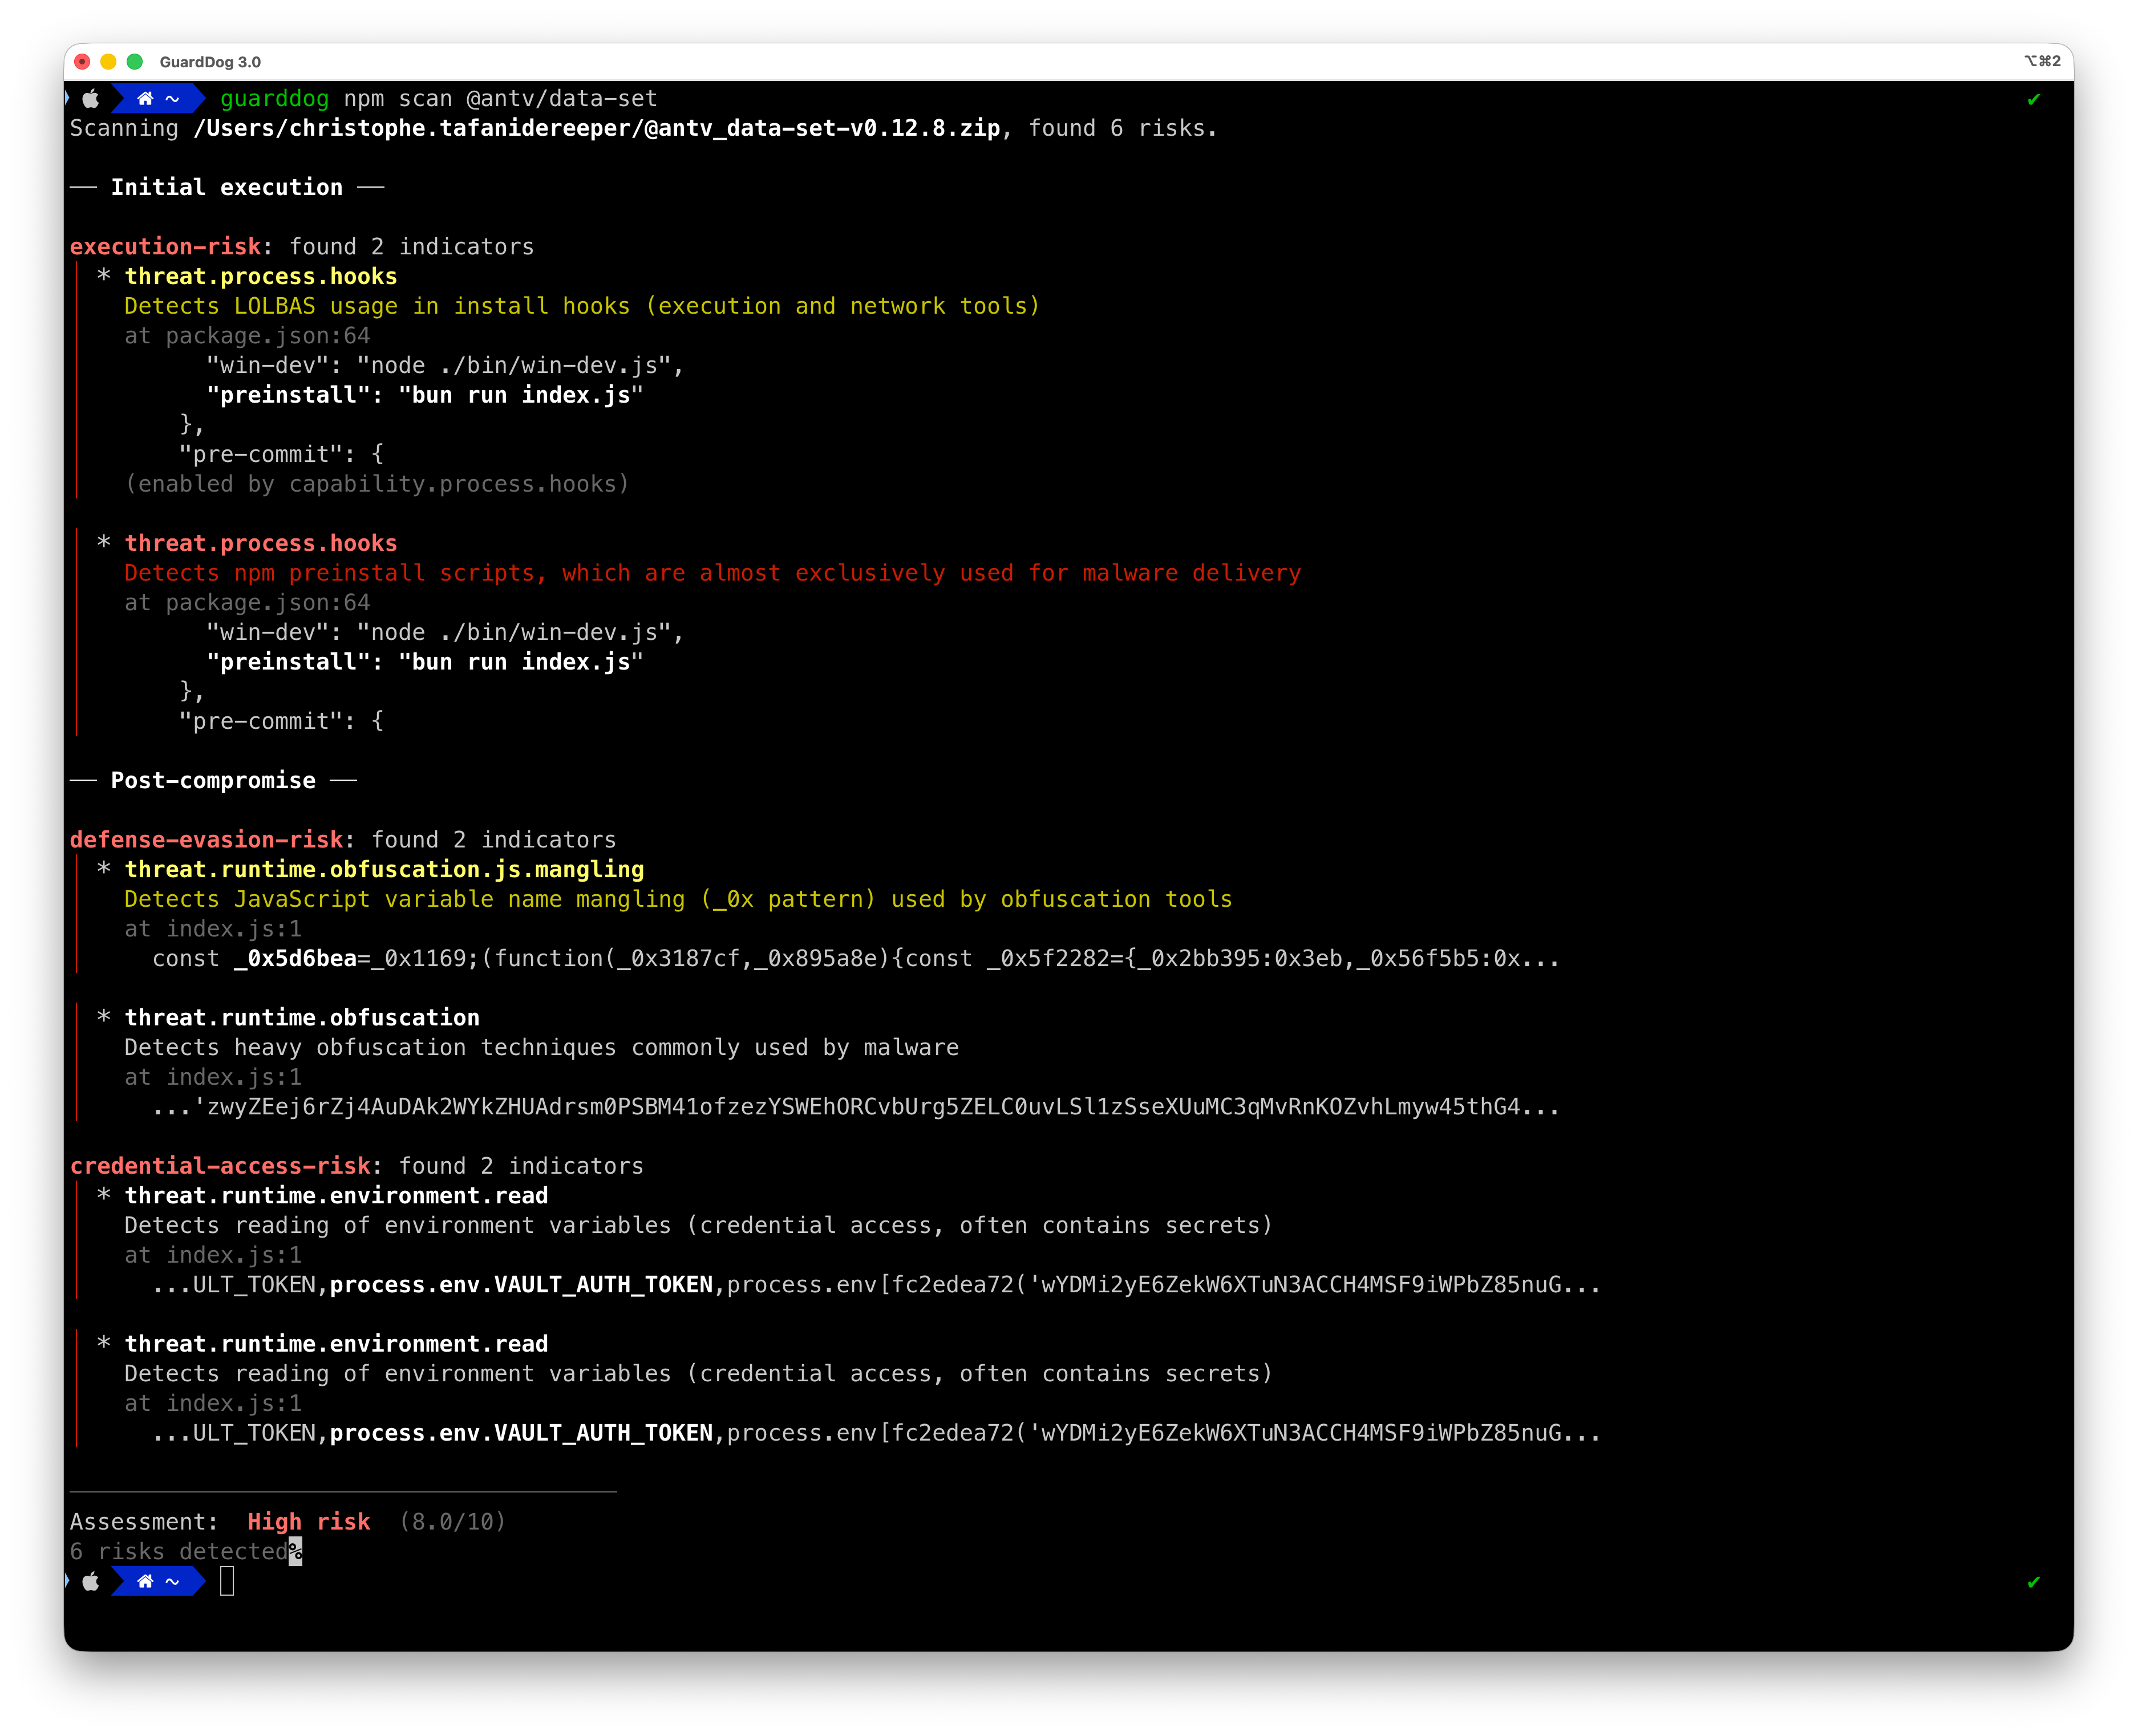 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
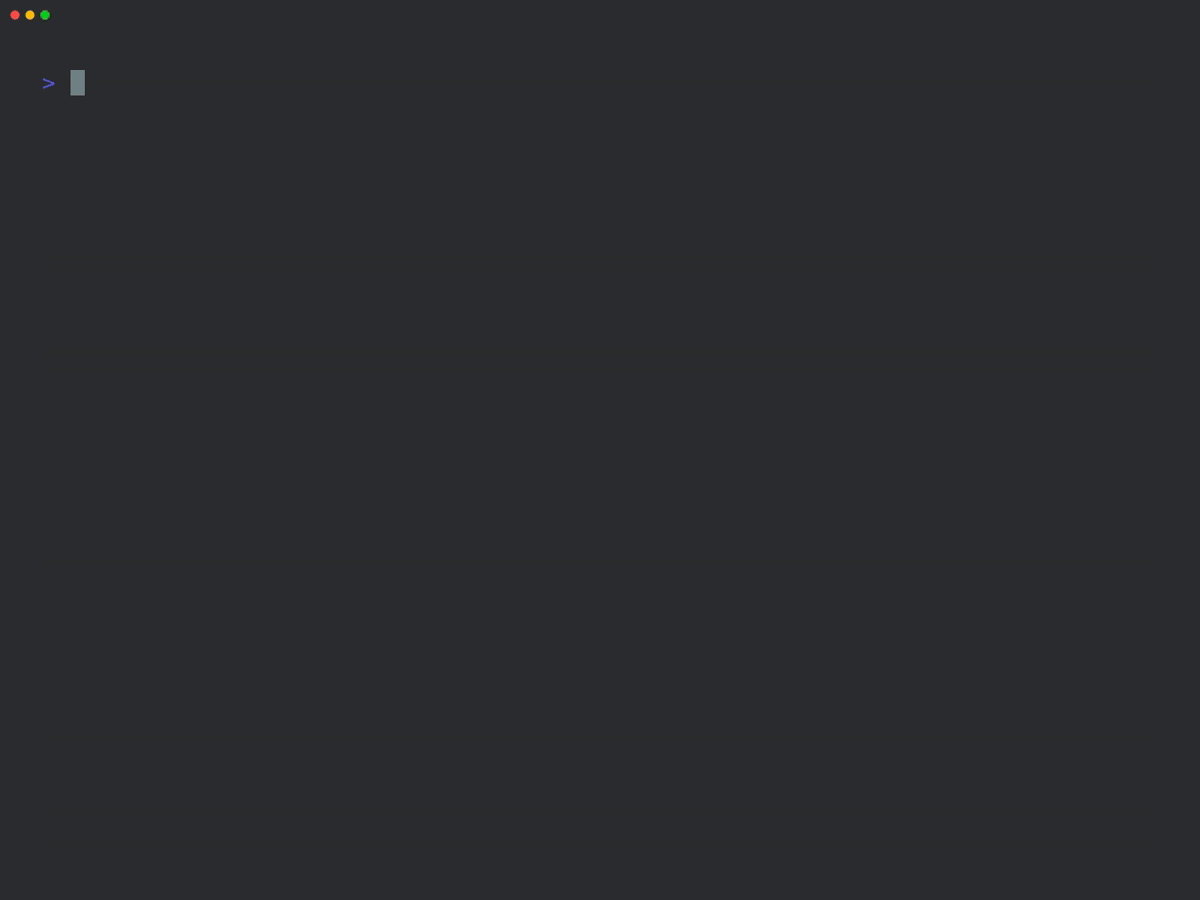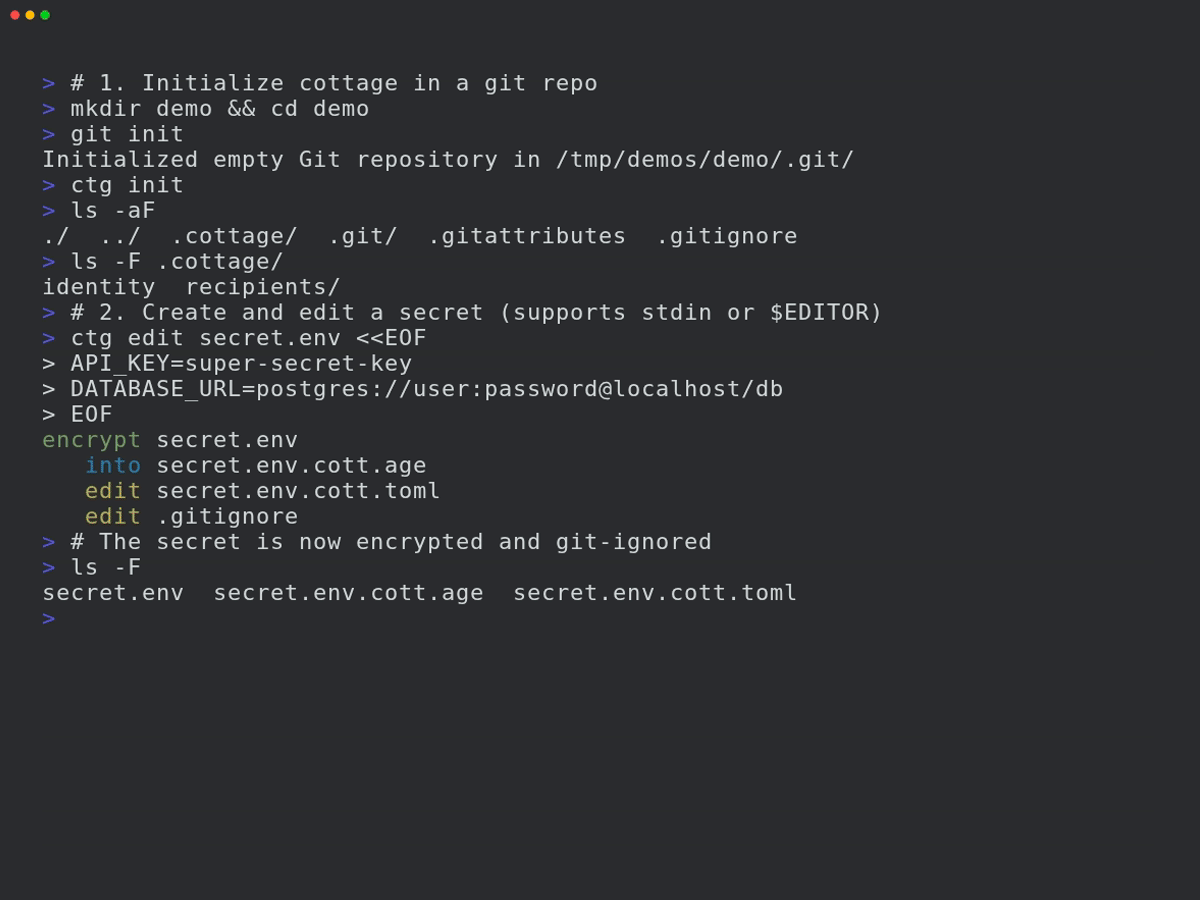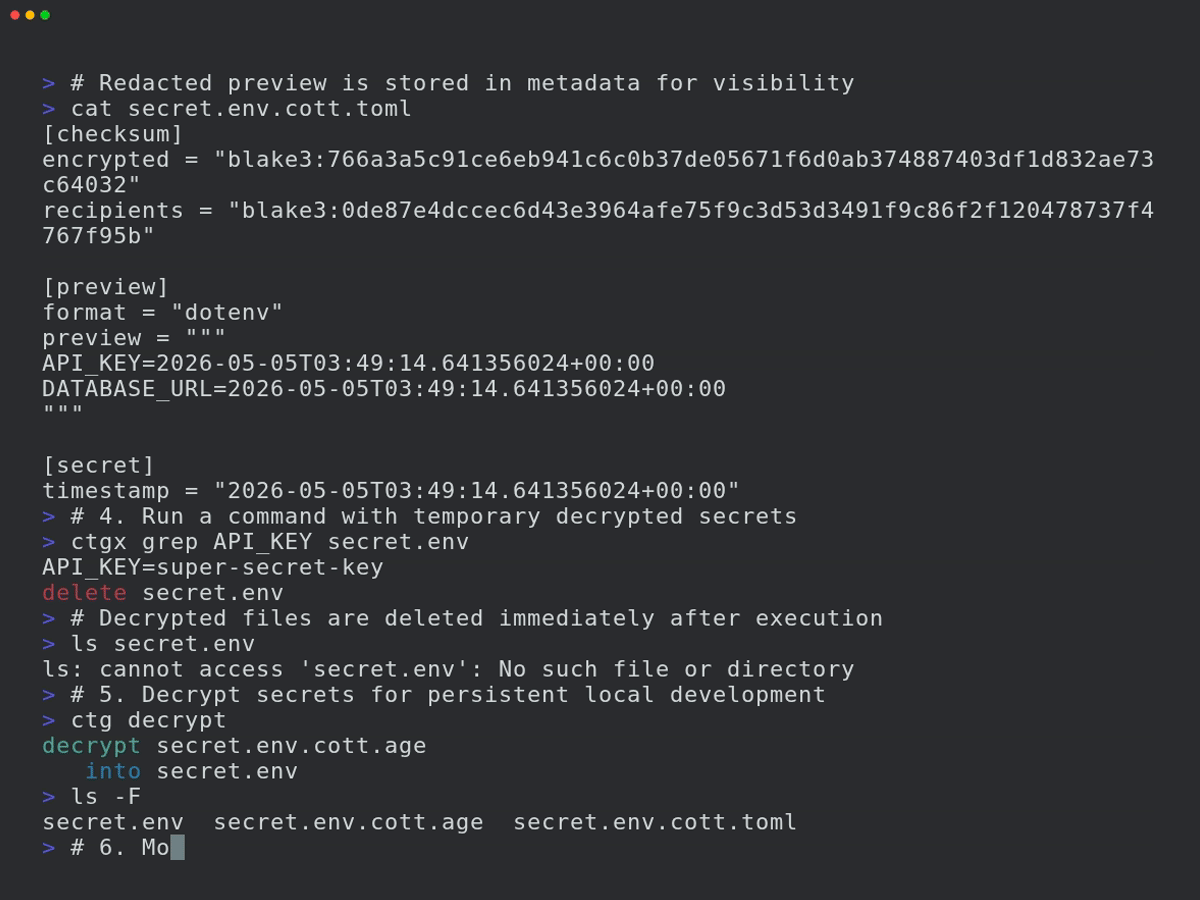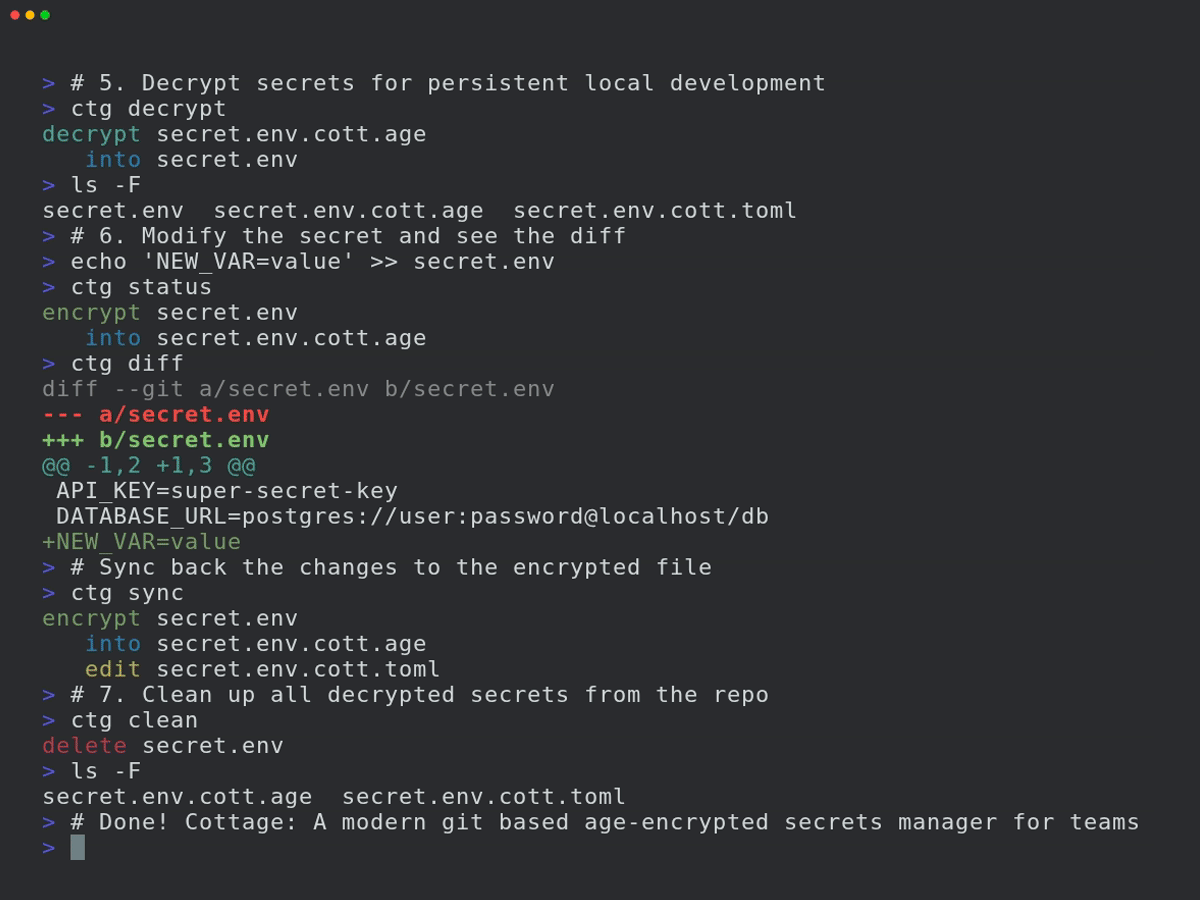 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
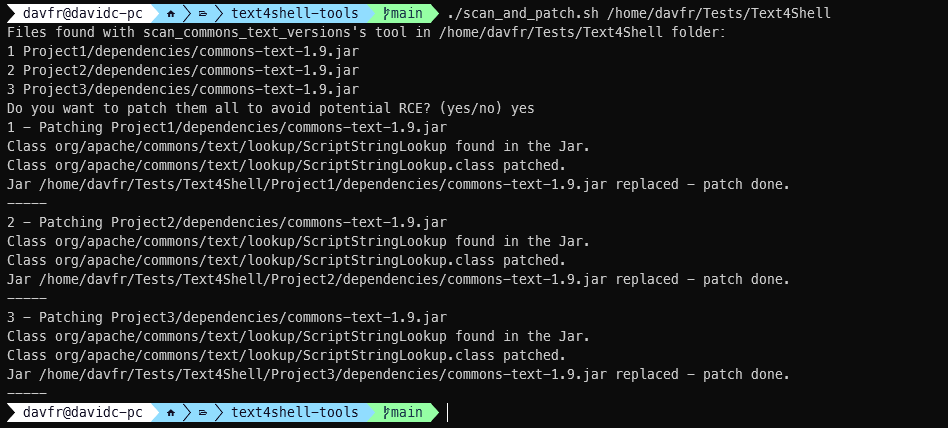 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
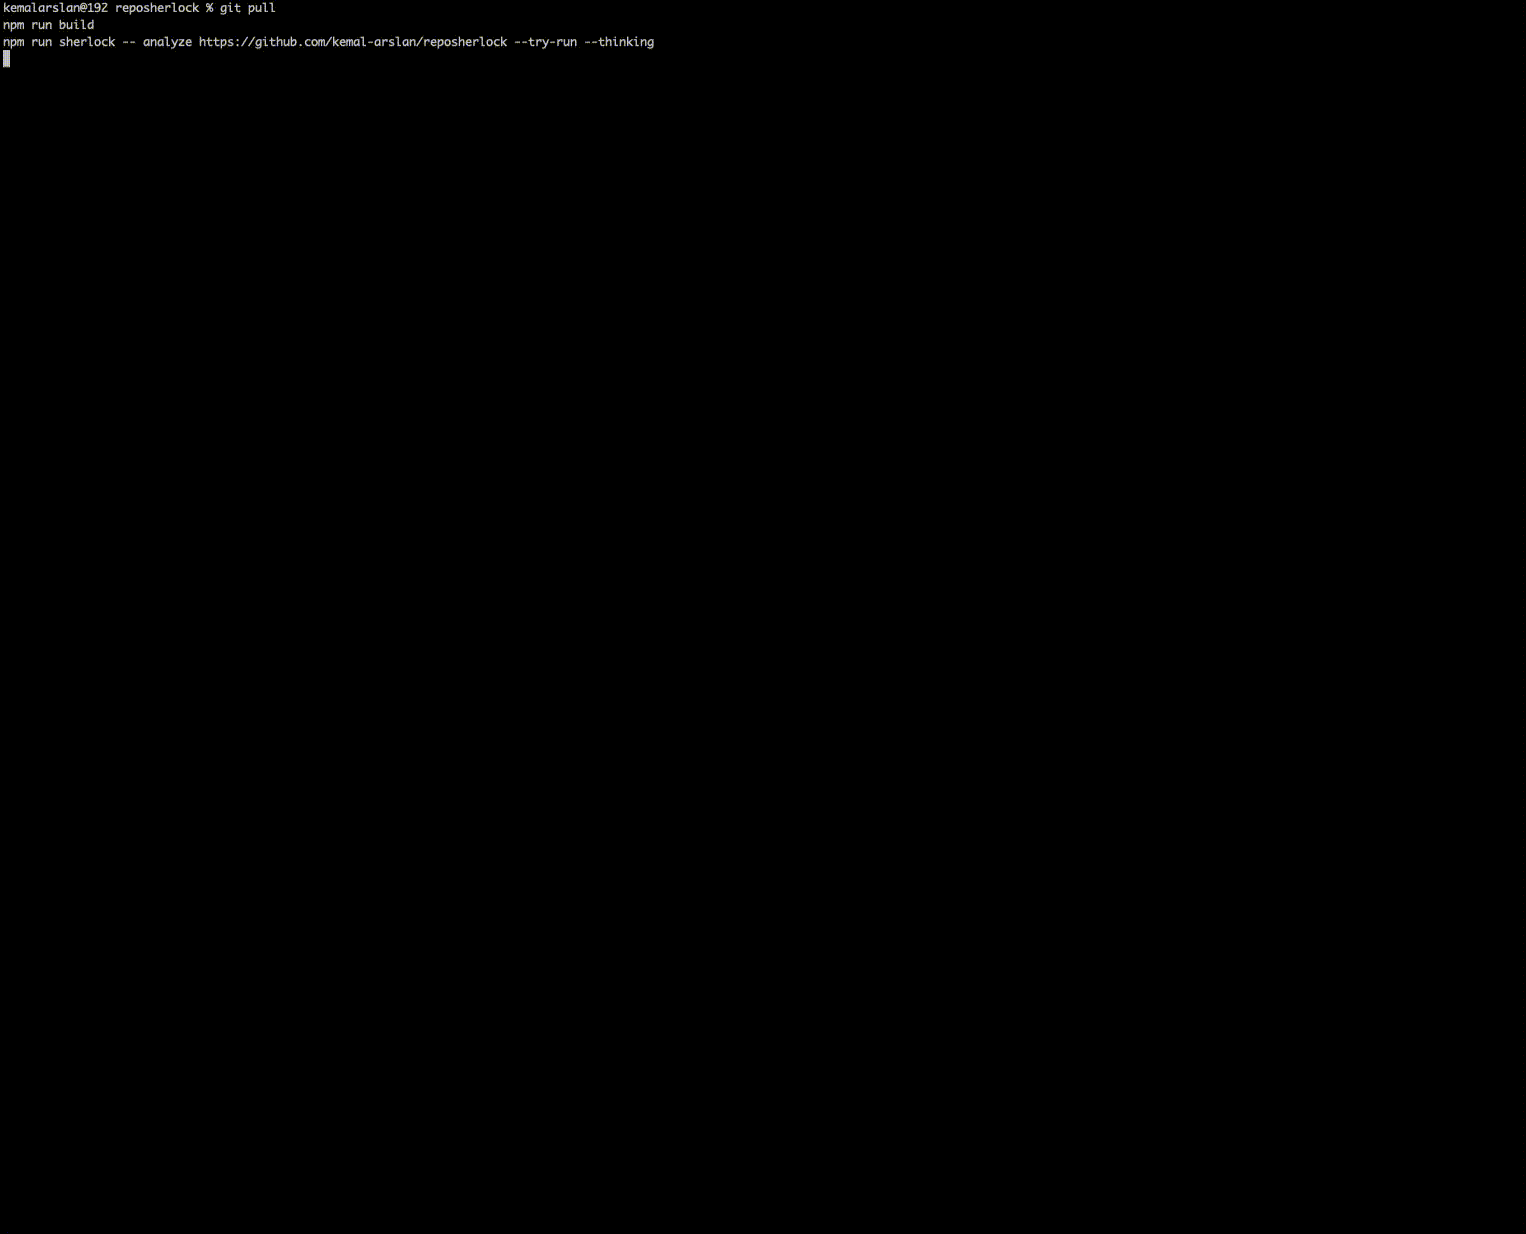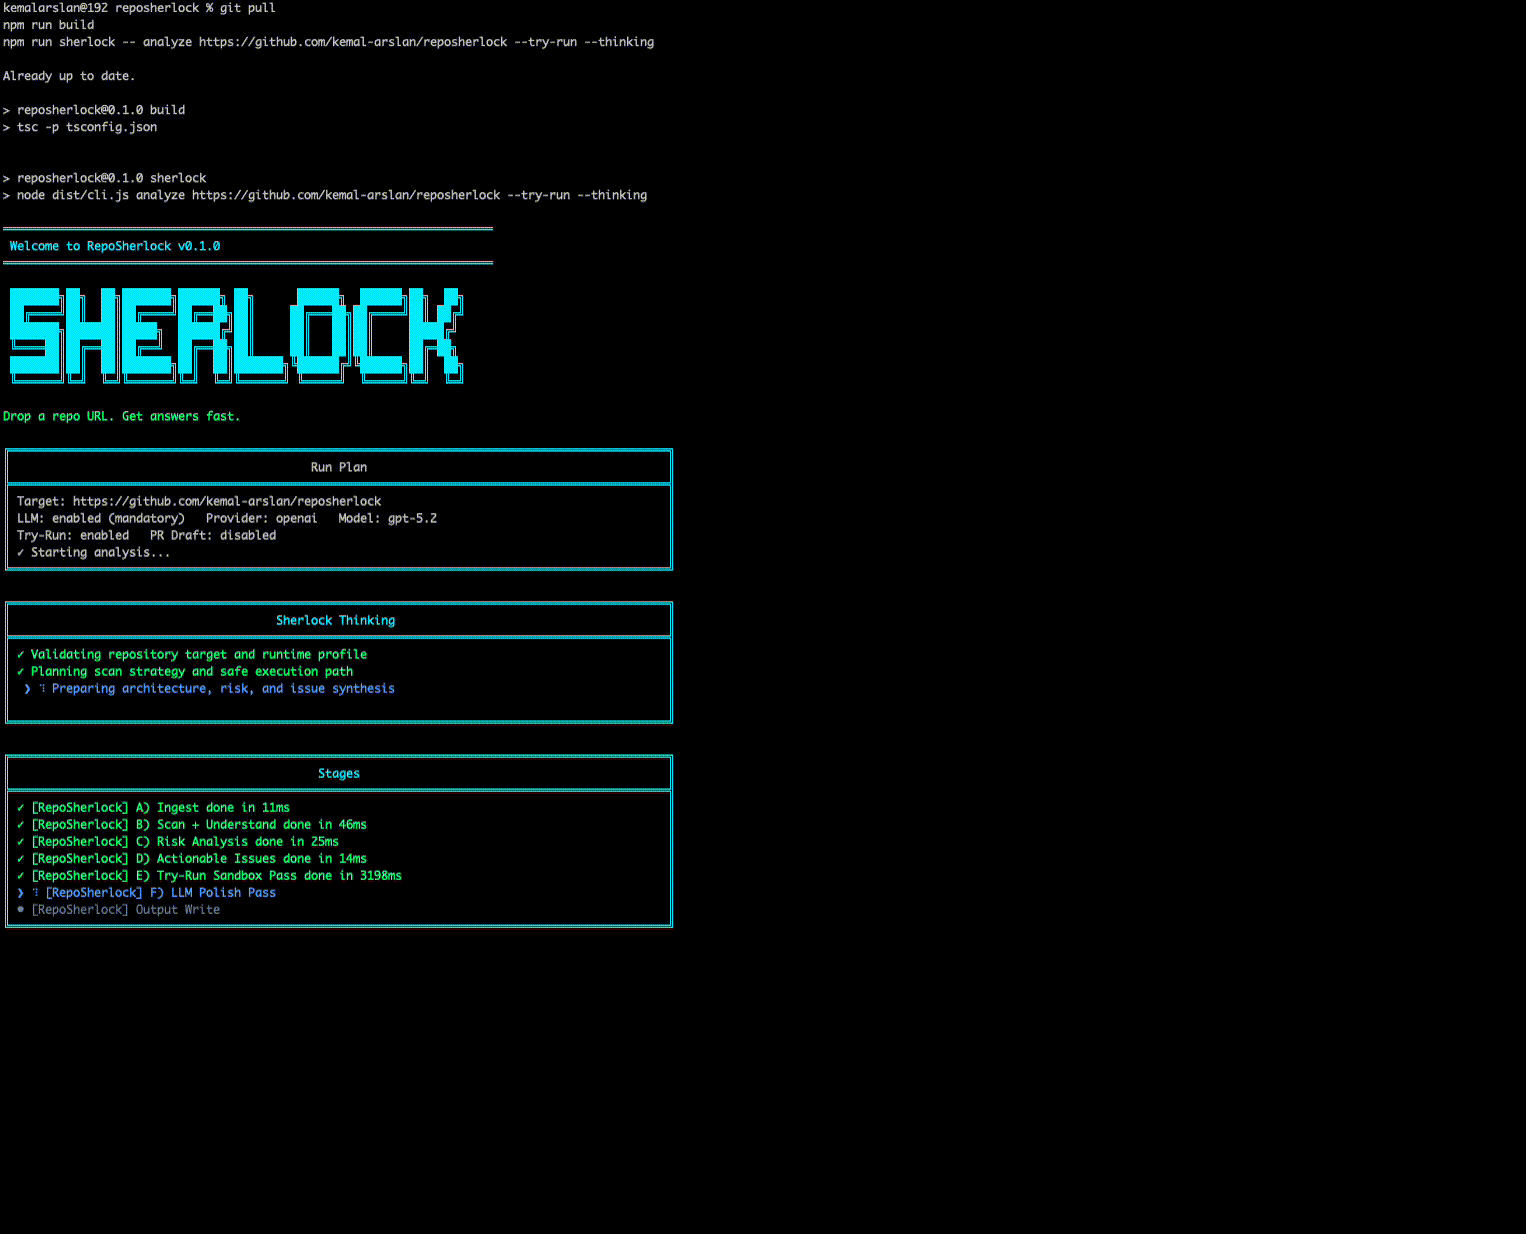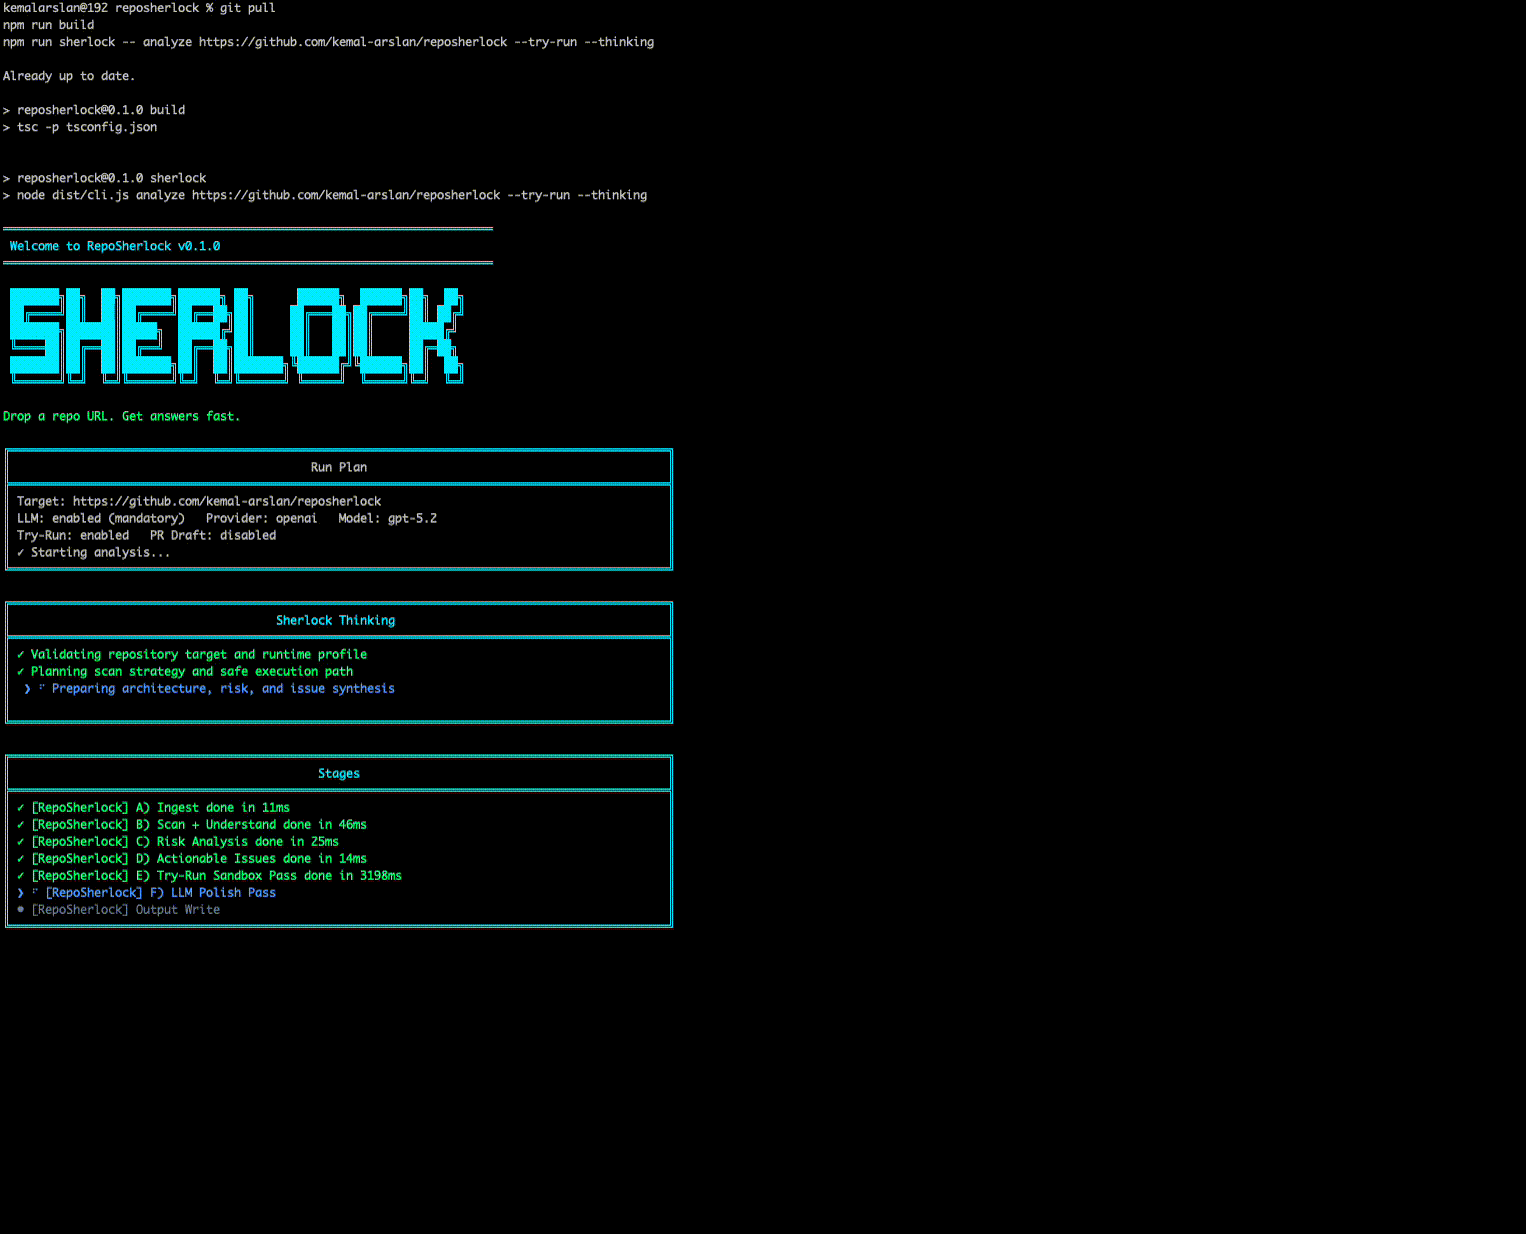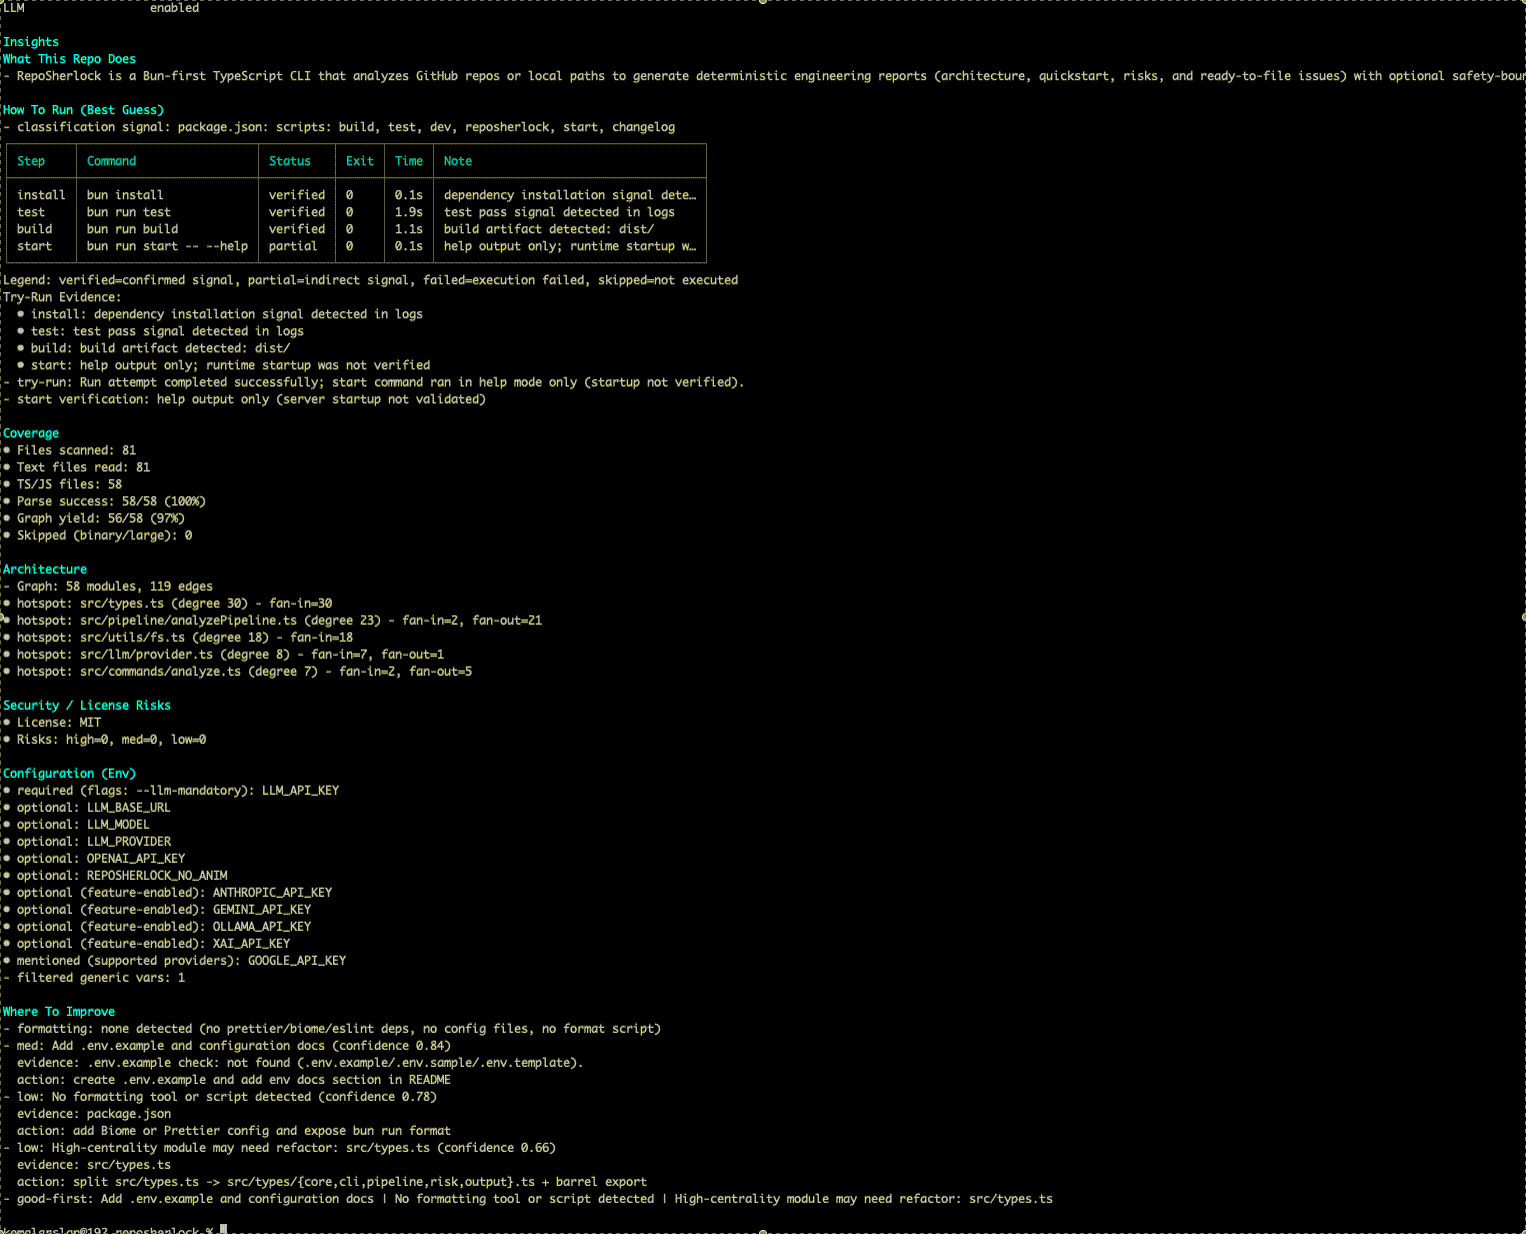 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 bx33661/cve-2026-30039
Security advisory and bilingual write-up detailing CVE-2026-30039, a symlink traversal vulnerability in rarfile affecting versions up to 4.2, leading…
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
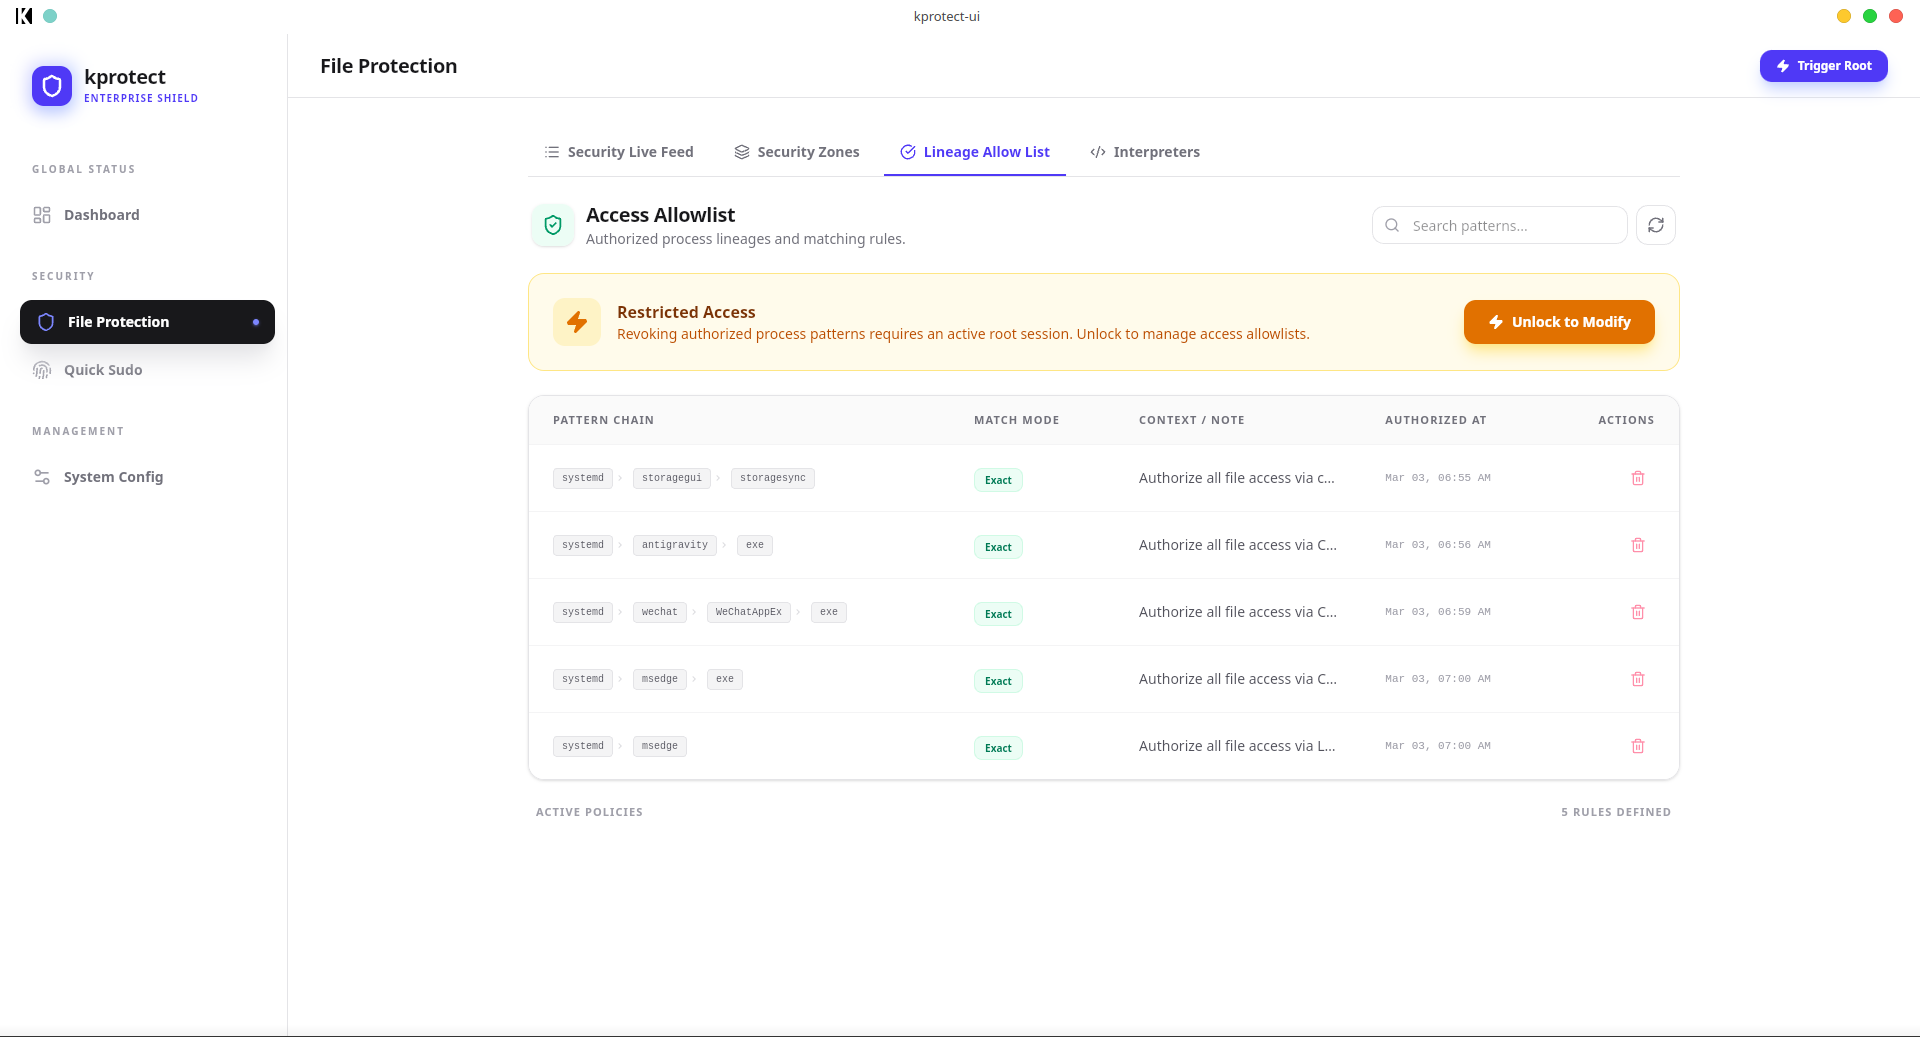 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…