chomtesh
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
dns-subdomain-enumerationinformation-gatheringosint+7
134
mr-rizwan-syed/chomteshCHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 whitelisthackers/wosind
An OSINT tool for collecting public information.
 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
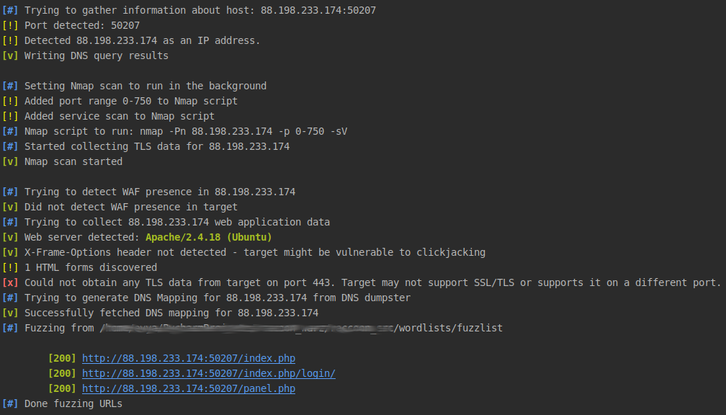 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning

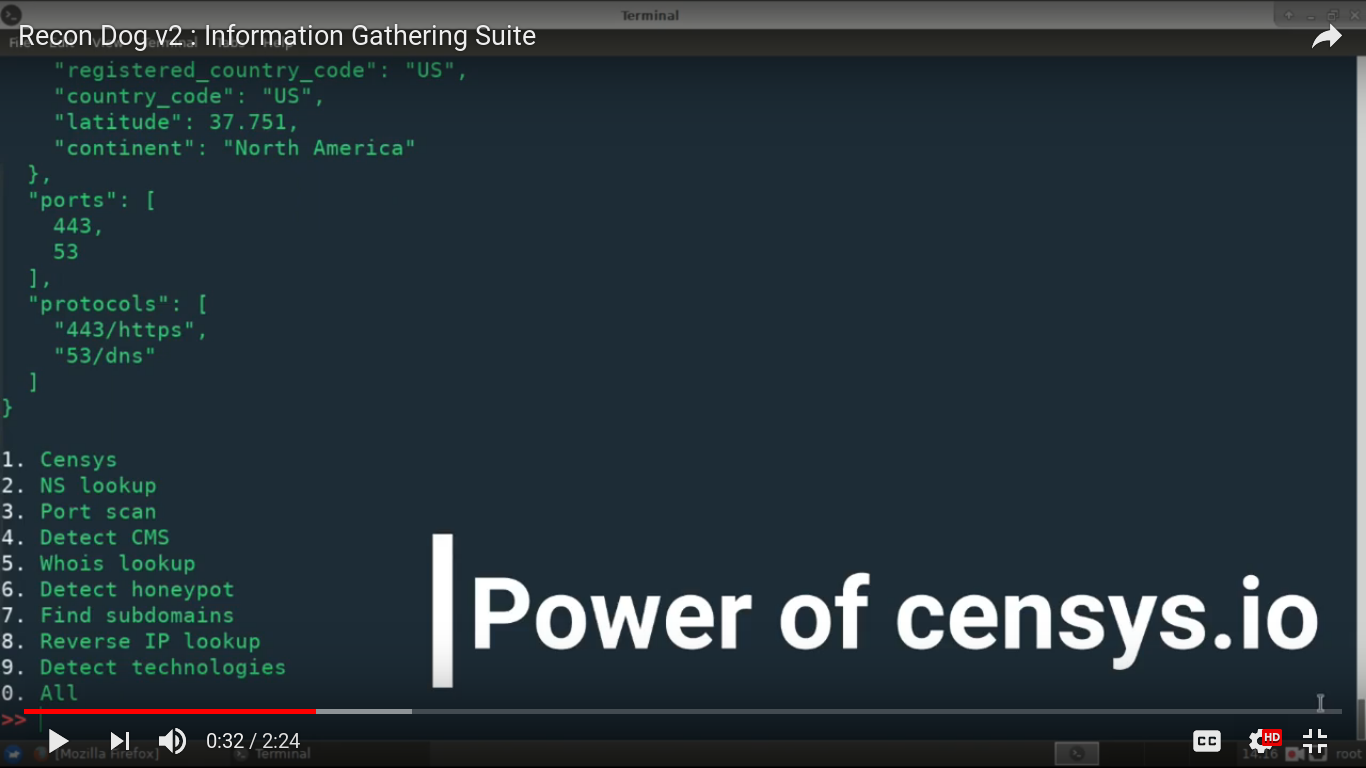
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
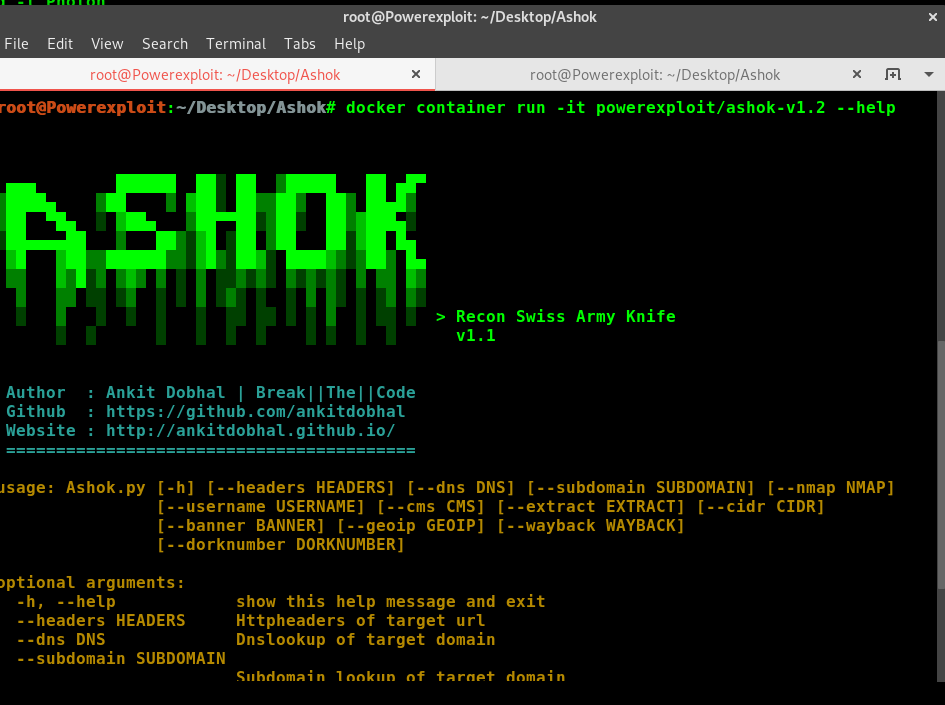 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
 paulsec/api-dnsdumpster.com
Python client for dnsdumpster.com to retrieve DNS records, subdomains, and network maps for reconnaissance and security research.
 shivamrai2003/reconky-automated_bash_script
Reconky is an great Content Discovery bash script for bug bounty hunters which automate lot of task and organized in the well mannered form which…
 dariusztytko/vhosts-sieve
Searching for virtual hosts among non-resolvable domains
 esecuritylab/kostebek
Automated reconnaissance tool that discovers organization domains by querying trademark databases via Google, Bing, Yahoo, and trademark registries.

 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
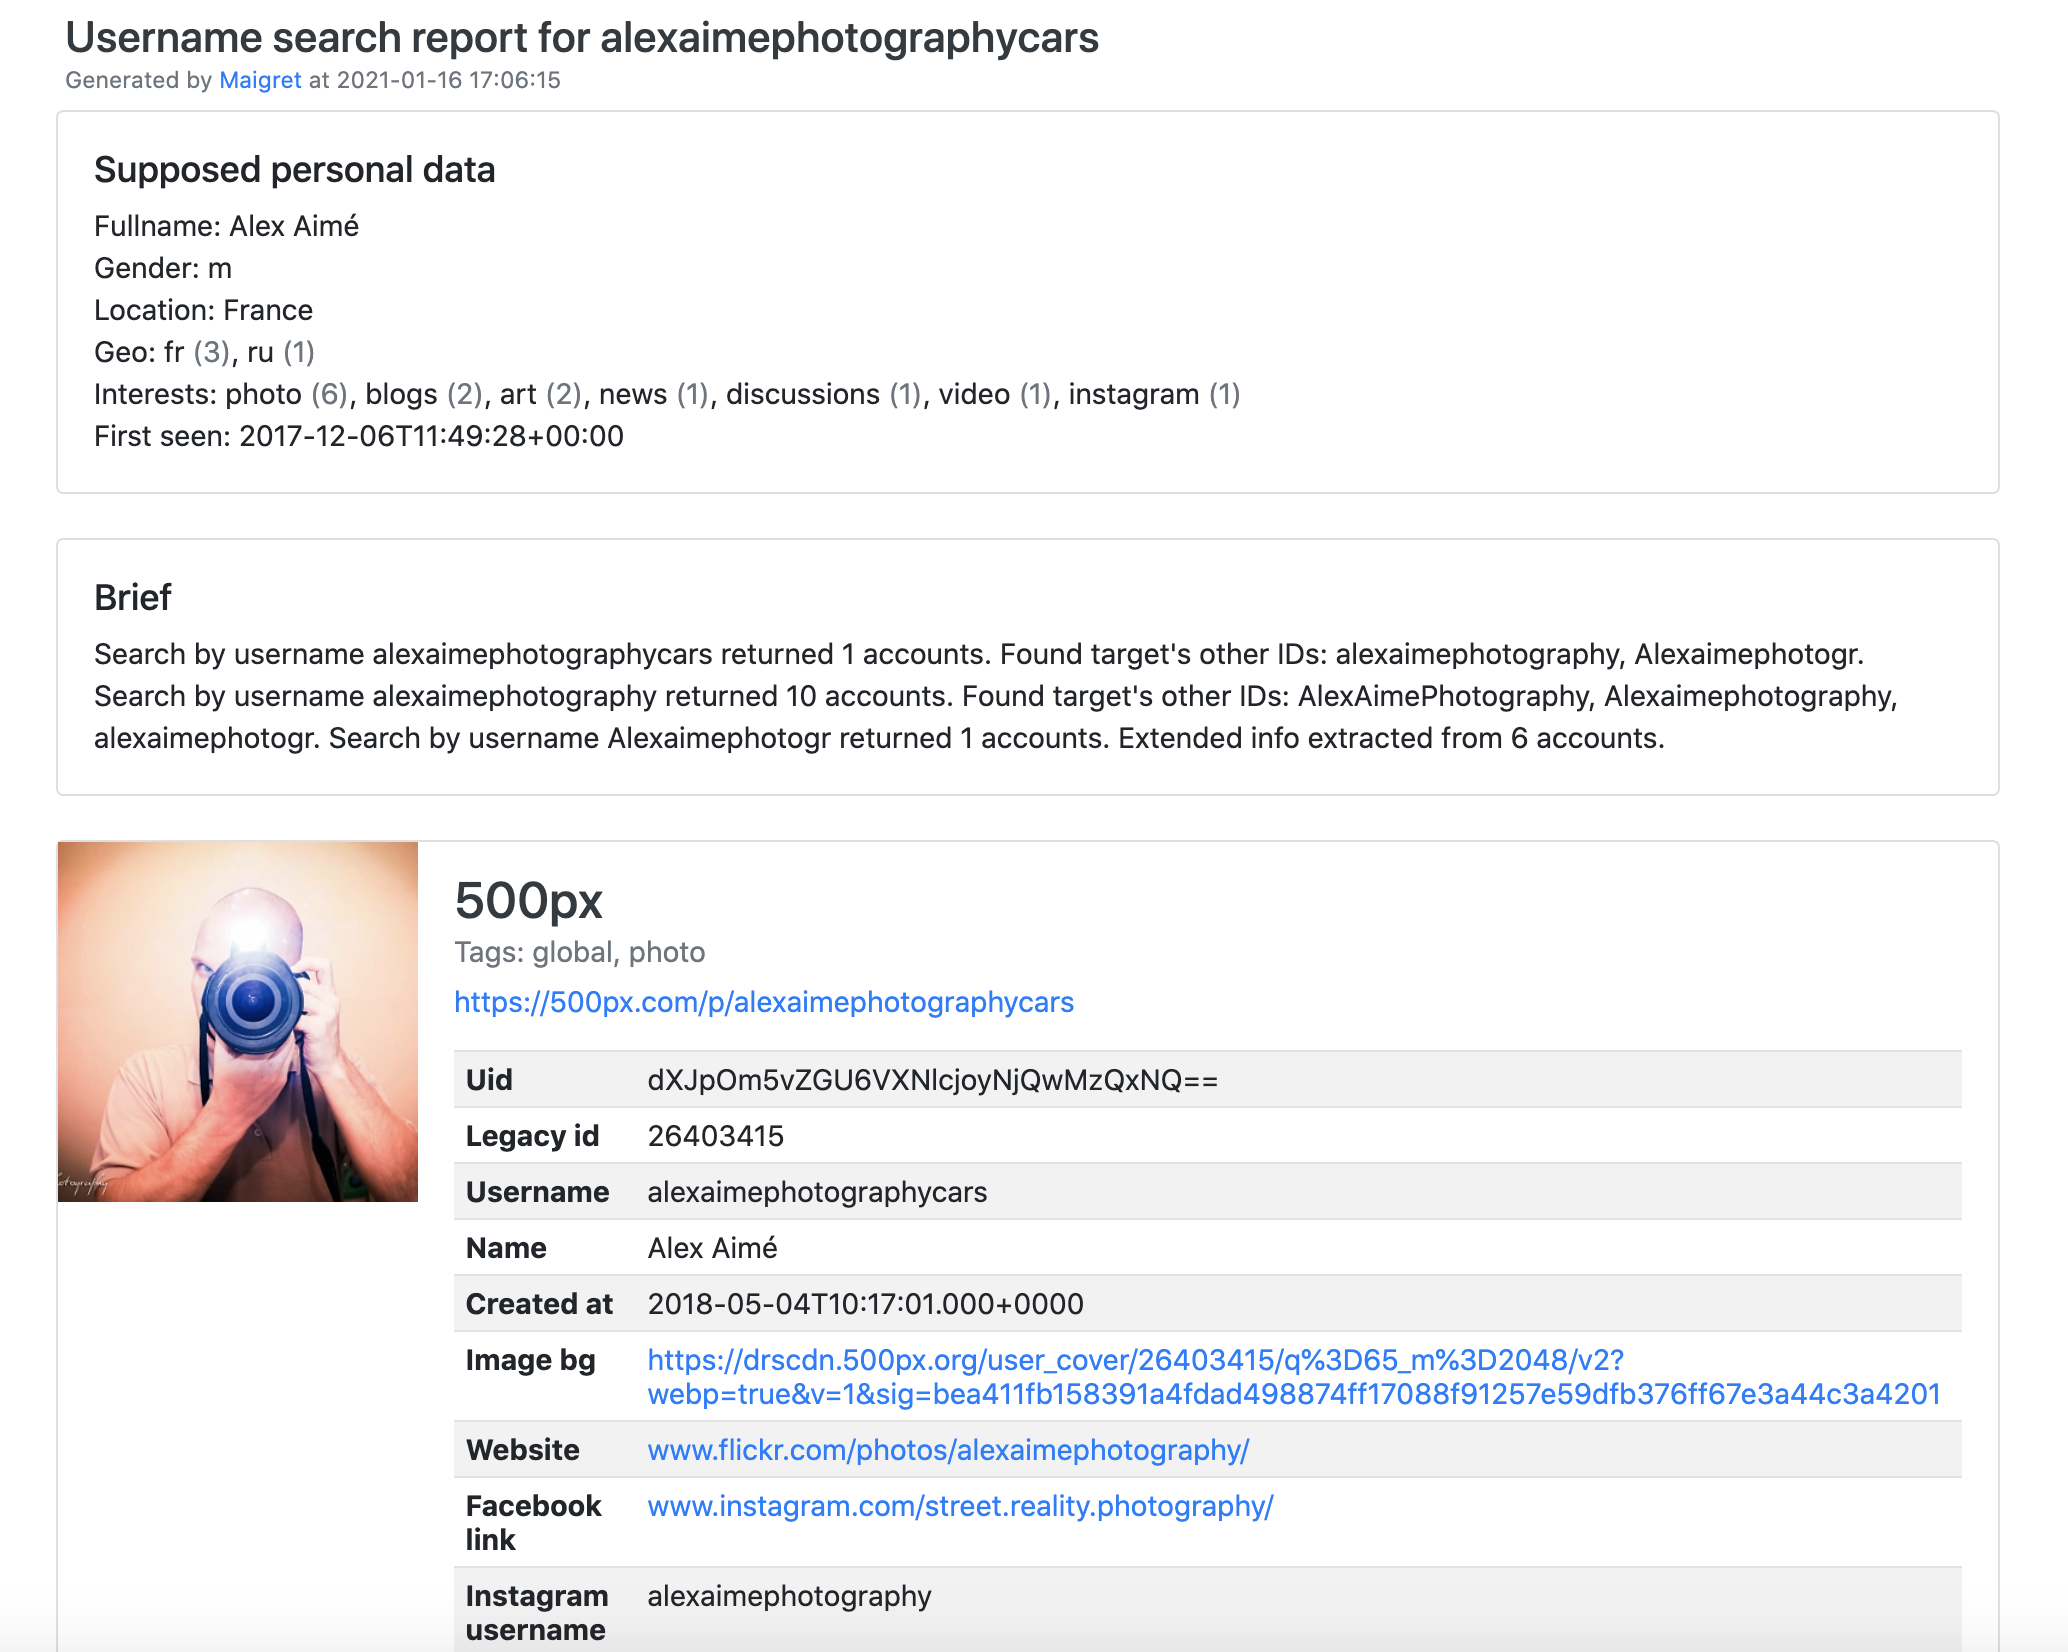 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites