
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
ReconDog — Reconnaissance Swiss Army Knife | Kitploit
Tools/GitHubGitHub/s0md3v/recondog
OSINT (Open Source Intelligence)ReconnaissancePort ScanningInformation GatheringSubdomain EnumerationDNS Analysis
GitHubs0md3v/recondog

ReconDog

Reconnaissance Swiss Army Knife

View Repository
2.1k359857 years agoReviewed by Kitploit
Share


Photon
ReconDog

Reconnaissance Swiss Army Knife

Main Features

  • Wizard + CLA interface
  • Can extracts targets from STDIN (piped input) and act upon them
  • All the information is extracted with APIs, no direct contact is made to the target

Utilities

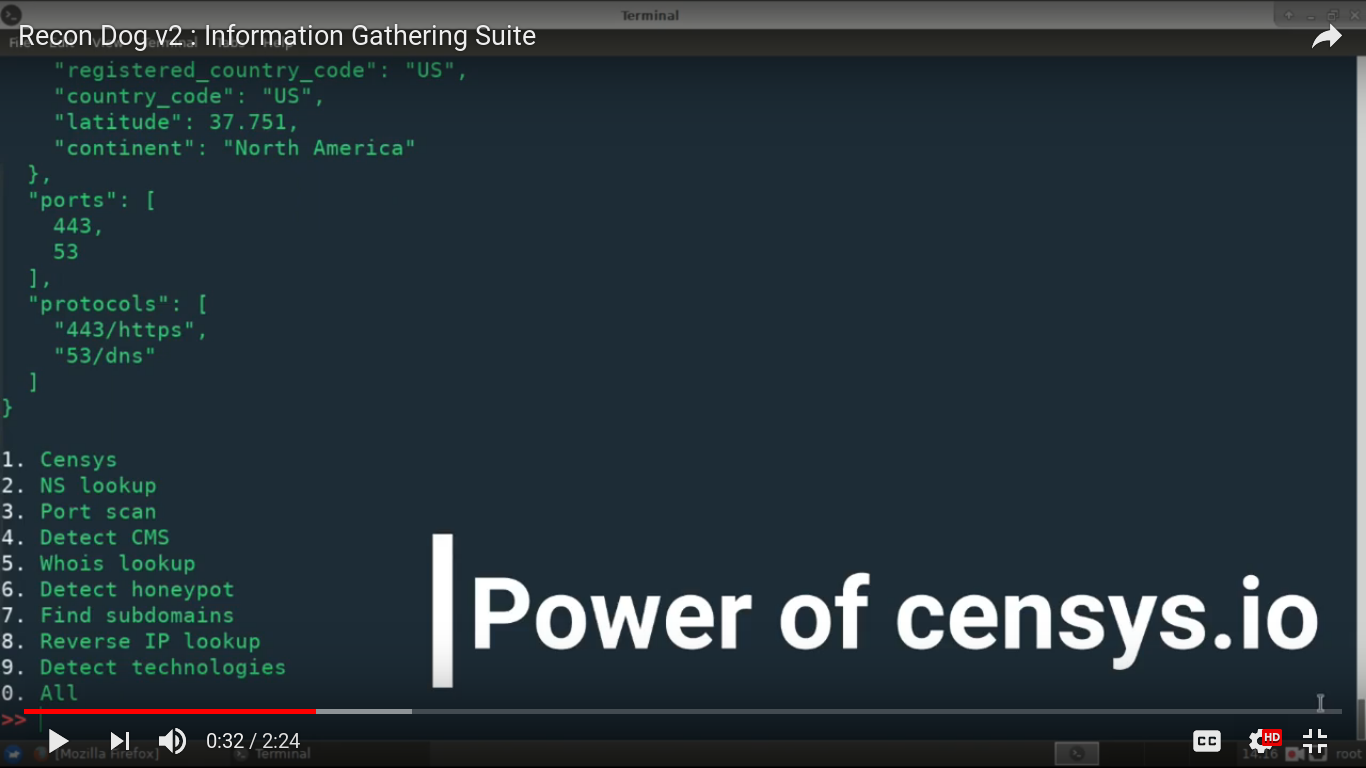
  • Censys: Uses censys.io to gather massive amount of information about an IP address.
  • NS Lookup: Does name server lookup
  • Port Scan: Scan most common TCP ports
  • Detect CMS: Can detect 400+ content management systems
  • Whois lookup: Performs a whois lookup
  • Detect honeypot: Uses shodan.io to check if target is a honeypot
  • Find subdomains: Uses findsubdomains.com to find subdomains
  • Reverse IP lookup: Does a reverse IP lookup to find domains associated with an IP address
  • Detect technologies: Uses wappalyzer.com to detect 1000+ technologies
  • All: Runs all utilities against the target

Demo

demo

Compatibility

Recon Dog will run on anything that has a python interpreter installed. However, it has been tested on the following configurations:

Operating Systems: Windows, Linux, Mac
Python Versions: Python2.7, Python 3.6

Installation

Recon Dog requires no manual configuration and can be simply run as a normal python script.
However, a debian package can be downloaded from here if you want to install it.

Usage

Wizard Interface

Wizard interface is the most straightforward way you can use Recon Dog in. Just run the program, select what you want to do and enter the target, it's that simple.

CLA Interface

Recon Dog also has a Command Line Argument inteface. Here's how you can find subdomains:

python dog -t marvel.com -c 7

There's more to it! Do you have a program that can enumerate subdomains and you want to scan ports of all the subdomains it finds? Don't worry, Recon Dog is designed for handling with such cases. You can simply do this:

subdomainfinder -t example.com | python dog --domains -c 3

If you just want to print the targets, don't use the -c option.
Also, it doesn't matter what kind of output the other program generates, Recon Dog uses regular expressions to find targets which makes it easy to integrate will literally every tool. There are two switchs available:

--domains    extract domains from STDIN
--ips        extract ip addresses from STDIN

Contribution & License

You can contribute in following ways:

  • Report bugs
  • Develop plugins
  • Give suggestions to make it better
  • Fix issues & submit a pull request

Do you want to have a conversation in private? Hit me up on my twitter, inbox is open :)
Recon Dog is licensed under Apache 2.0 License.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →