
awesome-bugbounty-tools
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
curated-resourcesexploitationfuzzing+5
6.4k
vavkamil/awesome-bugbounty-toolsCurated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
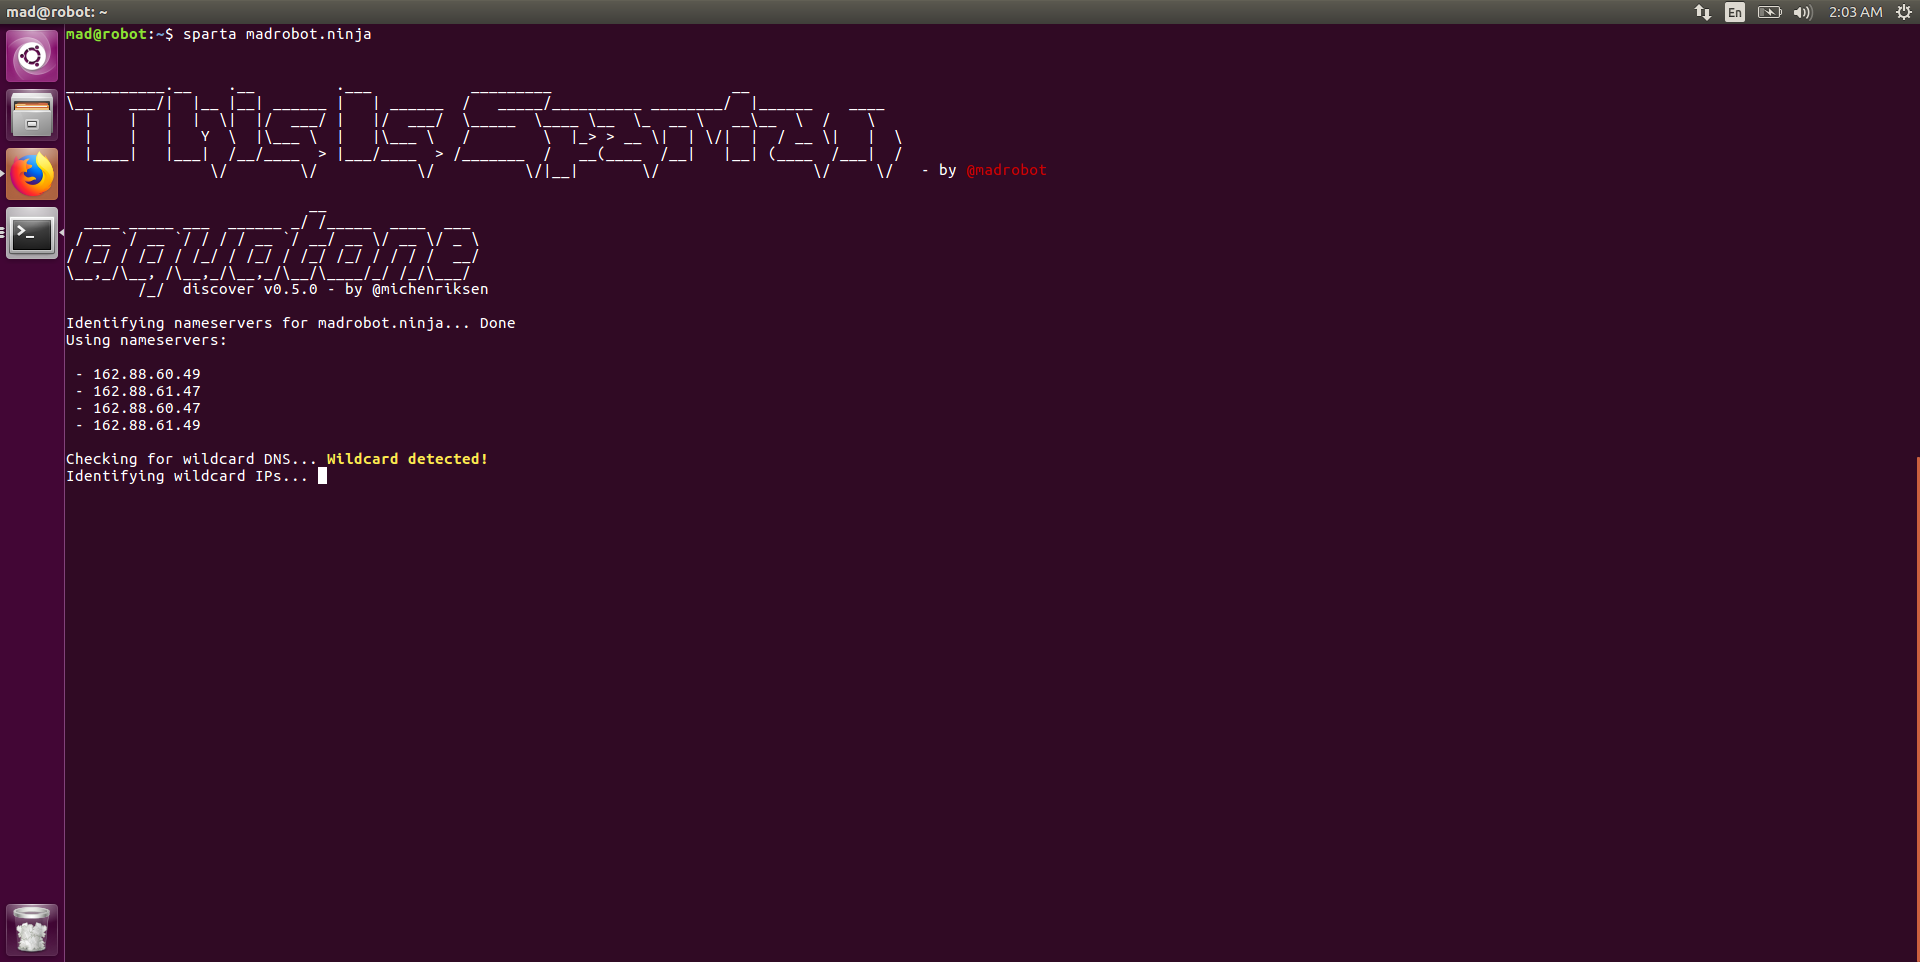 mad-robot/spartan
Automated reconnaissance framework integrating subdomain enumeration, live host probing, port scanning, CMS detection, and directory brute-forcing…
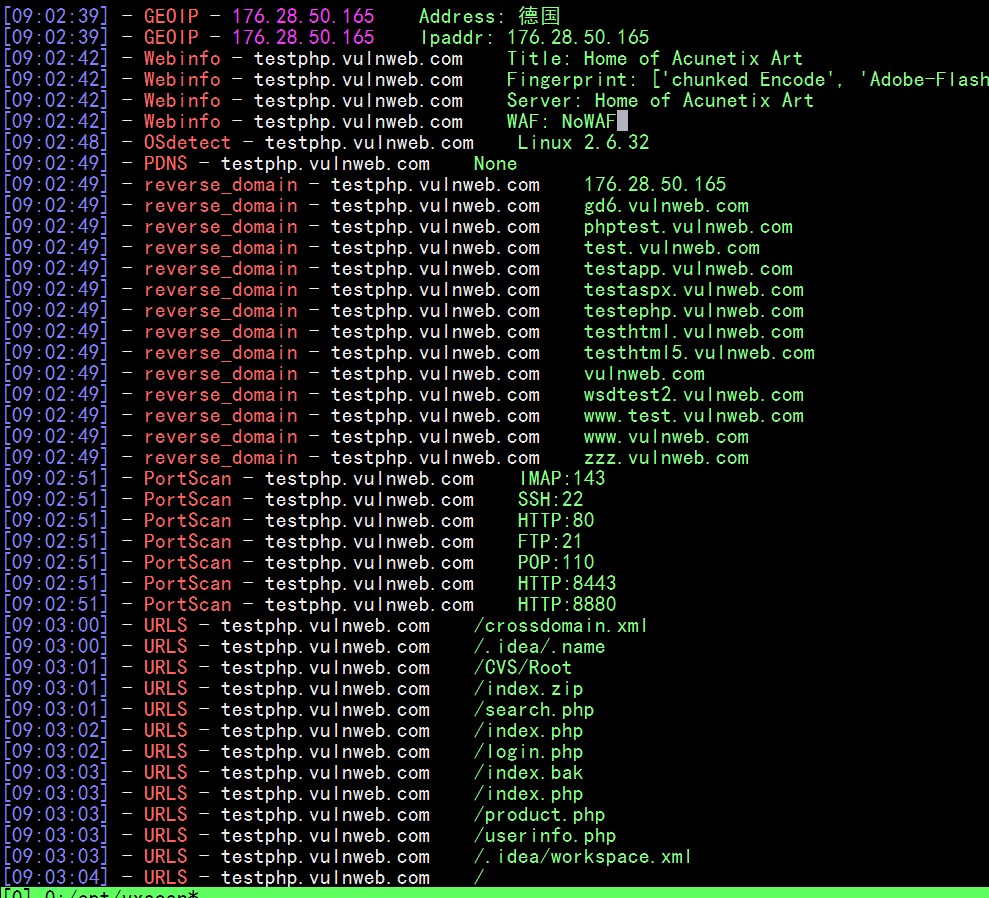 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via…
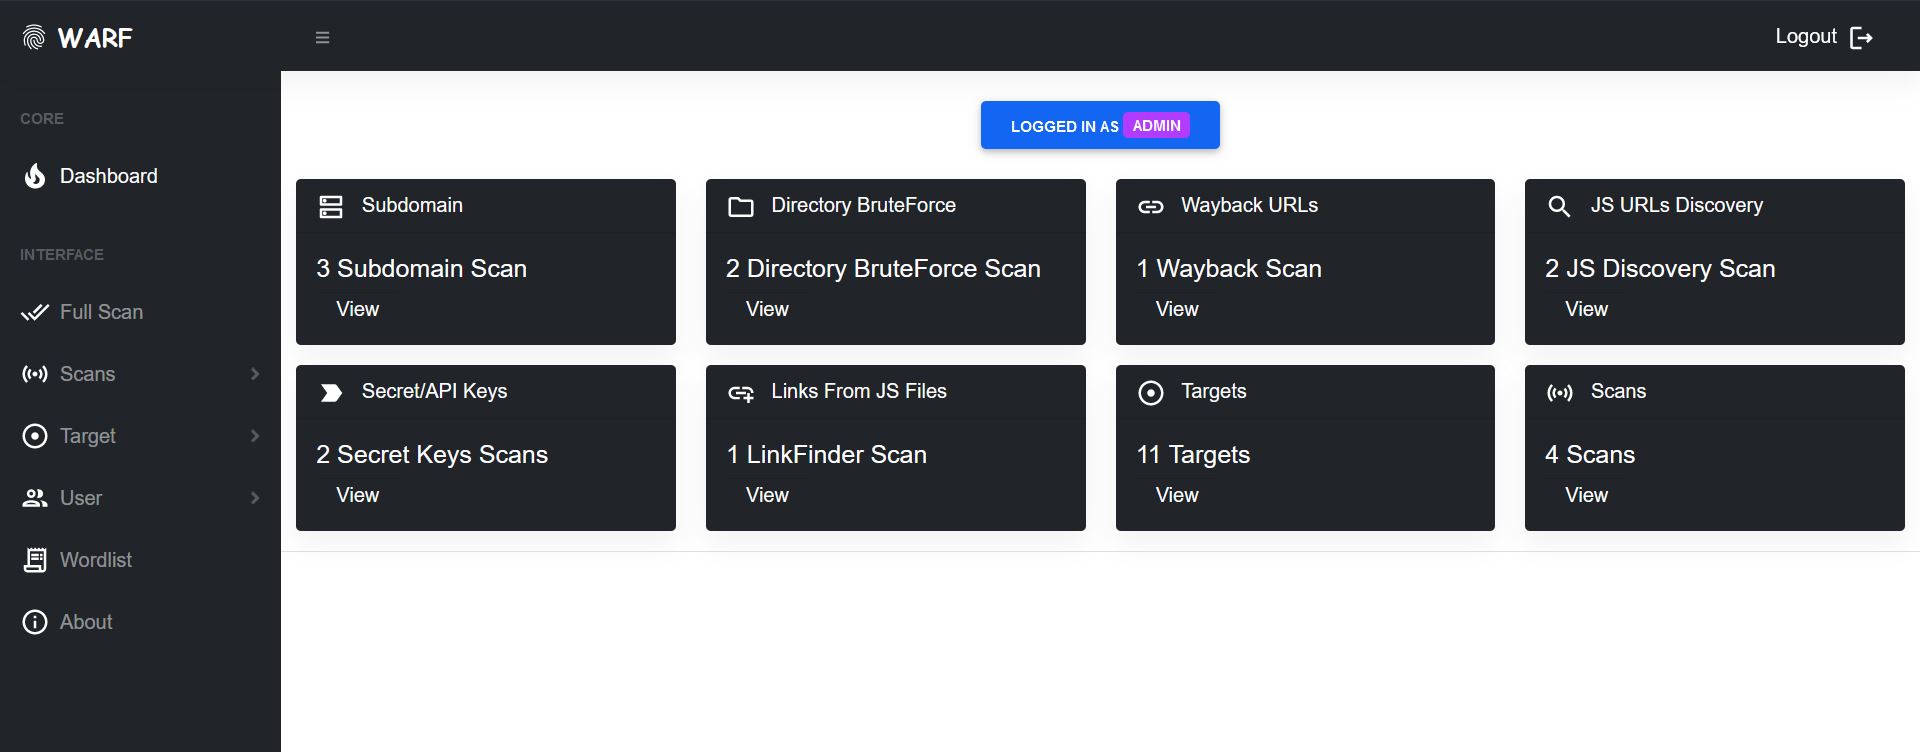 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
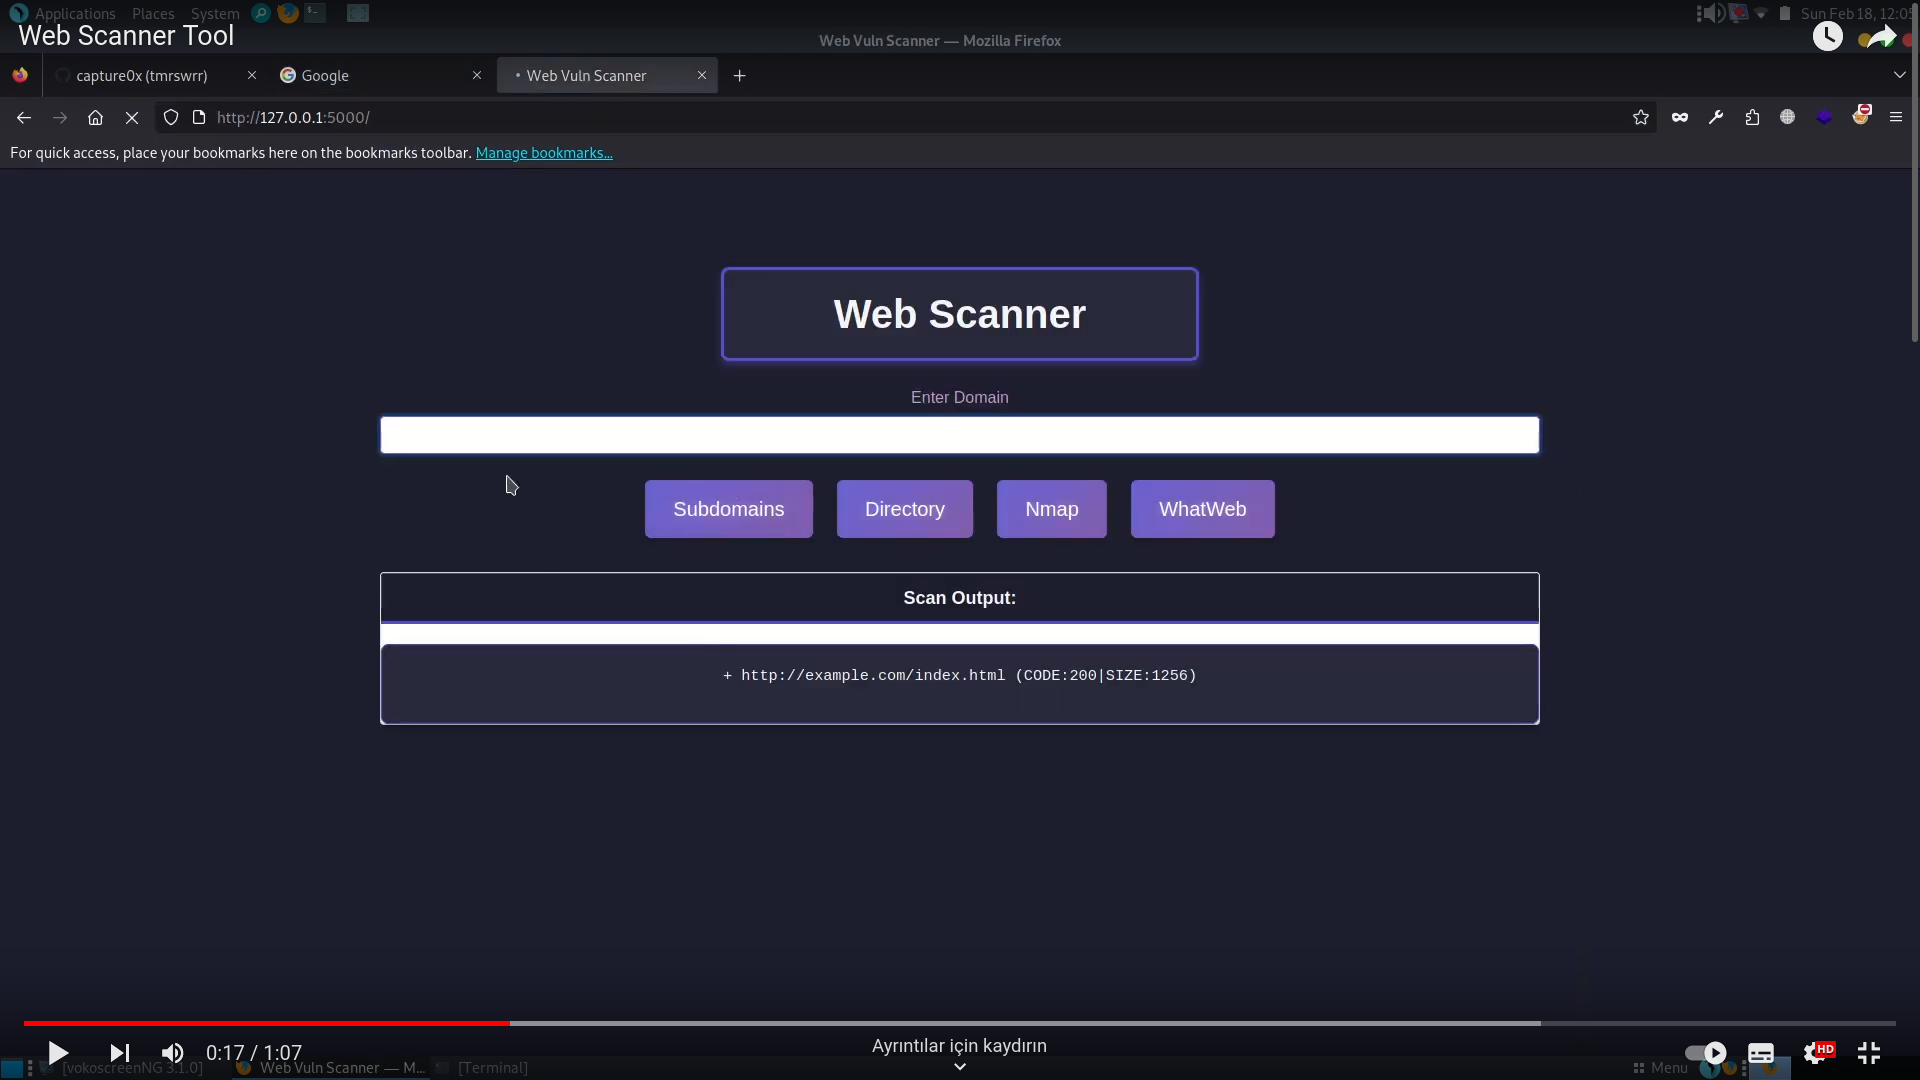 capture0x/web-scanner
Python-based web domain scanner integrating Sublist3r, Dirble, Nmap, and WhatWeb for subdomain discovery, directory enumeration, network scanning,…
 red-team-labs/waldo
Multithreaded Python tool for brute-forcing hidden directories and subdomains on target web servers to aid in reconnaissance and information…
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…