

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.9k7h 5m ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
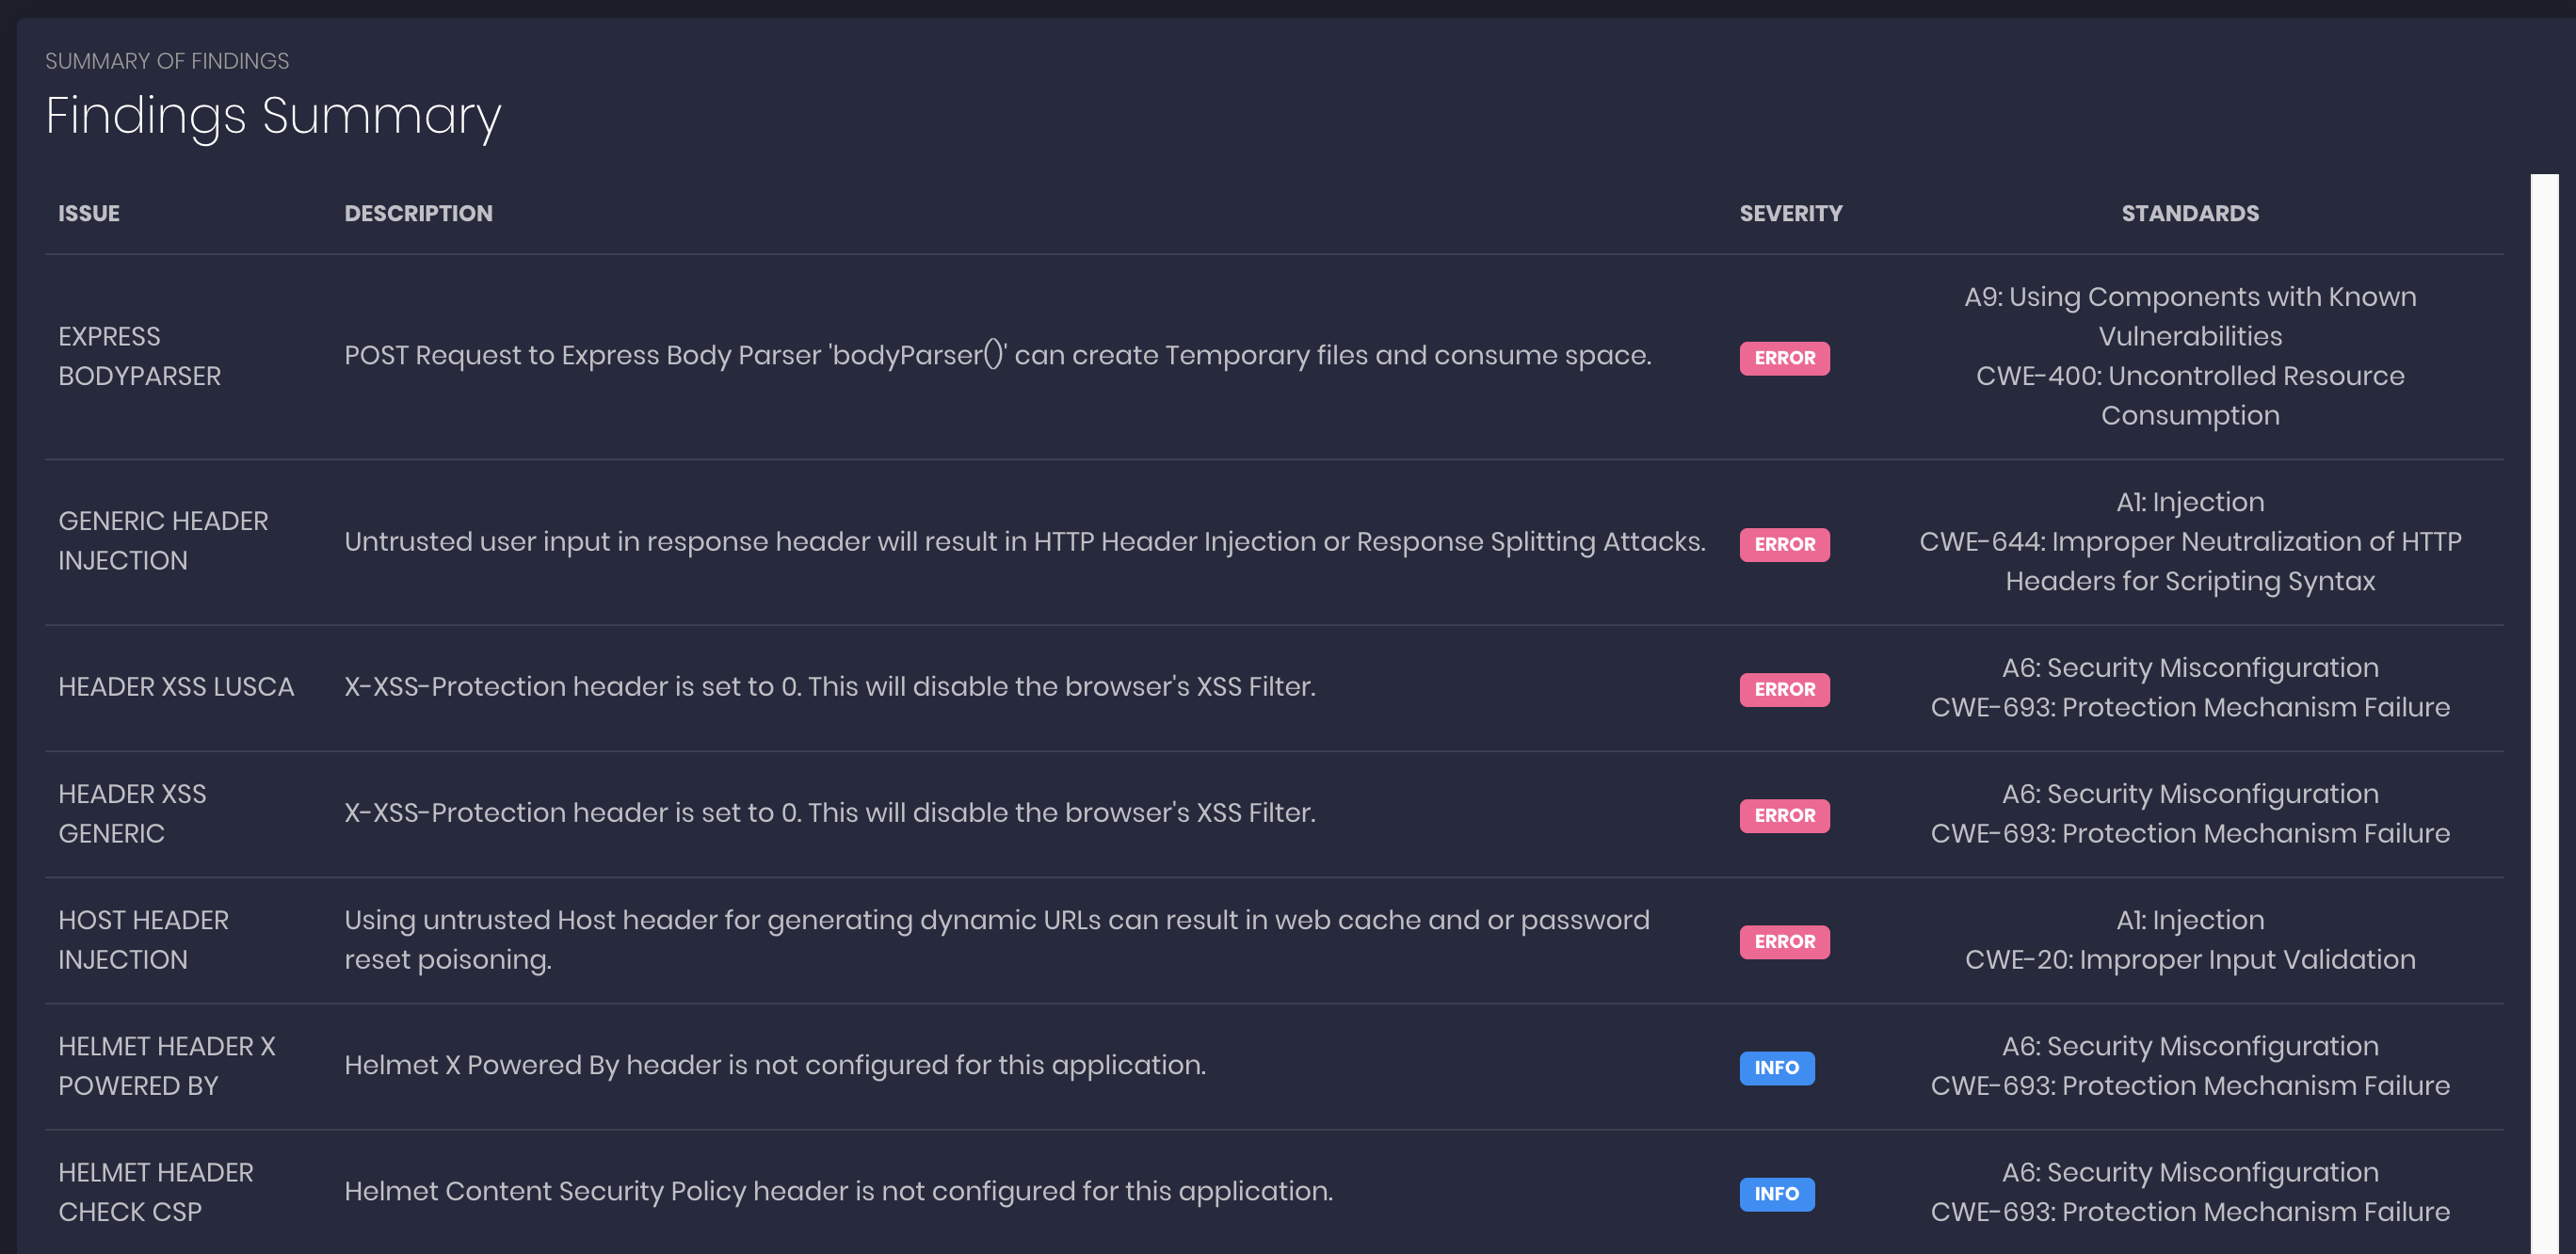 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 agrawalsmart7/scodescanner
Command-line static analysis scanner that detects critical vulnerabilities in PHP and YAML source code using custom semgrep rules, with Jira and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 niffyhunt/codeguard-copilot
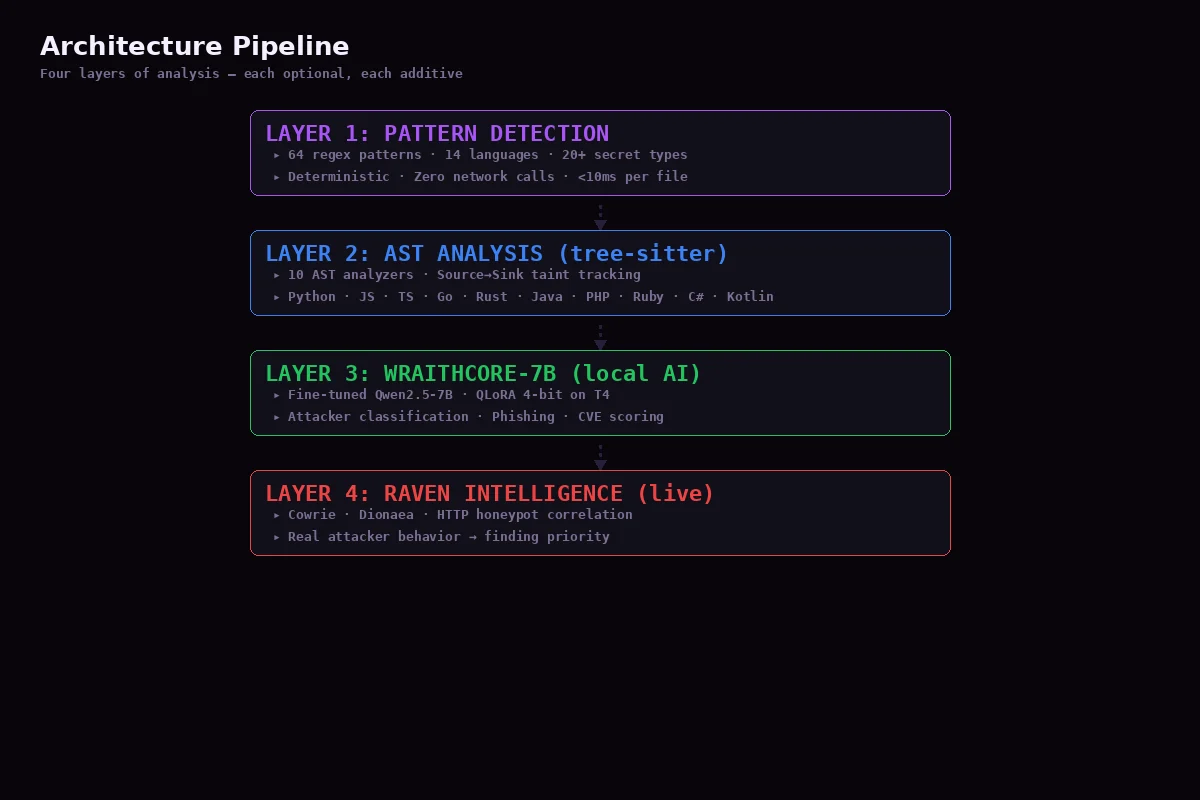
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…