Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
nodejsscan — nodejsscan is a static security code scanner for Node.js applications. | Kitploit
Tools/GitHubGitHub/ajinabraham/nodejsscan
Static AnalysisVulnerability ScannersStatic Code Analysis (SAST)Code AnalysisWeb SecurityDevSecOpsTop in Code Analysis #14Top in Static Code Analysis (SAST) #11
GitHub
2.6k343691 month agoReviewed by Kitploit
ajinabraham/nodejsscan

nodejsscan

nodejsscan is a static security code scanner for Node.js applications.

View RepositoryWebsite
Share

nodejsscan nodejsscan icon

Static security code scanner (SAST) for Node.js applications powered by libsast and semgrep.

Made with Love in India Tweet

platform License python Tests

Support nodejsscan

  • Donate via Paypal: Donate via Paypal
  • Sponsor the Project: Github Sponsors

e-Learning Courses & Certifications

OpSecX Video Course OpSecX Node.js Security: Pentesting and Exploitation - NJS

Run nodejsscan

docker pull opensecurity/nodejsscan:latest
docker run -it -p 9090:9090 opensecurity/nodejsscan:latest

Setup nodejsscan locally

Install Postgres and configure SQLALCHEMY_DATABASE_URI in nodejsscan/settings.py or as environment variable.

From version 4 onwards, windows support is dropped.

git clone https://github.com/ajinabraham/nodejsscan.git
cd nodejsscan
python3 -m venv venv
source venv/bin/activate
pip install -r requirements.txt
python3 manage.py recreate-db # Run once to create database schema

To run nodejsscan

./run.sh

This will run nodejsscan web user interface at http://127.0.0.1:9090

Command Line Interface(CLI) and Python API

njsscan_cli

  • CLI: https://github.com/ajinabraham/njsscan#command-line-options
  • API: https://github.com/ajinabraham/njsscan#python-api

Presentations

Watch the video

Integrations

Slack Alerts

Create your slack app Slack App and set SLACK_WEBHOOK_URL in nodejsscan/settings.py or as environment variable.

nodejsscan slack alert

Email Alerts

Configure SMTP settings in nodejsscan/settings.py or as environment variable.

CI/CD or DevSecOps

  • Github Action: https://github.com/ajinabraham/njsscan#github-action
  • Gitlab CI/CD: https://github.com/ajinabraham/njsscan#gitlab-cicd
  • Travis CI: https://github.com/ajinabraham/njsscan#travis-ci

Build Docker image

docker build -t nodejsscan .
docker run -it -p 9090:9090 nodejsscan
  • CLI Docker Image: https://github.com/ajinabraham/njsscan#build-locally

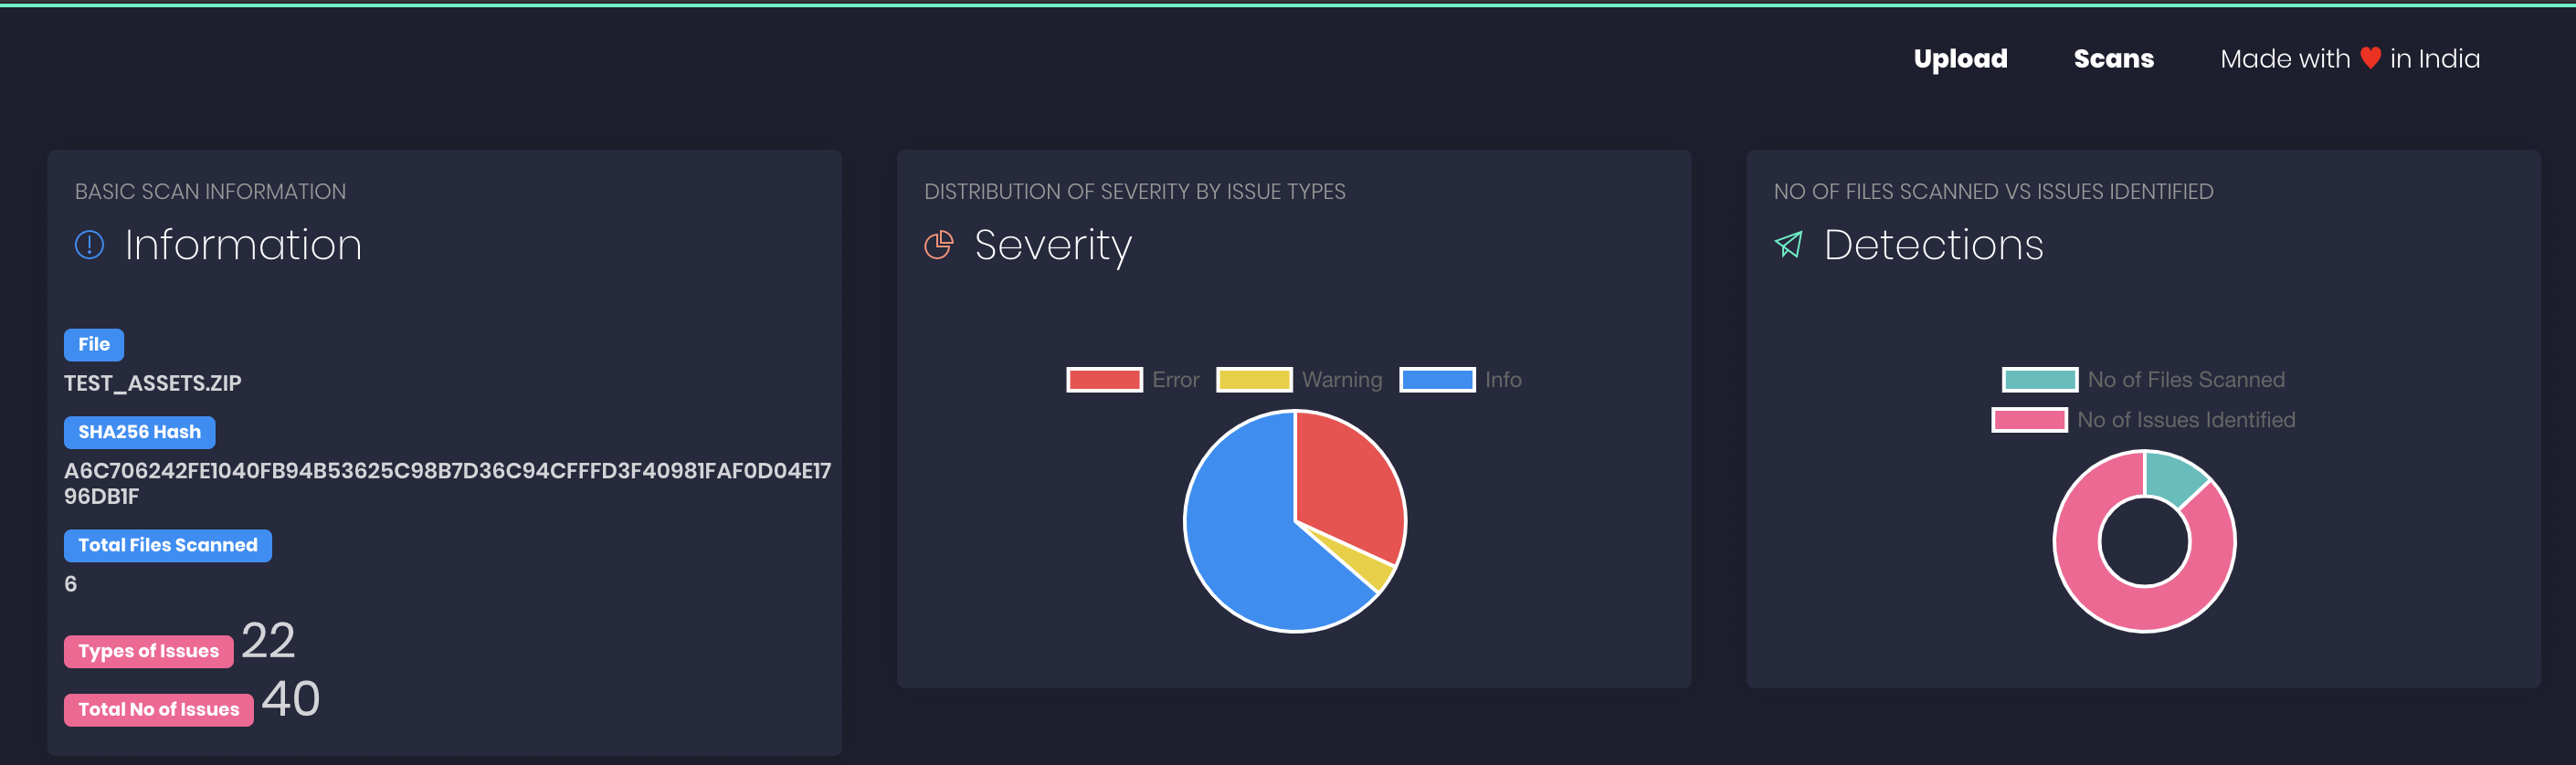
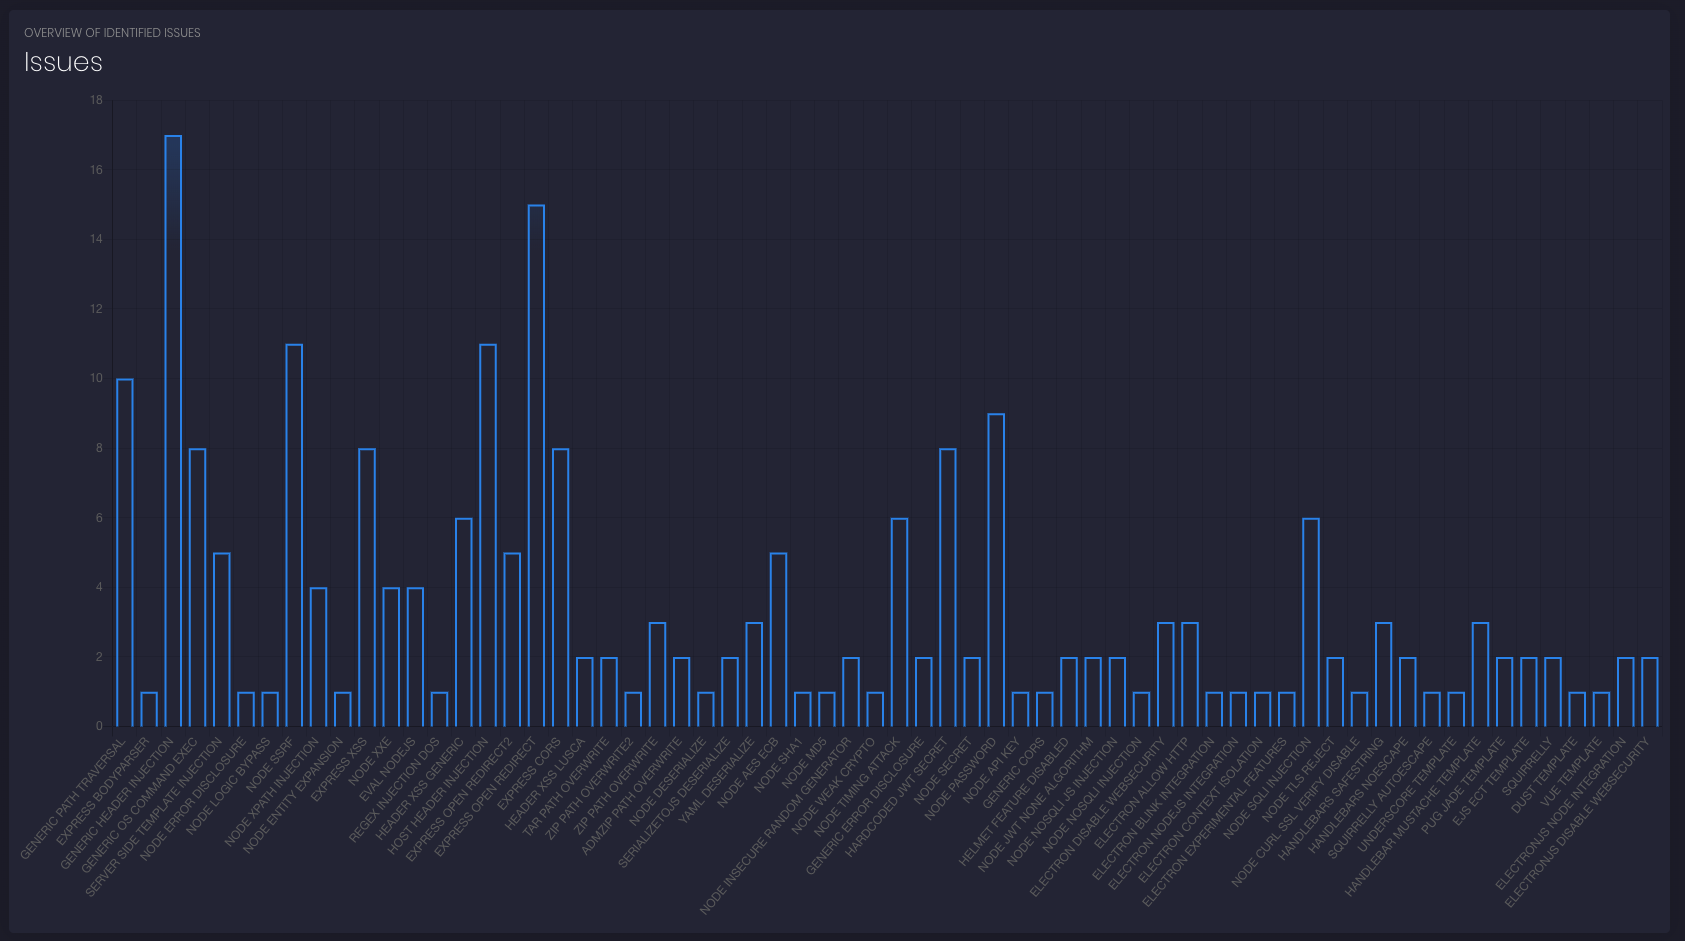
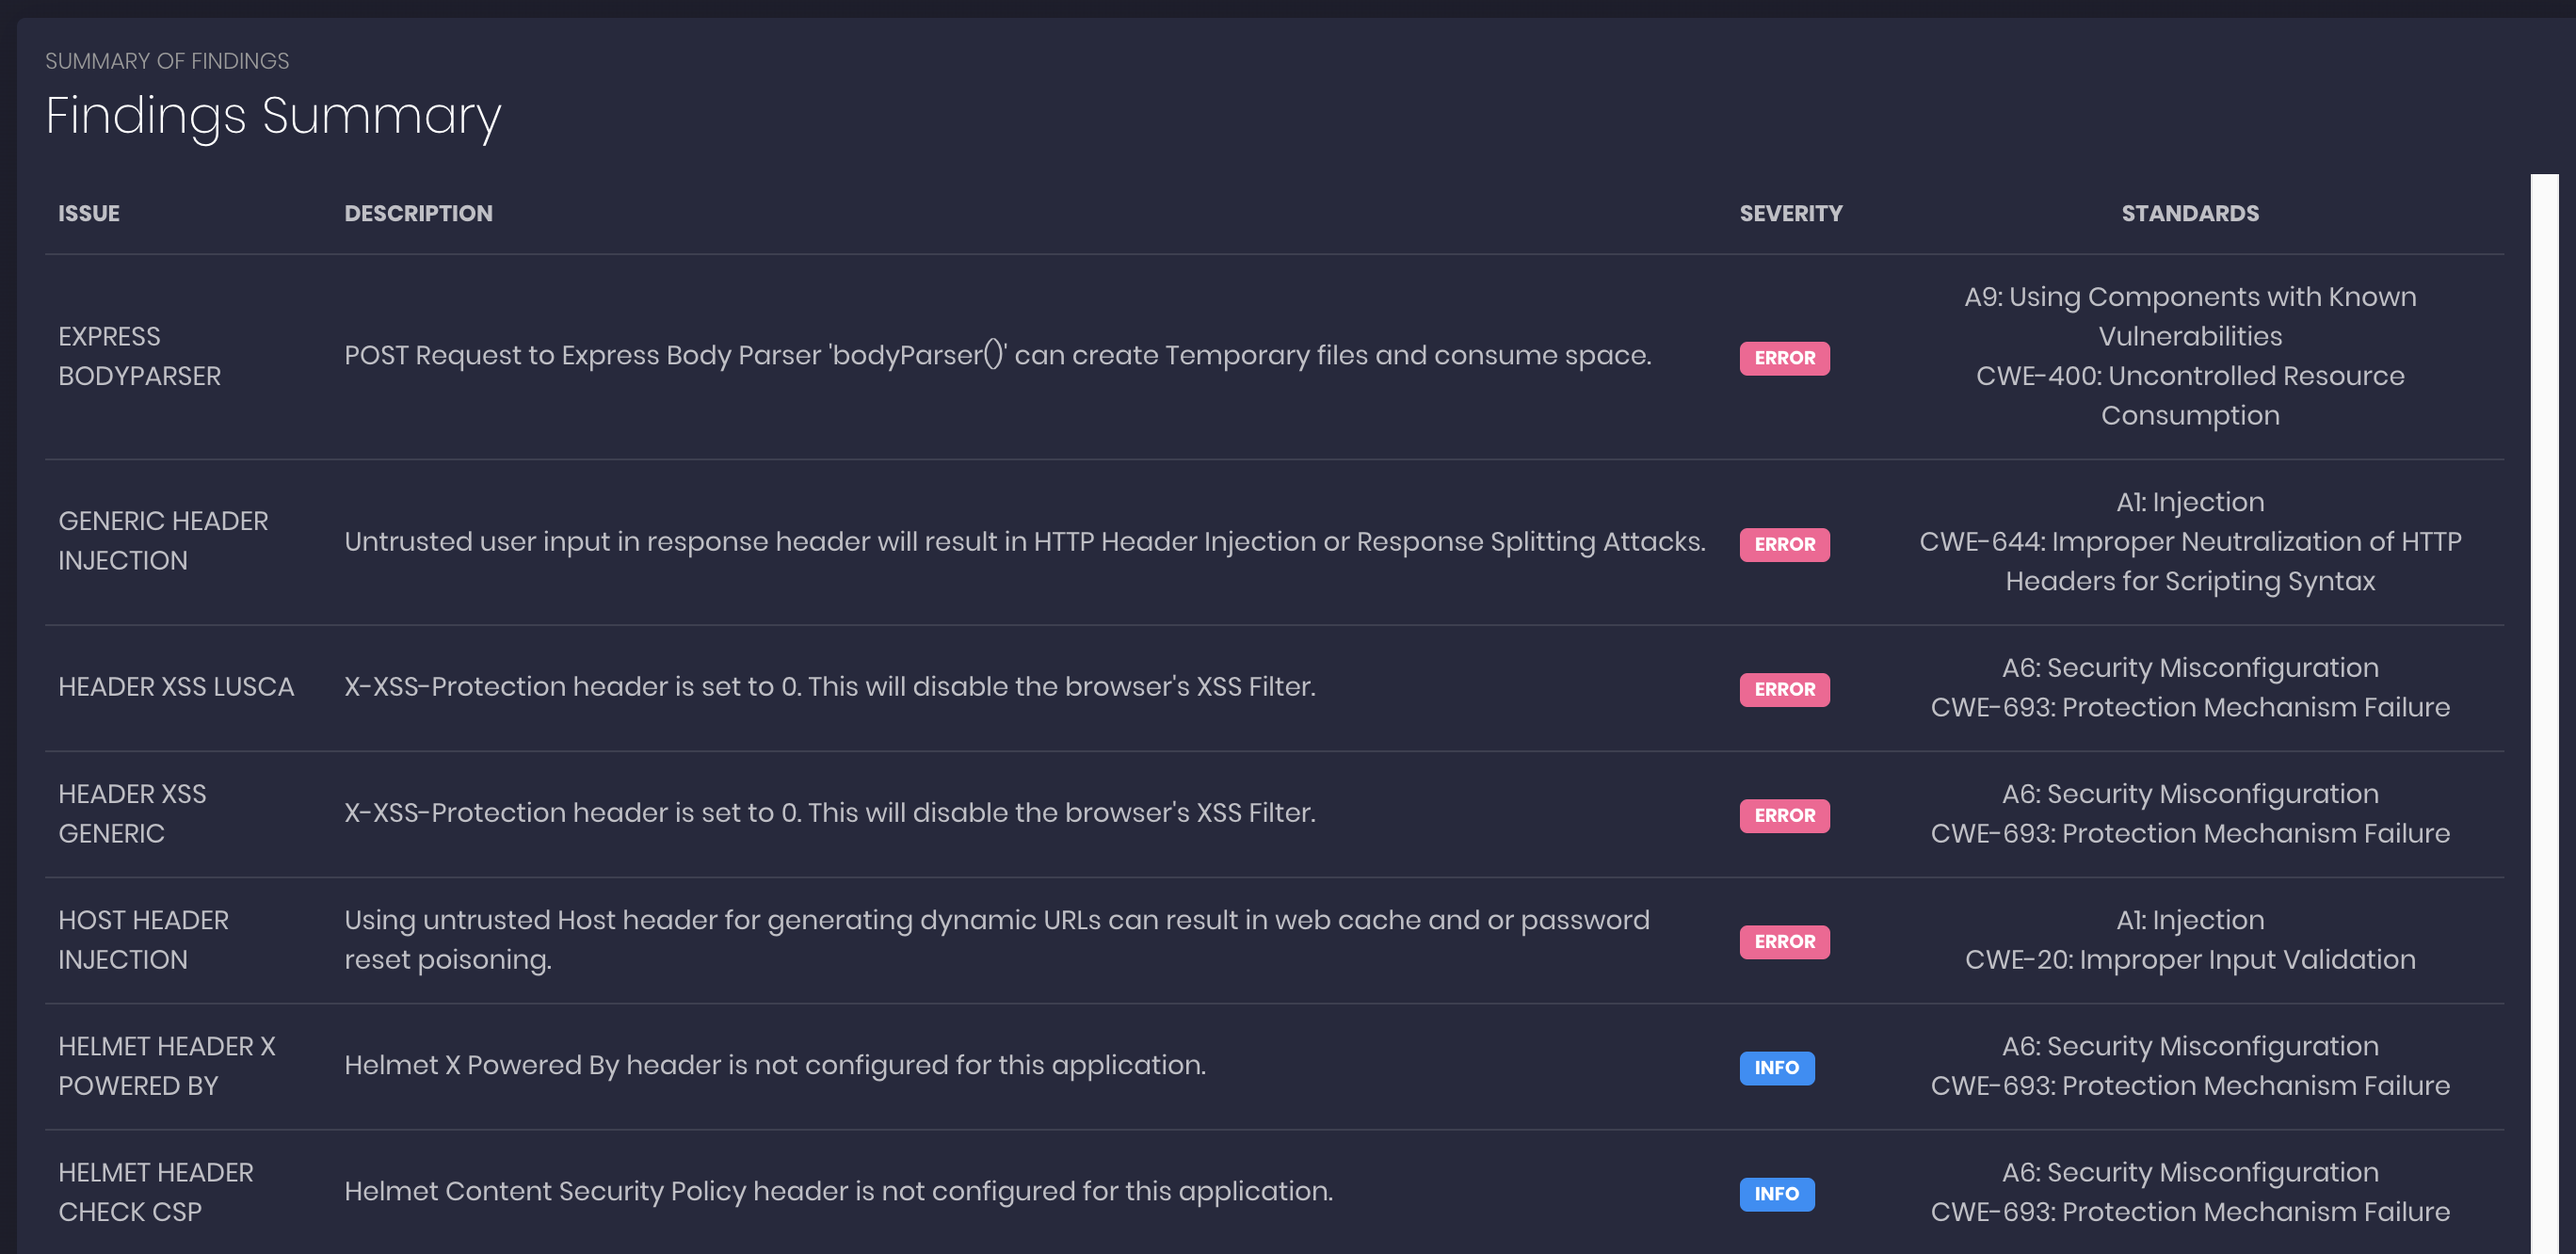
nodejsscan screenshots

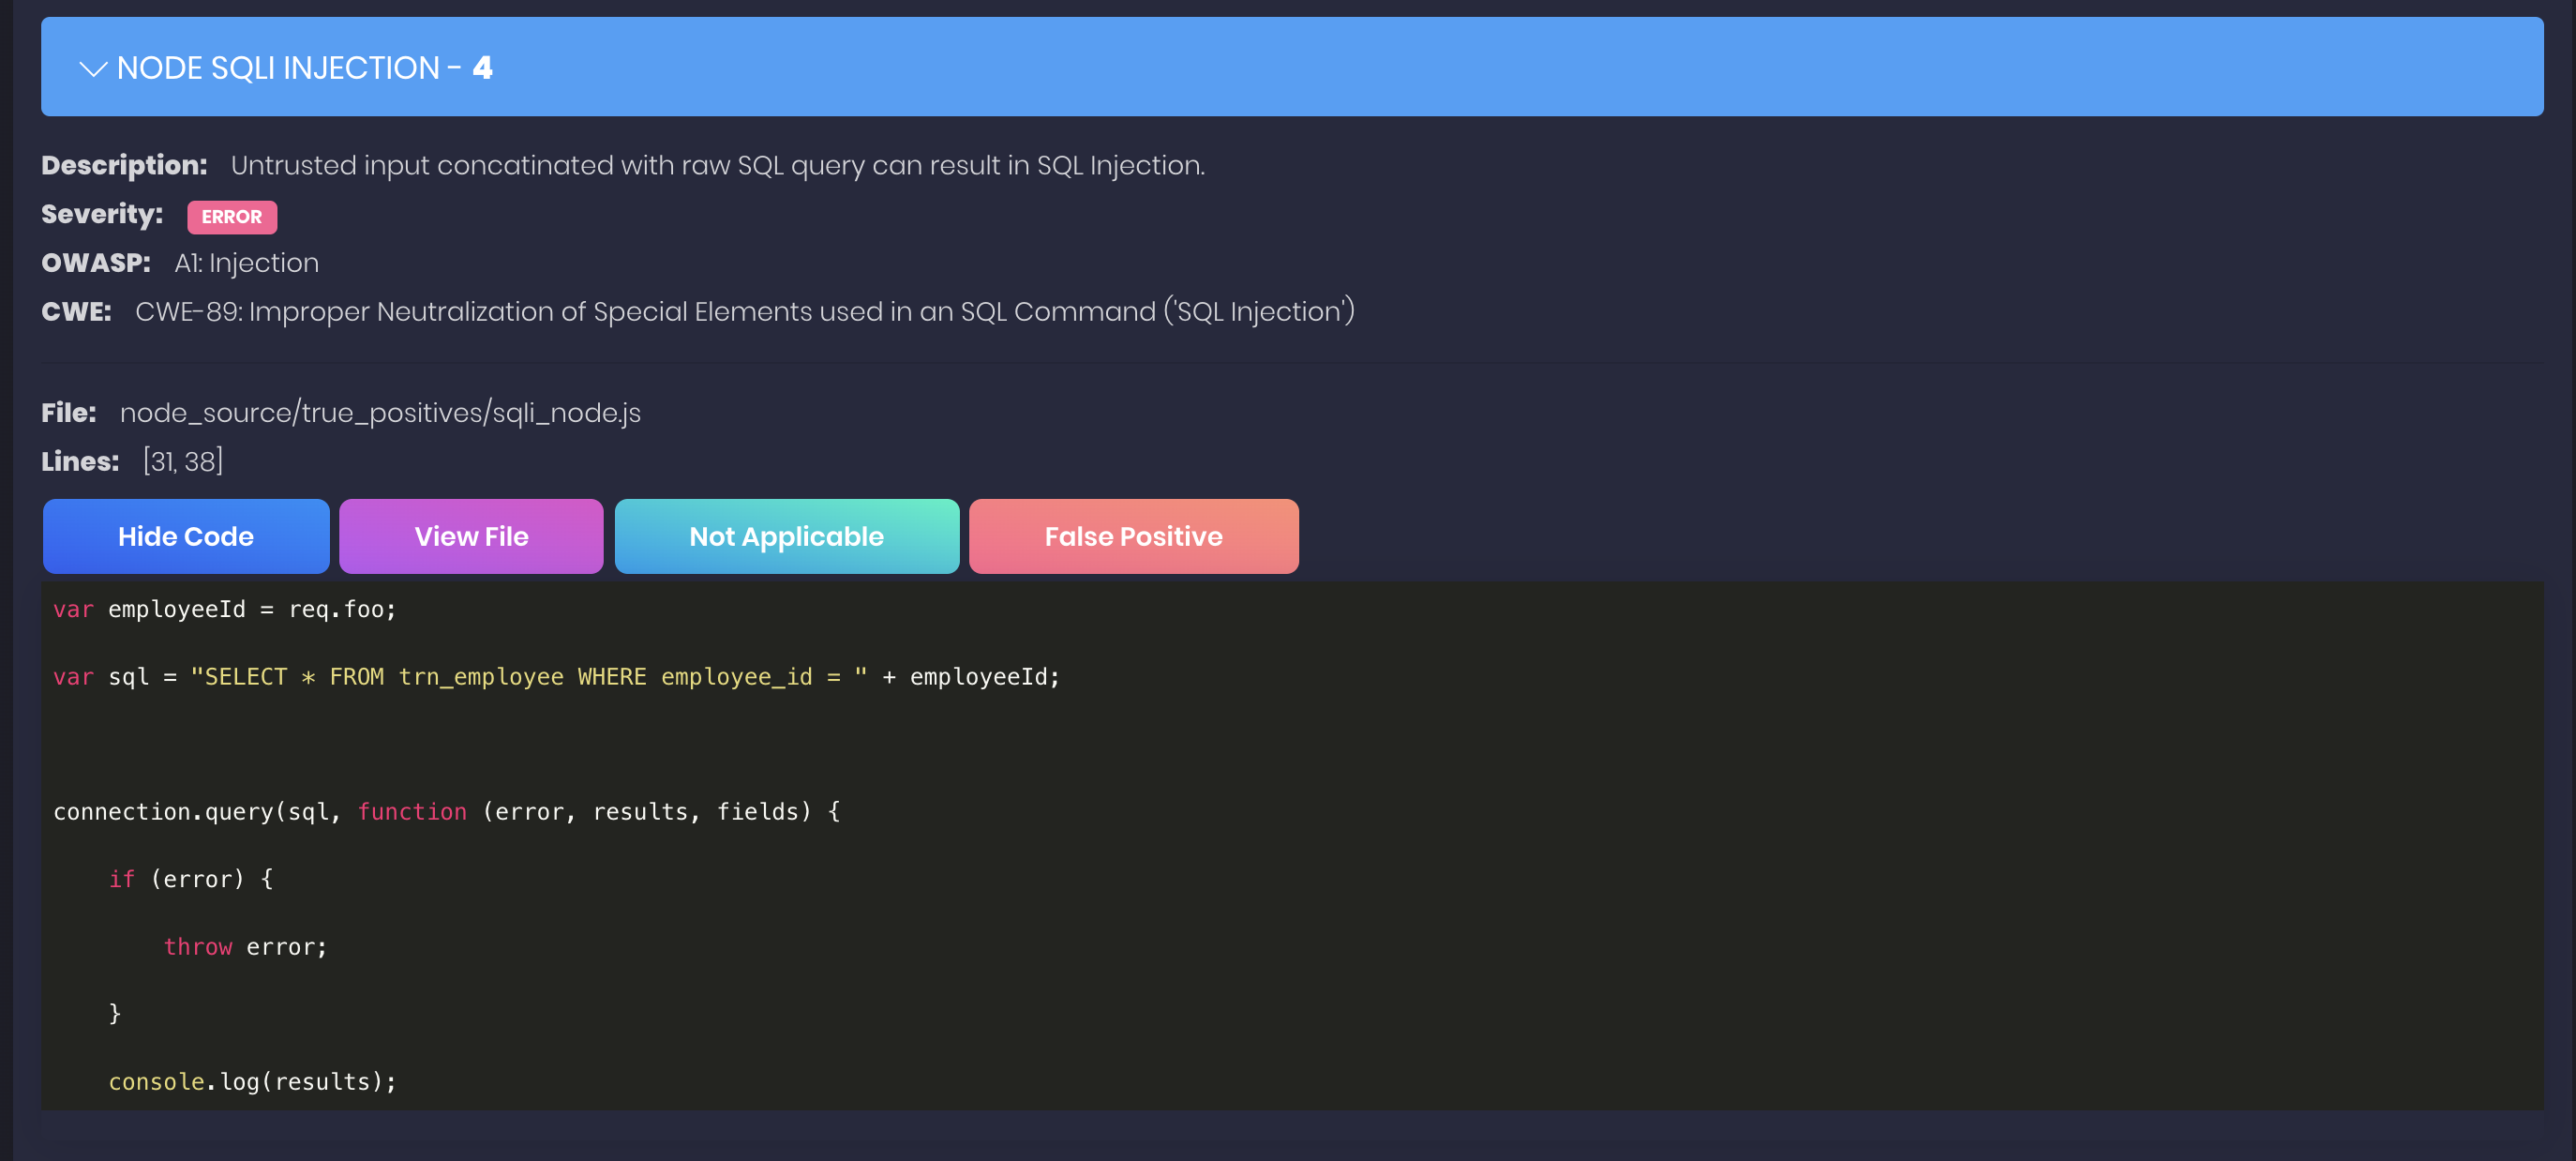
nodejsscan web ui nodejsscan dashboard nodejsscan charts nodejsscan overview nodejsscan findings

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    790
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    508
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    435
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    263
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    260

Explore all tools

Browse our collection of tools

View all tools →