
Archived
vmp2
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
binary-analysiscode-analysisdynamic-code-analysis+3
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
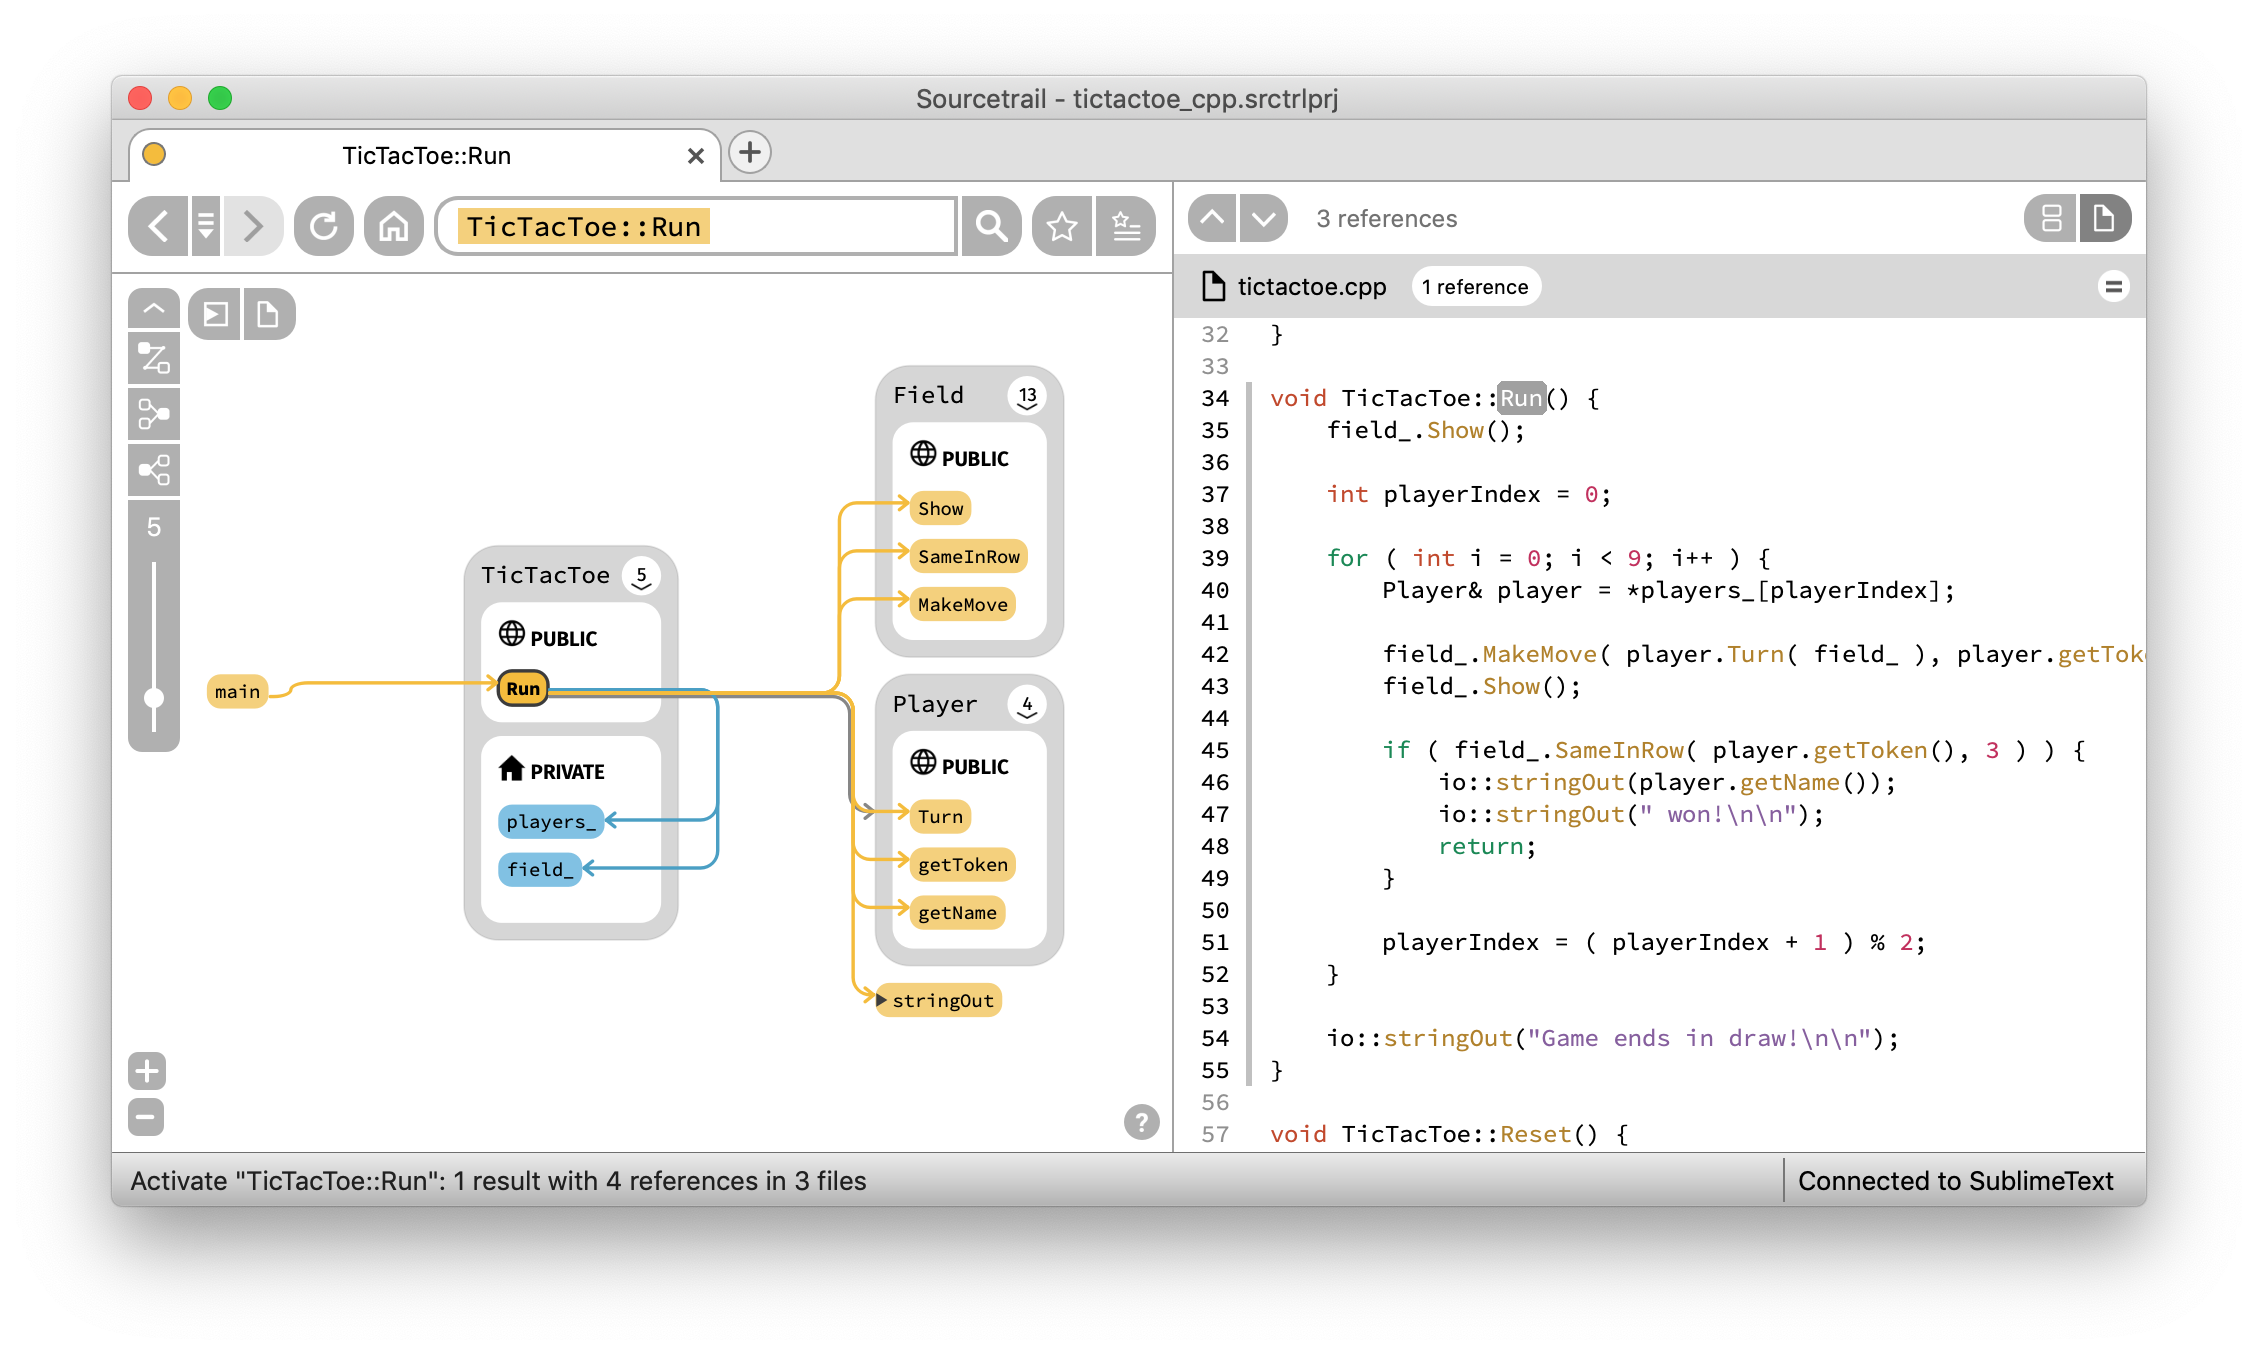 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 scastillo-jp/braces-fork
Temporary fork of braces with a minimal security patch for CVE-2026-93687, created only to validate dependency override behavior and Fortify/FoD…
 sleepthegod/cve-2026-9618-patch
Hardened PHP replacement handlers for PeachPay Stripe capture and void AJAX endpoints, adding nonce verification, capability checks, and strict order…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

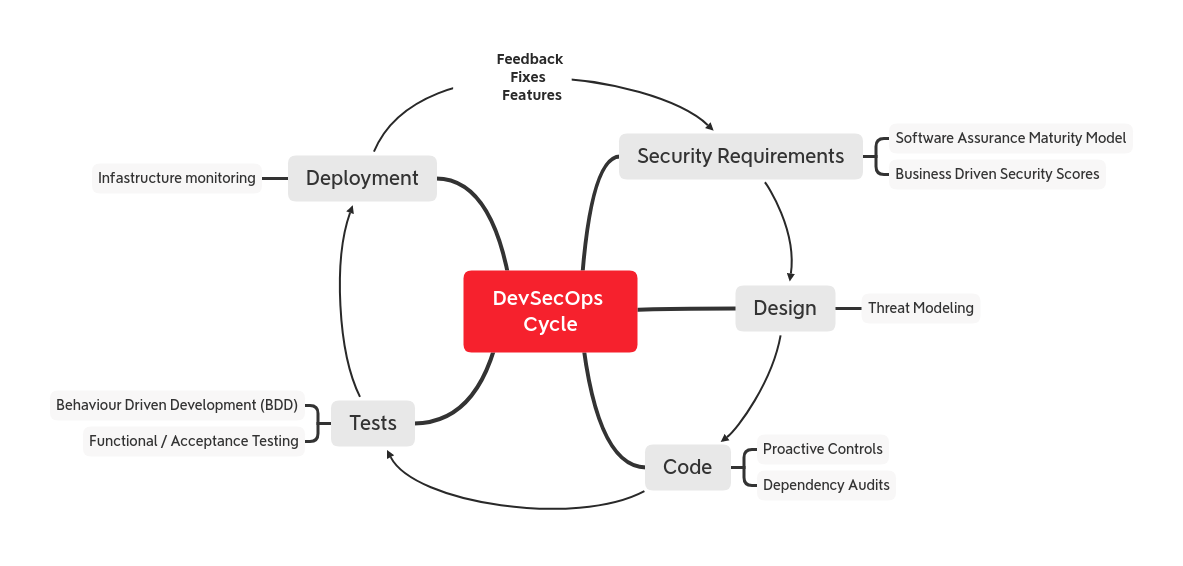 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
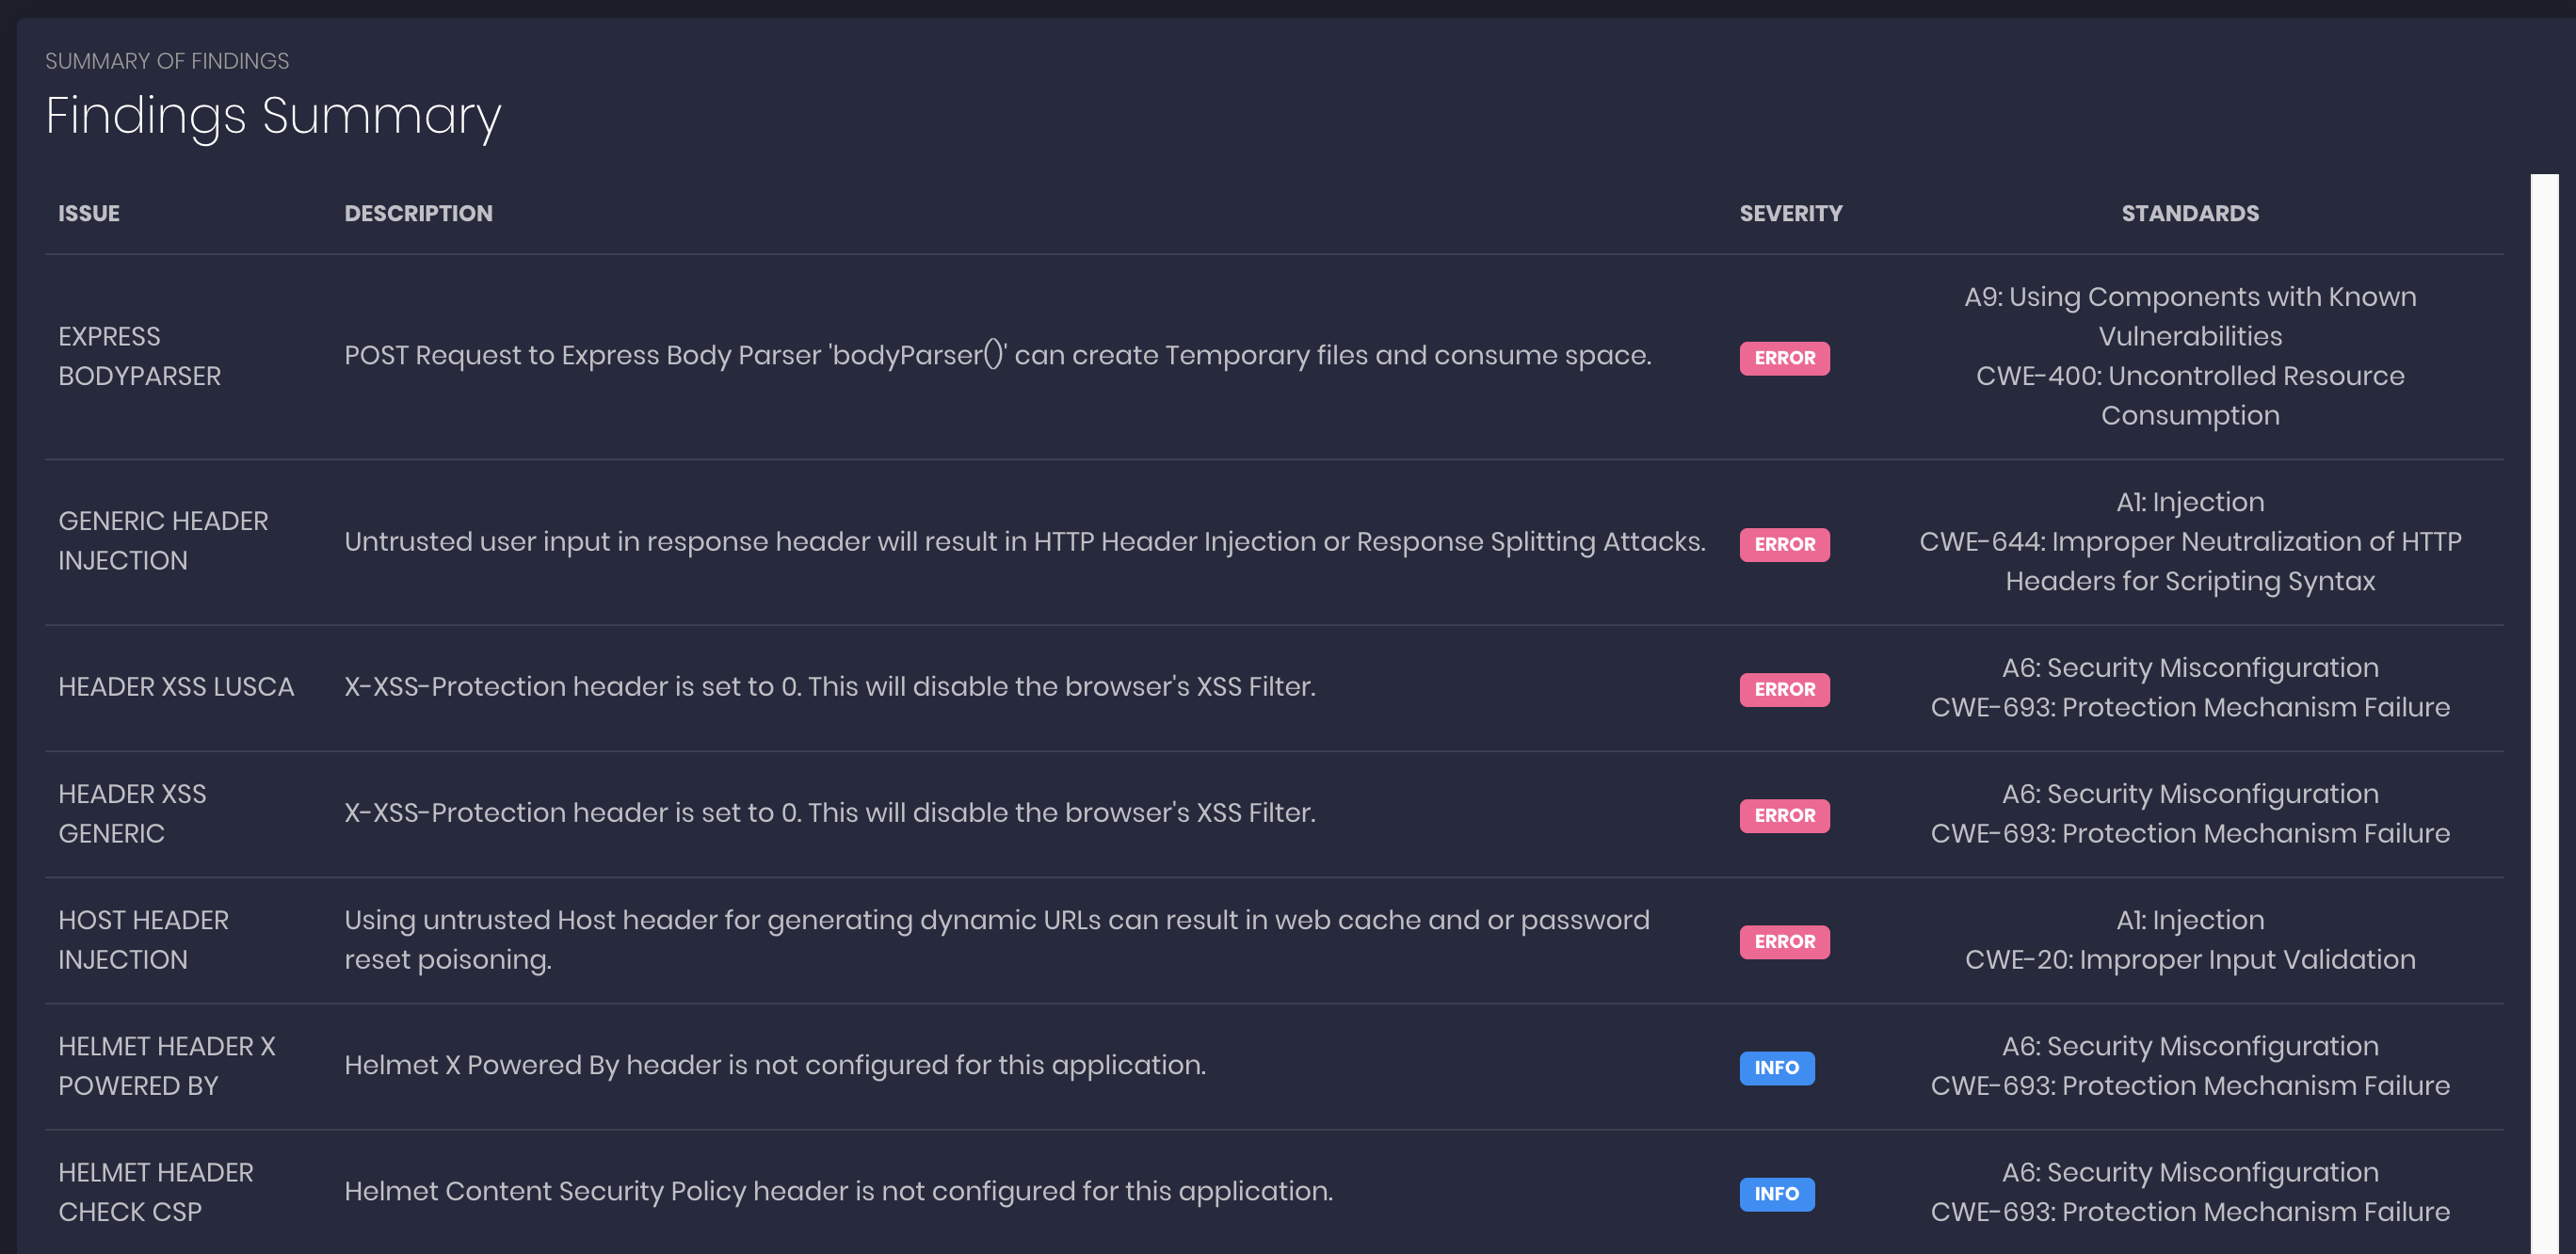 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 wireghoul/graudit
grep rough audit - source code auditing tool
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
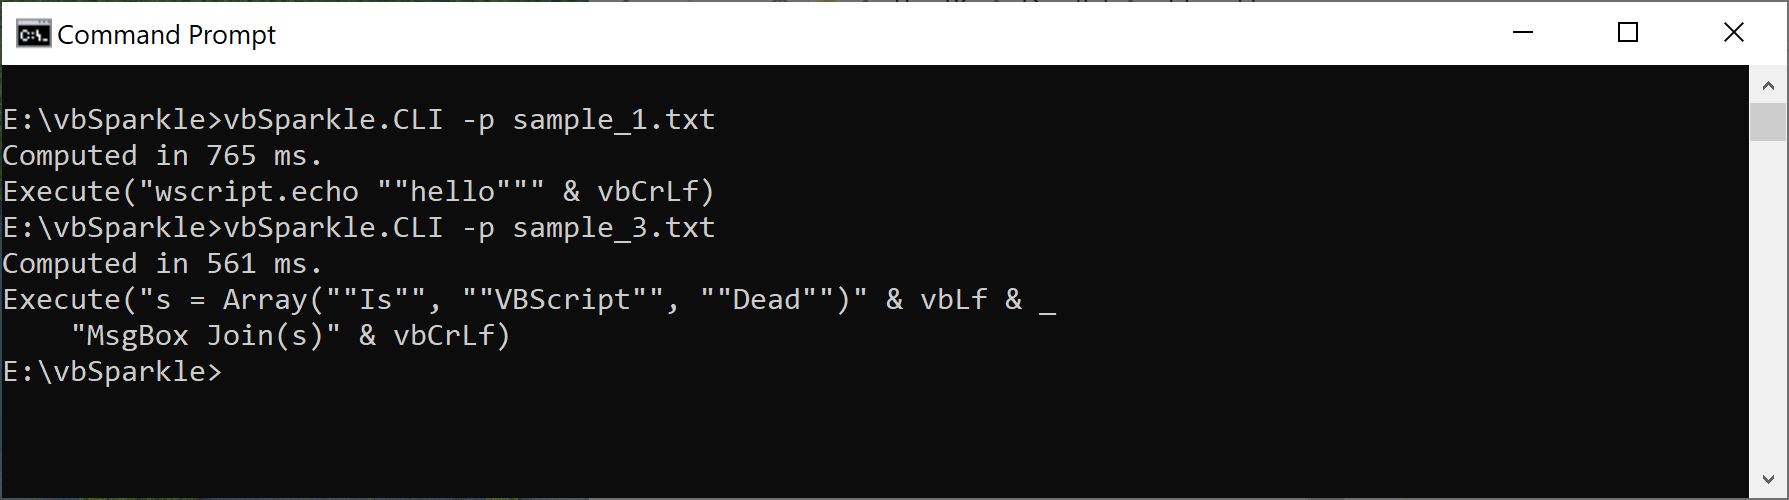 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation