php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…

Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…

Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…

Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.


Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.

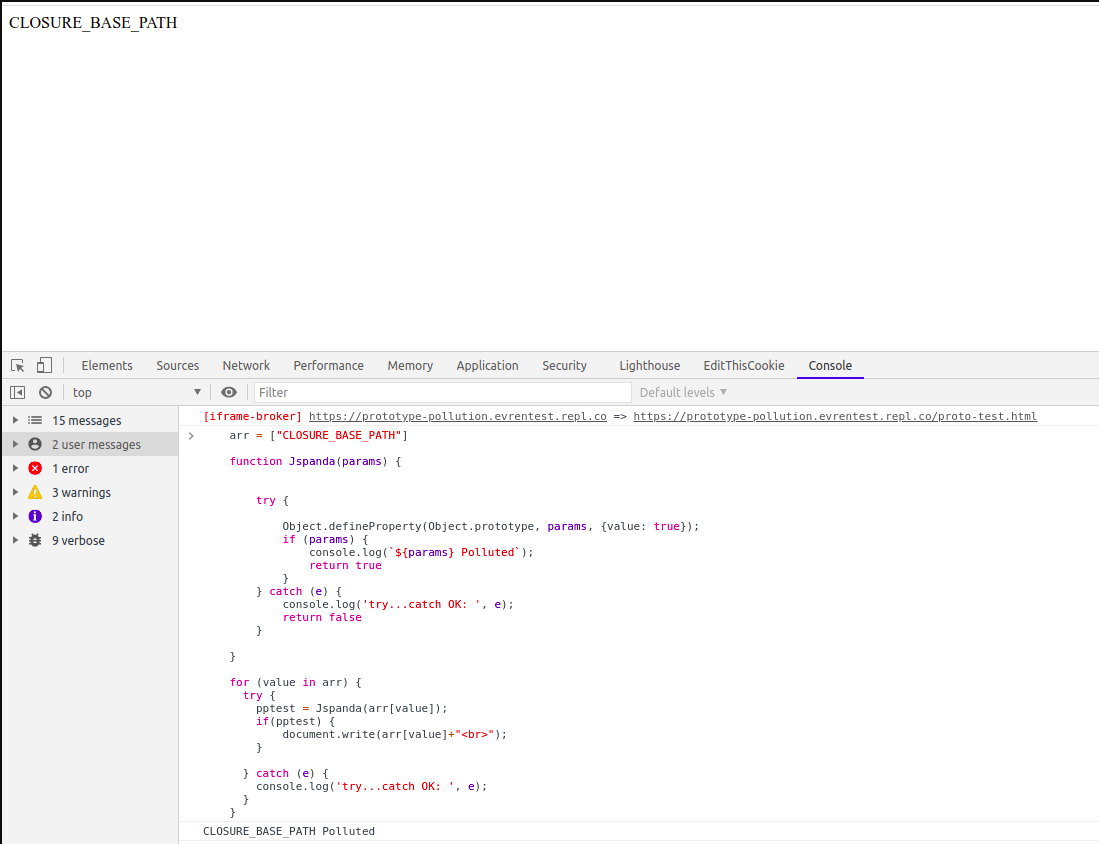
client-side prototype pullution vulnerability scanner

Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…

AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…

Checklist and tools for increasing security of Apache Airflow

Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits

AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…

Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…

CLI tool to scan codebases for quantum-vulnerable cryptography

AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…

Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.