

cryptoptic
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
code-analysisconfiguration-auditingcryptography+6
19
nationwide-group-oss/cryptopticCodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
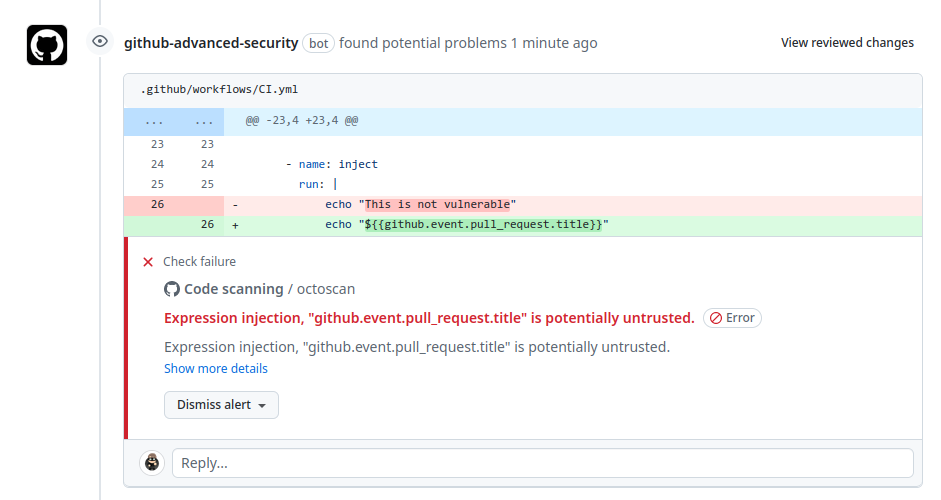 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
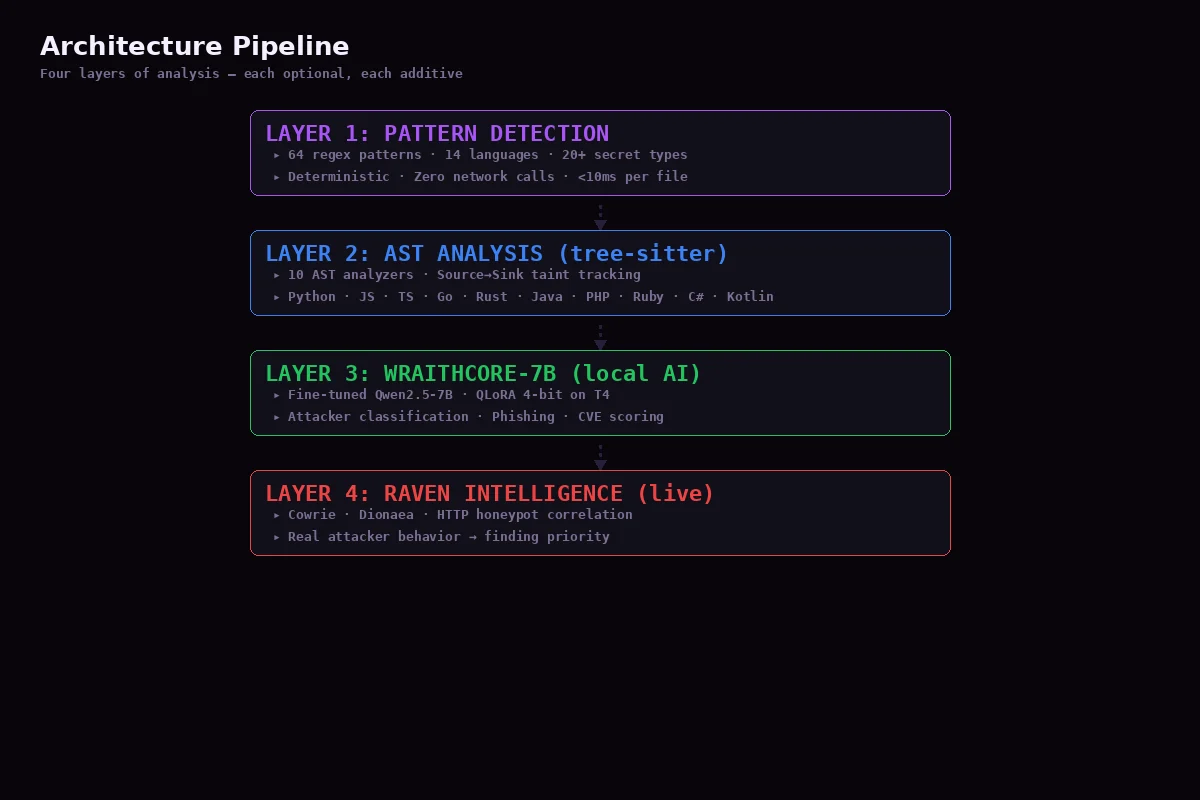 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
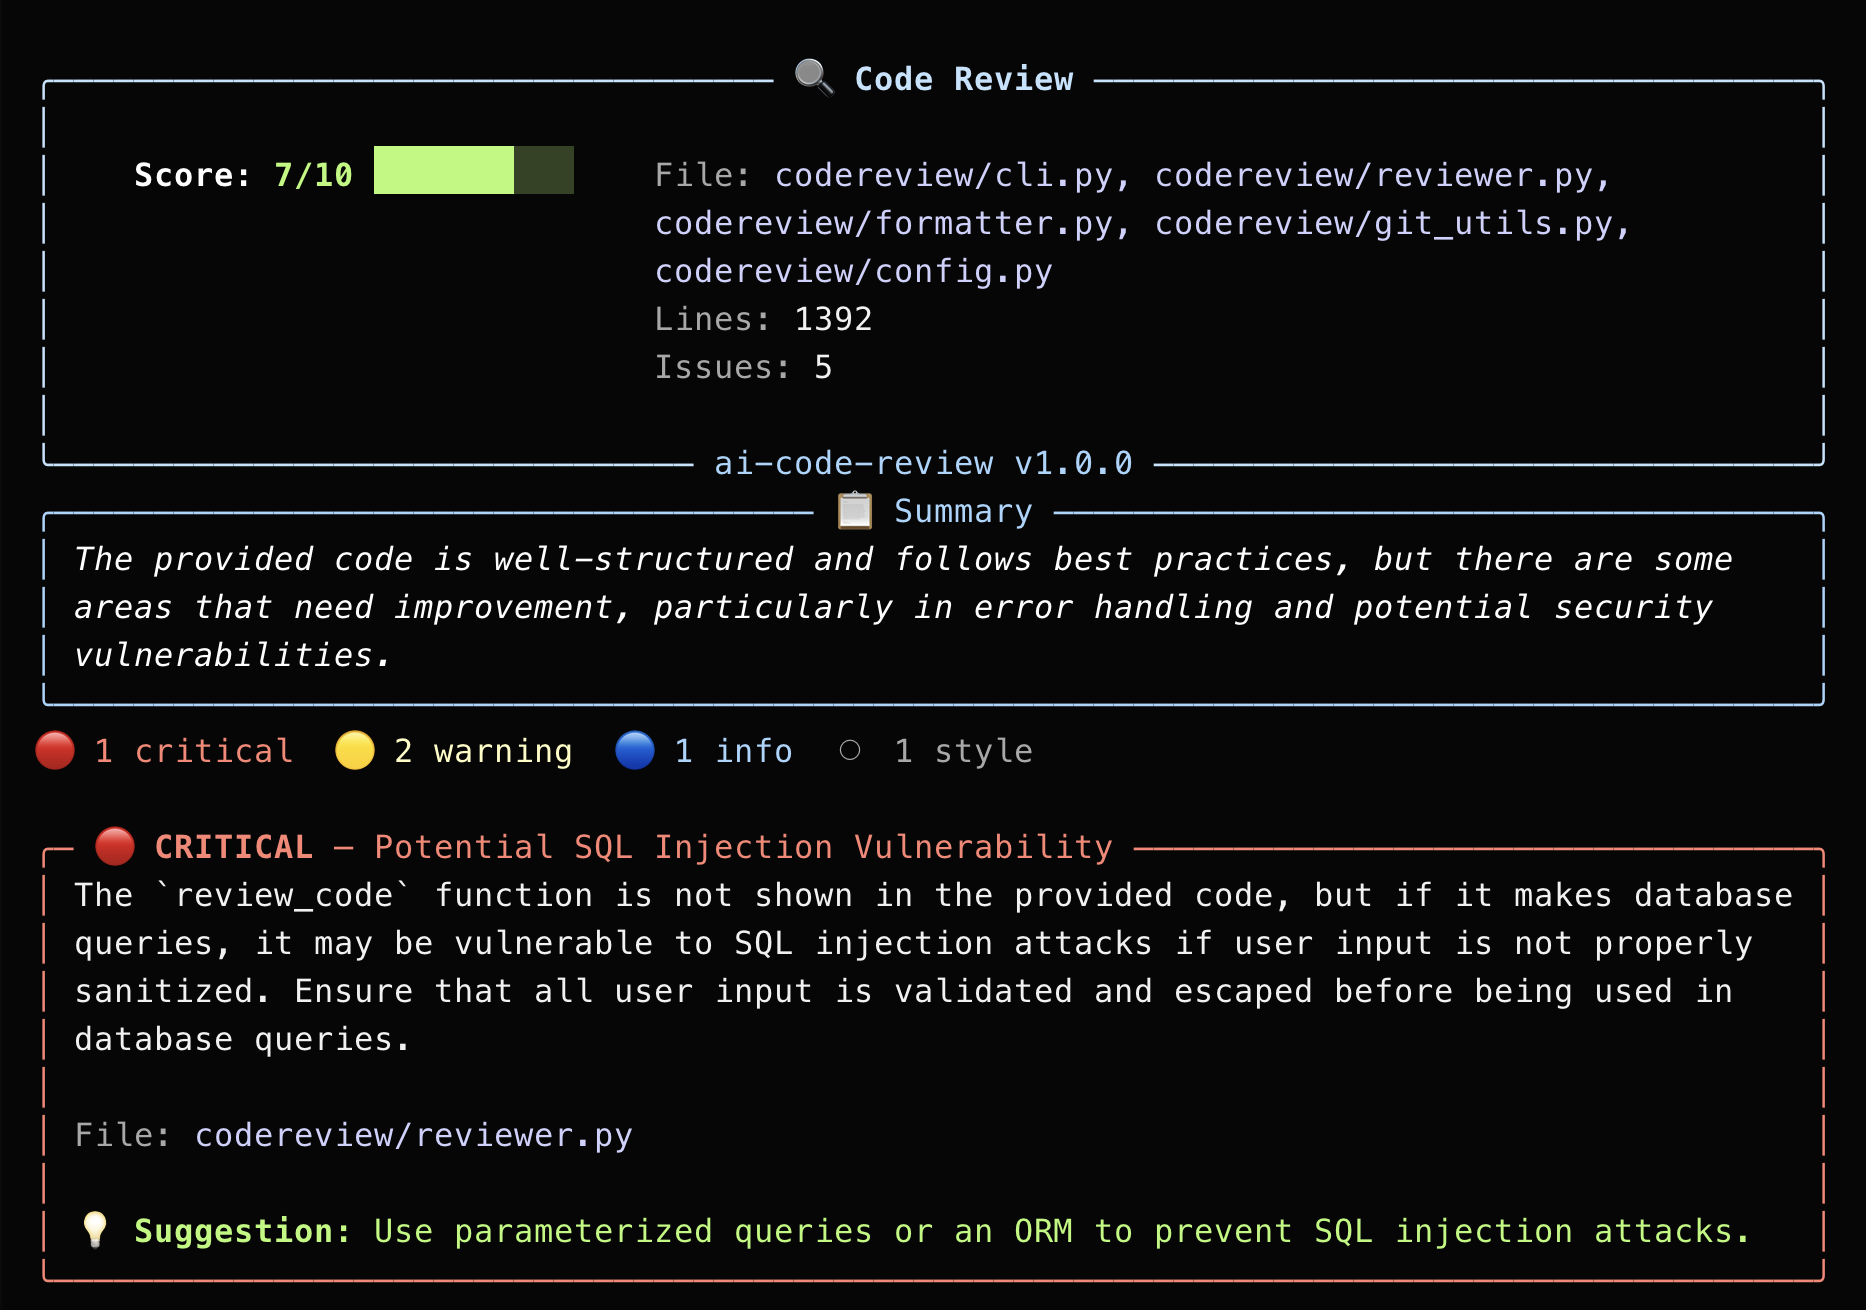 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 7alen7/cve-2026-48813-poc
Proof-of-concept exploit for terminal escape sequence injection via malicious filenames that hides Flawfinder's scan findings; fixed in version…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
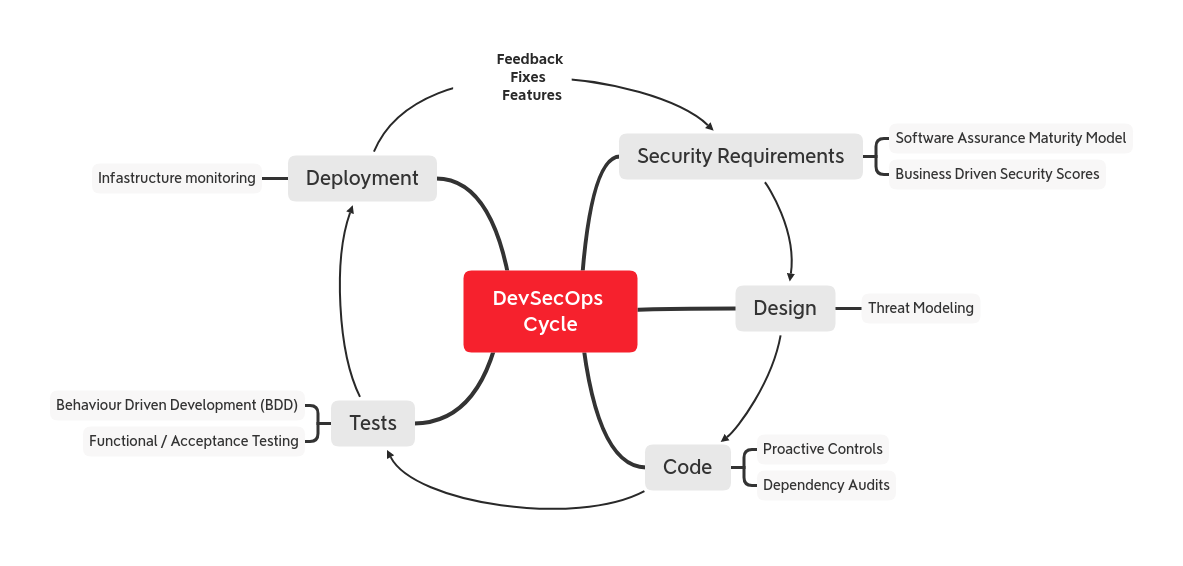 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 wireghoul/graudit
grep rough audit - source code auditing tool
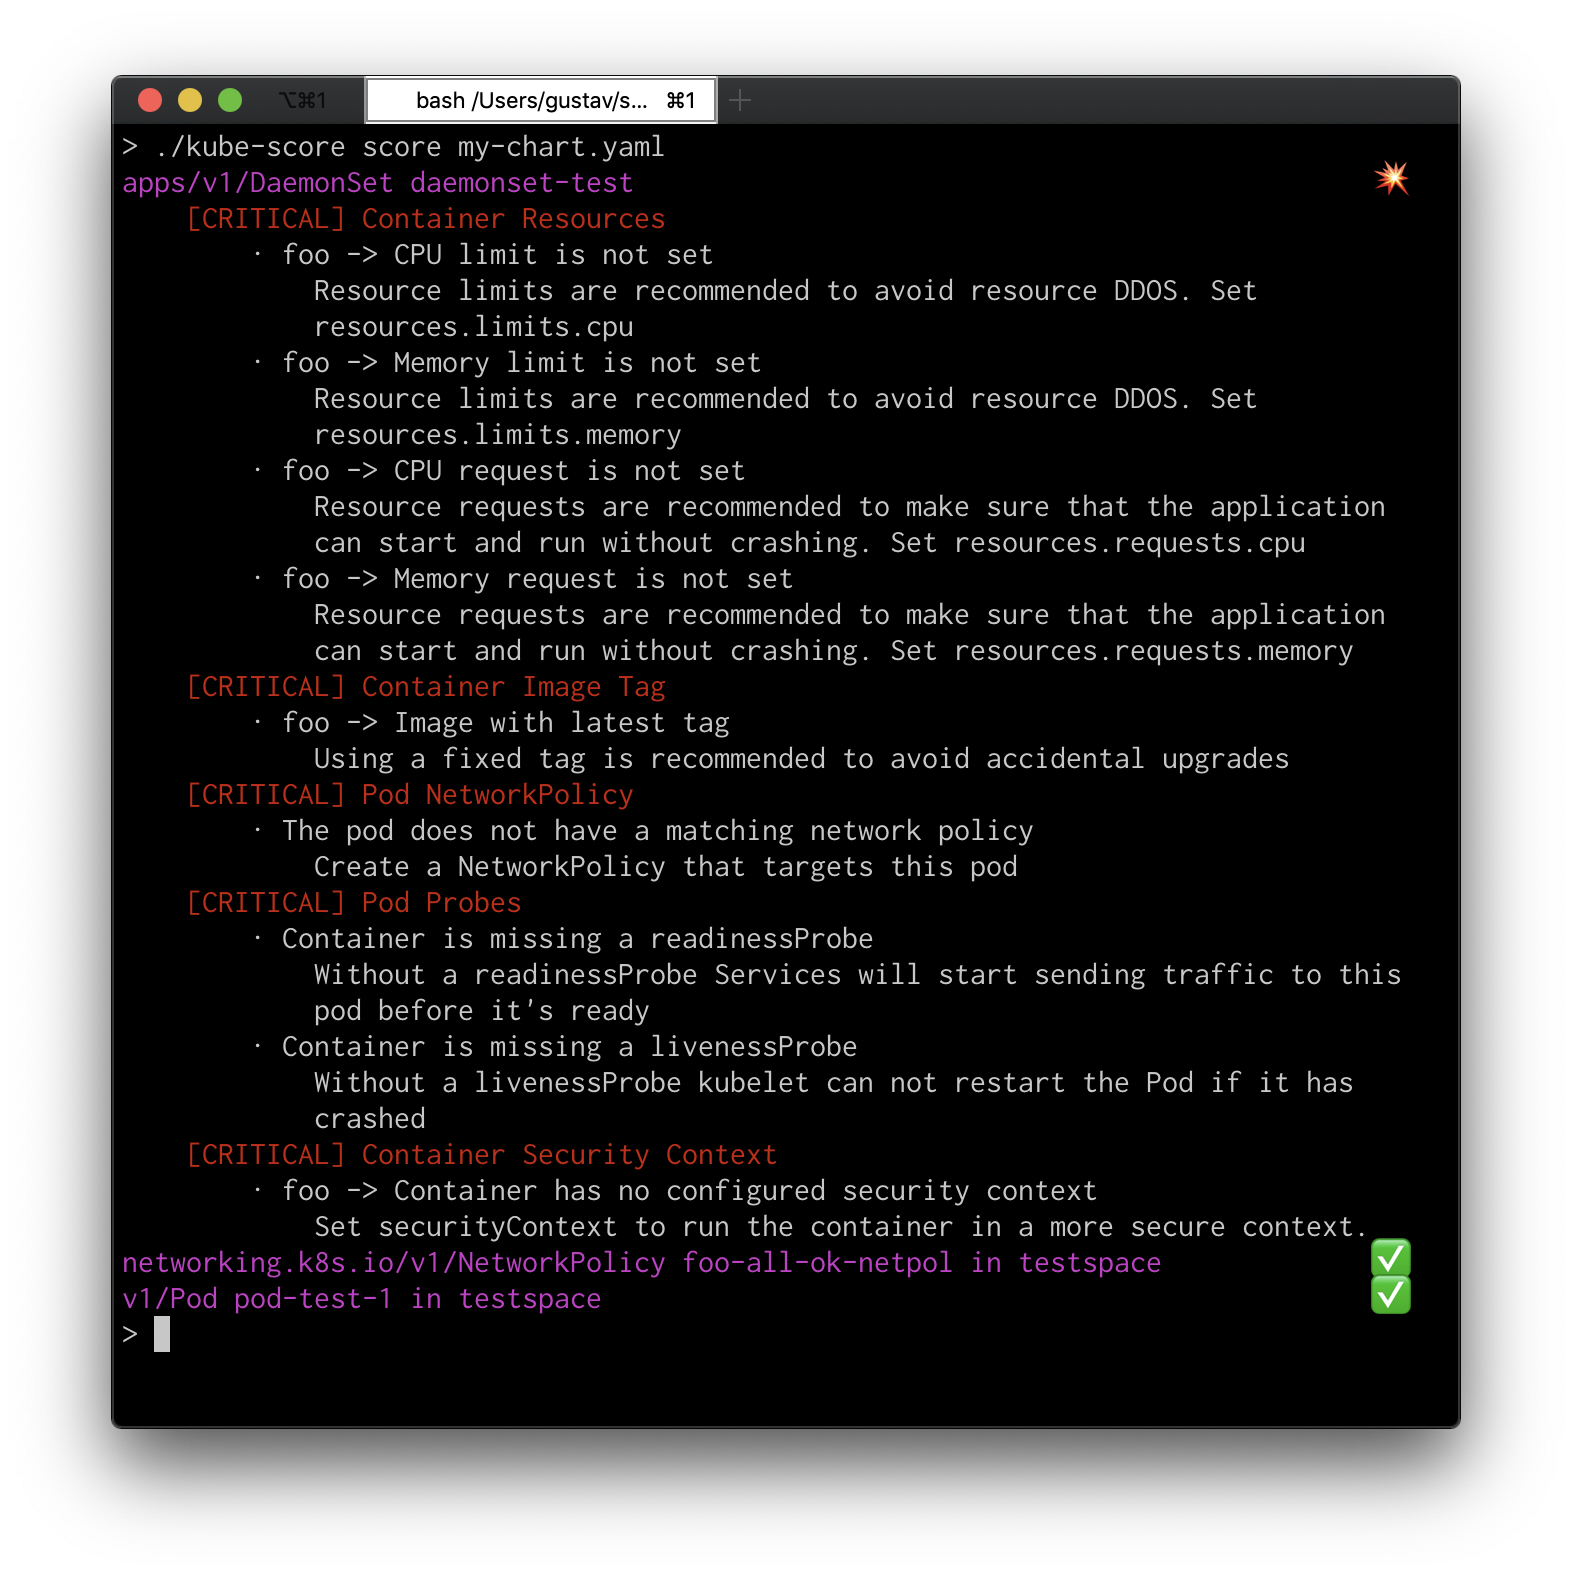 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
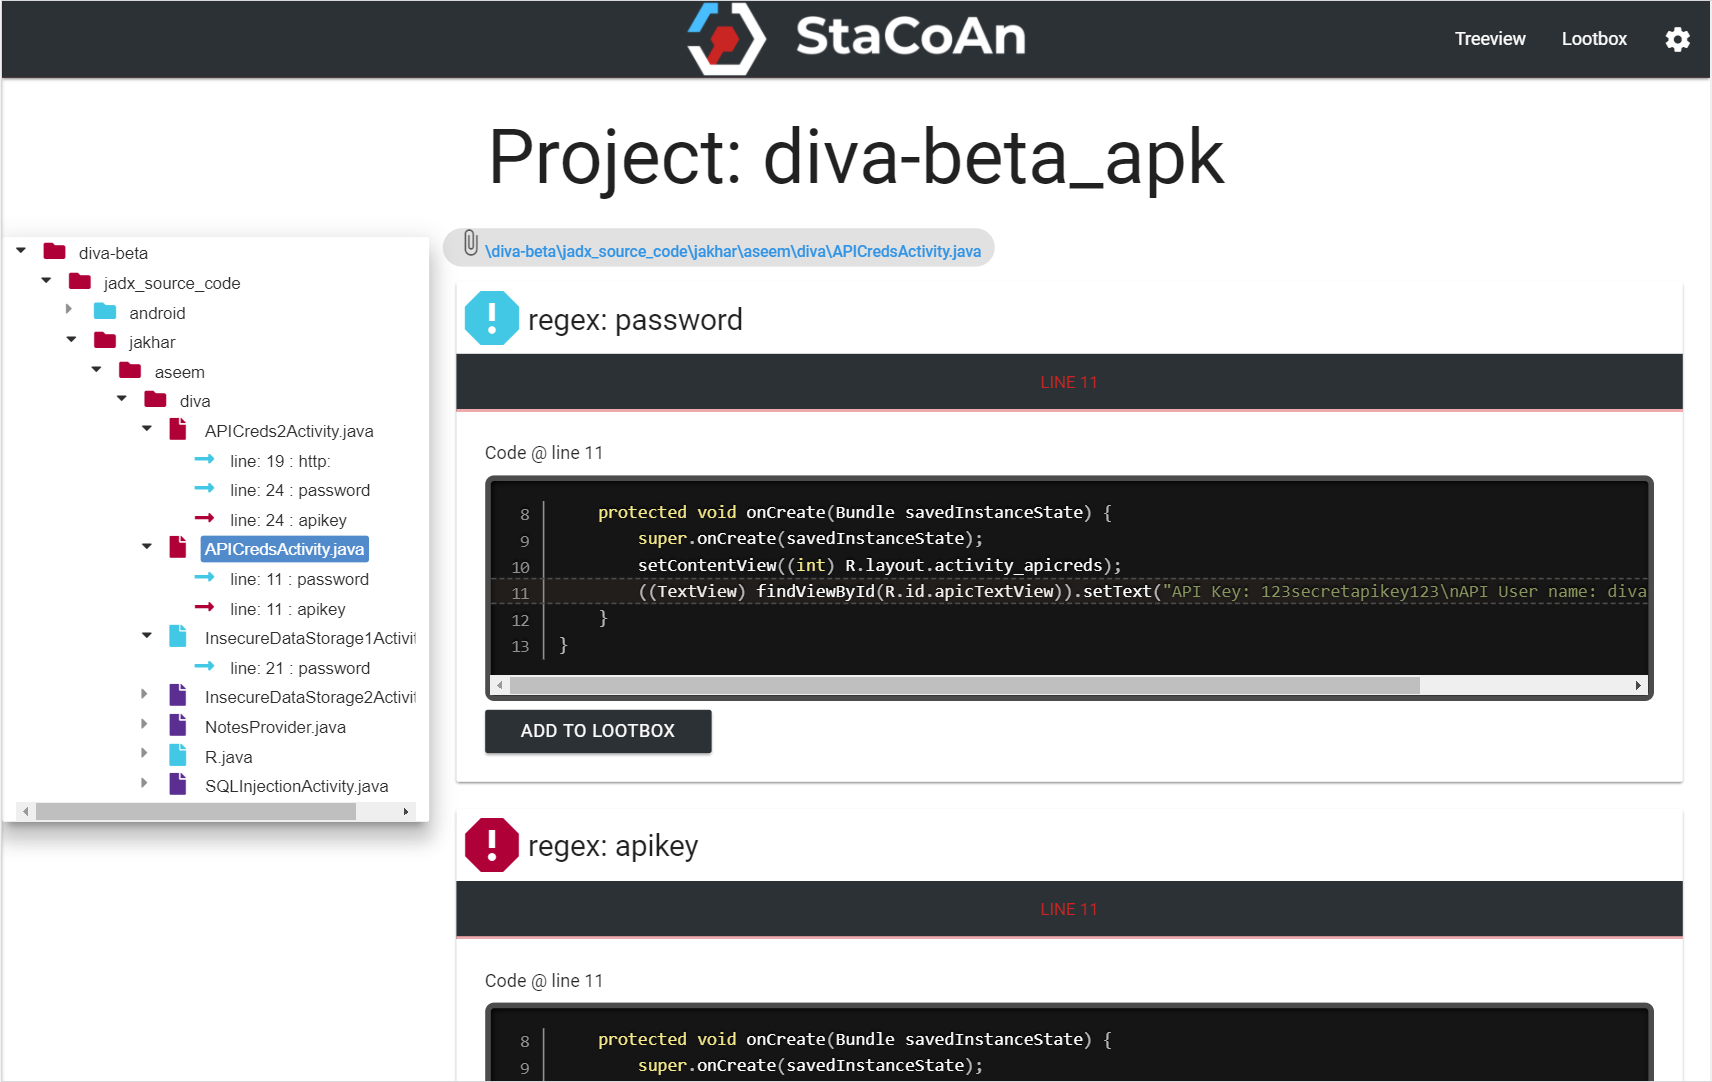 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code