

sast
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
cloud-securitycode-analysisdefensive-tools+9
211 days ago
vulnz/sastFree offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
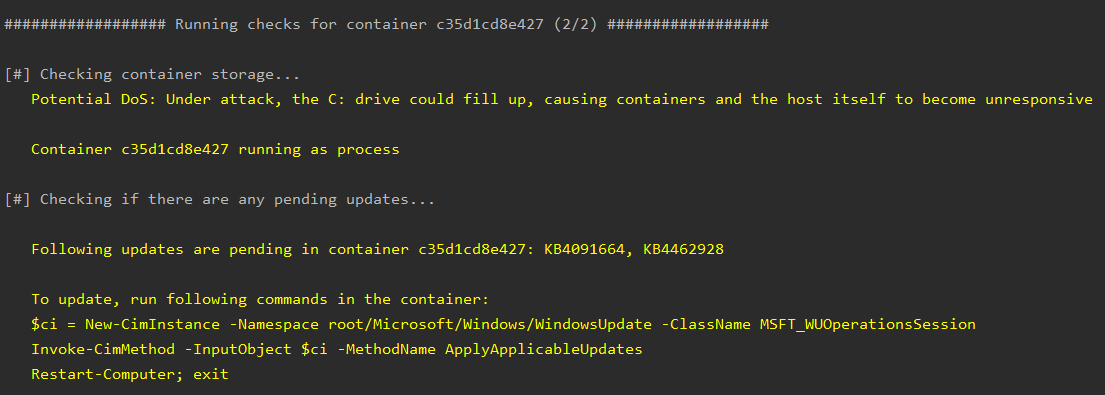 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
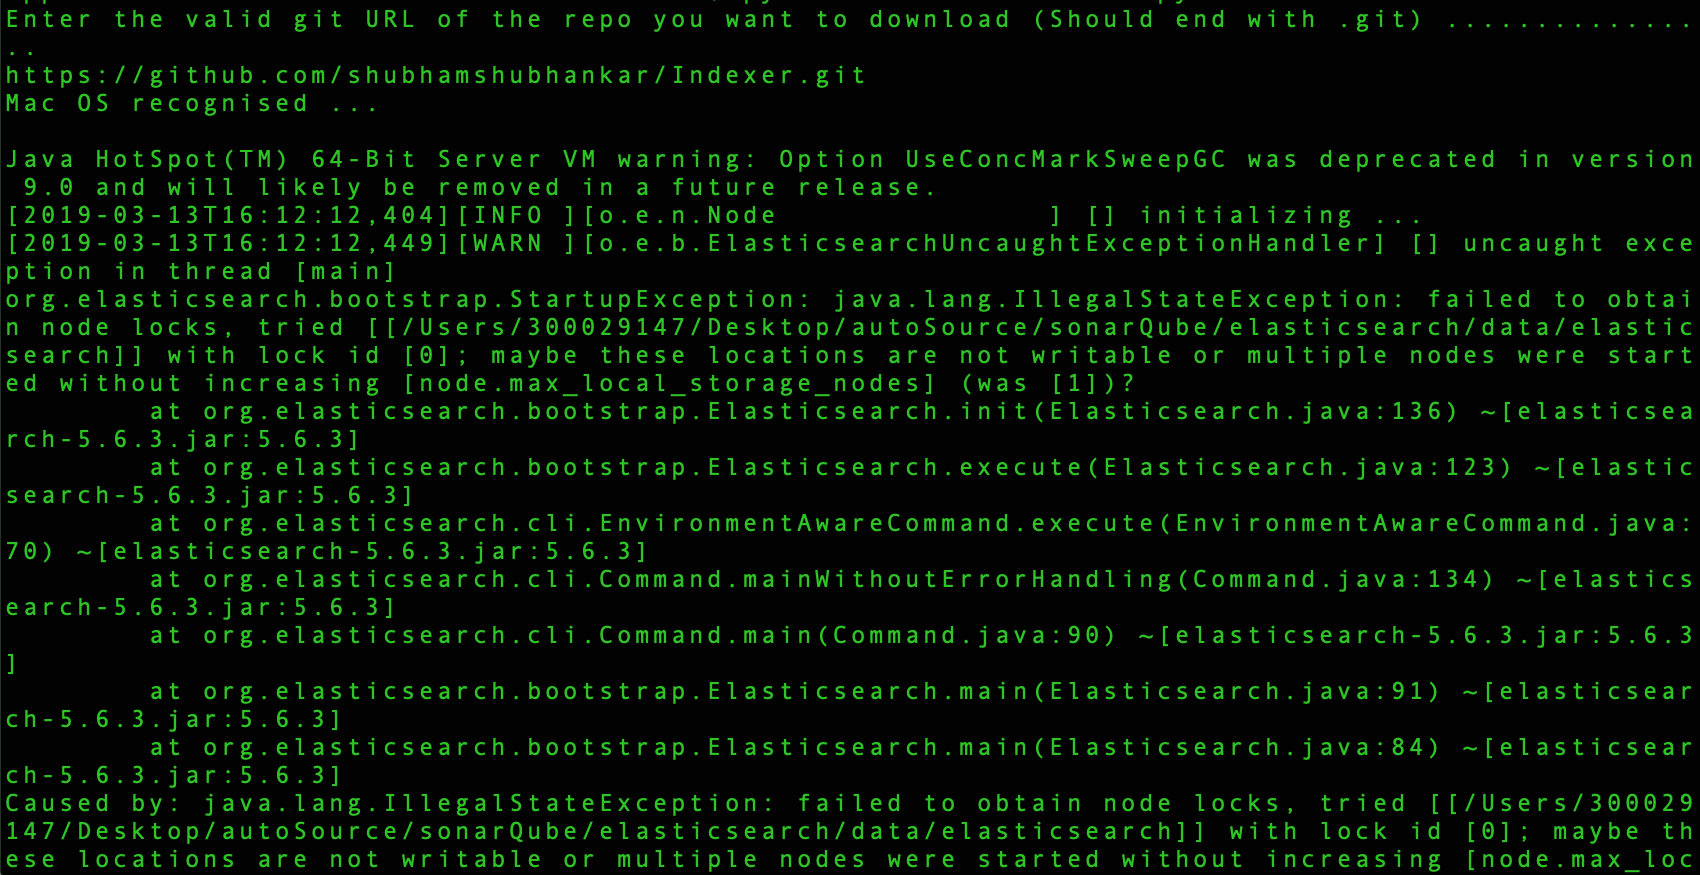 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
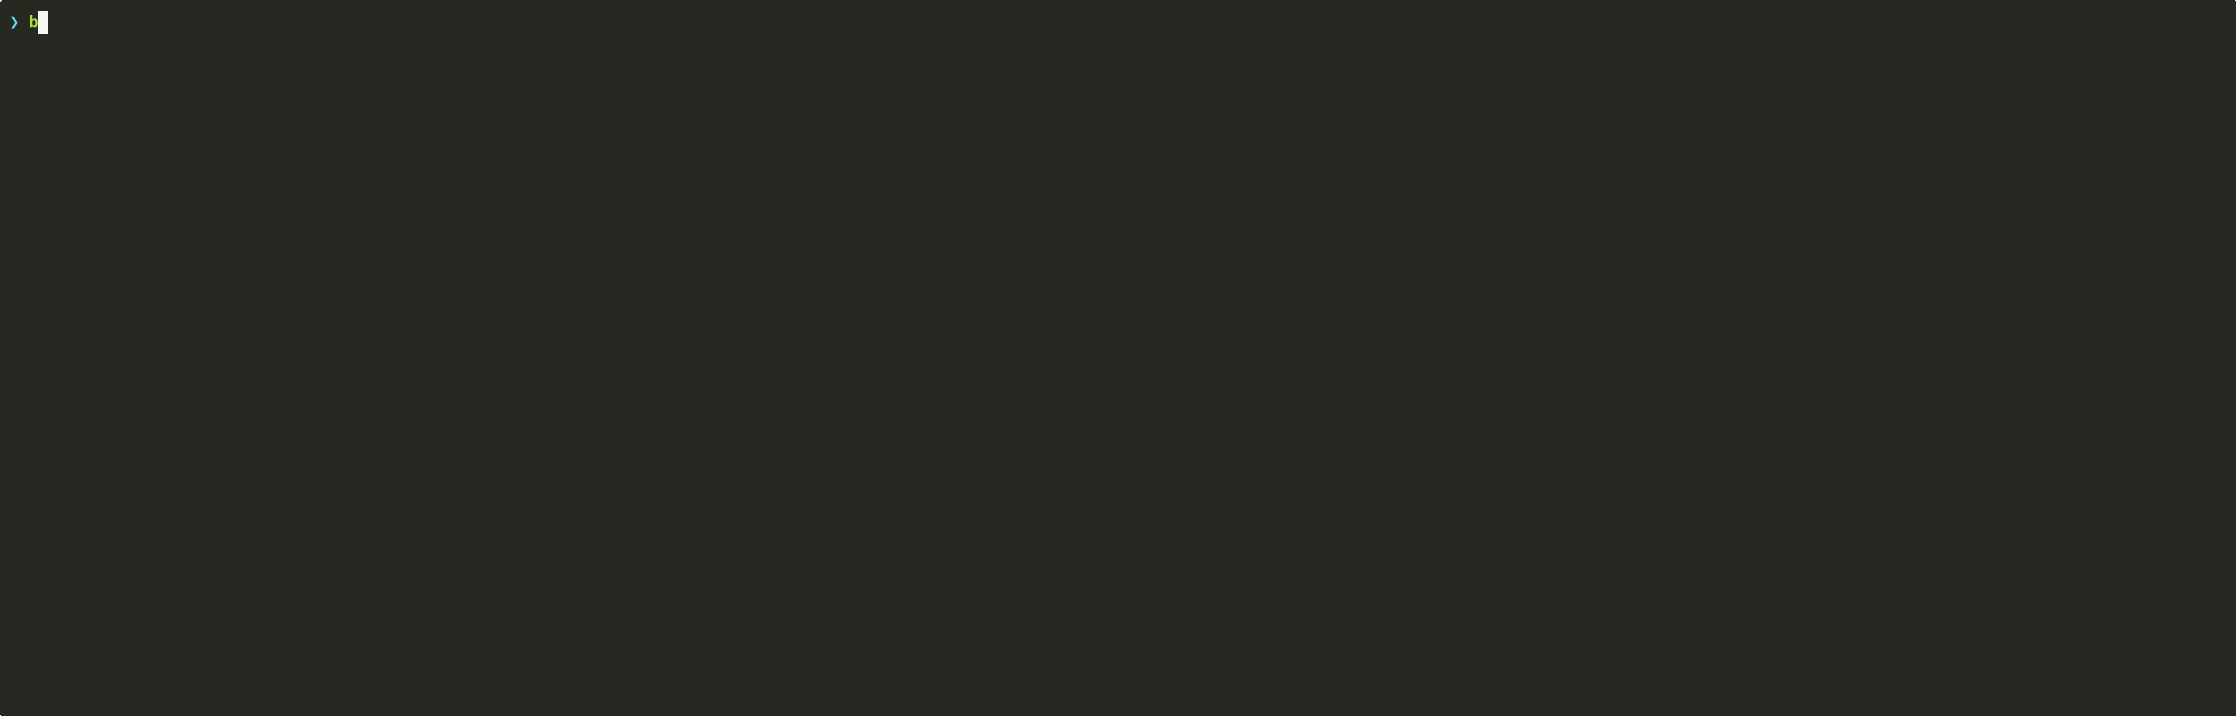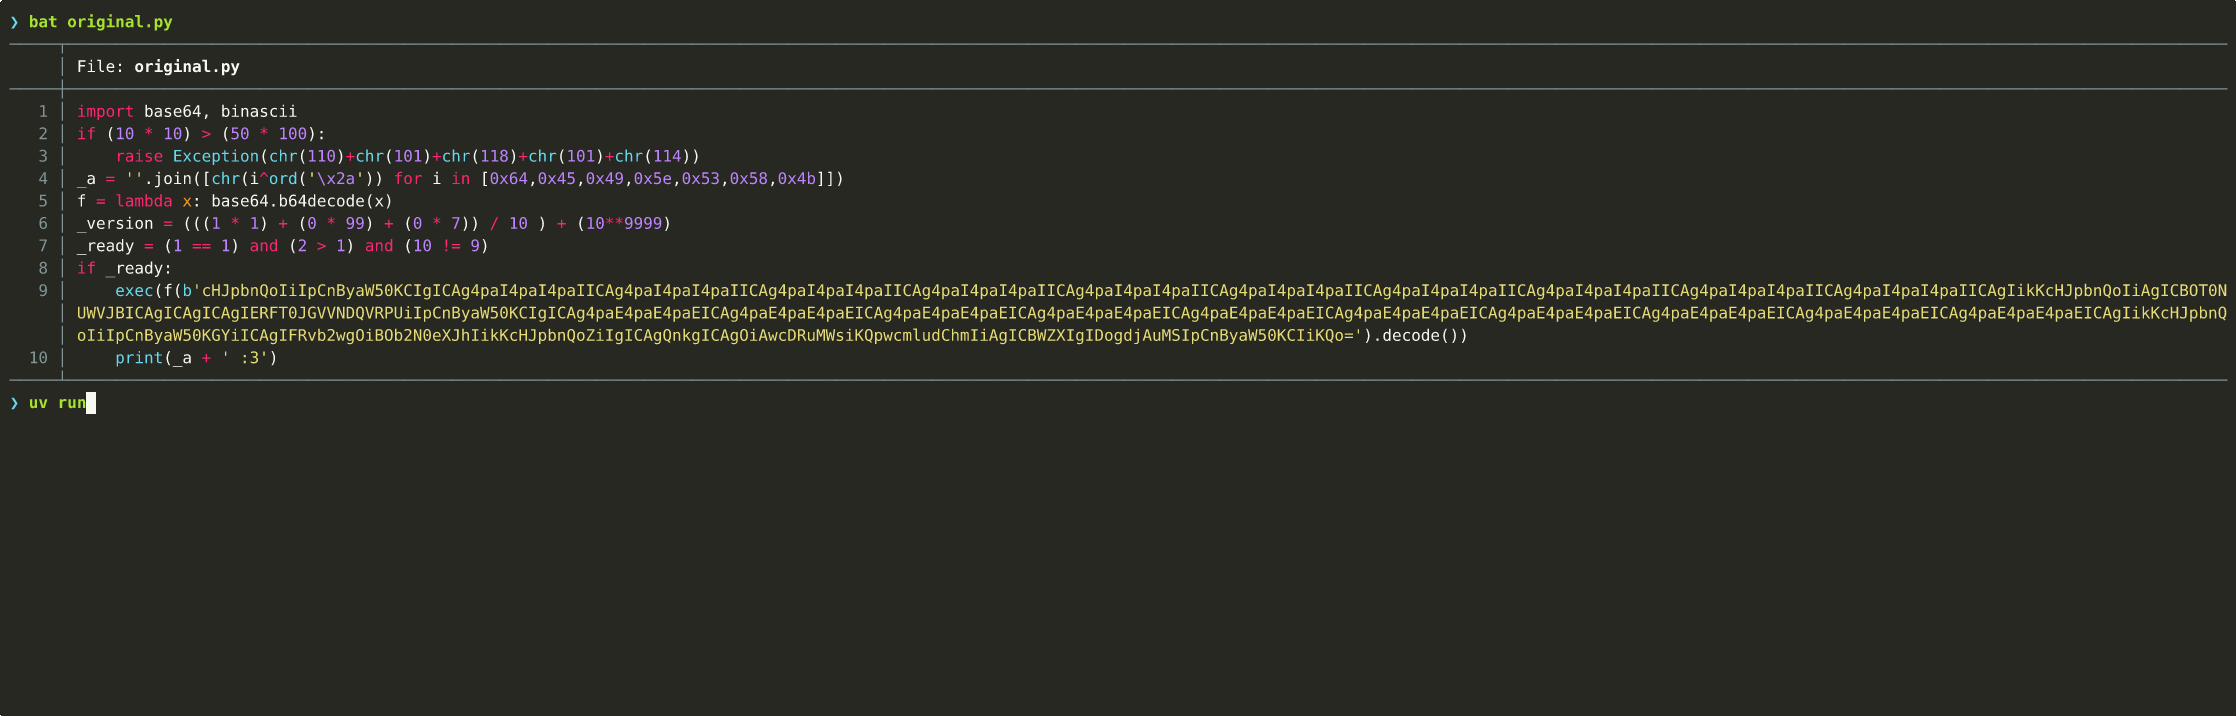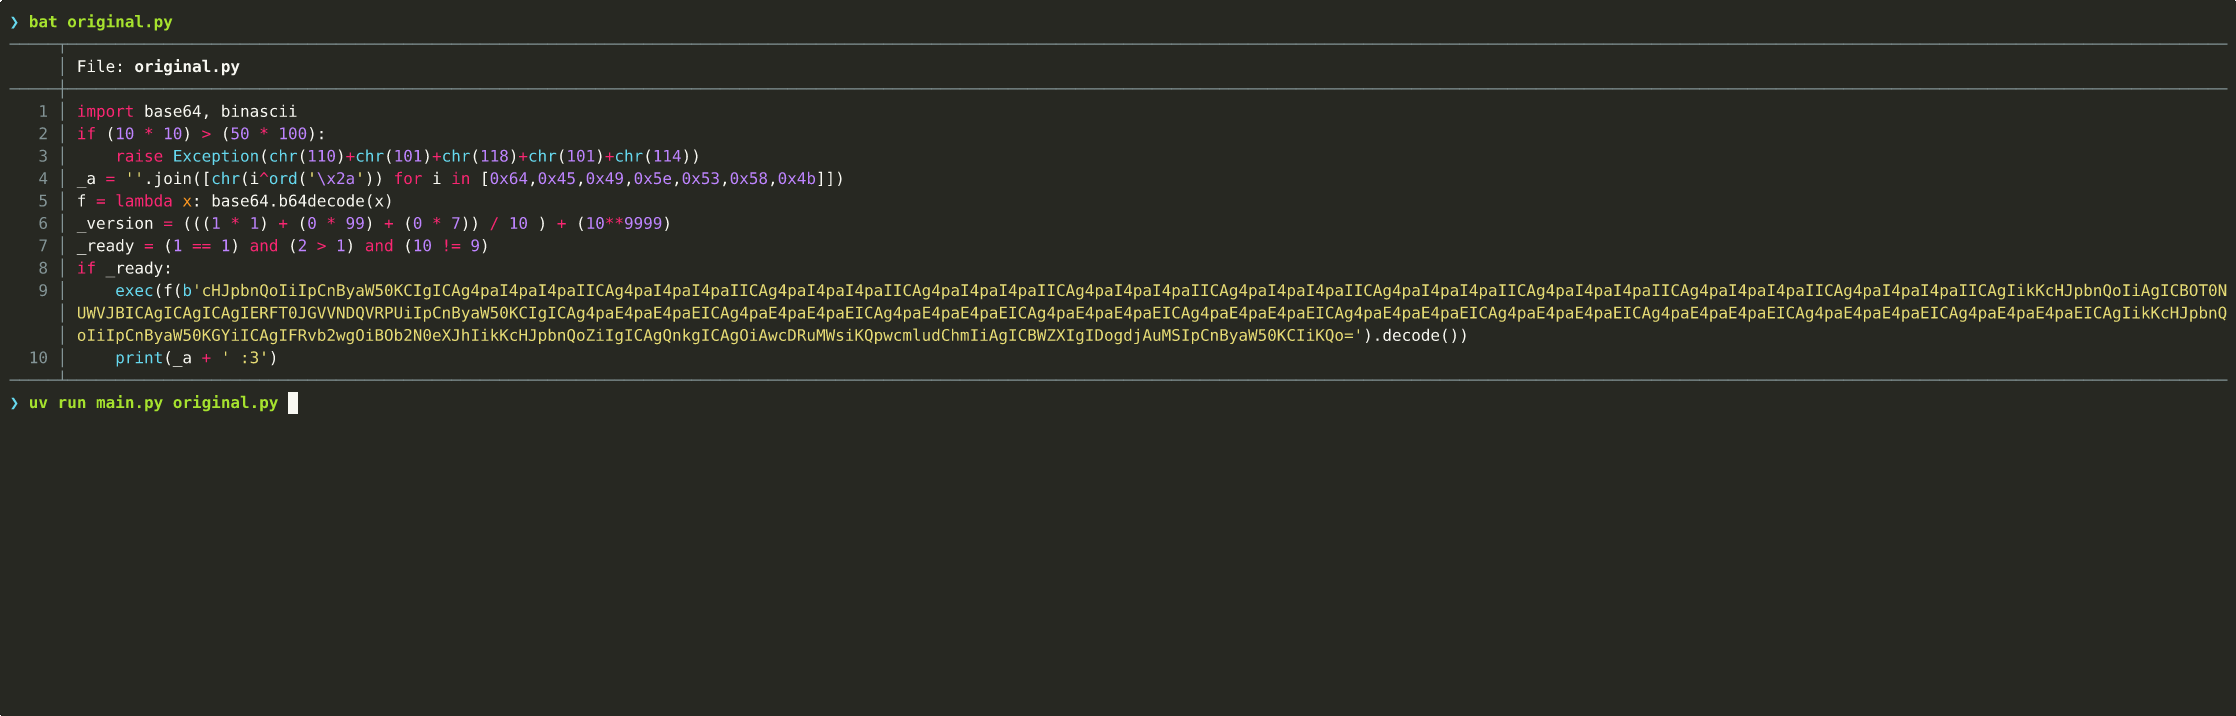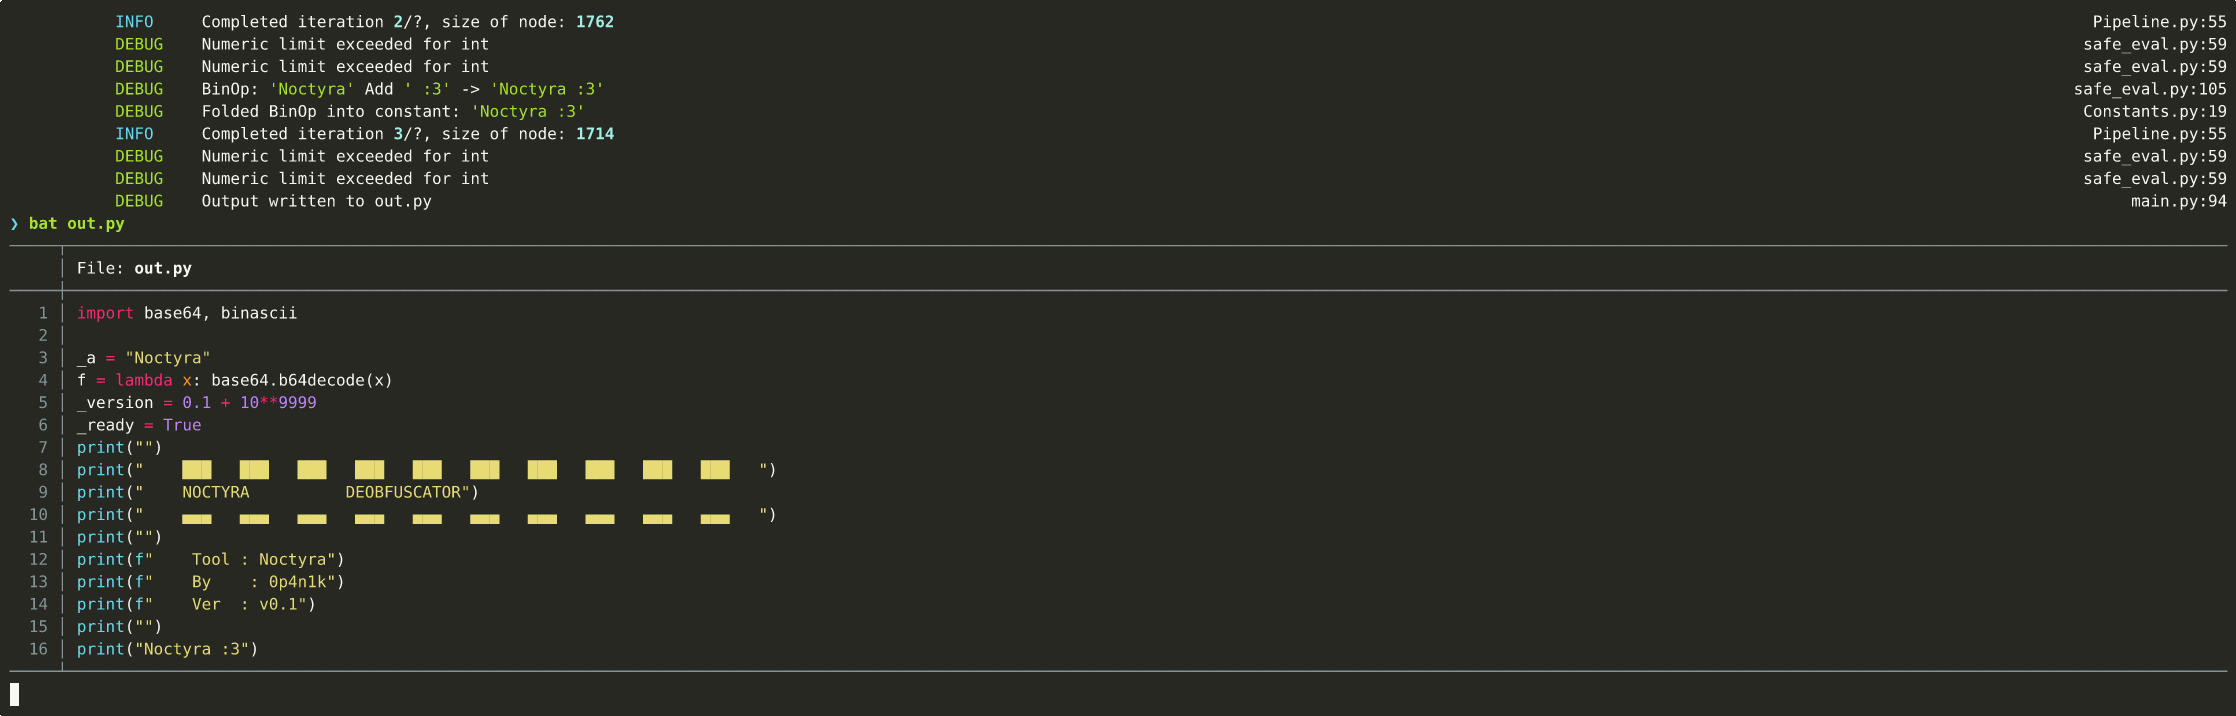 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
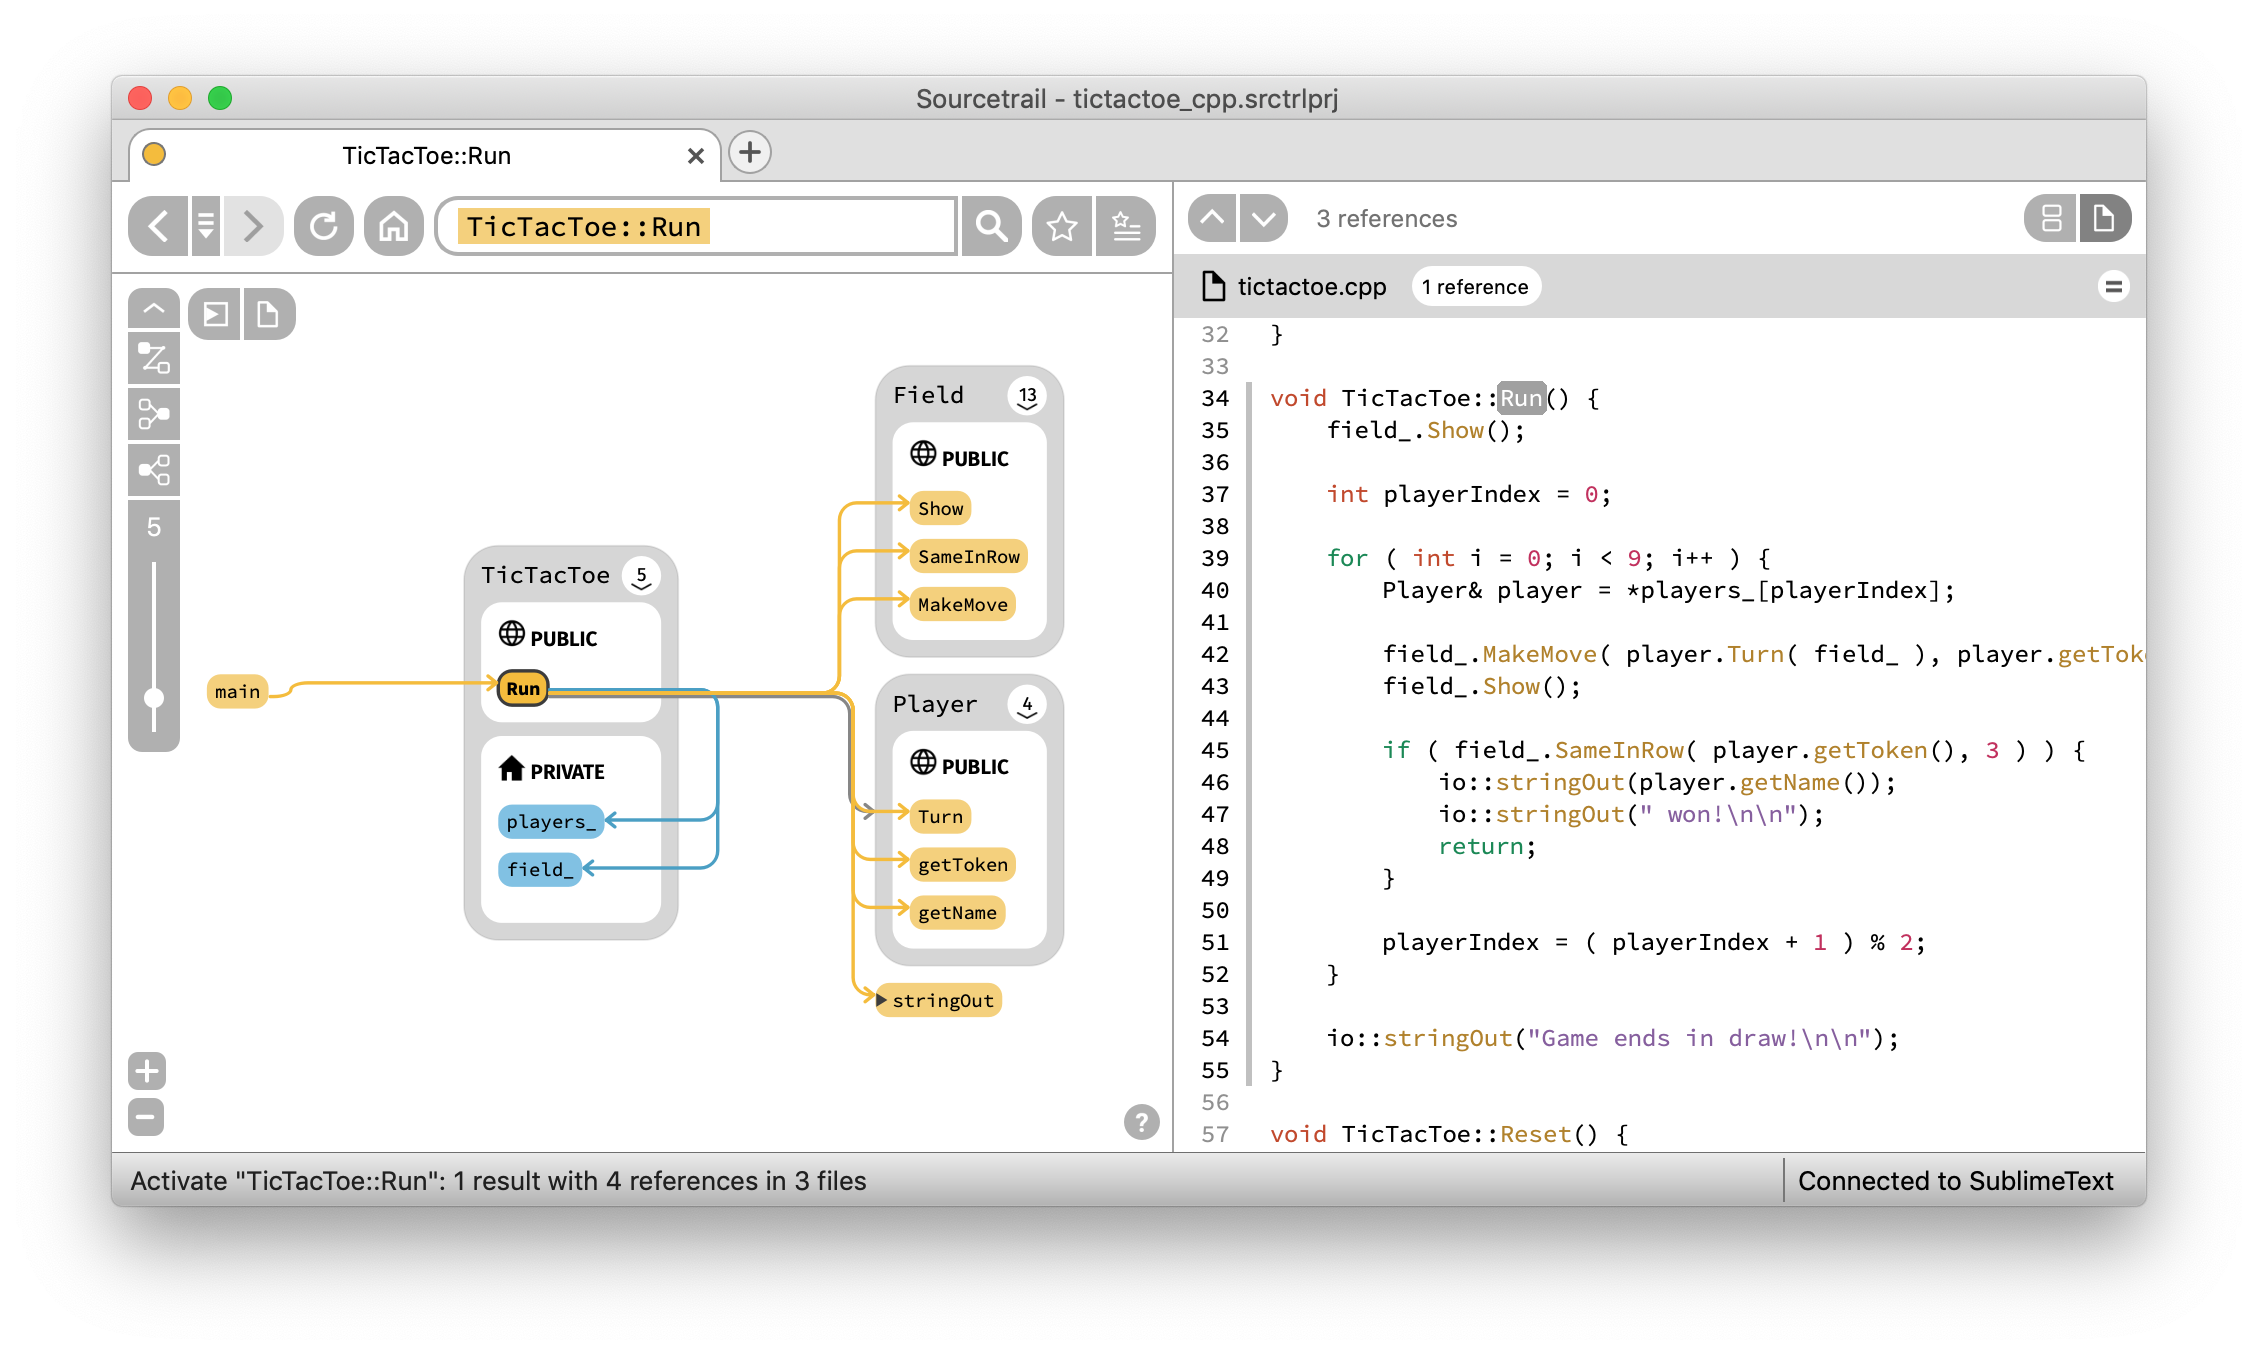 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.