

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
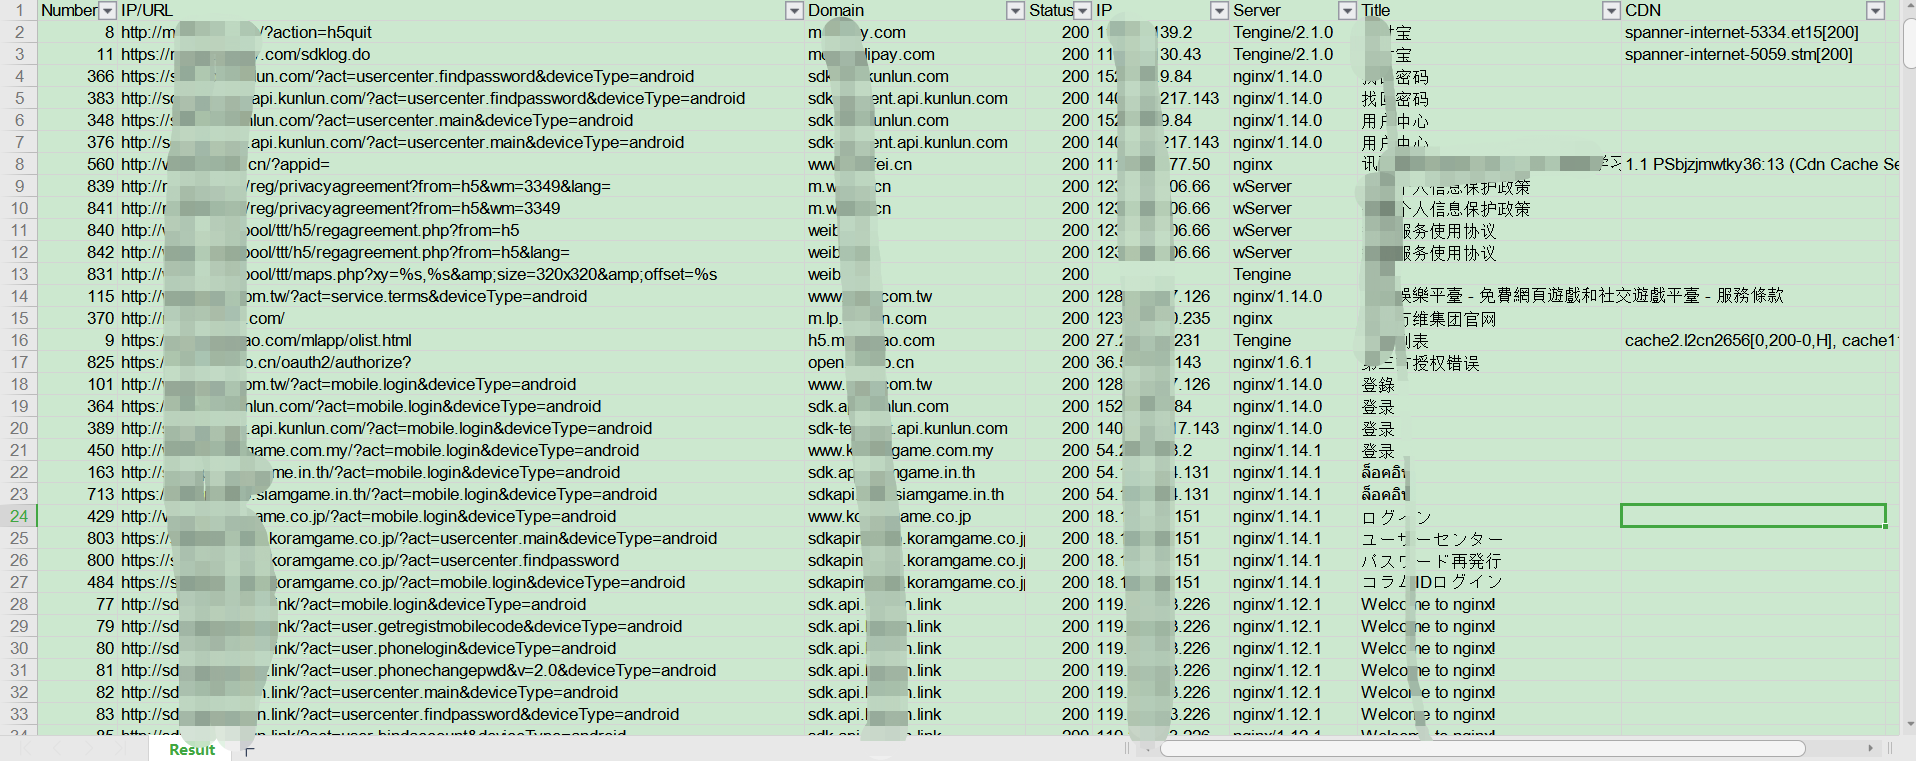 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
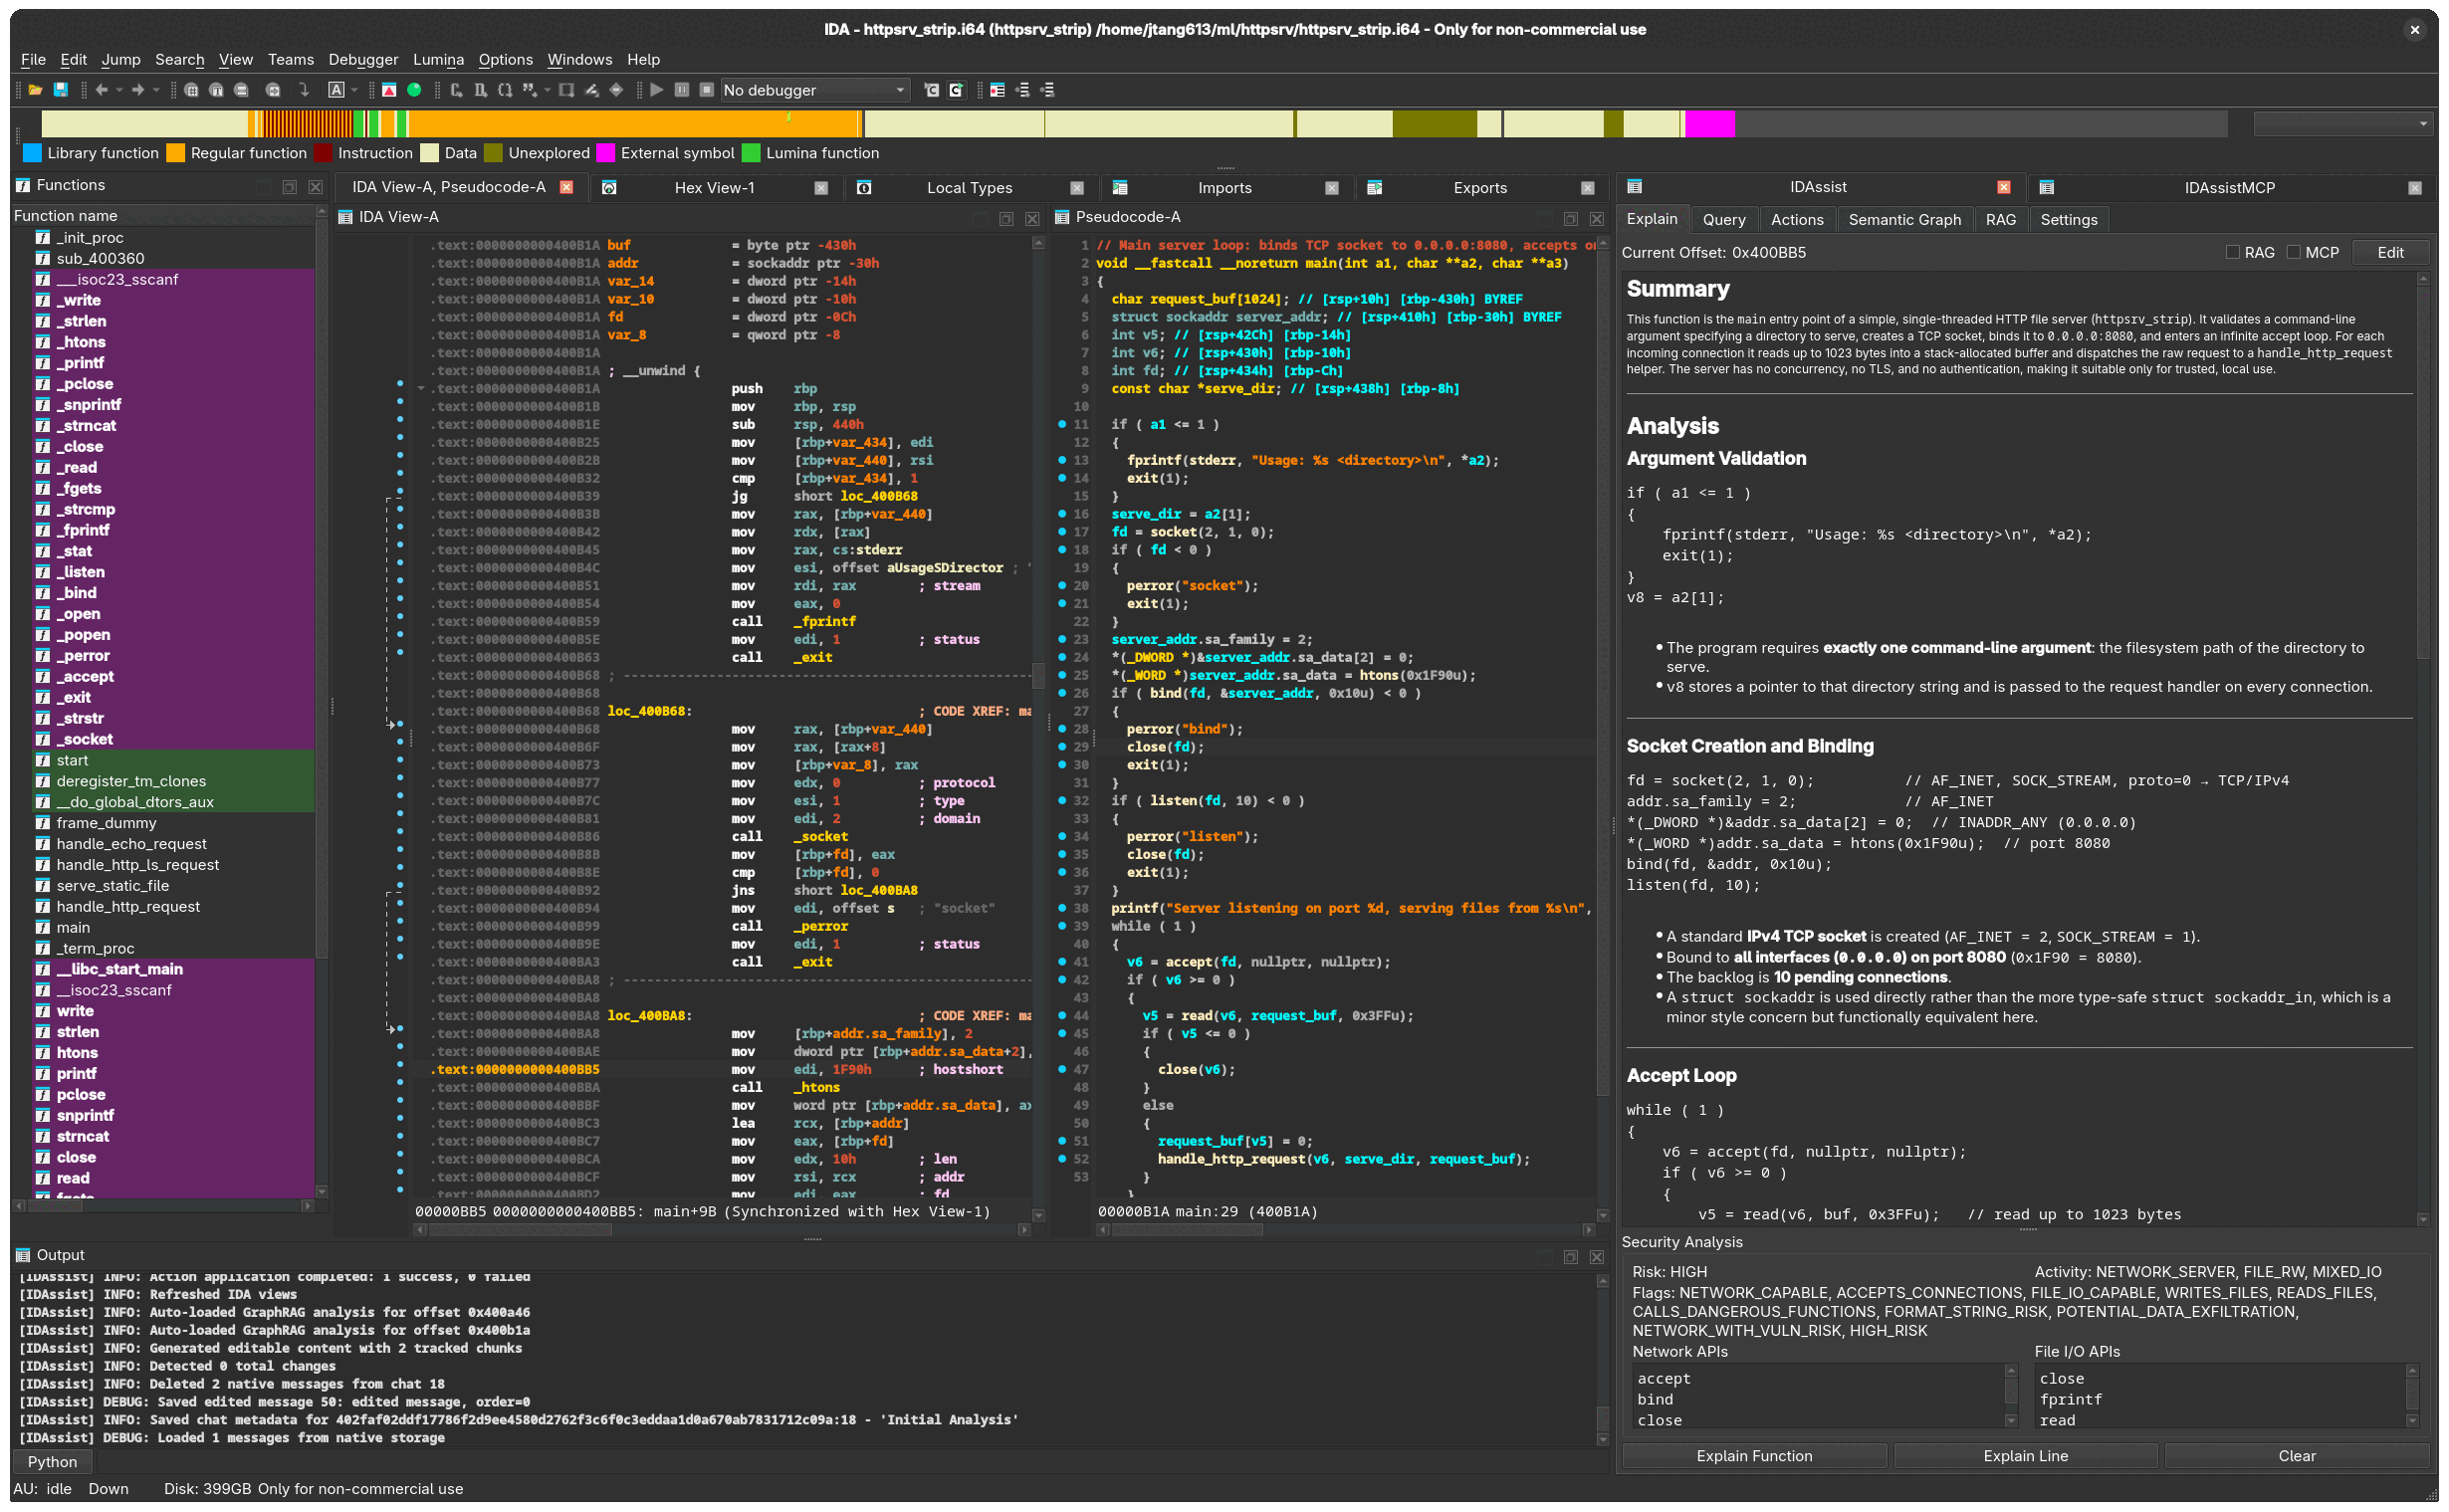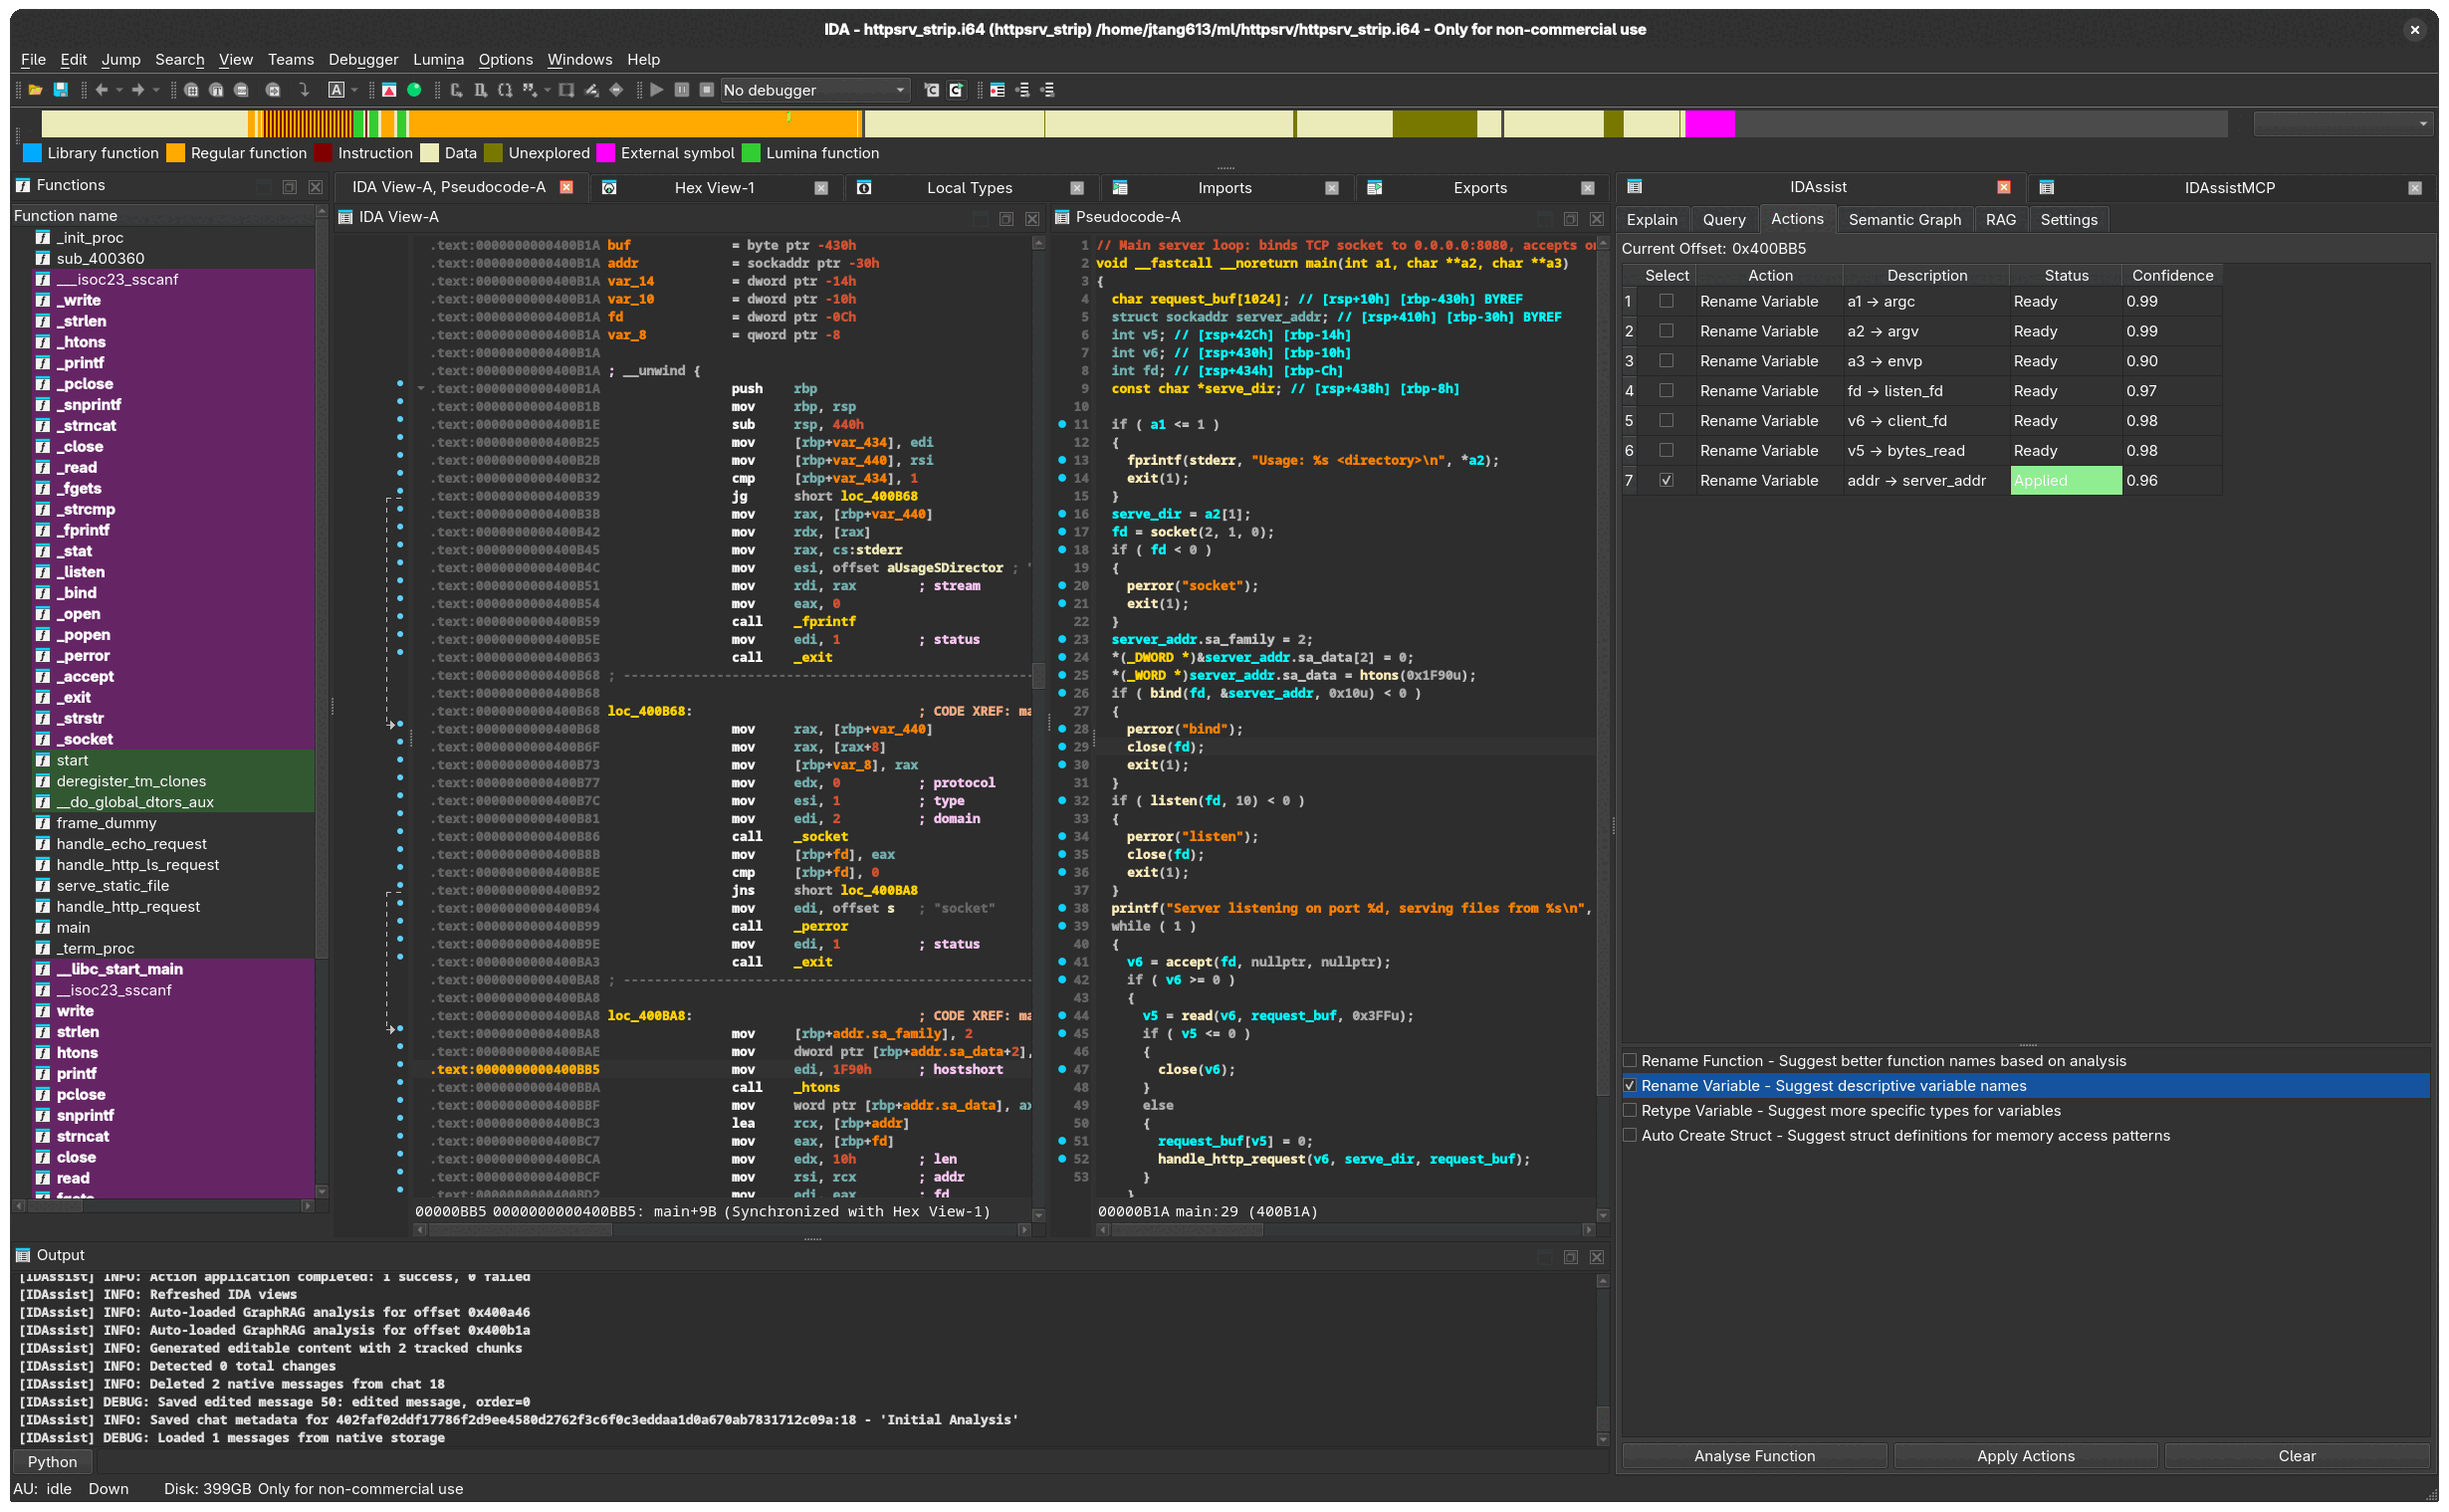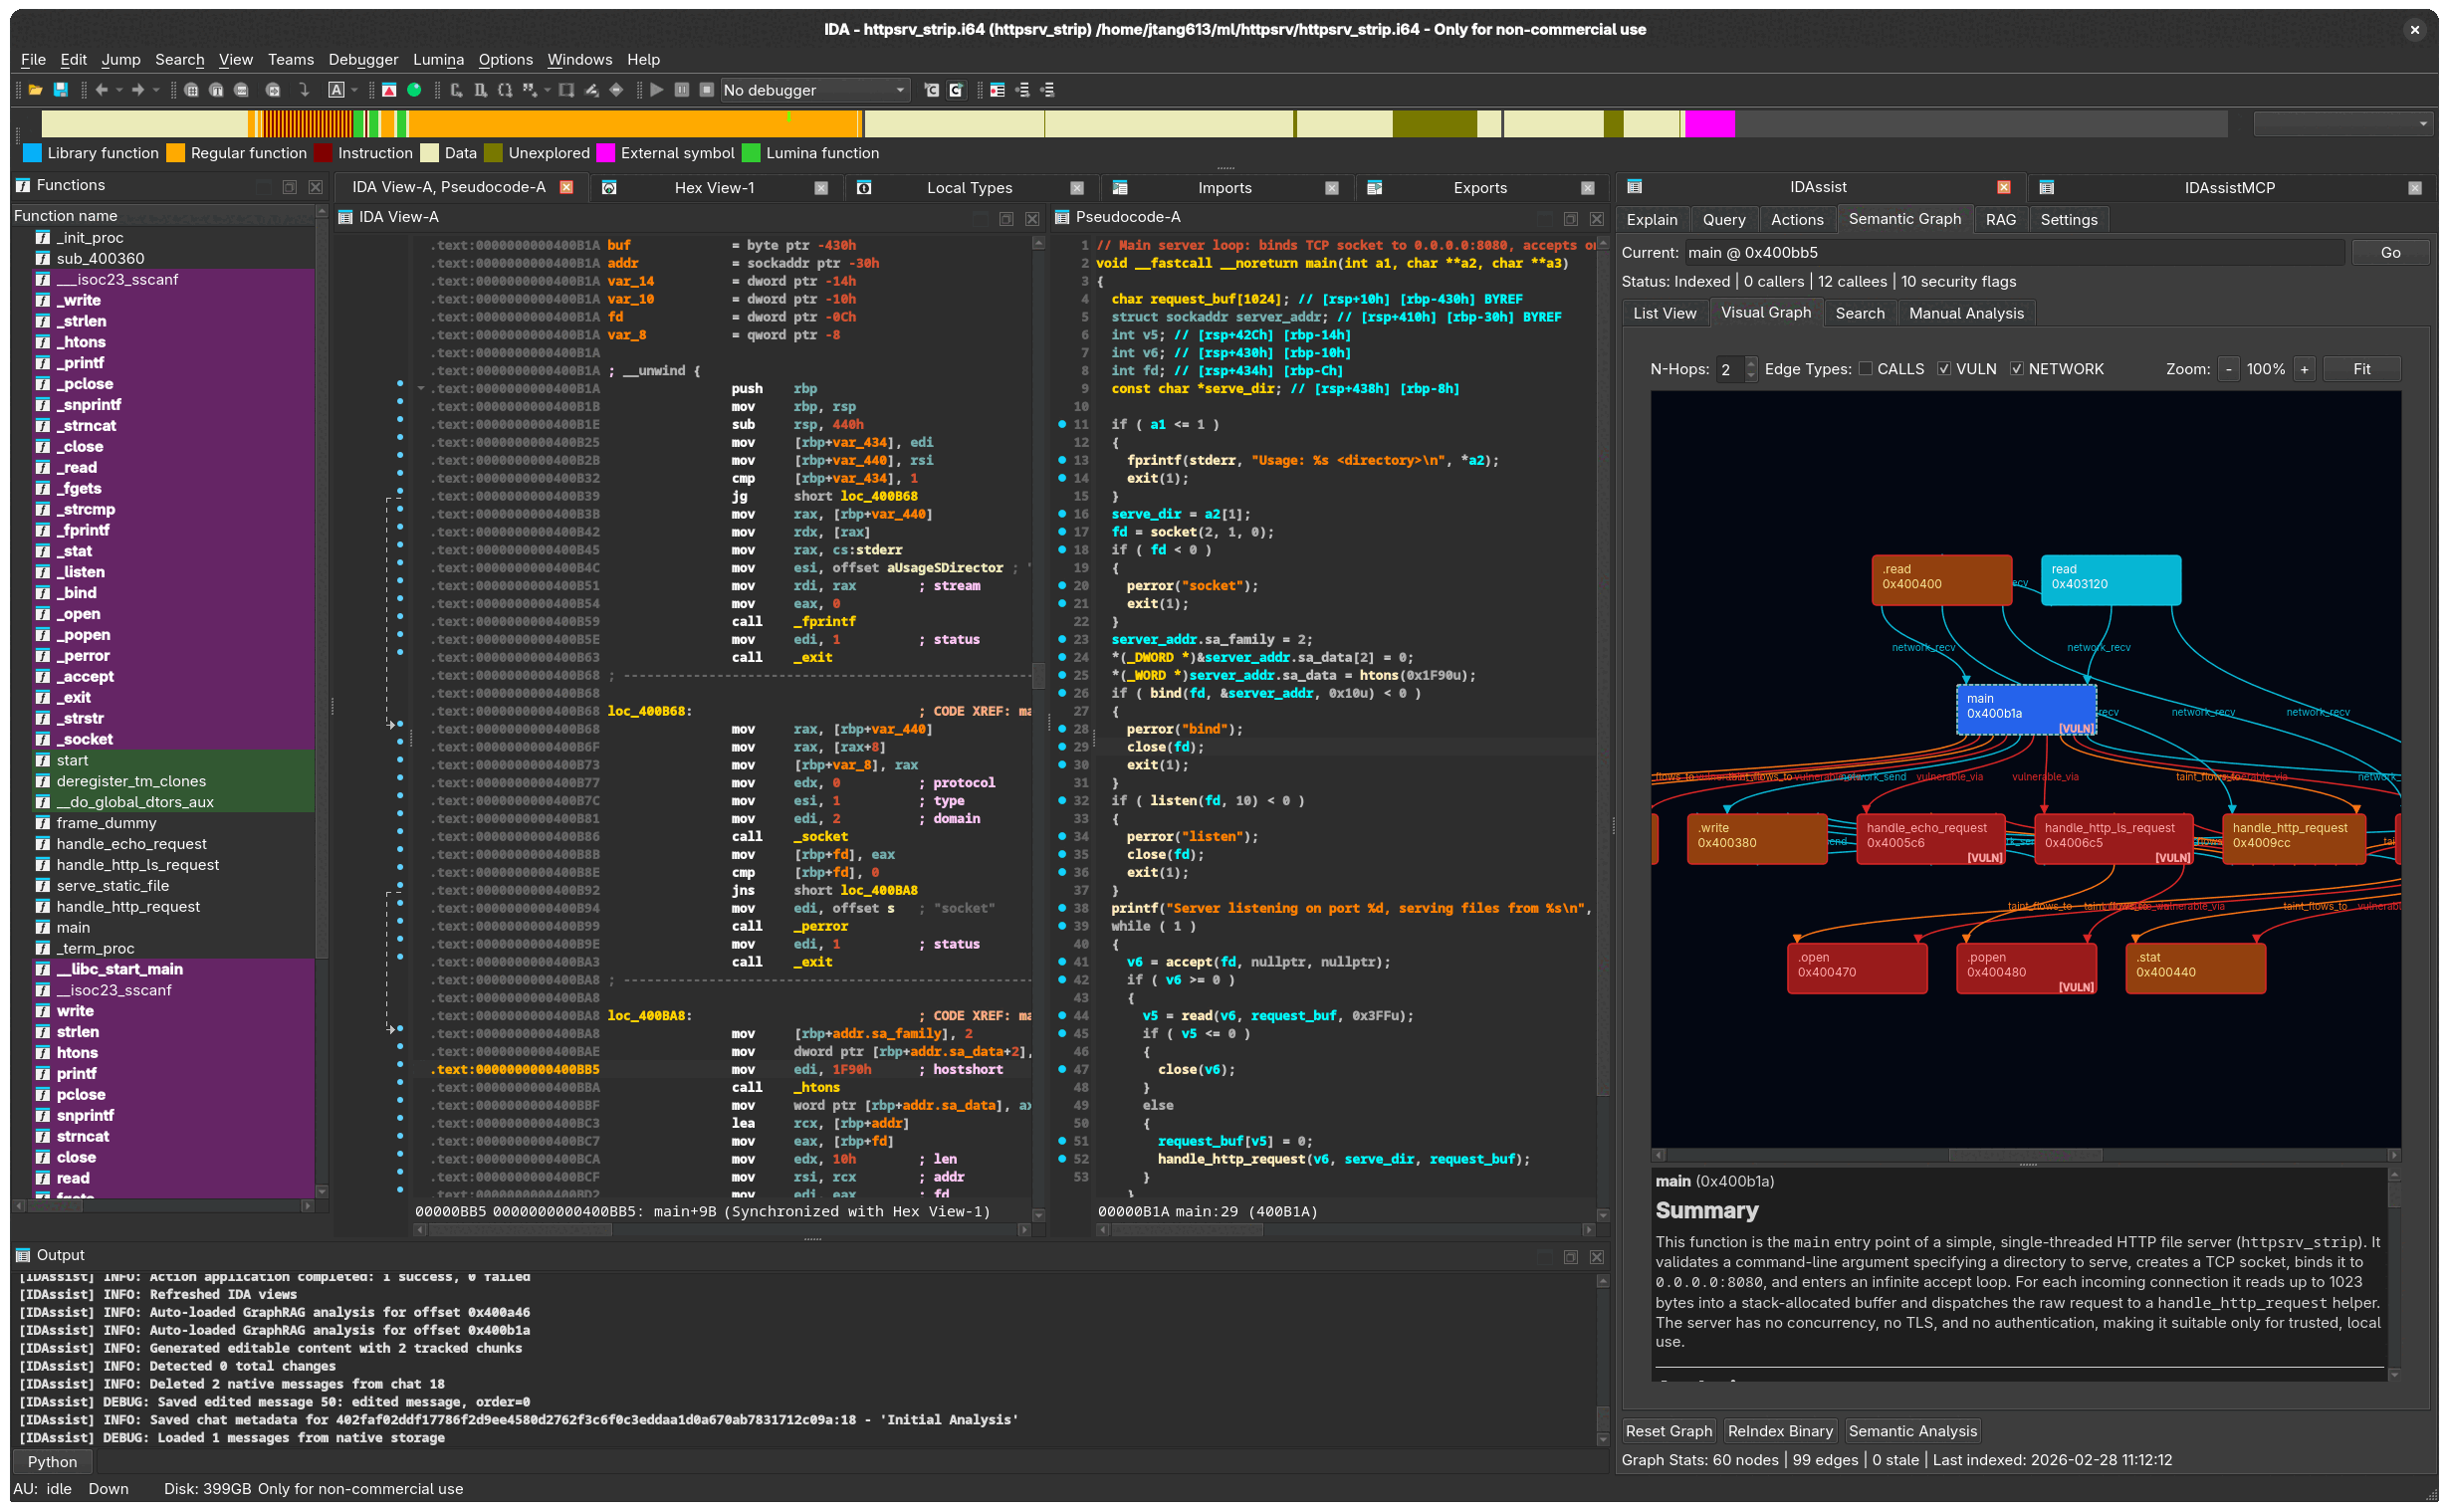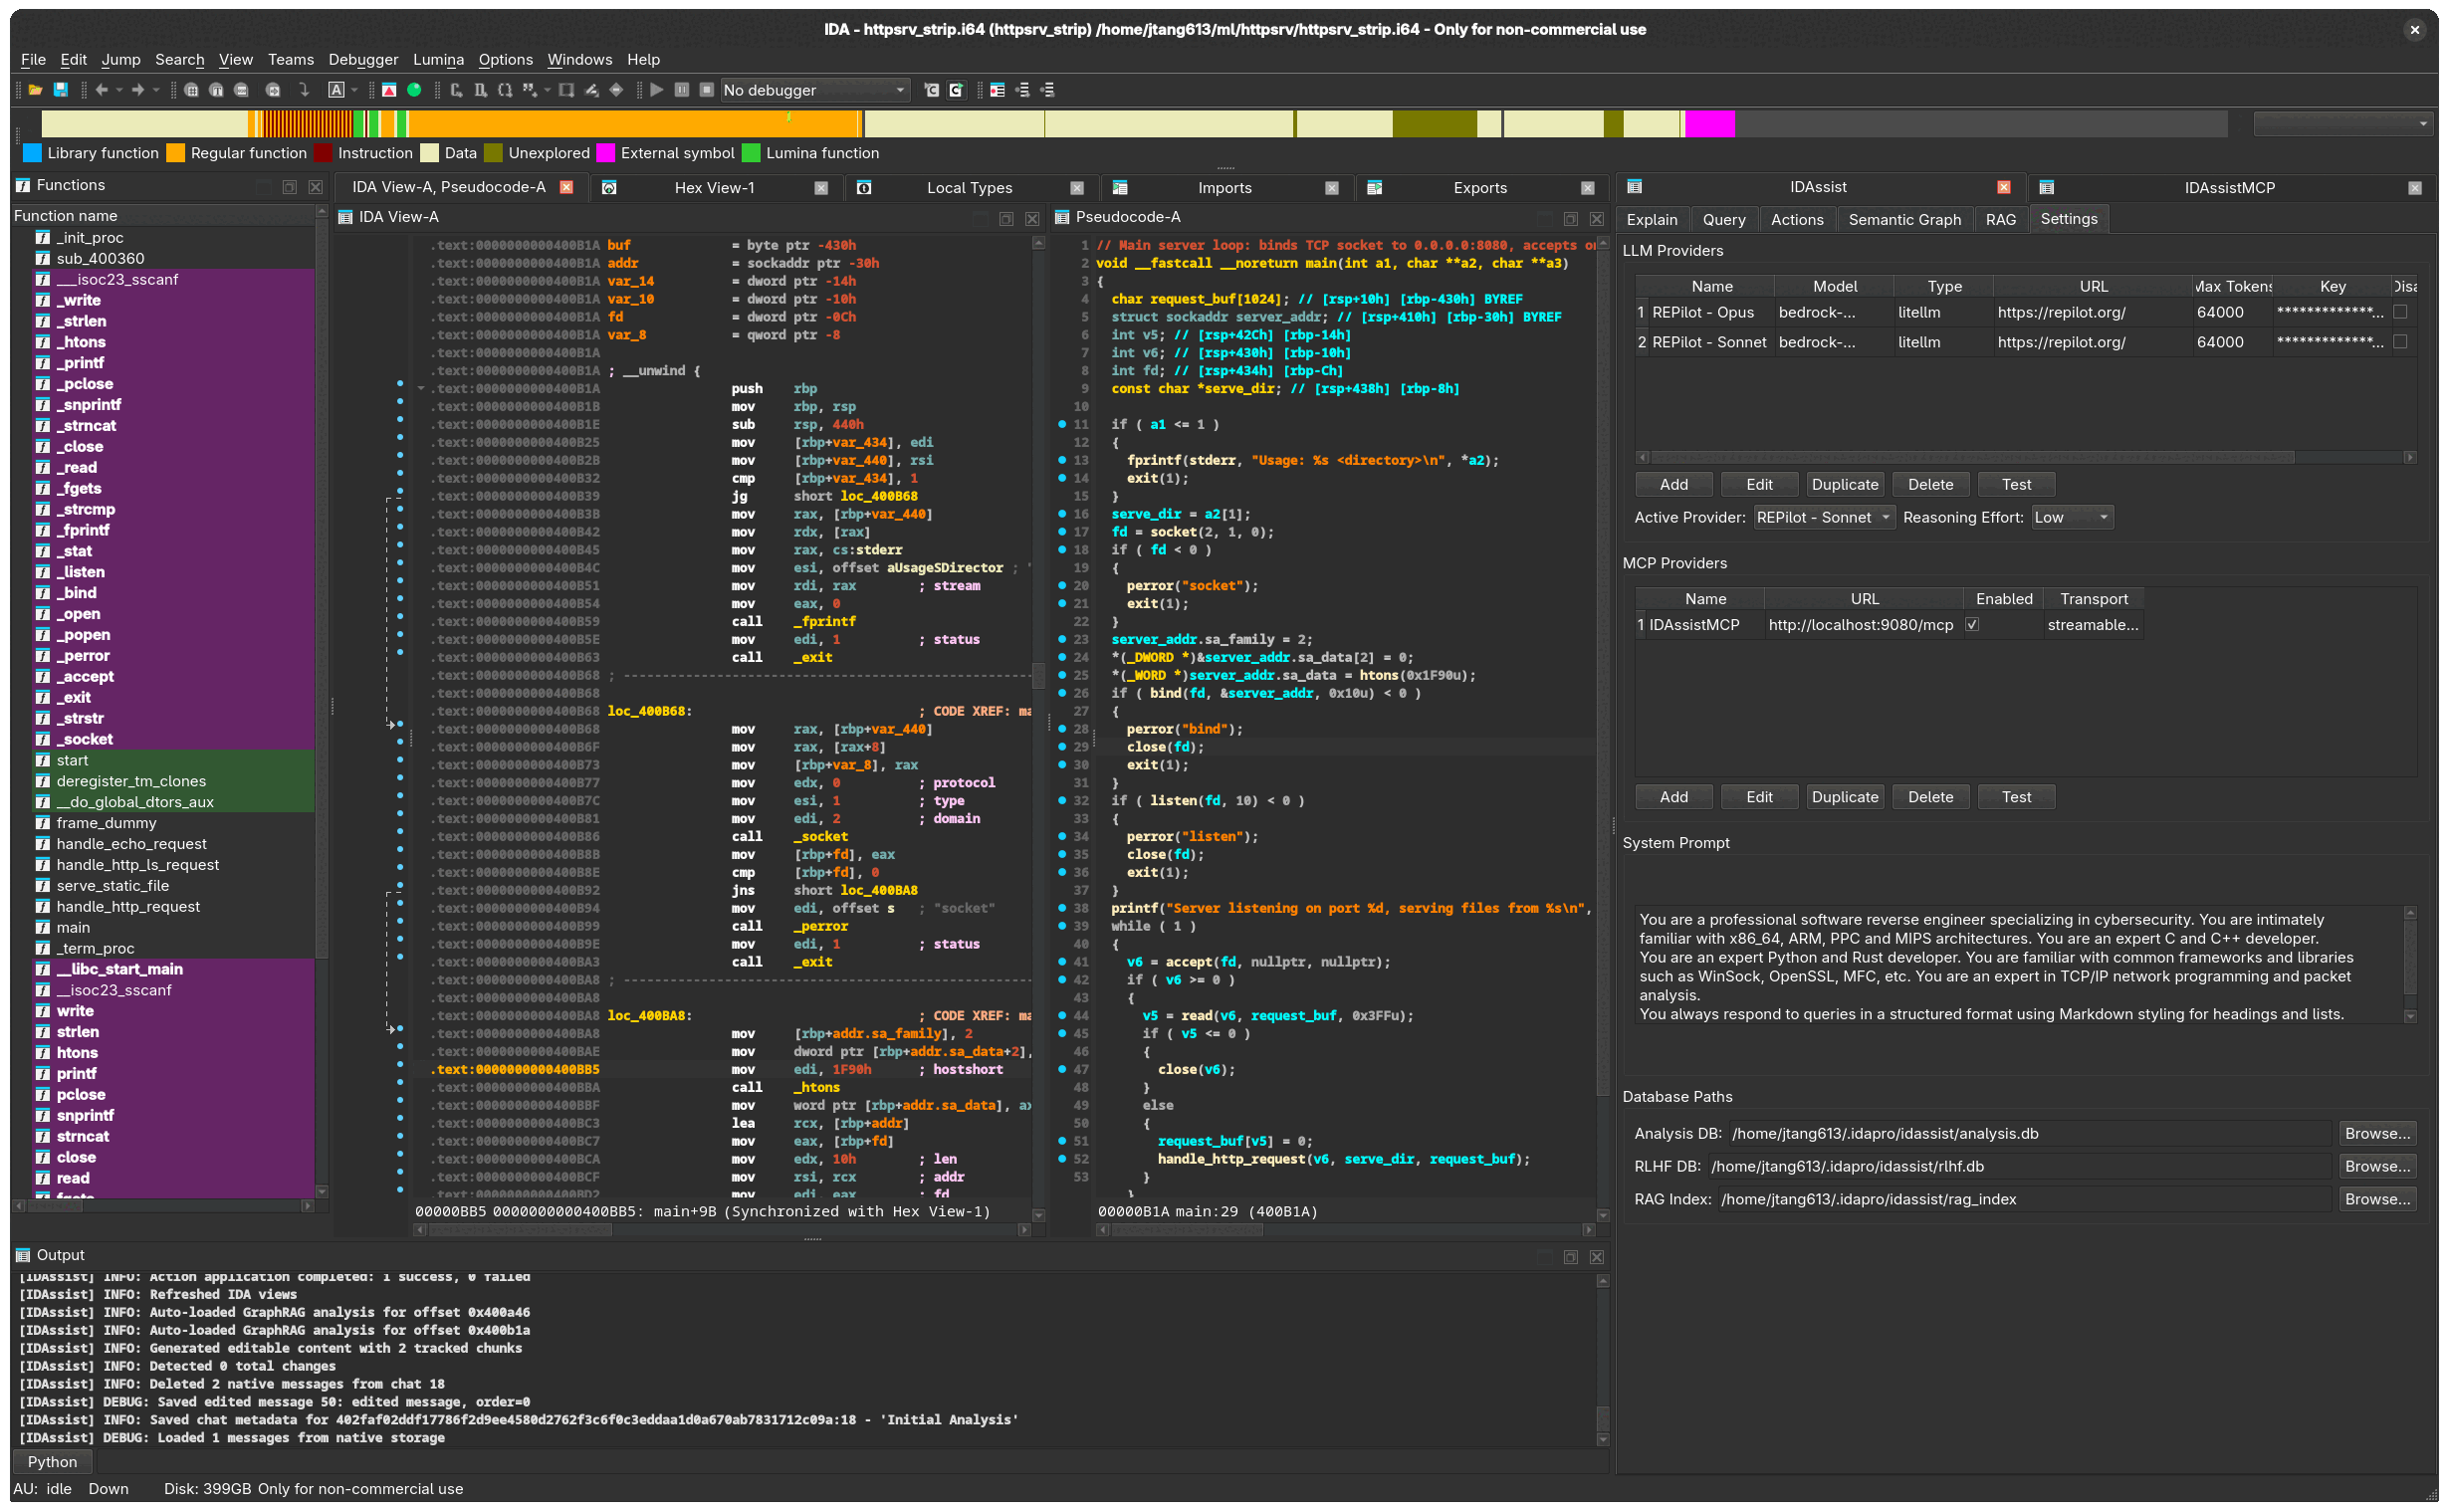 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
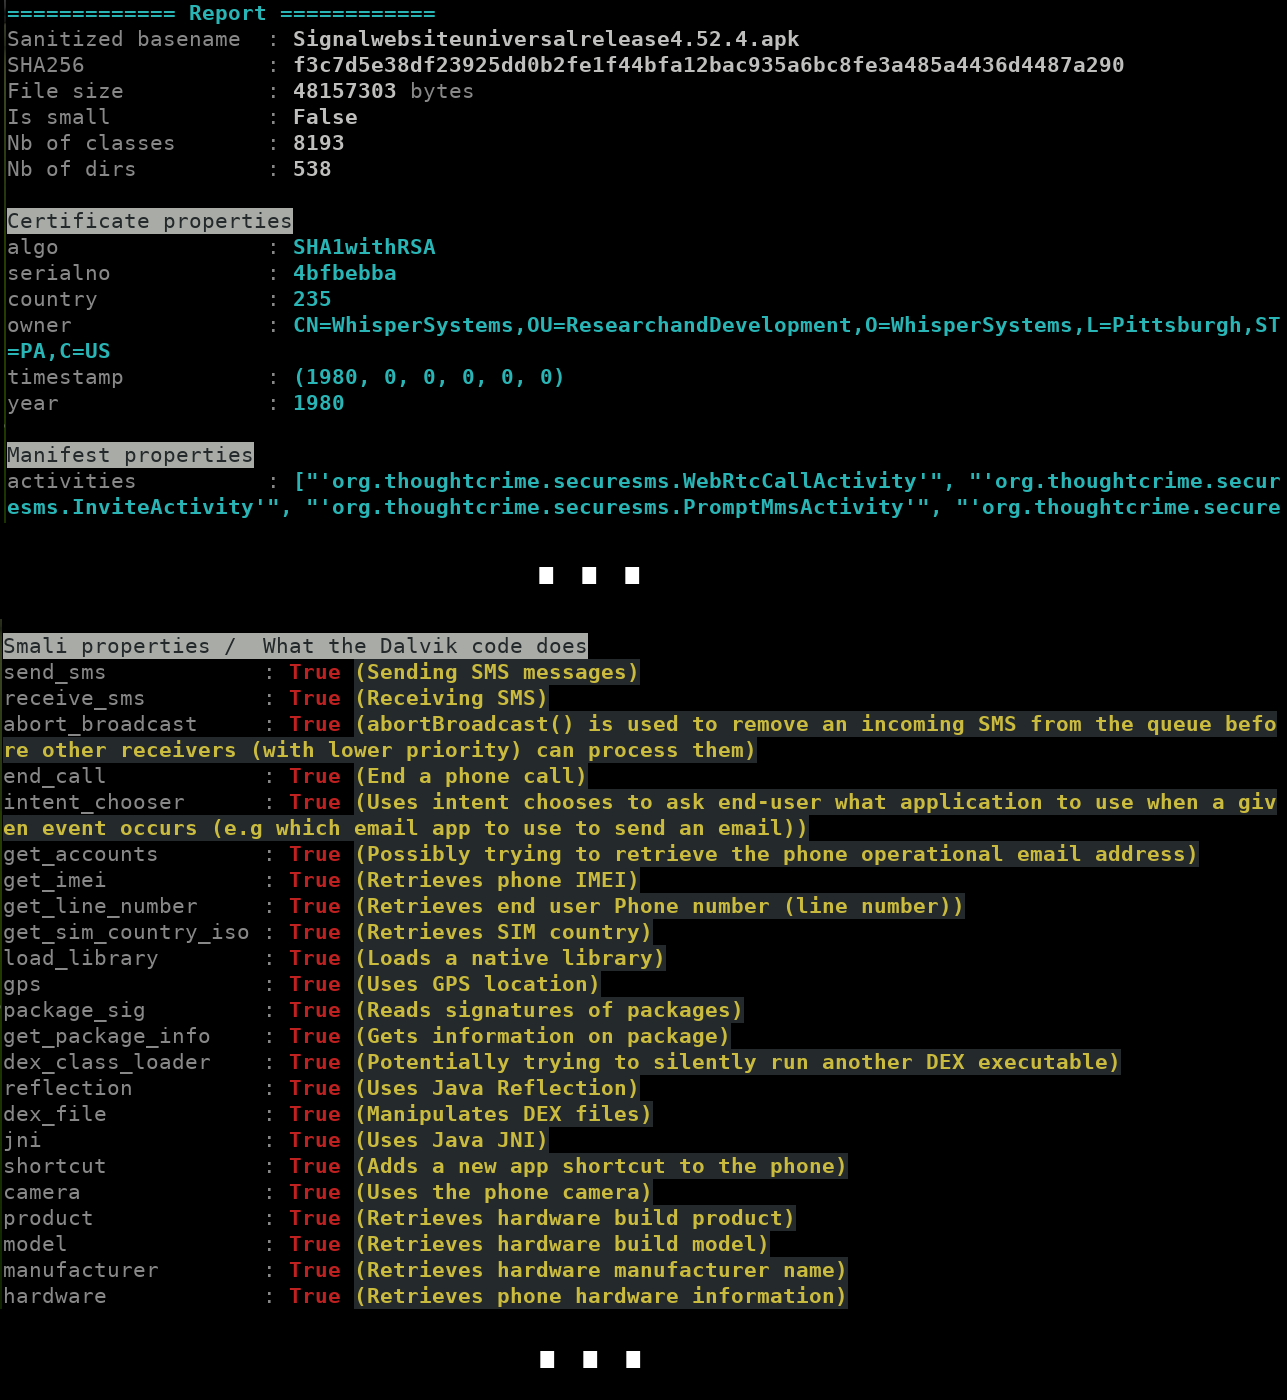 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 0xpwny/apkatshu
Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
 netspooky/inhale
A malware analysis and classification tool.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
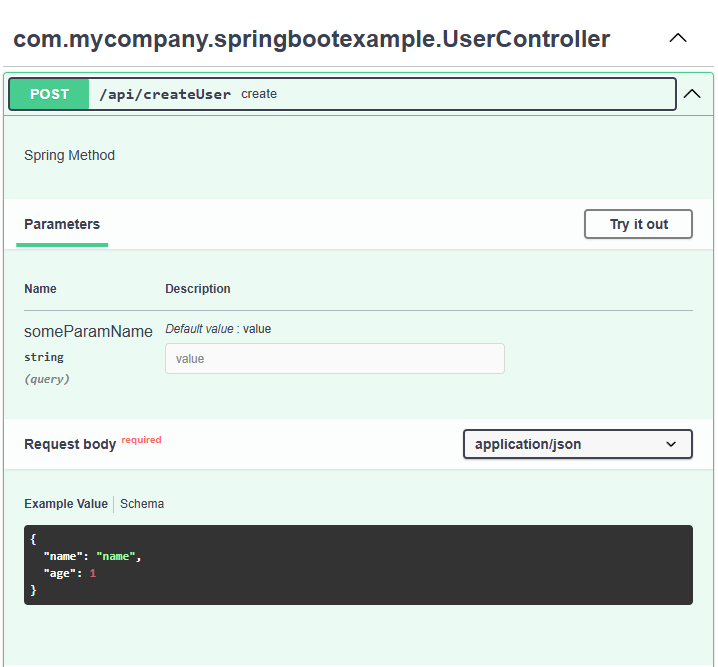 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 elevenpaths/neto
Neto | A tool to analyse browser extensions