
noir
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
api-securitydevsecopspenetration-testing+3
1.4k5 days ago
owasp-noir/noirHunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 mobsf/mobsfscan
mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…
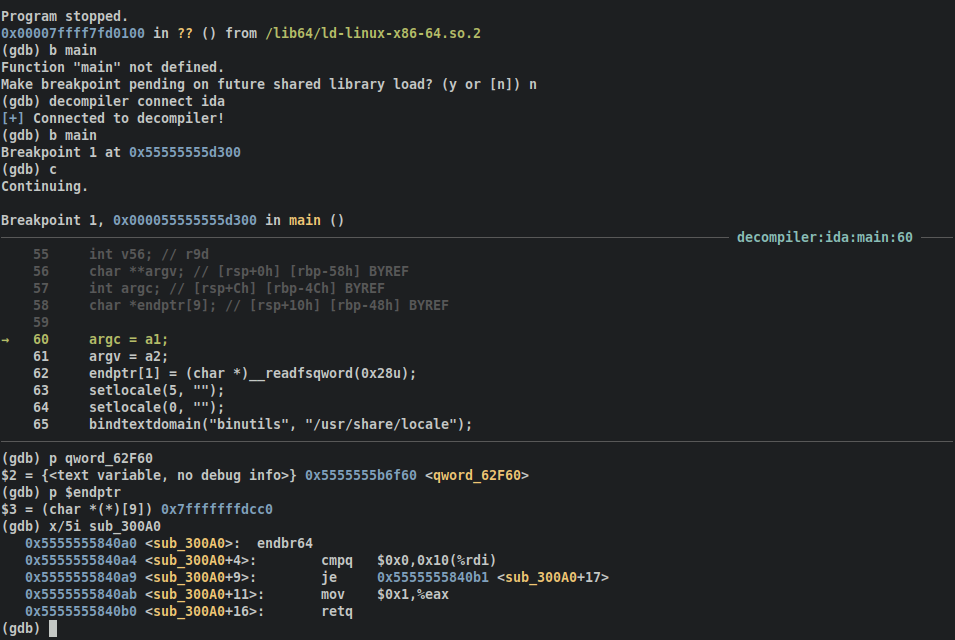 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 globocom/huskyci
Performing security tests inside your CI
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 cert-polska/malduck
🦆 Malduck is your ducky companion in malware analysis journeys
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
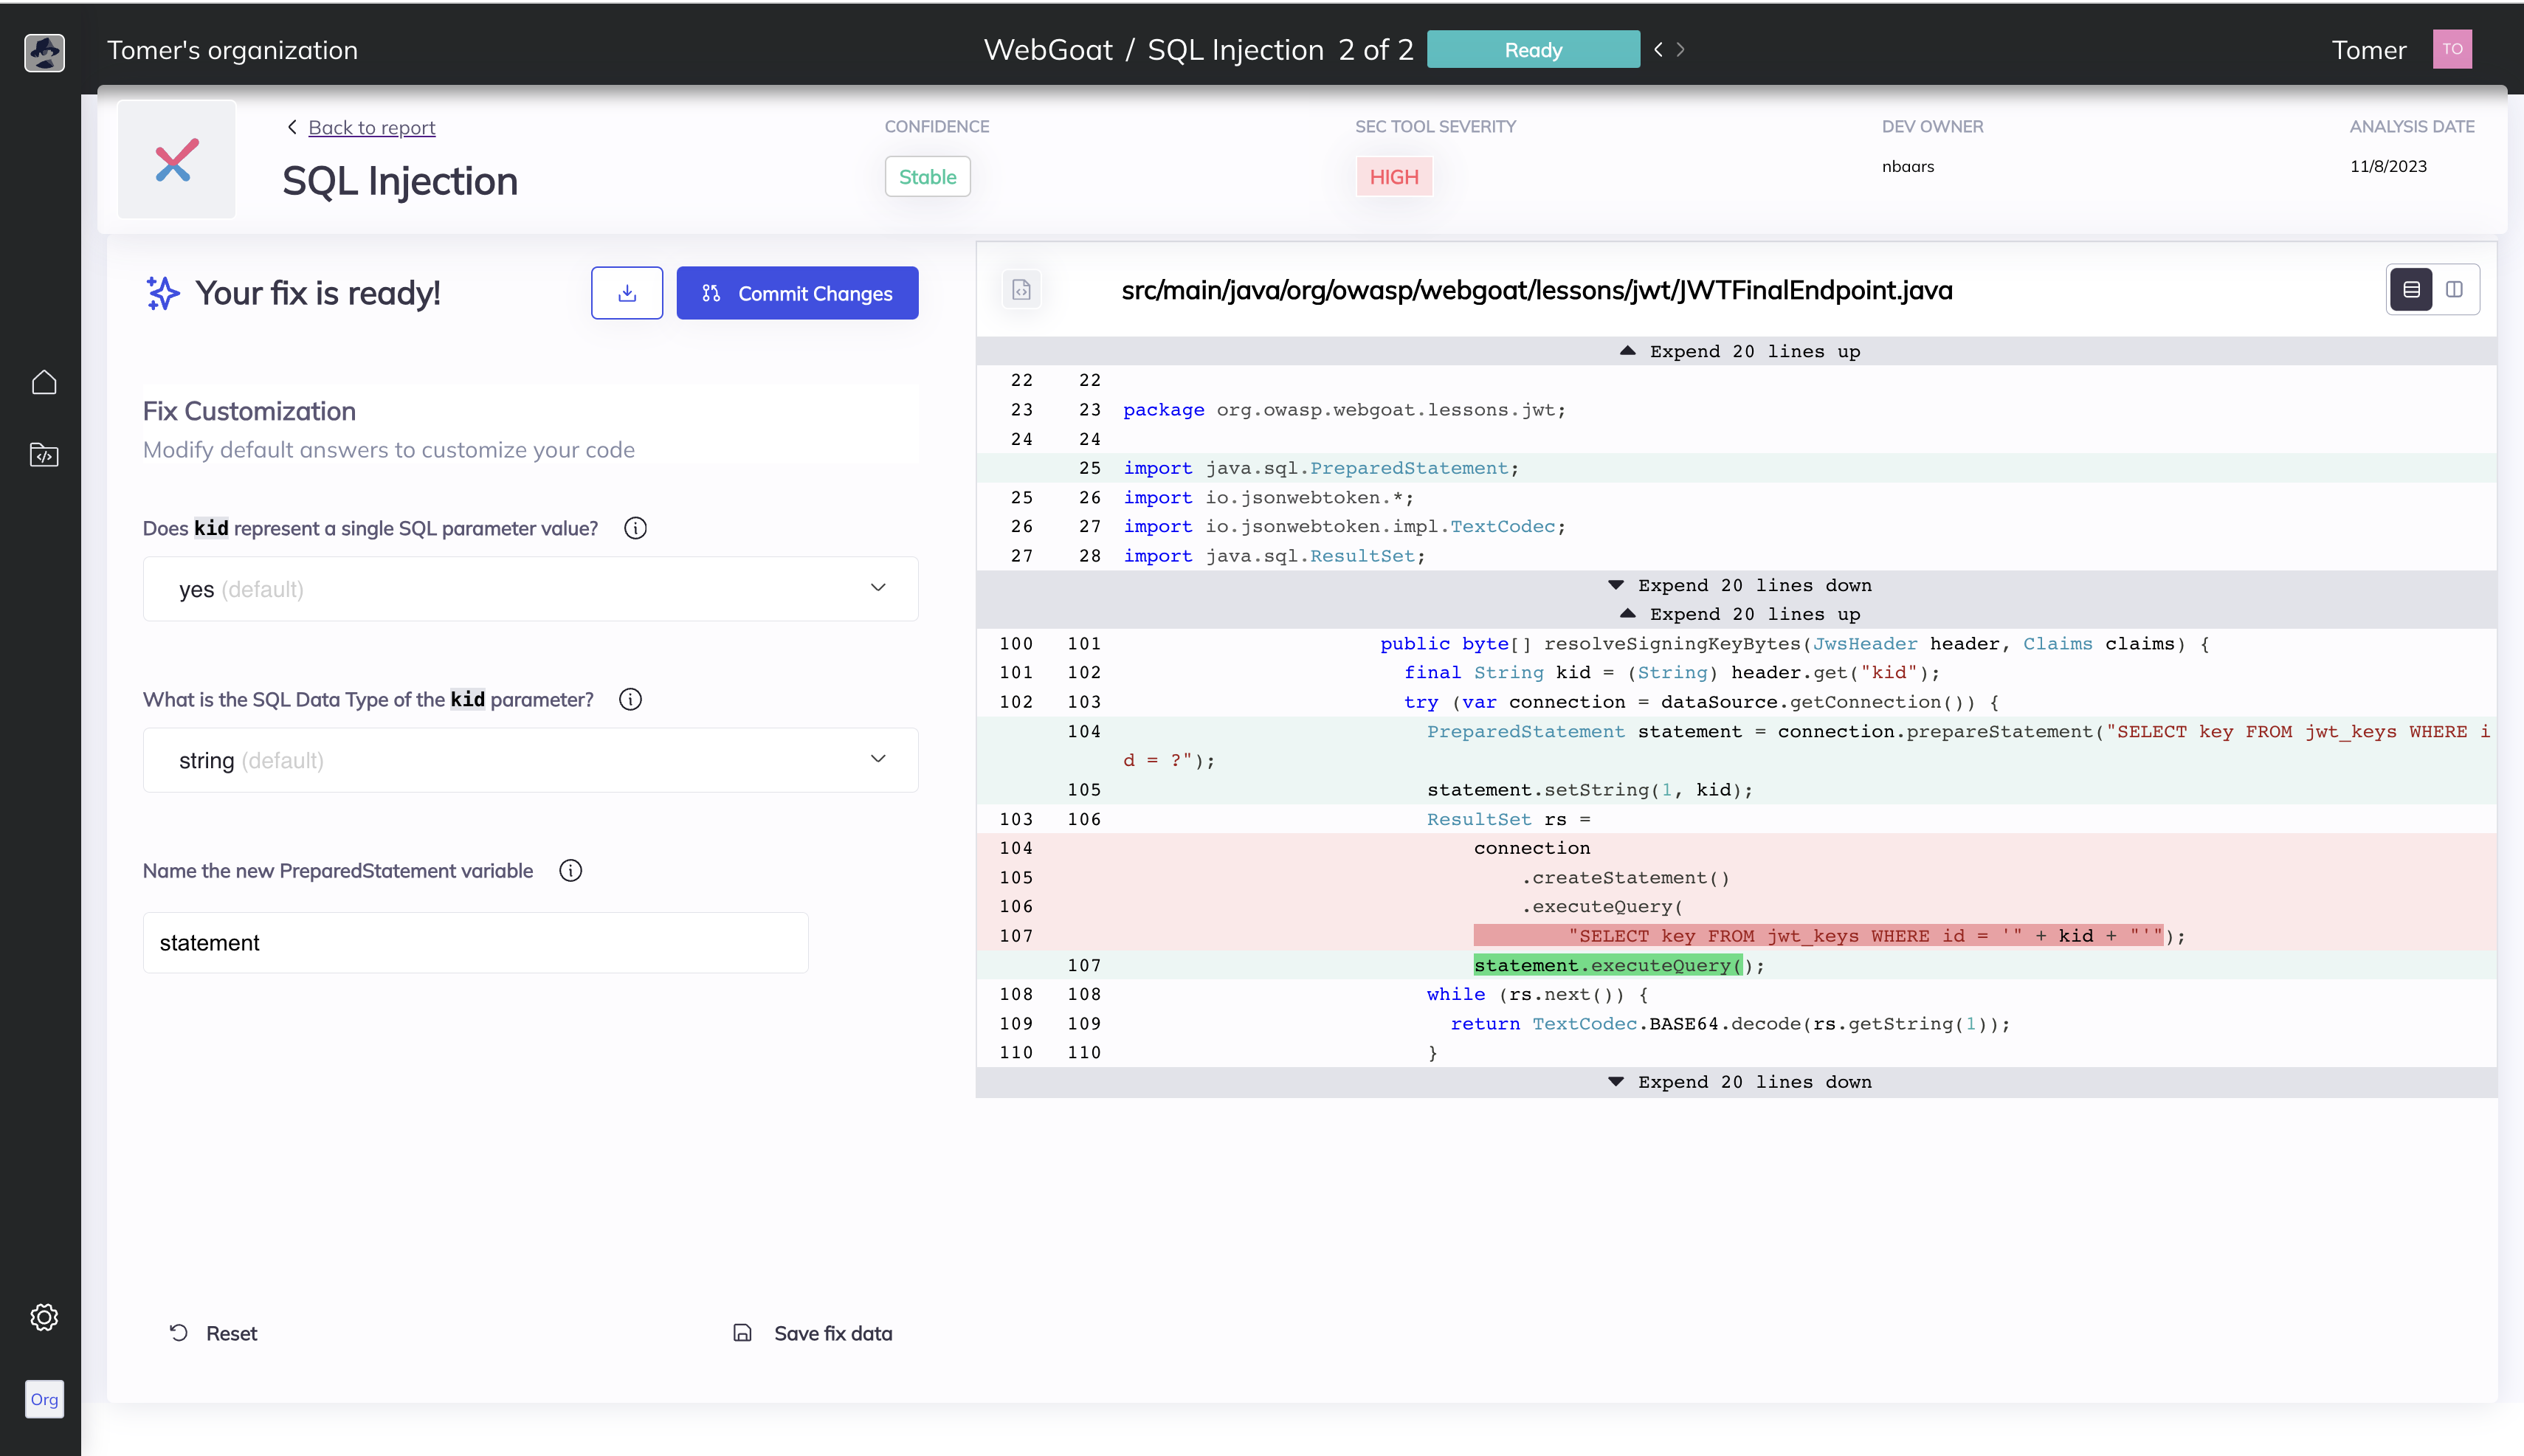 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
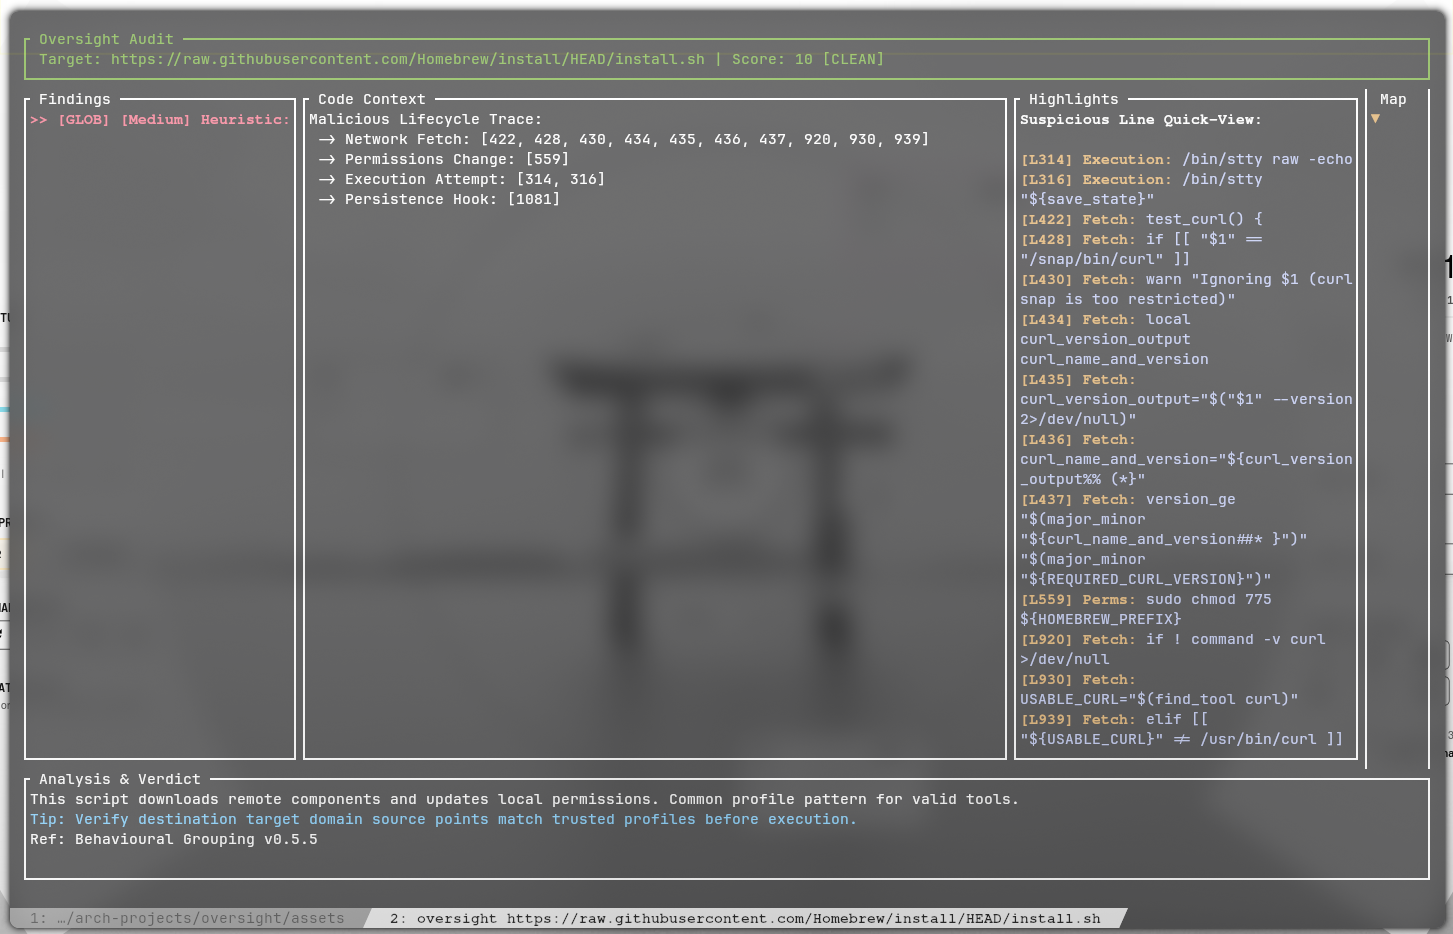 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
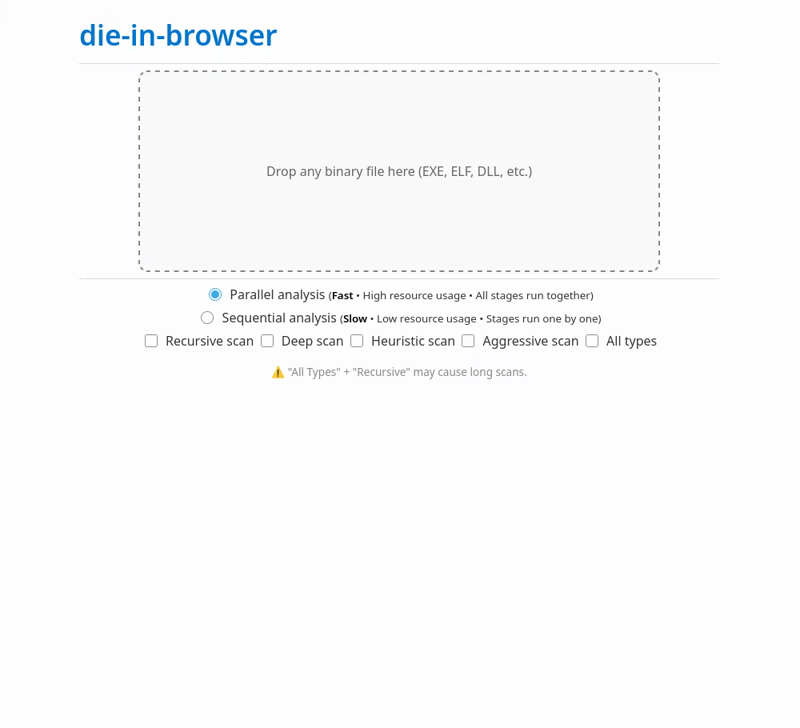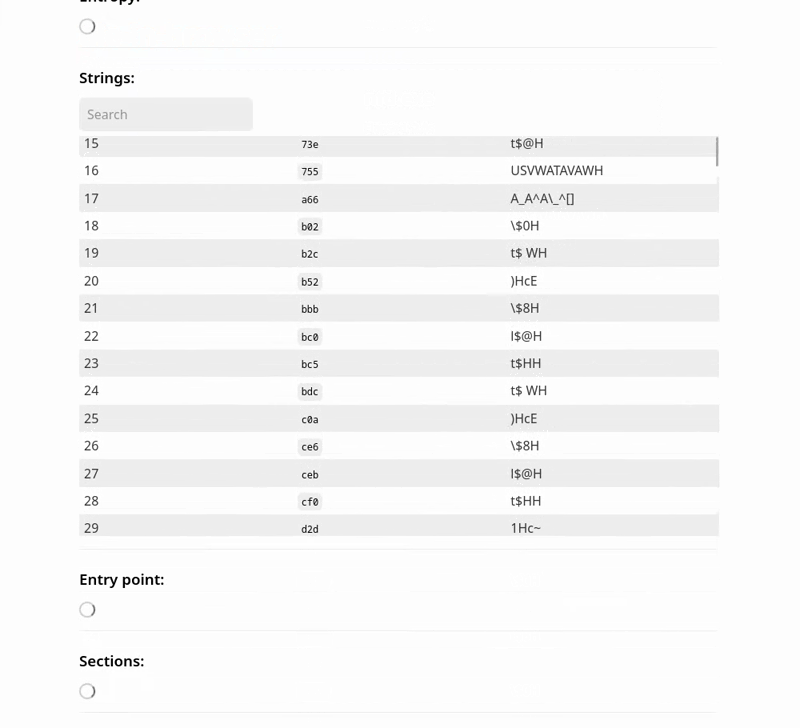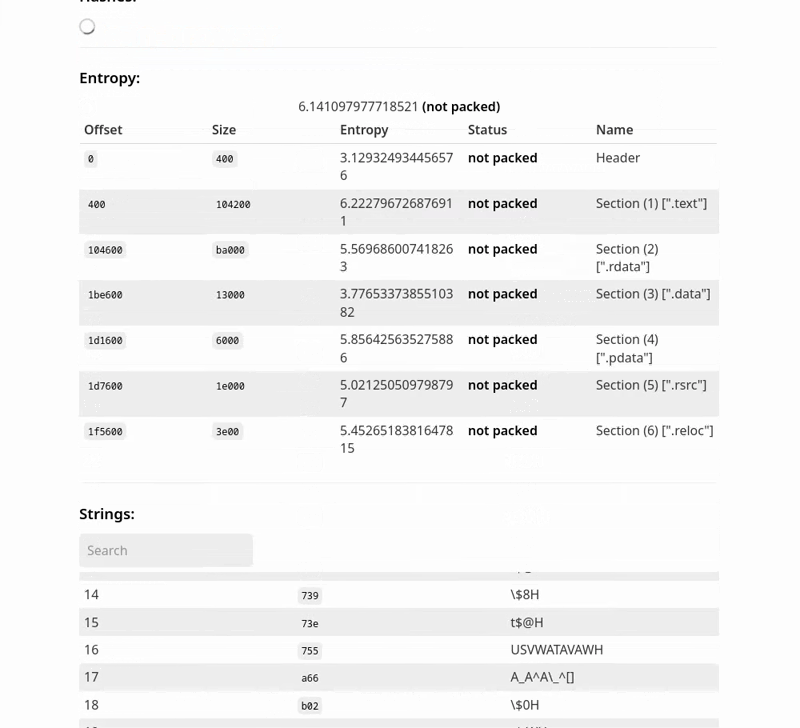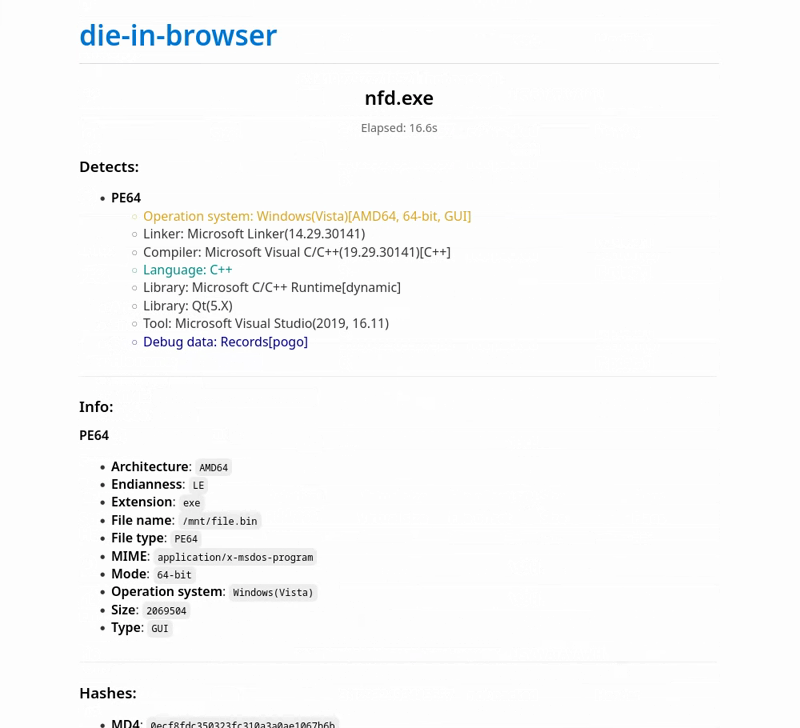 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 rocketchat/layne
A doggo that helps look for security issues in your repositories.