
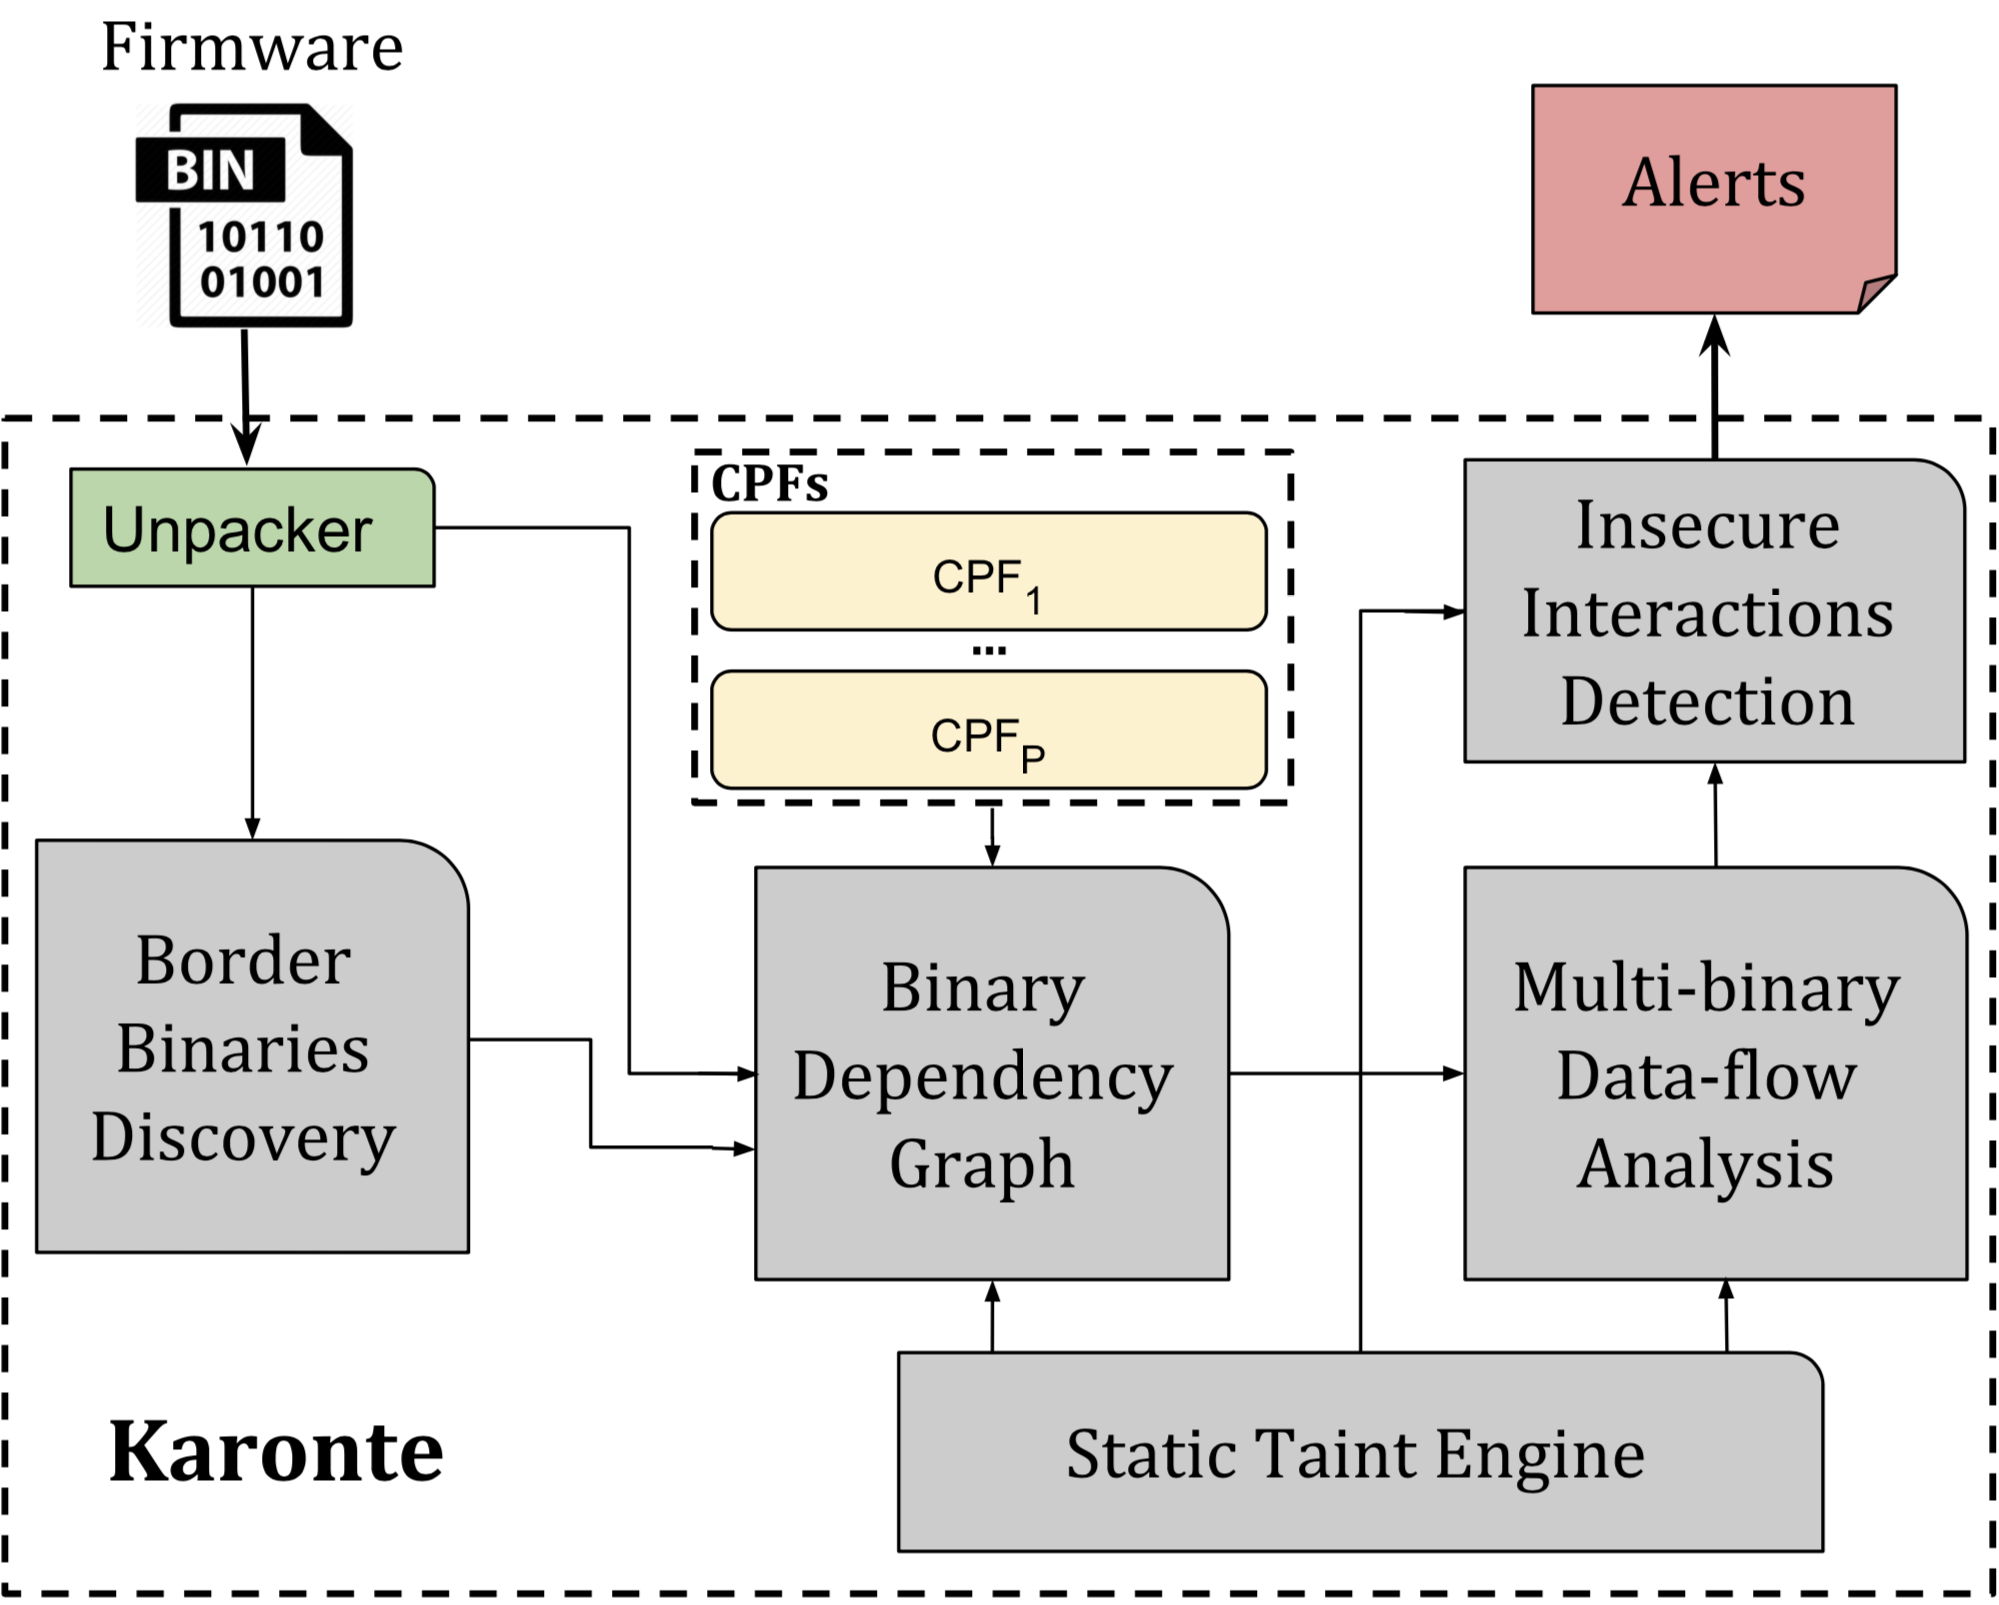
karonte
 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
binary-analysisembedded-systems-securityfirmware-analysis+2
434
ucsb-seclab/karonteKaronte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 mucoze/umay
IoT Malware Similarity Analysis Platform
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 superkhung/luadec-tplink
Modified luadec version to decompile TP-Link Archer C7 LUA firmware.
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
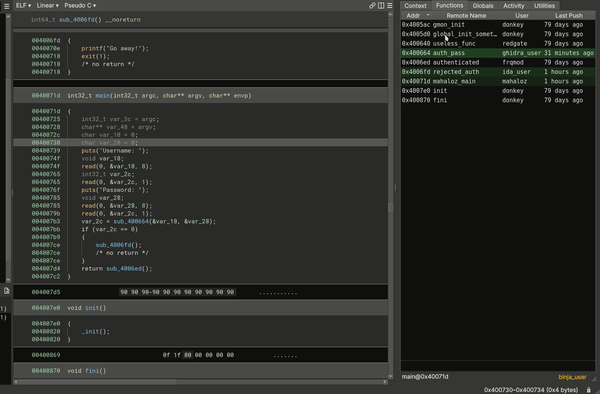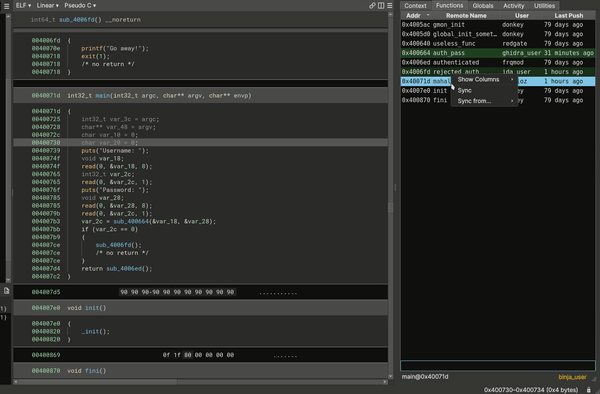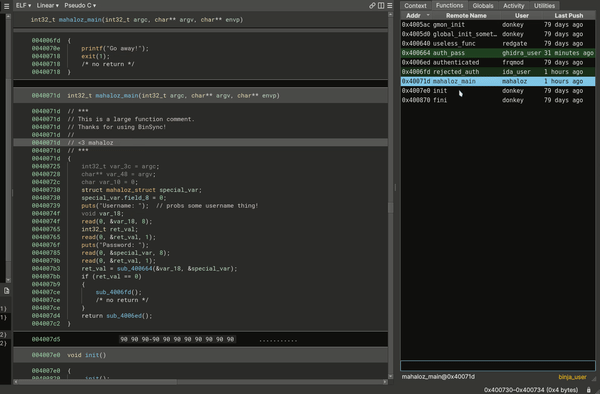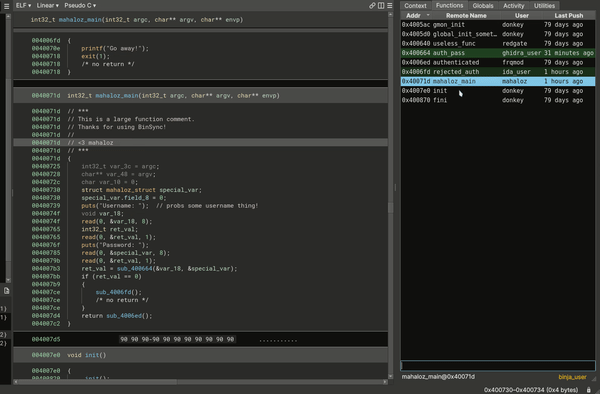 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
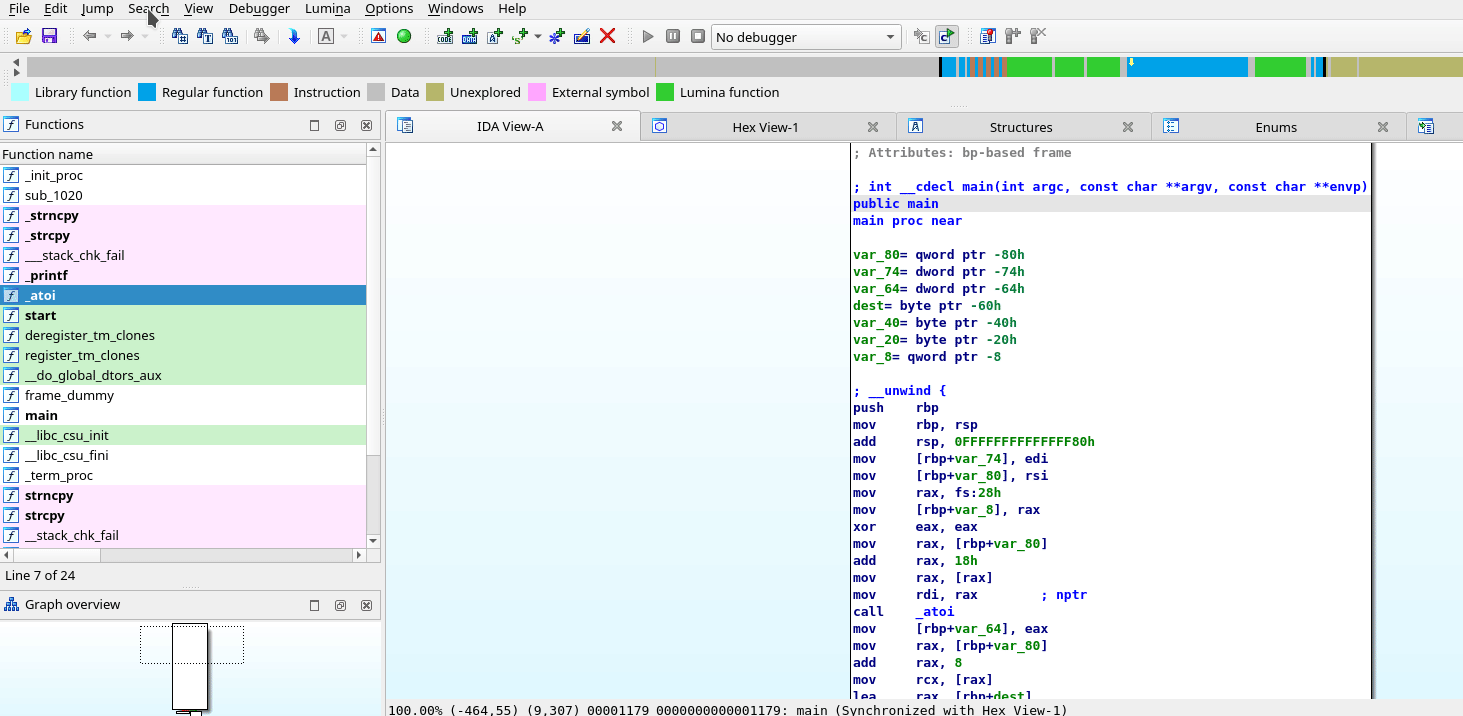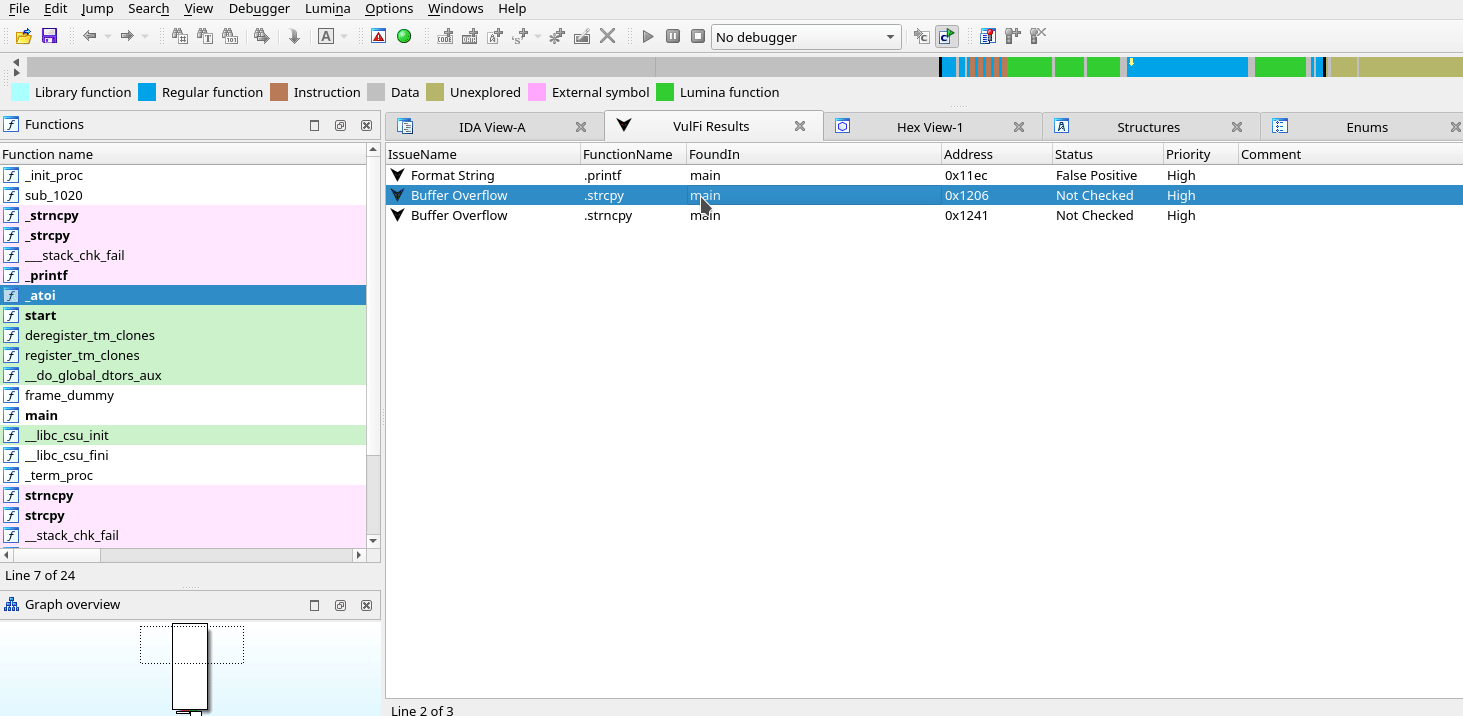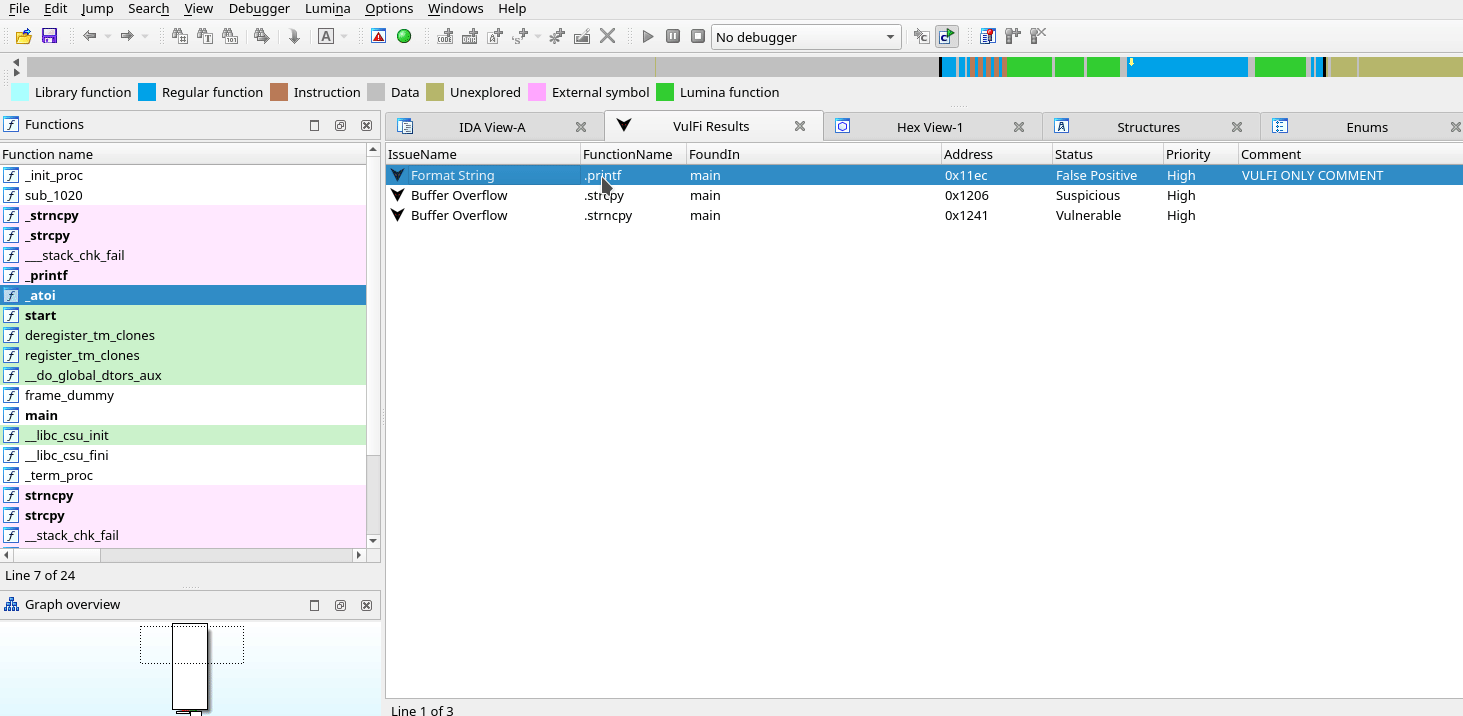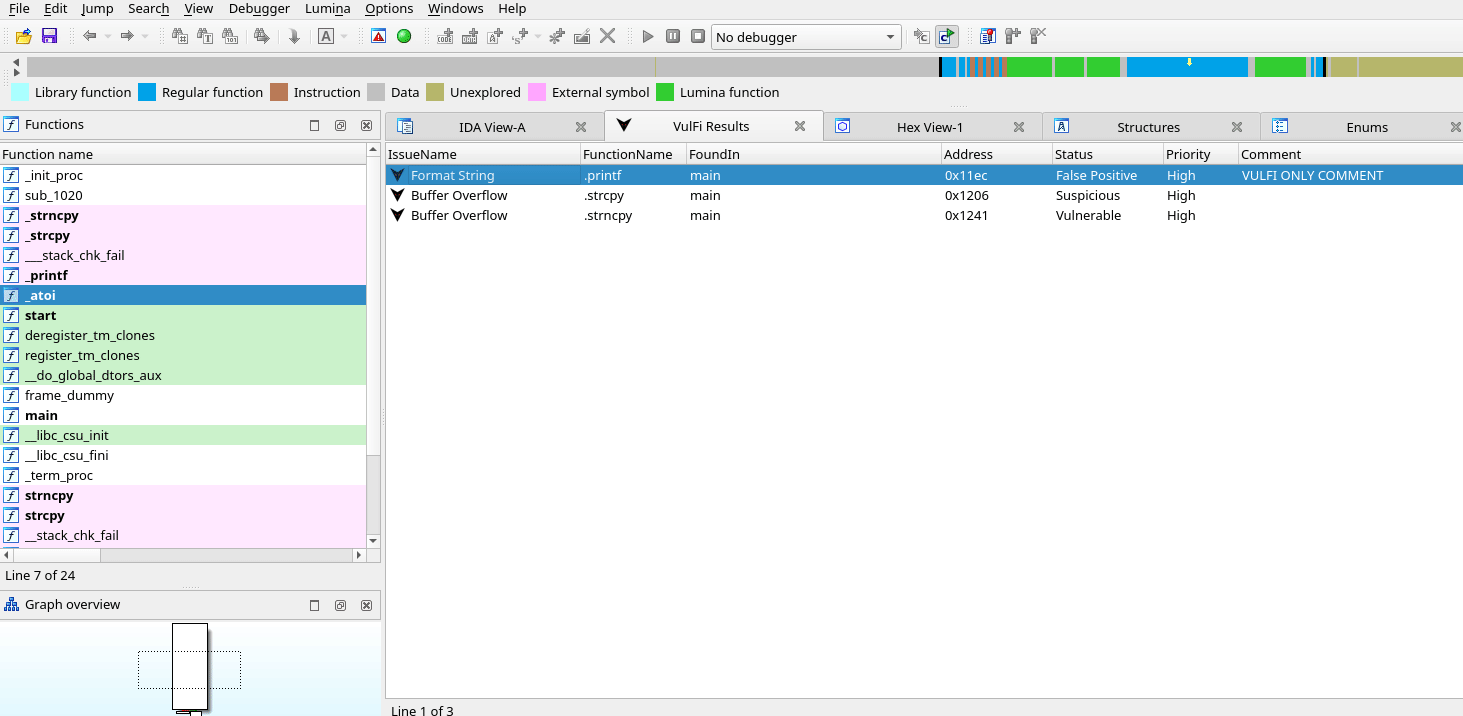 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.