
excelpeek
 slaughterjames/excelpeek
Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
digital-forensicsforensicsmalware-analysis+1
38
slaughterjames/excelpeekStatic analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
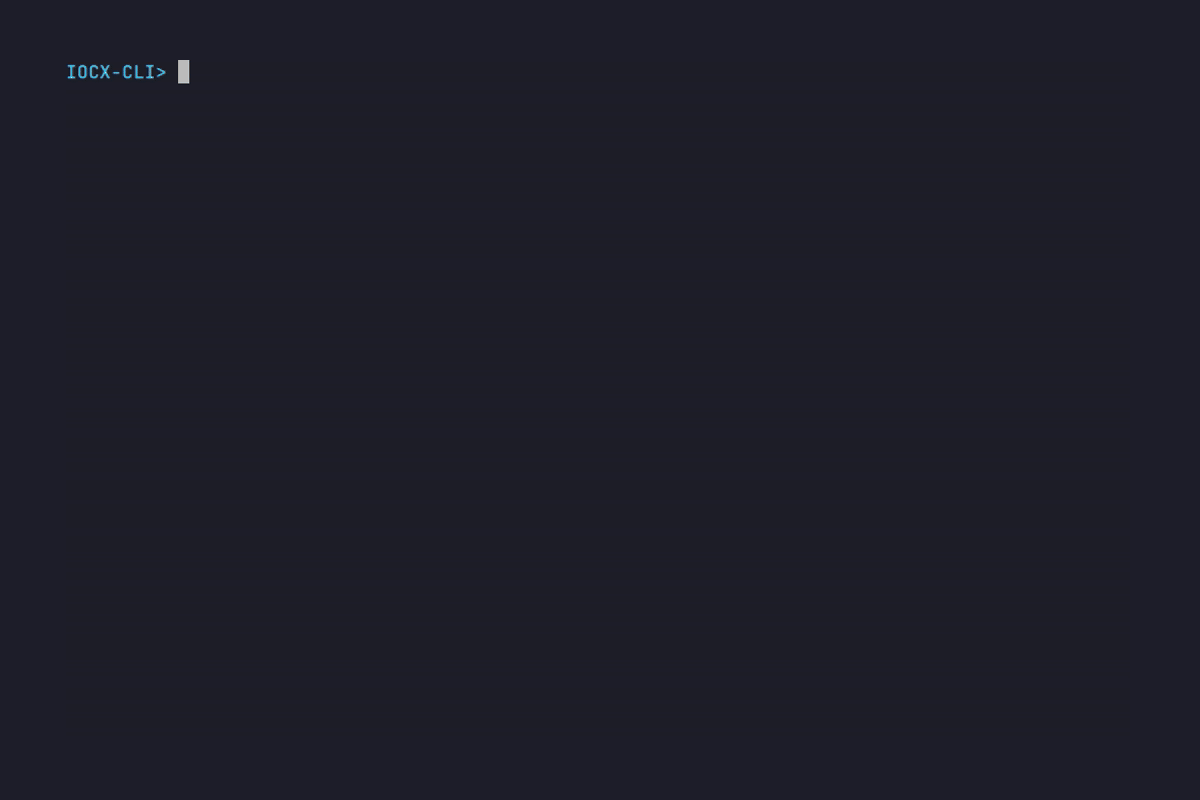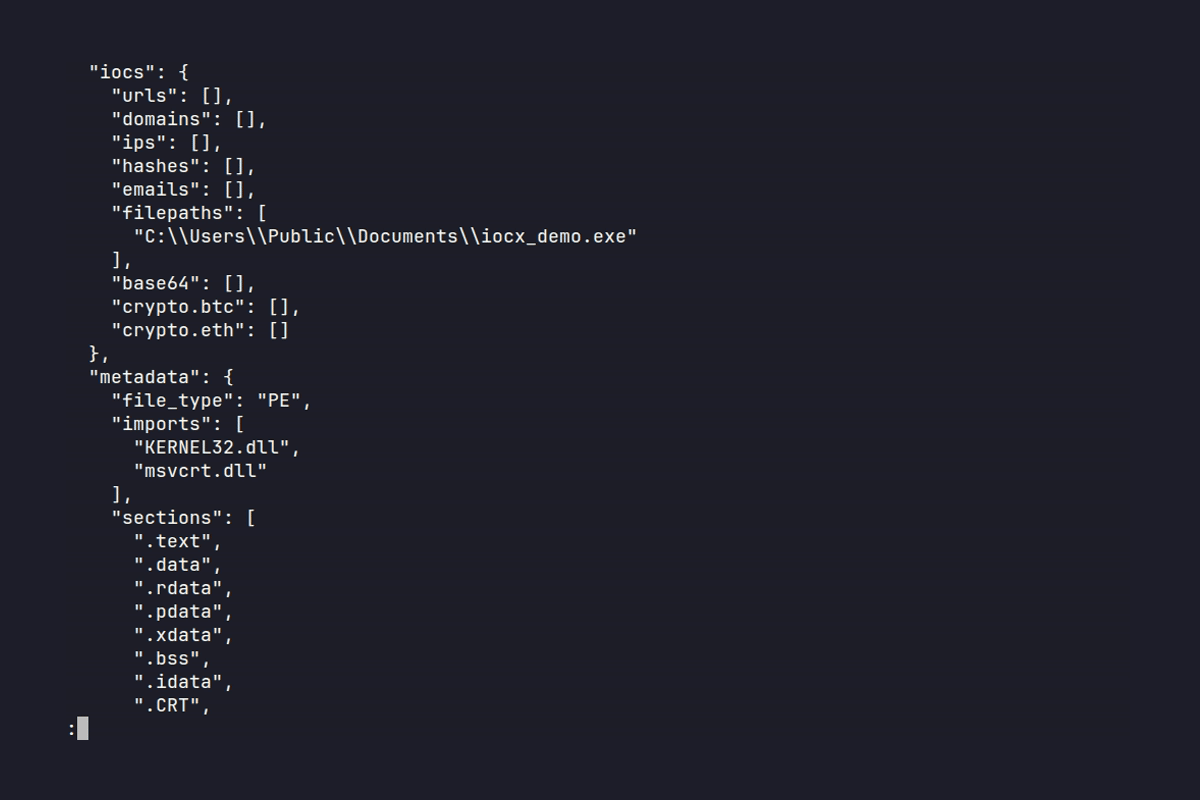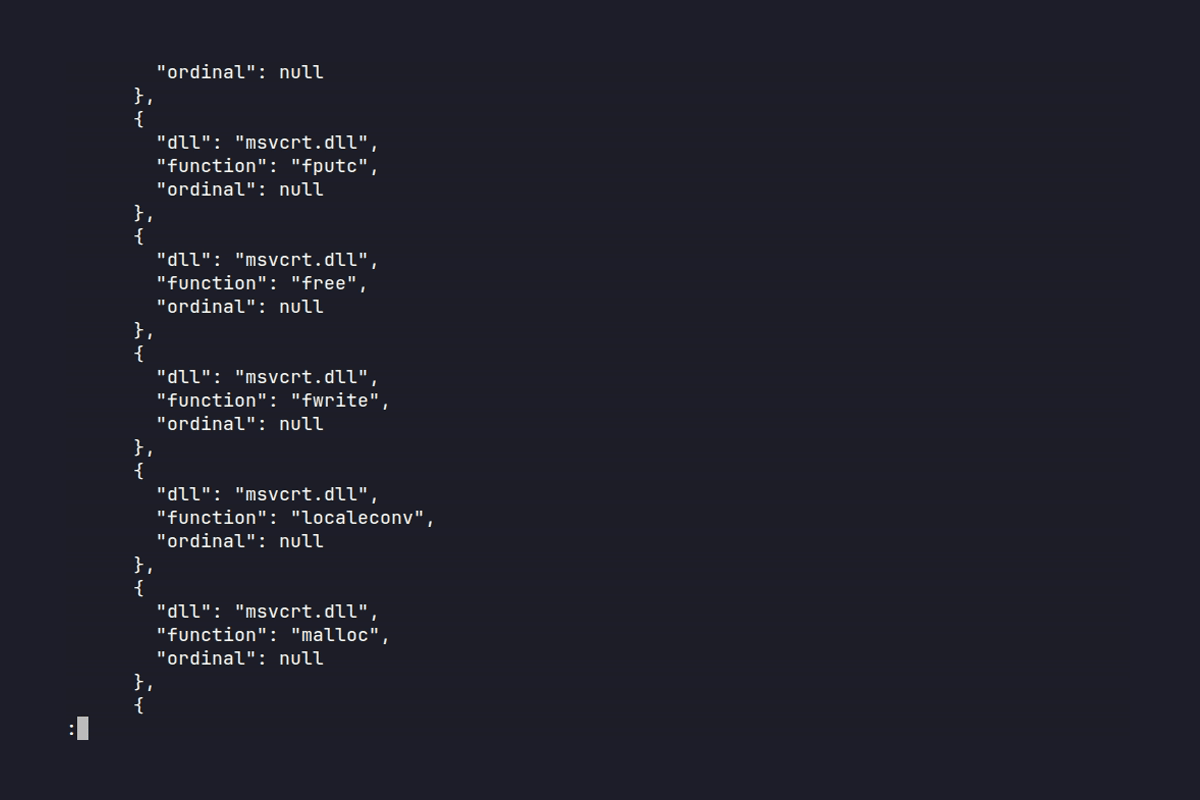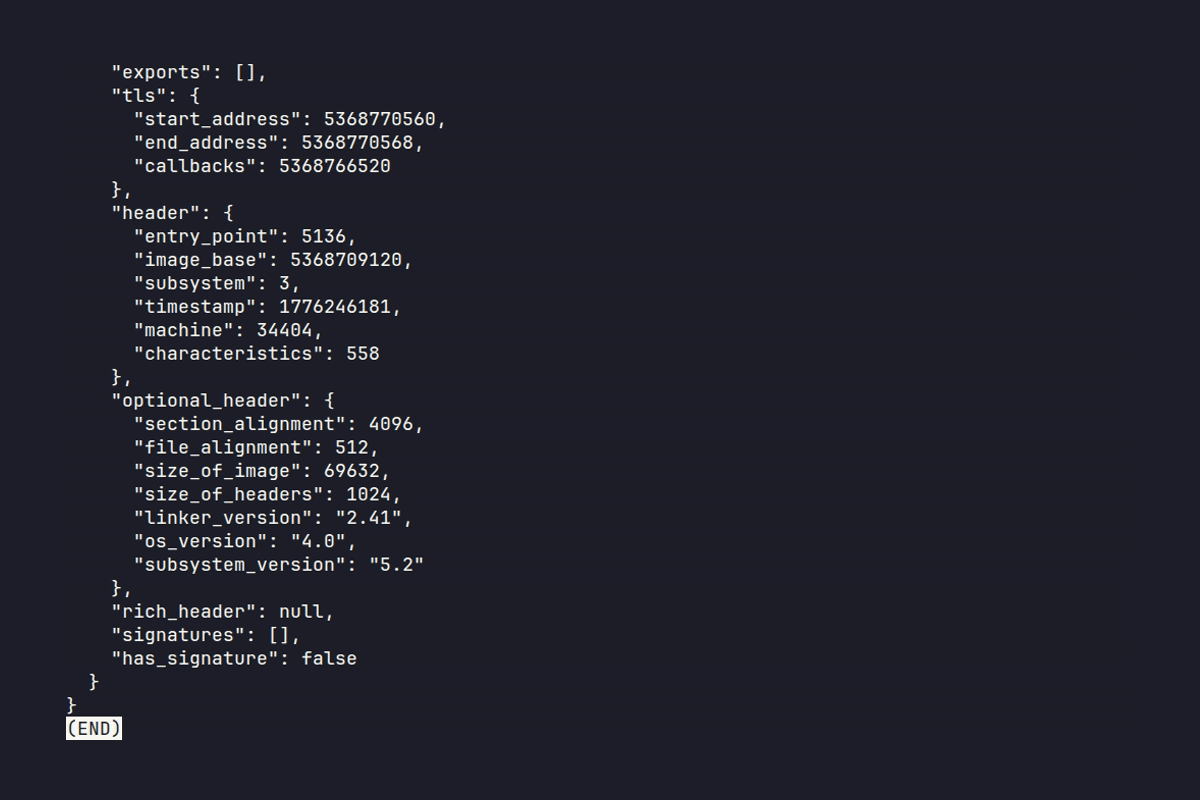 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
 jeremyrsellars/cve-2021-44228_scanner
Aims to find JndiLookup.class in nearly any directory or zip, jar, ear, war file, even deeply nested.
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
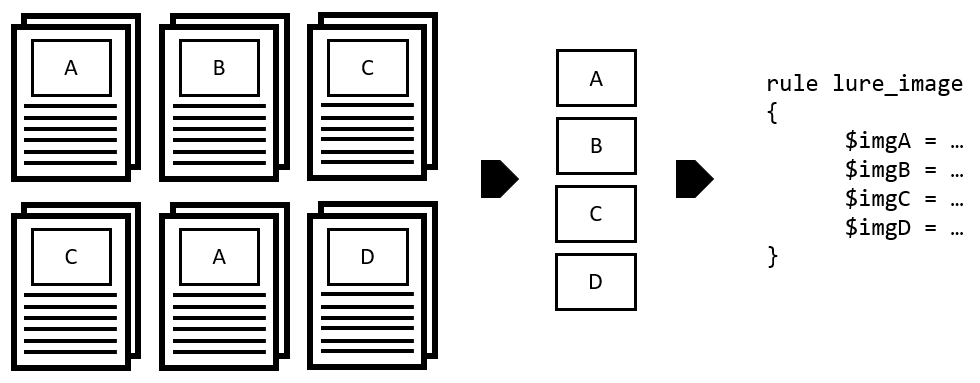 target/halogen
Automatically create YARA rules from malicious documents.
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
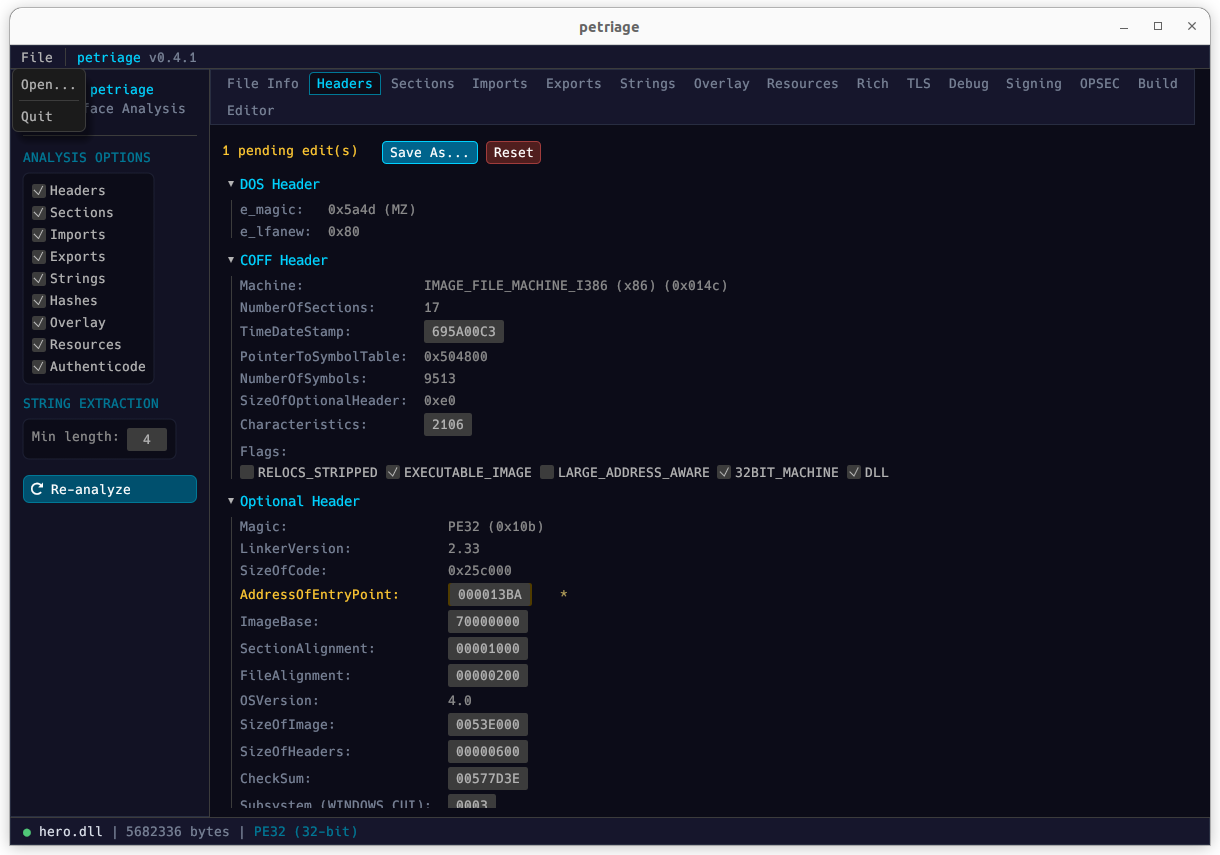 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
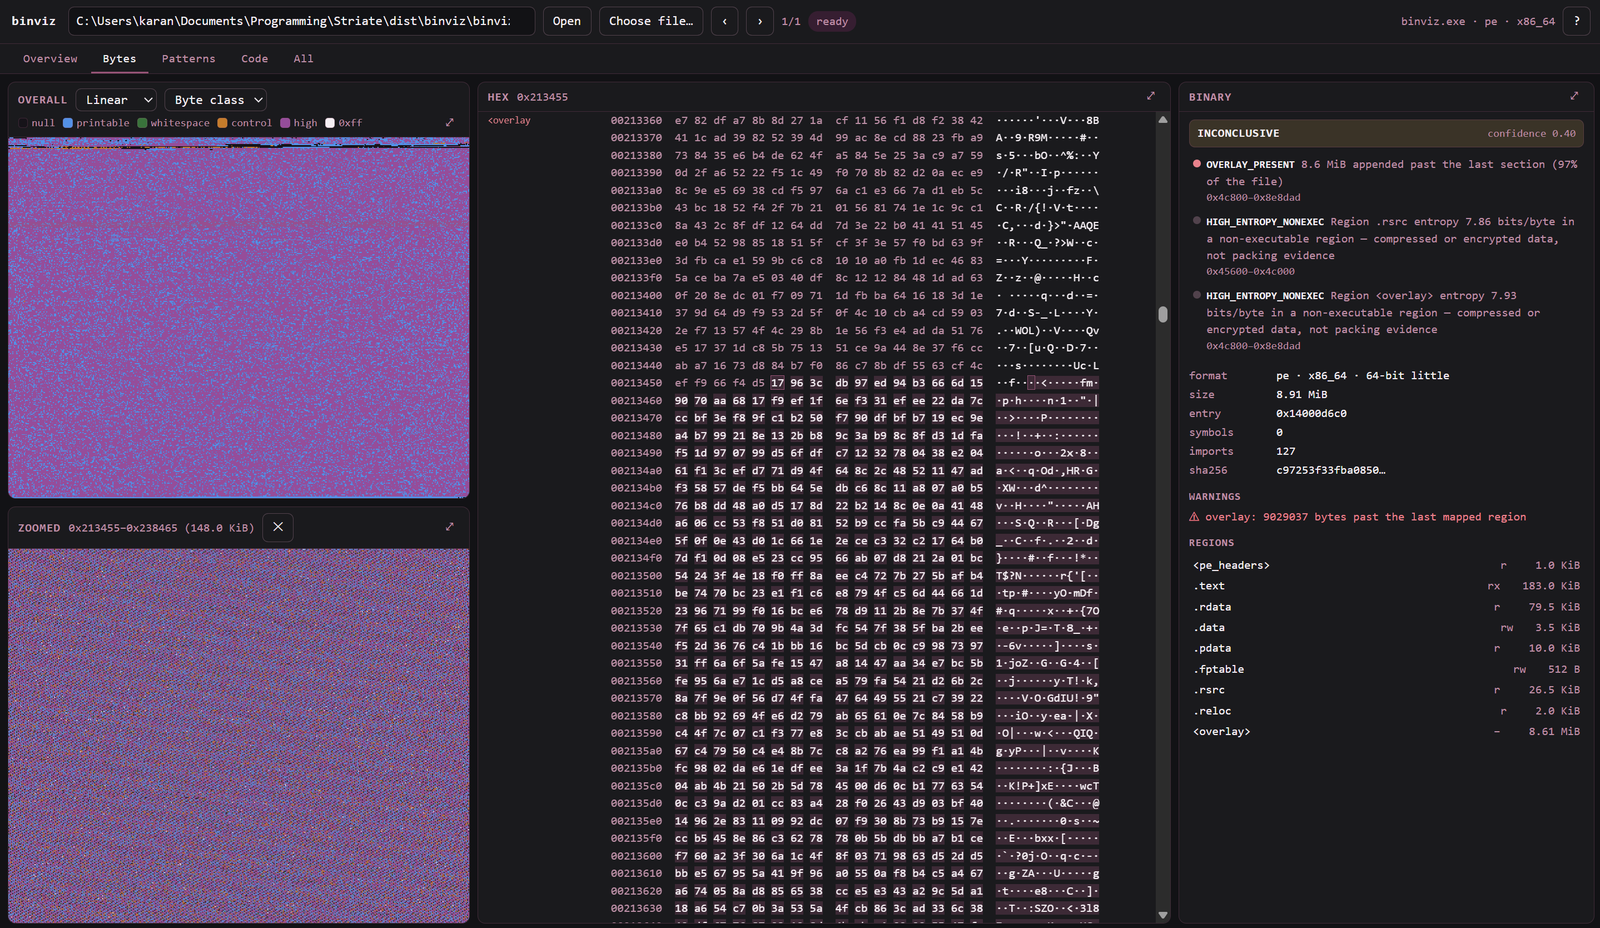 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.