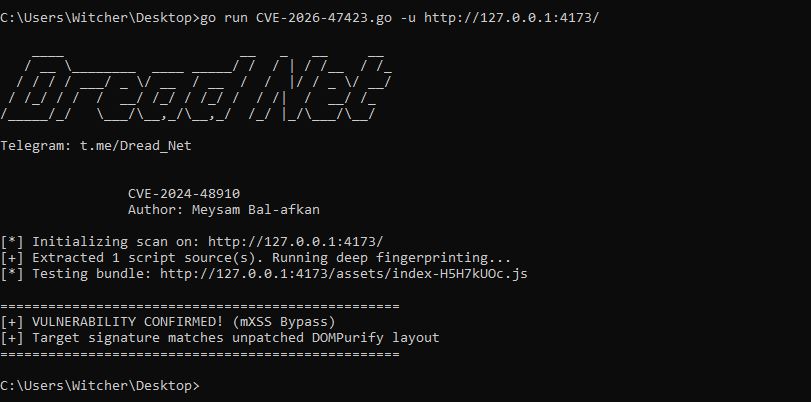
CVE-2026-47423-dompurify-xss-detector

Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles,…

Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles,…

C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.

Some siimple checks to see if JAR file is vulnerable to CVE-2021-44228

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

CVE-2020-26259 &&XStream Arbitrary File Delete

struts1 CVE-2014-0114 classLoader manipulation vulnerability patch

A Bitbucket Pipe to trigger SonarCloud analysis

OpenSSL toolkit implementing SSL/TLS protocols and a general-purpose cryptography library with ciphers, digests, public key algorithms, and X.509…

Apache synapse 反序列化 CVE–2017–15708

cabin partial analysis

Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…

This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…

This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule

CVE-2021-46364: YAML Deserialization in Magnolia CMS


Scanner recursivo de arquivos desenvolvido em Python 3 para localização e varredura de versões vulneráveis do Log4j2, contemplando análise interna de…

Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.

CVE-2019-10172 PoC and Possible mitigations