
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-47423-dompurify-xss-detector — Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles, identifying unpatched allowed-tag layouts. | Kitploit
Tools/GitHubGitHub/galaxy-sc/cve-2026-47423-dompurify-xss-detector
Static AnalysisVulnerability ScannersExploitationWeb SecurityPenetration Testing
GitHubgalaxy-sc/cve-2026-47423-dompurify-xss-detector

CVE-2026-47423-dompurify-xss-detector

Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles, identifying unpatched allowed-tag layouts.

View Repository
385 months agoNot yet reviewed
Share

DOMPurify < 3.4.5 Sanitizer Bypass Detection Tool (Go)

A lightweight, high-performance scanner written in Go to detect production deployments of DOMPurify vulnerable to a complete sanitizer bypass via the <selectedcontent> re-clone logic flaw.

Instead of relying on easily stripped source comments or version variables, this tool performs logic fingerprinting on minified production JavaScript bundles to identify unpatched allowed-tag layouts.

Vulnerability Summary

In DOMPurify versions up to 3.4.4, the <selectedcontent> element was allowed by default. This introduces a logic flaw where Chromium/WebKit browsers refresh and re-clone the <selectedcontent> subtree after DOMPurify has already executed its sanitization pass, leading to an absolute XSS bypass when the payload is injected into the live DOM.
Features

  • Framework-agnostic (Works with React, Vue, Angular, or Vanilla JS bundle structures)
  • Automated dynamic JS asset parsing from root paths
  • Case-insensitive static analysis on compiled production code

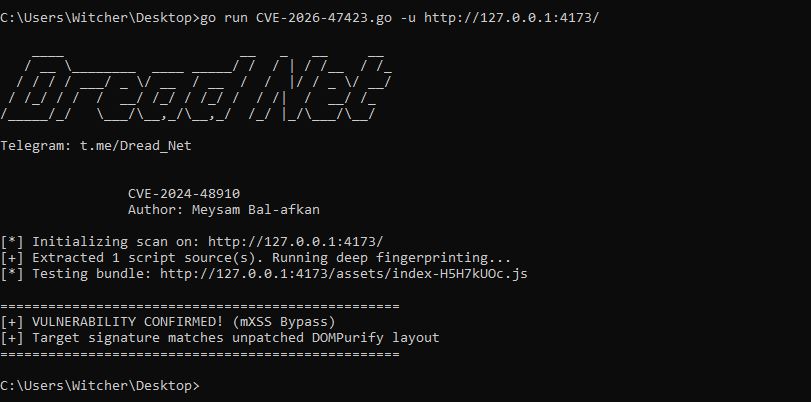
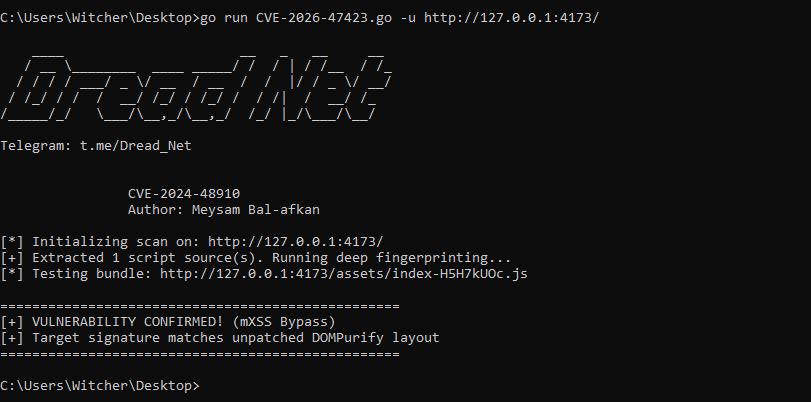
Proof of Concept

Exploit Output Screenshot

Usage

# Clone the repository
git clone https://github.com/Galaxy-sc/CVE-2026-47423-dompurify-xss-detector.git
cd CVE-2026-47423-dompurify-xss-detector

# Run against a target using parameters
go run CVE-2026-47423.go -u https://example.com

Remediation

Update dompurify to version 3.4.5 or higher via your package manager:

npm install [email protected]

If an immediate upgrade is not feasible, manually block the tag in your config layout:

DOMPurify.sanitize(userInput, { FORBID_TAGS: ['selectedcontent'] });

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





