
recaptcha
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
anti-botcaptcha-bypassdynamic-code-analysis+3
elyelysiox/recaptchaDocumentation and reverse engineering of reCAPTCHA
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
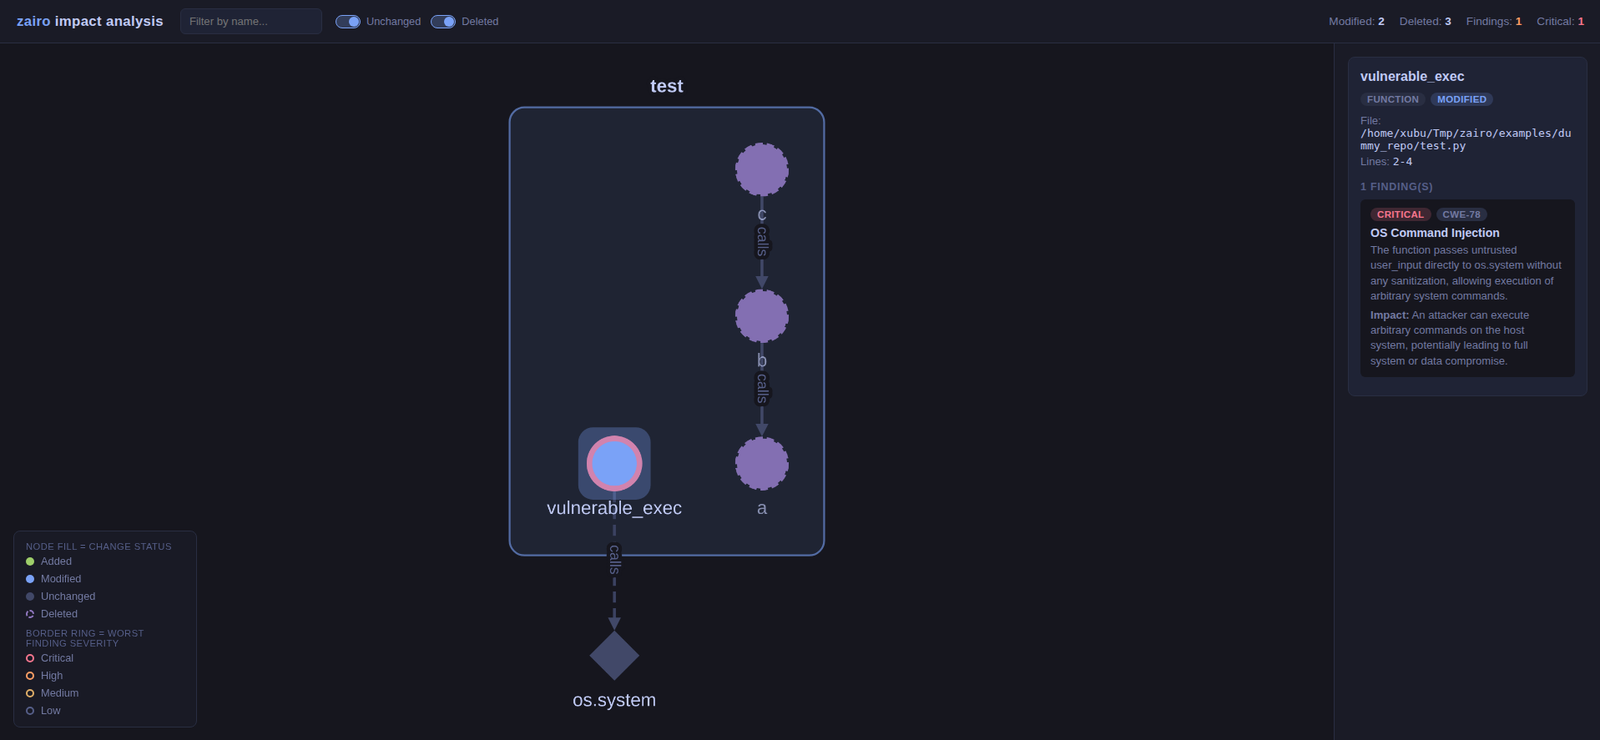 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 eset/malware-research
Code written as part of our various malware investigations
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
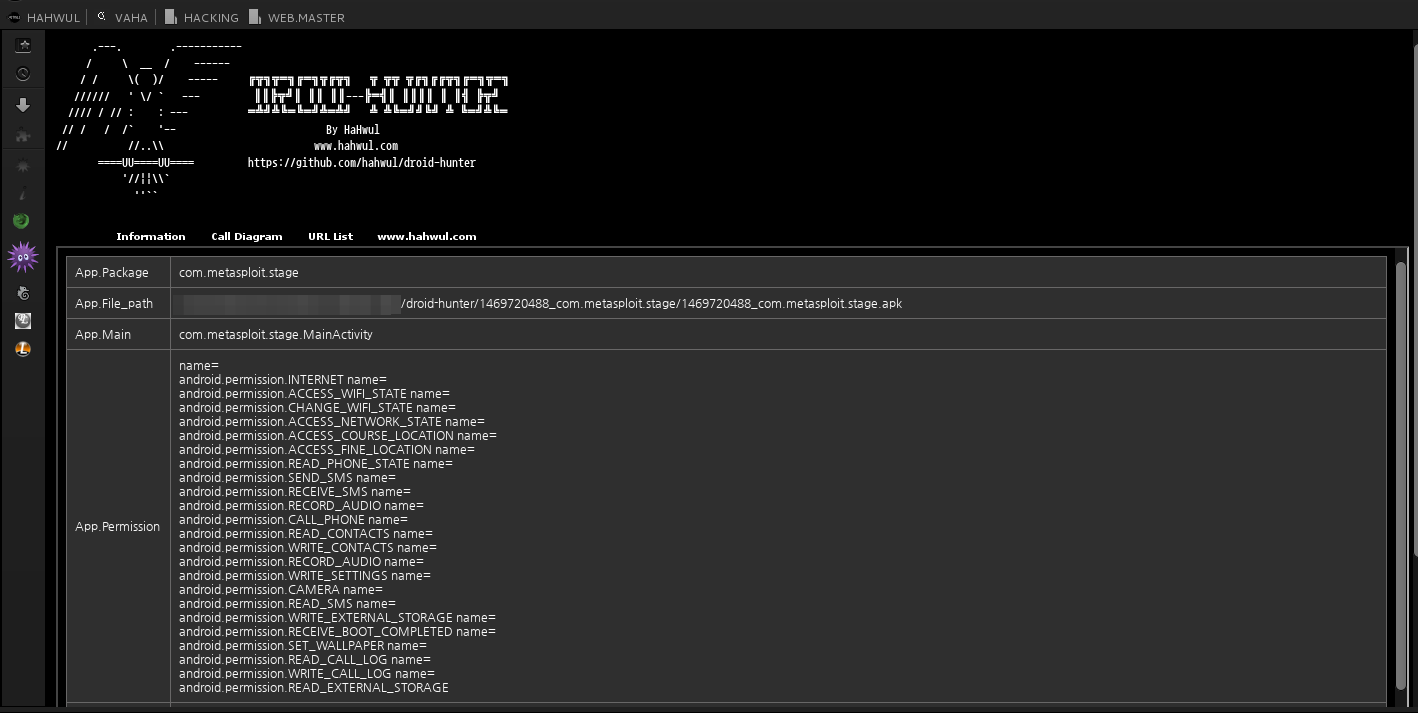 hahwul/droid-hunter
(deprecated) Android application vulnerability analysis and Android pentest tool
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 ianoboyle/cve-2025-57833
Example Vulnerable application for CVE-2025–57833
 h1nayoshi/smalien
Information flow analysis tool for Android applications