

ConcoLLMic
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
ai-securitybinary-analysiscode-analysis+8
160
concollmic/concollmicLLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
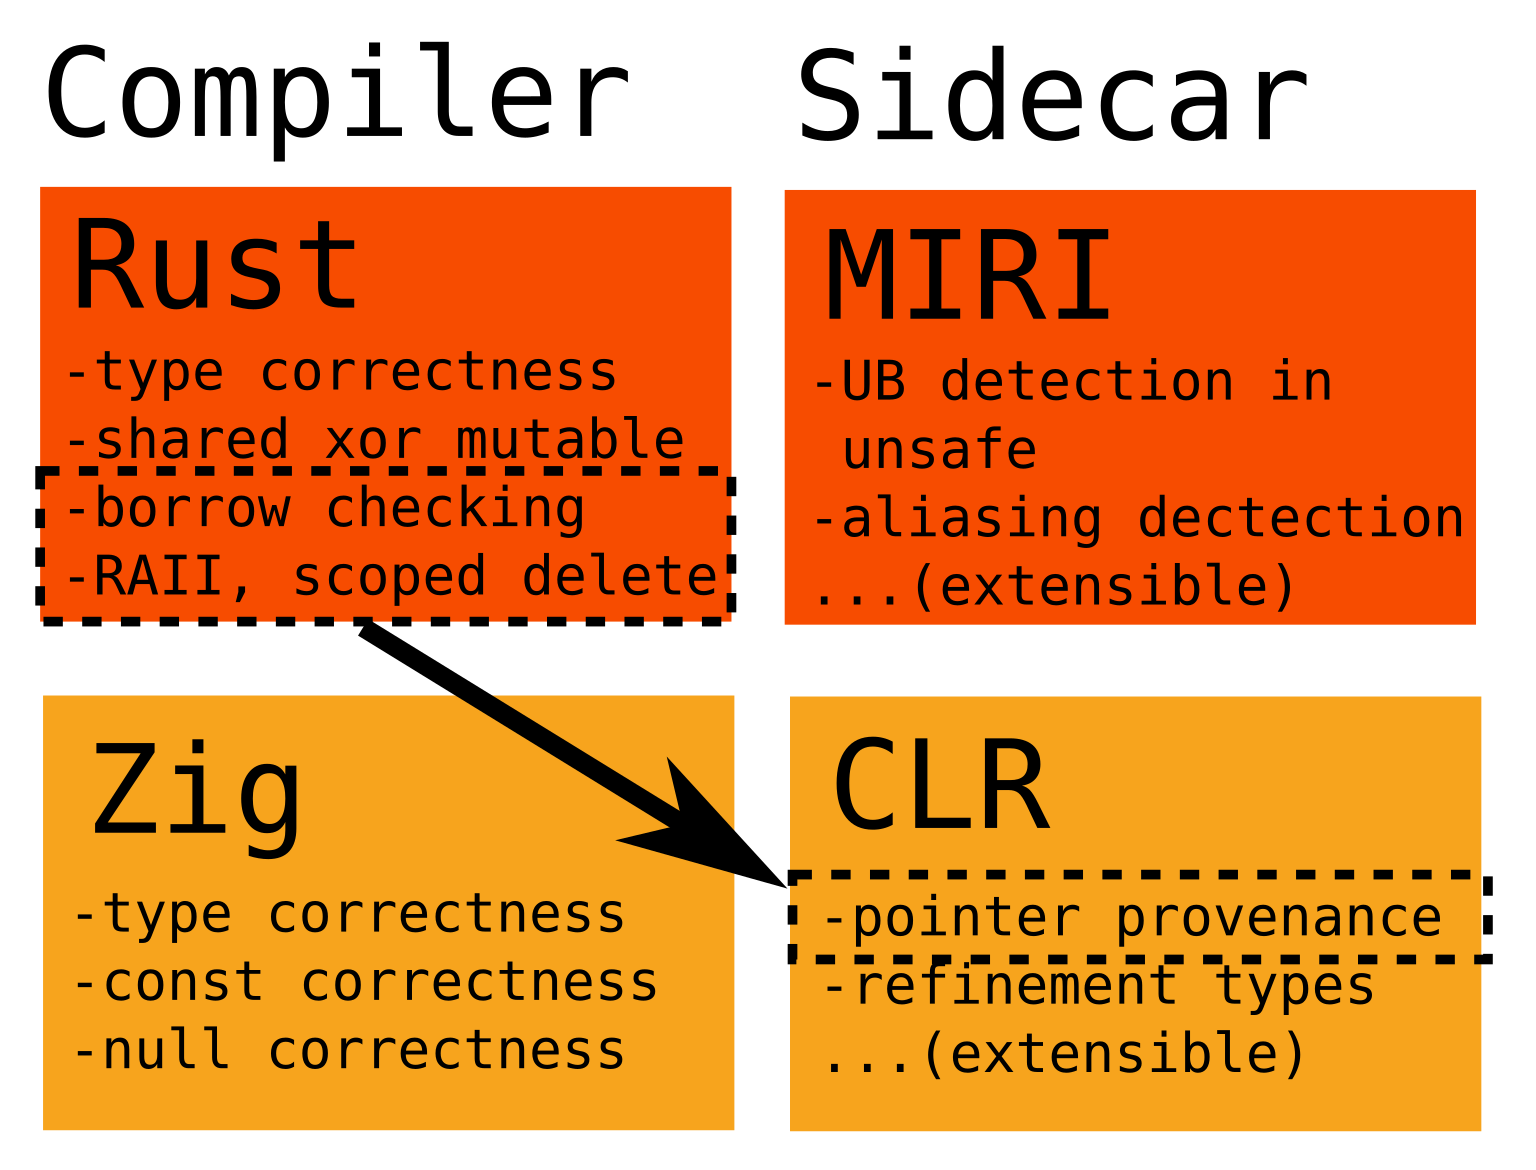 ityonemo/clr
Checker for Lifetimes and other Refinement types
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
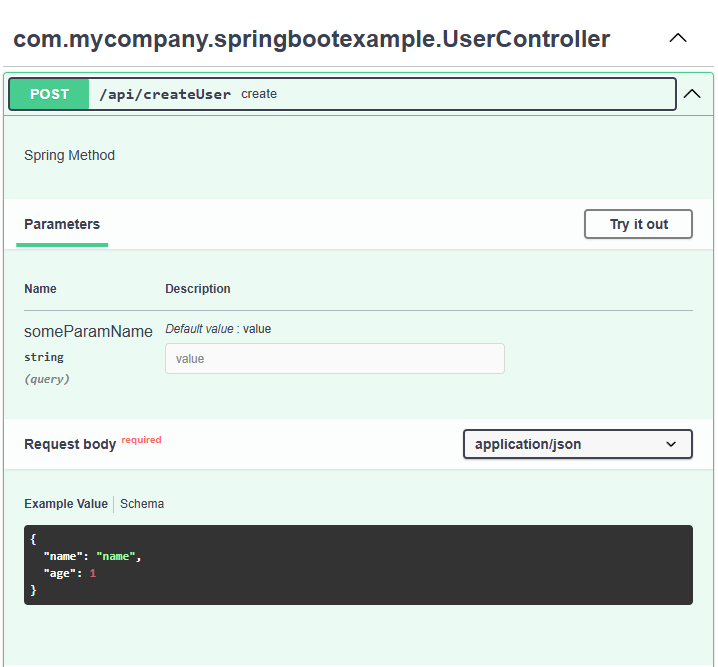 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
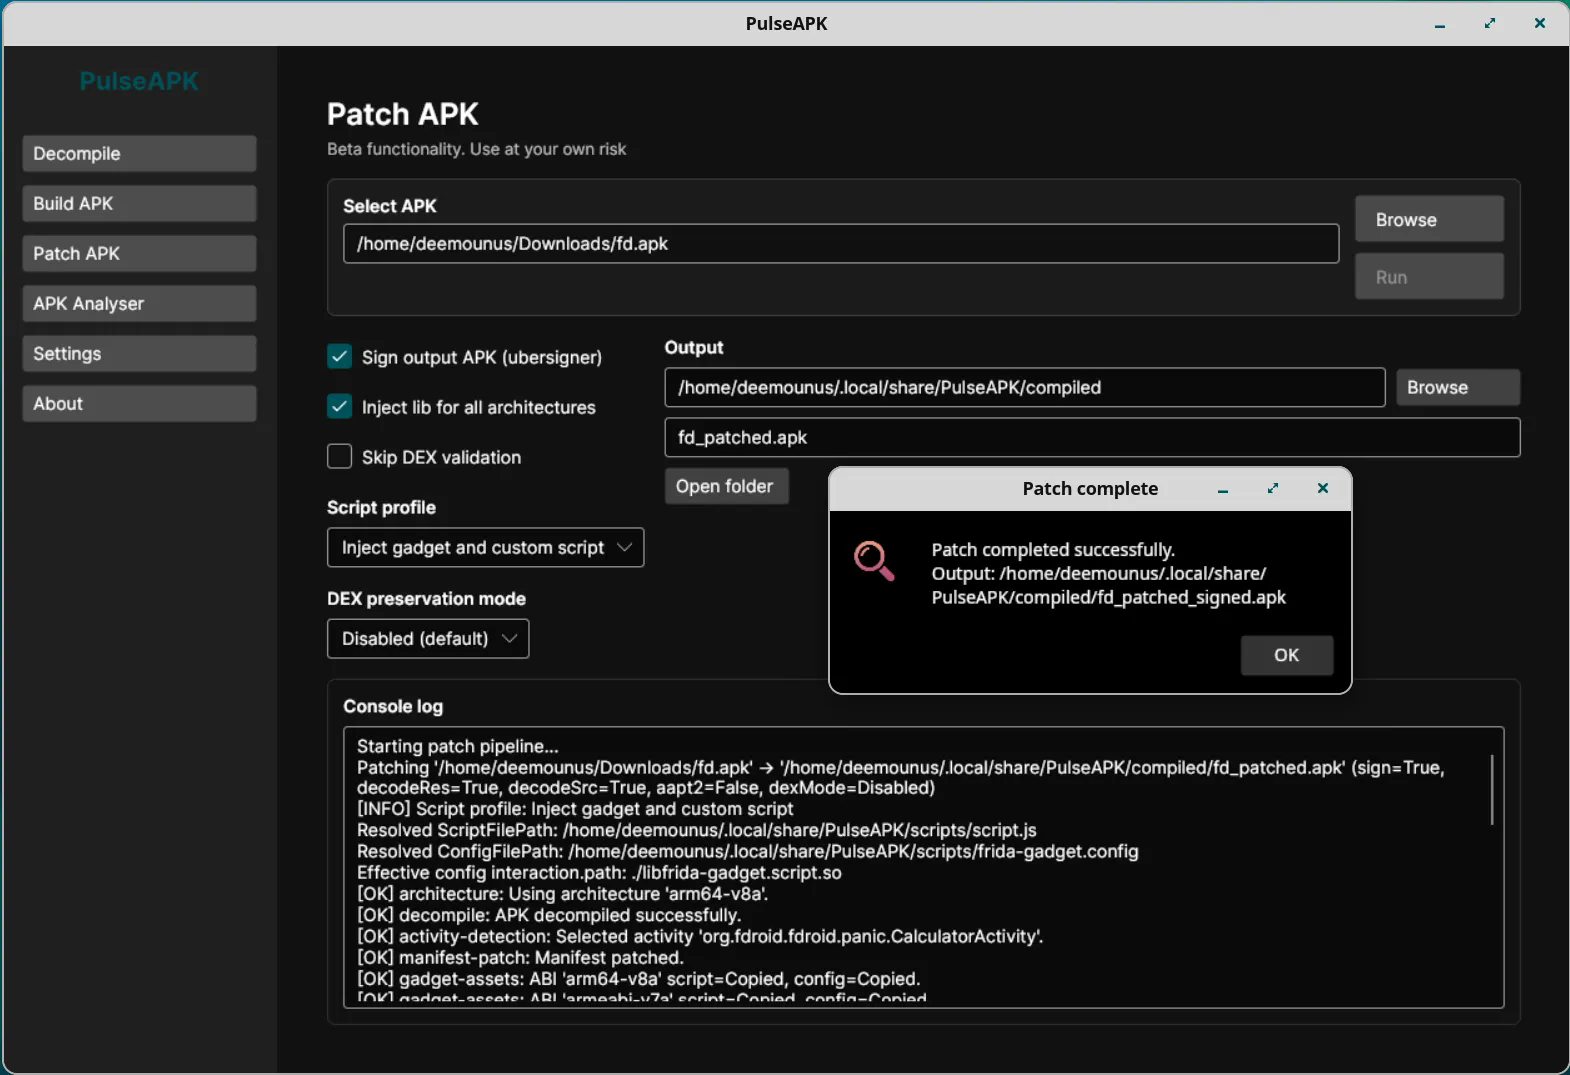 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
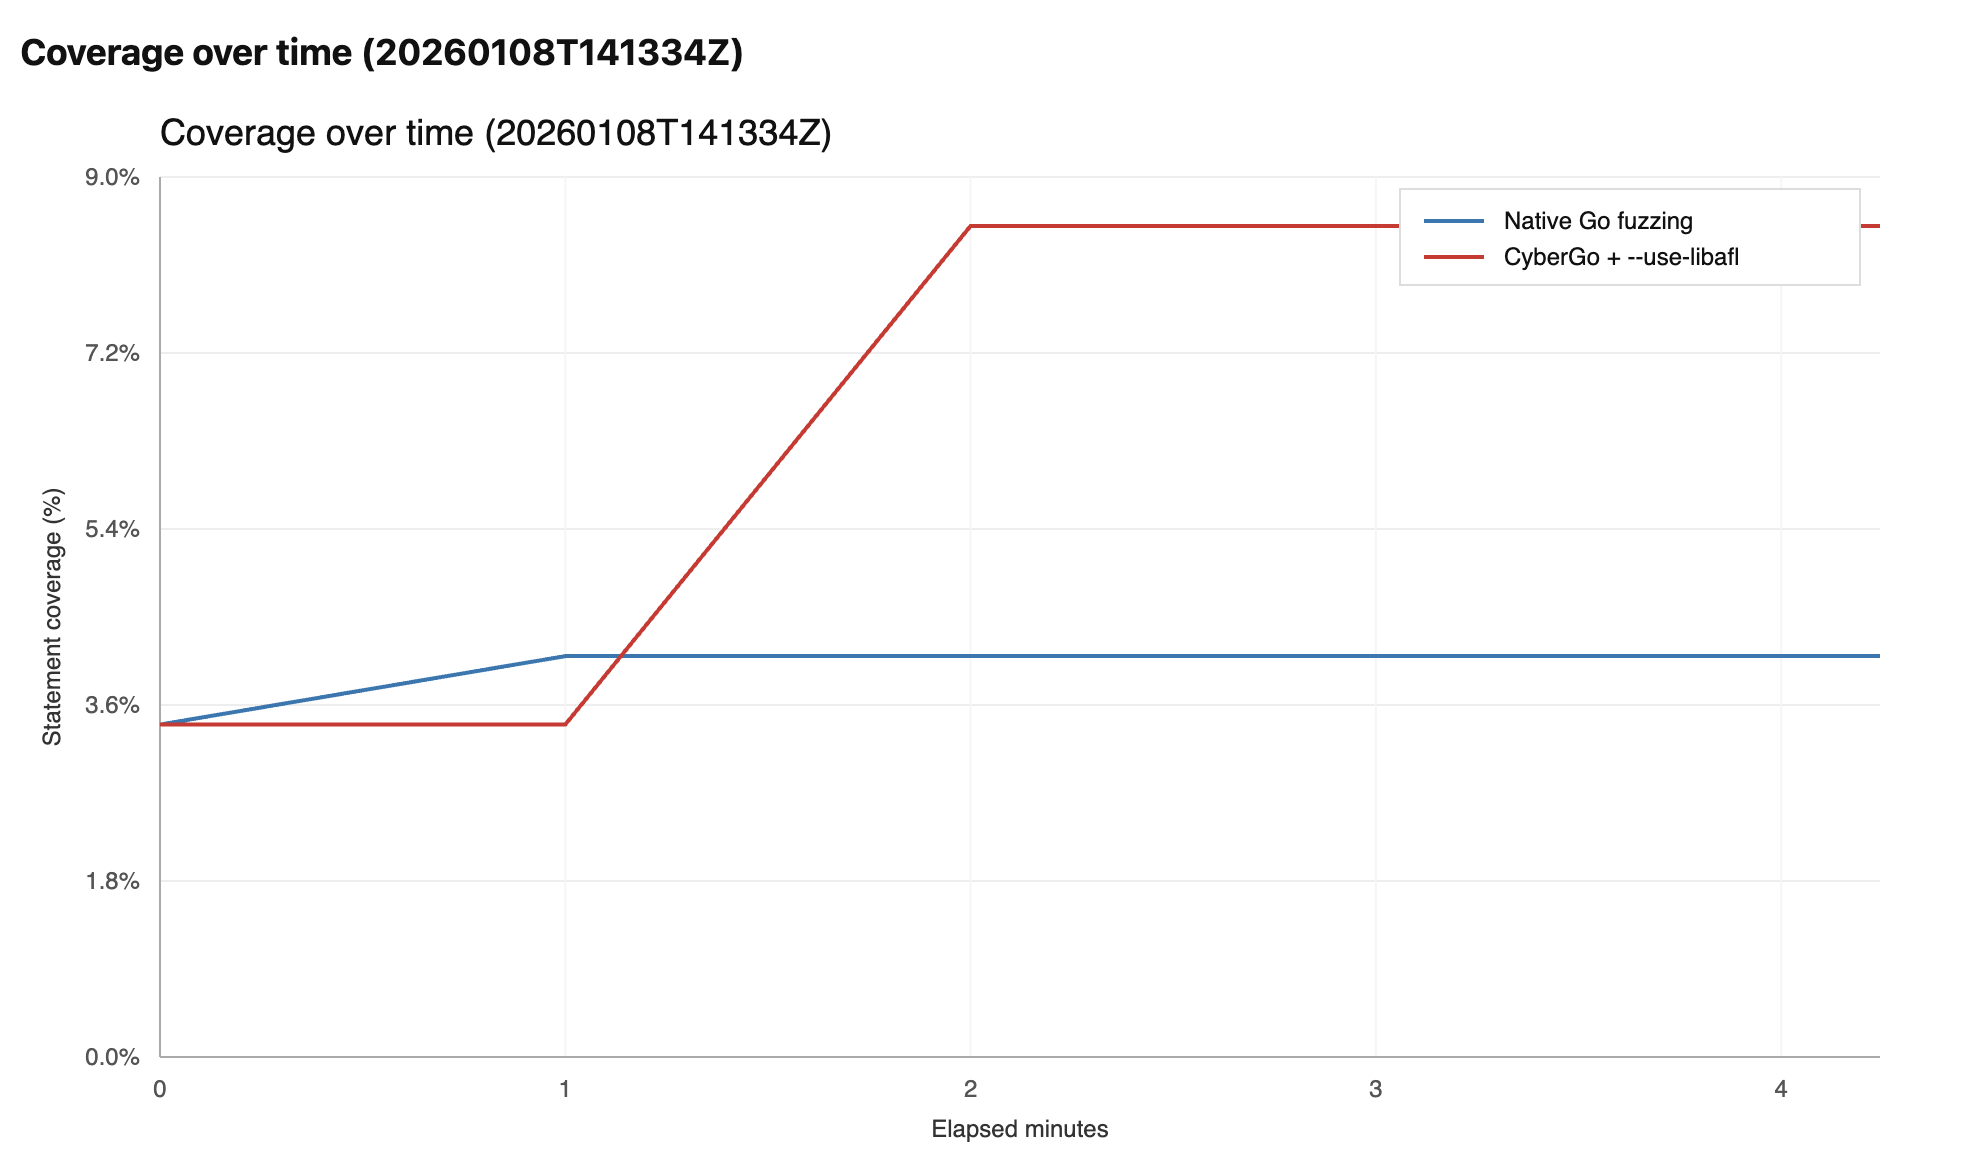 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery