
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
138 results
Vba2Graph preview

Vba2Graph

GitHubmalwarecantfly/vba2graph

Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents.
code-analysismalware-analysisreverse-engineering+1
283
6 years ago
AndroPyTool preview

AndroPyTool

GitHubalexmyg/andropytool

A framework for automated extraction of static and dynamic features from Android applications

android-securitydynamic-analysis-sandboxingmalware-analysis+2
3816 years ago
Apkatshu preview

Apkatshu

GitHub0xpwny/apkatshu

Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
android-securityinformation-gatheringmobile-security+1
2523 years ago
IDA2Obj preview

IDA2Obj

GitHubjhftss/ida2obj

Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
binary-analysisdebuggersfuzzing+2
1215 years ago
BFScan preview

BFScan

GitHubblackfan/bfscan

Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…

android-securityapi-securityinformation-gathering+5
25711 months ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
ai-assisted-reversingandroid-securitybinary-analysis+8
7010h 1m ago
iocs preview

iocs

GitHubthreatlabz/iocs

This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
curated-resourcesincident-responseioc-management+4
796 days ago
maldrolyzer preview

maldrolyzer

GitHubmaldroid/maldrolyzer

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
android-securitycommand-and-controlinformation-gathering+3
11211 years ago
r2web preview

r2web

GitHubradareorg/r2web

Access radare2 from anywhere, anytime.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
5129 days ago
Apepe preview

Apepe

GitHub0xdsm/apepe

Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
android-securityinformation-gatheringmobile-app-pentesting+1
1551 year ago
donut-decryptor preview

donut-decryptor

GitHubvolexity/donut-decryptor

Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
binary-analysisdefensive-toolsdigital-forensics+4
1413 months ago
AntiOreans-CodeDevirtualizer preview

AntiOreans-CodeDevirtualizer

GitHub67-6f-64/antioreans-codedevirtualizer

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
binary-analysisbinary-exploitationcode-analysis+5
823 years ago
2024 preview

2024

GitHub100daysofyara/2024

Rules shared by the community from 100 Days of YARA 2024
curated-resourceseducationlearning-paths-courses+2
901 year ago
z9 preview

z9

GitHubsh1n0g1/z9

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.

forensicslog-analysismalware-analysis+2
683 years ago
sgxray preview

sgxray

GitHubbaiduxlab/sgxray

Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…

binary-analysisfuzzinghardware-security+2
435 years ago
pdfresurrect preview

pdfresurrect

GitHubenferex/pdfresurrect

Analyze and help extract older "hidden" versions of a pdf from the current pdf.
data-recoverydigital-forensicsstatic-analysis
1024 years ago
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
android-securitybinary-analysiscode-analysis+5
391 month ago
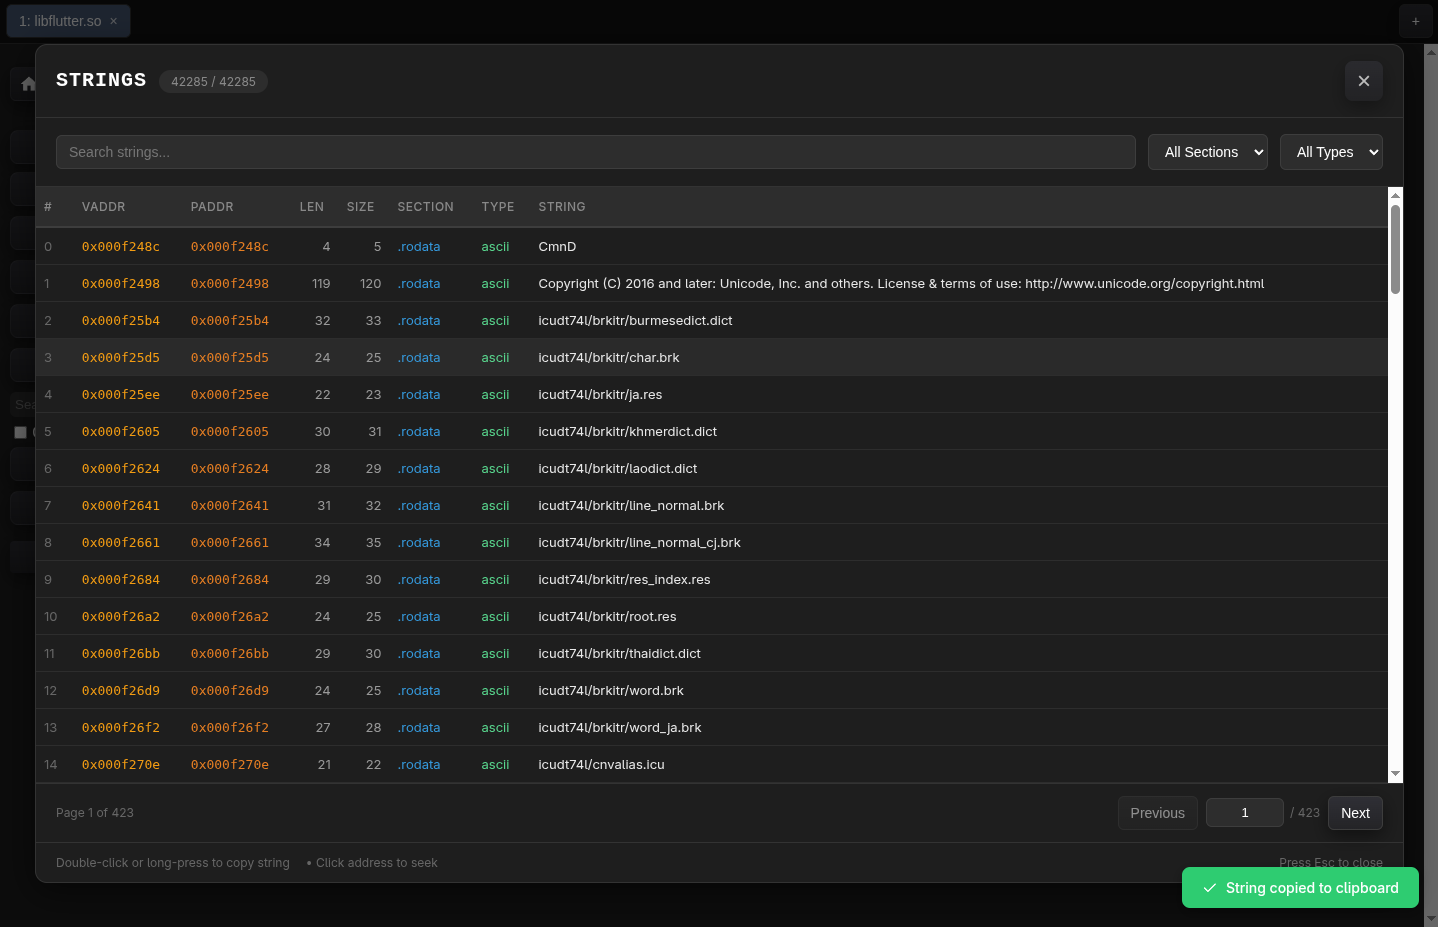
aotopsy preview

aotopsy

GitHubbronils/aotopsy

Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…

binary-analysismobile-app-pentestingmobile-security+2
411 month ago
Previous123…8Next