
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
132 results
CVE-2024-51132-POC preview

CVE-2024-51132-POC

GitHubjacklosingheart/cve-2024-51132-poc

Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…

code-analysisexploitationinformation-gathering+3
1
1 year ago
jshound preview

jshound

GitHubambitsecurity/jshound

Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.

api-securitycrawlerinformation-gathering+5
1211 days ago
cherrybomb preview

cherrybomb

GitHubblst-security/cherrybomb

CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…

api-securityapi-security-testingdynamic-analysis-sandboxing+3
1.2k2 years ago
WSSAT preview

WSSAT

GitHubyalcinyolalan/wssat

WEB SERVICE SECURITY ASSESSMENT TOOL

api-security-testingdynamic-analysis-sandboxinginformation-gathering+3
3885 years ago
blitzstrike preview

blitzstrike

GitHubshinthink/blitzstrike

MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…

exploitationinformation-gatheringpayload-generation+8
5151 month ago
vulnhawk preview

vulnhawk

GitHubmomenbasel/vulnhawk

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

ai-securityapi-security-testingcloud-security+8
904 months ago
xssearch preview

xssearch

GitHubaffolter-engineering/xssearch

Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.

crawlerinformation-gatheringpayload-generation+9
64 days ago
Securiscan preview

Securiscan

GitHubvighnesh91/securiscan

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

ai-securityapi-securityapi-security-testing+8
29 days ago
-LogicSentry-AI preview

-LogicSentry-AI

GitHubvighnesh91/-logicsentry-ai

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

ai-securityapi-security-testingcode-analysis+9
122 days ago
Enigma- preview

Enigma-

GitHubgmh5225/enigma-

C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…

ai-assisted-reversingai-securitybinary-analysis+5
15 months ago
testing-handbook preview

testing-handbook

GitHubtrailofbits/testing-handbook

Trail of Bits Testing Handbook - appsec.guide

code-analysiscryptographycurated-resources+9
1413 days ago
React2Shell preview

React2Shell

GitHubphanhoangkhang/react2shell

Isolated Docker lab and static scanner for CVE-2025-55182, with vulnerable/patched Next.js builds and PoC validation of RSC Flight deserialization.

dynamic-analysis-sandboxingeducationexploitation+6
2 months ago
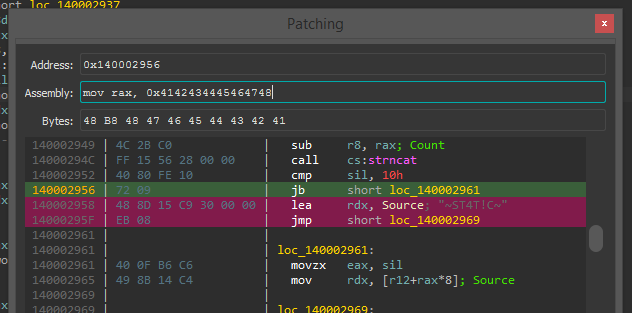
patching preview

patching

GitHubgaasedelen/patching

An Interactive Binary Patching Plugin for IDA Pro

binary-analysisbinary-exploitationdebuggers+8
1.3k1 year ago
ParrotNG preview

ParrotNG

GitHubikkisoft/parrotng

Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.

exploitationpenetration-testingstatic-analysis+3
4811 years ago
trivy-module-wordpress preview

trivy-module-wordpress

GitHubaquasecurity/trivy-module-wordpress

Trivy example module for WordPress

container-securitydevsecopsstatic-analysis+3
54 years ago
sleigh preview

sleigh

GitHublifting-bits/sleigh

CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…

binary-analysiscode-analysisdynamic-code-analysis+4
1945 days ago
pyREtic preview

pyREtic

GitHubmynameismeerkat/pyretic

pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering

binary-analysiscode-analysisdebuggers+5
2673 years ago
javascript-deobfuscator preview

javascript-deobfuscator

GitHublolcaken/javascript-deobfuscator

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)

code-analysisdynamic-code-analysismalware-analysis+4
825 days ago
Previous123…8Next