
kyubisweep
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
code-analysisconfiguration-auditingdevsecops+3
5
tanmayshahane/kyubisweepA lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 abdozkaya/rsc-security-auditor
🛡️ Audit your Next.js & React Server Components stack for critical vulnerabilities (CVE-2025-66478, CVE-2025-55184). Detects risks & generates fix…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 git-akki/cso-vibecheck
Senior-CSO security audit skill for vibe-coded apps. 22-check audit anchored to real 2026 incidents (Moltbook, Lovable CVE-2025-48757). Drop-in…
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
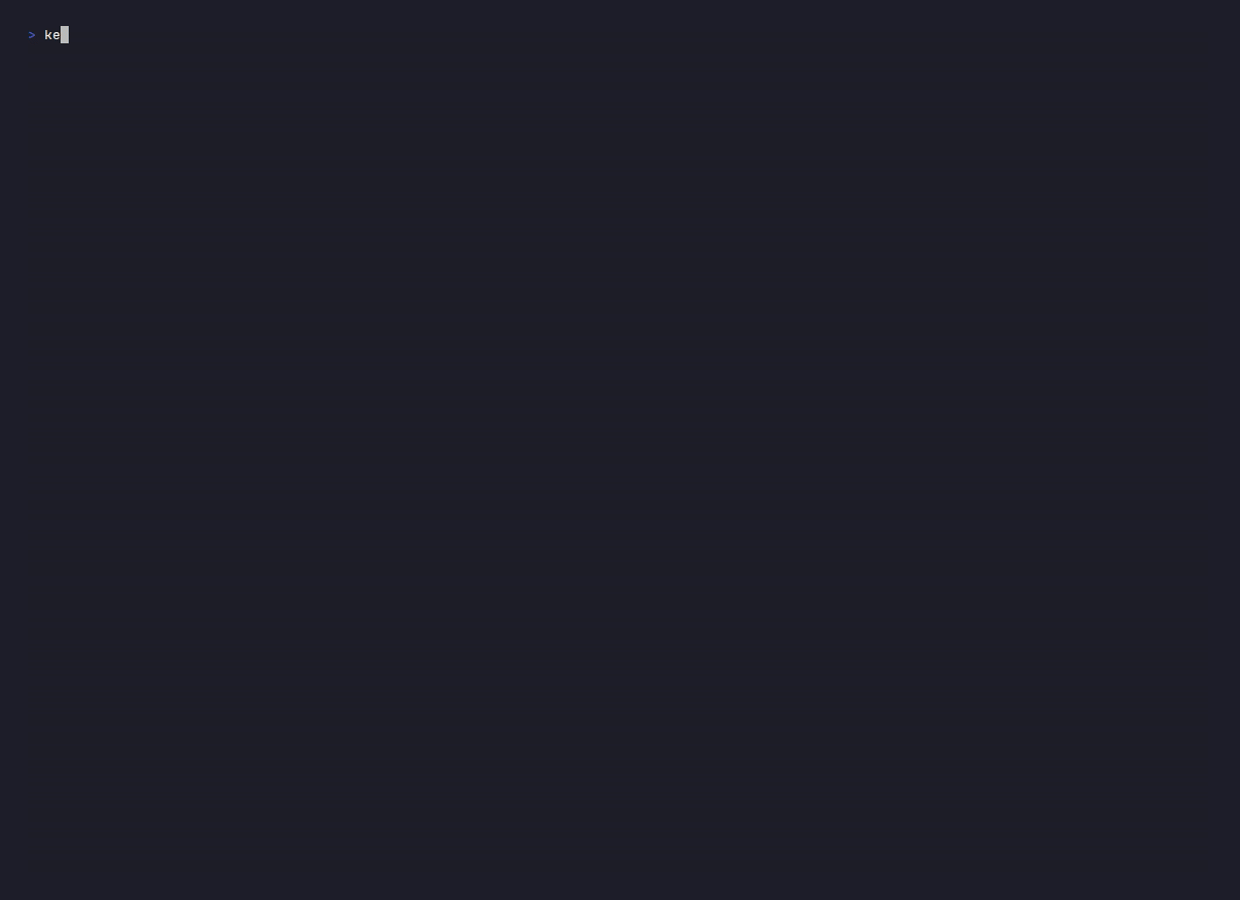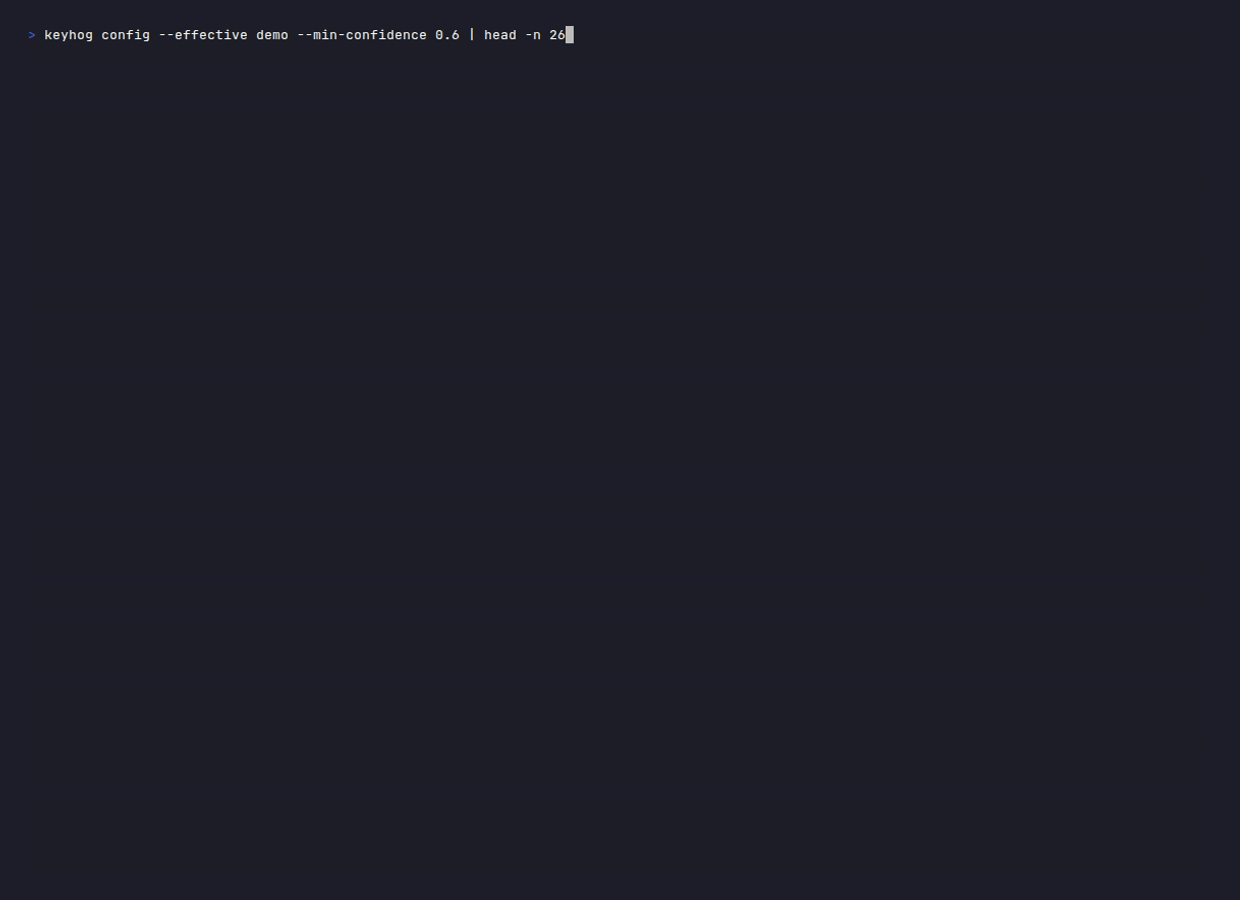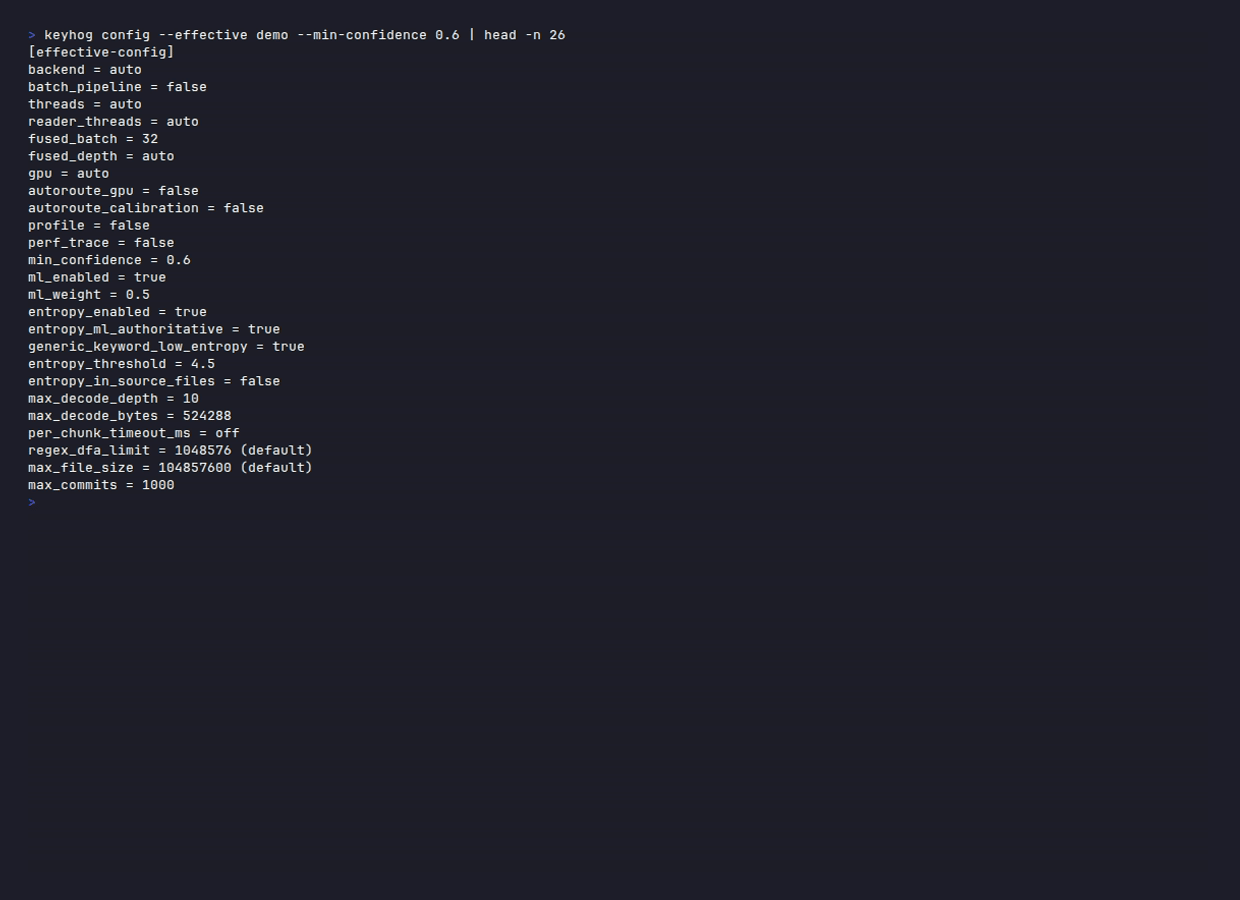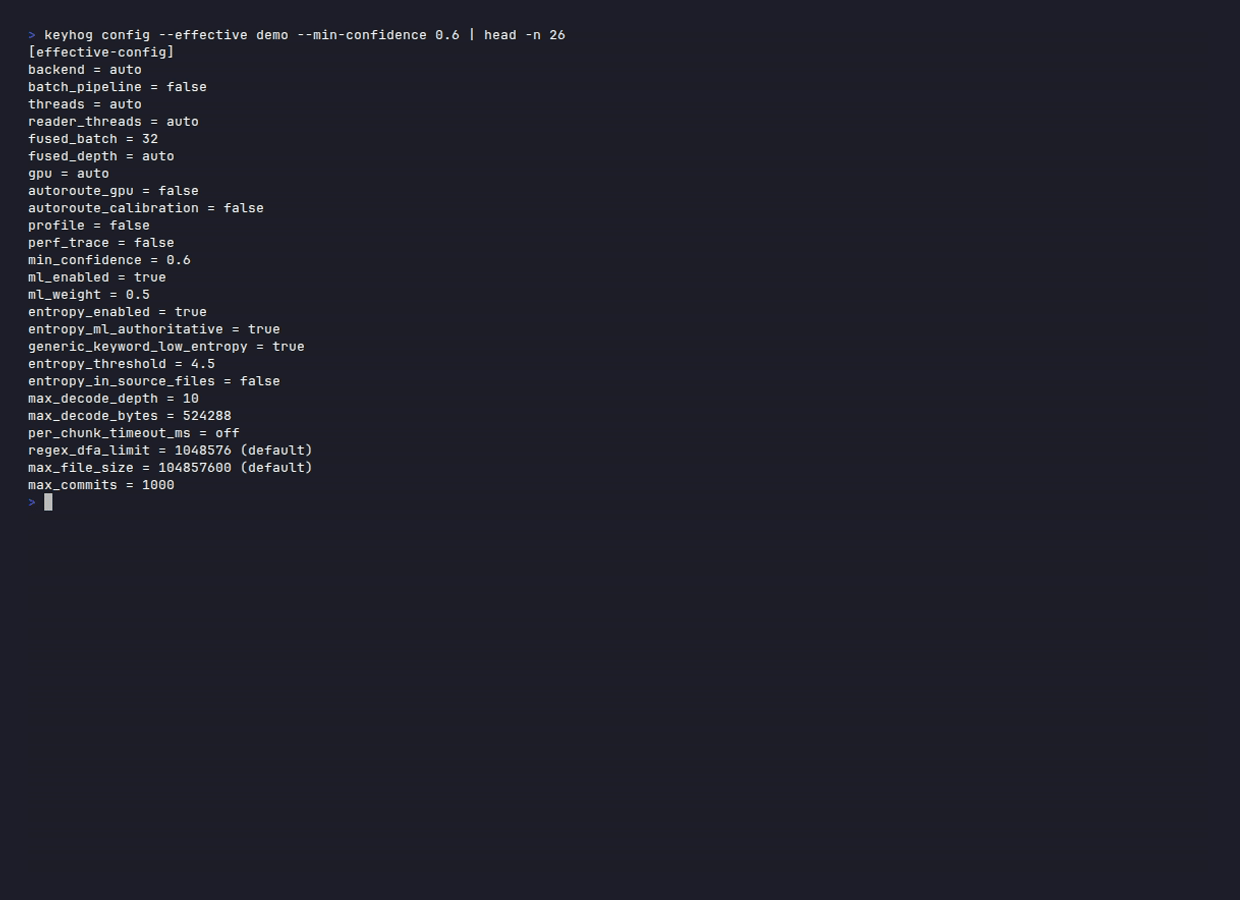 santhreal/keyhog
Open-source secret scanner in Rust
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 califio/ngxray
ngxray — nginx config security scanner
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 skyscanner/whispers
Identify hardcoded secrets in static structured text
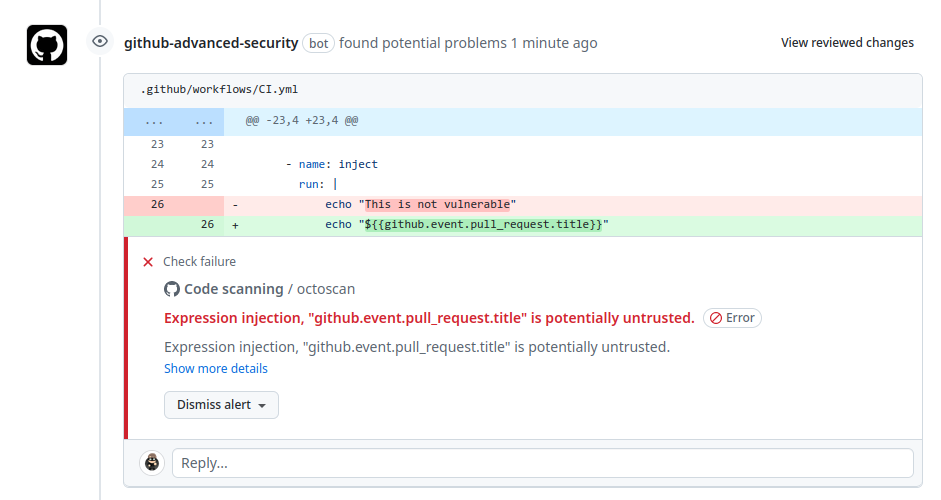 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…