

smalien
 h1nayoshi/smalien
Information flow analysis tool for Android applications
android-securitydynamic-analysis-sandboxinginformation-gathering+2
12
h1nayoshi/smalienInformation flow analysis tool for Android applications
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 josue87/apkvuln
Static analysis of APKs with regular expressions
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 gmh5225/cve-2022-35737
Proof-of-concept exploit code and technical analysis for CVE-2022-35737, an integer overflow in SQLite3's sqlite3_str_vappendf function enabling…
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 synacktiv/krustyloader-analysis
KrustyLoader Analysis
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
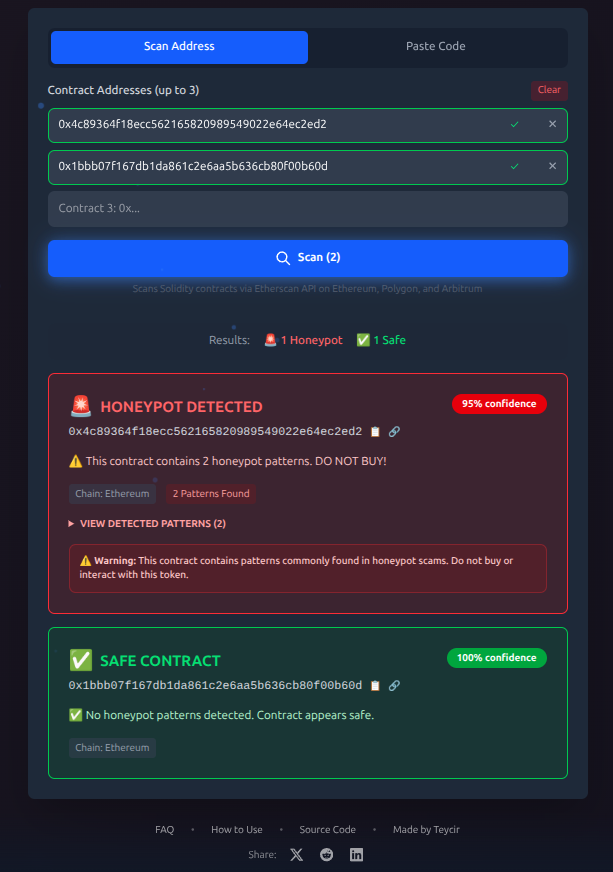 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 alvaroguzmancode/cve-2026-98432
Rust detector and local lab for CVE-2026-98432, a Linux IPv4 TCP use-after-free in inet_opt/ireq_opt: static ELF analysis, kprobe reachability…
 capivara-research/cve-2026-90931
Bilingual analysis and safe lab PoC for CVE-2026-90931, a stored XSS in LaraDashboard's SVG media upload, with source verifier, marker payload, and…
 saretawa/cve-2026-40489
Proof-of-concept and patch analysis for CVE-2026-40489, a stack buffer overflow in editorconfig-core-c ec_glob(), with build steps and a Python crash…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…