

noir
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
api-securitydevsecopspenetration-testing+3
owasp-noir/noirHunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
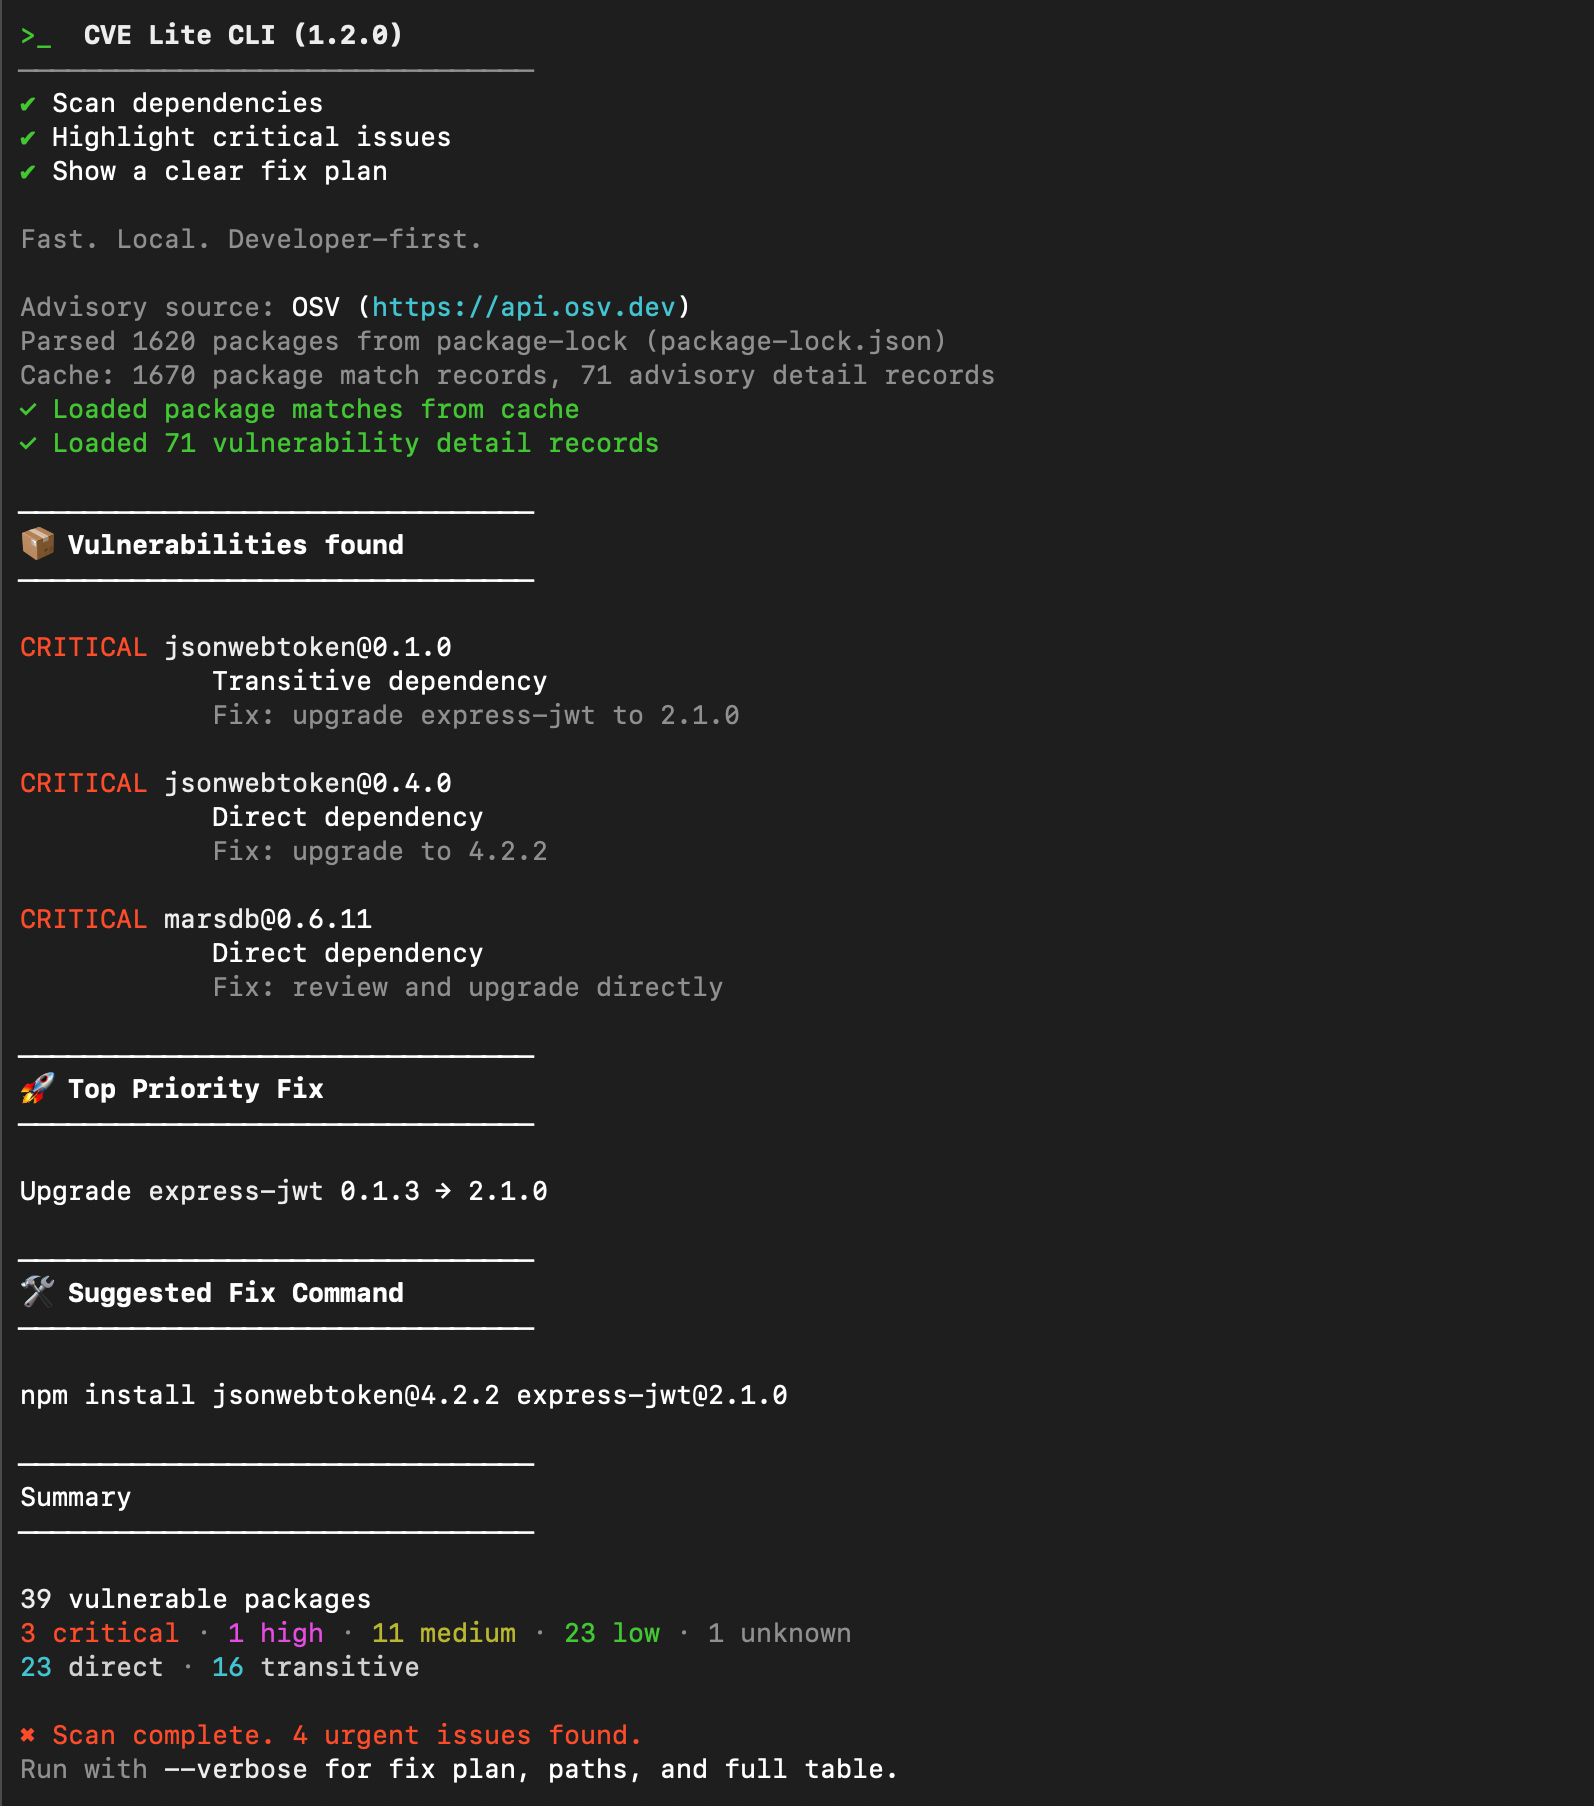 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
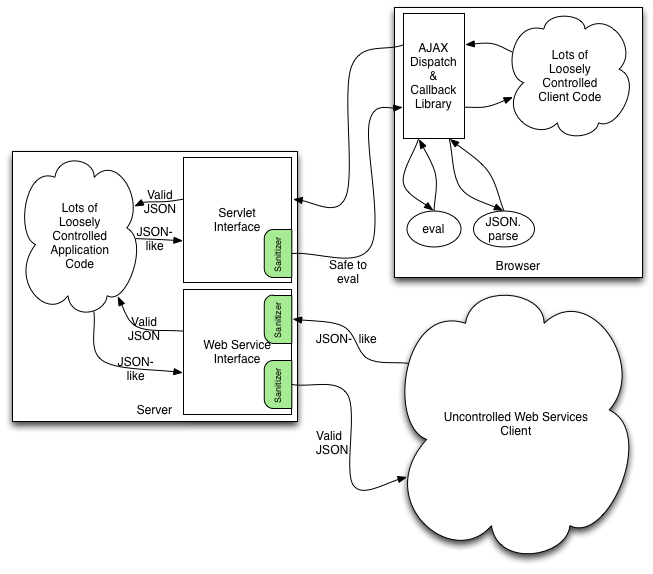 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 owasp/decodebox
Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…
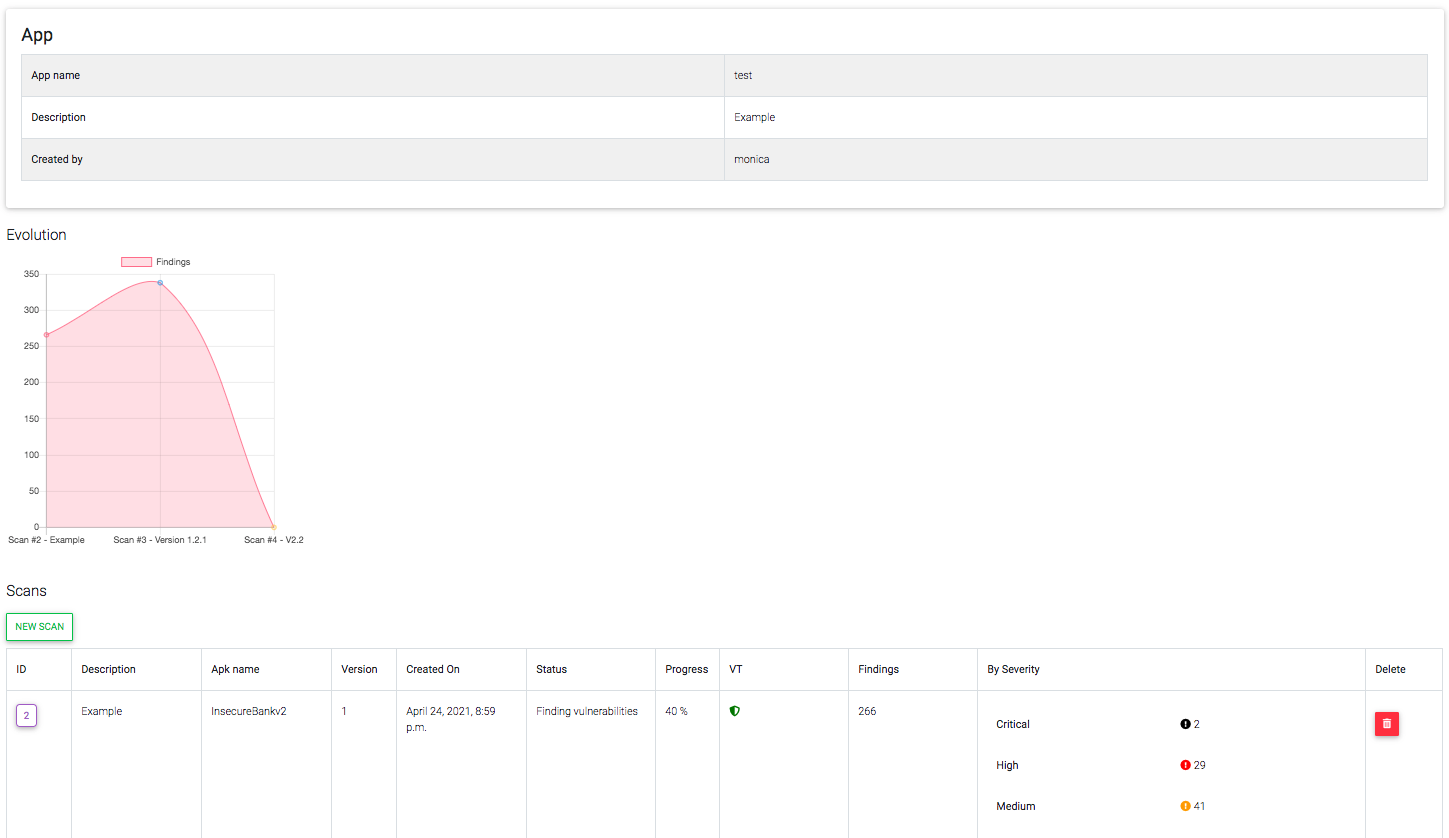 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.