Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

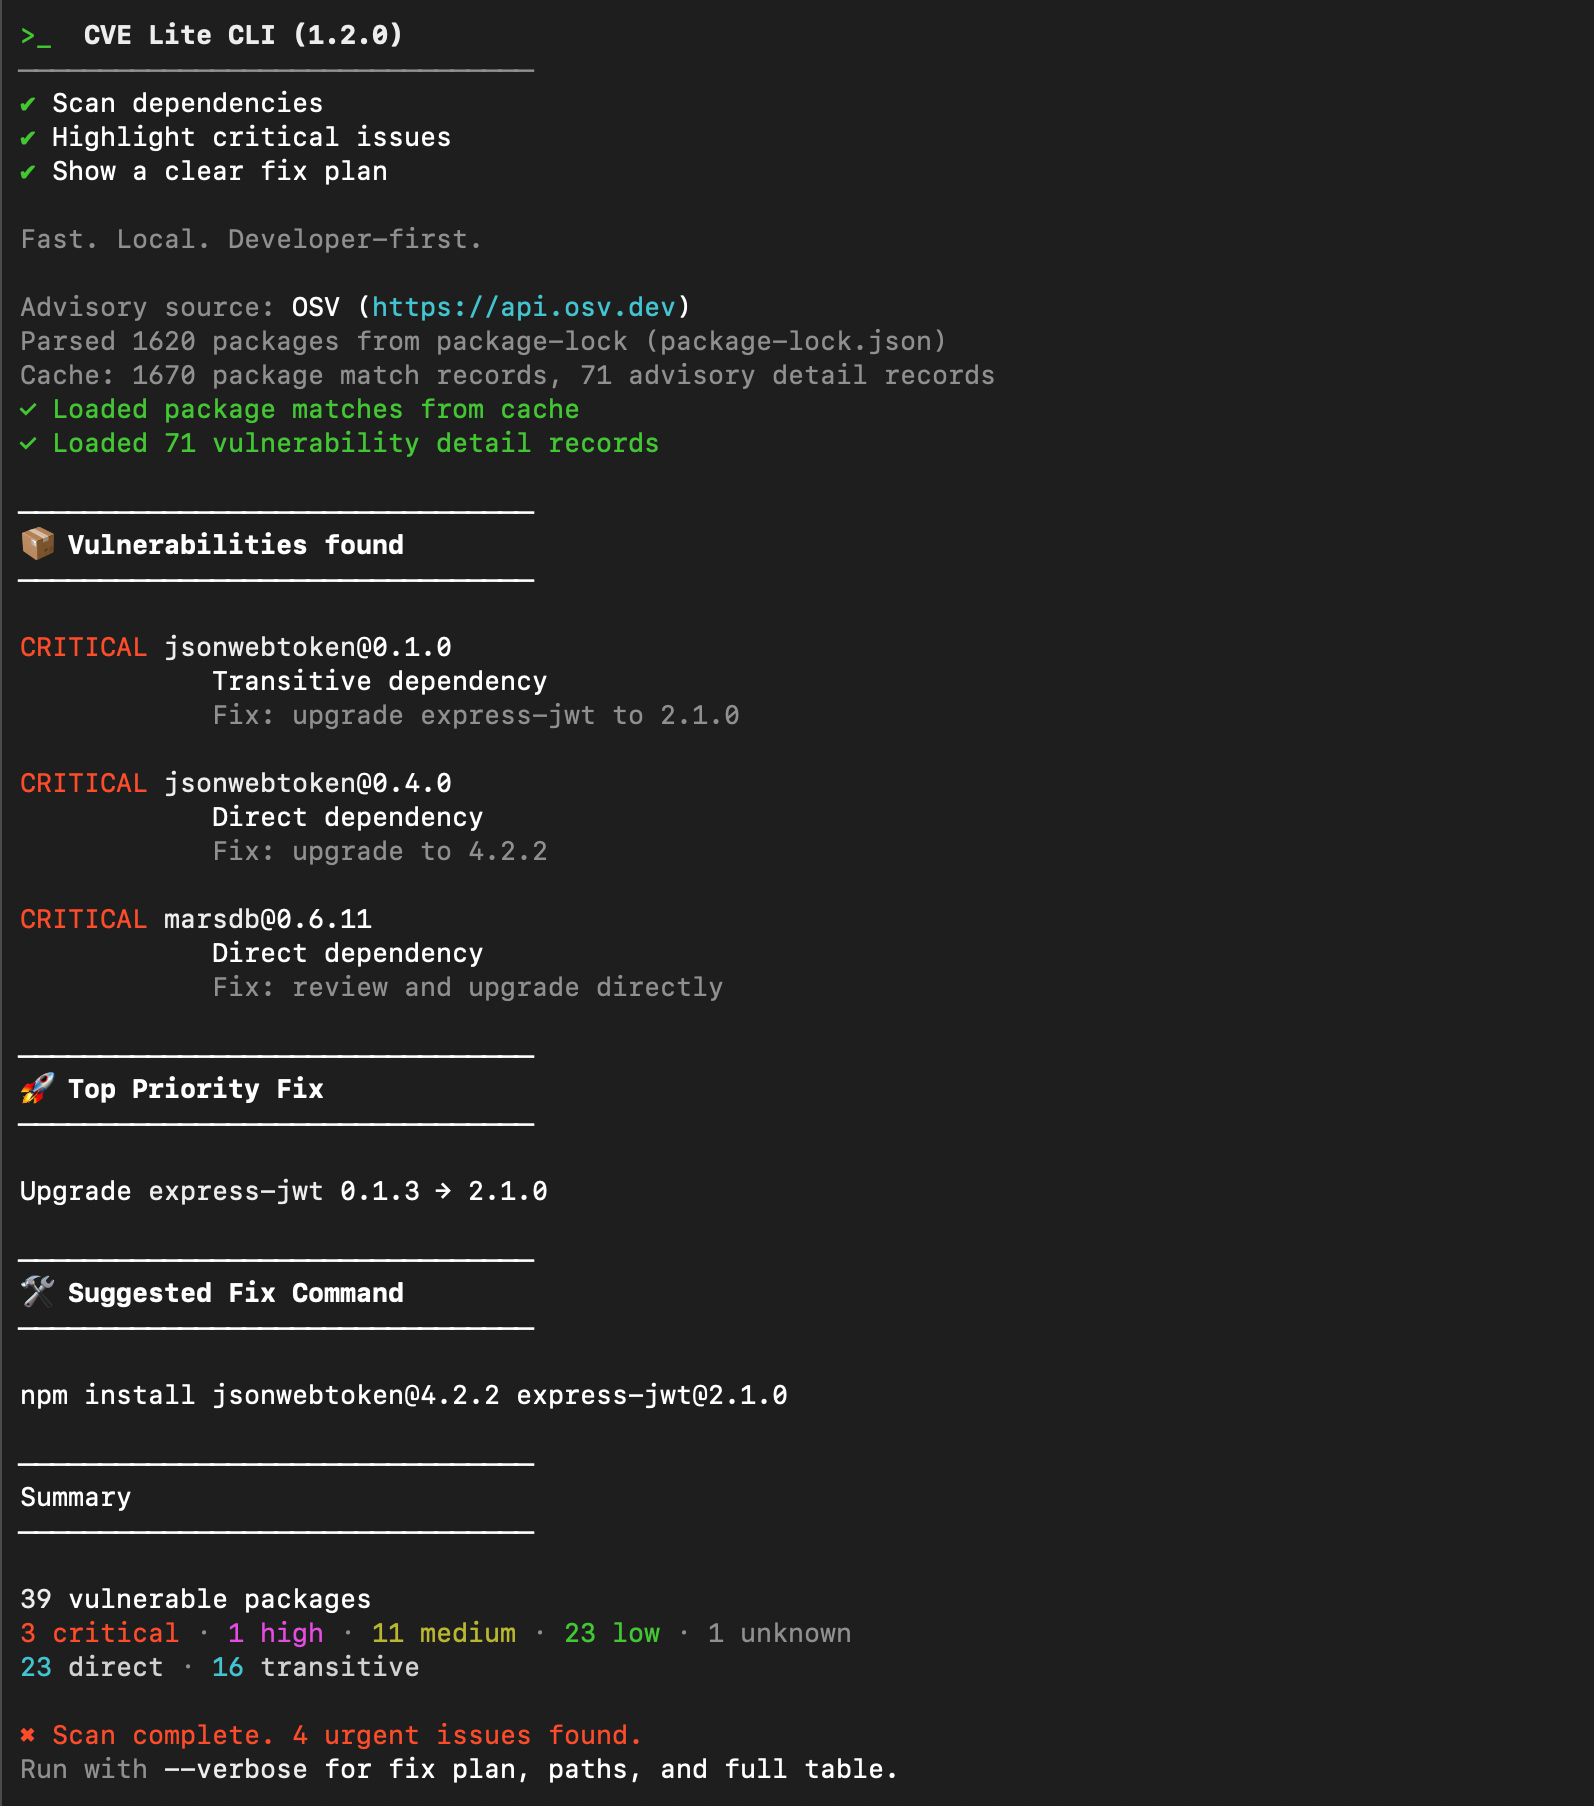
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.

Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.

Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Django application that performs SAST and Malware Analysis for Android APKs

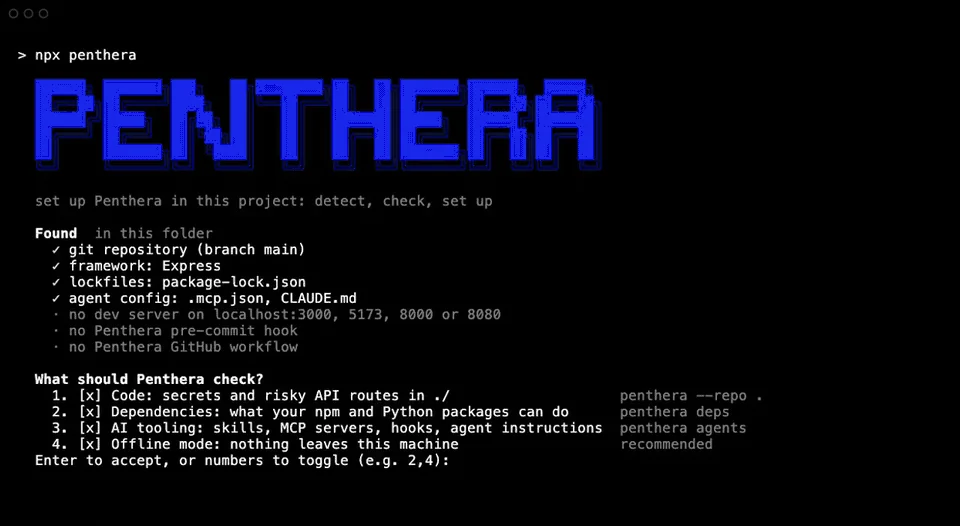
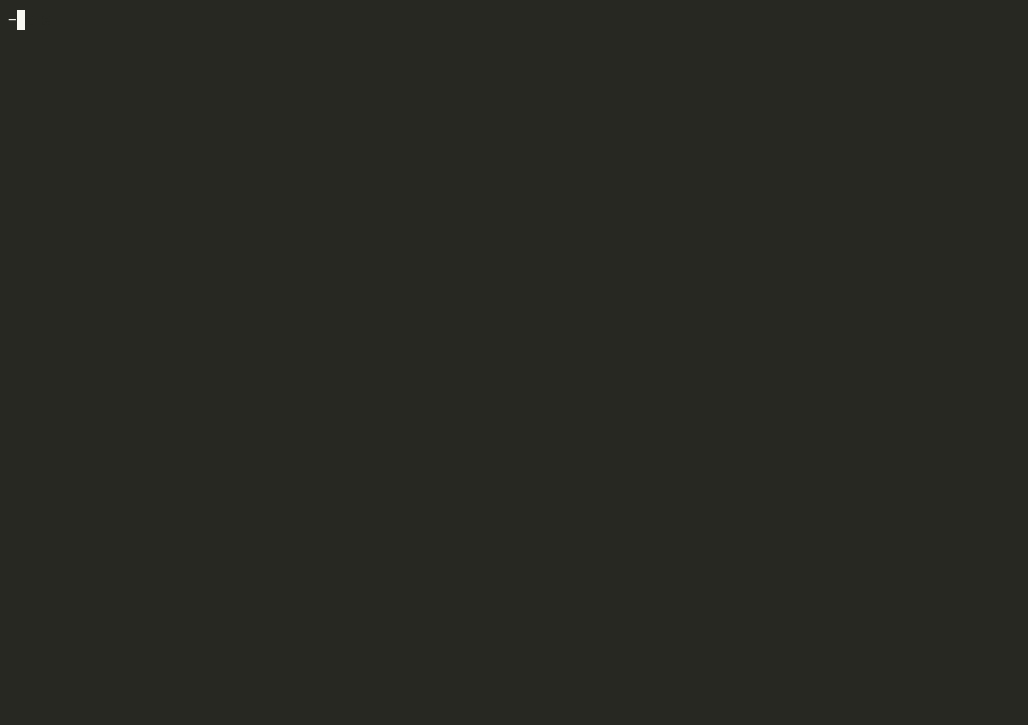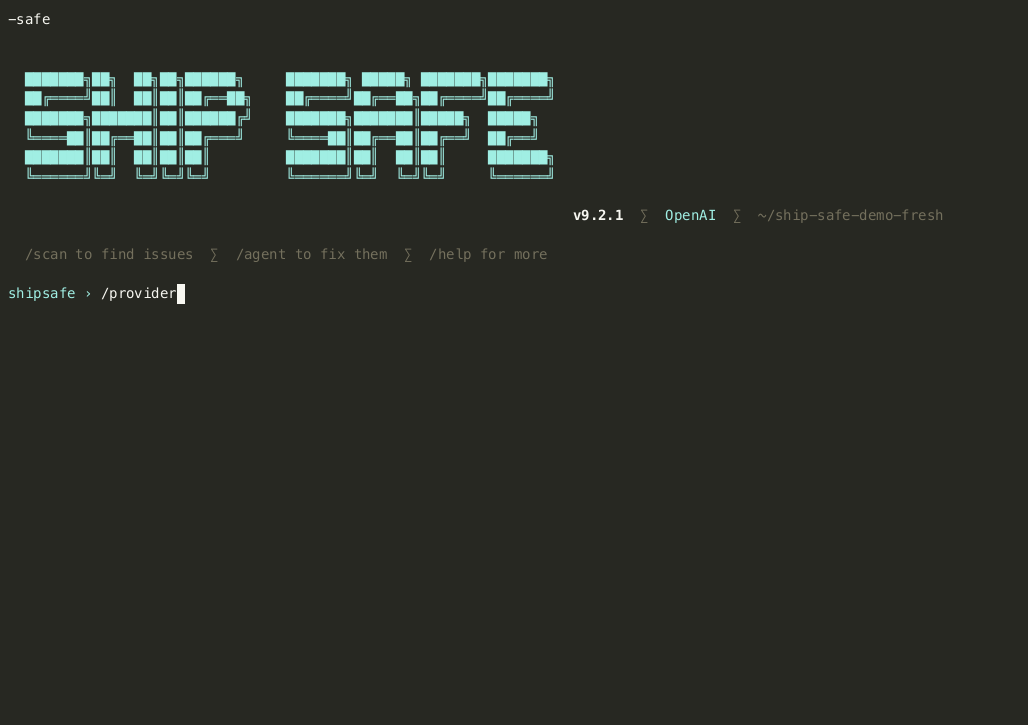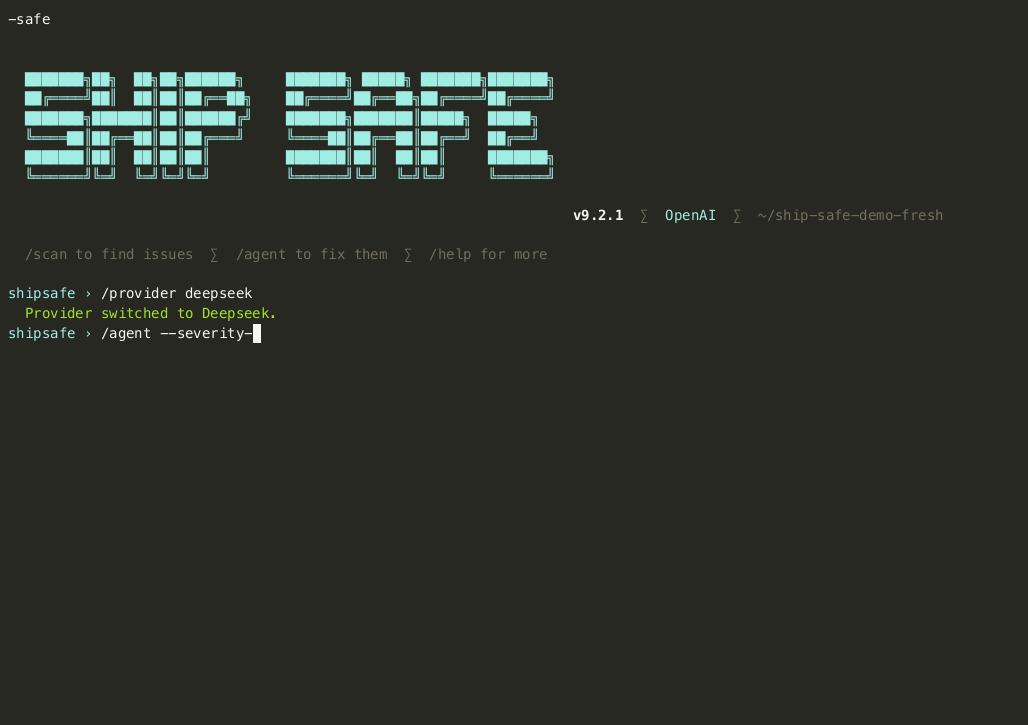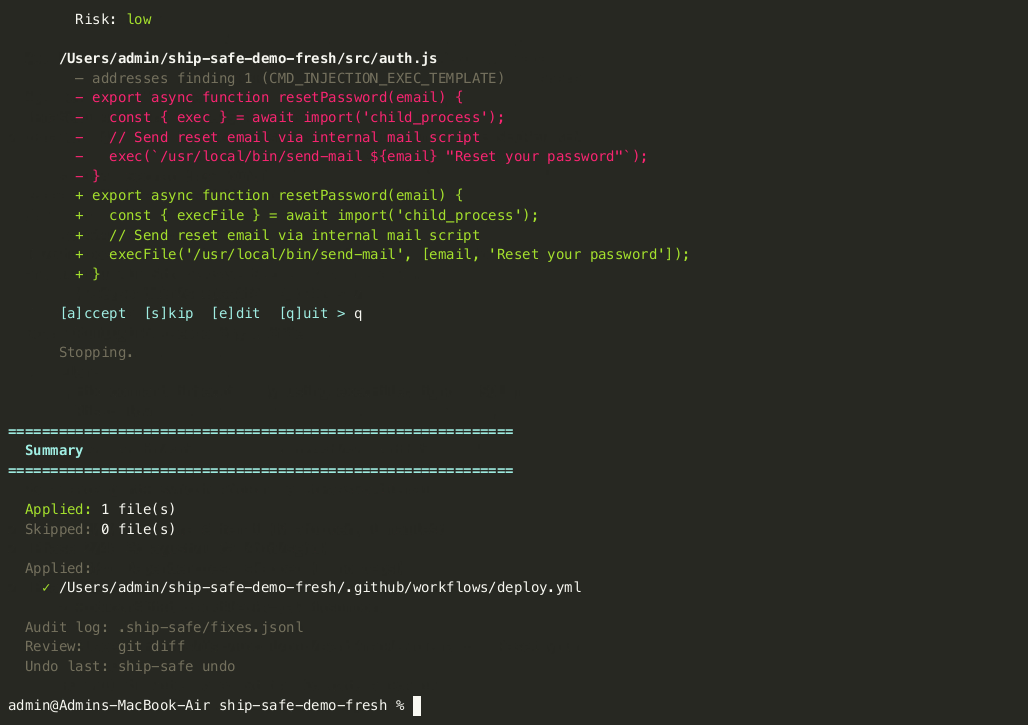
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.

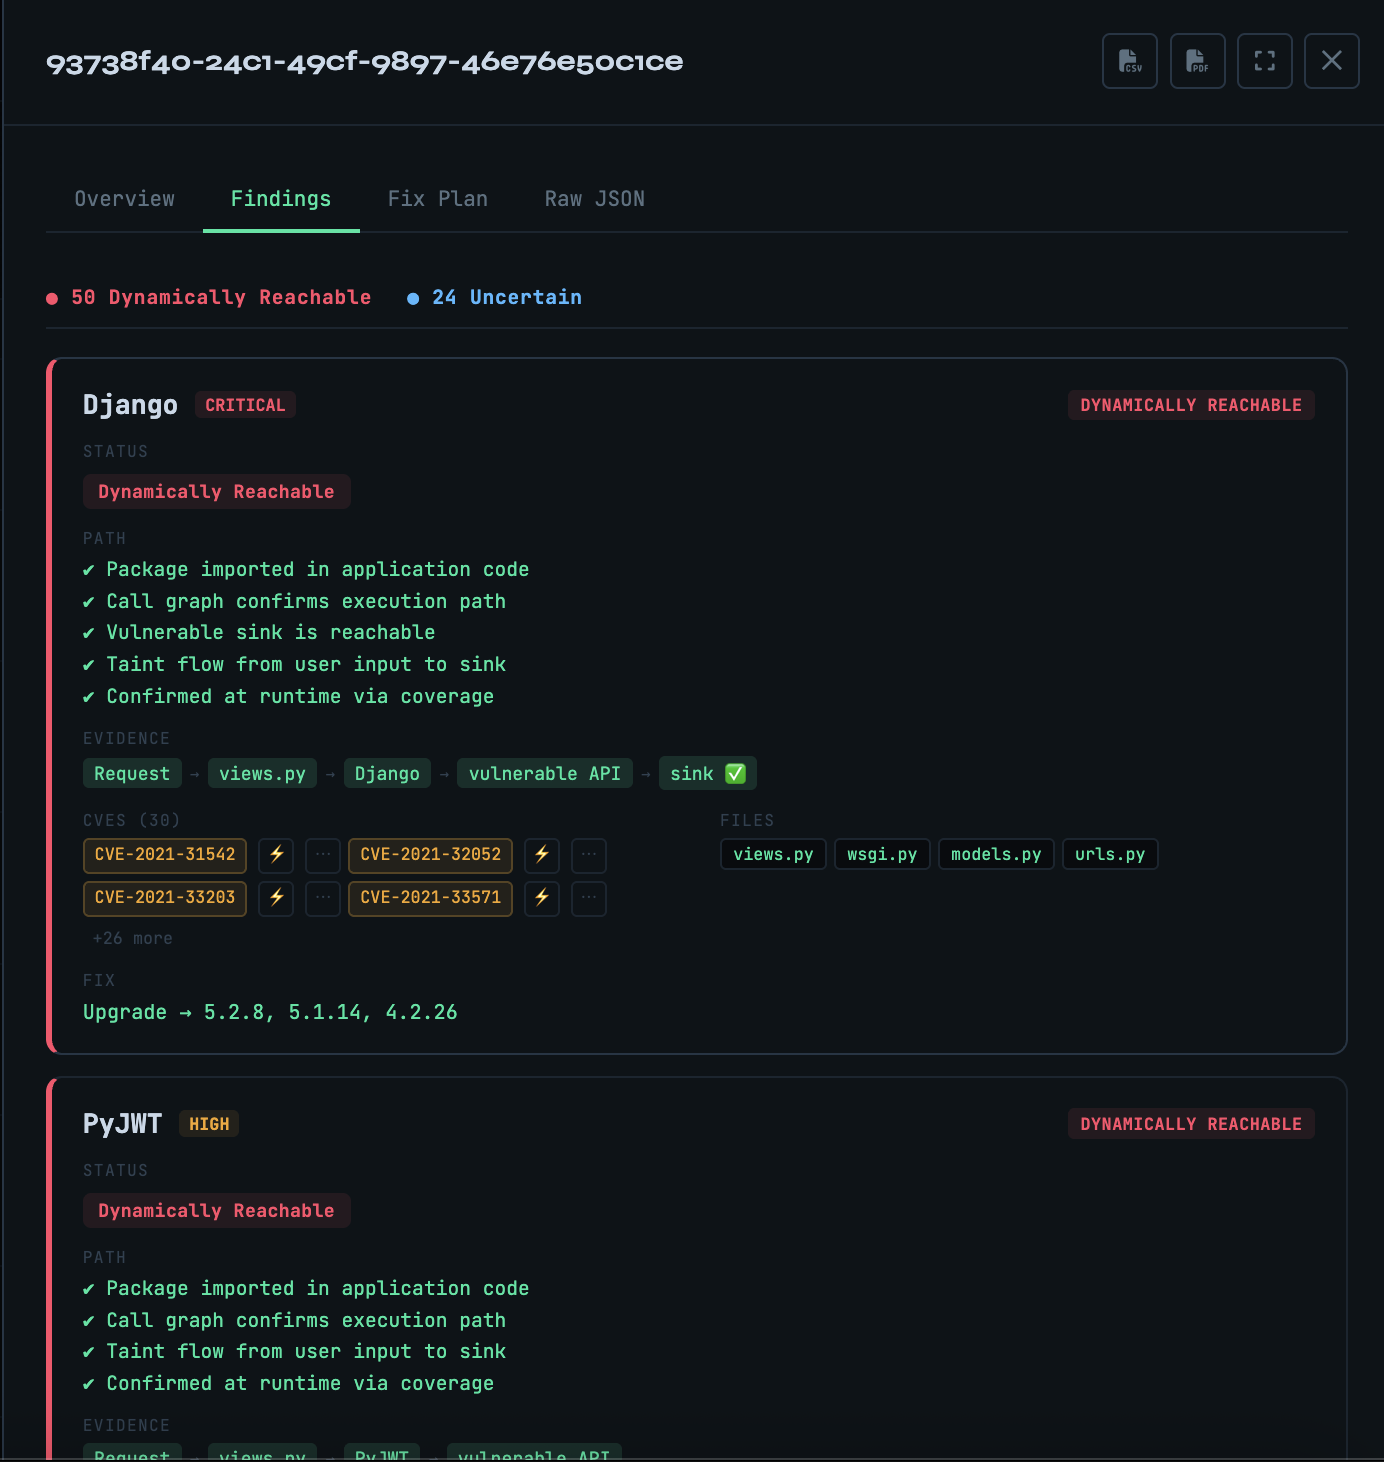
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

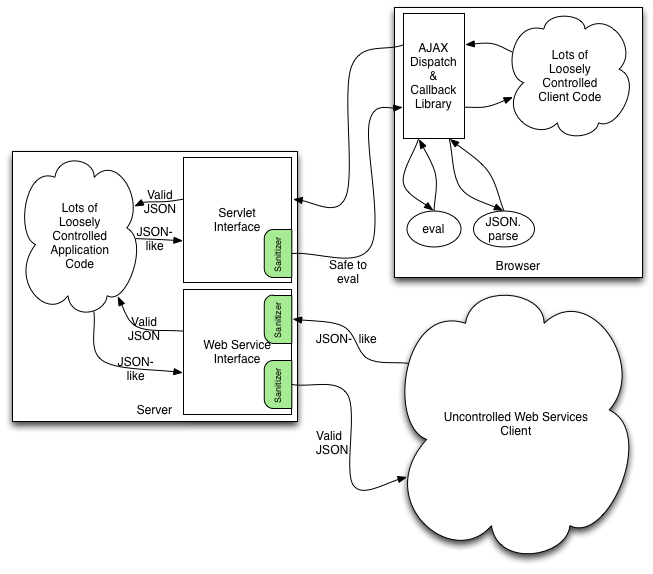
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.

Source code for the Binaries of OWASP WrongSecrets

The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…

Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

OWASP Secure Agent Playbook Project