Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Program for determining types of files for Windows, Linux and MacOS.

UNIX-like reverse engineering framework and command-line toolset

🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.


A powerful and user-friendly binary analysis platform!

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

Ghidra is a software reverse engineering (SRE) framework

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…

Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…

Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…

Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.

Client-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…

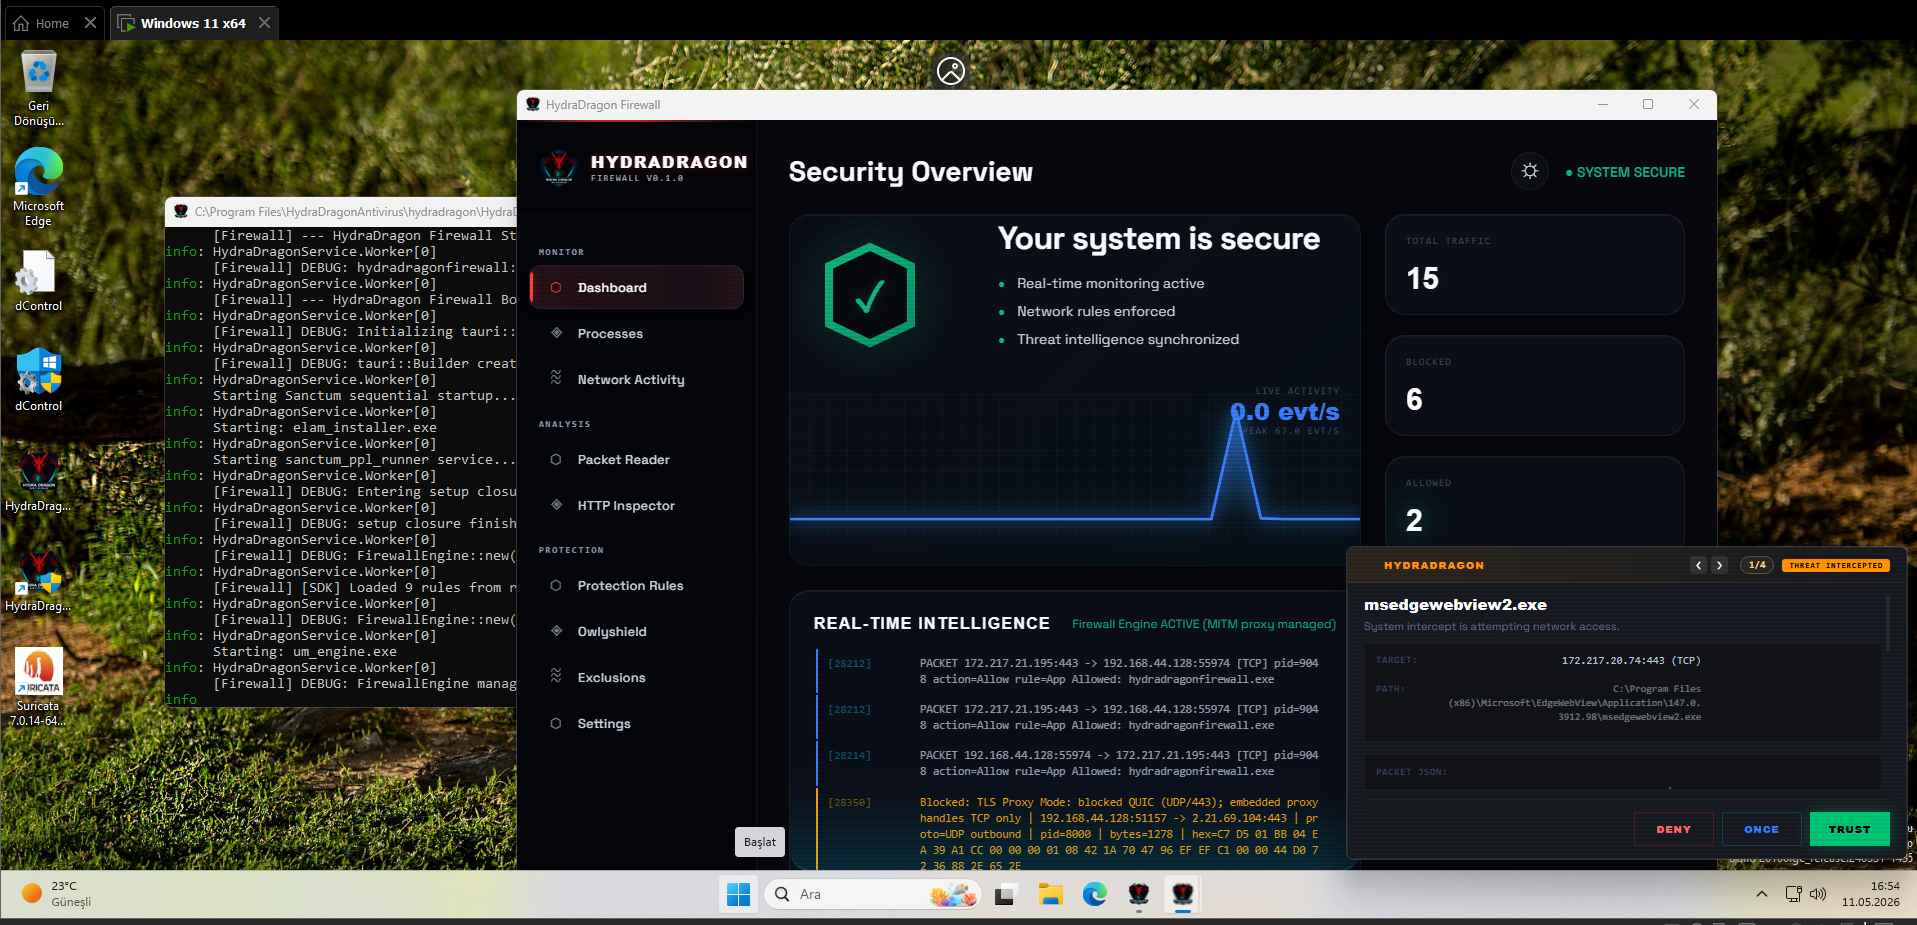
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…


Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes