
CVE-2026-67595
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
command-and-controlmalware-analysisstatic-analysis+4
ilhomjonr/cve-2026-67595CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
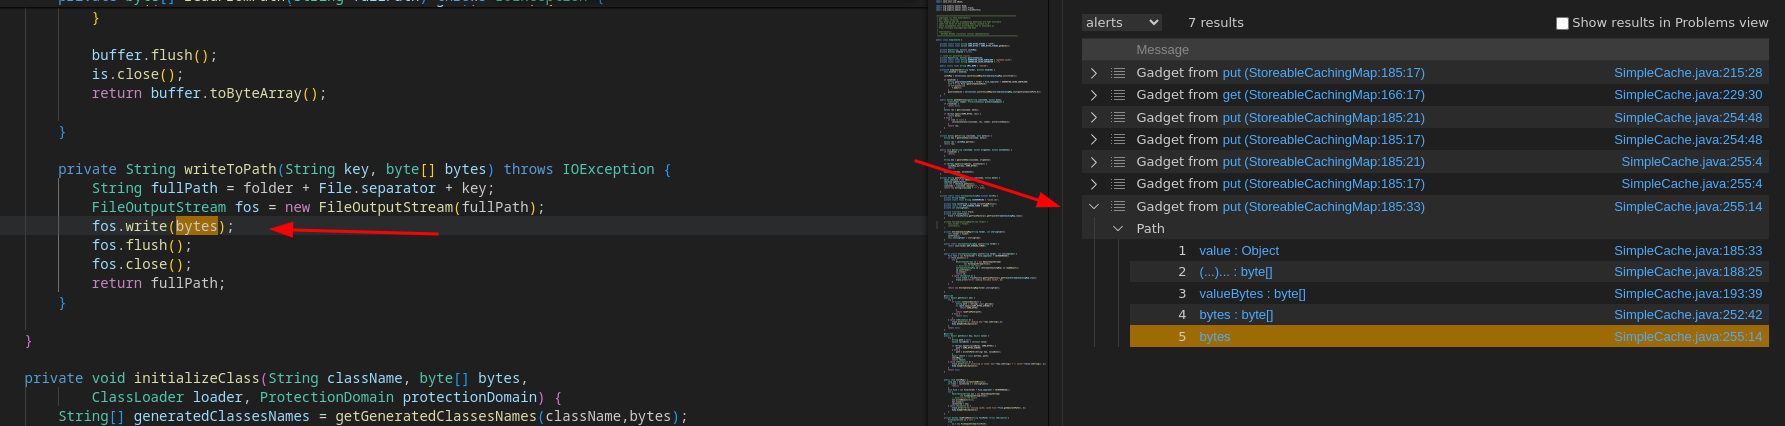 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
 renewablehacking/cve-2020-7598
Educational lab demonstrating CVE-2020-7598 prototype pollution in minimist with a vulnerable Node.js/Express app, exploit payload, and…
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 jftierno/-cve-2018-6574
Exploit for CVE-2018-6574, a Go command injection vulnerability. Provides a targeted payload for testing and validating the flaw in affected systems.
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 aserper/ddetect
Simple DDE object detector