
rz-ghidra
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
binary-analysisreverse-engineeringstatic-analysis
rizinorg/rz-ghidraDeep ghidra decompiler and sleigh disassembler integration for rizin
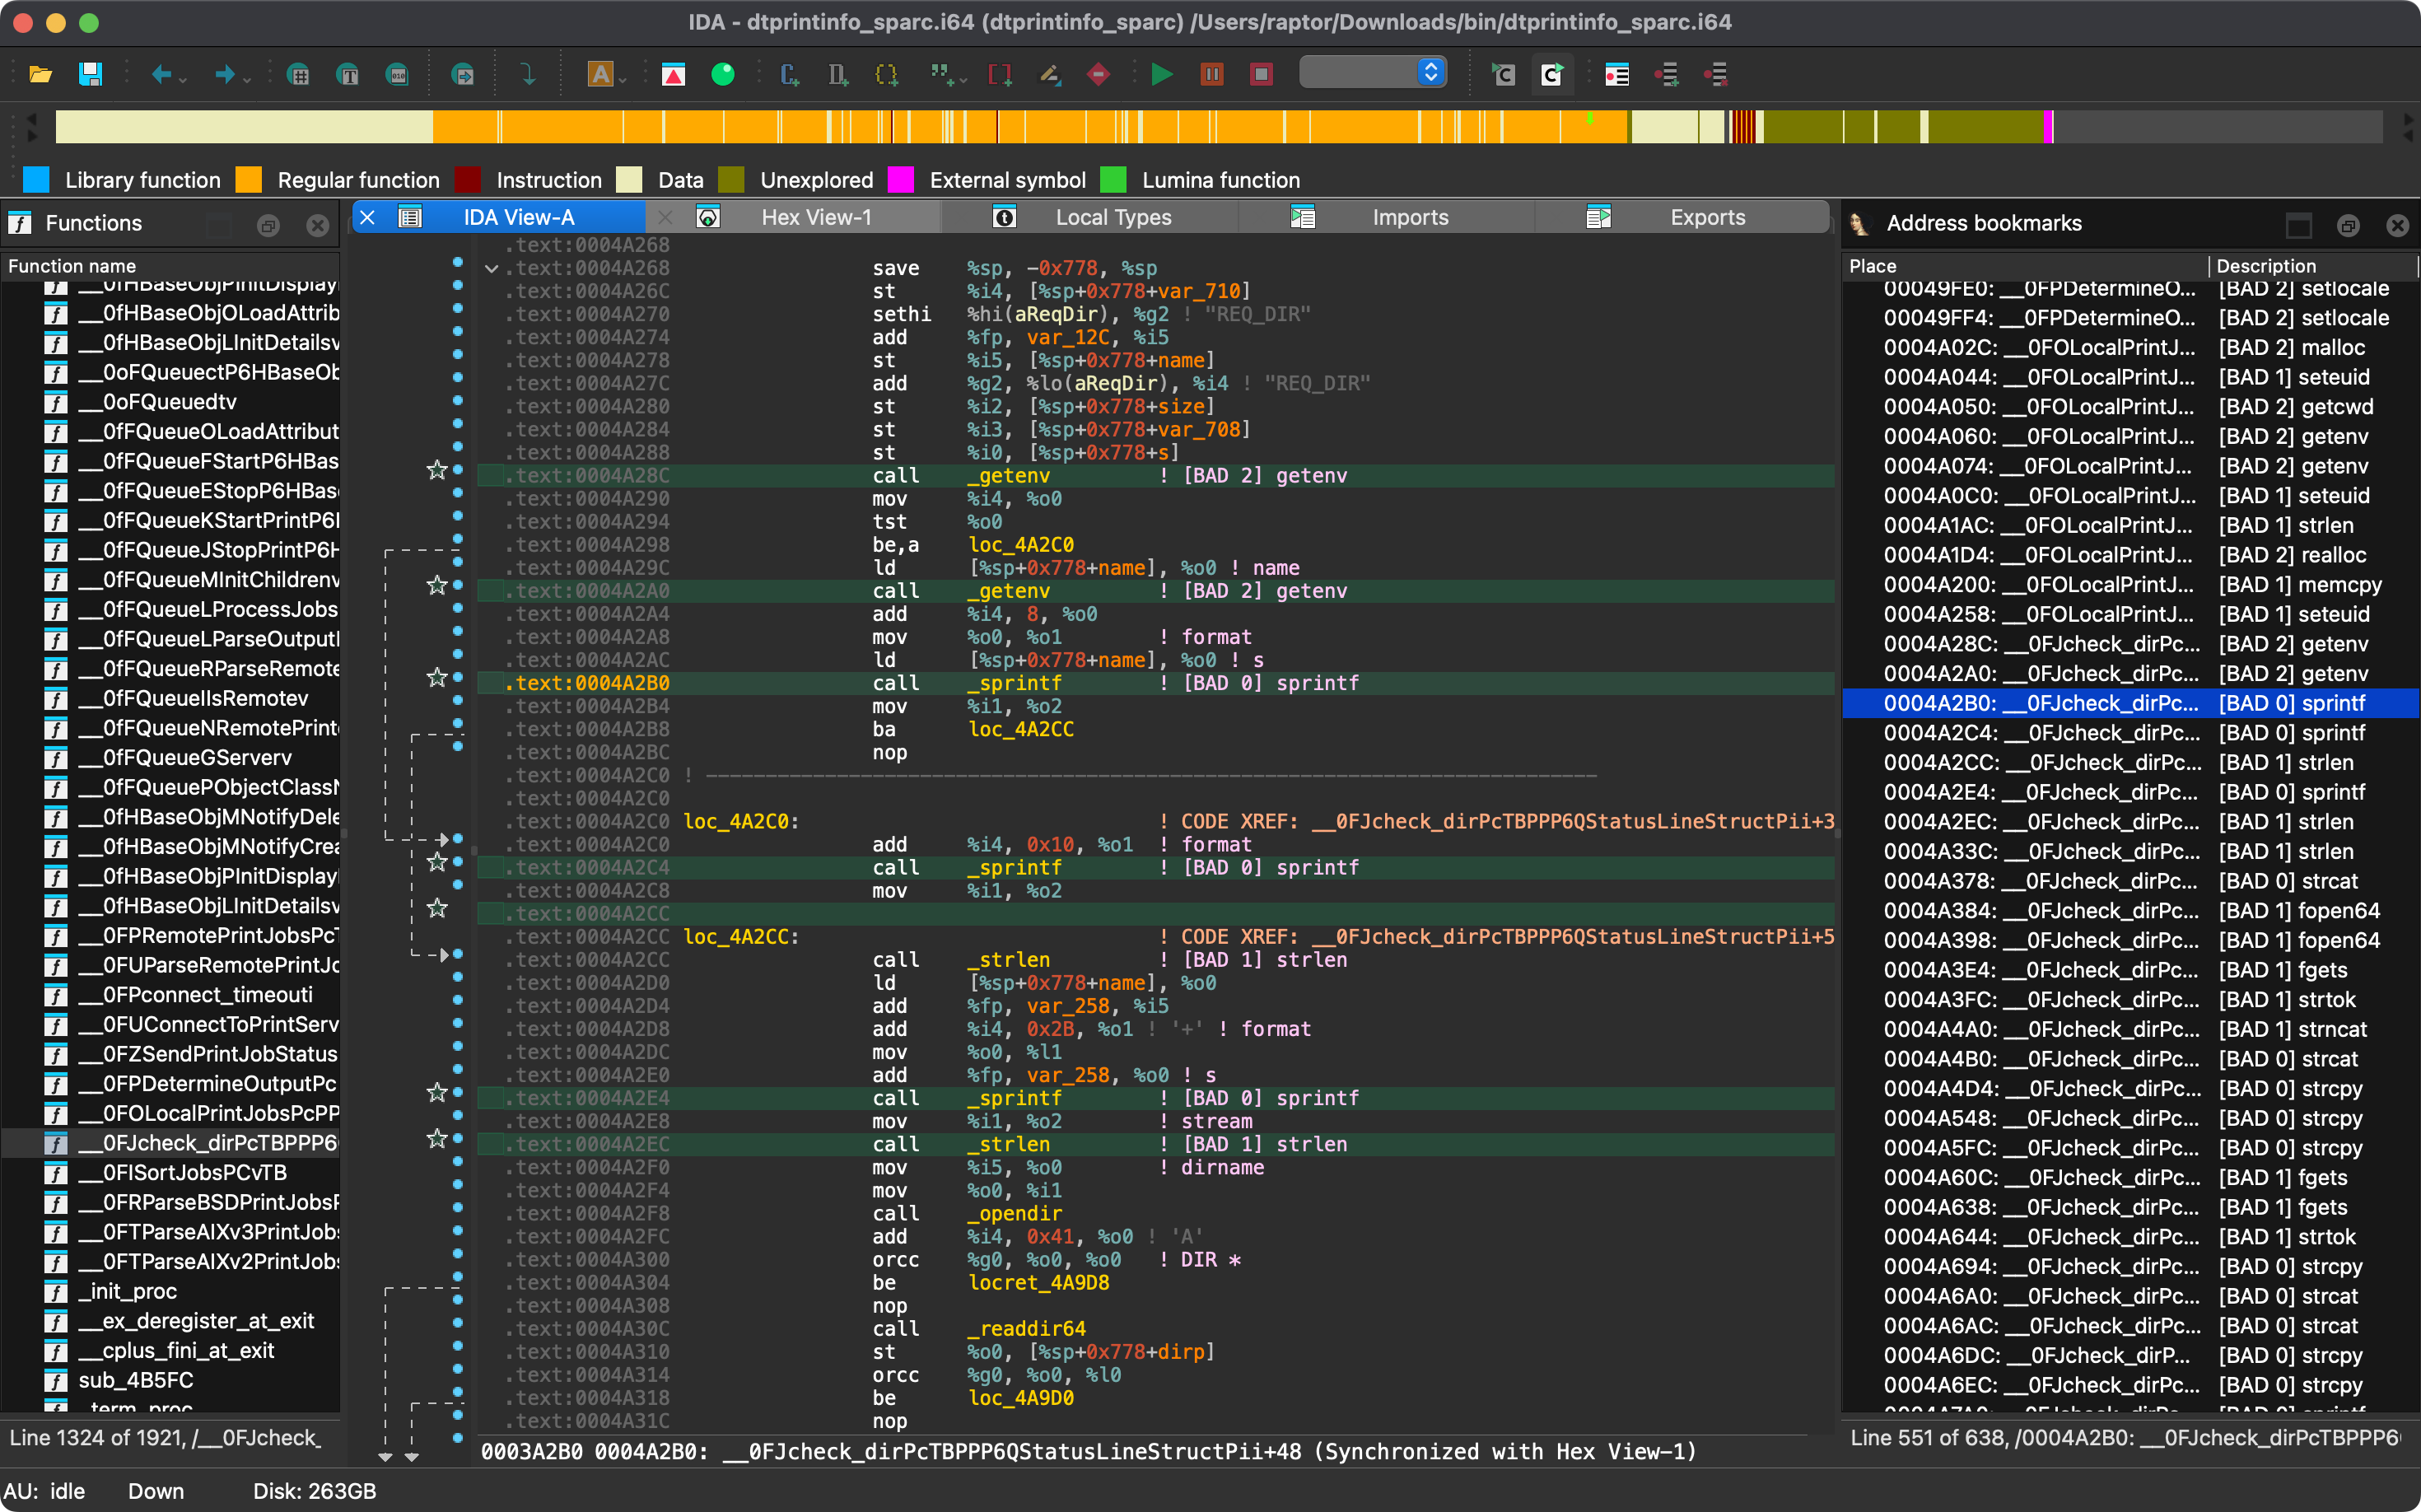 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
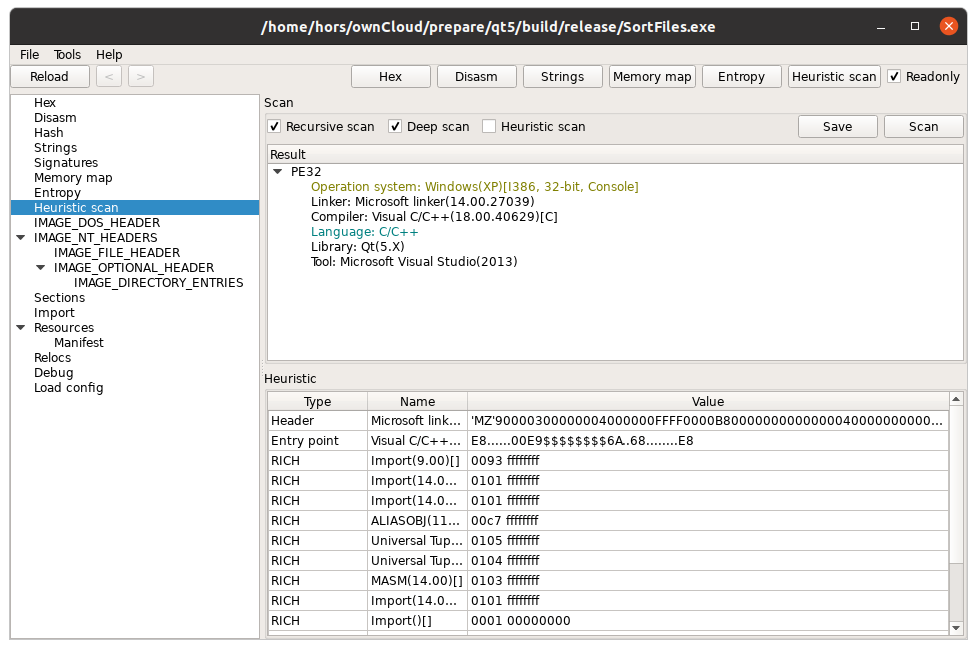 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
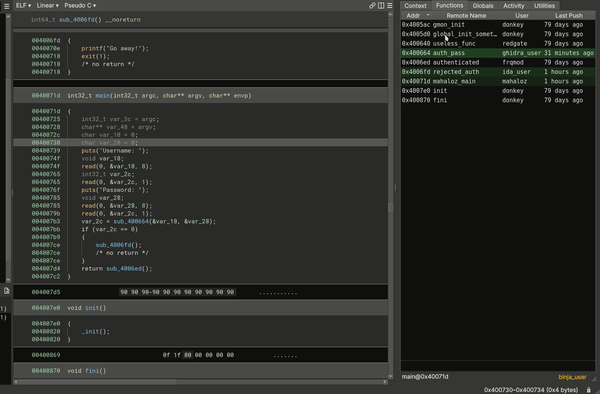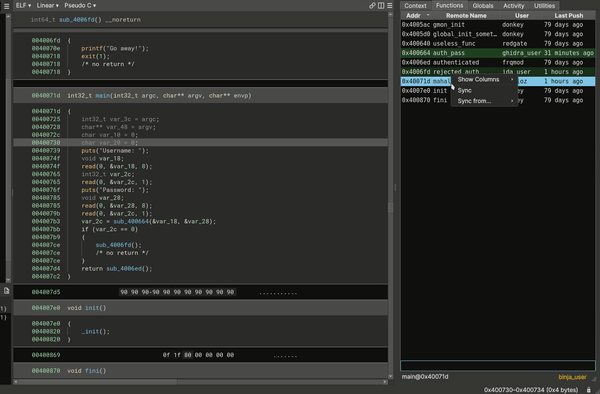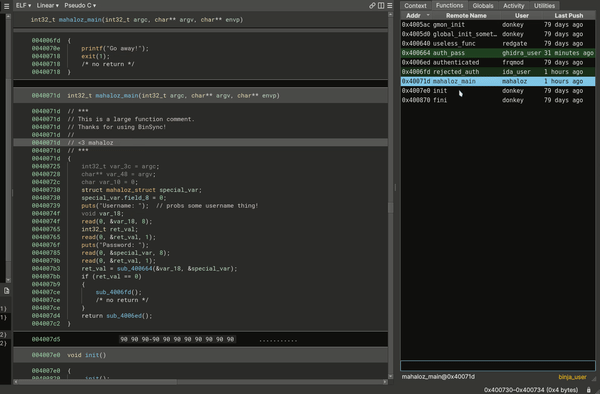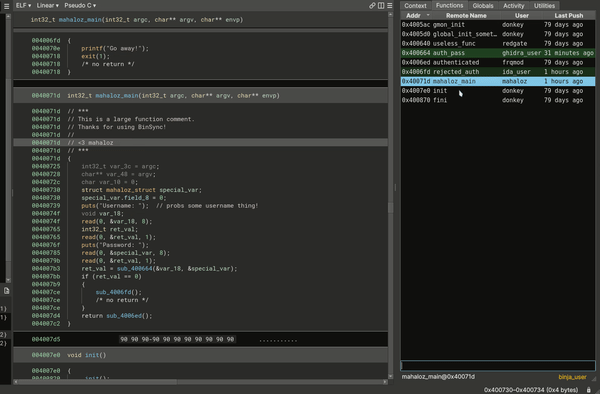 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
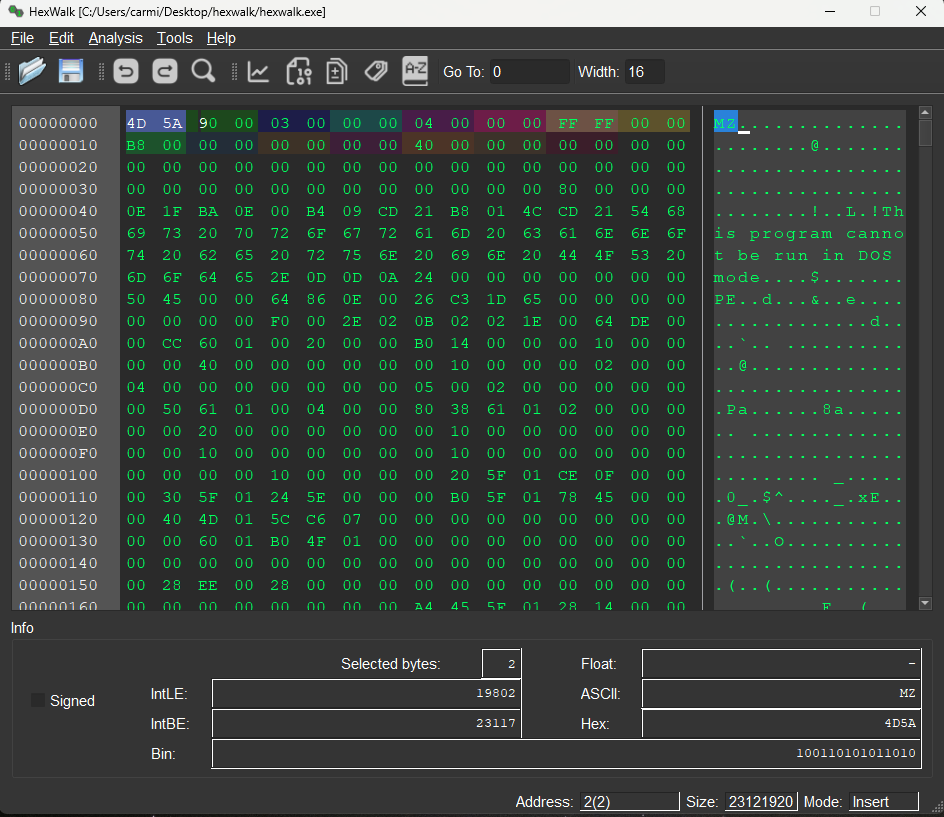 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
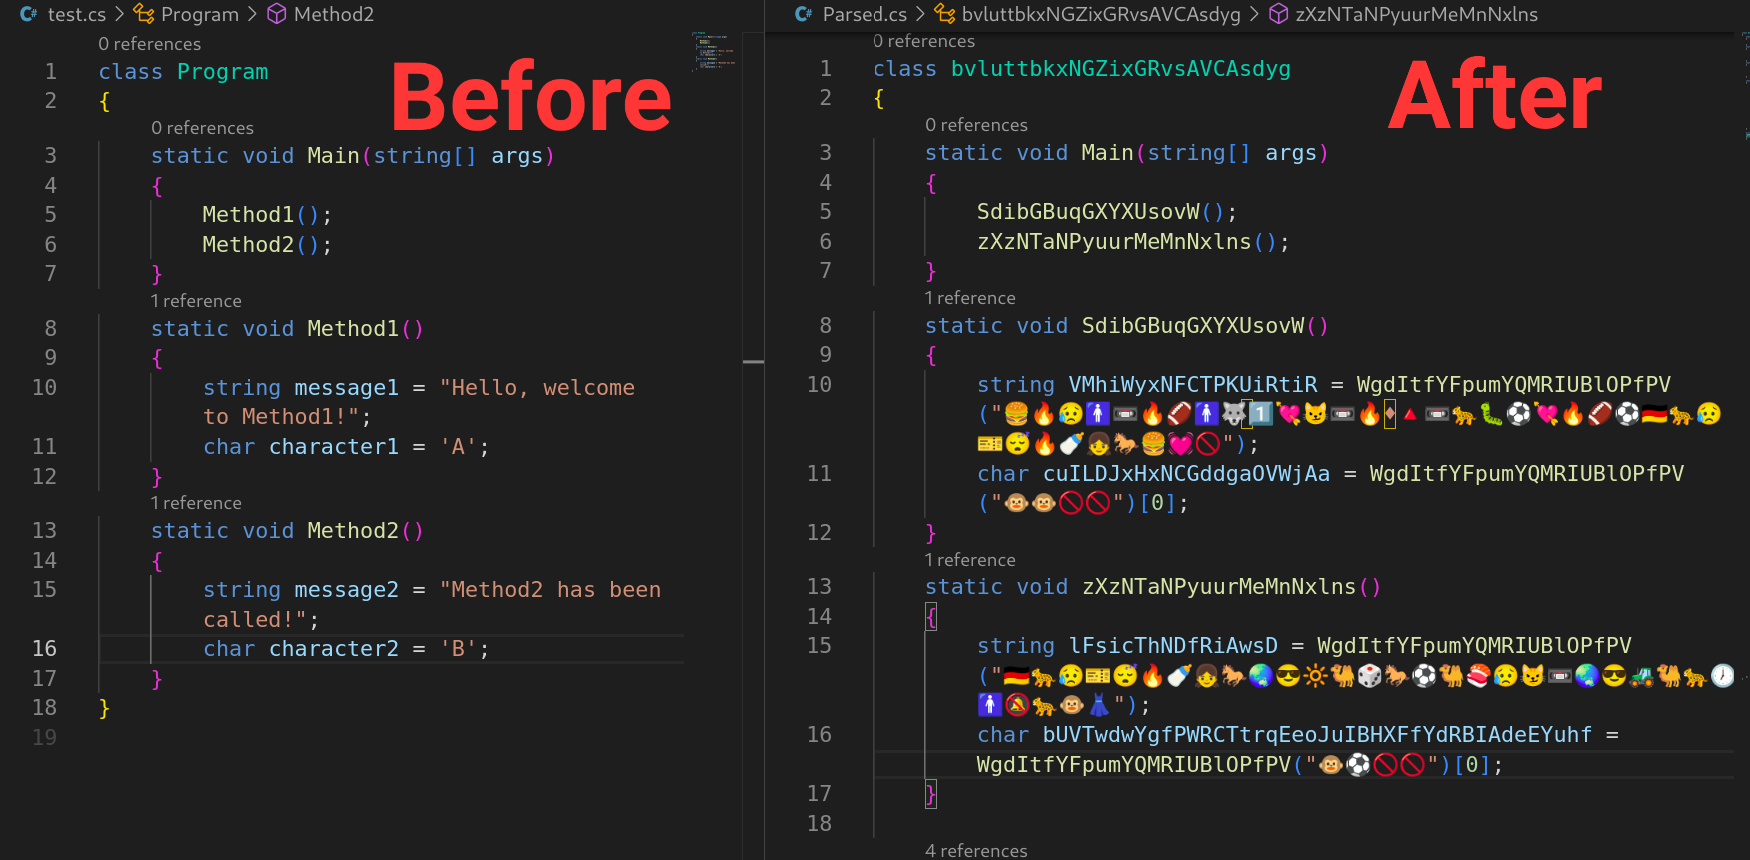 tomiwa-ot/emojify
C# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
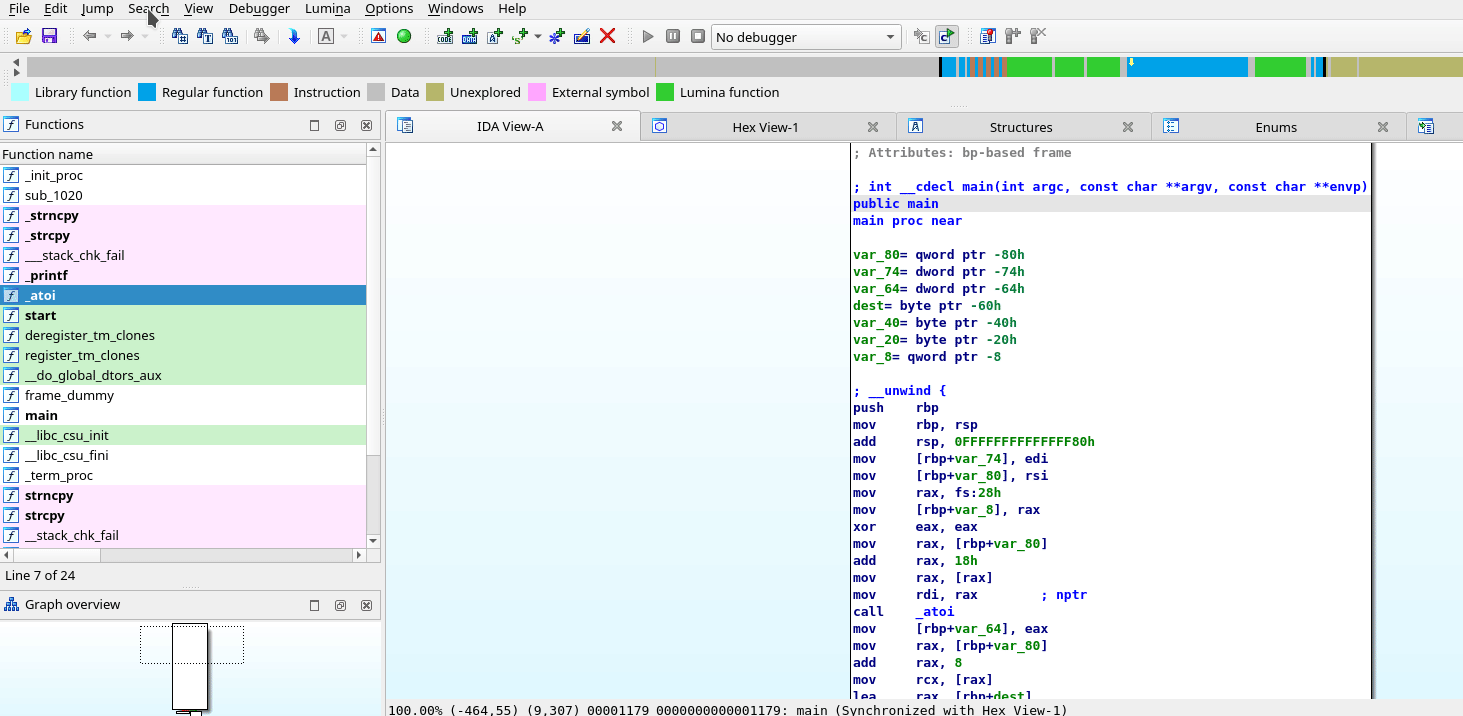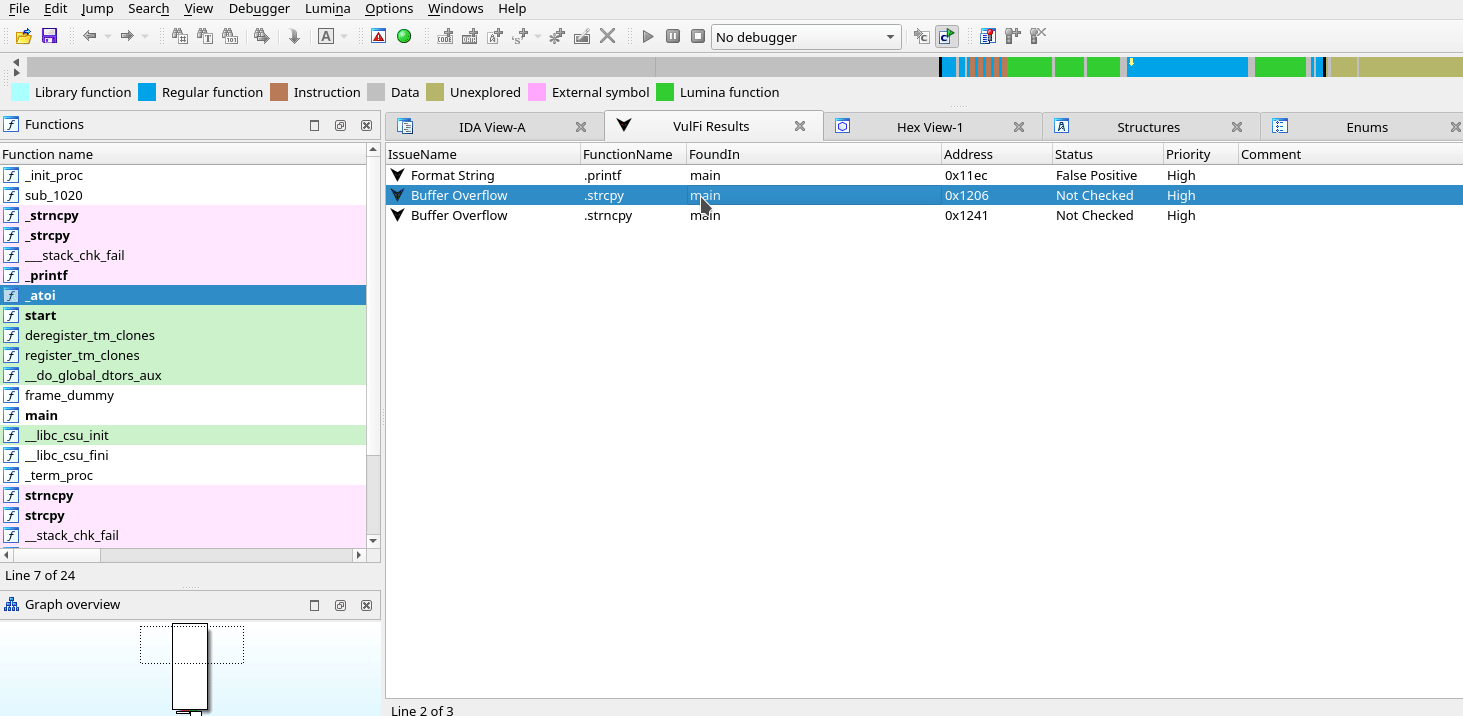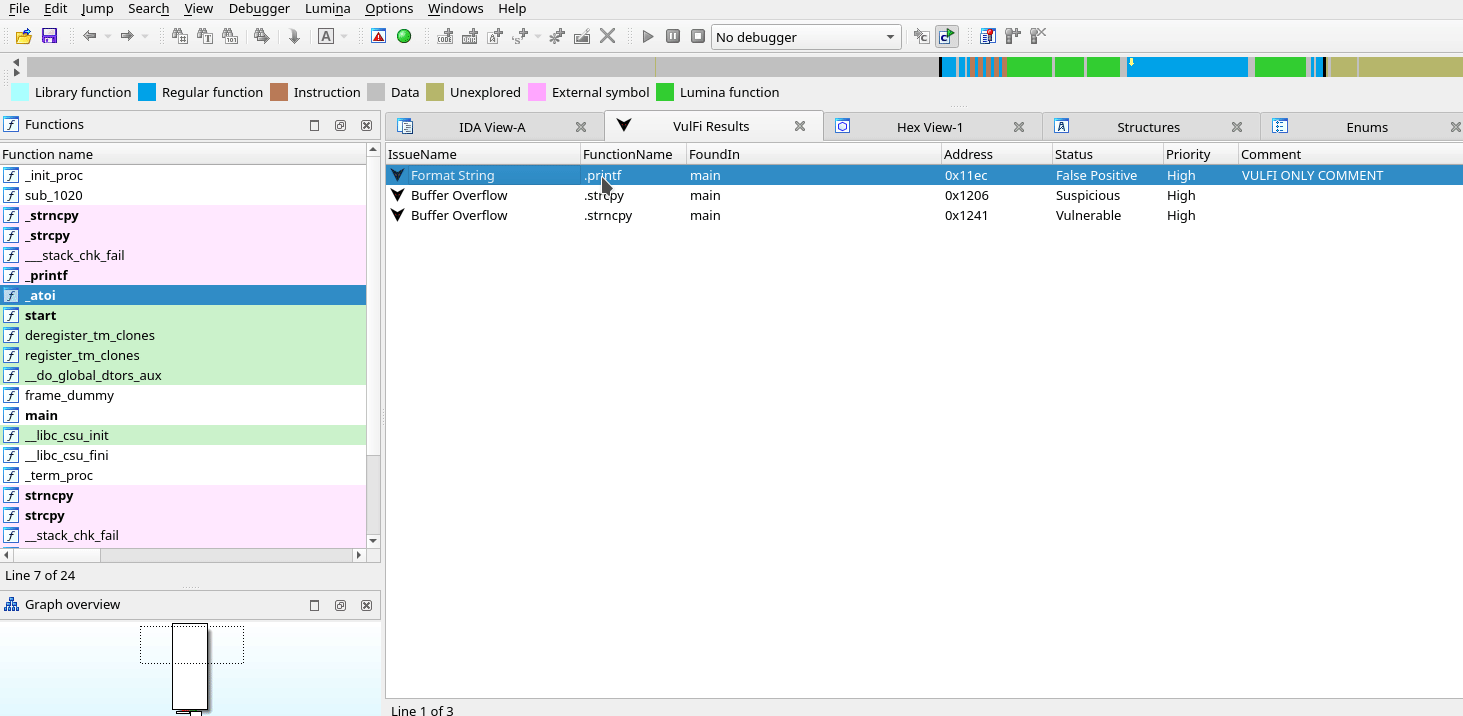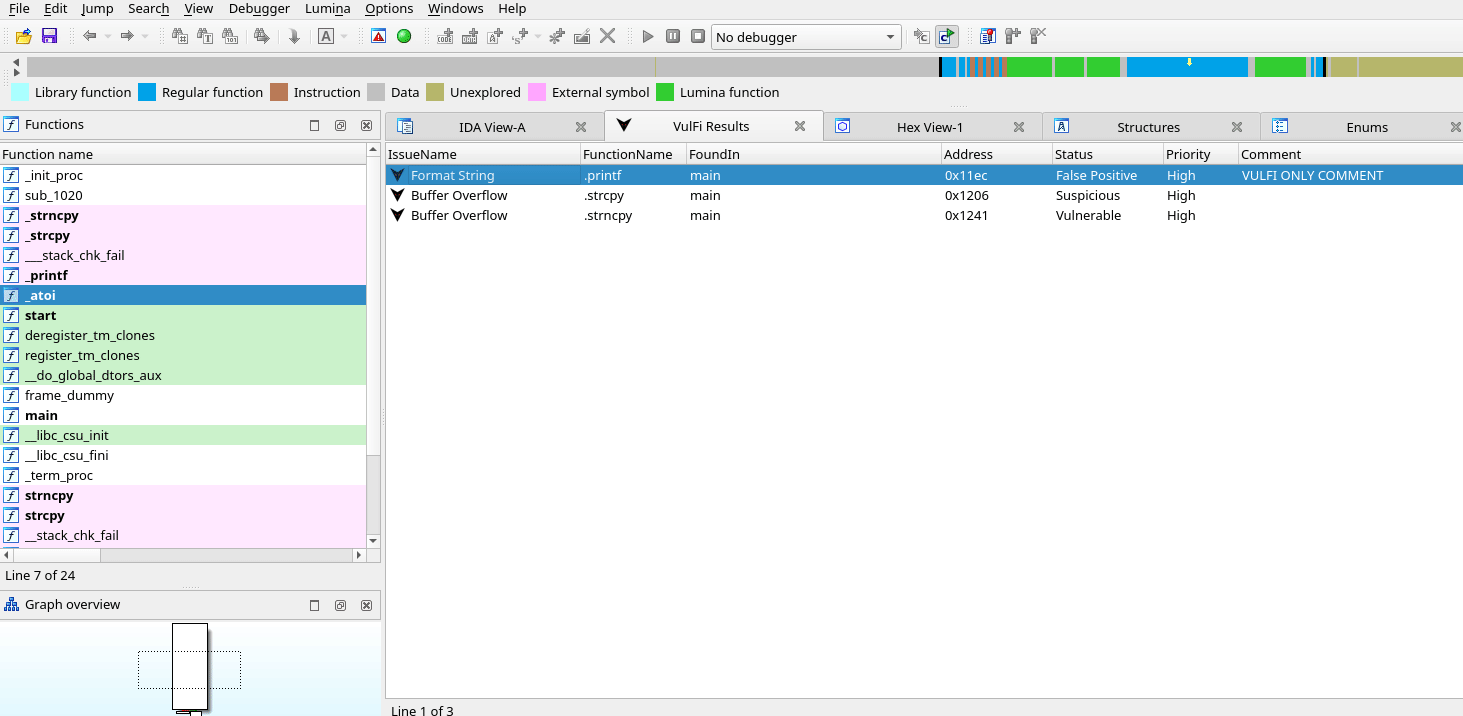 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.