

javascript-deobfuscator
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
code-analysisdynamic-code-analysismalware-analysis+4
2
lolcaken/javascript-deobfuscatorDeobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
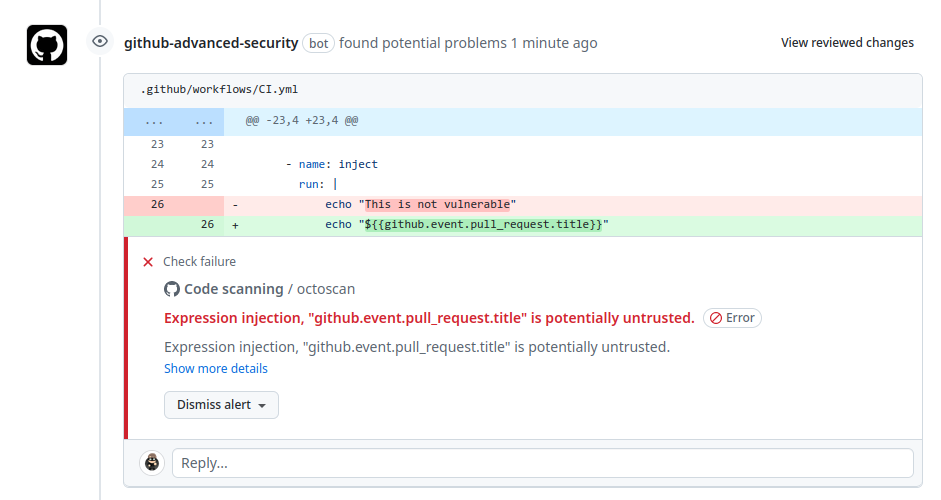 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 califio/ngxray
ngxray — nginx config security scanner
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx