

blitzstrike
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
exploitationinformation-gatheringpayload-generation+8
496
shinthink/blitzstrikeMCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
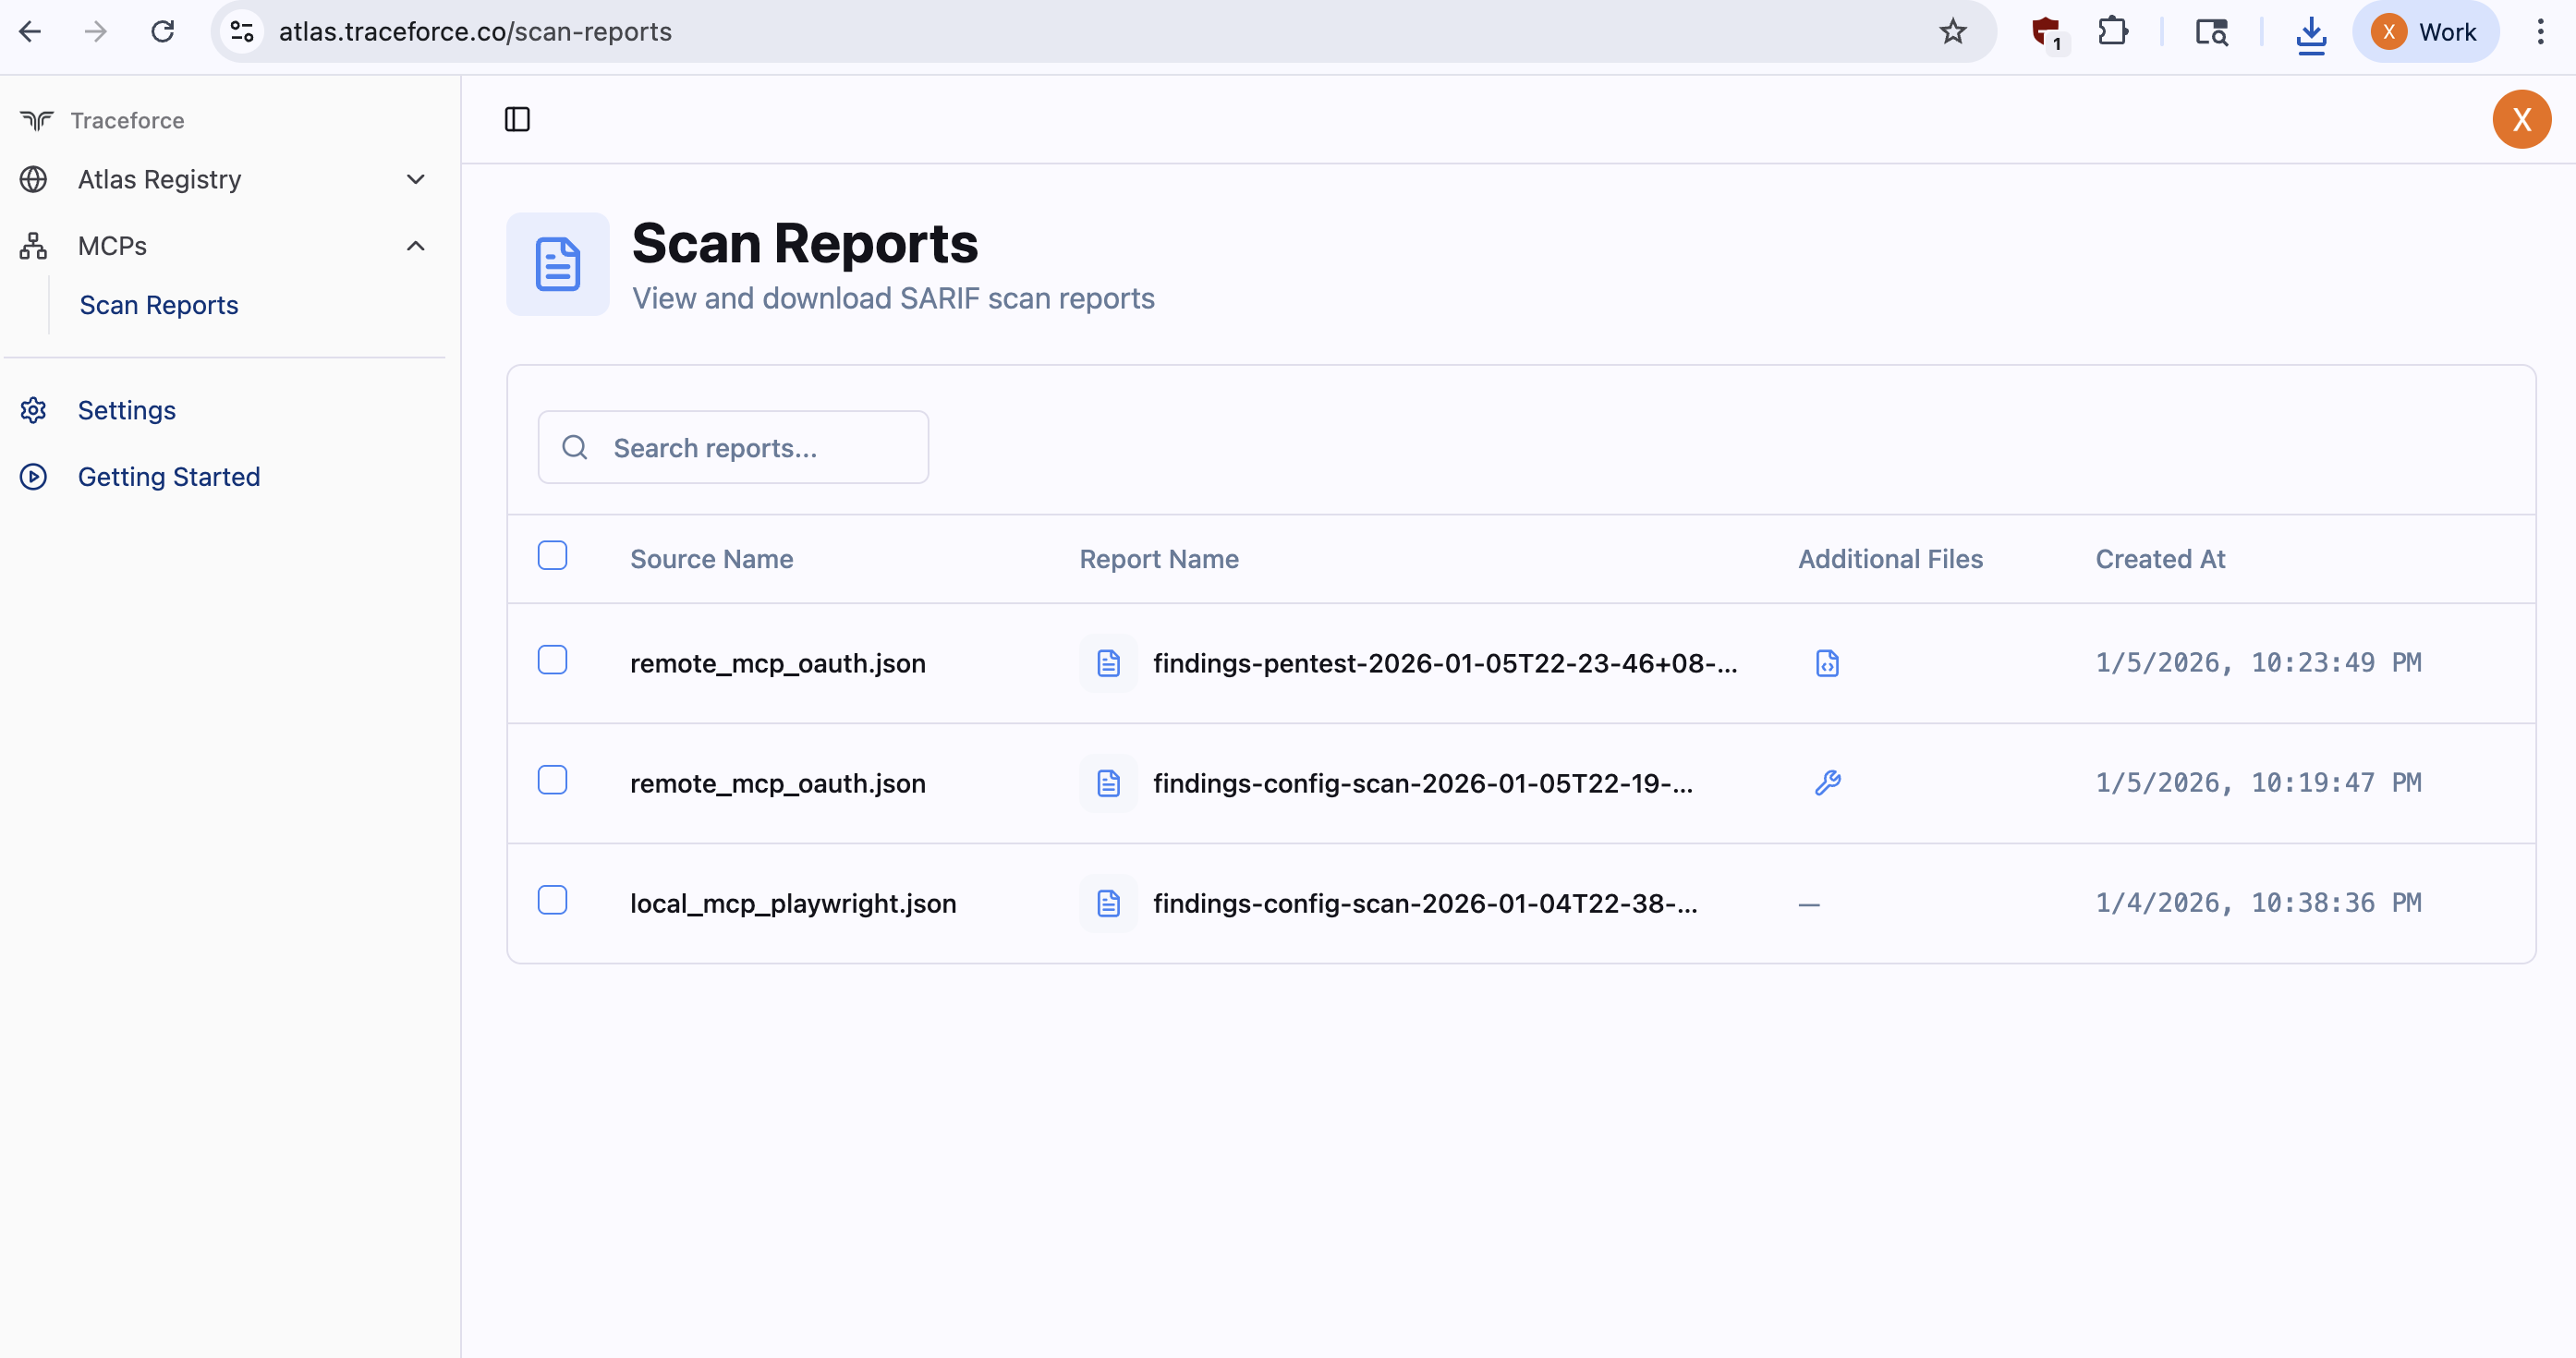 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
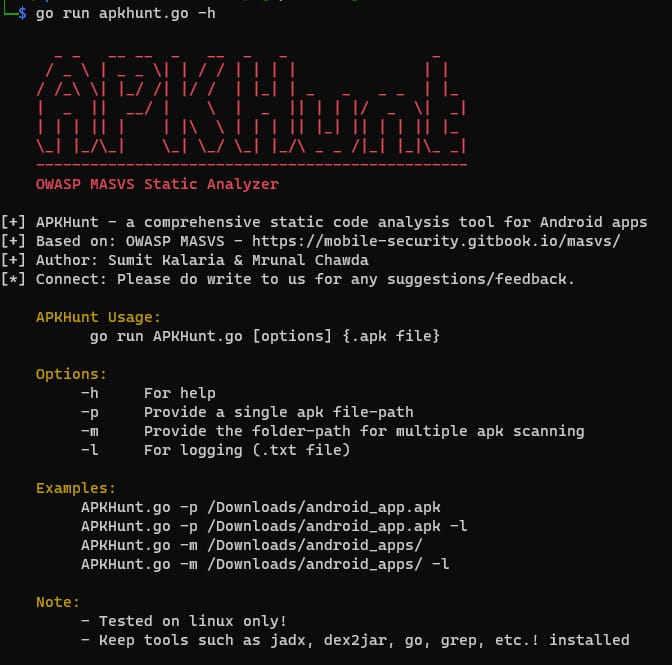 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 mergebase/log4j-detector
File-system scanner that detects vulnerable Log4J versions (CVE-2021-44228, CVE-2021-45046) by analyzing compiled Java classes, including nested…
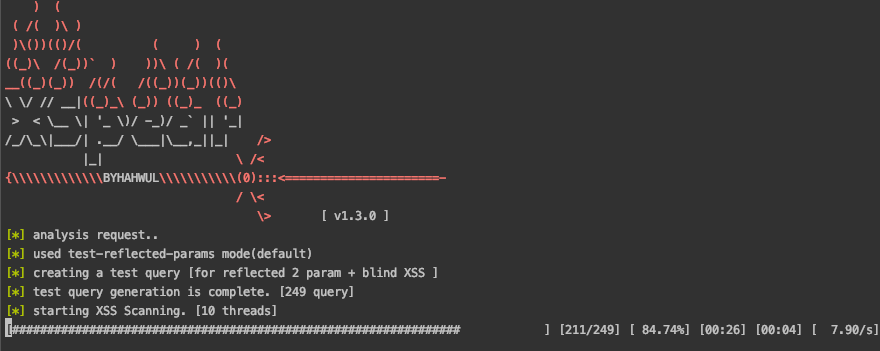 hahwul/xspear
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
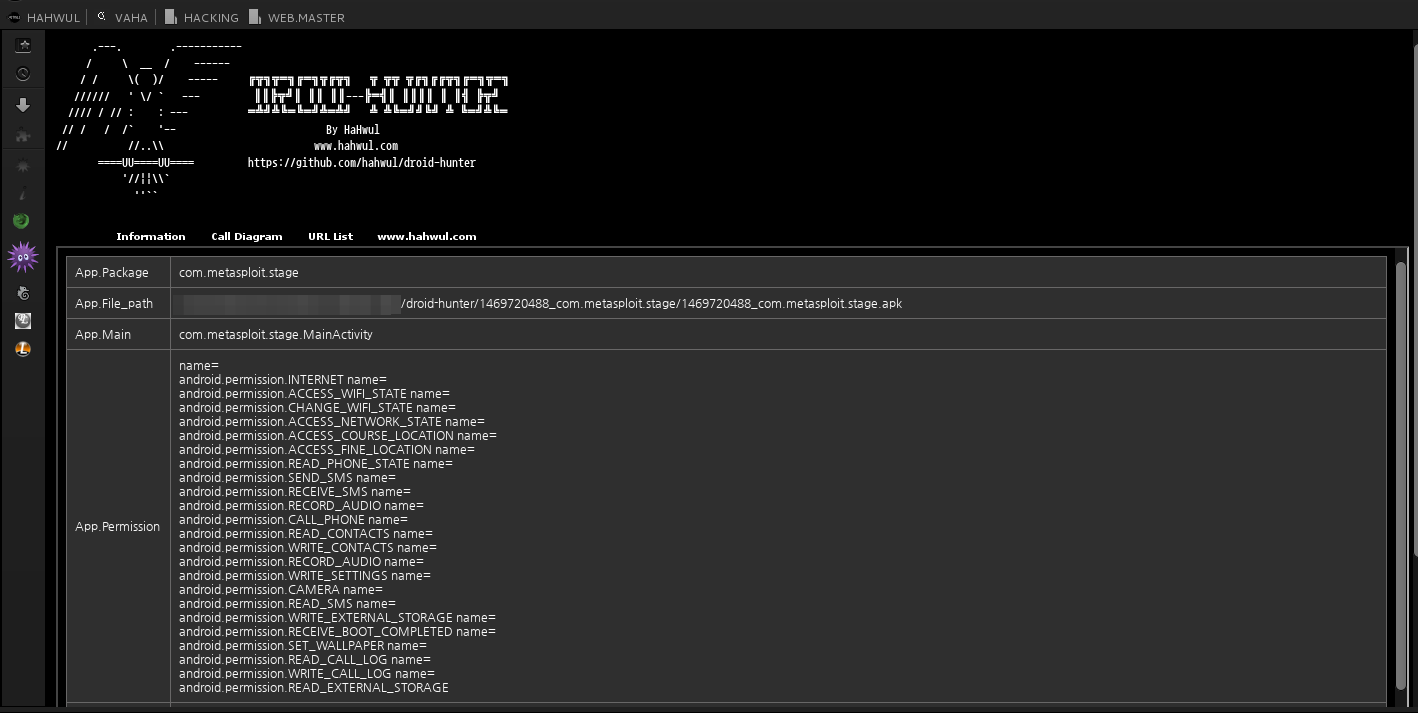 hahwul/droid-hunter
(deprecated) Android application vulnerability analysis and Android pentest tool