
kingfisher
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
cloud-securitycontainer-securitydevsecops+7
1.3k
mongodb/kingfisherDetect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
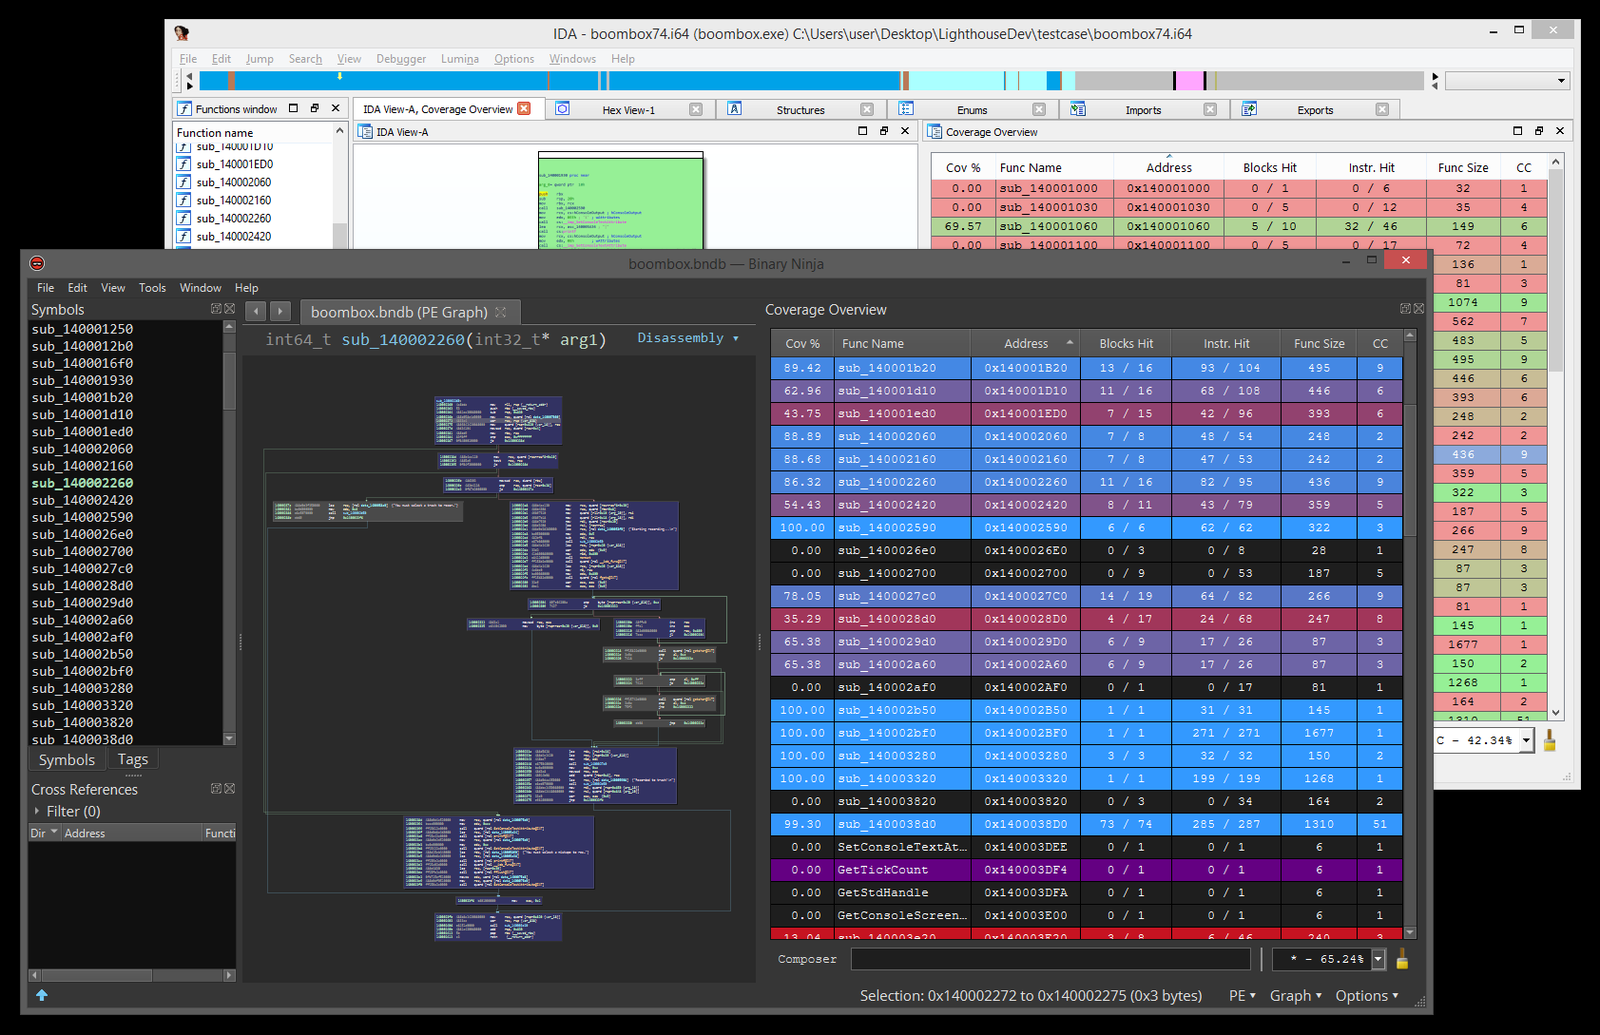 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 volexity/donut-decryptor
Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
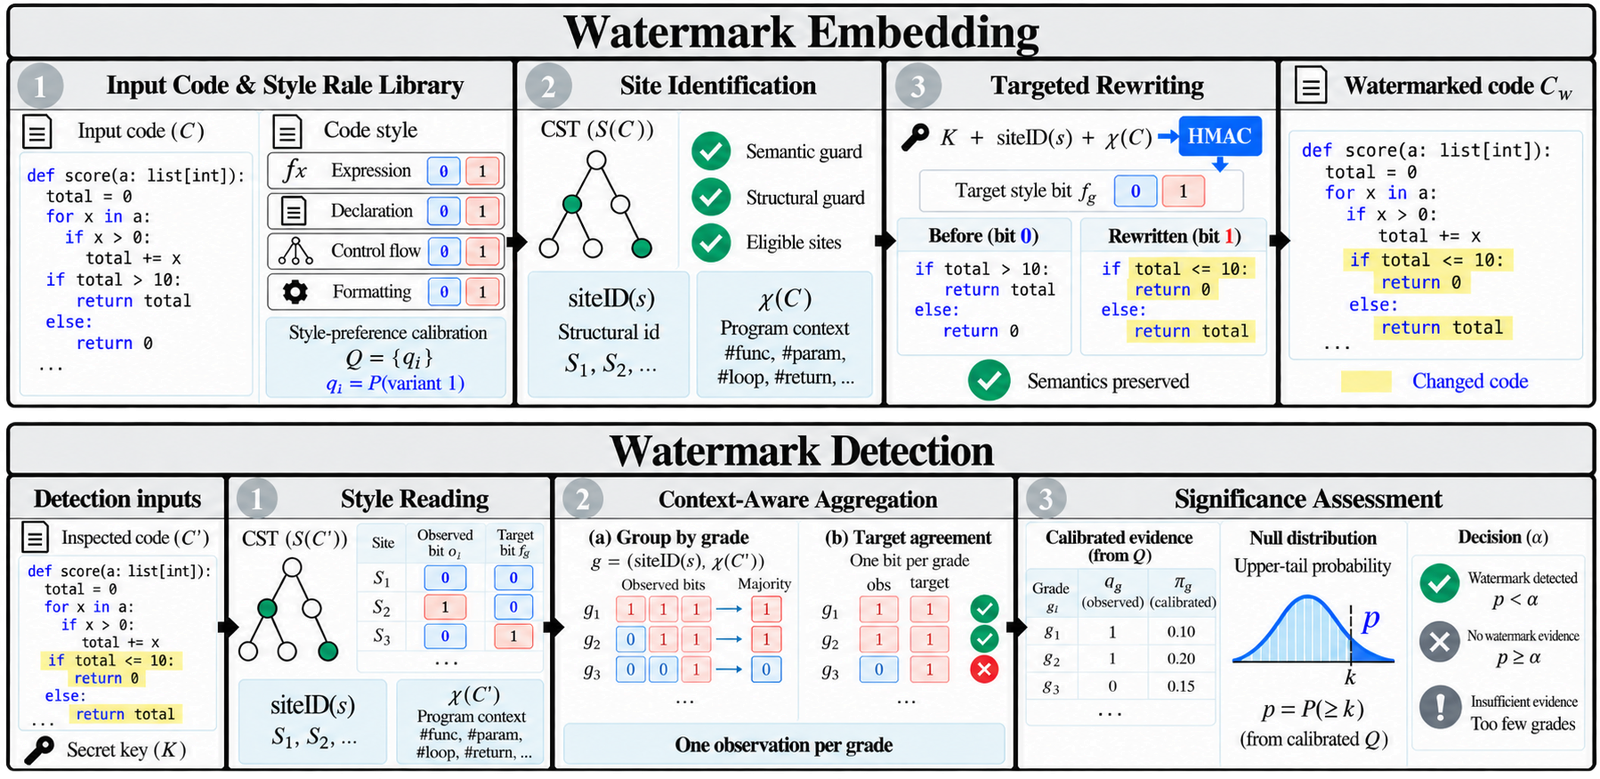 suhanmen/sew
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
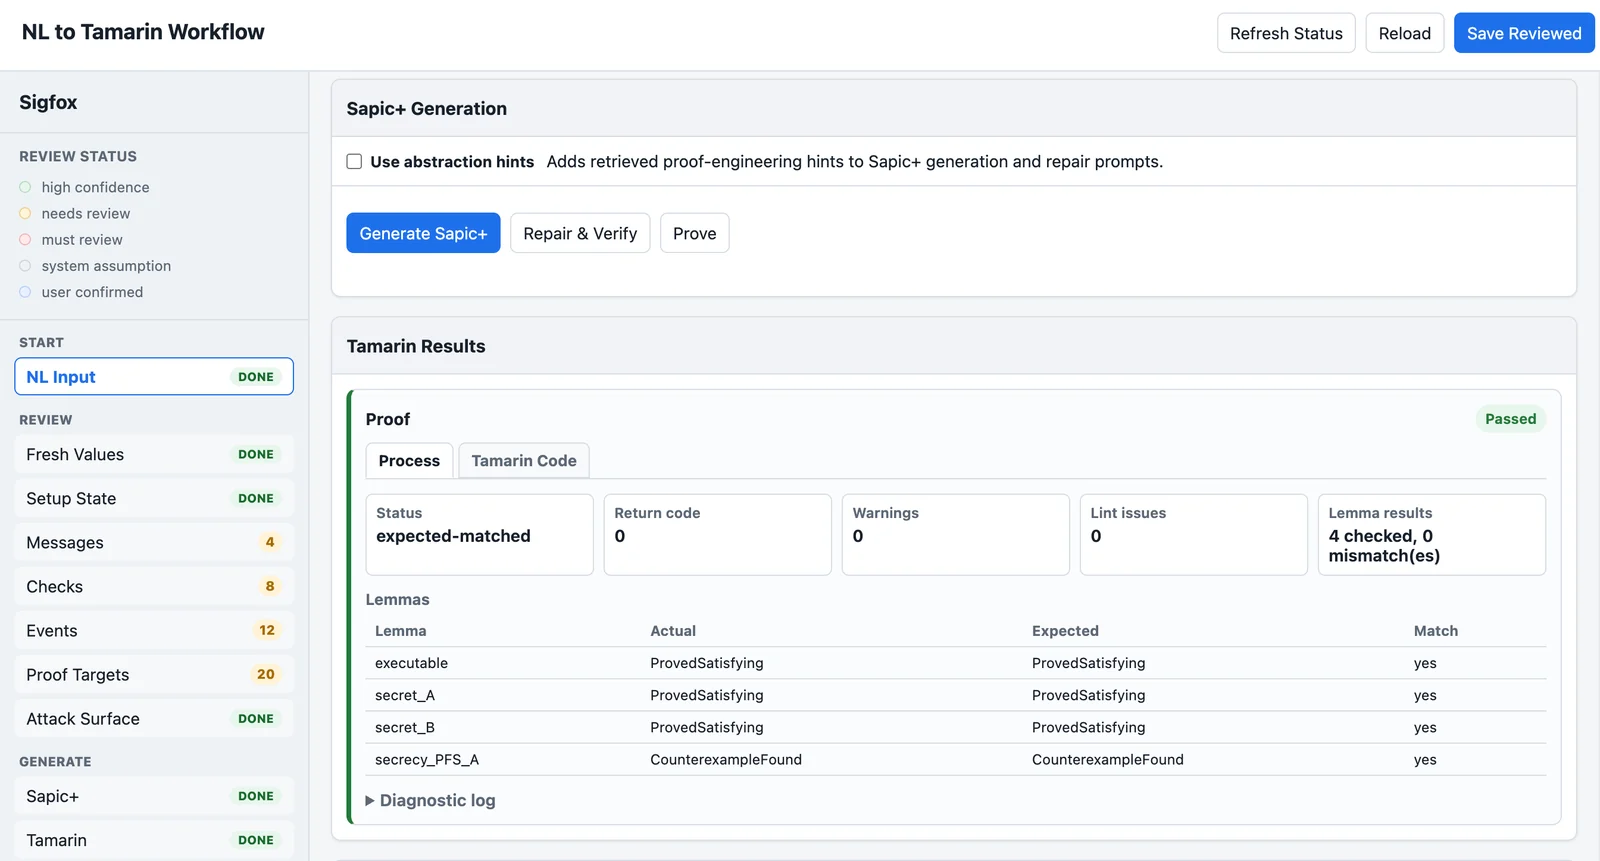 laplace1002/tamarinagent
Human-in-the-loop UI that converts natural-language or C/C++ protocol descriptions into a reviewable Protocol IR, then generates Sapic+/Tamarin…
 tls456/cve-2026-43805-poc
CVE-2026-43805 IOKit IODMACommand race analysis and proof of concept
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…