

CVE-2026-25645
 jaycelation/cve-2026-25645
Insecure Temp File Reuse in extract_zipped_paths()
exploitationpapers-researchstatic-analysis+2
jaycelation/cve-2026-25645Insecure Temp File Reuse in extract_zipped_paths()
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
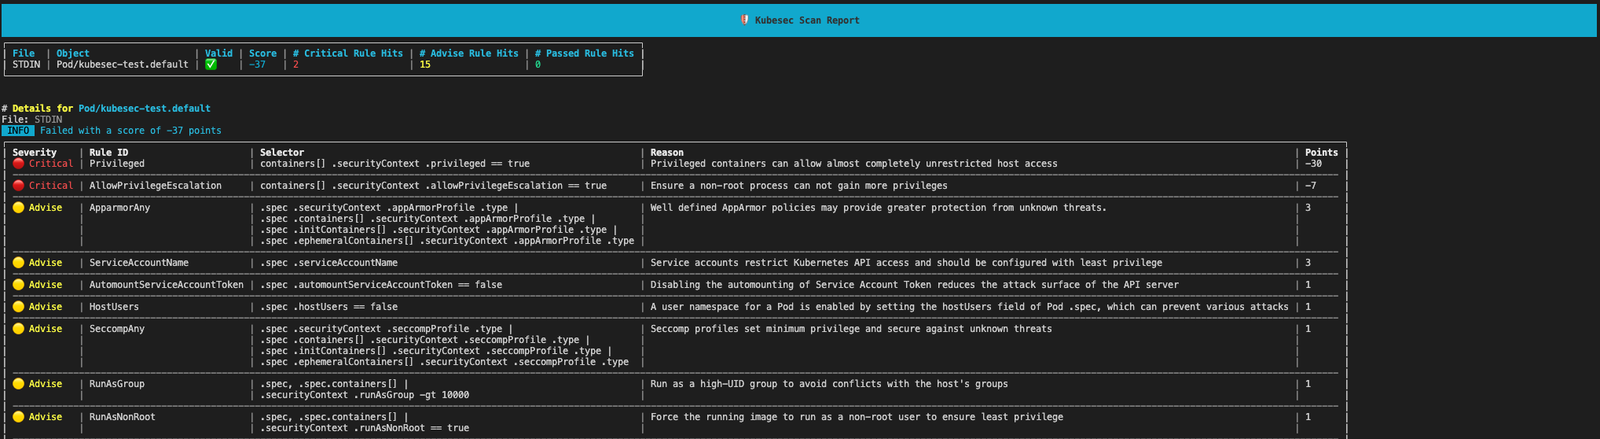 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
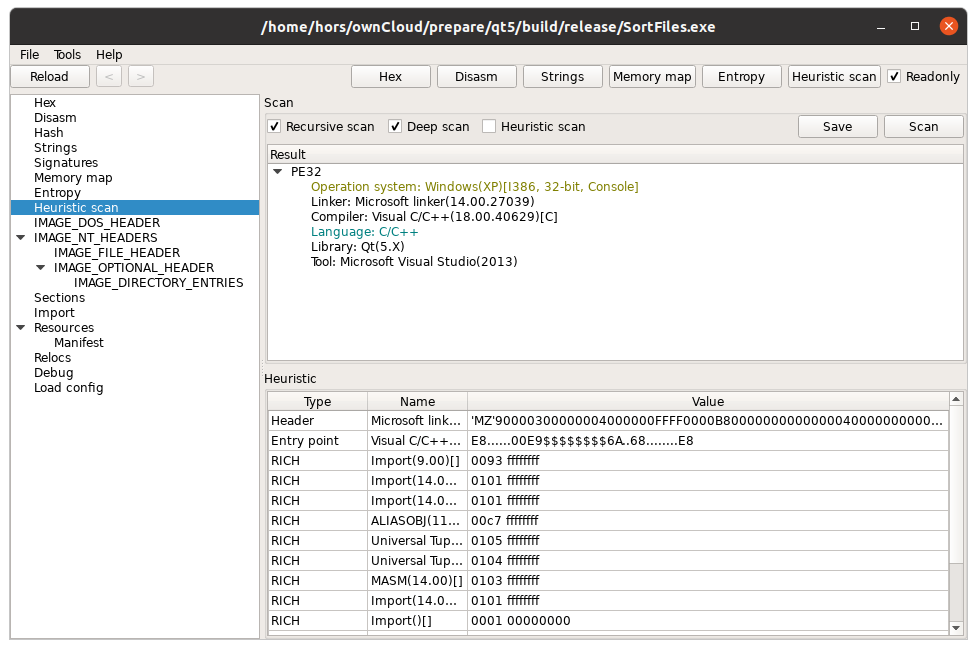 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter
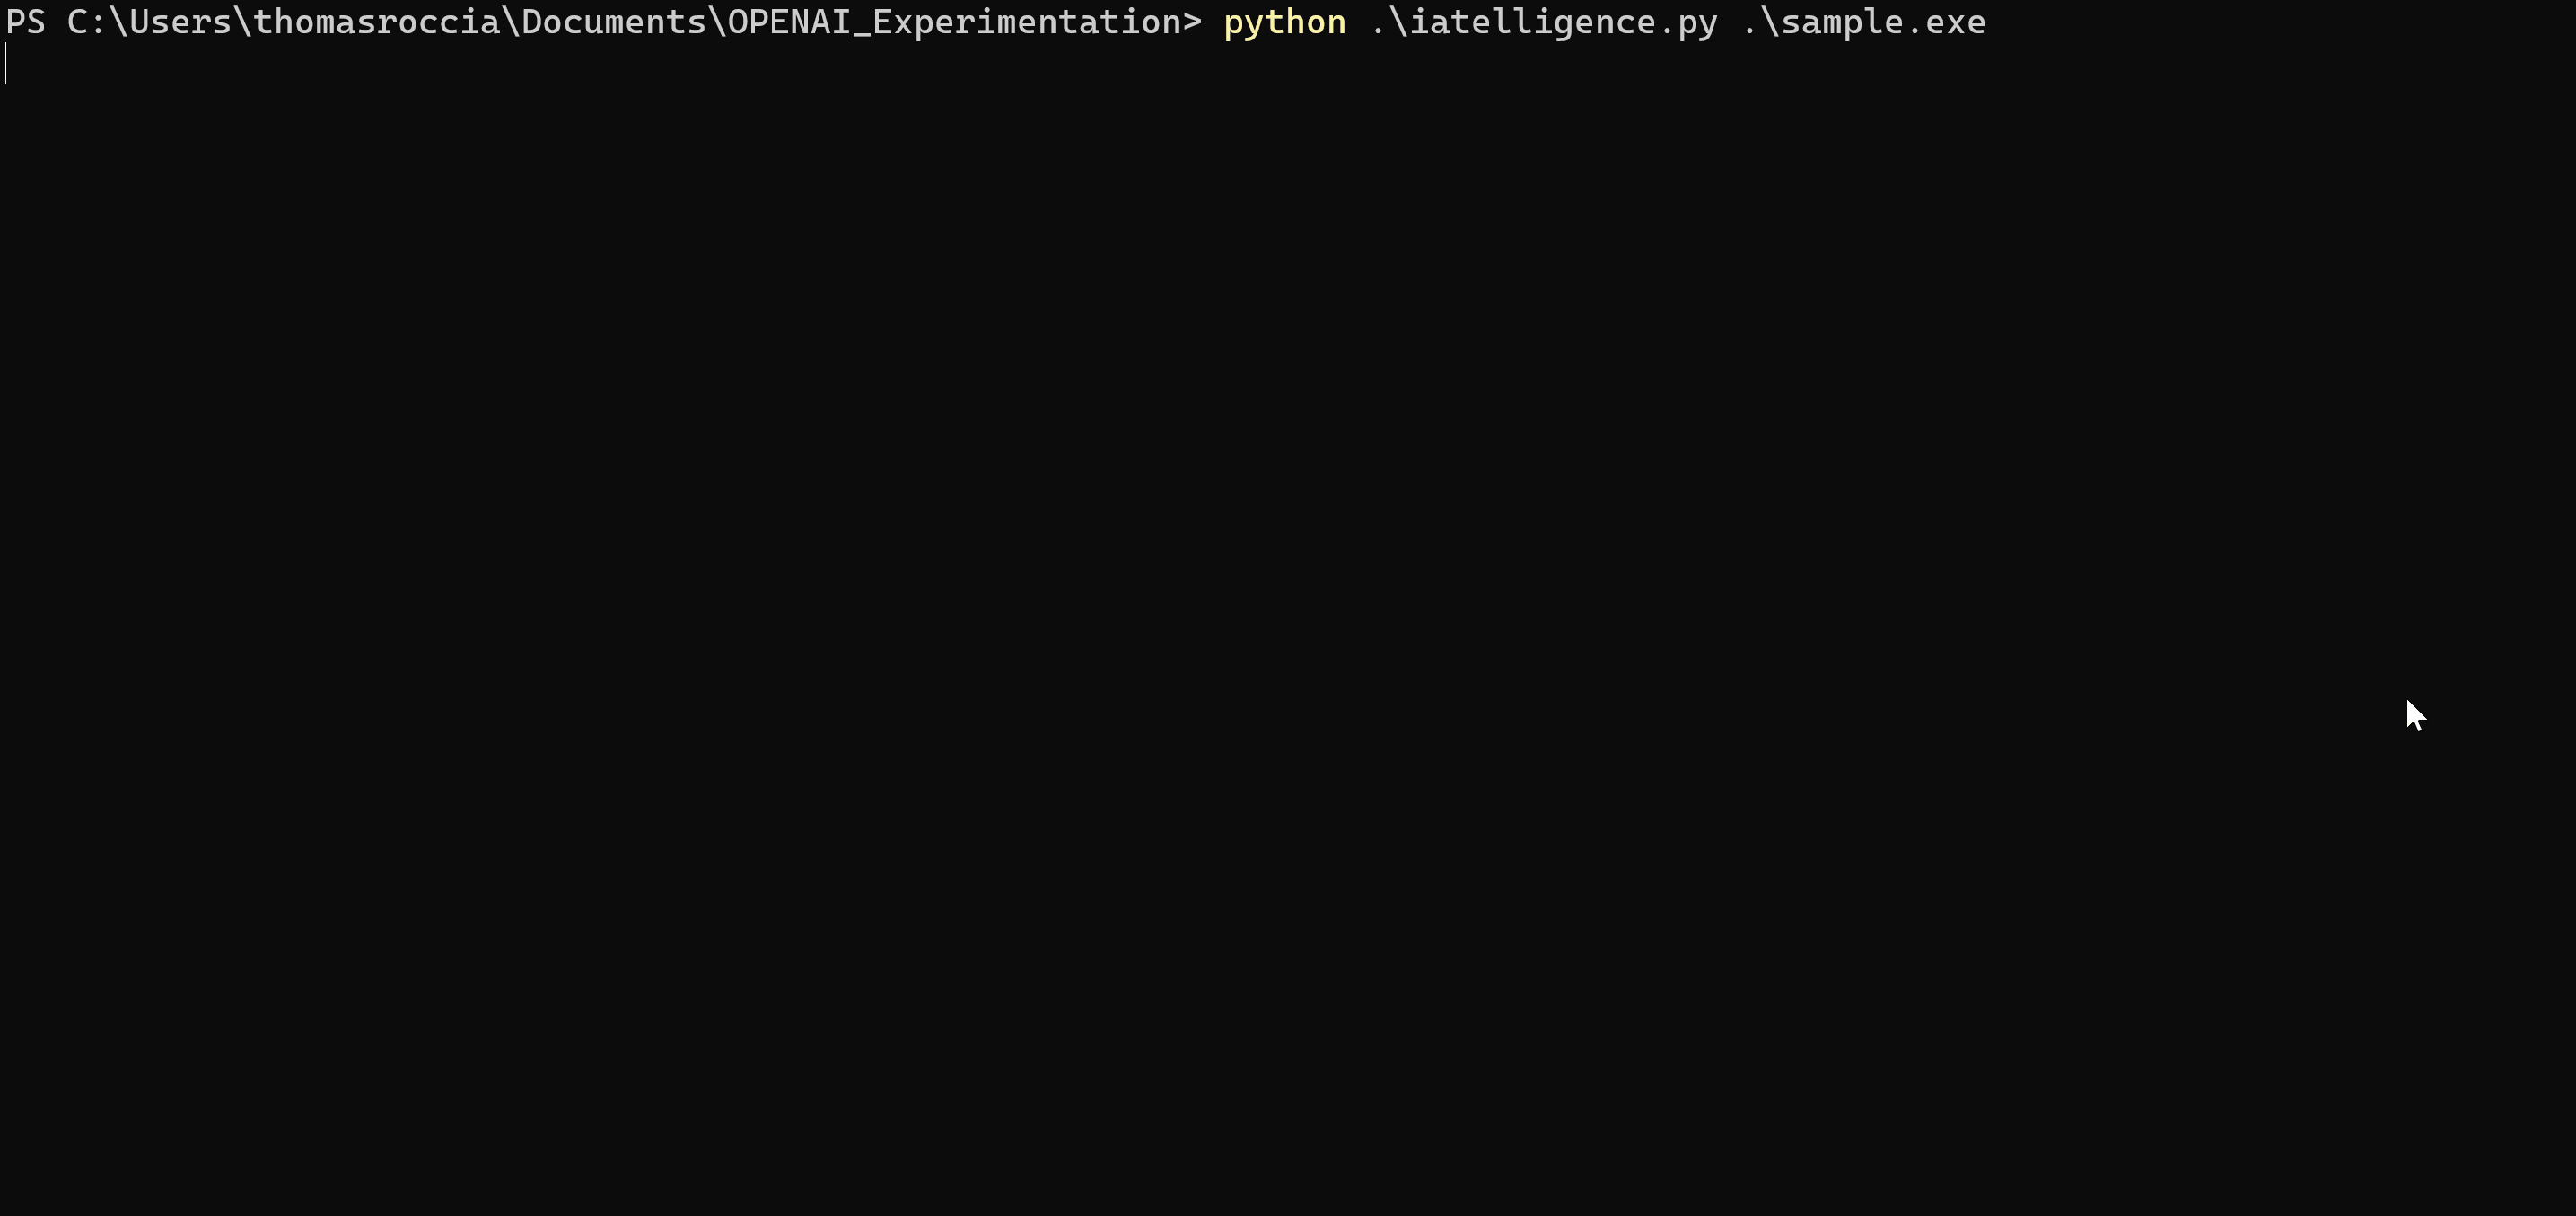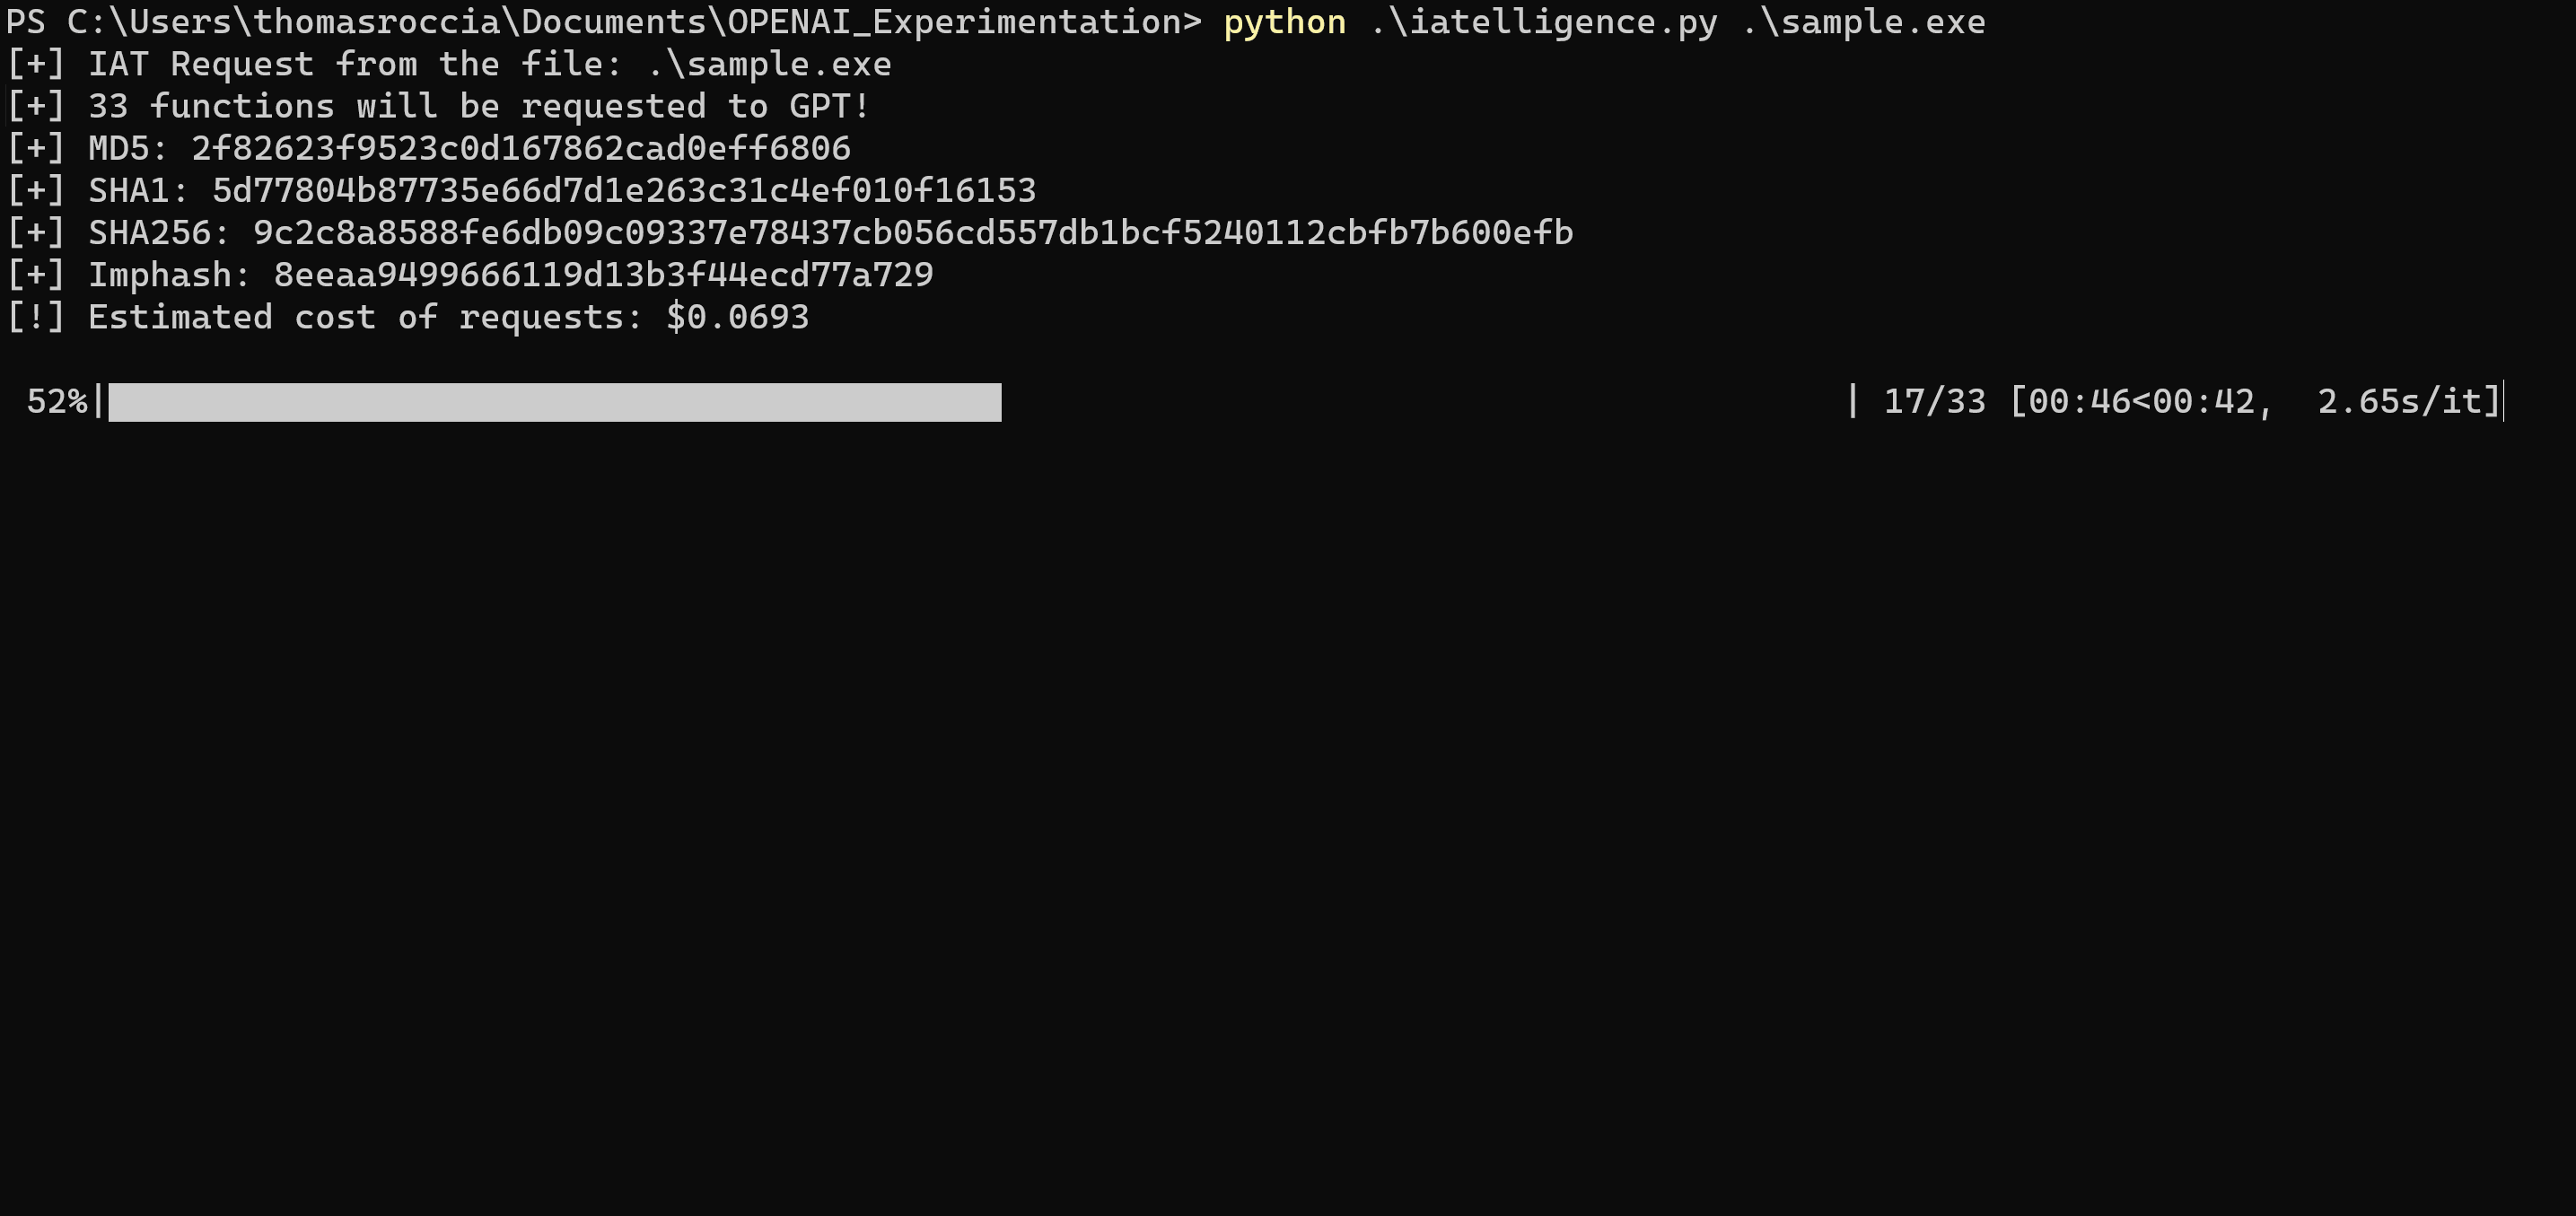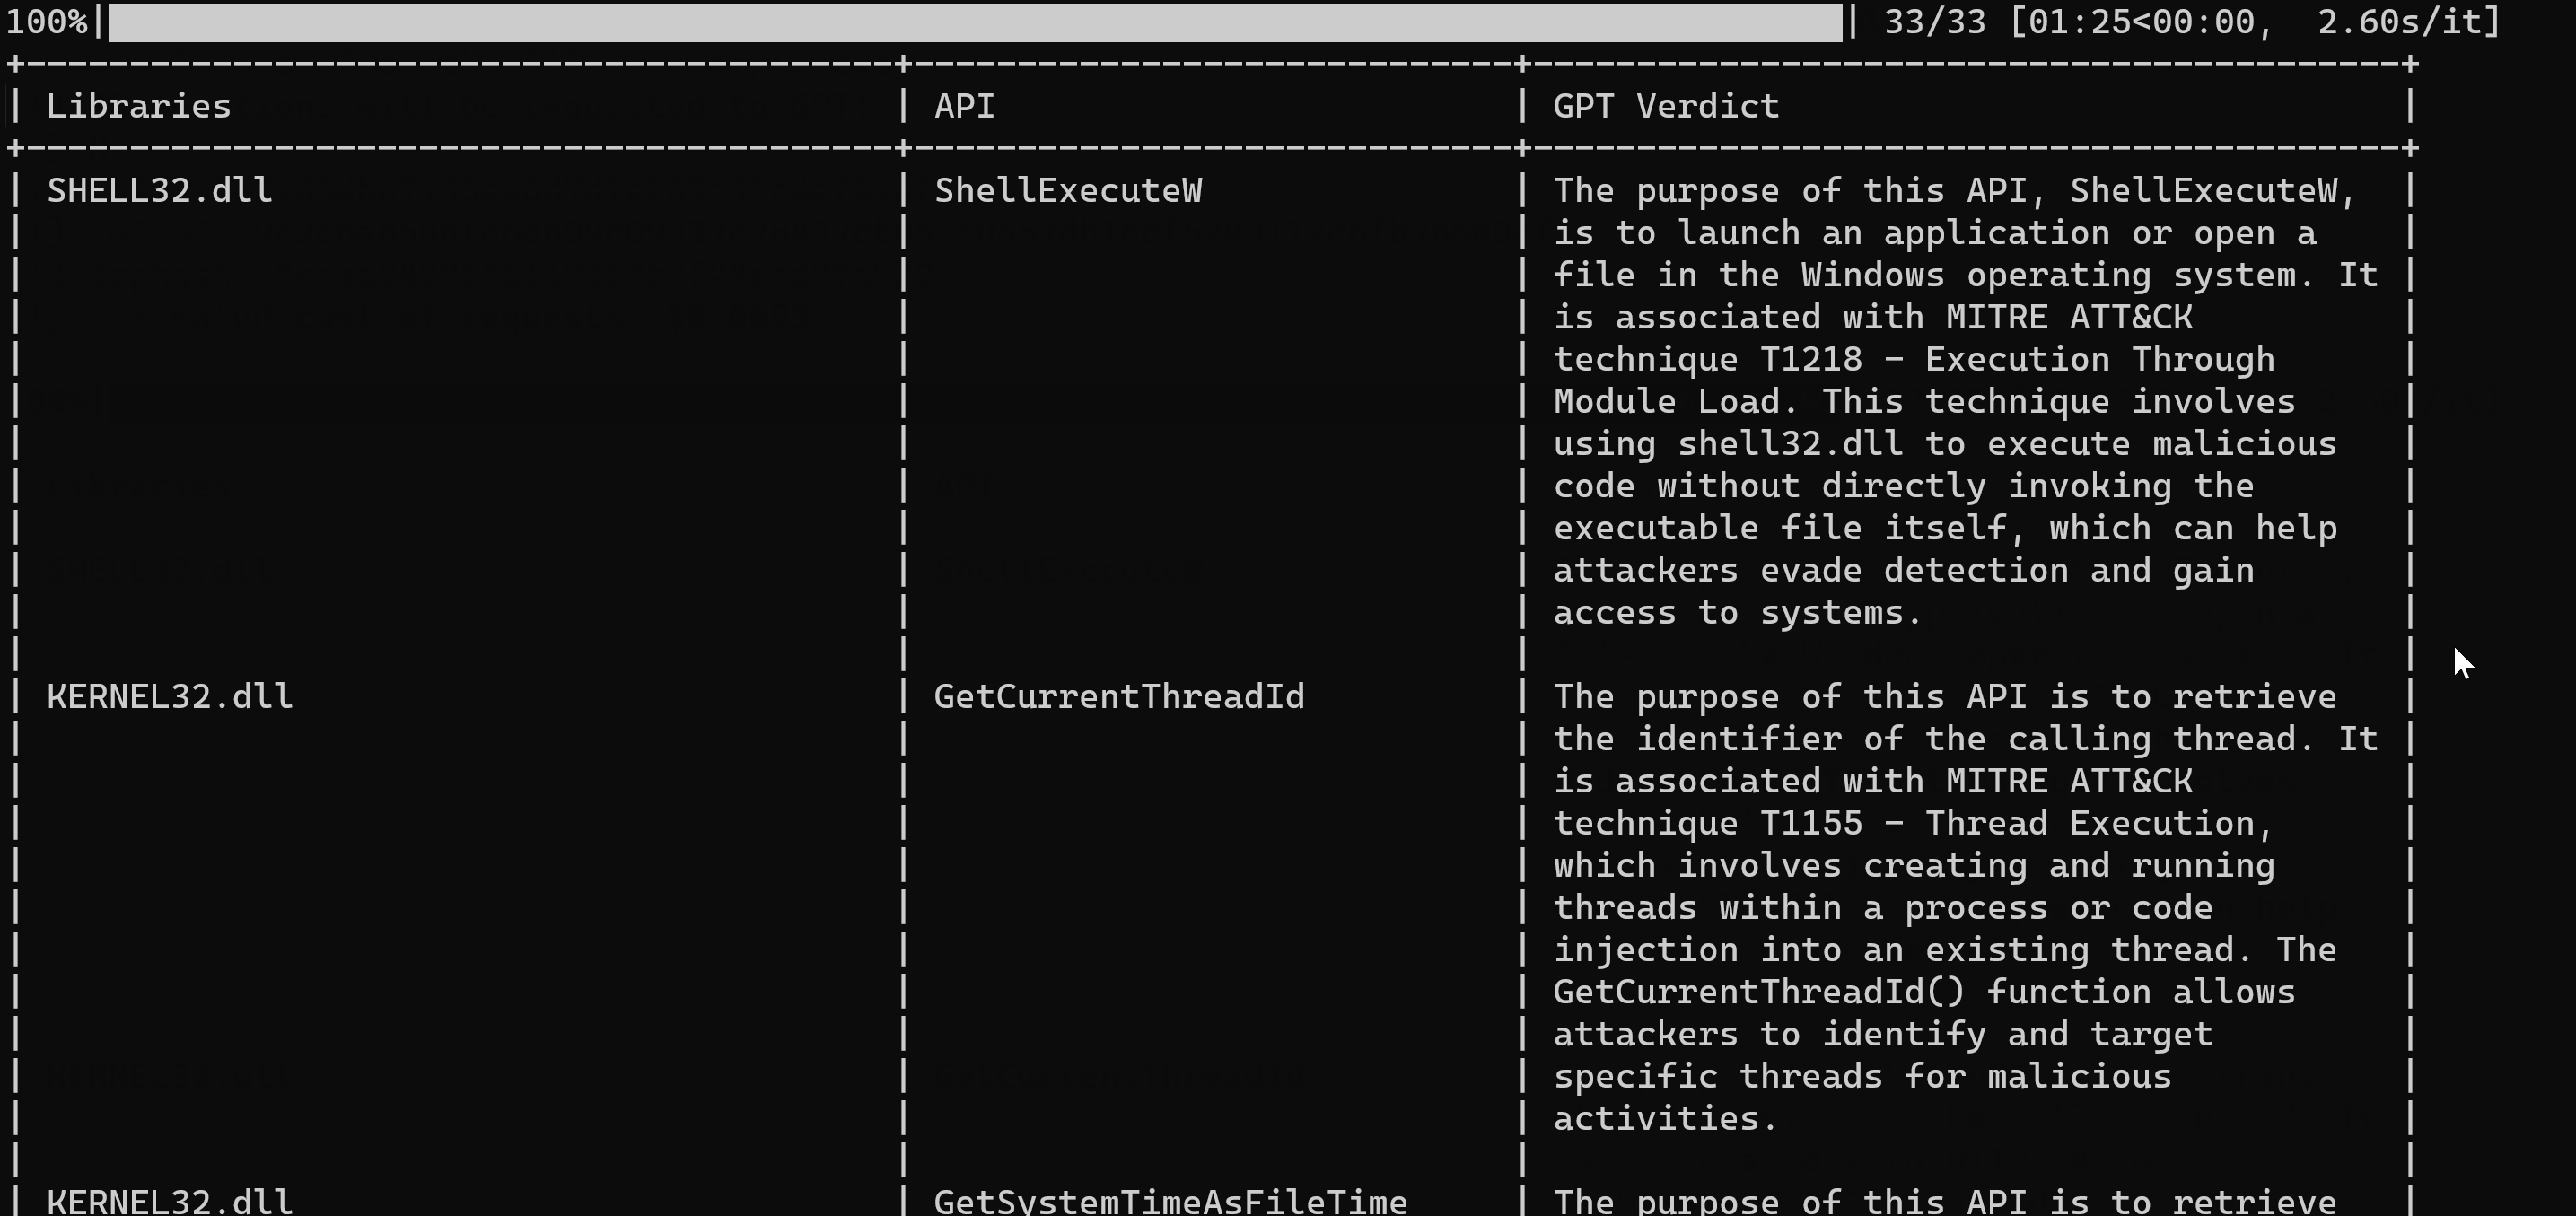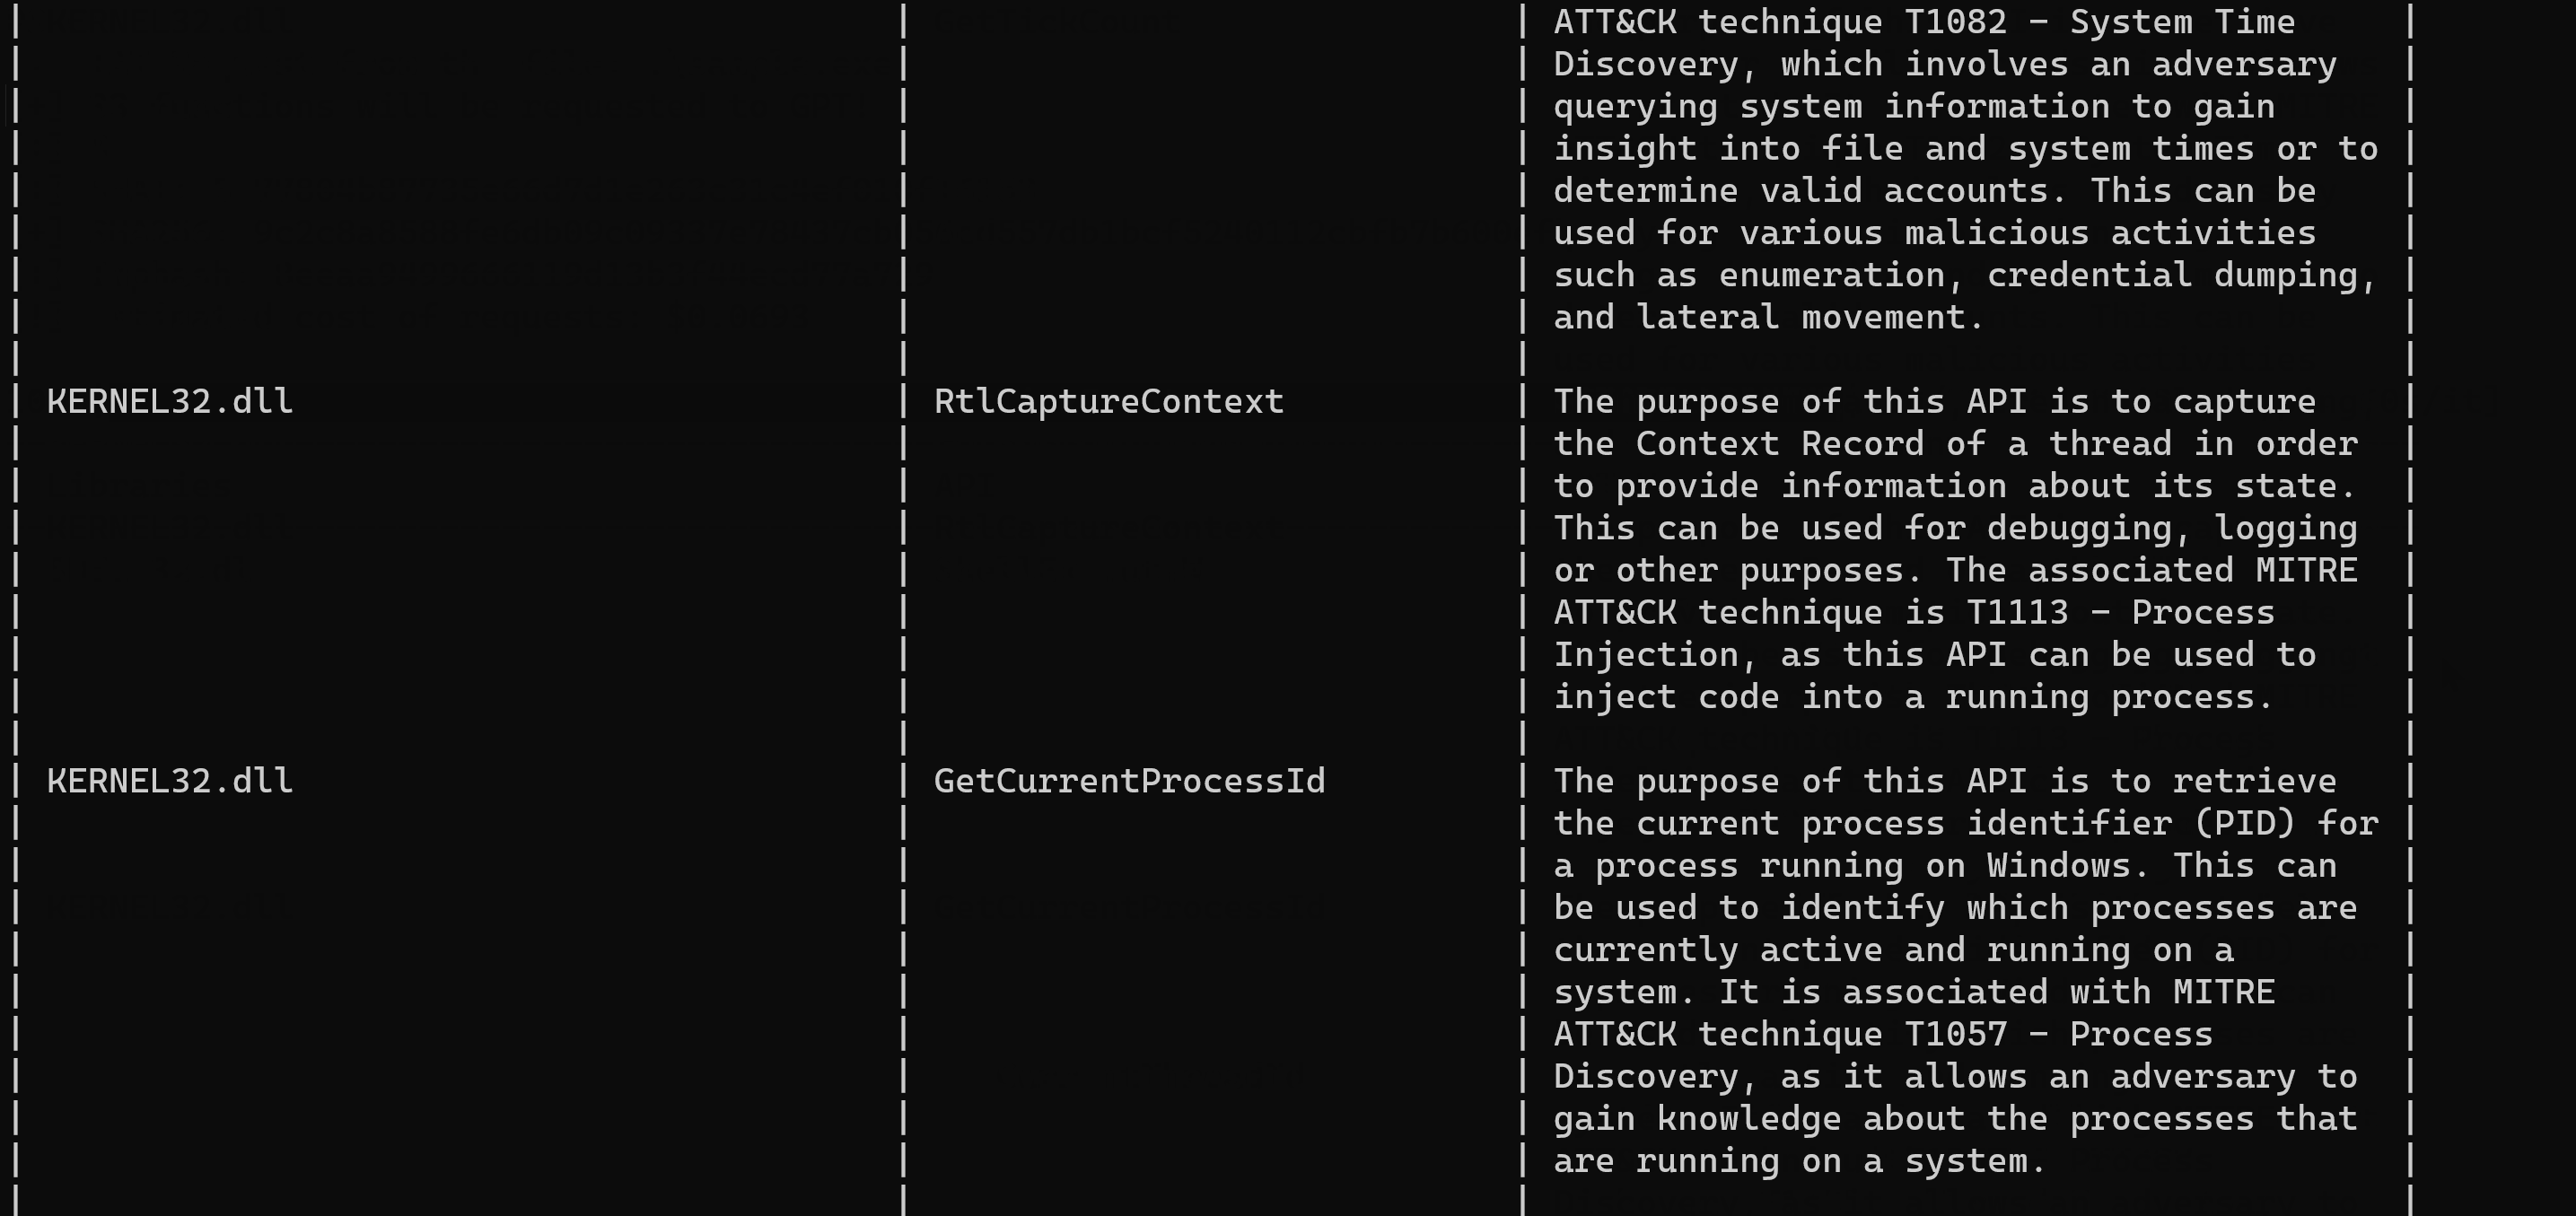 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 enferex/pdfresurrect
Analyze and help extract older "hidden" versions of a pdf from the current pdf.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…